OWASP CICD-Goat 的完整 VAPT 报告 — 捕获 9 个 CTFd flag,4 个严重 + 5 个高危发现(含 CVE-2024-23897),映射至 OWASP Top 10 CI/CD 安全风险,附 PoC、修复建议及面试速览摘要。

<div align="center"> # CICD-Goat VAPT 渗透测试报告 </div> > 针对 [OWASP CICD-Goat](https://github.com/cider-security-research/cicd-goat) 的完整漏洞评估与渗透测试——一个故意设计为存在漏洞的 CI/CD 环境(Jenkins、Gitea、GitLab、CTFd)——端到端映射至 **OWASP Top 10 CI/CD 安全风险**。 <div align="center"> [](https://github.com/cider-security-research/cicd-goat) [](./findings) [](./ctfd/challenge-cross-reference.md) [](./LICENSE.md) [](https://linkedin.com/in/dheerajkumarjayaswal) [](https://github.com/dheeraj-jayaswal) </div> --- ## 🧭 本仓库与我其他仓库的关系 | 仓库 | 内容简介 | |---|---| | **[CICD-Goat-Vapt-Writeup](https://github.com/dheeraj-jayaswal/CICD-Goat-Vapt-Writeup)** *(本仓库)* | 针对 OWASP CICD-Goat 的完整 VAPT 报告——包含 16 项发现(含 CVE-2024-23897),映射至 OWASP Top 10 CI/CD 安全风险,附 PoC 与面试级摘要 | | [From-Dev-To-Attacker](https://github.com/dheeraj-jayaswal/From-Dev-To-Attacker) | 我的旗舰实战日志——67 篇原创漏洞模式分析,以开发者视角撰写,涵盖所得税、银行、零售、电商、货运物流与教育等行业领域影响框架 | | [From-Pentester-To-Red-Teamer](https://github.com/dheeraj-jayaswal/From-Pentester-To-Red-Teamer) | 我从 Web/API 渗透测试转型红队的分阶段 24 个月路线图——阶段、实验环境、认证,以及公开记录的进展 | | [AppSec-From-The-Trenches](https://github.com/dheeraj-jayaswal/AppSec-From-The-Trenches) | 渗透测试工具与方法论参考——我实际如何使用 Burp Suite、Nmap、Metasploit、Hydra、Hashcat 等,以及我的 WAPT 方法论 | | [API-From-The-Trenches](https://github.com/dheeraj-jayaswal/API-From-The-Trenches) | API 安全深度系列——OWASP API Top 10 覆盖、BOLA、JWT 攻击、GraphQL 测试、完整方法论 | | [Bug-Bounty-Hunting-Companion](https://github.com/dheeraj-jayaswal/Bug-Bounty-Hunting-Companion) | 真实公开披露的漏洞赏金报告,拆解为可复现的检查清单 | | [DarkWeb-From-The-Trenches](https://github.com/dheeraj-jayaswal/DarkWeb-From-The-Trenches) | 威胁情报与暗网 OSINT 方法论——凭据泄露监控、勒索软件追踪、前期威胁情报 | | [.pcap-Arsenal](https://github.com/dheeraj-jayaswal/.pcap-Arsenal) | 按协议整理的抓包文件,用于 Web/API/网络层分析与学习 | | [Pentest-Engagement-Playbook](https://github.com/dheeraj-jayaswal/Pentest-Engagement-Playbook) | 顾问级范围界定、ROE、严重性判定依据与高管报告模板——项目背后的客户交付操作手册 | --- ## 为什么写这个 大多数 CI/CD 安全报告要么纯理论(一张幻灯片解释"管道投毒执行"),要么纯追 CTF flag(一句"这是 flag,下一个")。本仓库两者皆非:以下每一项发现都是**经过完整验证、有 PoC 支撑的漏洞**,映射至具体的 [OWASP CI/CD-SEC](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/docs/02-owasp-top10-cicd-mapping.md) 风险类别,以你在面试或真实客户报告中实际想要表达的方式撰写——包括死胡同、错误假设,以及它们是如何被纠正的。 如果你正在准备 AppSec/DevSecOps/CI-CD 安全面试,正在为涉及 CI/CD 工具链的渗透测试项目做准备,或者只是想亲手、具体地了解“Poisoned Pipeline Execution”或“Insufficient Credential Hygiene”在实际流量中究竟是什么样子——这份材料就是为你写的。 ## 目标环境 | 字段 | 值 | |---|---| | 目标 | [OWASP CICD-Goat](https://github.com/cider-security-research/cicd-goat) — 本地 Docker Compose 部署 | | 项目类型 | 经授权的自主学习实验环境(灰盒) | | 技术栈 | Jenkins 2.332.1、Gitea 1.16.5、GitLab 15.11.13-ee、CTFd、Docker Compose | | 范围 | `localhost:3000`(Gitea)、`:8080`/`:50000`(Jenkins)、`:4000`(GitLab)、`:8000`(CTFd)、`:8008`(prod-sim) | | 方法论 | 阶段 0–3(范围界定 → 指纹识别 → 漏洞识别 → 利用) | 完整交战规则:[`docs/00-engagement-overview.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/docs/00-engagement-overview.md)。 > ⚠️ **本仓库中的所有测试均针对测试者自己的本地、一次性、故意存在漏洞的 Docker Compose 实验环境执行。** 未涉及任何生产系统、共享基础设施或第三方数据。在自行尝试任何内容之前,请先从[官方仓库](https://github.com/cider-security-research/cicd-goat)启动你自己的 CICD-Goat 副本。 ## 结果一览 | ID | 标题 | 严重性 | OWASP CI/CD 映射 | CTFd Flag | |---|---|---|---|---| | [F-010](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-010-jenkins-secrets-exposure-console-logs.md) | Jenkins 构建控制台日志中的机密泄露 → 凭据窃取 → 未授权仓库写入 | **CRITICAL** | CICD-SEC-6, -4, -2 | flag1, flag2 | | [F-013](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-013-insecure-automerge-bypass.md) | 不安全的自动合并逻辑绕过代码审查(PR 范围的词差异启发式) | **CRITICAL** | CICD-SEC-1, -5 | flag10 | | [F-016](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-016-CVE-2024-23897-jenkins-cli-arbitrary-file-read.md) | CVE-2024-23897 — Jenkins CLI 在控制器上的任意文件读取 | **CRITICAL** | CICD-SEC-7 | flag8 | | [F-017](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-017-gitlab-runner-token-secret-theft.md) | GitLab 共享运行器注册令牌 → 实例范围的 CI/CD 机密窃取 | **CRITICAL** | CICD-SEC-2, -6 | flag11 | | [F-019](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-019-jenkins-controller-rce-agent-label-override.md) | 通过代理标签覆盖实现 Jenkins 控制器节点代码执行 | **CRITICAL** | CICD-SEC-5, -4 | flag5 | | [F-018](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-018-decoupled-pipeline-branch-exclusion-bypass.md) | 解耦流水线仓库 + 分支排除过滤器绕过 | HIGH | CICD-SEC-4, -6 | flag3 | | [F-020](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-020-shared-agent-filesystem-credential-leak.md) | 共享代理文件系统暴露 FreeStyle 作业凭据 | HIGH | CICD-SEC-6, -5 | flag6 | | [F-021](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-021-checkov-sast-config-override-bypass.md) | Checkov SAST 配置覆盖导致未被检测到的 IaC 错误配置 | HIGH | CICD-SEC-1, -8 | flag7 | | [F-014](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-014-flask-secret-key-cicd-variable.md) | 从 CI/CD 流水线变量派生的 Flask 会话密钥 | HIGH | CICD-SEC-6 | flag11(经由 F-017) | 另有 **6 项信息性 / 辅助性发现**(阳性对照、RBAC 边界确认、轻微信息泄露)位于 [`findings/informational/`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/informational)。 ### 各项发现如何串联 若干发现并非彼此独立——一项发现会直接促成或补全另一项。这部分在面试中往往比任何单项发现本身更能给人留下印象: 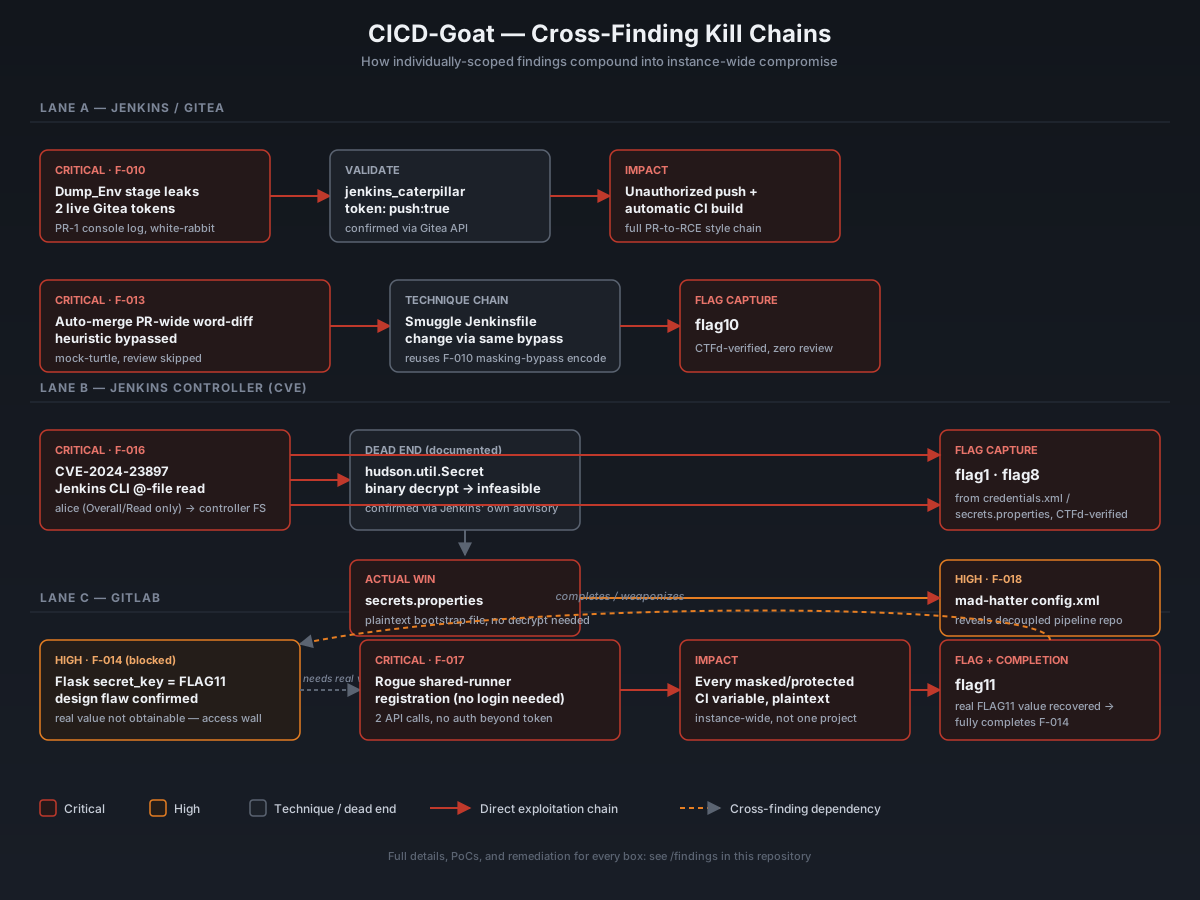 **11 个 CTFd 挑战中已解决并验证 flag 的有 9 个**——请参阅完整的[挑战交叉引用](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/ctfd/challenge-cross-reference.md),其中包括一个如实记录的案例(Dormouse/flag9),在该案例中访问控制边界在持续攻击下依然守住。 ## 完整目录 以下每个文件都直接链接——文件夹树只是展示它们的组织方式。 ### 📋 交战文档 | 文件 | 内容 | |---|---| | [`docs/00-engagement-overview.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/docs/00-engagement-overview.md) | 交战规则、范围、技术栈 | | [`docs/01-methodology.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/docs/01-methodology.md) | 贯穿始终的分阶段测试方法论 | | [`docs/02-owasp-top10-cicd-mapping.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/docs/02-owasp-top10-cicd-mapping.md) | 完整的 CICD-SEC-1 至 -10 参考分类体系 | | [`docs/03-remediation-roadmap.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/docs/03-remediation-roadmap.md) | 按优先级排列的可操作修复清单 | | [`docs/04-interview-prep.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/docs/04-interview-prep.md) | 每项发现的口语化摘要 + 可能的后续问题 | | [`docs/05-lessons-learned.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/docs/05-lessons-learned.md) | 回顾——哪些有效、哪些无效、下次应如何改进 | ### 🔍 侦察 | 文件 | 内容 | |---|---| | [`recon/01-fingerprinting.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/recon/01-fingerprinting.md) | 阶段 1——对范围内每项服务进行未认证指纹识别 | | [`recon/02-authenticated-enumeration.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/recon/02-authenticated-enumeration.md) | 阶段 2——获得初始访问后进行认证枚举 | ### 🚨 严重与高危发现 | 文件 | |---| | [F-010 — Jenkins 通过控制台日志泄露机密](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-010-jenkins-secrets-exposure-console-logs.md) | | [F-013 — 不安全的自动合并绕过](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-013-insecure-automerge-bypass.md) | | [F-014 — 来自 CI/CD 变量的 Flask 密钥](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-014-flask-secret-key-cicd-variable.md) | | [F-016 — CVE-2024-23897 Jenkins CLI 任意文件读取](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-016-CVE-2024-23897-jenkins-cli-arbitrary-file-read.md) | | [F-017 — GitLab runner 令牌机密窃取](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-017-gitlab-runner-token-secret-theft.md) | | [F-018 — 解耦流水线分支排除绕过](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-018-decoupled-pipeline-branch-exclusion-bypass.md) | | [F-019 — 通过 agent 标签覆盖实现 Jenkins 控制器 RCE](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-019-jenkins-controller-rce-agent-label-override.md) | | [F-020 — 共享 agent 文件系统凭据泄露](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-020-shared-agent-filesystem-credential-leak.md) | | [F-021 — Checkov SAST 配置覆盖绕过](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/F-021-checkov-sast-config-override-bypass.md) | ### ℹ️ 信息性 / 辅助发现 | 文件 | |---| | [F-006 — 私有仓库枚举缺口](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/informational/F-006-private-repo-enumeration-gap.md) | | [F-007 — 额外的 Jenkins 用户](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/informational/F-007-additional-jenkins-user.md) | | [F-009 — Job Read 与 ExtendedRead](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/informational/F-009-job-read-vs-extendedread.md) | | [F-011 — 正确的 withCredentials 用法(阳性对照)](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/informational/F-011-correct-withcredentials-usage.md) | | [F-012 — 凭据 API 连接中断](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/informational/F-012-credentials-api-connection-drop.md) | | [F-015 — 匿名镜像仓库枚举](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/findings/informational/F-015-anonymous-registry-enumeration.md) | ### 🎯 CTFd | 文件 | 内容 | |---|---| | [`ctfd/challenge-cross-reference.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/ctfd/challenge-cross-reference.md) | 完整的逐 flag 交叉引用,包括受阻的 Dormouse/flag9 调查和 Duchess/flag4 更正 | ## 仓库结构 ``` . ├── docs/ # Engagement context, methodology, mappings, remediation, interview prep │ ├── 00-engagement-overview.md │ ├── 01-methodology.md │ ├── 02-owasp-top10-cicd-mapping.md │ ├── 03-remediation-roadmap.md │ ├── 04-interview-prep.md │ └── 05-lessons-learned.md ├── recon/ # Phase 1 & 2 — fingerprinting and authenticated enumeration │ ├── 01-fingerprinting.md │ └── 02-authenticated-enumeration.md ├── findings/ # One file per confirmed finding, full PoC + remediation │ ├── F-010-...md ... F-021-...md │ └── informational/ # INFO/LOW severity supporting observations ├── ctfd/ │ └── challenge-cross-reference.md └── LICENSE.md ``` ## 阅读路径 - **只想看重点?** 从[上方的结果表](#results-at-a-glance)开始,然后阅读 F-010、F-013、F-016 和 F-017——这四条是最完整的端到端攻击链。 - **准备面试?** 直接前往 [`docs/04-interview-prep.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/docs/04-interview-prep.md)——其中包含每项主要发现的一段式口语化总结,以及常见的追问问题。 - **正在构建/加固 CI/CD 流水线?** 直接前往 [`docs/03-remediation-roadmap.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/docs/03-remediation-roadmap.md)——一份按优先级排列、可操作的检查清单。 - **刚接触 CI/CD 安全概念?** 从 [`docs/02-owasp-top10-cicd-mapping.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/docs/02-owasp-top10-cicd-mapping.md) 开始,了解整个仓库所围绕组织的参考分类体系。 ## 关于 OWASP Top 10 CI/CD 安全风险 此处的每一项发现都对照 [OWASP Top 10 CI/CD 安全风险(2023)](https://owasp.org/www-project-top-10-ci-cd-security-risks/) 进行了映射——完整的参考表(CICD-SEC-1 至 CICD-SEC-10)位于 [`docs/02-owasp-top10-cicd-mapping.md`](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/docs/02-owasp-top10-cicd-mapping.md),因为它在各项单独发现中被频繁引用。 ## 免责声明 本仓库记录的测试**仅针对本地、自托管、故意存在漏洞的培训实验环境**([OWASP CICD-Goat](https://github.com/cider-security-research/cicd-goat))进行,用于教育和作品集展示目的。此处没有任何内容针对、引用或曾对任何生产系统、第三方服务或真实凭据进行测试。请勿将本仓库中的任何技术用于你并不拥有或未获得明确书面授权测试的系统。 --- ## 🧠 测试理念 > *“最优秀的渗透测试人员首先像开发者一样思考,其次才像攻击者一样思考。如果你理解代码为何以某种方式编写,你总能发现比扫描器更多的东西。”* 我以三个阶段开展每一次工作: **1. 先理解,再攻击** —— 阅读应用程序。像真实用户一样使用它。在接触任何工具之前先理解业务逻辑。 **2. 手动优先,工具其次** —— 自动化扫描器只能发现它们被配置去发现的东西。有趣的漏洞总是通过思考而非扫描发现的。 **3. 像开发者一样撰写报告** —— 开发者无法理解或复现的发现,就是不会被修复的发现。 --- ## 👤 关于我 - 👤 **姓名** —— Dheeraj Kumar Jayaswal - 🌍 **所在地** —— 爱尔兰都柏林郡都柏林 - 💼 **职位** —— 首席渗透测试顾问 | VikingCloud(此前为 Infosys Limited 攻击性安全技术负责人) - 🎯 **主要方向** —— Web 应用与 API 安全 —— 攻击性安全咨询 - 🏆 **经验** —— IT 领域 16+ 年 | 攻击性安全领域 9+ 年 - 🔎 **优势** —— 从全栈开发者起步(ASP.NET / SQL Server)—— 我像开发者一样思考,像黑客一样攻击 - 🎓 **正在攻读** —— OSWE —— OffSec Web Expert(OSCE3 方向) - 🏢 **行业领域** —— 所得税 · 银行 · 零售 · 电子商务 · 货运物流 · 教育 - 📝 **分享** —— 企业渗透测试实战笔记、方法论,以及来自真实项目的实用技术文章 --- ## 🏅 认证 | 认证 | 颁发机构 | 状态 | |---|---|---| | Certified Ethical Hacker (CEH) | EC-Council | ✅ 2021 | | AWS Certified Solutions Architect – Associate | Amazon Web Services | ✅ 2022 | | AWS Certified Cloud Practitioner | Amazon Web Services | ✅ 2022 | | Executive Certificate in Cyber Security | IIT Kanpur | ✅ 2026 | | OSWE — OffSec Web Expert(OSCE3 方向) | OffSec | 🔄 进行中 | **未来方向 —— 红队:** OSCP → CRTO → OSEP、CRTP、CRTL、CRTE --- ## 📄 许可证 本内容依据 **[CC BY 4.0](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/LICENSE.md)** 许可协议授权。欢迎复用或改编本篇文章的任何部分——只需清晰注明 **Dheeraj Kumar Jayaswal** 的署名,并附上指向本仓库的链接。CICD-Goat 本身是 [Cider Security](https://github.com/cider-security-research/cicd-goat) 的独立项目——请去给原项目点个星。 --- ## 🤝 联系 [LinkedIn](https://linkedin.com/in/dheerajkumarjayaswal) — 欢迎咨询、合作与安全讨论。 欢迎提供反馈、指正和 PR(例如针对 flag9/Dormouse,或 [CTFd 交叉引用](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/ctfd/challenge-cross-reference.md) 中 Duchess/flag4 的后续内容)——详见 [CONTRIBUTING.md](https://github.com/dheeraj-jayaswal/cicd-goat-vapt-writeup/blob/main/CONTRIBUTING.md)。


