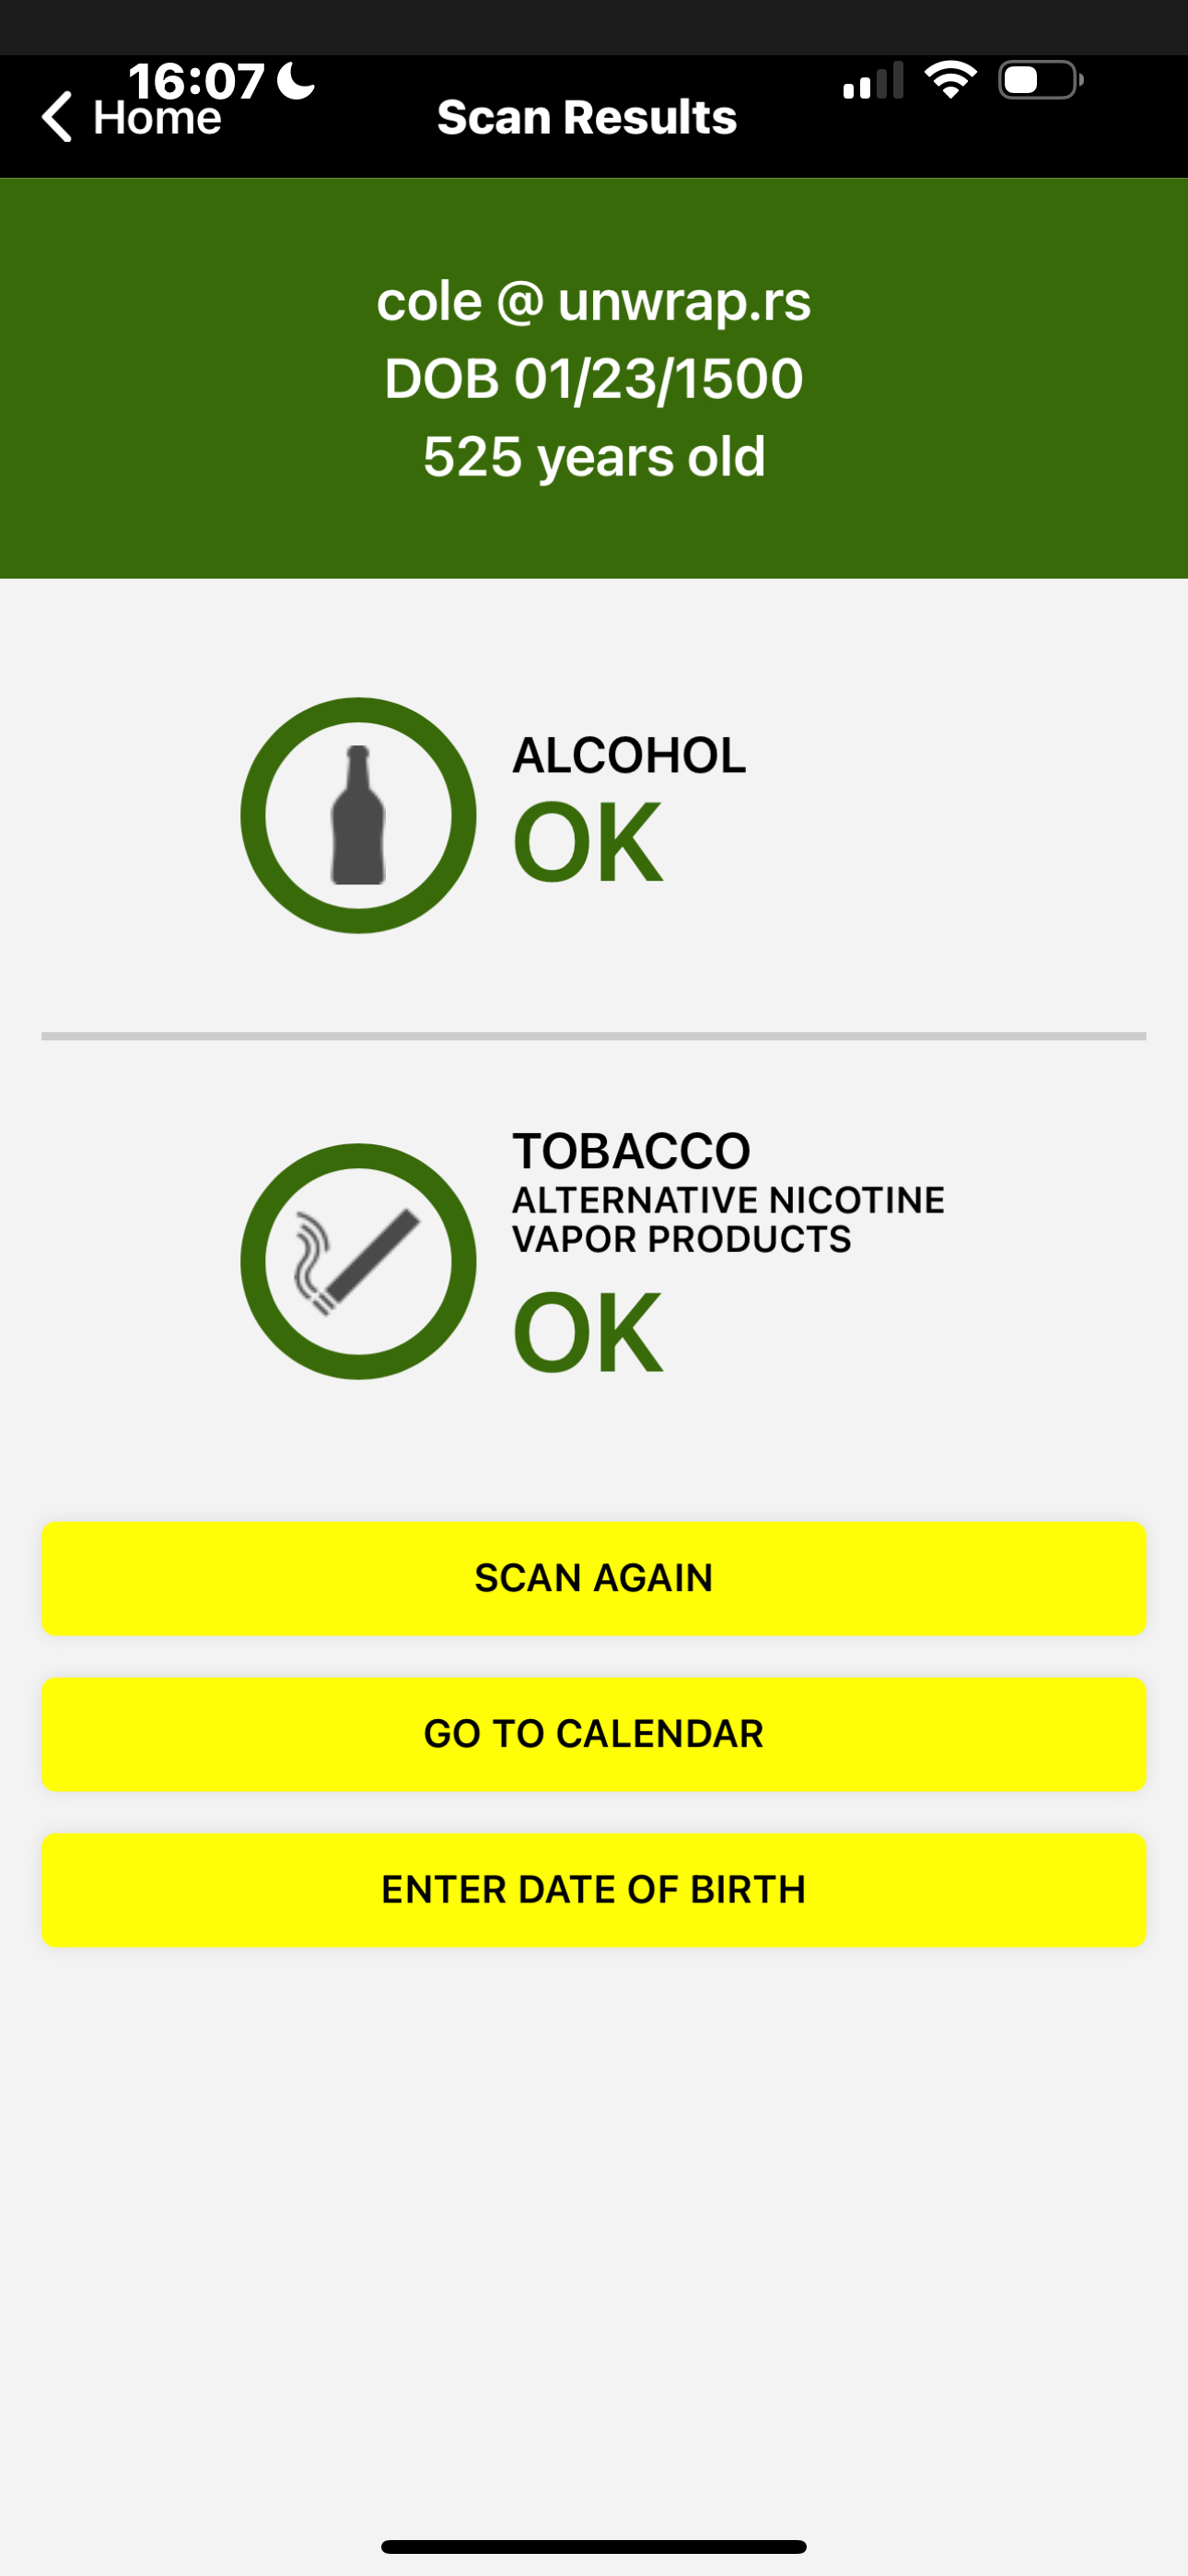
本仓库包含全面的安全研究,记录了影响政府身份证明、企业解决方案和消费类应用的 AAMVA 标准 PDF417 条码验证系统中的关键漏洞。研究包括一个功能完整的概念验证(PoC),展示了身份证验证系统在处理驾照条码时的系统性缺陷。
重要提示: 此代码仅供安全研究使用。有关允许的用途,请参阅 LICENSE.md 文件。
本研究遵循以下原则:
本研究展示了已分配的漏洞:
基础评分:10.0(严重)
向量:AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:N
细分:
漏洞利用示例:```rust // Temporal validation bypass demonstration let license = CaliforniaLicense::builder() .birth_date("06201500") // Year 1500 - Medieval era .validate(); // Returns OK in affected systems
## 协调历史与供应商响应总结
### 披露时间线
- **2025年3月22日**:向MITRE提交初始CVE请求
- **2025年3月25日**:向IDScan.net提交概念验证并获得确认
- **2025年3月28日**:收到TokenWorks漏洞确认
- **2025年4月3日**:CISA VINCE案例VU#396042正式开启
- **2025年4月9日至16日**:与受影响供应商进行广泛技术讨论
- **2025年6月18日**:CISA案例结案决定(视为“已知风险”不予受理)
- **2025年7月1日**:经过延长的协调期后公开披露
### 供应商回应与技术分歧
#### IDScan.net(Joshua Sheetz,CISO/工程副总裁)
**初步回应**:*“经过调查,发现您只是在伪造条码数据。这是常见标准。”*
**技术立场**:
- 声称其解析器“仅读取数据”,不负责验证
- 认为不可能的值(524岁个体)在“解析器”中可以接受
- 将特定实现漏洞视为AAMVA标准局限性
- 与其自身关于“数百项算法安全检查”的营销声明相矛盾
**营销与现实差距**:
- VeriScan网站承诺“假证检测/身份证认证”
- 声称能“识别假证”并执行“安全检查”
- 技术分析显示验证程度极低,仅满足格式合规性
#### TokenWorks回应
- 将问题视为“DMV实施问题”
- 淡化供应商对加密验证的责任
- 未提供修复时间表
#### CISA决定(2025年6月18日)
**最终裁决**:*“CISA认为这不构成漏洞,因为这是AAMVA DL标准中的已知风险。”*
**对CISA立场的技术分析**:
该决定似乎将标准局限性问题与特定实现漏洞混为一谈。研究记录了以下不同技术问题:
1. **多层漏洞分类**:
- **第一层**:AAMVA标准加密缺陷(已确认)
- **第二层**:特定实现验证失败(CISA未予受理)
- **第三层**:营销声明与实际安全能力不符(未予处理)
2. **已记录的特定实现问题**:
- **CWE-20(不恰当的输入验证)**:接受生理上不可能的值
- **CWE-345(数据真实性验证不足)**:无加密检查
- **CWE-770(无限制资源分配)**:无速率限制
- **CWE-841(行为工作流实施不当)**:无模式检测
## 概念验证证据
### 密苏里州ShowMeID政府应用绕过
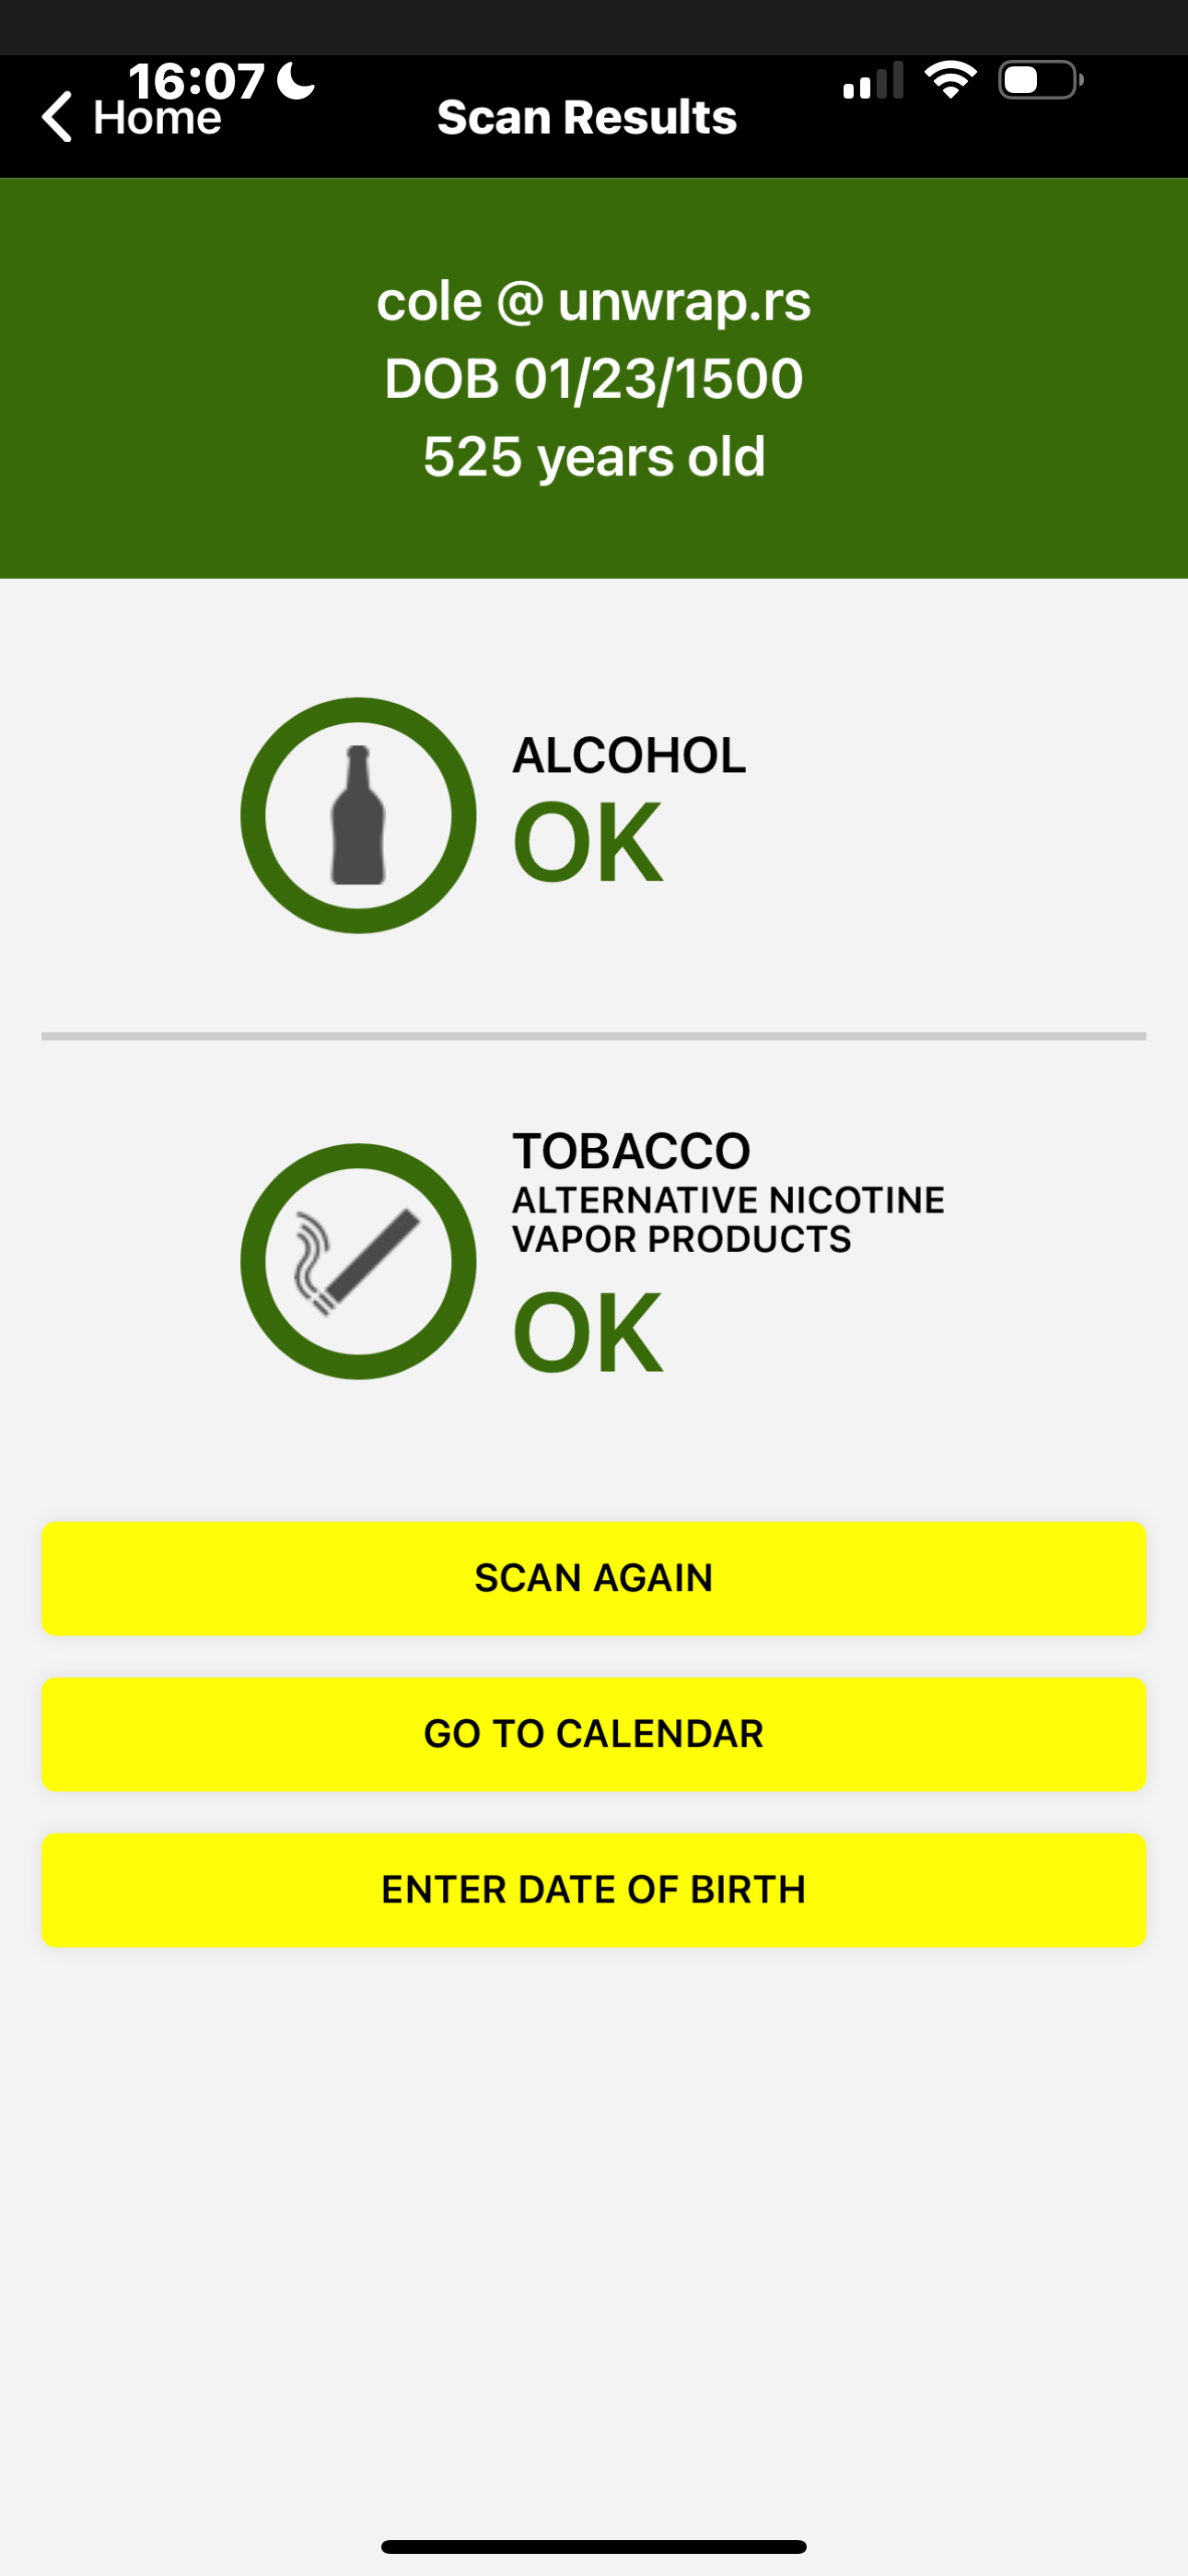 密苏里州ShowMeID绕过证据```shell
gpg --verify signatures/show_me_id/img.png.asc scan_proof/show_me_id/img.png
影响:完全绕过密苏里州官方身份验证应用,揭示了州级身份验证系统中的系统性漏洞。
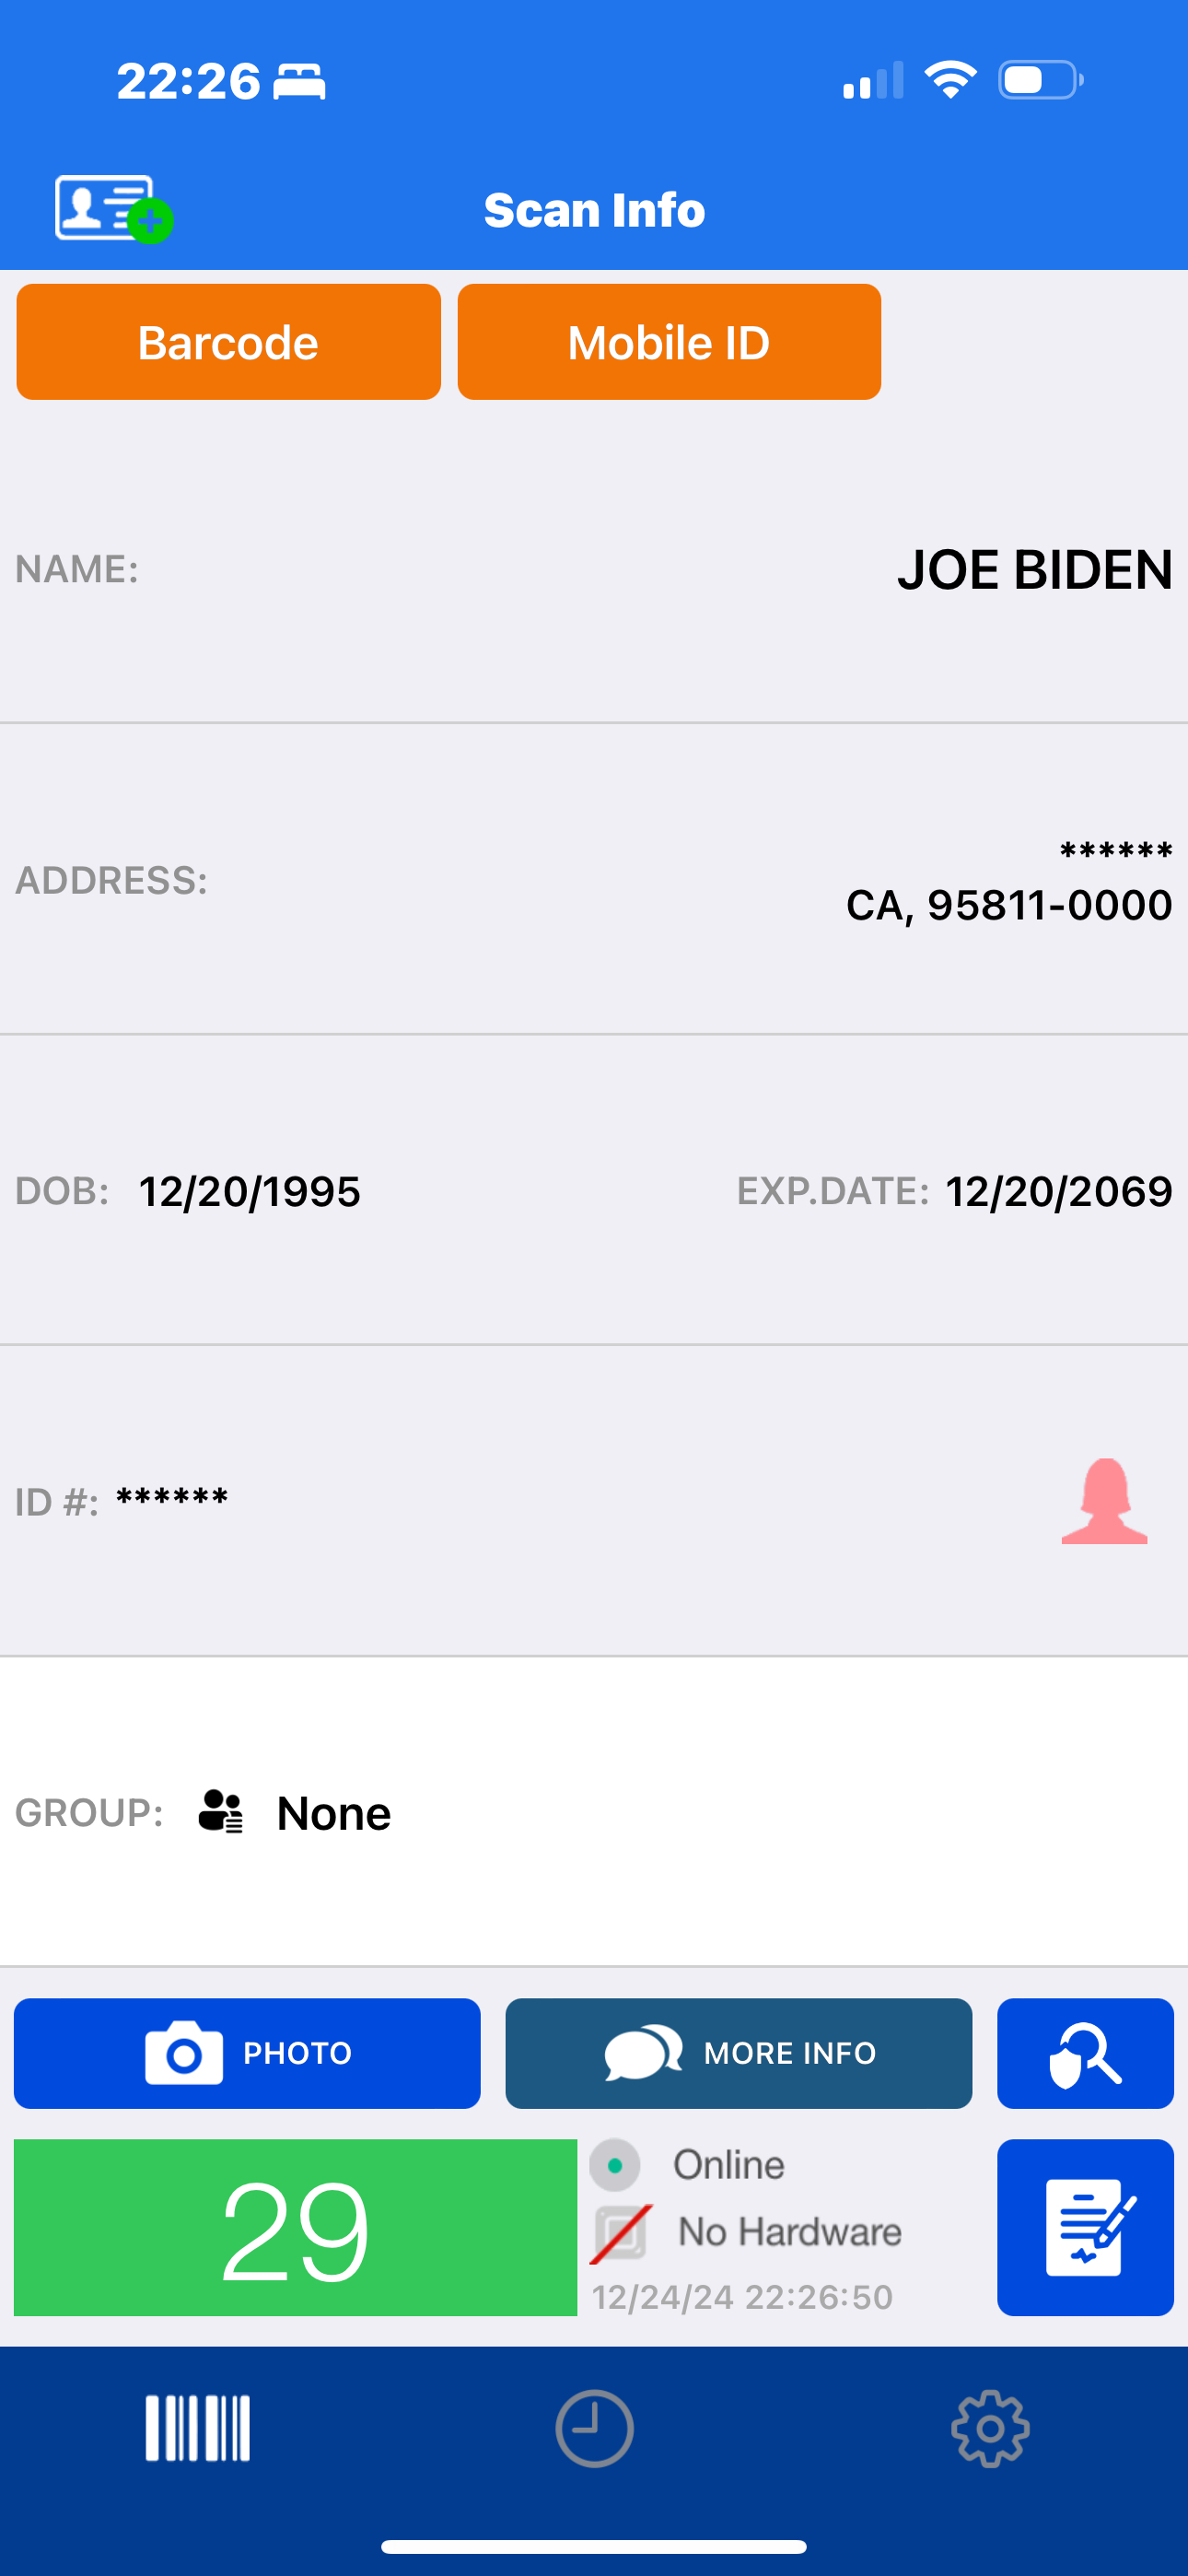 ```shell
gpg --verify signatures/veriscan/california/andrew_before.png.asc scan_proof/veriscan/california/andrew_before.png
gpg --verify signatures/veriscan/california/andrew_after.png.asc scan_proof/veriscan/california/andrew_after.png
#### 亚利桑那许可证验证绕过
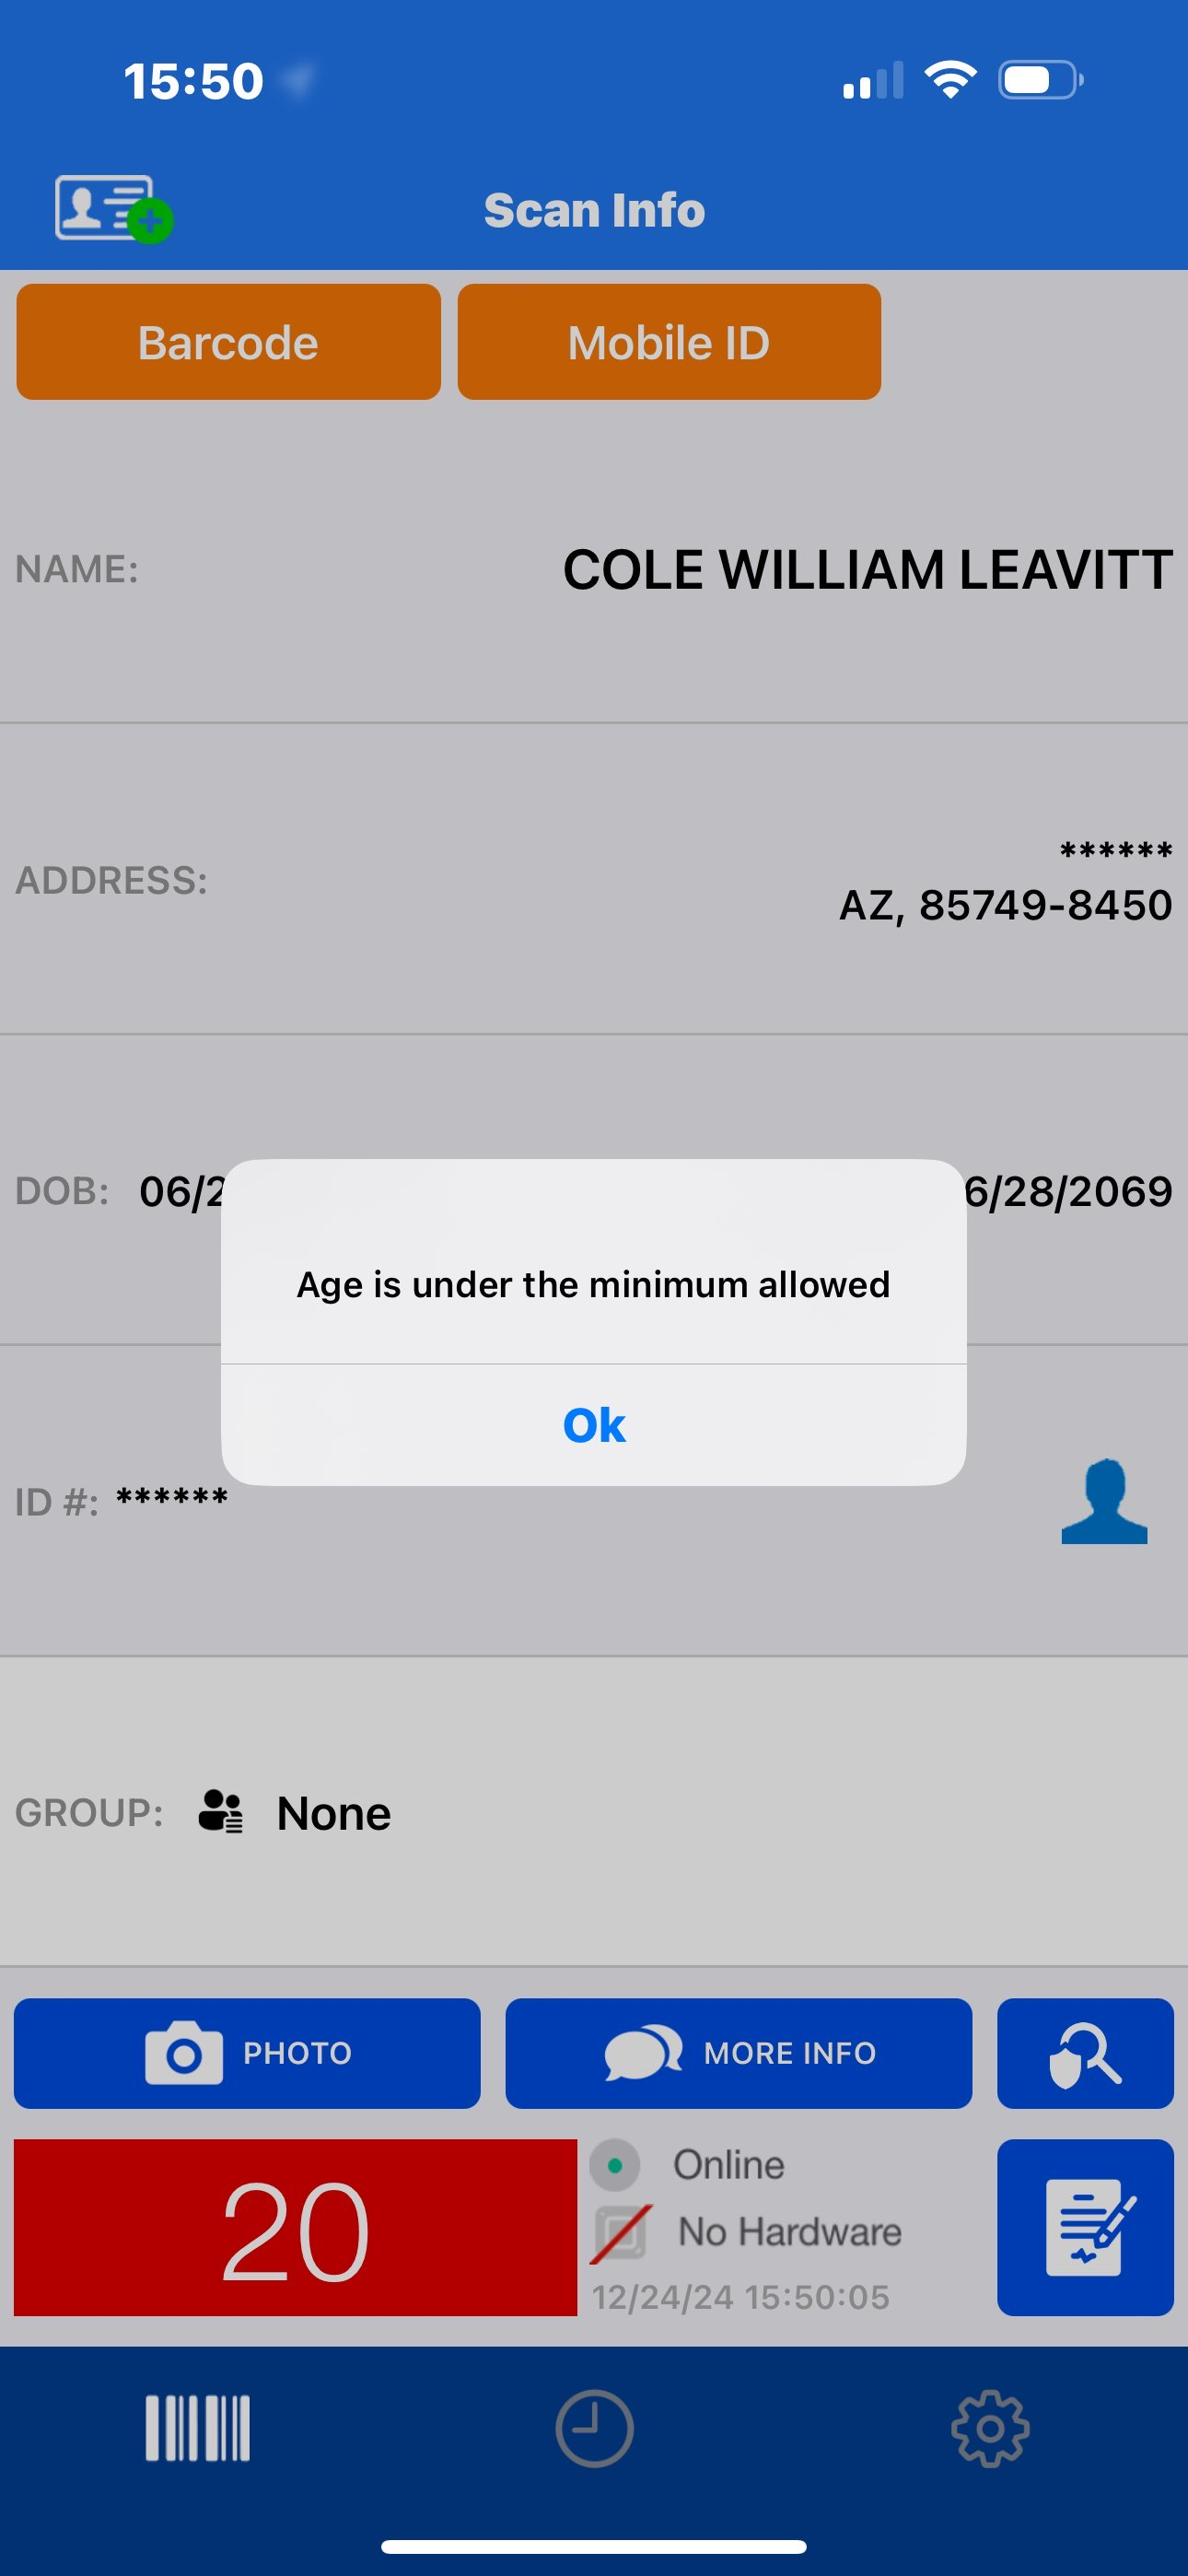
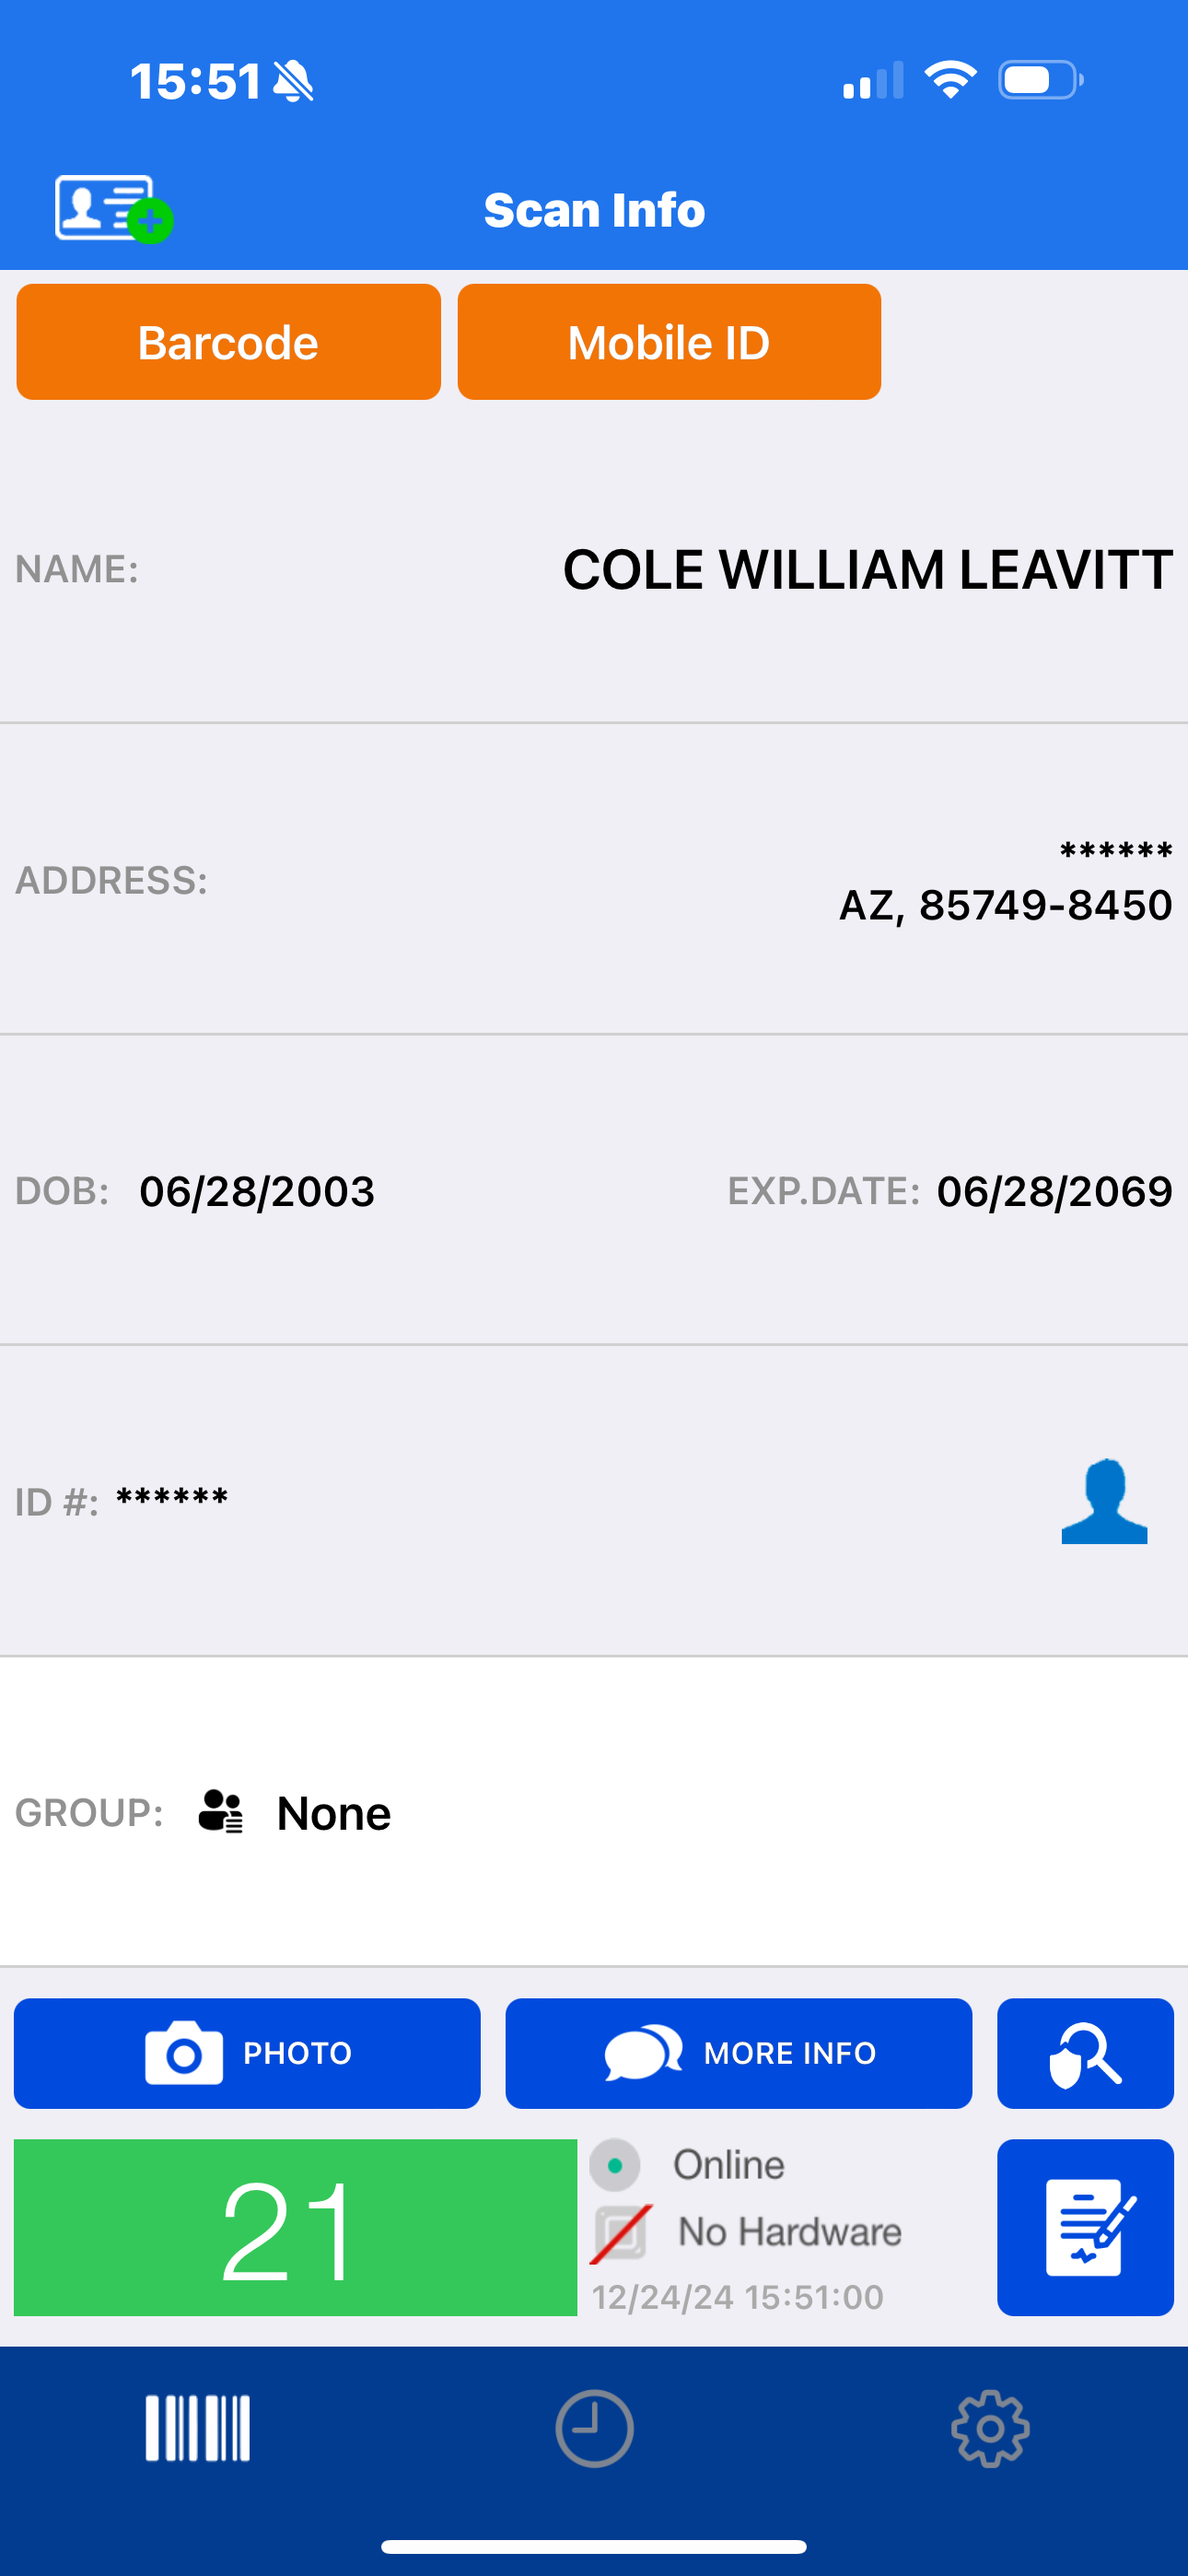
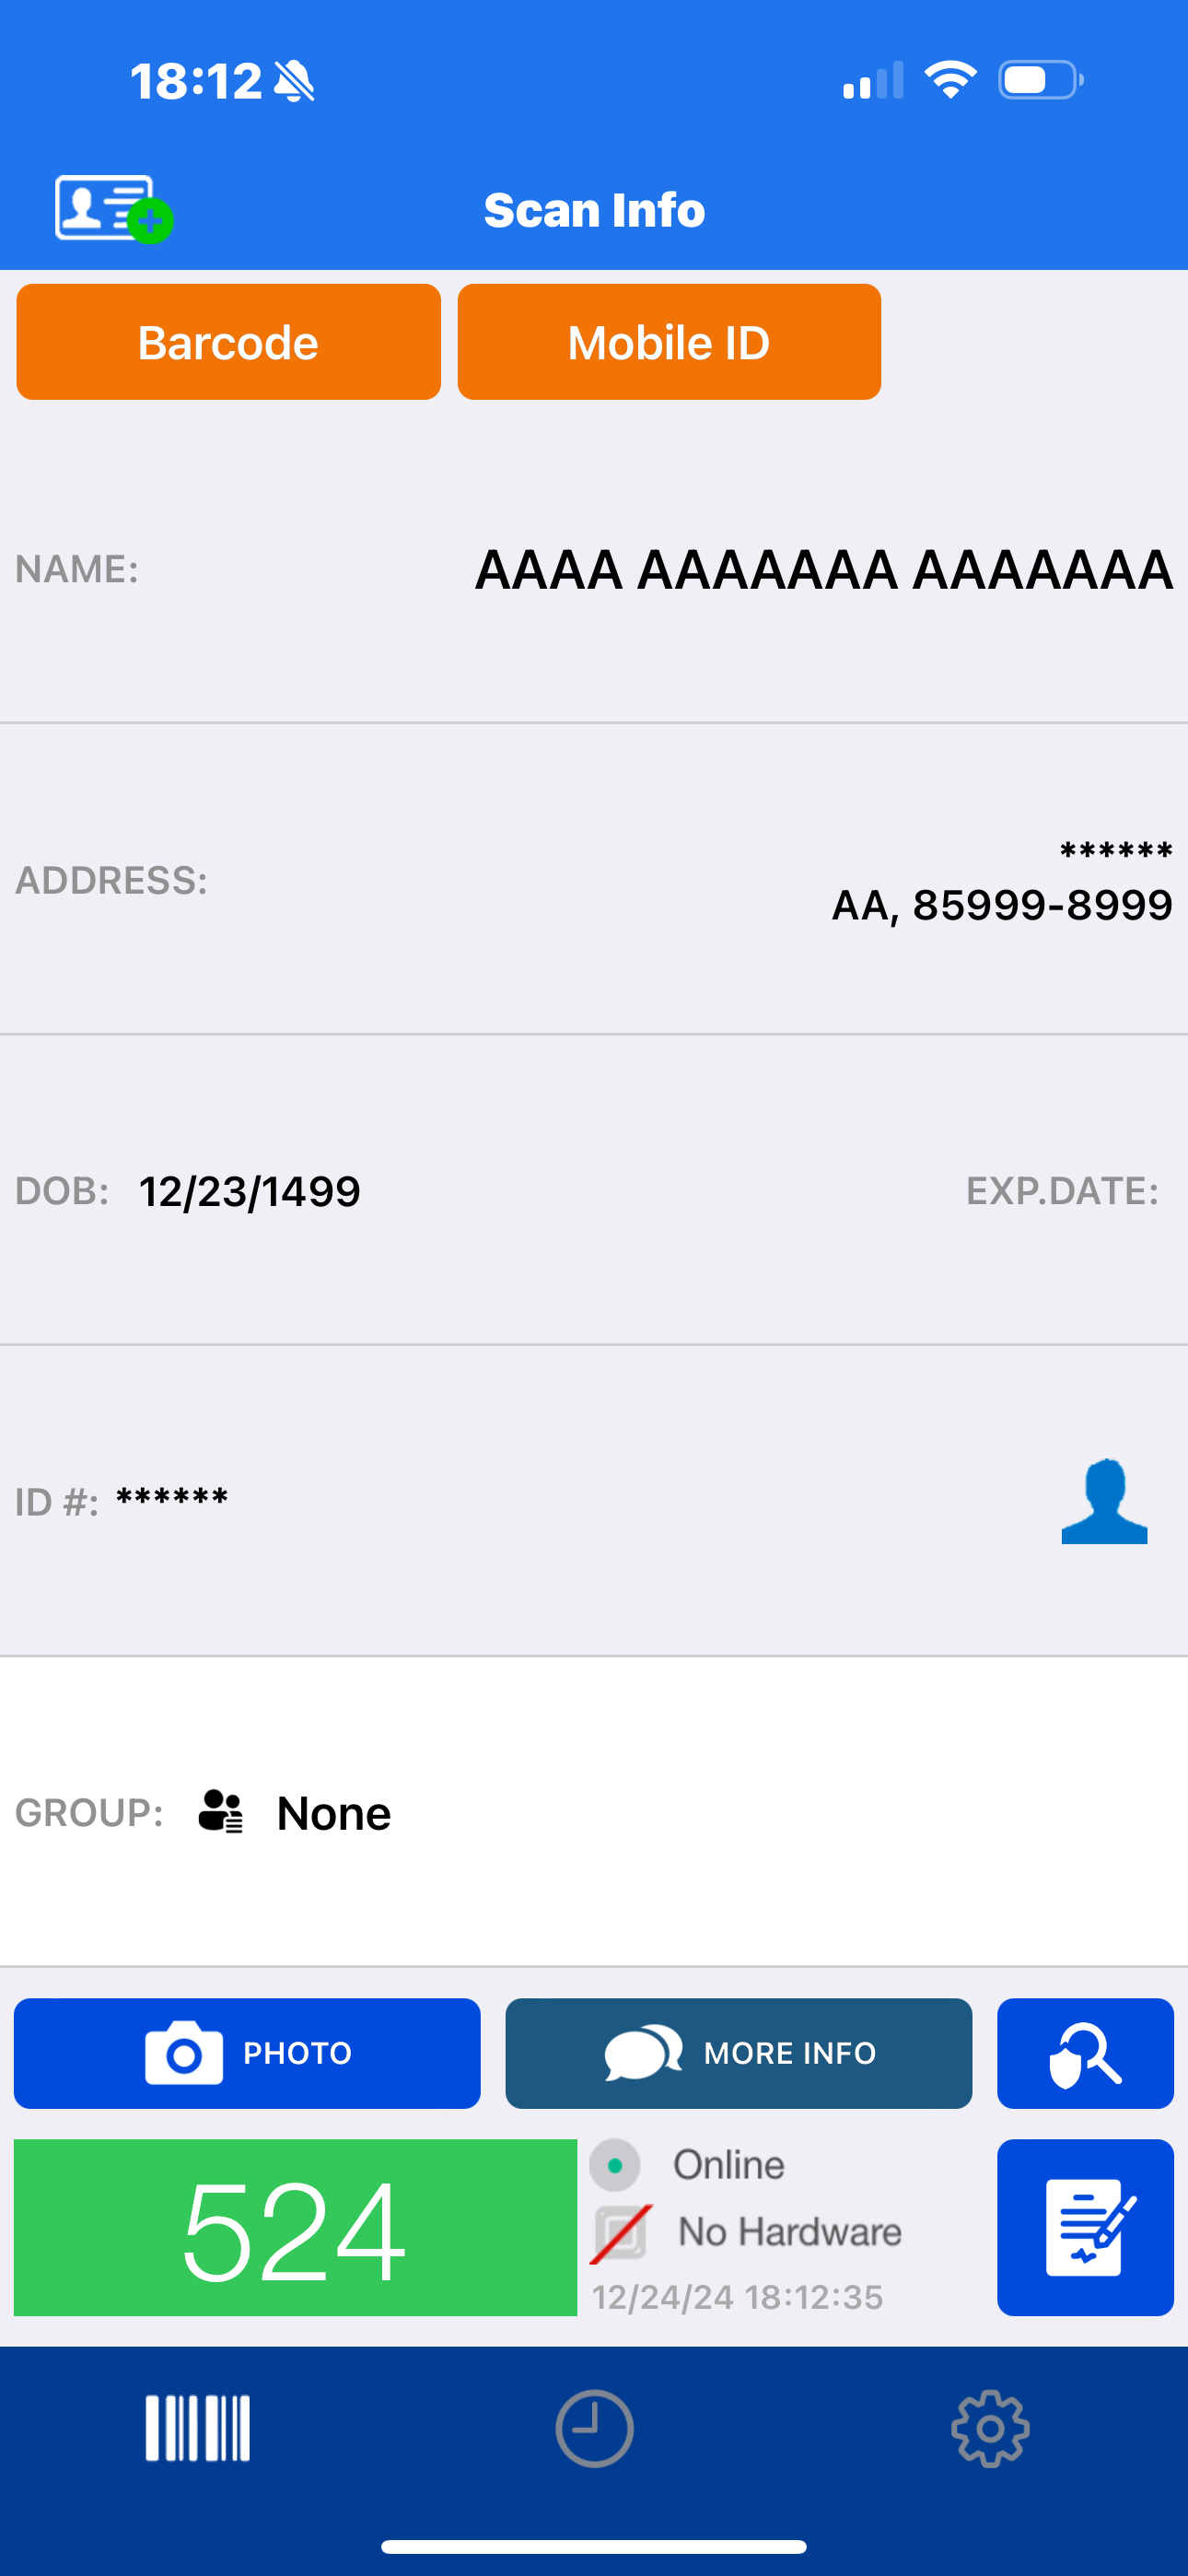
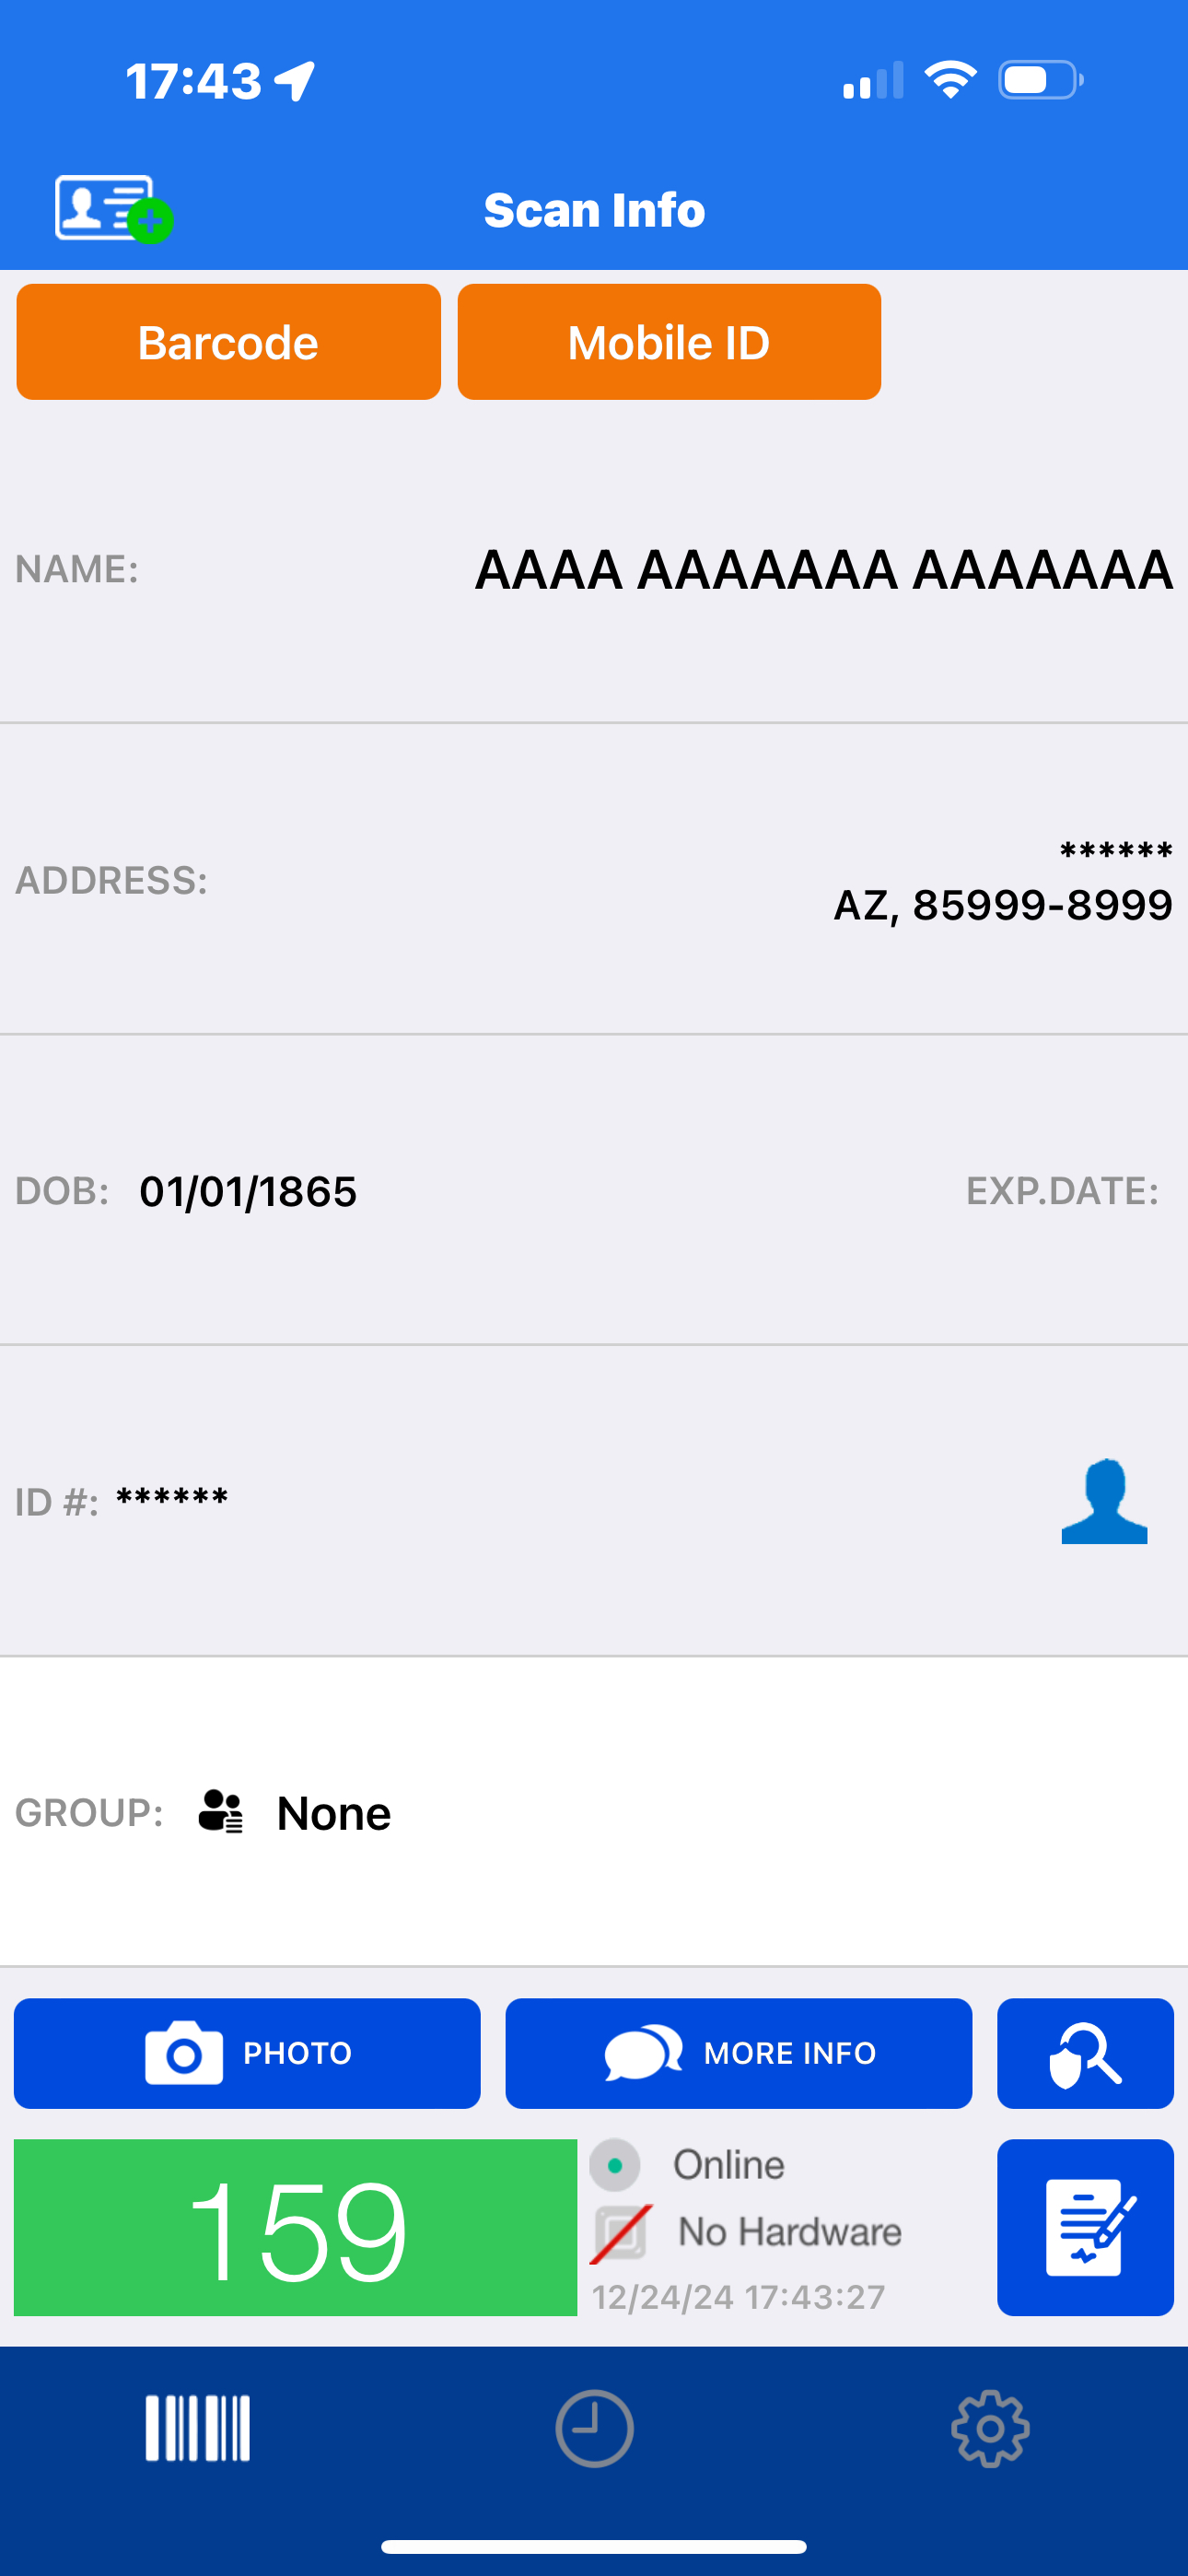```shell
gpg --verify signatures/veriscan/arizona/unanimous.png.asc scan_proof/veriscan/arizona/unanimous.png
gpg --verify signatures/veriscan/arizona/unanimous_1.png.asc scan_proof/veriscan/arizona/unanimous_1.png
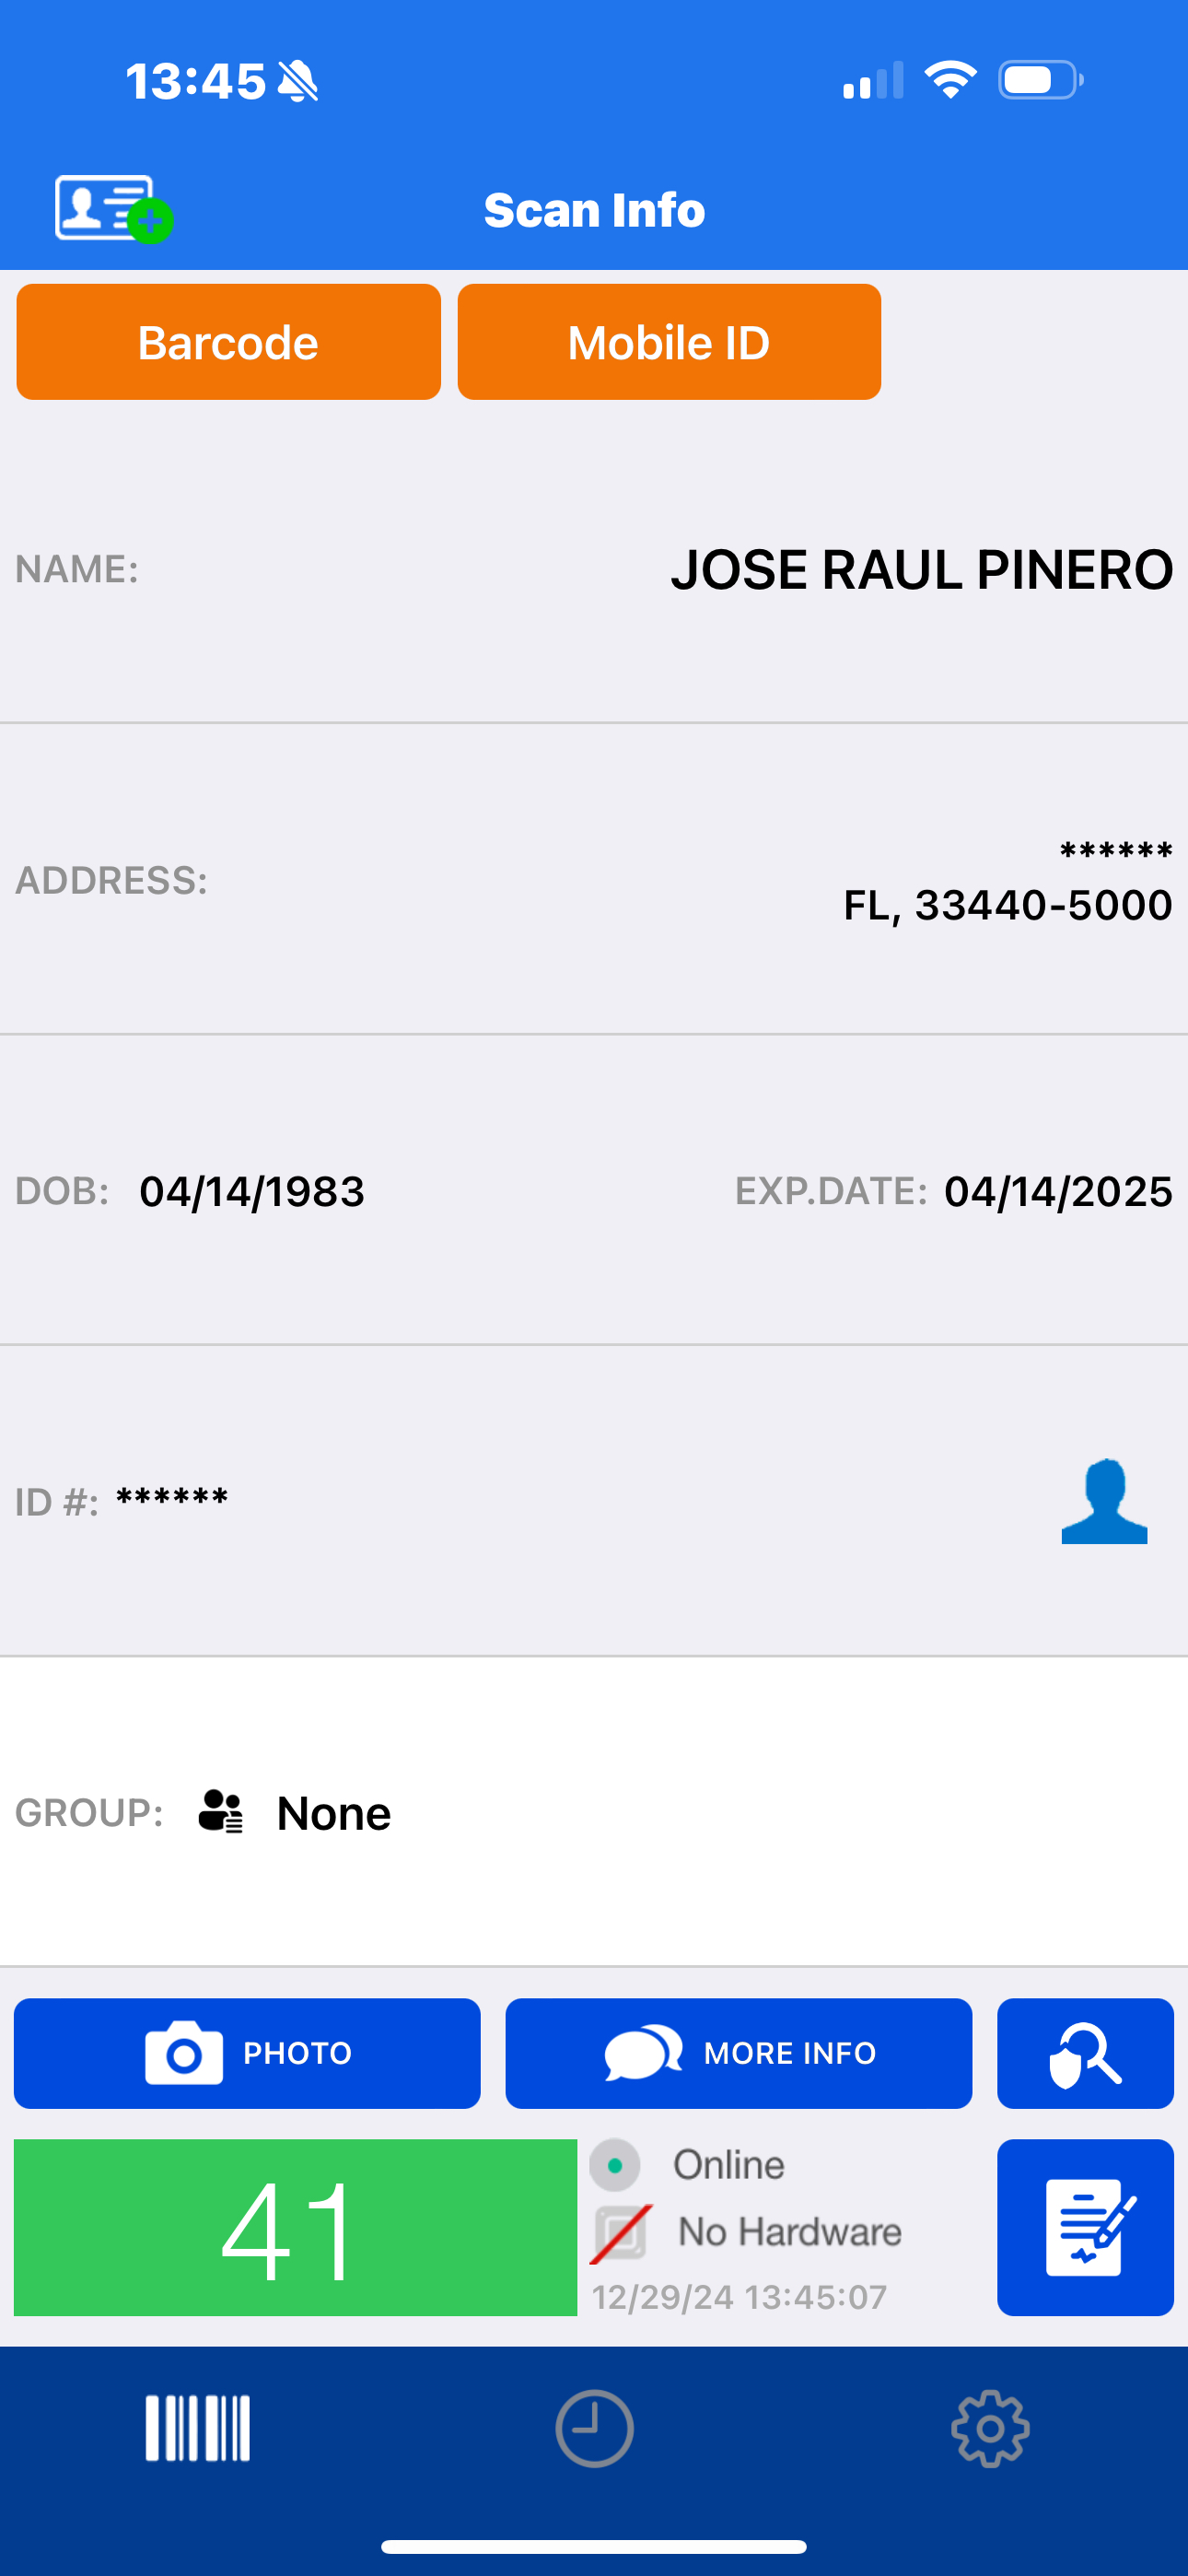
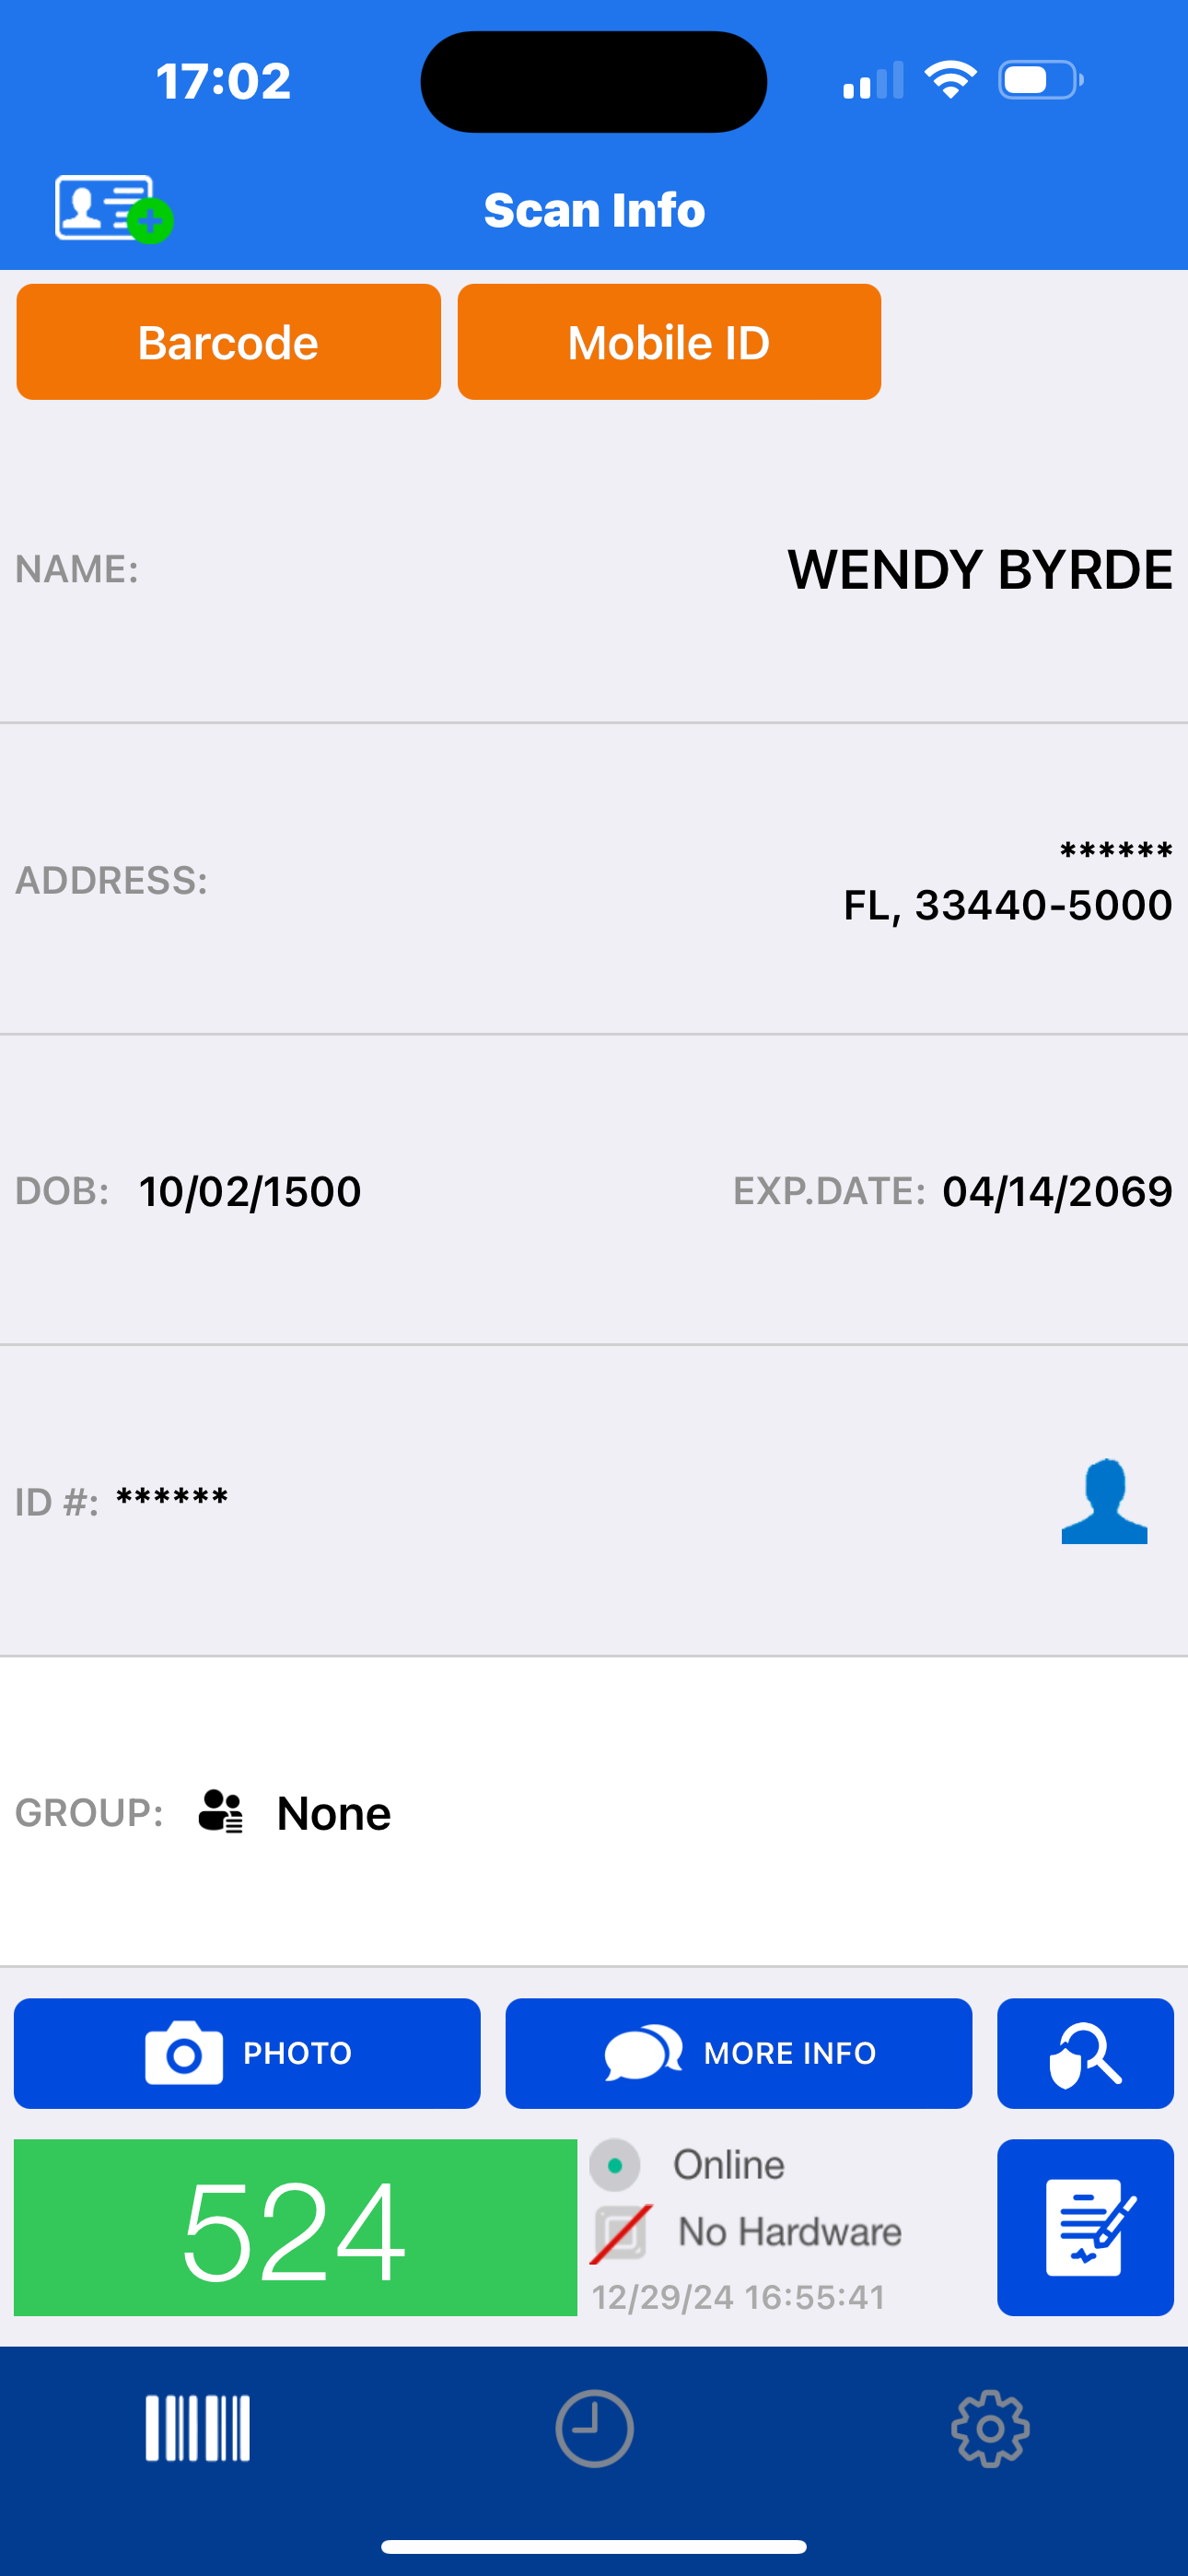 ```shell
gpg --verify signatures/veriscan/florida/wendy_synthesized.png.asc scan_proof/veriscan/florida/wendy_synthesized.png
#### 佐治亚州驾照验证绕过
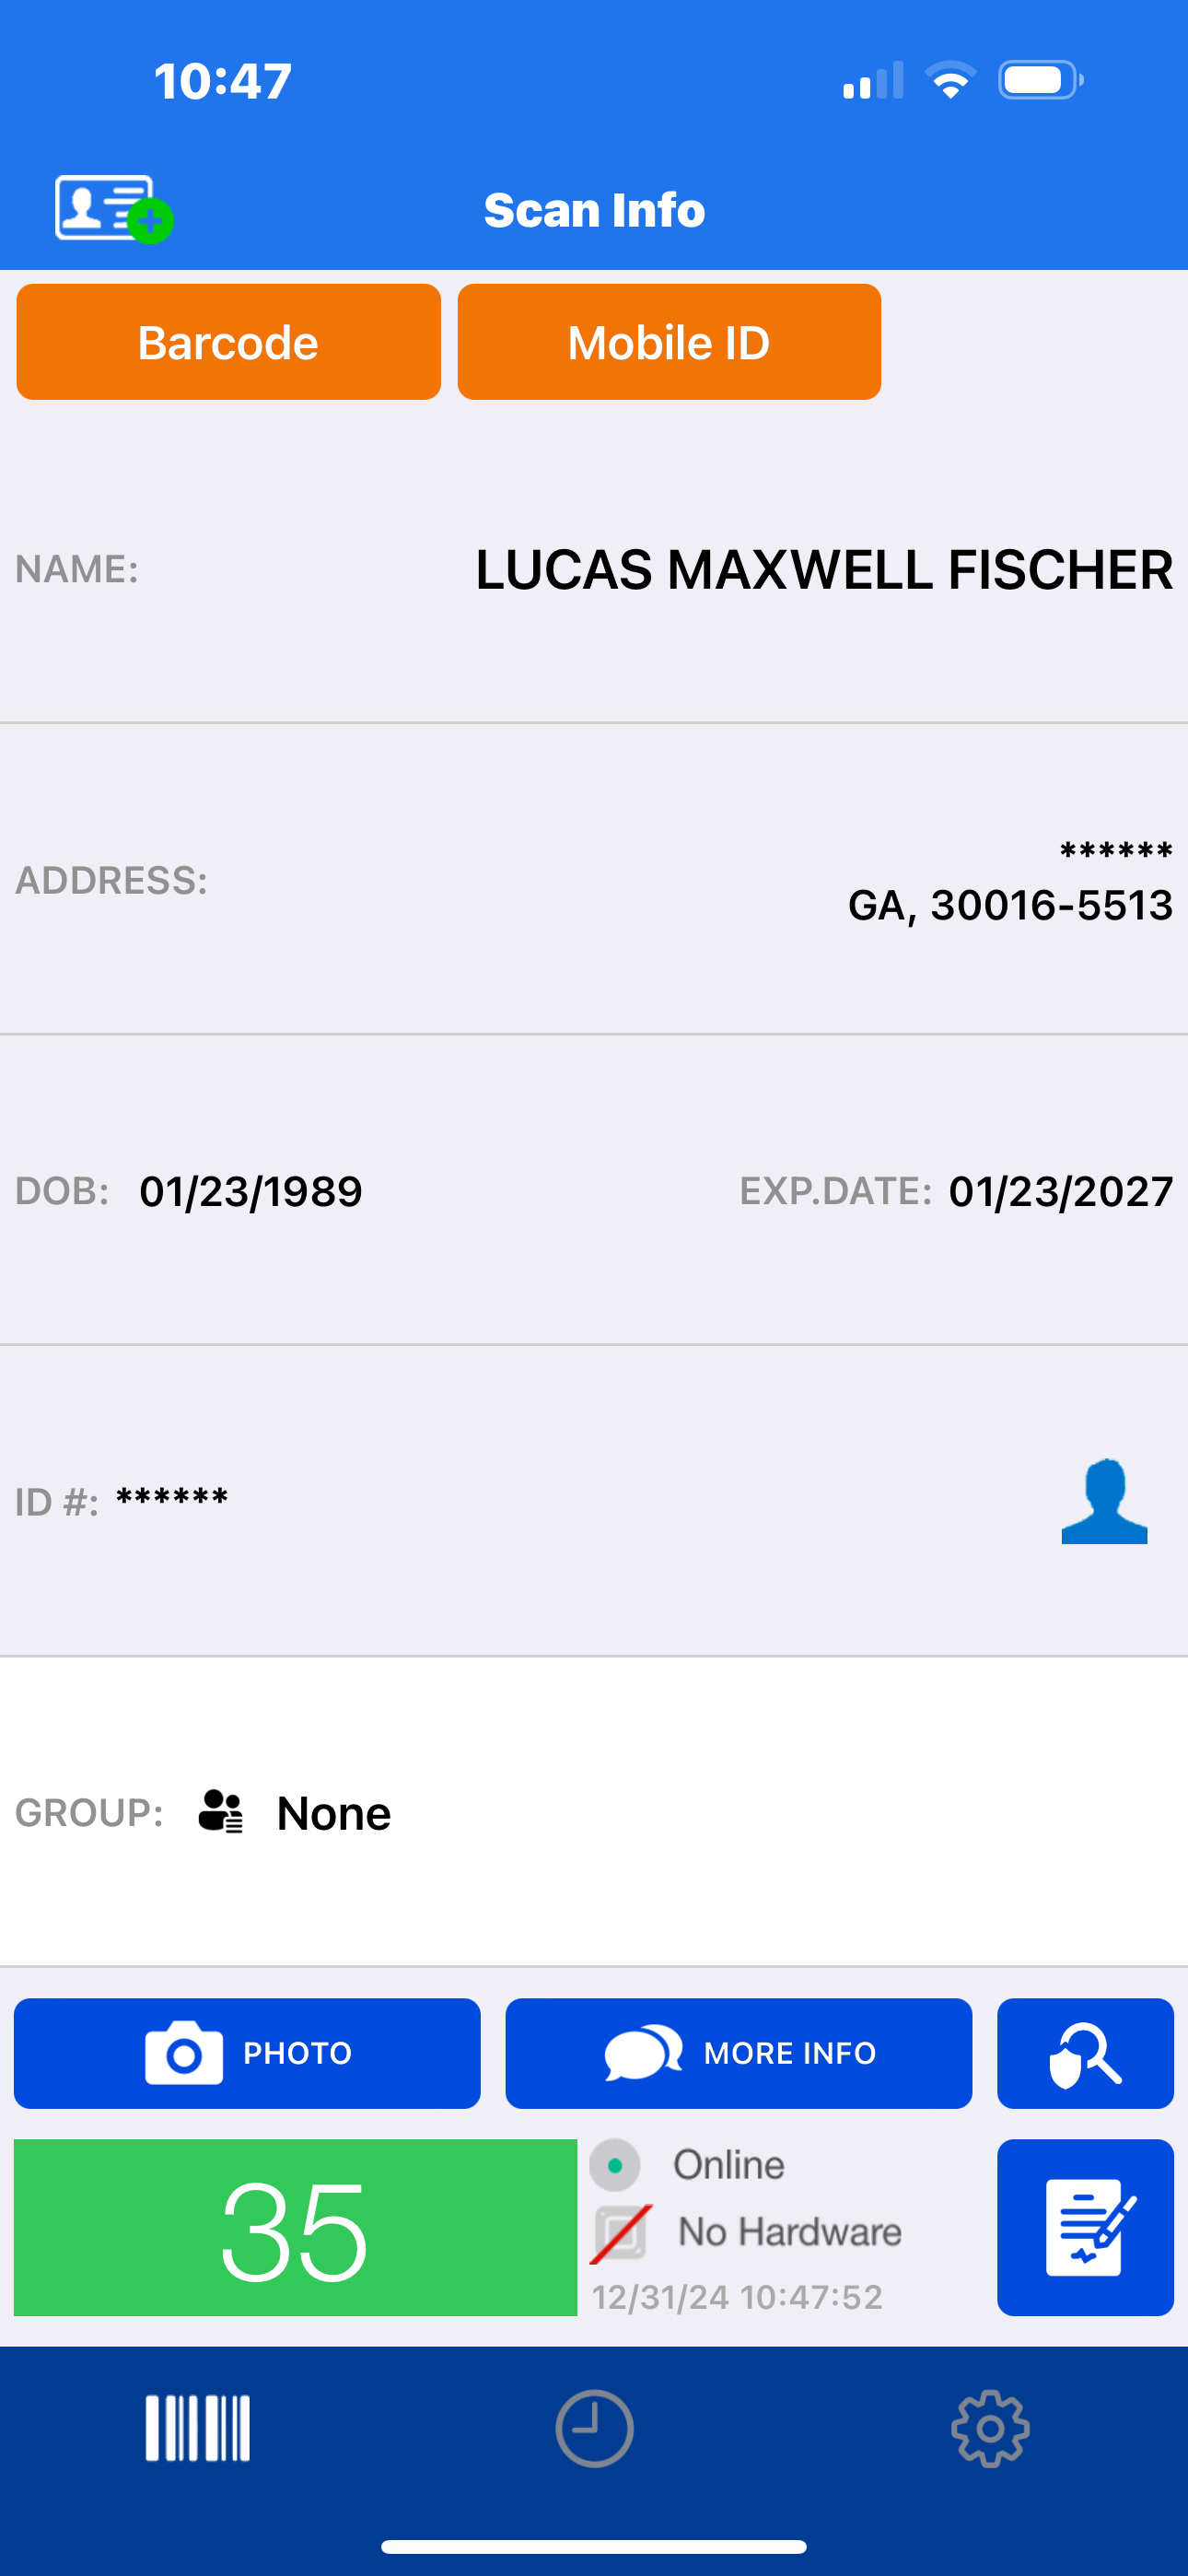
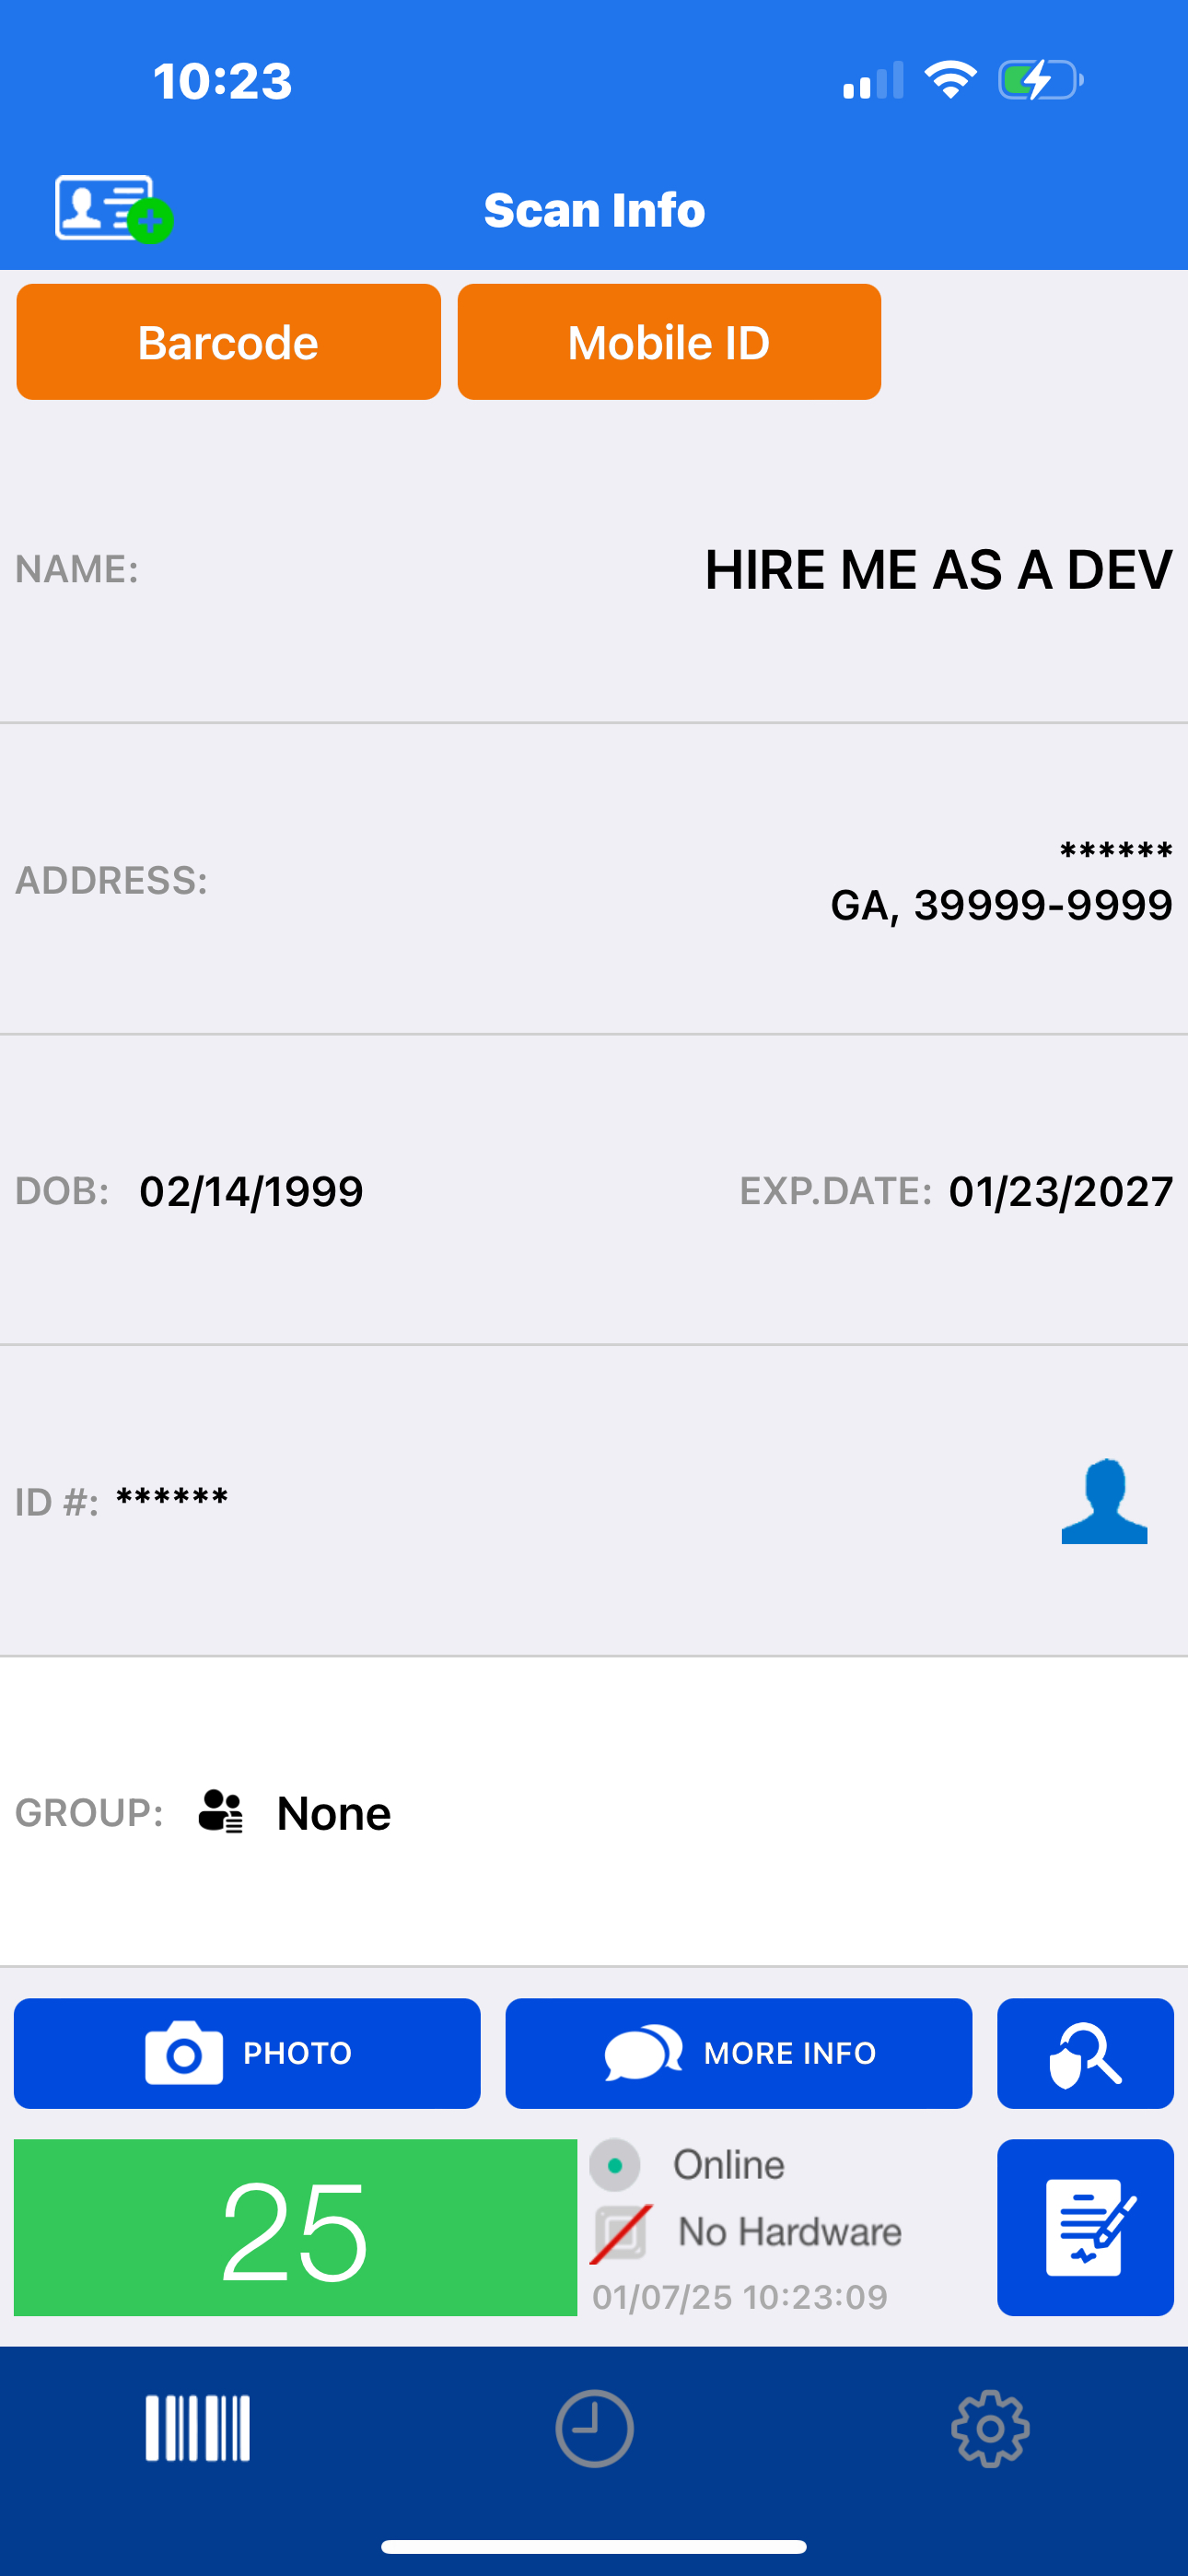```bash
# Verify Georgia bypass evidence
gpg --verify signatures/veriscan/georgia/hire_me_2.png.asc scan_proof/veriscan/georgia/hire_me_2.png
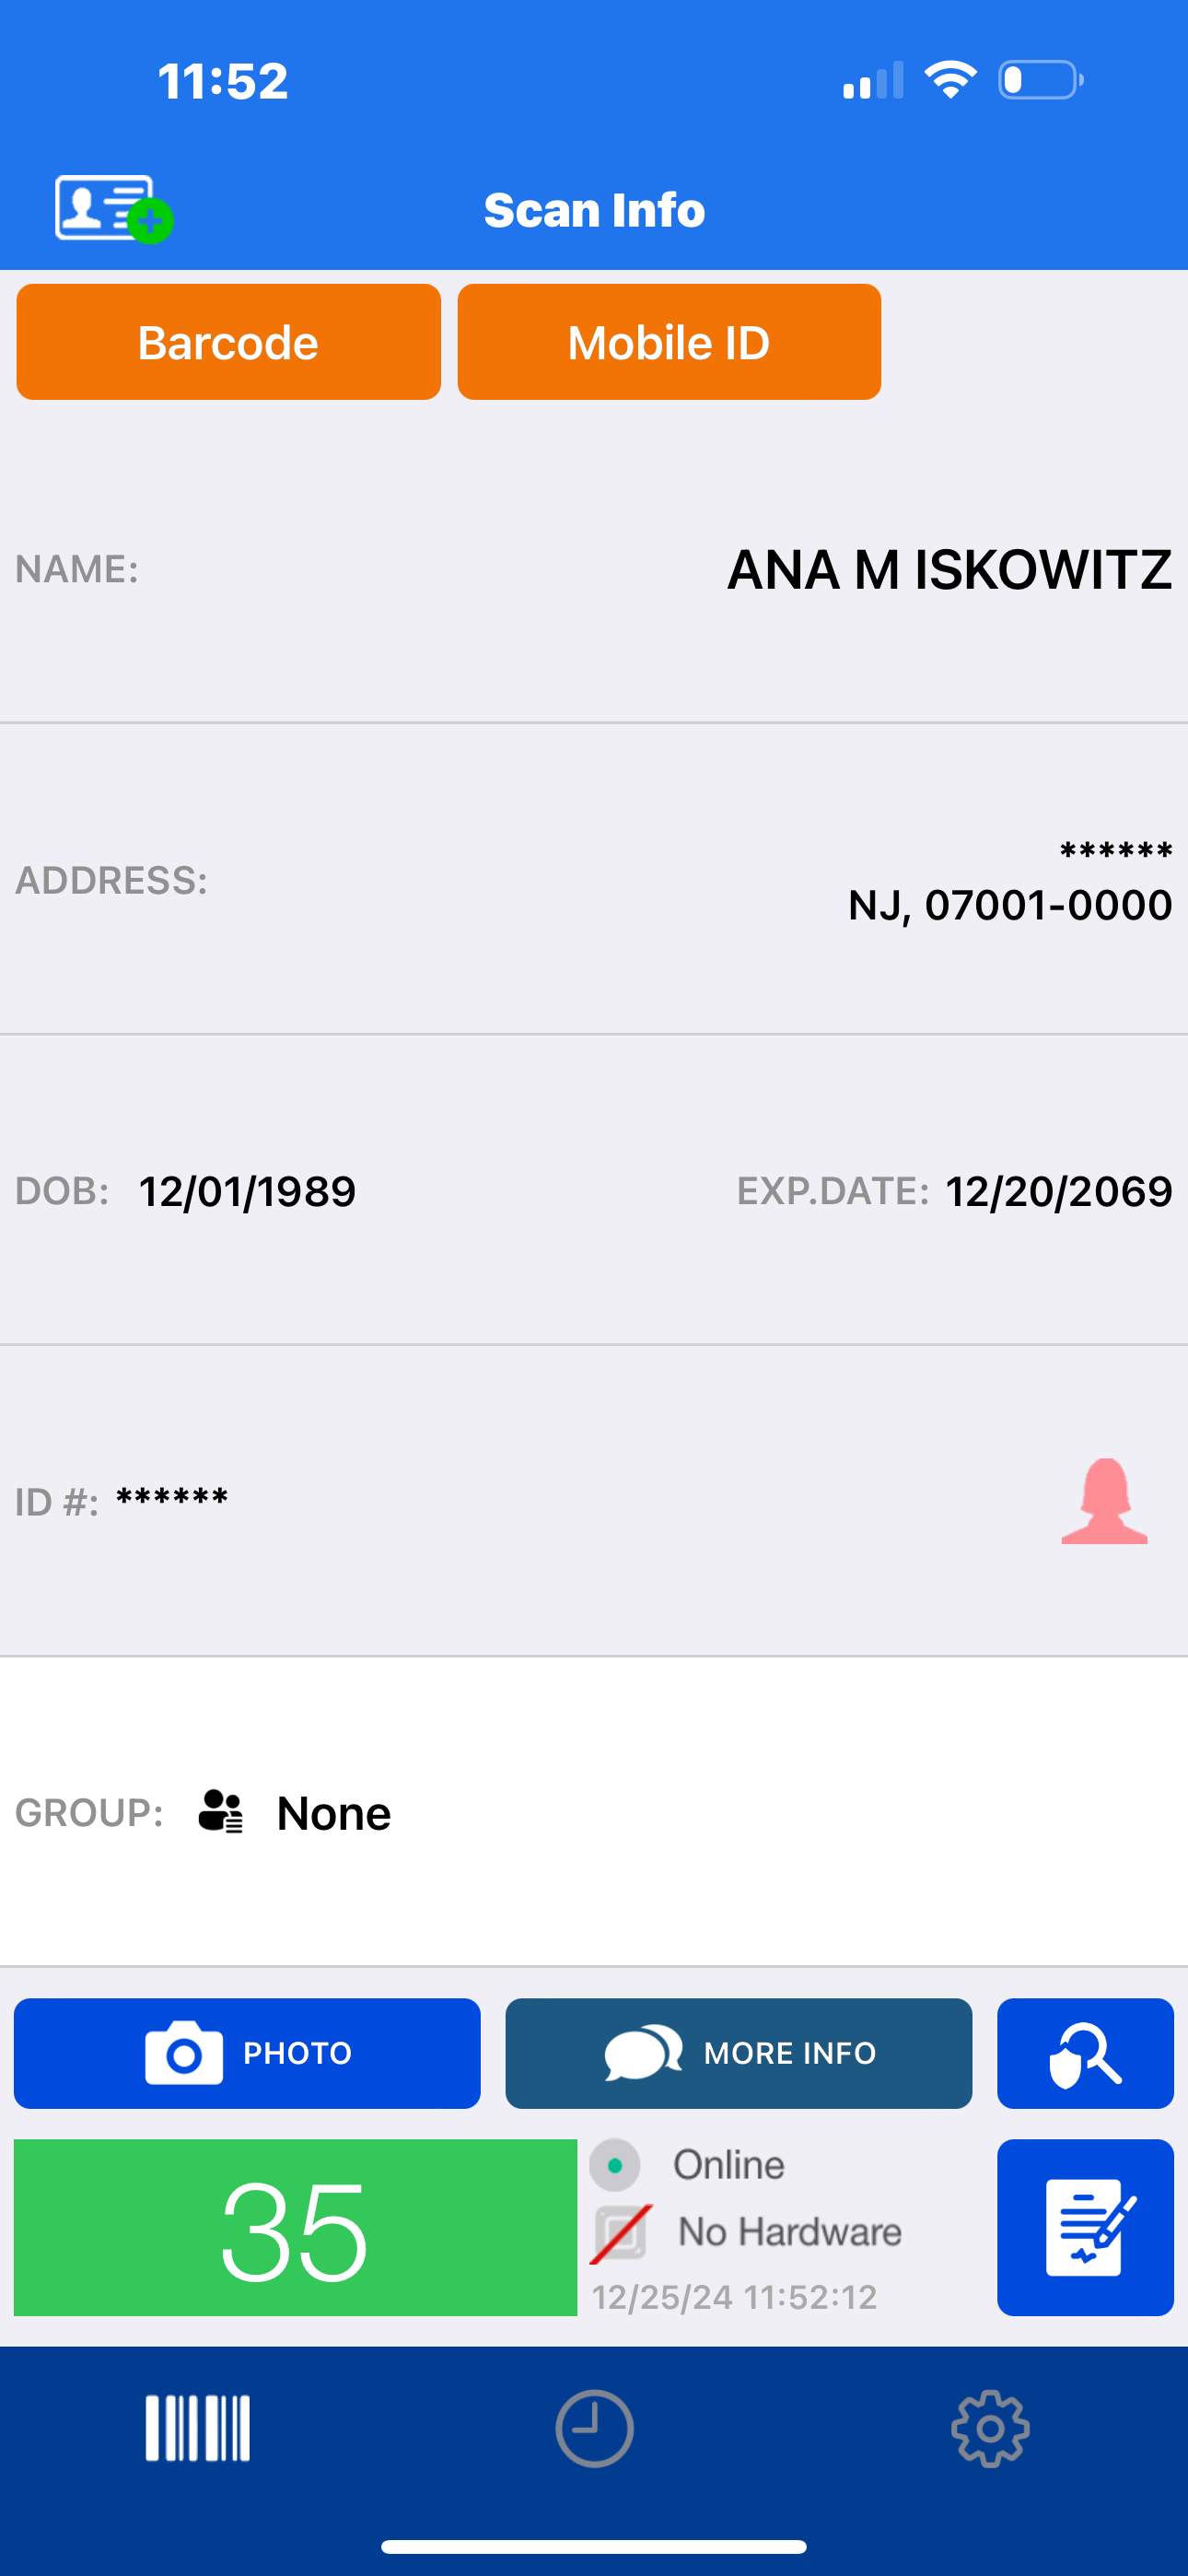
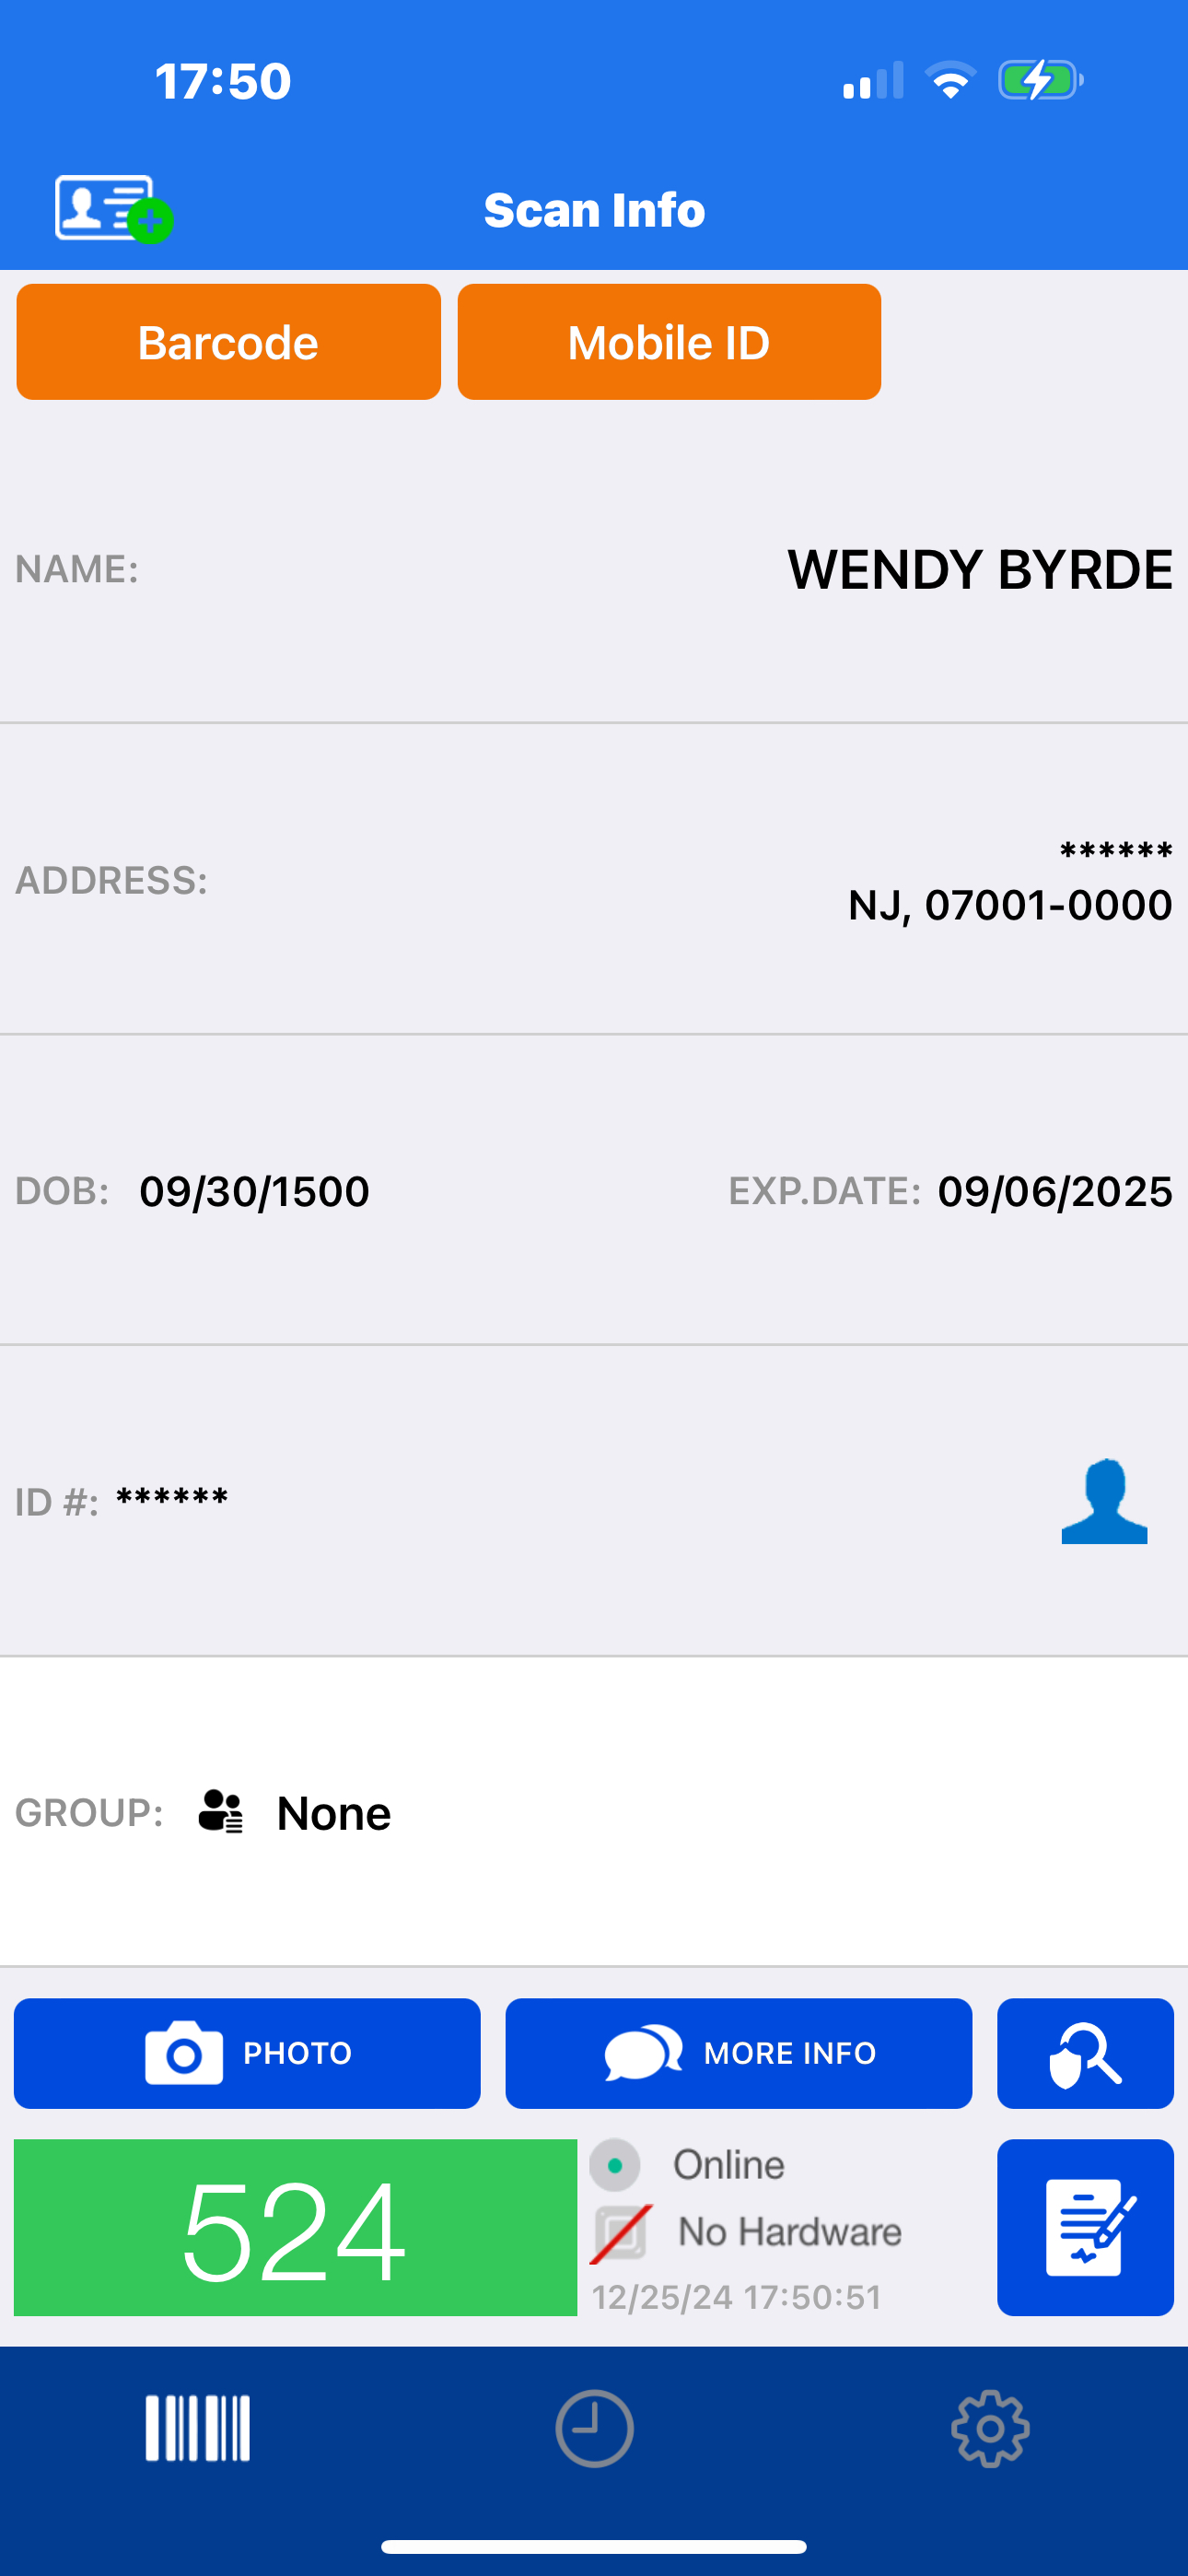 ```shell
gpg --verify signatures/veriscan/new_jersey/wendy_synthesized.png.asc scan_proof/veriscan/new_jersey/wendy_synthesized.png
#### 南卡罗来纳州许可证验证绕过
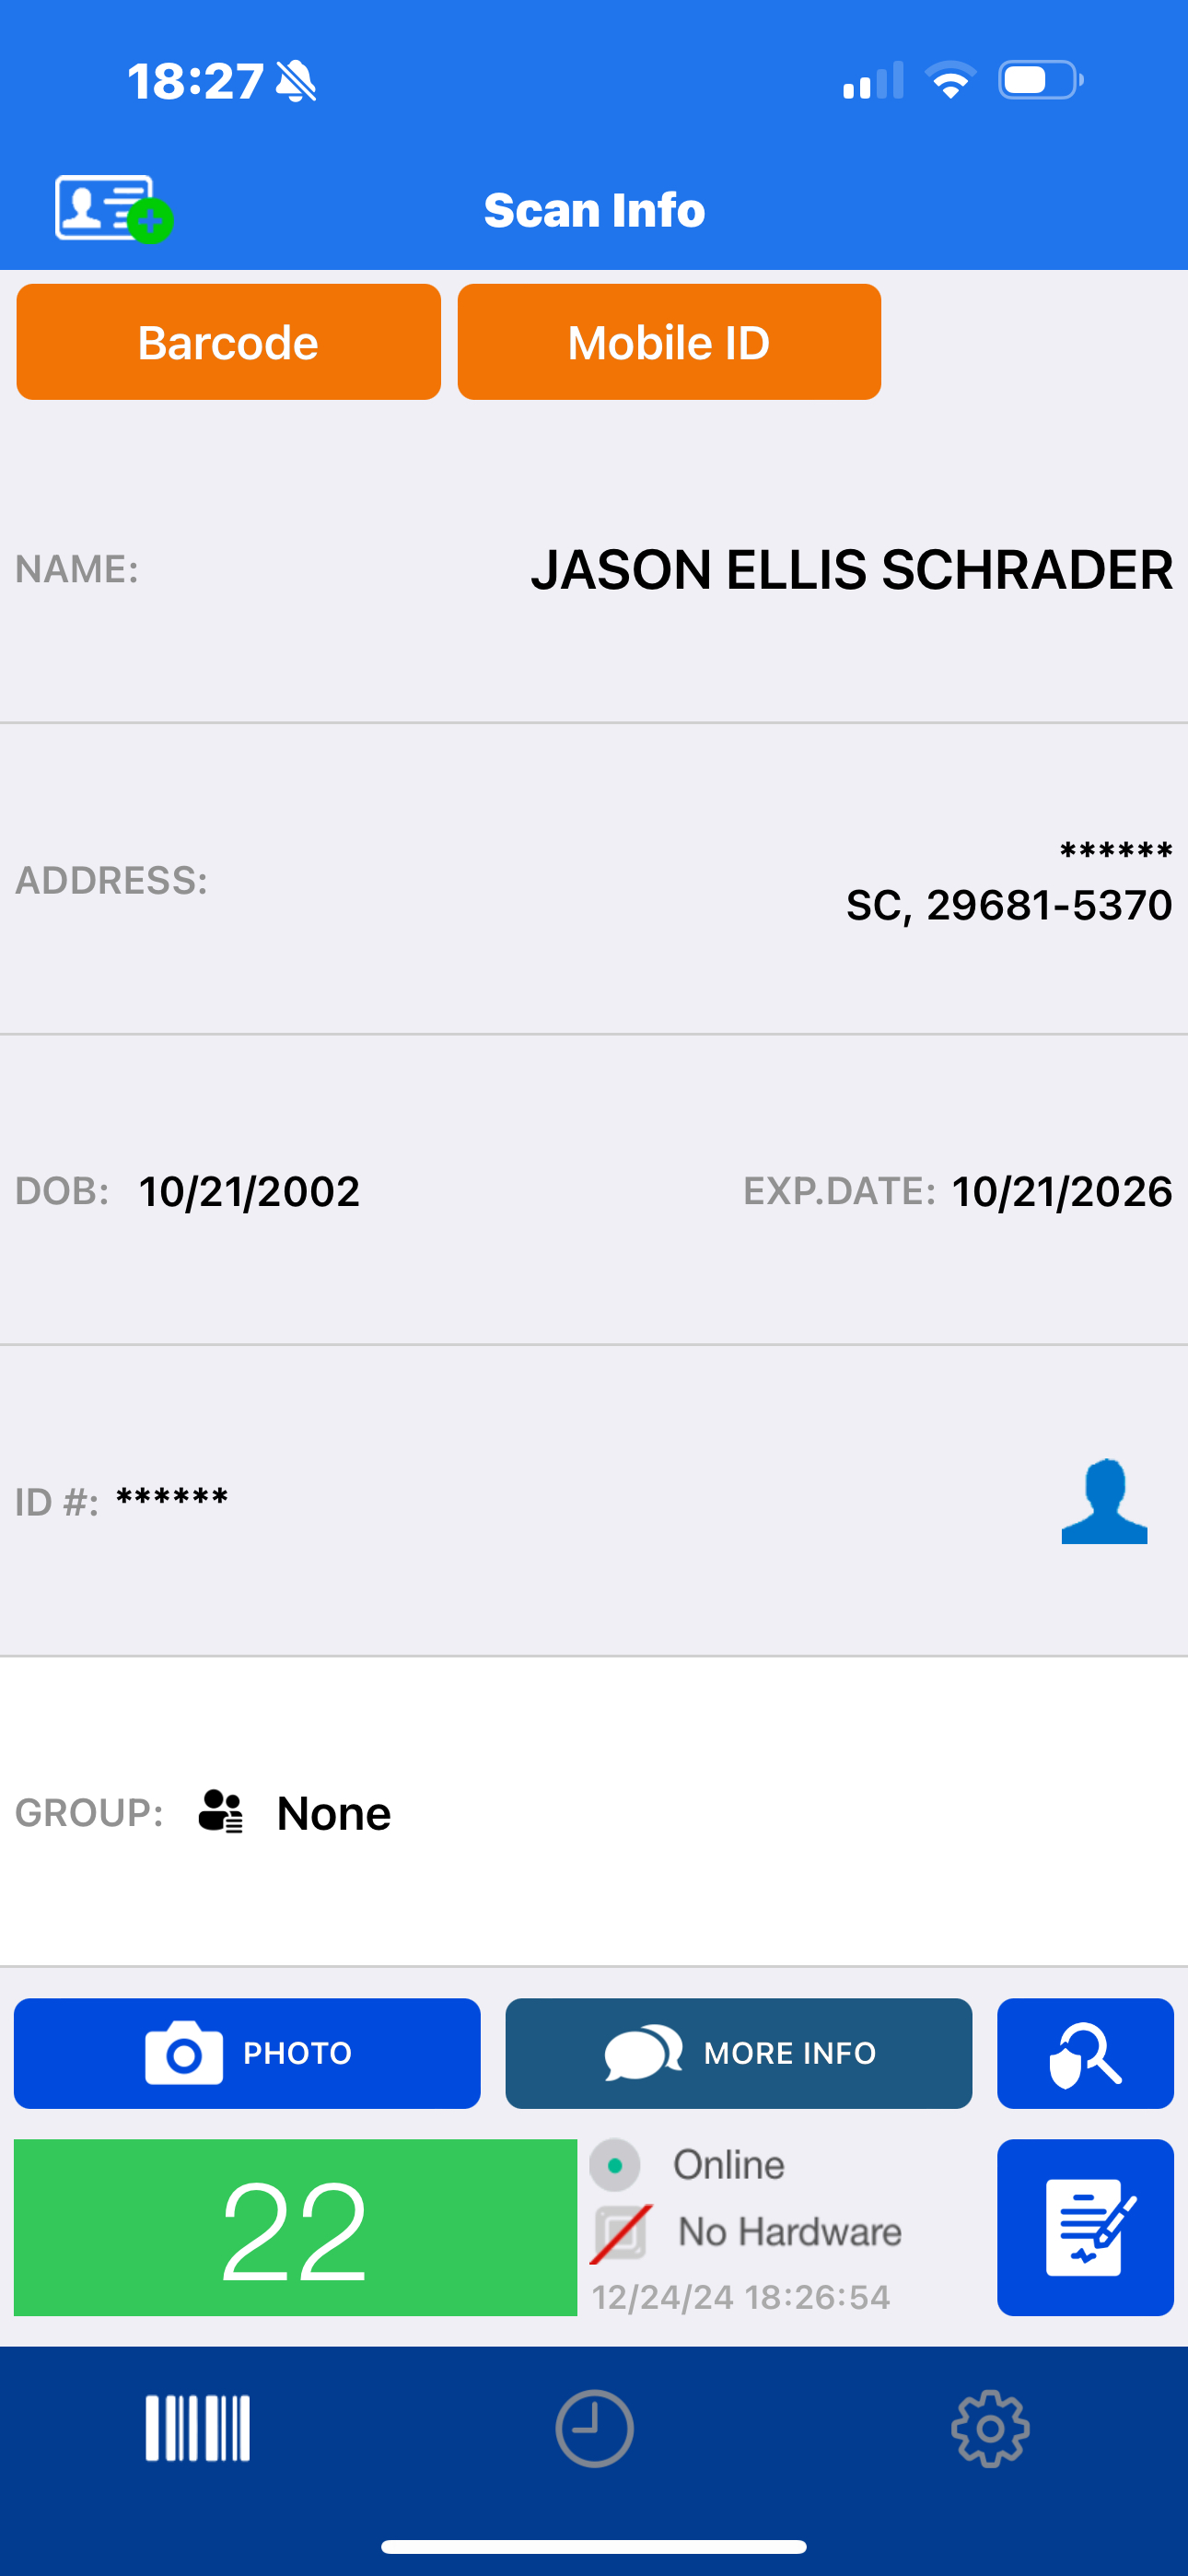
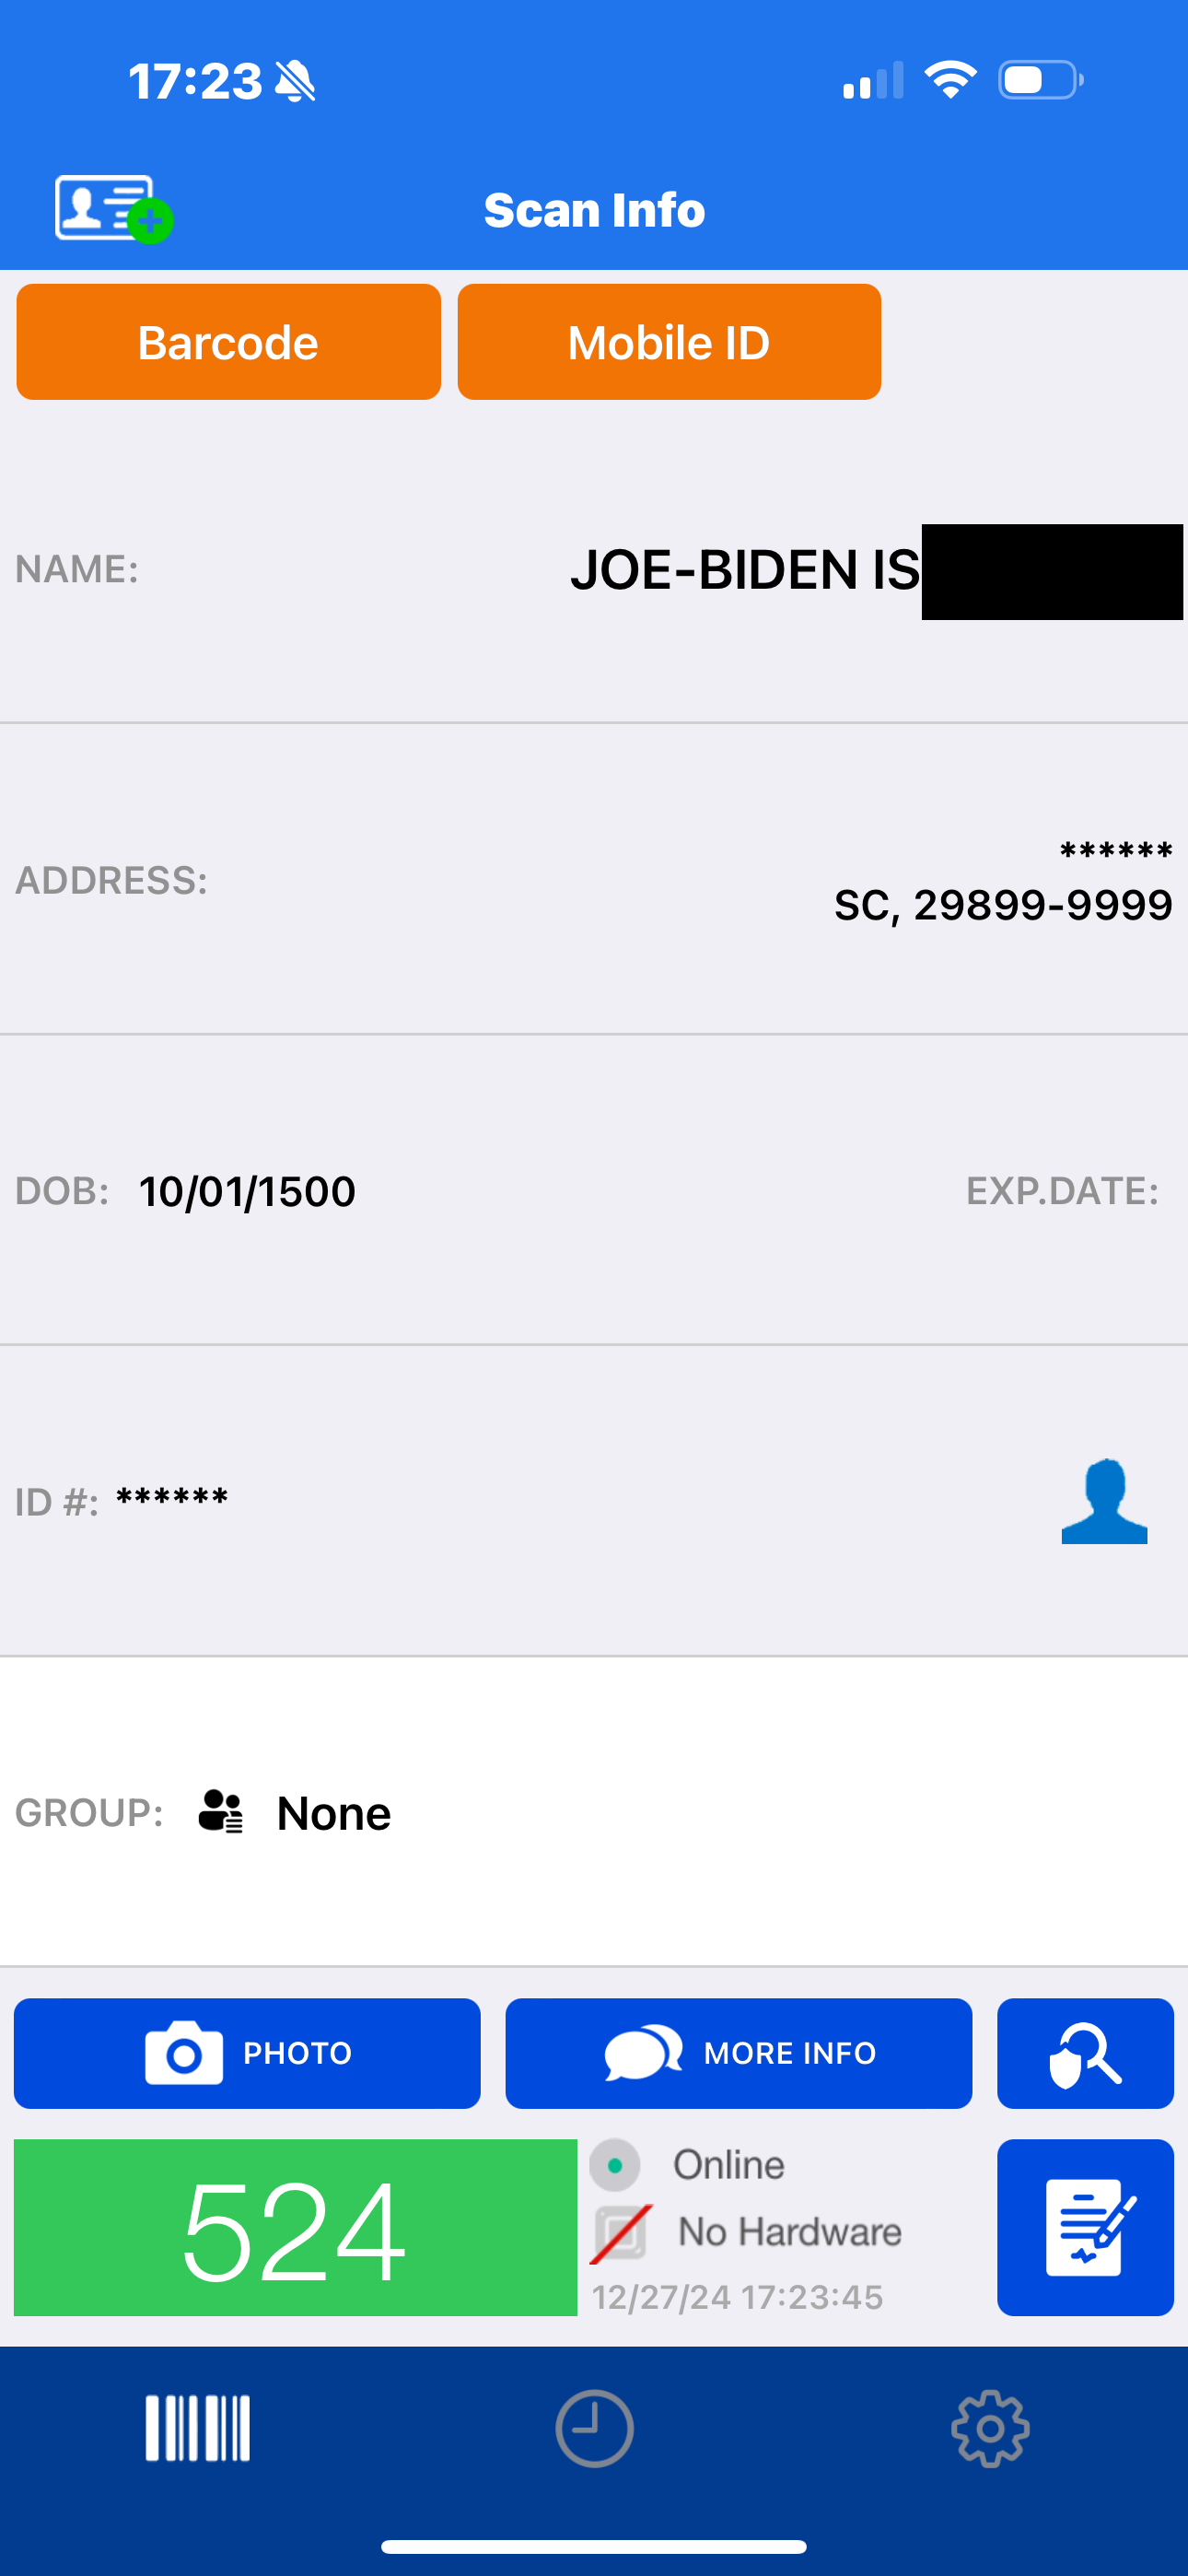```shell
gpg --verify signatures/veriscan/south_carolina/slander.png.asc scan_proof/veriscan/south_carolina/slander.png
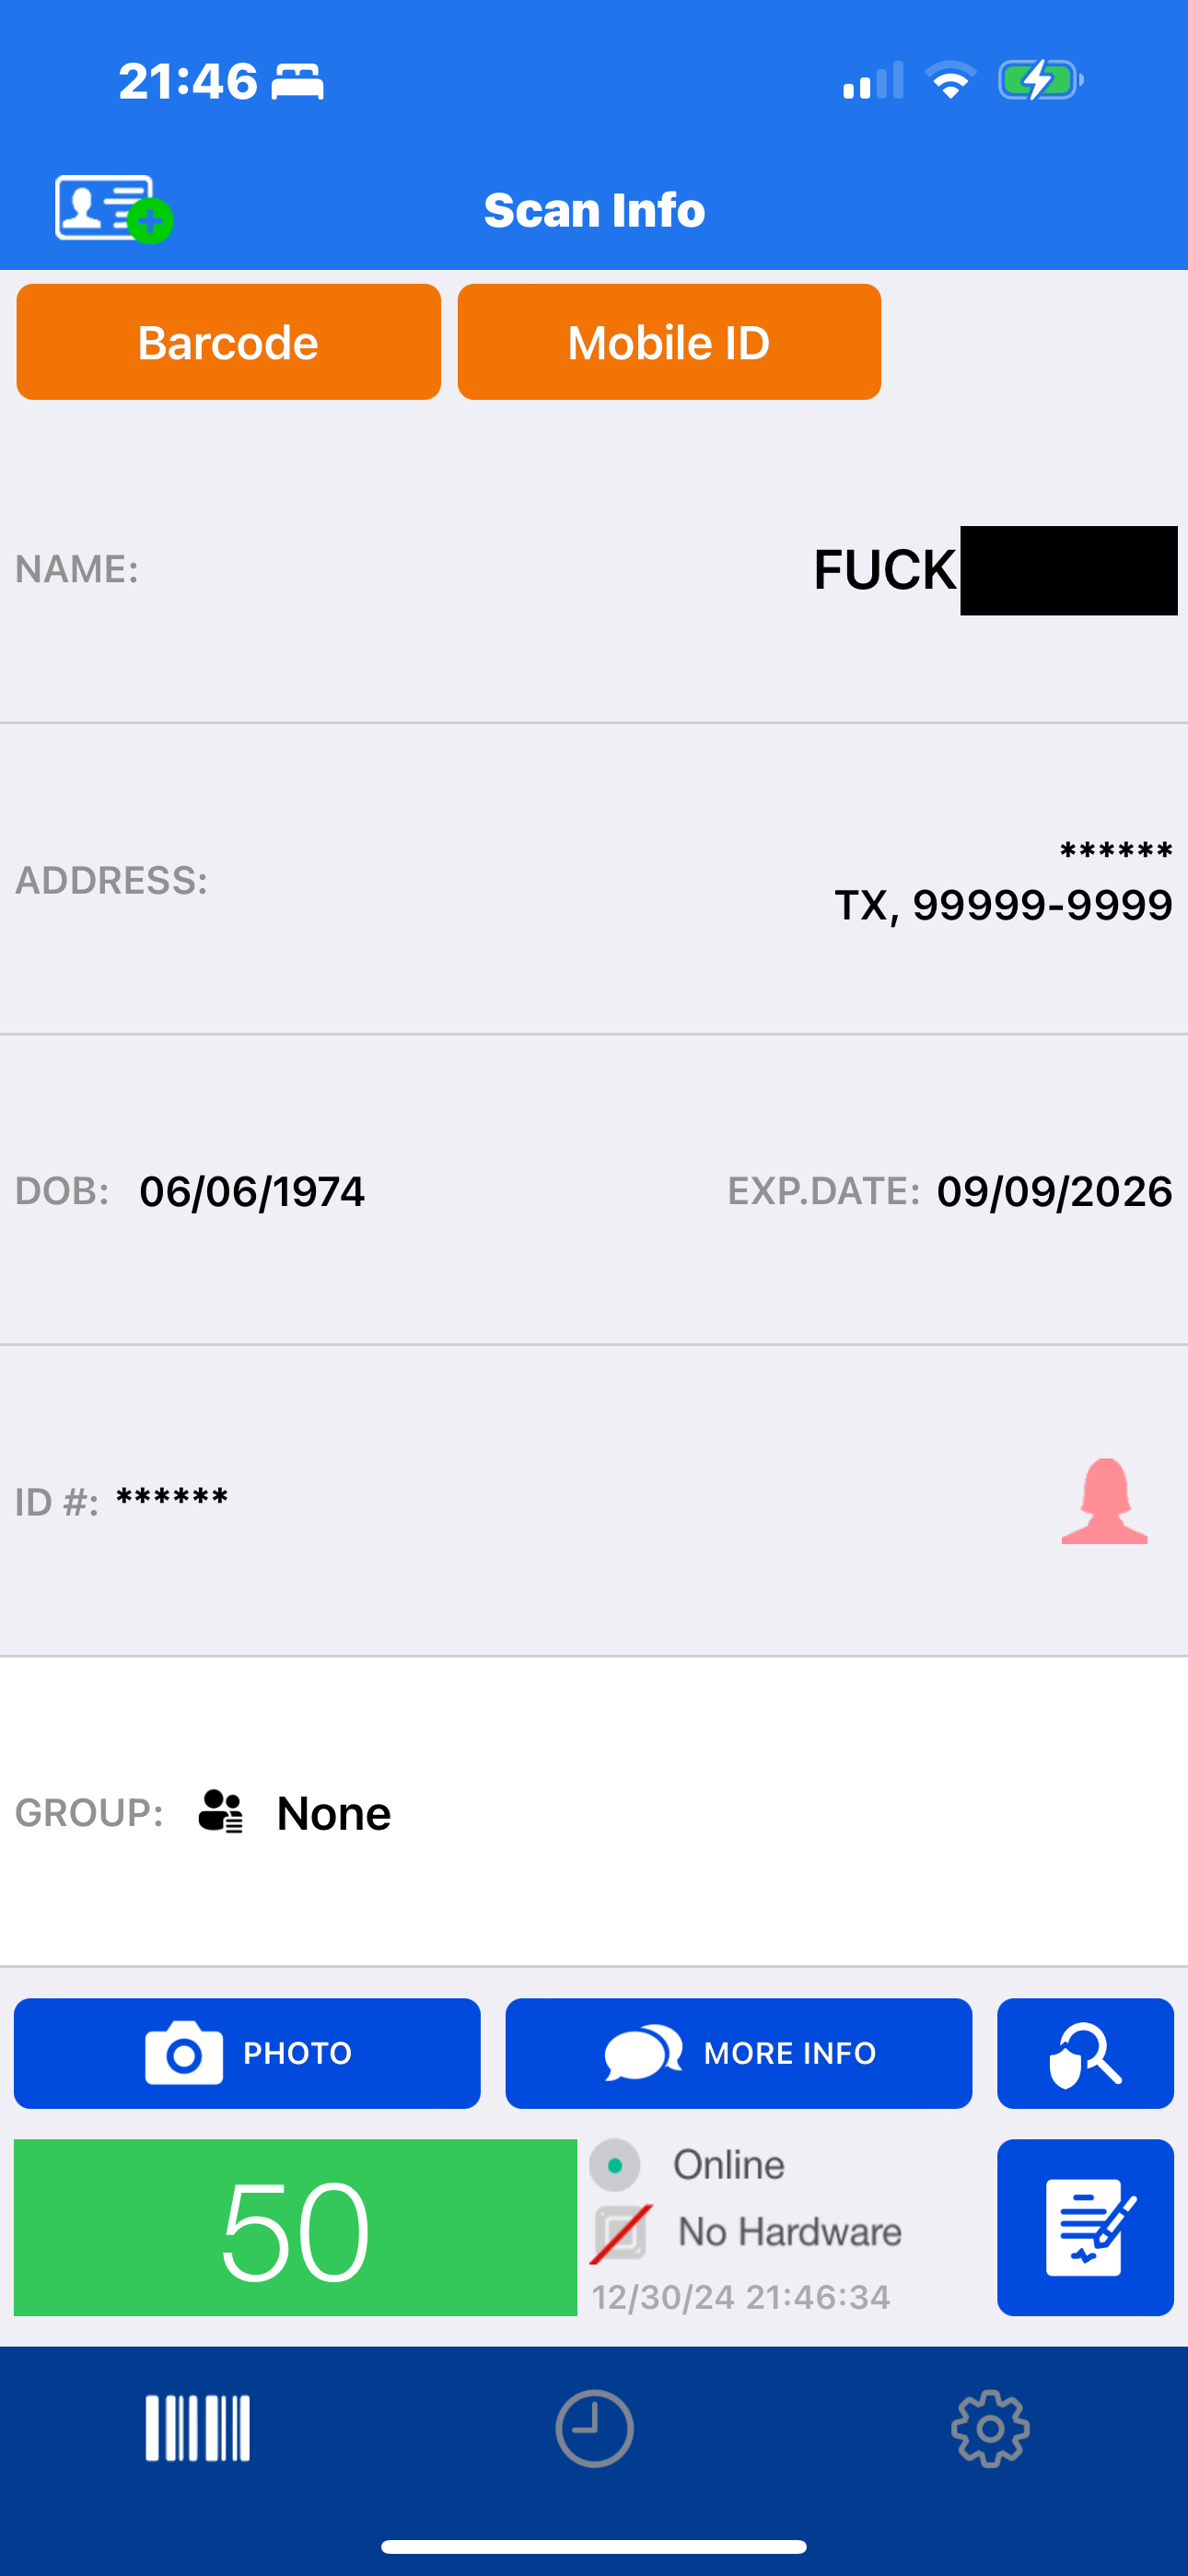 德克萨斯州绕过证据——展示跨州实现的一致漏洞模式```shell
gpg --verify signatures/veriscan/texas/slander.png.asc scan_proof/veriscan/texas/slander.png
## Technical Evidence and Vendor Rebuttals
## 技术证据与供应商反驳

### Documented Vulnerabilities
### 已记录的漏洞

#### 1. Temporal Validation Bypass
#### 1. 时间验证绕过
**Finding**: VeriScan accepts birth dates from medieval times (e.g., year 1500)
**发现**: VeriScan 接受中世纪时期的出生日期(例如,年份1500)
**Vendor Response**: *"Where do you draw the line, especially in just a parser"*
**供应商回应**: *"你在哪里划定界限,尤其是在一个解析器中"*
**Technical Counter**: Human physiological limits provide clear validation boundaries (max ~122 years)
**技术反驳**: 人类生理限制提供了明确的验证边界(最大约122年)

#### 2. Pattern Detection Failure
#### 2. 模式检测失败
**Finding**: Same license number with different names accepted repeatedly
**发现**: 相同驾照号码与不同姓名被重复接受
**Vendor Response**: *"We would not know if the first or second scan was real"*
**供应商回应**: *"我们无法知道第一次或第二次扫描是否真实"*
**Technical Counter**: Pattern detection flags suspicious behavior regardless of which is authentic
**技术反驳**: 模式检测会标记可疑行为,无论哪次是真实的

#### 3. Marketing Claims Discrepancy
#### 3. 营销声明差异
**Finding**: Product marketed as providing "security checks" and "fake ID detection"
**发现**: 产品宣传提供"安全检查"和"假身份证检测"
**Vendor Response**: *"Using only our parsing tool...you are limited to what feature sets you have"*
**供应商回应**: *"仅使用我们的解析工具...您受限于所拥有的功能集"*
**Technical Counter**: Marketing materials explicitly claim validation capabilities
**技术反驳**: 营销材料明确声称验证能力

#### 4. Commercial License Implications
#### 4. 商业驾照影响
**Finding**: CDL (Commercial Driver's License) bypass poses public safety risks
**发现**: CDL(商业驾照)绕过构成公共安全风险
**Vendor Response**: Not specifically addressed
**供应商回应**: 未特别回应
**Technical Impact**: Hazmat/transport credential spoofing potential
**技术影响**: 危险品/运输凭证欺骗的可能性

## CVE-2025-31337: IDScan.net Validation Flaw
## CVE-2025-31337: IDScan.net 验证缺陷