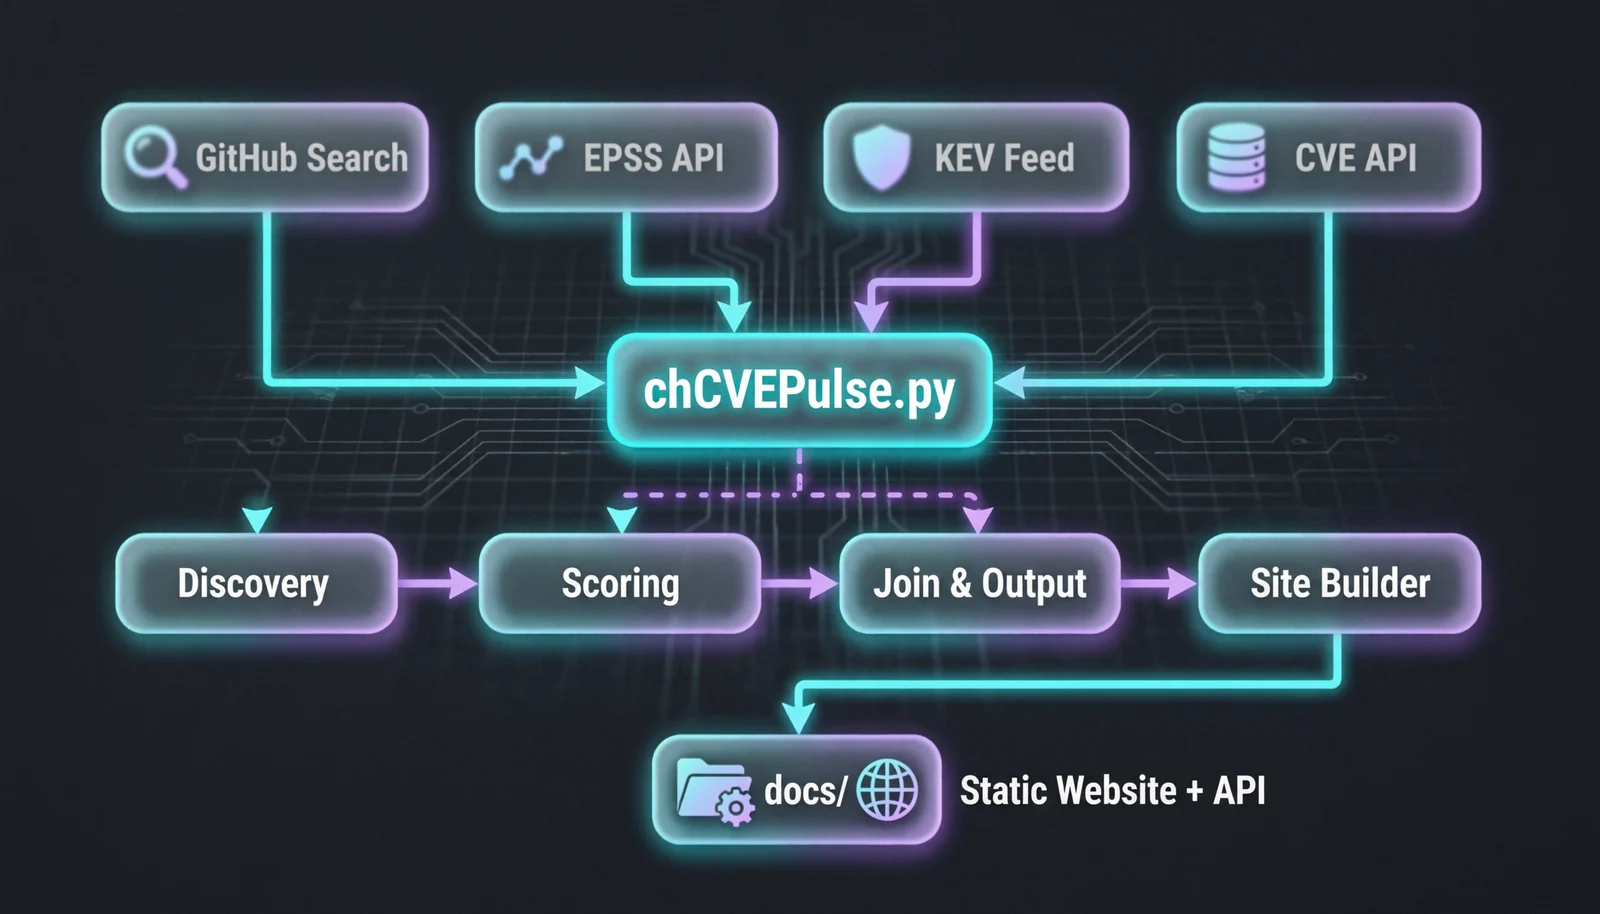
实时 CVE PoC(概念验证)聚合器,具备智能搜索与威胁情报功能

CVE Pulse 自动从 GitHub 发现、评分并索引 CVE 概念验证。
它使用 EPSS 评分 和 CISA KEV 数据对其进行丰富,构建每日 快照与差异对比,并提供快速、可搜索的 静态网站
Ch4120N – 安全爱好者与自动化爱好者。
📧 [email protected]
-windows)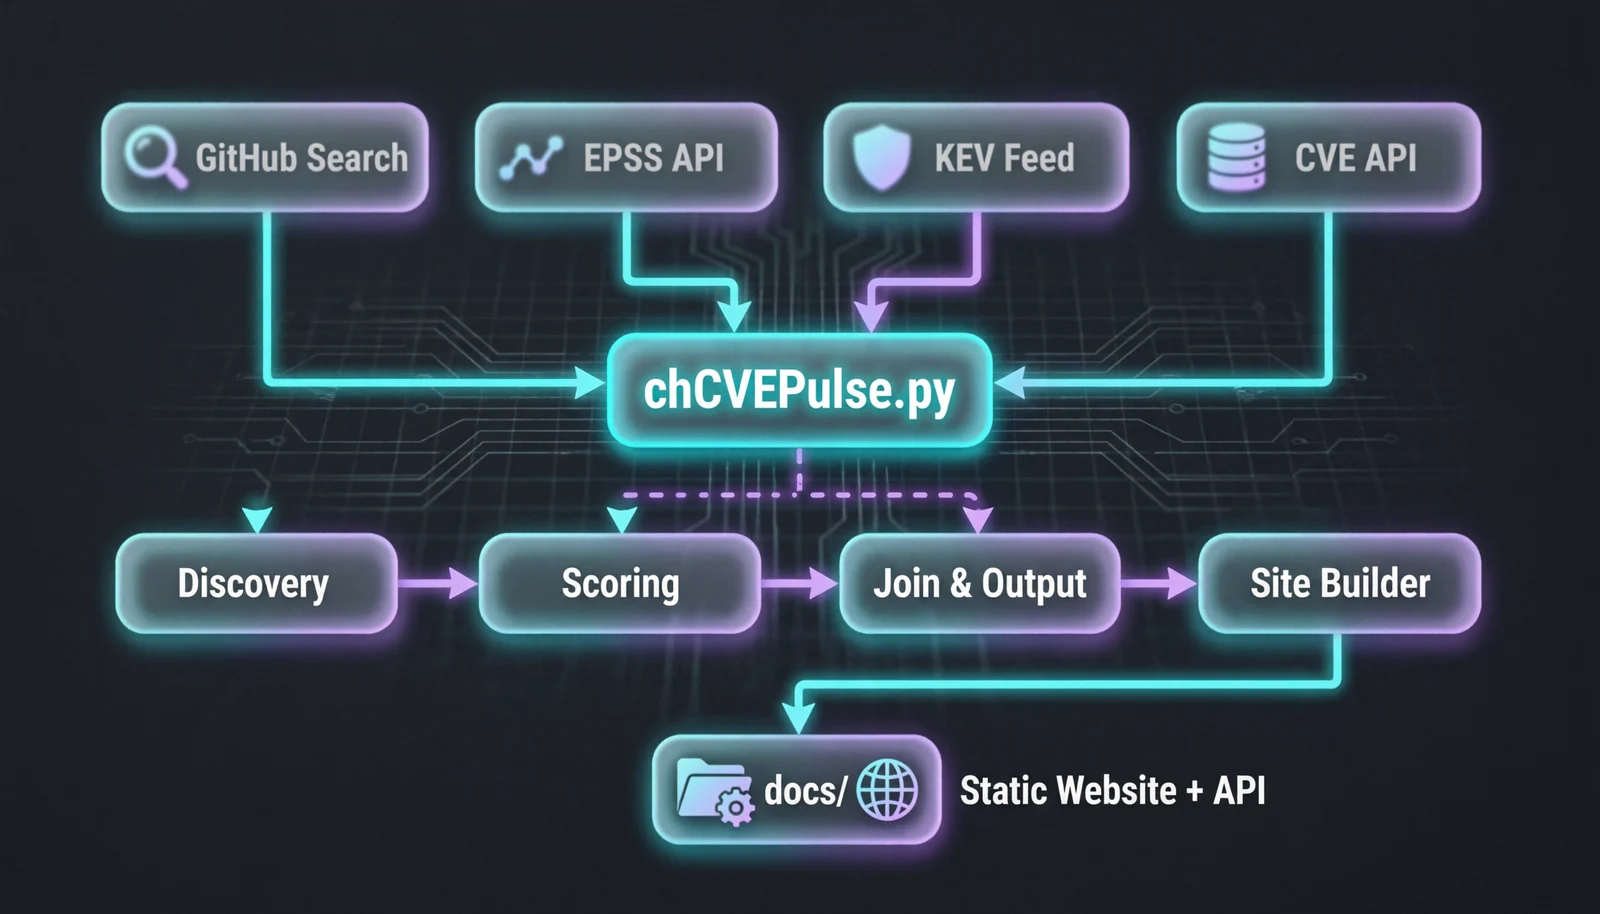
fetch-epss 下载 EPSS 评分排名前 2000 的 CVE。fetch-kev 下载 CISA KEV 目录。sync-cves 读取 data/github.txt 并从 MITRE API 获取 CVE 元数据,然后为每个 CVE 创建/更新 markdown 文件。pipeline(或单独的 build-* 命令):
github.txt 或之前的低置信度 CVE)。build-site 生成 CVE_list.json、trending_poc.json 和静态 HTML 页面。docs/)部署到 GitHub Pages。git clone https://github.com/Ch4120N/Ch4120N-CVE-Pulse.git cd Ch4120N-CVE-Pulse
pip install -r requirements.txt
python chCVEPulse.py fetch-epss python chCVEPulse.py fetch-kev
python chCVEPulse.py sync-cves
export GITHUB_TOKEN=your_token_here python chCVEPulse.py pipeline --days 7
python chCVEPulse.py build-site
---

## 📦 安装

**环境要求:**
- Python 3.9+
- `pip`

安装软件包:```bash
pip install -r requirements.txt
(requirements.txt 包含 requests、jinja2 以及其他依赖项。)
所有操作都通过单一脚本 chCVEPulse.py 完成。
示例:```bash
python chCVEPulse.py fetch-epss --limit 2000 python chCVEPulse.py fetch-kev
python chCVEPulse.py sync-cves --cve CVE-2025-12345
python chCVEPulse.py pipeline --days 7 --mode daily --limit 50
python chCVEPulse.py build-site --html-mode summary
### 完整流水线

`pipeline` 子命令可以进行微调:

- `--days`:回溯搜索 GitHub 的天数(默认:7)
- `--mode`:`daily`(近期 CVE,速度更快)或 `weekly`(更广泛的扫描)
- `--limit`:最多扫描的 CVE 数量(默认:50)
- `--cve`:指定一个或多个要扫描的 CVE ID
- `--skip-discovery`:仅从现有数据重新生成输出
- `--check-links`:验证仓库 URL 是否仍然有效

---

## 📊 输出与网站

流水线成功运行后,`docs/` 包含:

- **`index.html`** – 主搜索页面(由 `logic.js` 和 `style.css` 驱动)
- **`CVE_list.json`** – 所有 CVE 及其描述和 PoC 链接
- **`trending_poc.json`** – 最近更新的 PoC(来自自动更新的 README)
- **`api/v1/`** – 完整的类 REST JSON 端点:
  - `joined_top.json` – 带有 PoC、EPSS 和 KEV 状态的高优先级 CVE
  - `kev.json` – 增强的 KEV 列表
  - `epss_top.json` – 带有 PoC 的顶级 EPSS CVE
  - `cve/{CVE-ID}.json` – 每个 CVE 的详细 PoC 信息
  - `snapshots/` – 每日状态快照
  - `diffs/` – 逐日变化

搜索支持**模糊匹配**、供应商/产品过滤器以及否定词(例如 `-windows`)。

---

## 🗂️ 项目结构```
Ch4120N-CVE-Pulse/
├── chCVEPulse.py
├── scripts/
│   ├── config.py
│   ├── helpers.py
│   ├── github_api.py
│   ├── scoring.py
│   ├── discovery.py
│   ├── outputs.py
│   ├── diff.py
│   ├── joined.py
│   ├── site.py
│   ├── sync.py
│   ├── fetch_epss.py
│   ├── fetch_kev.py
│   └── pipeline.py
├── templates/
│   └── index.html# Jinja2 template for the website
├── data/
│   ├── github.txt# CVE -> PoC URL list (edit this)
│   ├── blacklist.txt
│   ├── cache/
│   └── evidence/
├── docs/
│   ├── api/v1/
│   └── index.html, style.css, logic.js
├── requirements.txt
└── README.md
几乎所有设置都位于 scripts/config.py 中:
GITHUB_SOURCES – 指向你的 data/github.txt 的路径EPSS_API_URL、KEV_URL、CVE_API_TEMPLATE – 外部 API 端点HIGH_EPSS_THRESHOLD – “高”警报的最低 EPSS 值TOP_KEV_COUNT – 保留多少条 KEV 条目SNAPSHOT_RETENTION_DAYS – 旧快照保留多长时间建议使用 GitHub token 以提高 API 速率限制(设置为 GITHUB_TOKEN 环境变量)。
三个 GitHub Actions 工作流保持一切更新:
sync_cve_pocs.yml – 每天运行,读取 data/github.txt,获取最新的 CVE 元数据并更新 markdown 文件。hot_cves.yml – 每 6 小时运行一次,更新本 README 中的 Trending PoCs 部分。site.yml – 构建静态网站并部署到 GitHub Pages。所有工作流都位于 .github/workflows/ 中。
下面的 Trending PoCs 表格由 CI 流水线每 6 小时自动更新。
本项目旨在用于威胁情报、漏洞管理和防御性安全研究。
请勿将链接的仓库用于任何非法或未经授权的活动。
作者不托管也不认可 PoC 代码——他们仅索引公开可用的信息。
GPLv3 许可证 – 完整文本请参见 LICENSE 文件。
"Stay ahead of threats – track every CVE PoC in real time."
⭐ 如果这个项目对你有帮助,请考虑给它一个 star!
Made with ❤️ by Ch4120N
| 命令 | 描述 |
|---|
fetch-epss | 下载 EPSS 数据 |
fetch-kev | 下载 KEV 目录 |
sync-cves | 从 data/github.txt 更新 CVE markdown 文件 |
build-site | 生成静态网站(CVE 列表 + HTML) |
build-diffs | 基于最近两次快照构建每日差异 |
build-joined | 创建合并的 KEV+EPSS+PoC JSON 端点 |
pipeline | 运行完整流水线(发现 → 输出 → 差异 → 网站) |
| 来源 | 描述 |
|---|
| GitHub Search API | 发现提及 CVE ID 的仓库 |
| GitHub GraphQL | 获取 star 数、语言、主题、fork/归档状态 |
| FIRST EPSS | 漏洞利用预测评分系统 |
| CISA KEV | 已知被利用漏洞目录 |
| MITRE CVE API | 官方 CVE 描述、参考、产品 |
| Stars | Updated | Repository | Description |
|---|
| 4070⭐ | 4 hours ago | copy-fail-CVE-2026-31431 | Copy Fail (CVE-2026-31431): 9-year-old Linux kernel LPE found by Theori's Xint Code |
| 576⭐ | 8 days ago | cve_2026_31431 | Exploit POC for CVE_2026_31431 |
| 329⭐ | 20 hours ago | CVE-2026-54121 | Certighost POC |
| 245⭐ | 8 hours ago | CVE-2026-43499-popsicle | CVE-2026-43499 Implementation for 6.12.23-android16-5-g75e9b1c7ae7c-abogki463945075-4k |
| 231⭐ | 4 days ago | CVE-2026-41089 | Netlogon and CLDAP vulnerability research with a proof of concept. |
| 304⭐ | 1 day ago | CVE-2026-21858 | n8n Ni8mare - Unauthenticated Arbitrary File Read to RCE Chain (CVSS 10.0) |
| 208⭐ | 14 days ago | CVE-2026-24061 | Exploitation of CVE-2026-24061 |
| 159⭐ | 6 days ago | CVE-2026-43499 | CVE-2026-43499 PoC |
| 177⭐ | 2 days ago | CVE-2026-62911 | POC pre-auth RCE on Exchange |
| 825⭐ | 2 days ago | CVE-2026-24061 | CVE-2026-24061 exploit PoC |
| 141⭐ | 17 hours ago | CVE-2026-42980-POC | CVE-2026-42980 PUBLIC EXPLOIT + RESEARCH |
| 101⭐ | 17 hours ago | CVE-2026-75604-poc | CVE-2026-75604 Next.js Windows RCE poc |
| 124⭐ | 7 days ago | CVE-2026-41651 | |
| 102⭐ | 23 hours ago | CVE-2026-43499-Poc-Analysis | Vulnerability analysis and Proof of Concept (PoC) for CVE-2026-43499 affecting Xiaomi devices. For educational and research purposes only. |
| 111⭐ | 25 days ago | CVE-2026-31431-Advanced-Exploit | CVE-2026-31431 纯文件利用 |
| 18⭐ | 6 days ago | CVE-2026-43499-Poc-Analysis | Vulnerability analysis and Proof of Concept (PoC) for CVE-2026-43499 affecting Xiaomi devices. For educational and research purposes only. |
| 63⭐ | 29 days ago | CVE-2026-45504 | CVE-2026-45504 Microsoft Exchange File Read |
| 41⭐ | 8 days ago | CVE-2026-31431 | |
| 109⭐ | 6 days ago | Copy-Fail-Exploit-CVE-2026-31431 | Most Linux LPEs need a race window or a kernel-specific offset. Copy Fail is a straight-line logic flaw, it needs neither. The same 732-byte Python script (or .c elf) roots every Linux distribution shipped since 2017. |
| 83⭐ | 7 days ago | CVE-2026-0073-Android-adbd-authentication-bypass-POC |
| Stars | Updated | Repository | Description |
|---|
| 1430⭐ | 1 day ago | CVE-2025-55182 | Explanation and full RCE PoC for CVE-2025-55182 |
| 792⭐ | 8 days ago | CVE-2025-55182-research | CVE-2025-55182 POC |
| 717⭐ | 2 days ago | CVE-2025-33073 | PoC Exploit for the NTLM reflection SMB flaw. |
| 528⭐ | 14 hours ago | CVE-2025-32463_chwoot | Escalation of Privilege to the root through sudo binary with chroot option. CVE-2025-32463 |
| 477⭐ | 8 days ago | CVE-2025-32463 | Local Privilege Escalation to Root via Sudo chroot in Linux |
| 313⭐ | 19 hours ago | CVE-2025-53770-Exploit | SharePoint WebPart Injection Exploit Tool |
| 314⭐ | 17 days ago | CVE-2025-55182 | RSC/Next.js RCE Vulnerability Detector & PoC Chrome Extension – CVE-2025-55182 & CVE-2025-66478 |
| 1062⭐ | 7 days ago | React2Shell-CVE-2025-55182-original-poc | Original Proof-of-Concepts for React2Shell CVE-2025-55182 |
| 406⭐ | 2 days ago | CVE-2025-24071_PoC | CVE-2025-24071: NTLM Hash Leak via RAR/ZIP Extraction and .library-ms File |
| 213⭐ | 1 day ago | CVE-2025-32023 | PoC & Exploit for CVE-2025-32023 / PlaidCTF 2025 "Zerodeo" |
| 385⭐ | 10 days ago | ColorOS-CVE-2025-10184 | ColorOS短信漏洞,以及用户自救方案 |
| 281⭐ | 17 hours ago | CVE-2025-55182-advanced-scanner- | |
| 432⭐ | 2 days ago | Next.js-RSC-RCE-Scanner-CVE-2025-66478 | A command-line scanner for batch detection of Next.js application versions and determining if they are affected by CVE-2025-66478 vulnerability. |
| 197⭐ | 1 day ago | POC-CVE-2025-24813 | his repository contains an automated Proof of Concept (PoC) script for exploiting CVE-2025-24813, a Remote Code Execution (RCE) vulnerability in Apache Tomcat. The vulnerability allows an attacker to upload a malicious serialized payload to the server, leading to arbitrary code execution via deserialization when specific conditions are met. |
| 190⭐ | 183 days ago | RSC-Detect-CVE-2025-55182 | RSC Detect CVE 2025 55182 |
| 194⭐ | 8 days ago | CVE-2025-30208-EXP | CVE-2025-30208-EXP |
| 142⭐ | 10 days ago | CVE-2025-32433 | CVE-2025-32433 https://github.com/erlang/otp/security/advisories/GHSA-37cp-fgq5-7wc2 |
| 119⭐ | 2 days ago | CVE-2025-43300 | This is POC for IOS 0click CVE-2025-43300 |
| 160⭐ | 8 days ago | CVE-2025-21756 | Exploit for CVE-2025-21756 for Linux kernel 6.6.75. My first linux kernel exploit! |
| 195⭐ | 27 days ago | CVE-2025-32756-POC | Proof of Concept for CVE-2025-32756 - A critical stack-based buffer overflow vulnerability affecting multiple Fortinet products. |
| Stars | Updated | Repository | Description |
|---|
| 2456⭐ | 2 days ago | CVE-2024-1086 | Universal local privilege escalation Proof-of-Concept exploit for CVE-2024-1086, working on most Linux kernels between v5.14 and v6.6, including Debian, Ubuntu, and KernelCTF. The success rate is 99.4% in KernelCTF images. |
| 689⭐ | 1 day ago | CVE-2024-38063 | poc for CVE-2024-38063 (RCE in tcpip.sys) |
| 497⭐ | 20 days ago | cve-2024-6387-poc | a signal handler race condition in OpenSSH's server (sshd) |
| 517⭐ | 1 day ago | CVE-2024-49113 | LdapNightmare is a PoC tool that tests a vulnerable Windows Server against CVE-2024-49113 |
| 526⭐ | 2 days ago | CVE-2024-6387_Check | CVE-2024-6387_Check is a lightweight, efficient tool designed to identify servers running vulnerable versions of OpenSSH |
| 224⭐ | 31 days ago | CVE-2024-38077 | RDL的堆溢出导致的RCE |
| 378⭐ | 23 days ago | cve-2024-6387-poc | 32-bit PoC for CVE-2024-6387 — mirror of the original 7etsuo/cve-2024-6387-poc |
| 333⭐ | 8 days ago | CVE-2024-21338 | Local Privilege Escalation from Admin to Kernel vulnerability on Windows 10 and Windows 11 operating systems with HVCI enabled. |
| 331⭐ | 5 days ago | CVE-2024-0044 | CVE-2024-0044: a "run-as any app" high-severity vulnerability affecting Android versions 12 and 13 |
| 320⭐ | 2 days ago | CVE-2024-4577 | PHP CGI Argument Injection (CVE-2024-4577) Remote Code Execution PoC |
| 285⭐ | 2 days ago | CVE-2024-21413 | CVE-2024-21413 PoC for THM Lab |
| 775⭐ | 1 day ago | CVE-2024-21413-Microsoft-Outlook-Remote-Code-Execution-Vulnerability | Microsoft-Outlook-Remote-Code-Execution-Vulnerability |
| 195⭐ | 2 days ago | CVE-2024-6387 | Remote Unauthenticated Code Execution Vulnerability in OpenSSH server (CVE-2024-6387) |
| 9⭐ | 40 days ago | CVE-2024-38077-POC | |
| 235⭐ | 59 days ago | CVE_2024_30078_POC_WIFI | basic concept for the latest windows wifi driver CVE |
| 181⭐ | 6 days ago | CVE-2024-25600 | Unauthenticated Remote Code Execution – Bricks <= 1.9.6 |
| 208⭐ | 2 days ago | CVE-2024-23897 | CVE-2024-23897 |
| 87⭐ | 40 days ago | CVE-2024-40725-CVE-2024-40898 | CVE-2024-40725 and CVE-2024-40898, affecting Apache HTTP Server versions 2.4.0 through 2.4.61. These flaws pose significant risks to web servers worldwide, potentially leading to source code disclosure and server-side request forgery (SSRF) attacks. |
| 113⭐ | 14 days ago | CVE-2024-6387 | PoC - Remote Unauthenticated Code Execution Vulnerability in OpenSSH server (Scanner and Exploit) |
| 156⭐ | 16 days ago | CVE-2024-21413 | Microsoft Outlook Information Disclosure Vulnerability (leak password hash) - Expect Script POC |
| Stars | Updated | Repository | Description |
|---|
| 784⭐ | 14 days ago | CVE-2023-38831-winrar-exploit | CVE-2023-38831 winrar exploit generator |
| 504⭐ | 2 days ago | Windows_LPE_AFD_CVE-2023-21768 | LPE exploit for CVE-2023-21768 |
| 381⭐ | 3 days ago | CVE-2023-32233 | CVE-2023-32233: Linux内核中的安全漏洞 |
| 418⭐ | 10 days ago | CVE-2023-0386 | CVE-2023-0386在ubuntu22.04上的提权 |
| 116⭐ | 8 days ago | CVE-2023-21839 | Weblogic CVE-2023-21839 RCE (无需Java依赖一键RCE) |
| 394⭐ | 19 days ago | CVE-2023-4911 | PoC for CVE-2023-4911 |
| 284⭐ | 13 days ago | CVE-2023-21608 | Adobe Acrobat Reader - CVE-2023-21608 - Remote Code Execution Exploit |
| 317⭐ | 35 days ago | CVE-2023-4863 | |
| 246⭐ | 2 days ago | CVE-2023-44487 | Basic vulnerability scanning to see if web servers may be vulnerable to CVE-2023-44487 |
| 245⭐ | 45 days ago | CVE-2023-7028 | This repository presents a proof-of-concept of CVE-2023-7028 |
| 228⭐ | 57 days ago | CVE-2023-3519 | RCE exploit for CVE-2023-3519 |
| 168⭐ | 2 days ago | CVE-2023-36745 | |
| 226⭐ | 10 days ago | CVE-2023-20887 | VMWare vRealize Network Insight Pre-Authenticated RCE (CVE-2023-20887) |
| 345⭐ | 2 days ago | CVE-2023-23397-POC-Powershell | |
| 183⭐ | 2 days ago | CVE-2023-28252 | |
| 136⭐ | 40 days ago | CVE-2023-2640-CVE-2023-32629 | GameOver(lay) Ubuntu Privilege Escalation |
| 240⭐ | 8 days ago | Weblogic-CVE-2023-21839 | |
| 205⭐ | 2 days ago | CVE-2023-46747-RCE | exploit for f5-big-ip RCE cve-2023-46747 |
| 236⭐ | 2 days ago | CVE-2023-29357 | Microsoft SharePoint Server Elevation of Privilege Vulnerability |
| 166⭐ | 8 days ago | CVE-2023-25157 | CVE-2023-25157 - GeoServer SQL Injection - PoC |
| Stars | Updated | Repository | Description |
|---|
| 1132⭐ | 1 day ago | CVE-2022-0847-DirtyPipe-Exploit | A root exploit for CVE-2022-0847 (Dirty Pipe) |
| 570⭐ | 8 days ago | CVE-2022-23222 | CVE-2022-23222: Linux Kernel eBPF Local Privilege Escalation |
| 360⭐ | 37 days ago | CVE-2022-21907 | HTTP Protocol Stack Remote Code Execution Vulnerability CVE-2022-21907 |
| 357⭐ | 15 hours ago | CVE-2022-40684 | A proof of concept exploit for CVE-2022-40684 affecting Fortinet FortiOS, FortiProxy, and FortiSwitchManager |
| 377⭐ | 35 days ago | CVE-2022-29464 | WSO2 RCE (CVE-2022-29464) exploit and writeup. |
| 735⭐ | 2 hours ago | CVE-2022-0847-DirtyPipe-Exploits | A collection of exploits and documentation that can be used to exploit the Linux Dirty Pipe vulnerability. |
| 437⭐ | 3 days ago | CVE-2022-25636 | CVE-2022-25636 |
| 487⭐ | 6 days ago | CVE-2022-2588 | exploit for CVE-2022-2588 |
| 497⭐ | 24 days ago | CVE-2022-0995 | CVE-2022-0995 exploit |
| 385⭐ | 2 days ago | CVE-2022-39197 | CobaltStrike <= 4.7.1 RCE |
| 414⭐ | 2 days ago | CVE-2022-33679 | One day based on https://googleprojectzero.blogspot.com/2022/10/rc4-is-still-considered-harmful.html |
| 281⭐ | 10 days ago | CVE-2022-0847 | CVE-2022-0847-DirtyPipe-Exploit CVE-2022-0847 是存在于 Linux内核 5.8 及之后版本中的本地提权漏洞。攻击者通过利用此漏洞,可覆盖重写任意可读文件中的数据,从而可将普通权限的用户提升到特权 root。 CVE-2022-0847 的漏洞原理类似于 CVE-2016-5195 脏牛漏洞(Dirty Cow),但它更容易被利用。漏洞作者将此漏洞命名为“Dirty Pipe” |
| 354⭐ | 18 hours ago | CVE-2022-21894 | baton drop (CVE-2022-21894): Secure Boot Security Feature Bypass Vulnerability |
| 609⭐ | 2 days ago | CVE-2022-38694_unlock_bootloader | This is a one-time signature verification bypass. For persistent signature verification bypass, check https://github.com/TomKing062/CVE-2022-38691_38692 |
| 377⭐ | 2 days ago | CVE-2022-0185 | CVE-2022-0185 |
| 284⭐ | 31 days ago | cve-2022-27255 | |
| 265⭐ | 172 days ago | CVE-2022-39952 | POC for CVE-2022-39952 |
| 238⭐ | 31 days ago | CVE-2022-20699 | Cisco Anyconnect VPN unauth RCE (rwx stack) |
| 236⭐ | 9 days ago | CVE-2022-30075 | Tp-Link Archer AX50 Authenticated RCE (CVE-2022-30075) |
| 218⭐ | 10 days ago | CVE-2022-34918 | CVE-2022-34918 netfilter nf_tables 本地提权 POC |