| item | content | remark |
|---|---|---|
| Authorized penetration range | http://192.168.88.141/ | Local test |
| Source code download | https://www.seacms.net/SeaCMS_V13.1_install_f.zip | Open source project |
| Scope of vulnerability | SeaCMS_V13.1 |
| category | content | remark |
|---|---|---|
| Vulnerability location(URL) | http://192.168.200.141/reg.php?action=reg | |
| Vulnerability type | Logic hole | |
| Vulnerability description | SeaCMS has a logical flaw that could be exploited by an attacker to allow any user to register accounts in bulk |
Visit the registration page and click Register to capture the package (this is the photo added later)
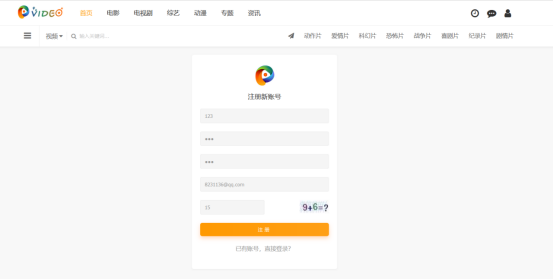
*The verification code here is 14*
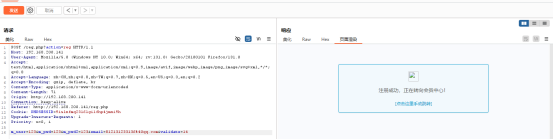
*Change your account number and email address*

*Try logging in to the first account here*
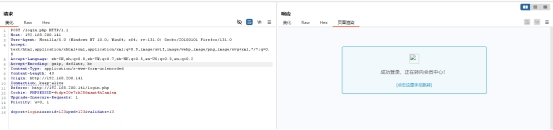
*Try to log in to the second account*