Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

··订阅源·联系·隐私·© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
haruspex — 漏洞研究助手,可从 IDA Hex-Rays 反编译器中提取伪代码。 | Kitploit
工具/GitHubGitHub/0xdea/haruspex
静态代码分析 (SAST)漏洞分析逆向工程二进制分析
GitHub0xdea/haruspex

haruspex

漏洞研究助手,可从 IDA Hex-Rays 反编译器中提取伪代码。

查看仓库网站
13110312天前Kitploit 审核通过

最受欢迎

查看全部 →

发现我们社区最常用的工具。

探索所有工具

浏览我们的工具集合

查看所有工具 →
分享

haruspex

build doc

“黑客技术是一门时刻质疑你所有假设的学科。”

-- Dave Aitel

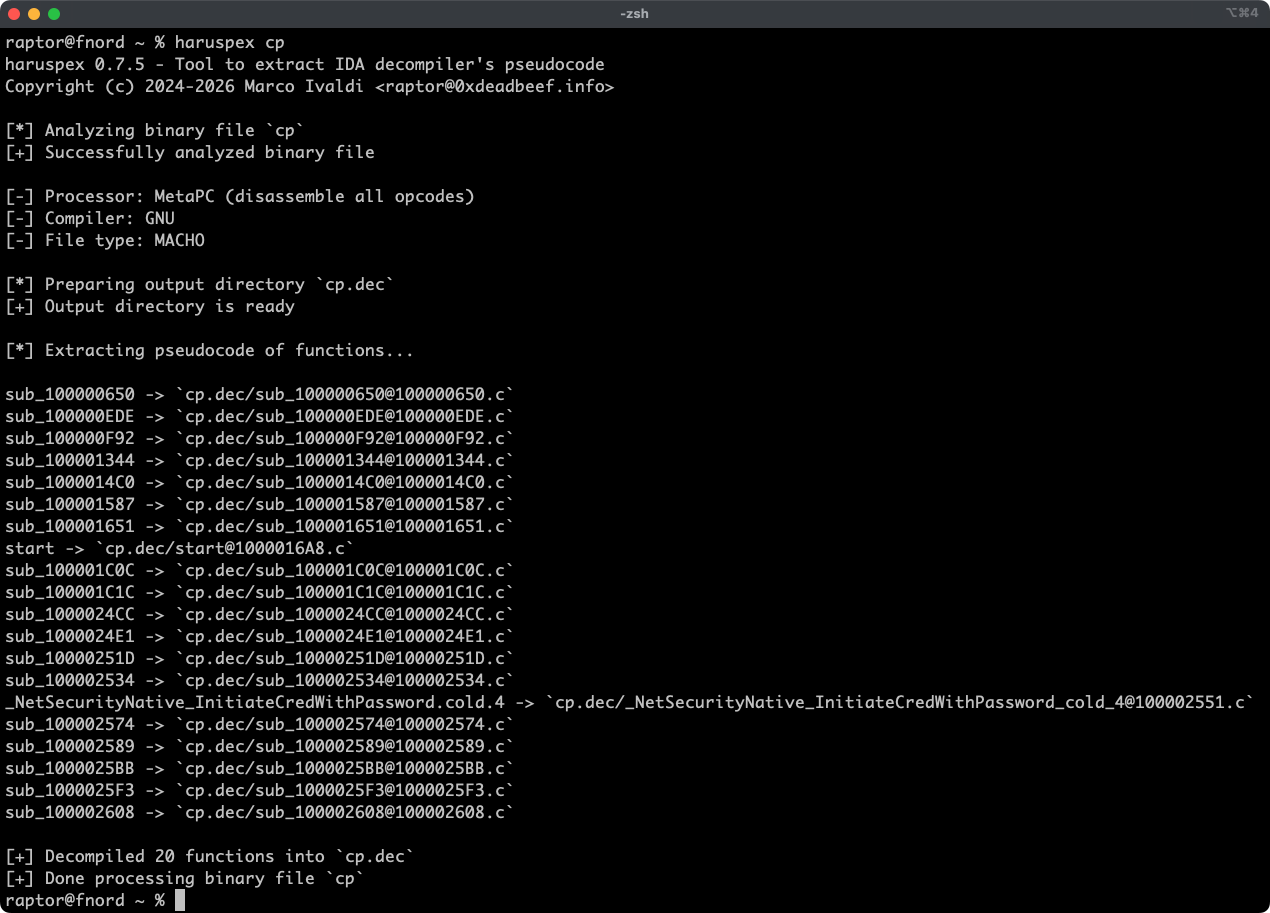
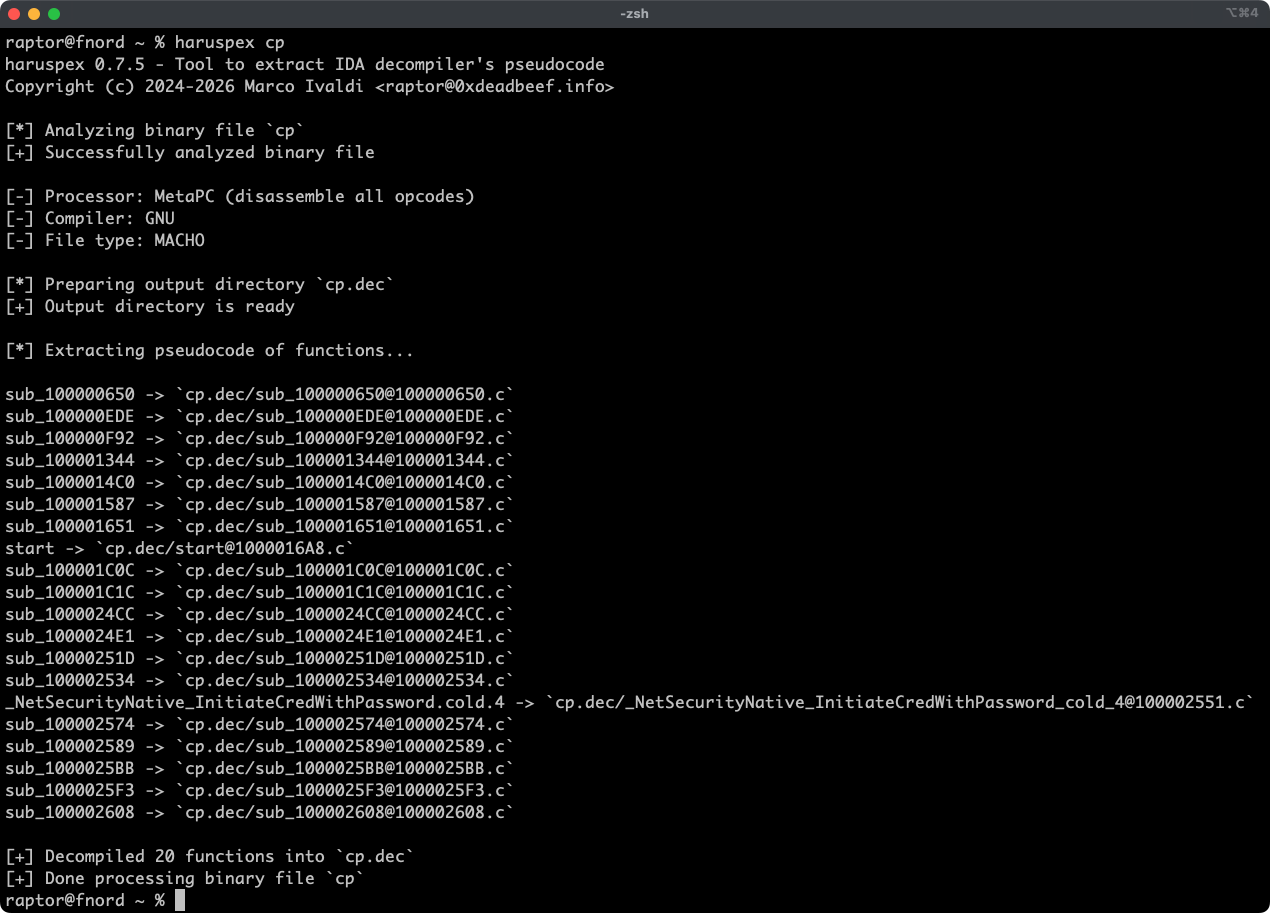
Haruspex 是一个极速的 IDA 无头插件,用于提取 IDA 反编译器生成的伪代码,其格式应适合导入 IDE,或由静态分析工具(如 Semgrep、weggli 或 oneiromancer)进行解析。
功能特性

  • 极速、无头用户体验,得益于 IDA 9.x 和 idalib-rs Rust 绑定。
  • 支持 IDA 的 Hex-Rays 反编译器所实现的任何架构的二进制目标。
  • 每个函数的伪代码存储在输出目录中的单独文件里,便于检查。
  • 全局和每个函数的类型定义被提取到与伪代码并列的头文件中。
  • 外部 crate 可以调用 [decompile_to_file] 来反编译一个函数,并将其伪代码和类型定义保存到磁盘。

文章

  • https://hex-rays.com/blog/streamlining-vulnerability-research-idalib-rust-bindings
  • https://hnsecurity.it/blog/streamlining-vulnerability-research-with-ida-pro-and-rust

另请参阅

  • https://github.com/0xdea/ghidra-scripts/blob/main/Haruspex.java
  • https://github.com/0xdea/semgrep-rules
  • https://github.com/0xdea/weggli-patterns
  • https://docs.hex-rays.com/release-notes/9_0#headless-processing-with-idalib
  • https://github.com/idalib-rs/idalib
  • https://github.com/xorpse/parascope
  • https://hnsecurity.it/blog/automating-binary-vulnerability-discovery-with-ghidra-and-semgrep

安装

获取最新版本的最简单方式是通过 crates.io:

  1. 下载、安装并配置 IDA(参见 https://hex-rays.com/ida-pro)。
  2. 安装 LLVM/Clang(参见 https://rust-lang.github.io/rust-bindgen/requirements.html)。
  3. 在 Linux/macOS 上,按如下方式安装:
    root@kitploit:~
    export IDADIR=/path/to/ida # if not set, the build script will check common locations
    cargo install haruspex --locked
    
    而在 Windows 上,请使用以下命令:
    root@kitploit:~
    $env:LIBCLANG_PATH="\path\to\clang+llvm\bin"
    $env:PATH="\path\to\ida;$env:PATH"
    $env:IDADIR="\path\to\ida" # if not set, the build script will check common locations
    cargo install haruspex --locked
    

编译

或者,你可以从源代码构建:

  1. 下载、安装并配置 IDA(参见 https://hex-rays.com/ida-pro)。
  2. 安装 LLVM/Clang(参见 https://rust-lang.github.io/rust-bindgen/requirements.html)。
  3. 在 Linux/macOS 上,按如下方式编译:
    root@kitploit:~
    git clone --depth 1 https://github.com/0xdea/haruspex
    cd haruspex
    export IDADIR=/path/to/ida # if not set, the build script will check common locations
    cargo build --release --locked
    
    而在 Windows 上,请使用以下命令:
    root@kitploit:~
    git clone --depth 1 https://github.com/0xdea/haruspex
    cd haruspex
    $env:LIBCLANG_PATH="\path\to\clang+llvm\bin"
    $env:PATH="\path\to\ida;$env:PATH"
    $env:IDADIR="\path\to\ida" # if not set, the build script will check common locations
    cargo build --release --locked
    

用法

  1. 确保 IDA 已使用有效许可证正确配置。
  2. 如果你的 IDA 安装位置非标准,请确保设置了 IDADIR 环境变量。
  3. 按如下方式运行:
    root@kitploit:~
    haruspex <binary_file>
    
  4. 在 binary_file.dec 目录中找到提取的伪代码和类型定义:
    root@kitploit:~
    vim <binary_file>.dec
    code <binary_file>.dec
    

兼容性

官方仅支持最新的 IDA 版本,但较旧版本也可能可用。下表总结了每个 IDA 版本的最新兼容版本:

[!NOTE] 查看 idalib-rs 文档以获取更多信息。

致谢

本项目的开发得到了以下组织的支持:

  • HN Security
  • Hex-Rays 通过其贡献者计划

更新日志

  • CHANGELOG.md

待办事项

  • 添加一个 Semgrep CI 回归测试,以确保已解析行的百分比不会下降。
  • 使用 .cpp 扩展名而不是 .c 来输出伪代码(参见此问题)?
  • 实现序列化输出,以促进自动化解析和分析。
  • 与 Semgrep 扫描集成(参见 https://github.com/0xdea/semgrep-rules)。
  • 与 weggli 扫描集成(参见 https://github.com/0xdea/weggli-patterns)。
  • 以 HexRaysPyTools 和 abyss 的风格改进反编译器输出。
  • 实现并行分析(参见 https://github.com/fugue-re/fugue-mptp)。
下载工具
IDA 版本最新兼容版本
v9.0.240925v0.2.4
v9.0.241217v0.3.5
v9.1.250226v0.6.2
v9.2.250908v0.7.5
v9.3.260213v0.8.1
v9.3.260327v0.9.0
v9.3.260421v0.9.3
v9.4.260714当前版本
v9.4.260915当前版本