
🔬 防御性安全研究 • 漏洞分析 • 检测
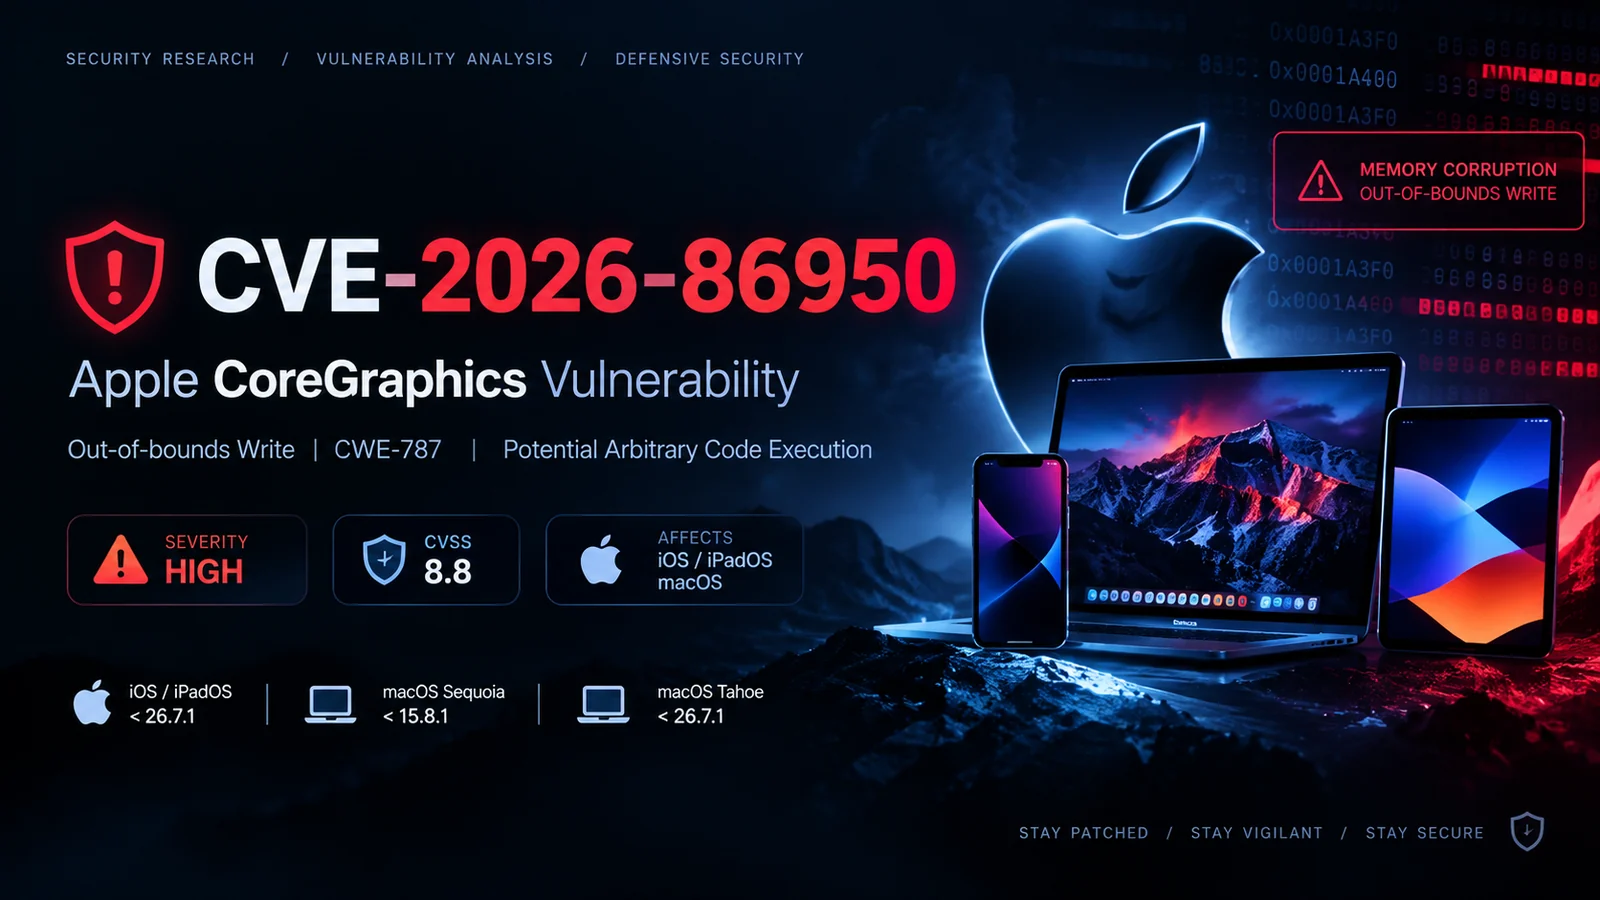
CVE-2026-86950 是一个影响 Apple CoreGraphics 组件的高危漏洞。
该漏洞被归类为越界写入(CWE-787),当存在漏洞的系统处理特制内容时,可能导致内存损坏和任意代码执行。
⚠️ 安全提示
本仓库仅用于经授权的安全研究、漏洞评估、检测和防御性分析。
| 属性 | 详情 |
|---|---|
| 🆔 CVE | CVE-2026-86950 |
| 🧩 组件 | Apple CoreGraphics |
| 🐛 弱点 | CWE-787 — 越界写入 |
| 🔥 严重性 | 高 |
| 📊 CVSS | 8.8 |
| 🌐 攻击向量 | 网络 |
| 👤 所需权限 | 无 |
| 🖱️ 用户交互 | 必需 |
| 💥 潜在影响 | 代码执行 / 内存损坏 |
| 🎯 利用状态 | 已报告有针对性的利用 |
该漏洞影响包含存在漏洞的 CoreGraphics 实现的特定版本 Apple 操作系统。
iOS / iPadOS
macOS Sequoia
macOS Tahoe
iOS / iPadOS       → 26.7.1+
macOS Sequoia     → 15.8.1+
macOS Tahoe       → 26.7.1+
💡 在执行评估之前,应根据 Apple 当前的安全公告核实版本号。
该漏洞属于:
CWE-787
Out-of-bounds Write
从概念上讲,越界写入发生在软件将数据写入为对象或缓冲区分配的内存区域之外时。
简化表示:
┌───────────────────────────────┐
│       Allocated Buffer        │
├───────────────┬───────────────┤
│   Valid Data  │     Valid     │
└───────────────┴───────────────┘
                  ↓
             ❌ Invalid Write
                  ↓
┌──────────────────────────────────────┐
│ Adjacent Memory / Control Structures │
└──────────────────────────────────────┘
根据周围的内存布局和特定缺陷的可利用性,内存损坏漏洞可能带来严重的安全后果。
潜在的安全后果可能包括:
实际影响取决于存在漏洞的执行路径、受影响的进程、缓解措施以及恶意内容到达目标系统的方式。
对于防御性评估,首先确定已安装的操作系统版本。
sw_vers
示例:
ProductName:    macOS
ProductVersion: 15.x.x
BuildVersion:   XXXXX
导航至:
Settings
   ↓
General
   ↓
About
   ↓
iOS Version / iPadOS Version
然后将已安装版本与 Apple 的安全更新信息进行比较。
主要缓解措施是将受影响的 Apple 设备更新到已修复安全问题的版本。
1. 🔎 Identify affected devices
2. 📋 Determine installed OS versions
3. 🔐 Apply Apple's security updates
4. 🔄 Reboot if required
5. 🧪 Verify the patched version
6. 📊 Monitor endpoints for suspicious activity
组织应优先处理处理不受信任文件或内容的系统。
本项目有意聚焦于非破坏性漏洞研究。
推荐工作流程:
                 ┌─────────────────┐
                 │ Identify Target  │
                 └────────┬────────┘
                          ↓
                 ┌─────────────────┐
                 │ Determine Build │
                 └────────┬────────┘
                          ↓
                 ┌─────────────────┐
                 │ Check Exposure  │
                 └────────┬────────┘
                          ↓
                 ┌─────────────────┐
                 │ Apply Patch     │
                 └────────┬────────┘
                          ↓
                 ┌─────────────────┐
                 │ Verify Fix      │
                 └────────┬────────┘
                          ↓
                 ┌─────────────────┐
                 │ Document Result │
                 └─────────────────┘
对于实验室研究,请尽可能使用隔离设备或虚拟化测试环境。
| 类别 | 评级 |
|---|---|
| 🔥 严重性 | 高 |
| 🌐 远程攻击可能性 | 可能适用 |
| 👤 身份验证 | 根据 CVSS 向量不需要 |
| 🖱️ 用户交互 | 必需 |
| 💻 机密性 | 高影响 |
| ✏️ 完整性 | 高影响 |
| 📴 可用性 | 高影响 |
[ ] Identify Apple devices in the environment
[ ] Collect OS/build versions
[ ] Identify systems below the fixed versions
[ ] Prioritize internet-facing / high-value endpoints
[ ] Deploy Apple's security updates
[ ] Verify successful patch deployment
[ ] Review endpoint telemetry
[ ] Investigate suspicious crashes or document-processing events
[ ] Record remediation status
本仓库可用于:
它有意避免提供针对真实世界系统的武器化利用。
本项目仅用于:
经授权的安全测试、防御性研究、教育和漏洞评估。
未经明确授权,请勿使用本仓库中的研究材料攻击系统。
维护者不对此处所提供信息的滥用负责。
🔎 NIST 国家漏洞数据库
CVE-2026-86950🍎 Apple 安全发布
🛡️ CISA 已知被利用漏洞目录
┌─────────────────────────────────────┐
│       CVE-2026-86950 Research       │
├─────────────────────────────────────┤
│ Status       │ 🟠 Research / Review │
│ Severity     │ 🔴 HIGH              │
│ Analysis     │ 🔬 Defensive         │
│ Exploitation │ 🚫 Not provided      │
└─────────────────────────────────────┘
保持补丁更新。保持警惕。保持安全。🔐