Skip to content
KitploitKITPLOIT
工具博客
Log in
提交
工具博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

··订阅源·联系·隐私·© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
CVE-2026-44277 — CVE-2026-44277 | Kitploit
工具/GitHubGitHub/0xblackash/cve-2026-44277
侦察漏洞分析漏洞利用Web应用程序漏洞利用信息收集渗透测试
GitHub0xblackash/cve-2026-44277

CVE-2026-44277

CVE-2026-44277

查看仓库
54个月前尚未审核

最受欢迎

查看全部 →

发现我们社区最常用的工具。

探索所有工具

浏览我们的工具集合

查看所有工具 →
分享

🚨 CVE-2026-44277 - FortiAuthenticator 未授权远程代码执行

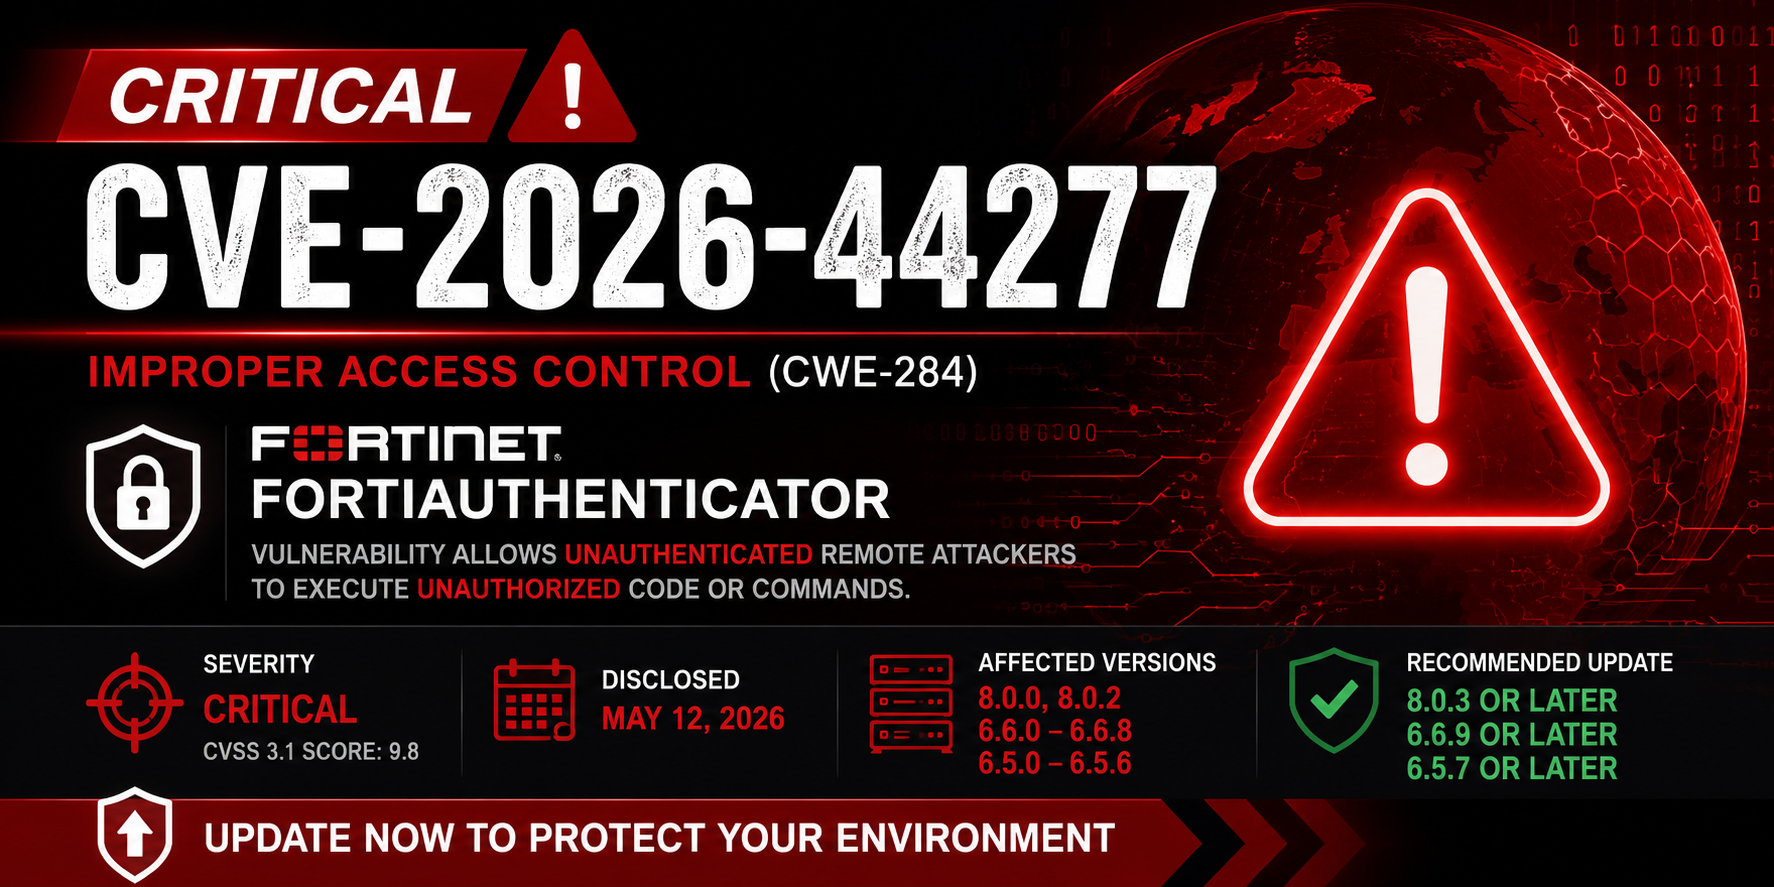
ChatGPT Image May 13, 2026, 05_25_26 PM

Fortinet FortiAuthenticator 中的严重未授权远程代码执行漏洞

Critical Fortinet RCE


📋 概述

CVE-2026-44277 是 Fortinet FortiAuthenticator 中的一个严重漏洞,允许未授权攻击者通过特定 API 端点的不当访问控制实现远程代码执行(RCE)。

🛠 受影响版本

产品受影响版本修复版本
FortiAuthenticator6.5.0 - 6.5.66.5.7+
FortiAuthenticator6.6.0 - 6.6.86.6.9+
FortiAuthenticator8.0.0 - 8.0.28.0.3+

注意:FortiAuthenticator Cloud 不受影响。

⚡ 影响

  • 未授权远程代码执行
  • 设备的完全入侵
  • 潜在横向移动至 Active Directory / RADIUS 环境
  • 对使用 FortiAuthenticator 进行双因素认证、RADIUS 或 SAML 的组织构成高风险

🧪 PoC 使用方法

python3 CVE-2026-44277.py http://target-ip

示例输出(存在漏洞):

[*] Testing → /api/v1/aaa → Reachable
[!!] Potential vulnerable endpoint found!
[!!] Target is likely vulnerable to CVE-2026-44277

🛡️ 缓解措施

  • 立即升级至最新修补版本
  • 限制访问 FortiAuthenticator 管理界面(使用 VPN + IP 白名单)
  • 禁用不必要的 API 访问

🔍 Shodan / FoFa 搜索语法

FoFa:

app="Fortinet-FortiAuthenticator"

Shodan:

"FortiAuthenticator" port:443
下载工具