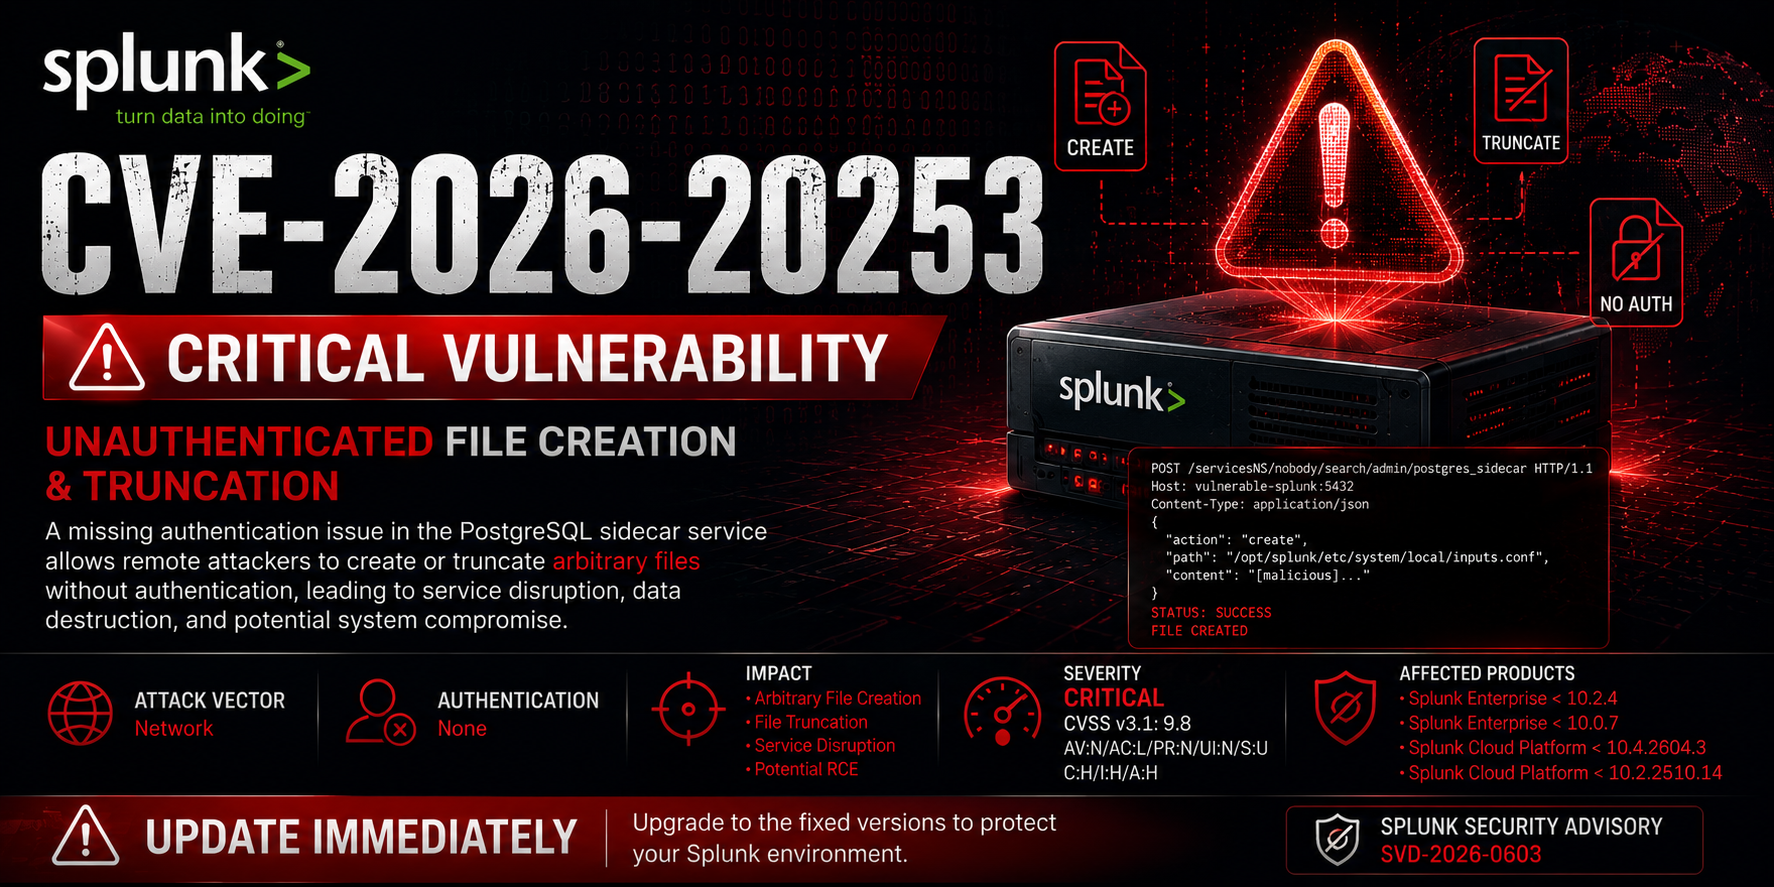


未认证的任意文件创建与截断漏洞,影响Splunk Enterprise与Splunk Cloud Platform。
CVE-2026-20253 是 Splunk Enterprise 与 Splunk Cloud Platform 中的一个高危漏洞,允许未认证的远程攻击者通过暴露的PostgreSQL sidecar服务端点创建或截断任意文件。
由于受影响的功能缺乏认证控制,攻击者可在无有效凭证的情况下执行文件操作。
成功利用可能导致:
| 属性 | 值 |
|---|---|
| CVE | CVE-2026-20253 |
| 厂商 | Splunk |
| 严重性 | 严重 |
| CVSS v3.1 | 9.8 |
| CWE | CWE-306 |
| 漏洞类型 | 缺失身份认证 |
| 攻击向量 | 网络 |
| 认证 | 无 |
| 用户交互 | 无 |
| 影响 | 文件创建 / 文件截断 |

漏洞存在于PostgreSQL sidecar服务组件中,该组件暴露了敏感的文件操作功能。
由于缺少身份认证检查:
Remote User
        │
        ▼
Accessible Sidecar Endpoint
        │
        ▼
Create Arbitrary Files
        │
        ▼
Truncate Existing Files
        │
        ▼
System Impact
攻击者只需拥有对暴露服务的网络访问权限。
Attacker
    │
    ▼
Locate Exposed Splunk Service
    │
    ▼
Connect To PostgreSQL Sidecar
    │
    ▼
Unauthenticated Request
    │
    ▼
Create/Overwrite Files
    │
    ▼
Service Disruption
    │
    ▼
Potential Escalation
Potential exposure of sensitive operational data.
Arbitrary file modification can compromise system integrity.
Critical files may be truncated, causing outages.
SIEM infrastructure may become unreliable or unavailable.
| 版本 | 状态 |
|---|---|
| < 10.2.4 | 受影响 |
| < 10.0.7 | 受影响 |
| 版本 | 状态 |
|---|---|
| < 10.4.2604.3 | 受影响 |
| < 10.2.2510.14 | 受影响 |
| 产品 | 安全版本 |
|---|---|
| Splunk Enterprise | 10.2.4+ |
| Splunk Enterprise | 10.0.7+ |
| Splunk Cloud Platform | 10.4.2604.3+ |
| Splunk Cloud Platform | 10.2.2510.14+ |
CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H
| 指标 | 值 |
|---|---|
| 攻击向量 | 网络 |
| 攻击复杂度 | 低 |
| 所需权限 | 无 |
| 用户交互 | 无 |
| 机密性 | 高 |
| 完整性 | 高 |
| 可用性 | 高 |
常见端口:
8000
8089
8191
5432
http.title:"Splunk"
product:"Splunk"
http.html:"Splunk"
title="Splunk"
body="Splunk"
app="Splunk"
app:"Splunk"
异常情况:
File creation events
File truncation events
Service failures
Configuration changes
Database sidecar access
find /opt/splunk -mtime -1
find /opt/splunk -size 0
journalctl -xe
grep -Ri "postgres" /opt/splunk/var/log/
寻找以下内容:
Unexpected empty files
Modified configuration files
Splunk restart anomalies
Unauthorized service access
Network connections to sidecar components
潜在目标:
server.conf
inputs.conf
outputs.conf
authentication.conf
web.conf
1. Discover vulnerable Splunk instance
2. Reach PostgreSQL sidecar endpoint
3. Submit crafted request
4. Create or truncate target file
5. Observe system impact
⚠️ 武器化利用代码已故意省略。
10.2.4+
10.0.7+
VPN-only access
Internal management network
ACL restrictions
Firewall filtering
File creation activity
Configuration modifications
Unexpected service restarts
Management Interfaces
        │
        ├── Internal VLAN
        ├── VPN Access
        └── Zero Trust Controls
启用:
Auditd
Sysmon for Linux
EDR telemetry
Network monitoring
该漏洞为何重要:
攻陷 Splunk 将极大影响组织检测攻击的能力。
CVE-2026-20253/
│
├── README.md
│
├── assets/
│   ├── CVE-2026-20253.png
│   └── screenshots/
│
├── advisory/
│   ├── technical-analysis.md
│   ├── attack-surface.md
│   └── patch-guidance.md
│
├── detection/
│   ├── sigma/
│   ├── yara/
│   ├── splunk-searches/
│   └── hunting-guide.md
│
├── iocs/
│   └── indicators.md
│
└── references/
    └── links.md
本仓库仅用于以下目的:
所有测试应仅针对您拥有或明确授权评估的系统进行。
Splunk Enterprise • 严重 • CVSS 9.8




