IFRIT 是一个基于AI的反向代理,它实时拦截传入请求,将每个请求分类为合法或恶意。合法流量被转发到后端;恶意流量则收到定制的AI生成的蜜罐响应,该响应使用伪造数据模仿请求的资源,诱骗攻击者浪费时间。
IFRIT 是一个智能反向代理,位于互联网和你的应用程序之间,实时分析每个请求。合法流量无缝通过。恶意流量?它会获得 AI 生成的蜜罐响应,浪费攻击者的时间,同时你收集情报。
subgraph "IFRIT Proxy Layer"
    B[🛡️ IFRIT Proxy]

    subgraph "AI Detection Engine"
        C1[🤖 Claude Sonnet 4]
        C2[🤖 Gemini 2.0 Flash]
    end

    subgraph "Threat Intelligence"
        D1[📊 AbuseIPDB]
        D2[🦠 VirusTotal]
        D3[🌍 IPInfo]
    end
end

subgraph Backend
    E[🎯 Your Application]
end

subgraph "Attacker Receives"
    F[🍯 Fake Data<br/>Honeypot Response]
end

subgraph "User Receives"
    G[📦 Real Data<br/>Protected]
end

A -->|Malicious Request| B
L -->|Normal Request| B

B --> C1
B --> C2

B --> D1
B --> D2
B --> D3

B -->|Attack Detected| F
B -->|Legitimate| E
E -->|Response| G

F -.->|Wasted Time| A
G -->|Secure Access| L

style A fill:#ff6b6b,stroke:#c92a2a,stroke-width:2px,color:#fff
style L fill:#51cf66,stroke:#2f9e44,stroke-width:2px,color:#fff
style B fill:#4c6ef5,stroke:#364fc7,stroke-width:3px,color:#fff
style C1 fill:#845ef7,stroke:#5f3dc4,stroke-width:2px,color:#fff
style C2 fill:#845ef7,stroke:#5f3dc4,stroke-width:2px,color:#fff
style D1 fill:#ff922b,stroke:#e8590c,stroke-width:2px,color:#fff
style D2 fill:#ff922b,stroke:#e8590c,stroke-width:2px,color:#fff
style D3 fill:#ff922b,stroke:#e8590c,stroke-width:2px,color:#fff
style E fill:#20c997,stroke:#12b886,stroke-width:2px,color:#fff
style F fill:#fa5252,stroke:#c92a2a,stroke-width:2px,color:#fff
style G fill:#51cf66,stroke:#2f9e44,stroke-width:2px,color:#fff
</details>

**简化流程:**

<div align="center">
  <img src="https://assets.kitploit.com/production/public/readmes/9318/20428ce8d35f40faaa17f7f8c313021a74af35675f384b2db7a60034dbfdcdf2.png" alt="IFRIT 简易流程图" width="650">
</div>

</div>


---


## 🚀 快速入门

> **两分钟之内完成启动并运行**

### 📦 安装

<table>
<tr>
<td width="50%">

**macOS(Apple Silicon)**```bash
curl -L -o ifrit-v0.3.2-darwin-arm64.tar.gz \
  https://github.com/0tSystemsPublicRepos/IfritProxy/releases/download/v0.3.2/ifrit-v0.3.2-darwin-arm64.tar.gz


tar -xzf ifrit-v0.3.2-darwin-arm64.tar.gz
cd ifrit-v0.3.2-darwin-arm64
./install.sh
Linux (x64)```bash
curl -LO https://github.com/0tSystemsPublicRepos/\
IfritProxy/releases/download/v0.3.2/
ifrit-v0.3.2-linux-amd64.tar.gz
tar -xzf ifrit-v0.3.2-linux-amd64.tar.gz cd ifrit-v0.3.2-linux-amd64 ./install.sh
</td>
</tr>
</table>
<div align="center">
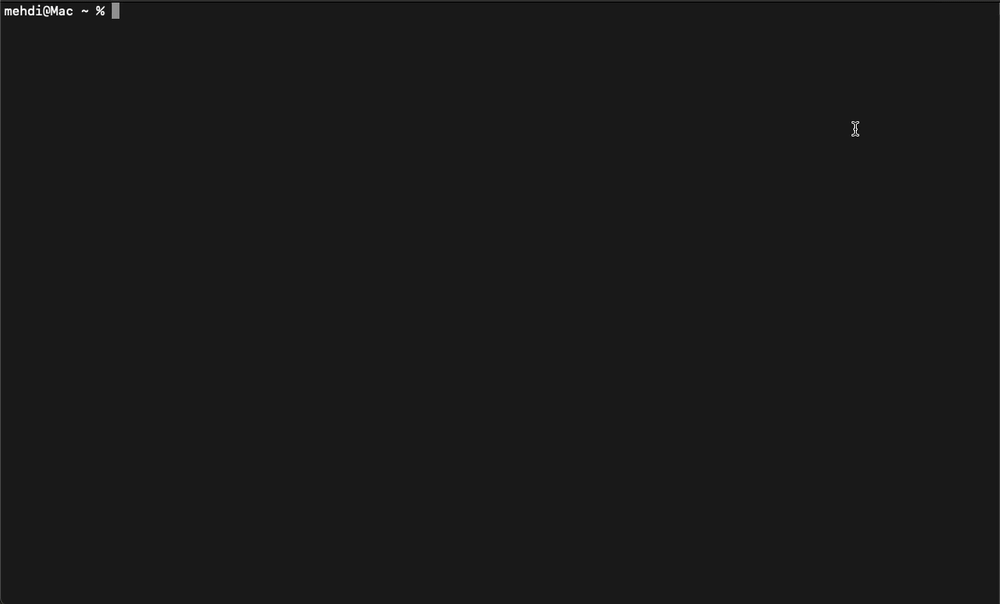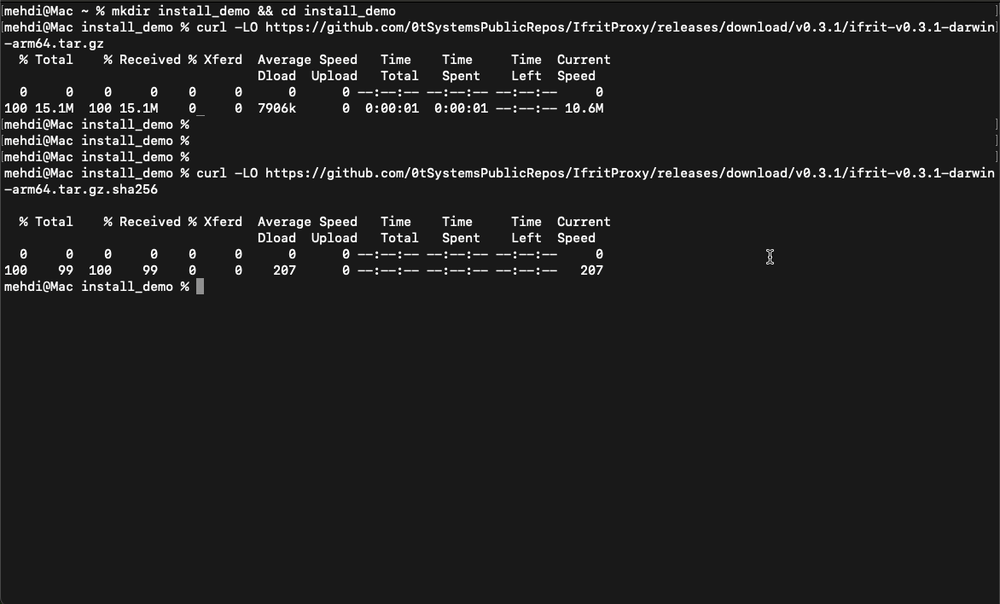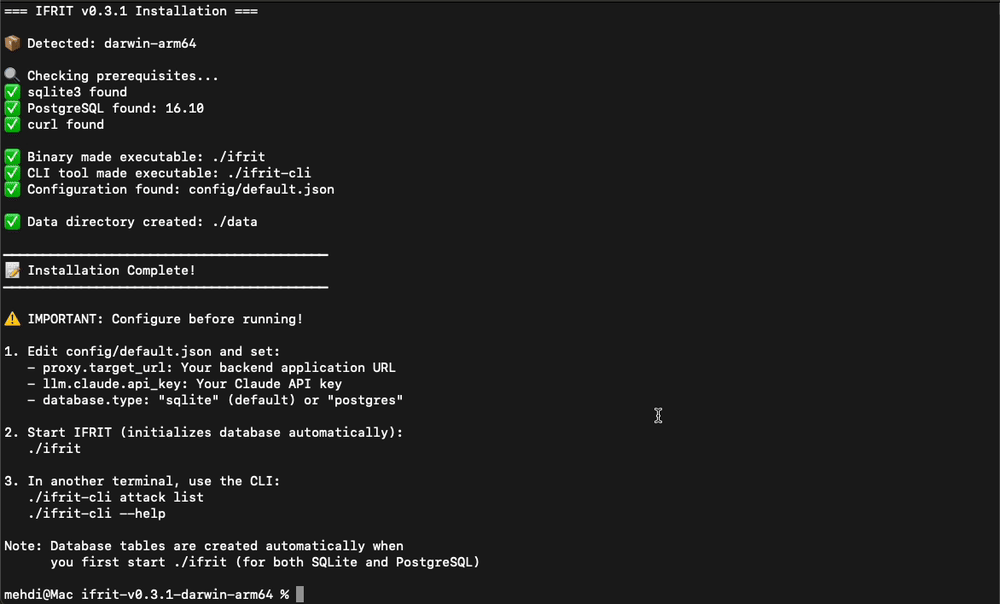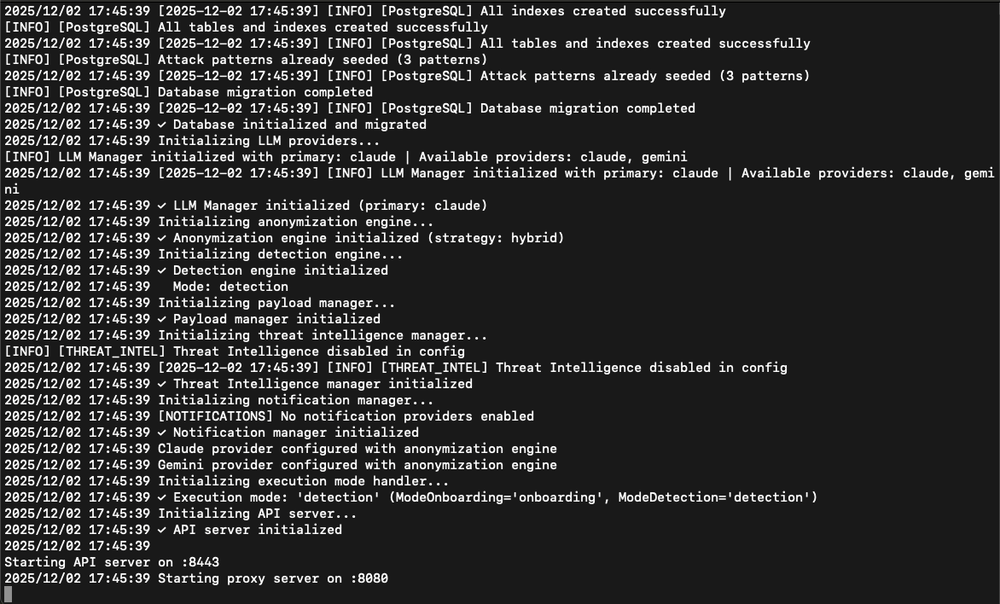
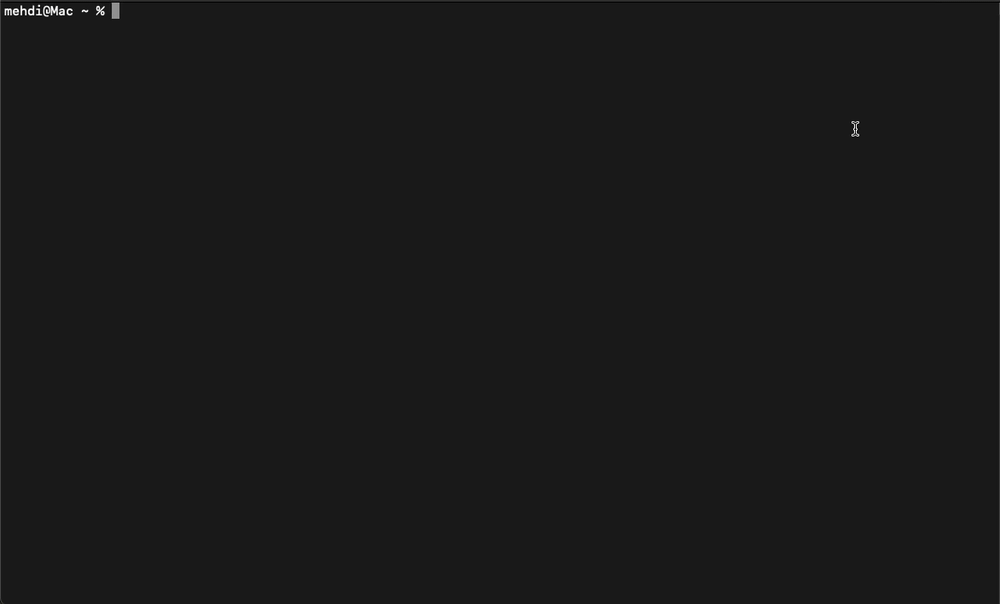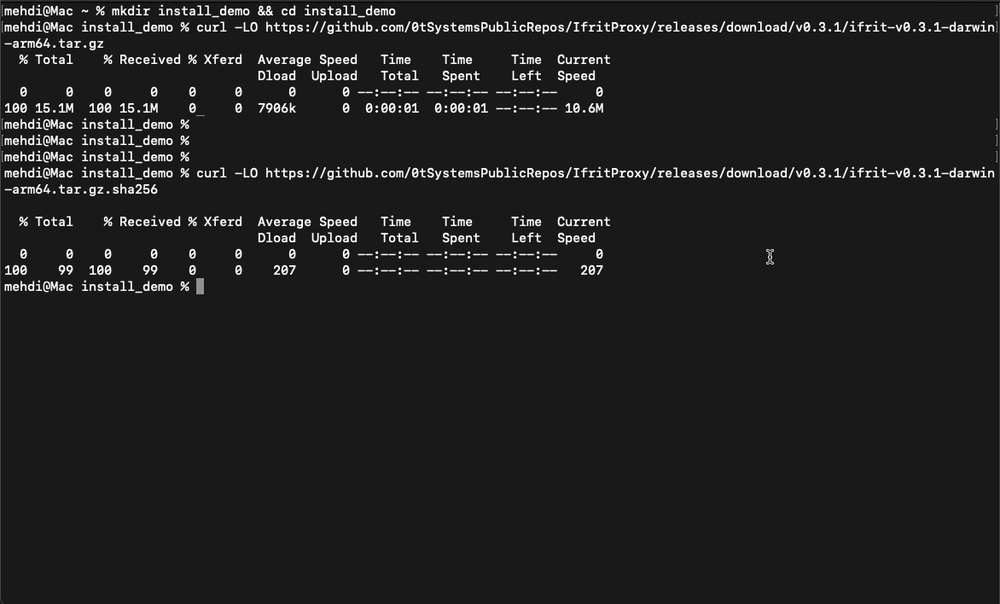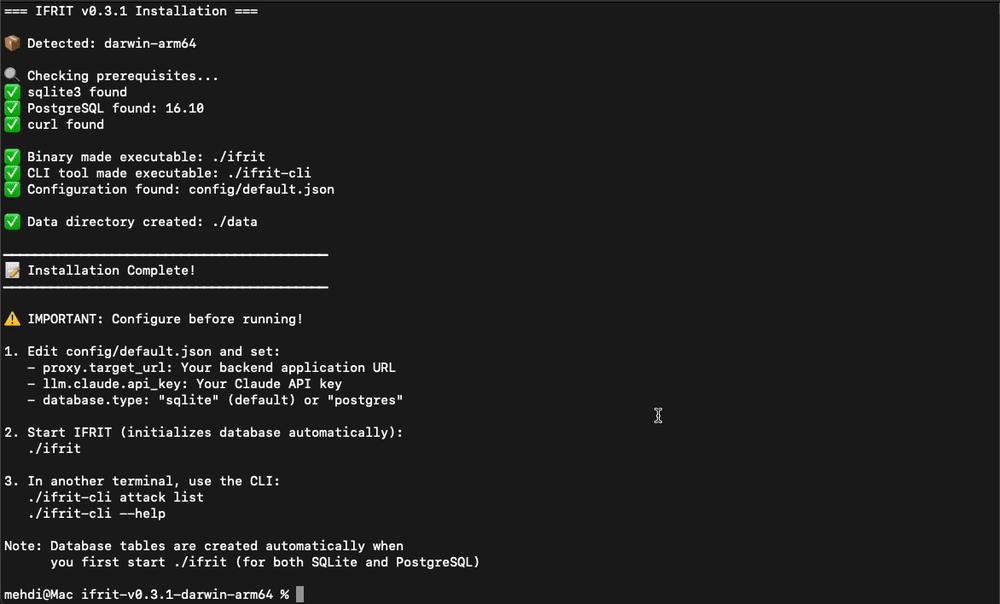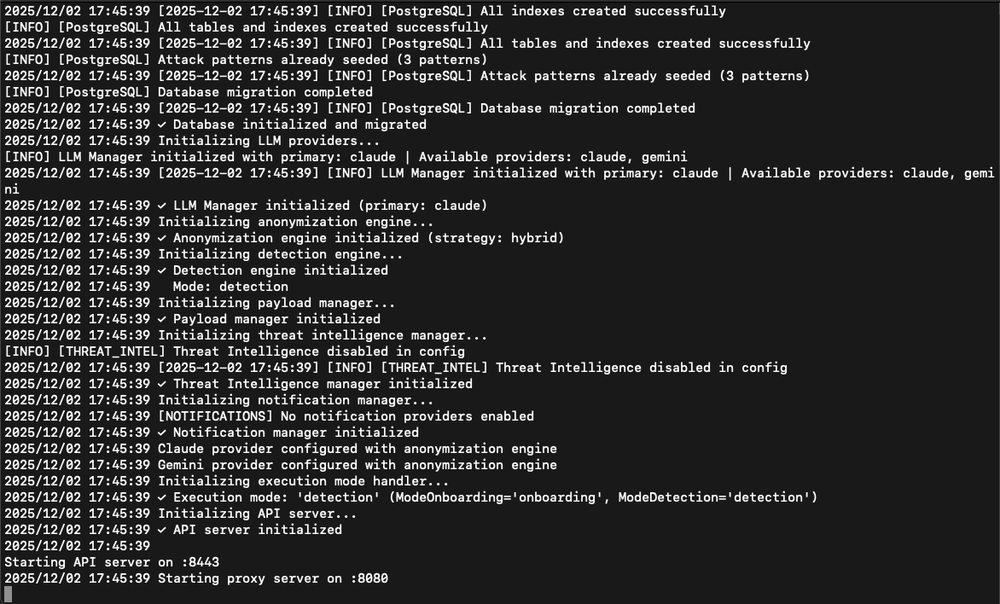
*安装演示 — 就是这么简单!*
</div>
### ⚙️ 配置(快速设置)```bash
# 1. Copy template
cp config/default.json.example config/default.json
# 2. Add your API keys
nano config/default.json # or use your favorite editor
开始的最小配置:```json { "llm": { "provider": "claude", // 👈 Choose: "claude" or "gemini" "claude": { "api_key": "sk-ant-..." // 🔑 Get from console.anthropic.com } }, "proxy": { "listen_port": 8080, "backend_url": "http://localhost:3000" // 🎯 Your app } }
### 🎬 启动

构建源代码或从可用的二进制文件安装```bash
# Build the binary
go build -o ifrit ./cmd/ifrit
(optional: build ifrit-cli as well)

# Start IFRIT (runs in background)
./ifrit &

# 🎉 You're protected! Access dashboard:
open http://localhost:8443
就这样! IFRIT 现在正在保护您的应用程序。
🧠 多 AI 智能选择您的 AI 提供商,或让 IFRIT 自动回退:
|
||
🎭 自适应欺骗引擎智能蜜罐响应,不断学习:
示例: SQL注入获得假用户数据库,路径遍历获得假文件列表。 |
🔍 威胁情报中心来自多个来源的实时增强信息:
|
📊 完全可见性指尖上的实时情报:
Query your intelligence./ifrit-cli threat top 10 ./ifrit-cli attacker view 45.67.89.1 ./ifrit-cli attack stats --last-24h |