
tlsx v1.3.0
快速且可配置的TLS抓取器,专注于基于TLS的数据收集。


功能 • 安装 • 用法 • 运行tlsx • 加入Discord
一个快速且可配置的TLS抓取工具,专注于基于TLS的数据收集与分析。
功能
- 快速且完全可配置的TLS连接
- 多种TLS连接模式
- 多种TLS探针
- 自动TLS回退以支持旧版TLS
- 预握手TLS连接(提前终止)
- 可自定义的加密套件/SNI/TLS选择
- JARM/JA3 TLS指纹
- TLS错误配置
- ASN、CIDR、IP、HOST和URL输入
- 标准输入/输出和TXT/JSON输出
安装
tlsx 需要 Go 1.24 才能成功安装。要安装,只需运行以下命令或从发布页面下载预编译的二进制文件。```console go install github.com/projectdiscovery/tlsx/cmd/tlsx@latest
## 使用方法```console
tlsx -h
这将显示工具的帮助信息。以下是它支持的所有选项开关。```console TLSX is a tls data gathering and analysis toolkit.
Usage: tlsx [flags]
Flags: INPUT: -u, -host string[] target host to scan (-u INPUT1,INPUT2) -l, -list string target list to scan (-l INPUT_FILE) -p, -port string[] target port to connect (default 443)
SCAN-MODE: -sm, -scan-mode string tls connection mode to use (ctls, ztls, openssl, auto) (default "auto") -ps, -pre-handshake enable pre-handshake tls connection (early termination) using ztls -sa, -scan-all-ips scan all ips for a host (default false) -iv, -ip-version string[] ip version to use (4, 6) (default 4)
PROBES: -san display subject alternative names -cn display subject common names -so display subject organization name -tv, -tls-version display used tls version -cipher display used cipher -hash string display certificate fingerprint hashes (md5,sha1,sha256) -jarm display jarm fingerprint hash -ja3 display ja3 fingerprint hash (using ztls) -wc, -wildcard-cert display host with wildcard ssl certificate -tps, -probe-status display tls probe status -ve, -version-enum enumerate and display supported tls versions -ce, -cipher-enum enumerate and display supported cipher -ct, -cipher-type value ciphers types to enumerate. possible values: all/secure/insecure/weak (comma-separated) (default all) -ch, -client-hello include client hello in json output (ztls mode only) -sh, -server-hello include server hello in json output (ztls mode only) -se, -serial display certificate serial number
MISCONFIGURATIONS: -ex, -expired display host with host expired certificate -ss, -self-signed display host with self-signed certificate -mm, -mismatched display host with mismatched certificate -re, -revoked display host with revoked certificate -un, -untrusted display host with untrusted certificate
CONFIGURATIONS: -config string path to the tlsx configuration file -r, -resolvers string[] list of resolvers to use -cc, -cacert string client certificate authority file -ci, -cipher-input string[] ciphers to use with tls connection -sni string[] tls sni hostname to use -rs, -random-sni use random sni when empty -rps, -rev-ptr-sni perform reverse PTR to retrieve SNI from IP -min-version string minimum tls version to accept (ssl30,tls10,tls11,tls12,tls13) -max-version string maximum tls version to accept (ssl30,tls10,tls11,tls12,tls13) -cert, -certificate include certificates in json output (PEM format) -tc, -tls-chain include certificates chain in json output -vc, -verify-cert enable verification of server certificate -ob, -openssl-binary string OpenSSL Binary Path -hf, -hardfail strategy to use if encountered errors while checking revocation status -proxy string socks5 proxy to use for tlsx
OPTIMIZATIONS: -c, -concurrency int number of concurrent threads to process (default 300) -cec, -cipher-concurrency int cipher enum concurrency for each target (default 10) -timeout int tls connection timeout in seconds (default 5) -retry int number of retries to perform for failures (default 3) -delay string duration to wait between each connection per thread (eg: 200ms, 1s)
UPDATE: -up, -update update tlsx to latest version -duc, -disable-update-check disable automatic tlsx update check
OUTPUT: -o, -output string file to write output to -j, -json display output in jsonline format -dns display unique hostname from SSL certificate response -ro, -resp-only display tls response only -silent display silent output -nc, -no-color disable colors in cli output -v, -verbose display verbose output -version display project version
PDCP: -pd, -dashboard upload or view output in the PDCP UI dashboard -pdu, -dashboard-upload string upload tlsx output file (JSONL format) to the PDCP UI dashboard -auth string PDCP API key for authentication -tid, -team-id string upload asset results to a specified team ID -aid, -asset-id string upload new assets to an existing asset ID -aname, -asset-name string asset group name
DEBUG: -health-check, -hc run diagnostic check up
## 将tlsx作为库使用

将tlsx作为库使用的示例位于[examples](https://github.com/projectdiscovery/tlsx/blob/main/examples)文件夹中。

## 运行tlsx

### tlsx的输入

**tlsx**需要**ip**来建立TLS连接,并接受如下所列的多种格式:```bash
AS1449 # ASN input
173.0.84.0/24 # CIDR input
93.184.216.34 # IP input
example.com # DNS input
example.com:443 # DNS input with port
https://example.com:443 # URL input port
输入主机可以使用 -host / -u 标志提供,多个值可以使用逗号分隔输入,类似地,使用 -list / -l 标志支持文件输入。
逗号分隔主机输入示例:```console $ tlsx -u 93.184.216.34,example.com,example.com:443,https://example.com:443 -silent
基于文件的主机输入示例:```console
$ tlsx -list host_list.txt
端口输入:
tlsx 默认连接 443 端口,可以通过 -port / -p 标志自定义,可以指定单个或多个端口,使用逗号分隔输入或包含端口列表的换行符分隔文件。
逗号分隔端口输入示例:``` $ tlsx -u hackerone.com -p 443,8443
基于文件的端口输入示例:```
$ tlsx -u hackerone.com -p port_list.txt
注:
当输入主机包含端口时,例如
8.8.8.8:443或hackerone.com:8443,将使用主机指定的端口进行 TLS 连接,而不是使用默认端口或通过-port / -p标志提供的端口。
TLS Probe (default run)
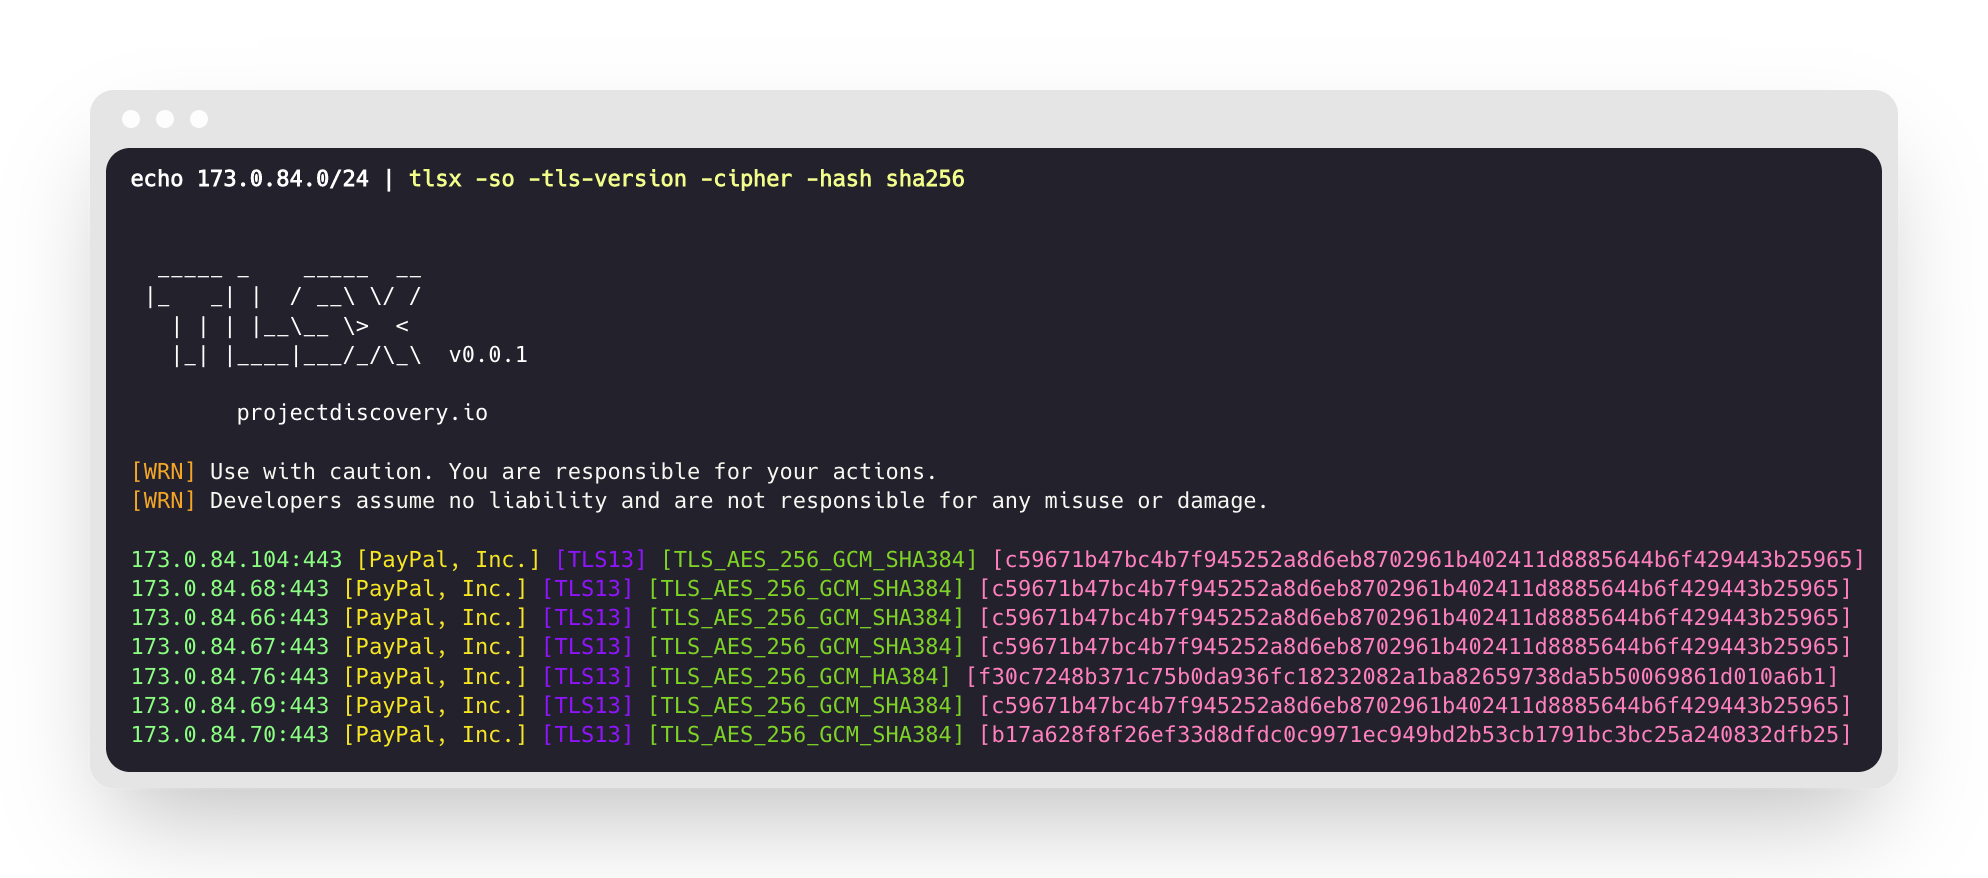
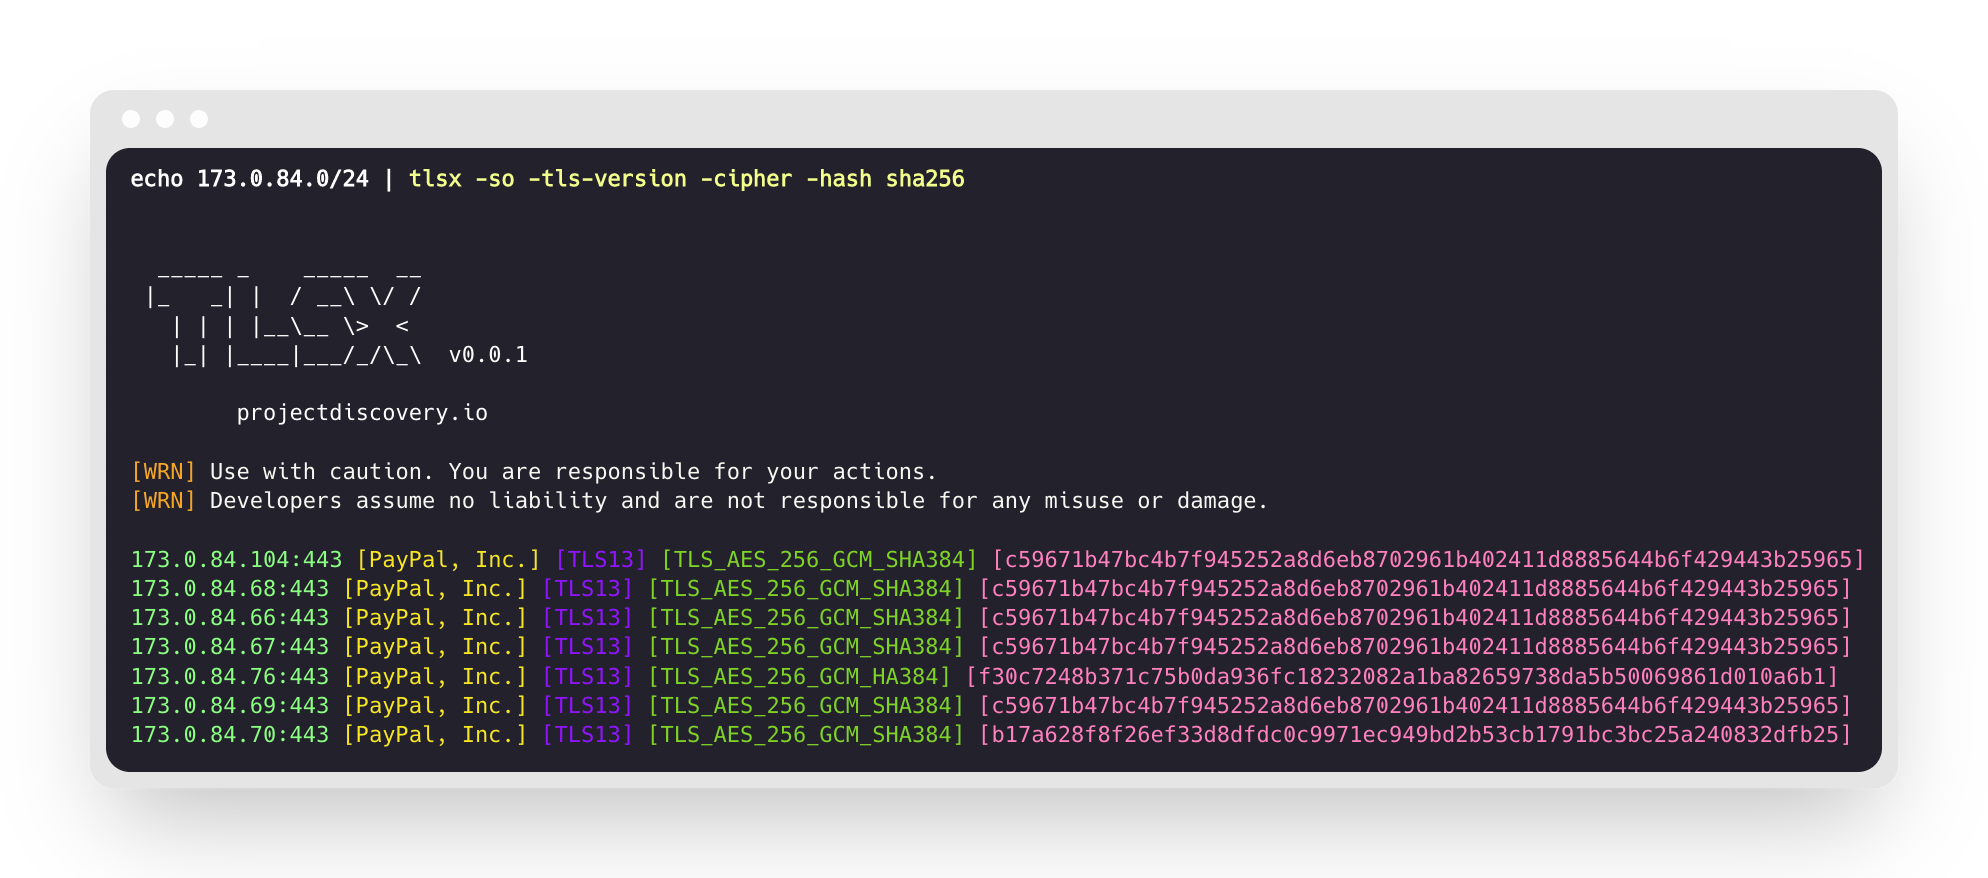
这将在给定的 CIDR 范围内运行工具,并返回在端口 443 上接受 tls 连接的主机。```console $ echo 173.0.84.0/24 | tlsx
|_ | | / \ / / | | | |_ > < || ||/_/_\ v0.0.1
projectdiscovery.io
[WRN] Use with caution. You are responsible for your actions. [WRN] Developers assume no liability and are not responsible for any misuse or damage.