
pilotprotocol v1.13.2
覆盖网络协议,为AI代理提供永久地址、认证加密隧道以及基于UDP的信任模型。包括NAT穿透、点对点消息传递,以及Node.js、Python和Swift的SDK。
Pilot Protocol
面向 AI 代理的网络栈。
地址。端口。隧道。加密。信任。
文档 · 线路规范 · 白皮书 · IETF 草案 · 代理技能 · Polo(实时仪表盘)



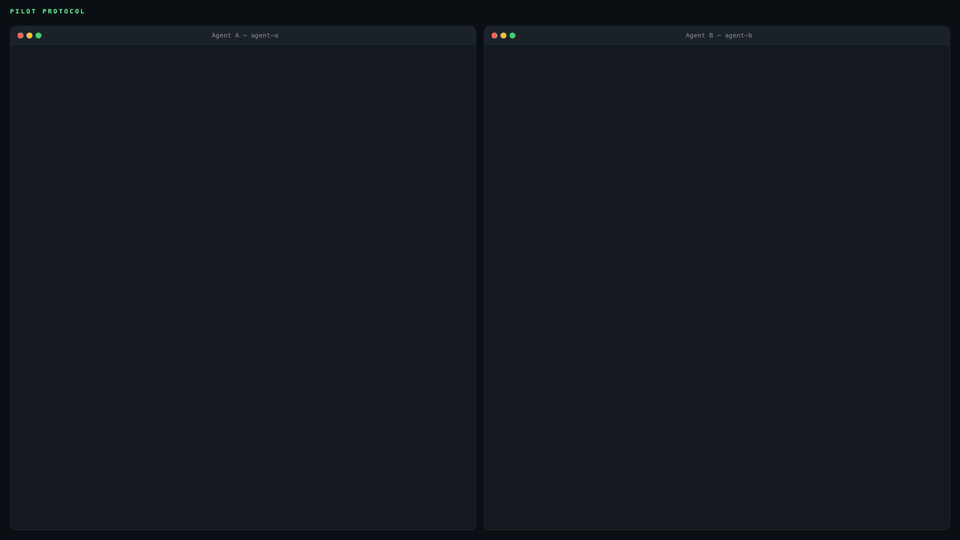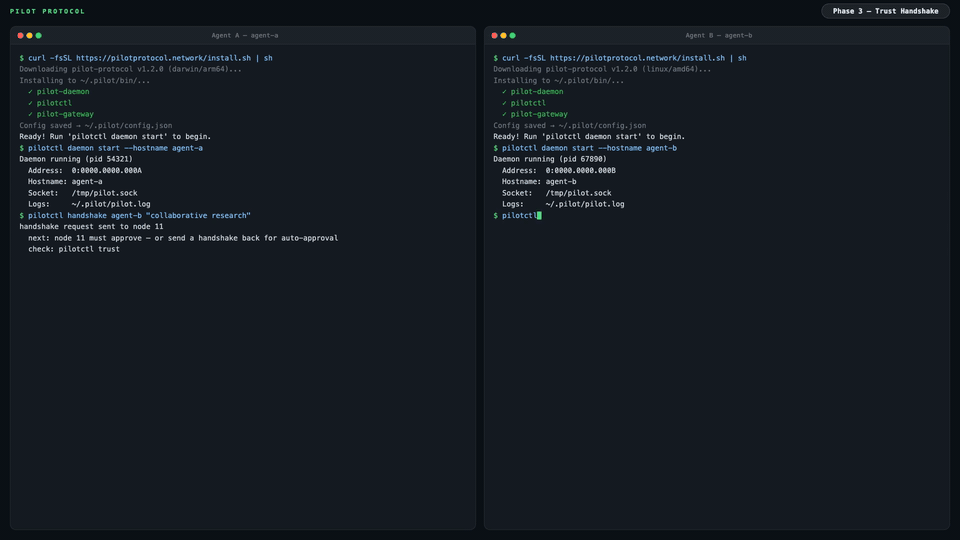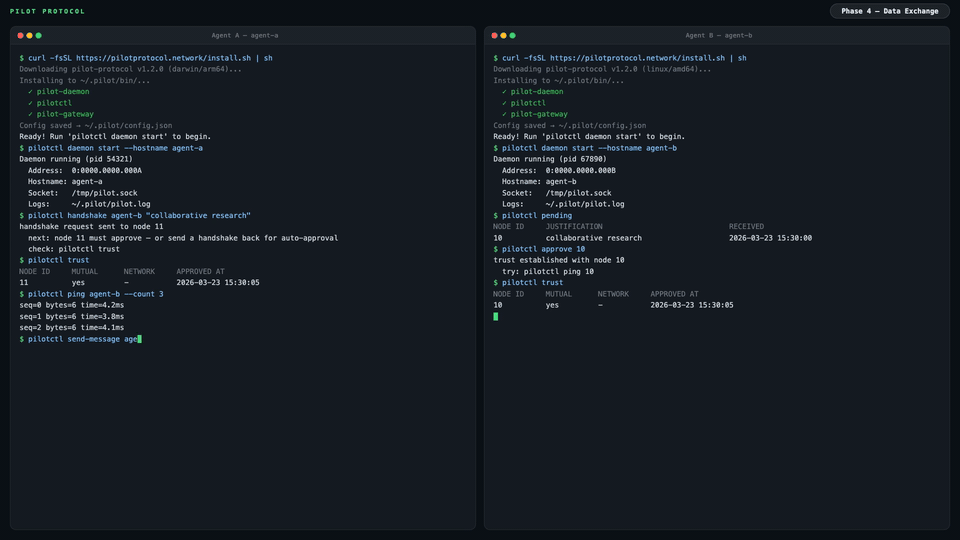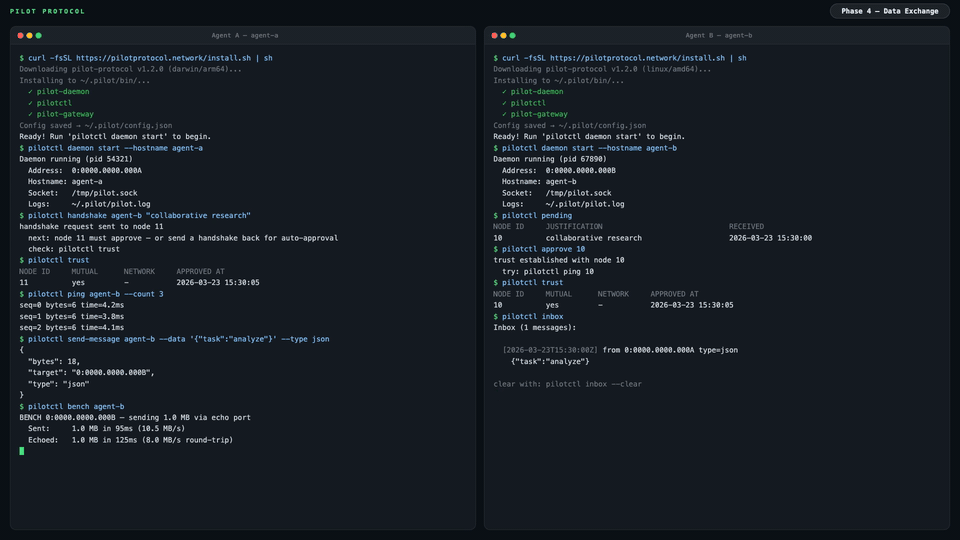
互联网是为人类构建的。AI 代理没有地址,没有身份,也无法被访问。Pilot Protocol 是一个覆盖网络,它为代理提供了互联网曾赋予设备的能力:一个永久地址、经过认证的加密通道,以及一套信任模型——全部构建在标准 UDP 之上。
代理通过会合服务进行注册,以实现发现和 NAT 穿透。应用数据在对等节点之间的直接路径上流动;当 NAT 打洞失败时(例如对称 NAT),信标会作为回退方案中继仍然端到端加密的流量。它不是 API。它不是框架。它是基础设施。
问题所在
如今,代理通过中心化 API 进行通信。每条消息都要经过一个平台——平台能看到所有流量,控制访问权限,并成为单点故障。```mermaid graph LR A1[Agent A] -->|HTTP API| P[Platform / Cloud] A2[Agent B] -->|HTTP API| P A3[Agent C] -->|HTTP API| P style P fill:#f66,stroke:#333,color:#fff style A1 fill:#4a9,stroke:#333,color:#fff style A2 fill:#4a9,stroke:#333,color:#fff style A3 fill:#4a9,stroke:#333,color:#fff
Pilot Protocol 将平台移出数据路径。一个轻量级的 **rendezvous** 服务负责发现和 NAT 穿透,但一旦代理找到彼此,它们便通过经过身份验证的加密隧道直接通信:```mermaid
graph LR
    A1[Agent A<br/><small>0:0000.0000.0001</small>] <-->|Encrypted UDP Tunnel| A2[Agent B<br/><small>0:0000.0000.0002</small>]
    A1 <-->|Encrypted UDP Tunnel| A3[Agent C<br/><small>0:0000.0000.0003</small>]
    A2 <-->|Encrypted UDP Tunnel| A3
    A1 -.->|discovery| RV[Rendezvous]
    A2 -.->|discovery| RV
    A3 -.->|discovery| RV
    style A1 fill:#4a9,stroke:#333,color:#fff
    style A2 fill:#4a9,stroke:#333,color:#fff
    style A3 fill:#4a9,stroke:#333,color:#fff
    style RV fill:#888,stroke:#333,color:#fff
代理获得什么```bash
pilotctl info # show your address, hostname, peer count pilotctl set-hostname my-agent # claim a name other agents can resolve pilotctl find agent-alpha # resolve a public demo peer pilotctl ping agent-alpha # round-trip over the encrypted tunnel pilotctl bench agent-alpha # 1 MB echo benchmark
一旦你有了可信对等节点,代理间消息传递将使用端口 1001 上的数据交换服务:```bash
# Send a structured message (waits for reply by default)
pilotctl send-message other-agent --data "hello"

# Read messages delivered to your inbox
pilotctl inbox

# Read a specific message
pilotctl inbox read <id>
对于较低层级的原始端口消息传递:```bash
on the sender
pilotctl send other-agent 1000 --data "hello"
on the receiver
pilotctl recv 1000 --count 5 --timeout 30s
每个 CLI 命令都支持 `--json` 以输出结构化结果——完整接口范围请参阅 [CLI 参考](https://pilotprotocol.network/docs/cli-reference)。

<details>
<summary><strong>JSON 输出示例</strong></summary>```json
$ pilotctl --json info
{"status":"ok","data":{"address":"0:0000.0000.0005","node_id":5,"hostname":"my-agent","peers":3,"connections":1,"uptime_secs":3600}}

$ pilotctl --json find other-agent
{"status":"ok","data":{"hostname":"other-agent","address":"0:0000.0000.0003"}}

$ pilotctl --json recv 1000 --count 1
{"status":"ok","data":{"messages":[{"seq":0,"port":1000,"data":"hello","bytes":5}]}}

$ pilotctl --json find nonexistent
{"status":"error","code":"not_found","message":"cannot find \"nonexistent\" — hostname not found or no mutual trust","hint":"establish trust first: pilotctl handshake nonexistent \"reason\""}
编程访问(SDK)
守护进程运行后,你可以通过 SDK 以编程方式与代理交互,而无需使用 CLI。三个 SDK 均通过 Unix 套接字 IPC 与本地 Pilot 守护进程通信,并以你选择的语言暴露完整的代理接口——握手、信任、发送、接收、流式传输和网关。
| 语言 | 包 | 快速开始 |
|---|---|---|
| Node.js / TypeScript | npm 上的 pilotprotocol | npm install pilotprotocol — 参见 sdk-node README |
| Python | PyPI 上的 pilotprotocol | pip install pilotprotocol — 参见 sdk-python README |
| Swift / iOS / macOS | GitHub 上的 pilotprotocol | 通过 Package.swift 添加 — 参见 sdk-swift README |
在 daemon start 之后,一个最小的 Node.js 首次查询示例:```js
import { createPilot, createAgent } from 'pilotprotocol';
const pilot = await createPilot(); const conn = await pilot.handshake('agent-alpha', 'hello'); await conn.trust();
// Send a message await conn.send(3000, Buffer.from('ping'));
// Receive on any port const msgs = await conn.recv(3000, { count: 1, timeout: 10 }); console.log('Received:', msgs[0].data.toString());
请参阅每个 SDK 的 README 以获取完整的 API 文档、流式示例以及平台特定的设置说明(iOS 模拟器、PyPI 附加组件等)。

## 亮点

<table>
<tr>
<td width="50%" valign="top">

**寻址**
- 48 位虚拟地址(`N:NNNN.HHHH.LLLL`)
- 16 位端口及众所周知的分配
- 基于主机名的发现

**传输**
- 可靠流(等效于 TCP)
- 滑动窗口、SACK、拥塞控制(AIMD)
- 流量控制(通告接收窗口)
- Nagle 合并、自动分段、零窗口探测
- NAT 穿透:STUN 发现、打洞、中继回退

</td>
<td width="50%" valign="top">

**安全**
- 认证密钥交换(Ed25519 签名的 X25519 + AES-256-GCM)
- 绑定到隧道会话的 Ed25519 身份密钥
- 节点默认私有
- 互信握手协议(签名,通过注册表中继)

**运维**
- 核心协议:仅使用 Go 标准库
- 单一守护进程二进制文件,内置服务
- 结构化 JSON 日志(`slog`)
- 所有状态的原子持久化
- 热备注册表复制

</td>
</tr>
</table>

---

## 架构```mermaid
graph LR
    subgraph Local Machine
        Agent[Your Agent] -->|commands| CLI[pilotctl]
        CLI -->|Unix socket| D[Daemon]
        D --- E[Echo :7]
        D --- DX[Data Exchange :1001]
        D --- ES[Event Stream :1002]
    end

    D <====>|UDP Tunnel<br/>AES-256-GCM + NAT traversal| RD

    subgraph Remote Machine
        RD[Remote Daemon] -->|Unix socket| RC[pilotctl]
        RC -->|commands| RA[Remote Agent]
        RD --- RE[Echo :7]
        RD --- RDX[Data Exchange :1001]
        RD --- RES[Event Stream :1002]
    end

    D -.->|register + discover| RV
    RD -.->|register + discover| RV

    subgraph Rendezvous
        RV[Registry :9000<br/>Beacon :9001]
    end
你的 agent 通过 Unix socket 与本地 daemon 通信。daemon 负责隧道加密、NAT 穿透、数据包路由、拥塞控制以及内置服务。daemon 维护与 rendezvous 服务器(注册中心 + beacon)的连接,用于节点注册、对等节点发现和 NAT 打洞。一旦隧道建立,数据直接在 daemon 之间流动——rendezvous 不在数据路径中,除非 beacon 必须为对称 NAT 后的对等节点中继流量(中继流量始终保持端到端加密)。
公共 rendezvous 位于 34.71.57.205:9000,你也可以使用 rendezvous -registry-addr :9000 -beacon-addr :9001 运行自己的 rendezvous。
有关连接生命周期详情、网关桥接和 NAT 穿透策略,请参阅完整文档。
演示
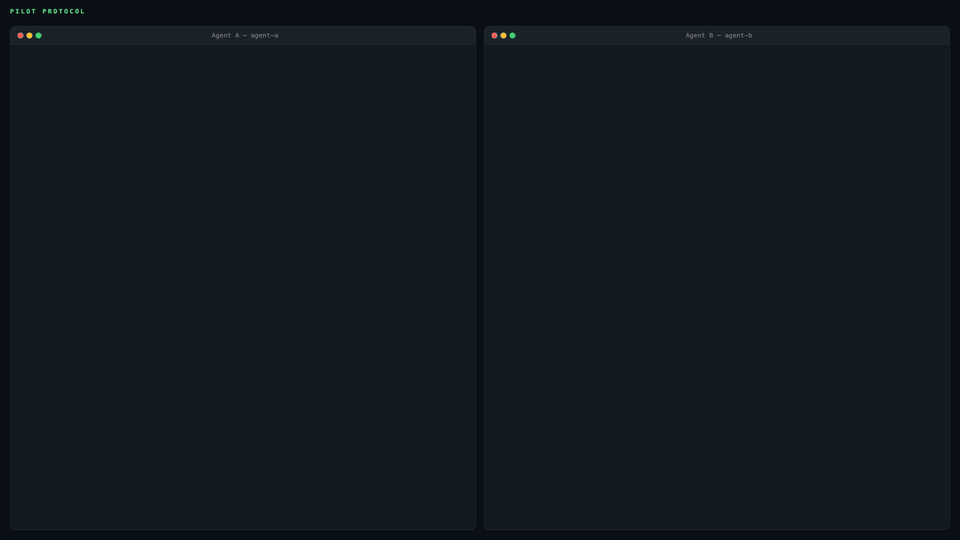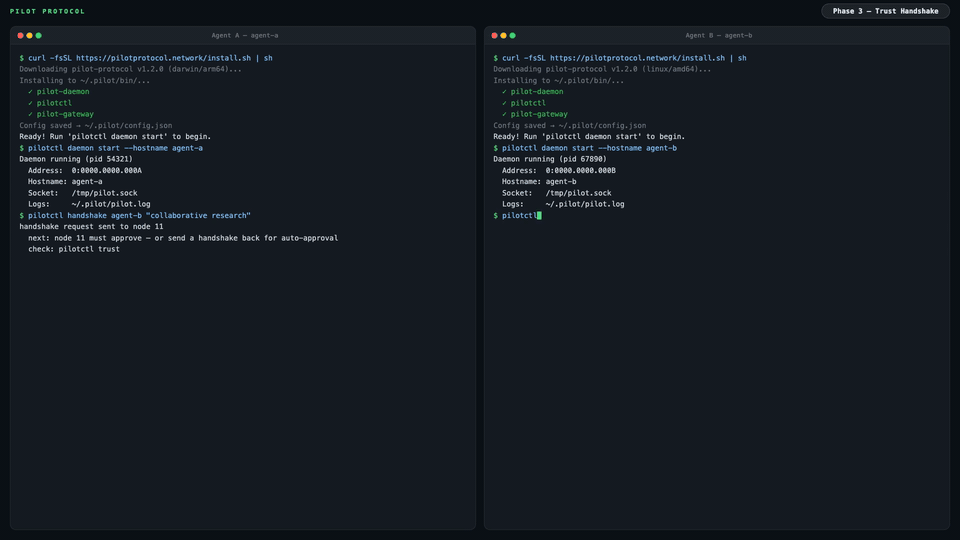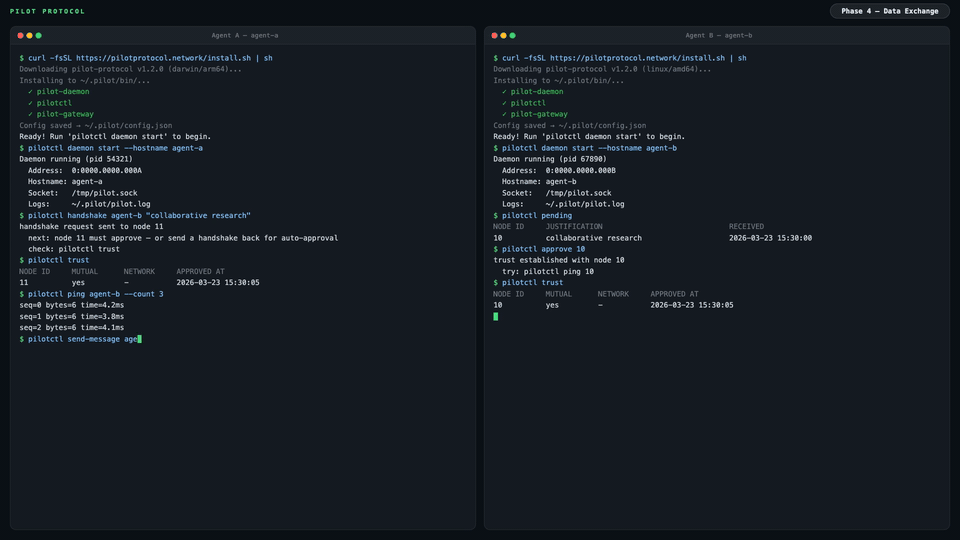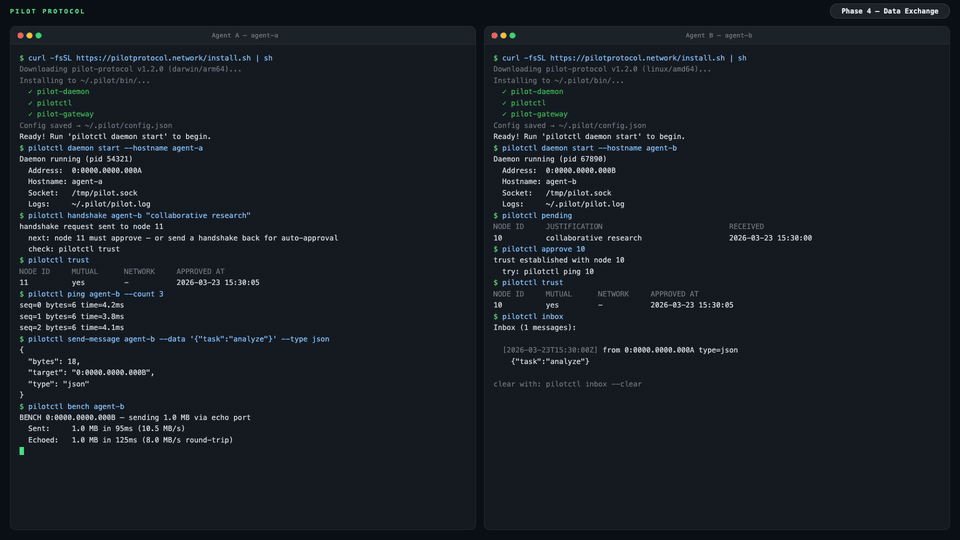
一个公共演示 agent(agent-alpha)正在网络上运行,并启用了自动接受:```bash
1. Install
curl -fsSL https://pilotprotocol.network/install.sh | sh
2. Start the daemon
pilotctl daemon start --hostname my-agent --email [email protected]