

noir v1.2.1
搜寻您代码中的每个端点,暴露影子API,映射攻击面
Hunt every Endpoint in your code, expose Shadow APIs, map the Attack Surface.


Documentation • Installation • Usage • GitHub Action • Contributing • Changelog
Noir is a SAST tool that reads source code and lists the endpoints an application exposes: paths, methods, parameters, headers, cookies, and the source files behind them. Shadow APIs, deprecated routes, and undocumented handlers are in the same inventory.
The inventory has three readers:
- Human reviewers start from attacker-reachable entry points instead of the whole repo.
- AI auditors get the same list plus per-endpoint review context (
--include callee,--ai-context). - DAST tools (ZAP, Burp Suite, Caido, Gori) get routes a crawler would never reach.
What Noir does
- Endpoint extraction. Static analysis across 264 frameworks.
- LLM fallback. OpenAI, Ollama, and other providers cover frameworks the static rules don't.
- Output formats. JSON, YAML, OpenAPI, SARIF, cURL, Postman, HTML, and more.
- DAST integration. Send endpoints to ZAP, Burp Suite, Caido, or Gori through a proxy, or export OpenAPI.
- AI review context.
--include calleeadds the functions each handler calls;--ai-contextadds guards, sources, sinks, validators, and signals. - CI/CD. GitHub Action, SARIF output, and exit codes.
Usage
brew install noir
noir scan <source_dir>
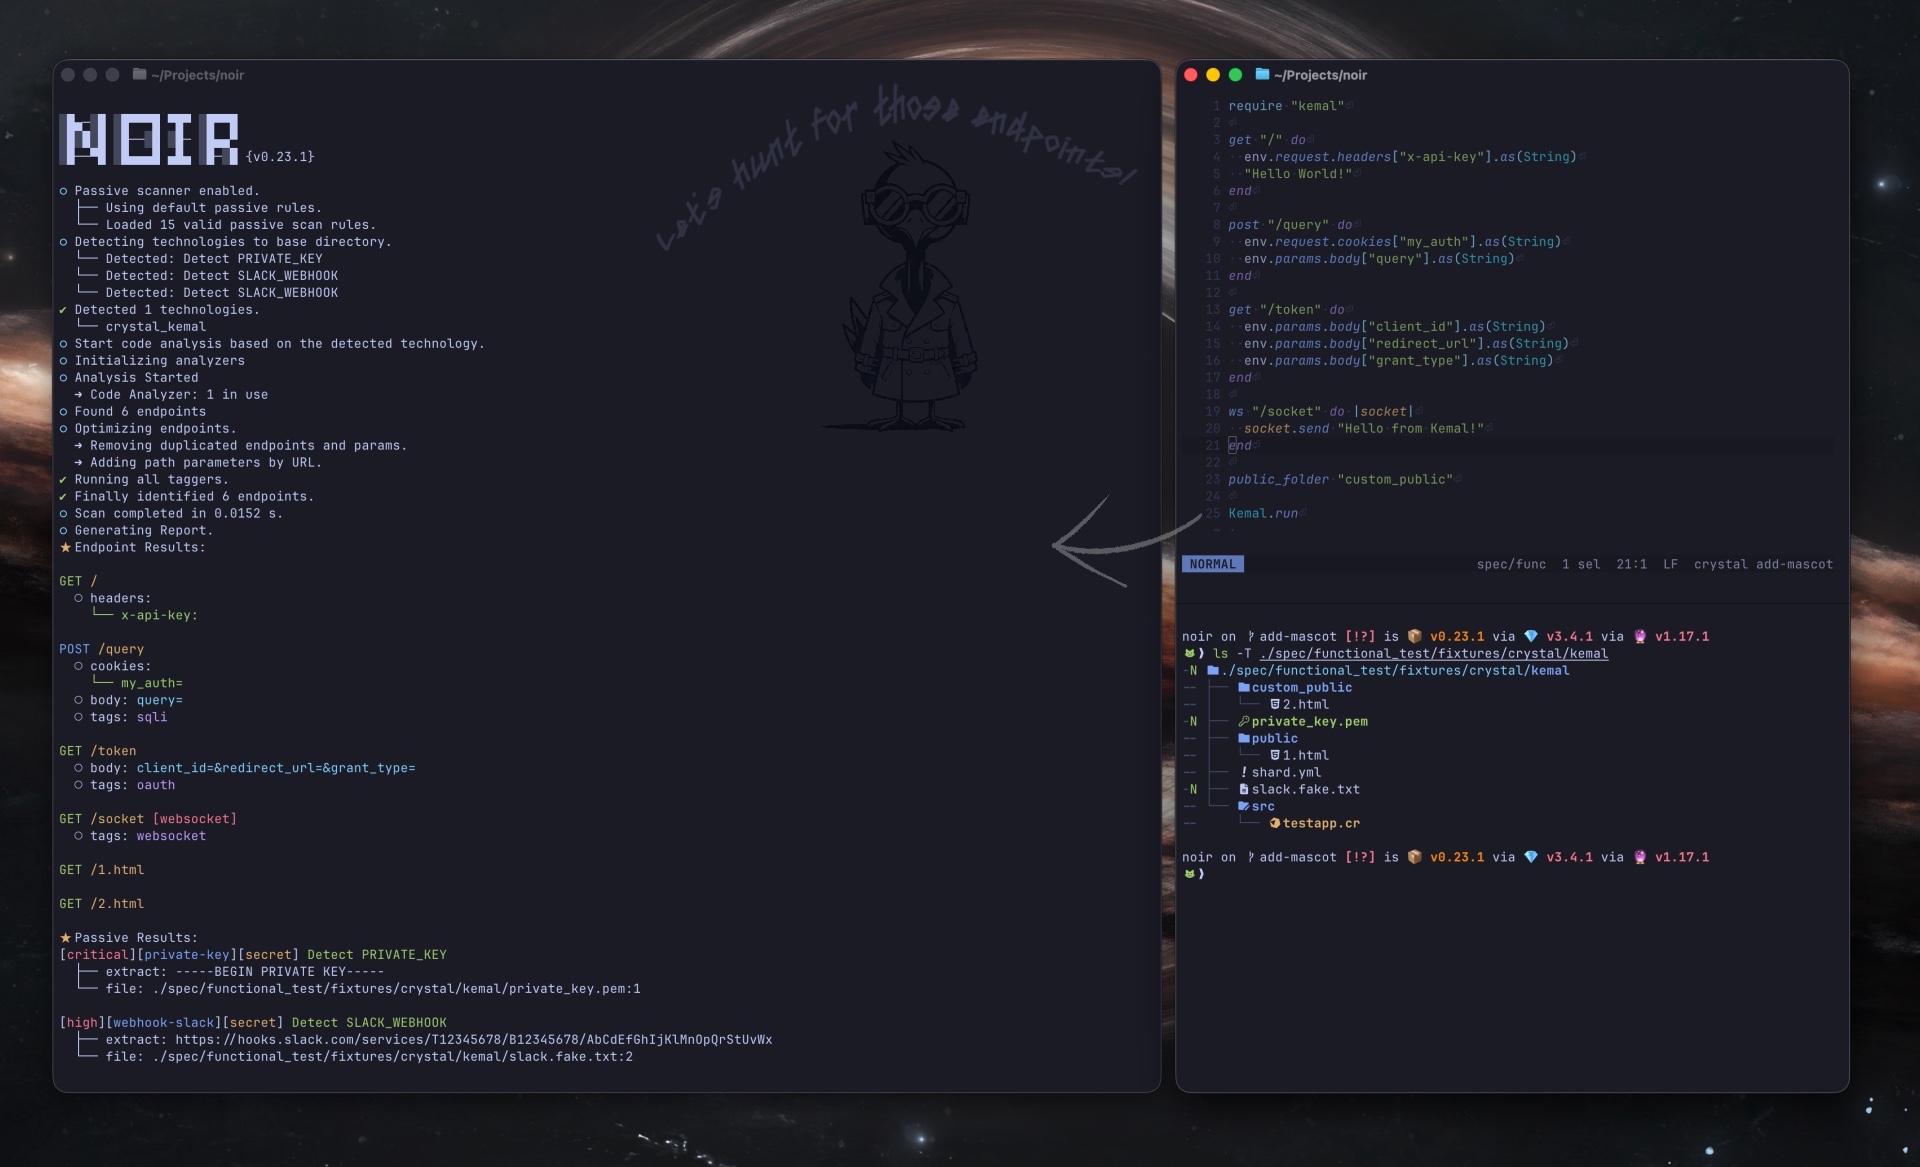
Other install methods (Snap, Docker, npm, Nix, packages) are on the Installation page. Run noir -h for every flag, or see the documentation and the GitHub Action page.
Roadmap
Noir started as a way to hand DAST tools the routes found in source code. The same inventory now serves human reviewers and AI auditors too, and the roadmap treats all three equally:
- Broaden language and framework coverage, with per-framework fixtures to check accuracy.
- Use LLMs where static analysis can't reach.
- Enrich the per-endpoint review context (guards, callees, sinks, validators, signals).
- Keep DAST integration first-class: OpenAPI, proxy targets, and hand-offs to ZAP, Burp Suite, Caido, and Gori.
OWASP Project
OWASP Noir joined the OWASP Foundation in June 2024.
- Official project page: https://owasp.org/projects/noir
- OWASP Nest: https://nest.owasp.org/projects/noir
News & Updates
- May 2026: Released v1.0.0, the stable 1.x line with a verb-based CLI.
- May 2026: Refreshed the roadmap to serve human reviewers, AI auditors, and DAST tools equally.
- August 2025: Presented at the OWASP Seoul Meetup. (Open Source Gardening)
- November 2024: Published a guest blog post "Powering Up DAST with ZAP and Noir" on the ZAP blog.
- June 2024: Joined OWASP as OWASP Noir
- Renamed the GitHub organization from noir-cr to owasp-noir
- Transitioned to co-leadership with @ksg97031
- November 2023: Moved the Noir repository to the noir-cr GitHub organization.
- August 2023: Started as @hahwul's personal project.
Core Team
Contributing
Noir is an open-source project made with ❤️. To contribute, see CONTRIBUTING.md and open a pull request.

Mascot
 | Hak (학) is the Noir mascot: a crane, which is what "학" means in Korean. More artwork is in the noir-artwork repository. |
|---|