

njsscan v1.0.1
面向Node.js应用的语义感知SAST扫描器,利用libsast模式匹配和semgrep语法感知分析,检测不安全代码模式。
njsscan
njsscan 是一款静态应用程序测试(SAST)工具,它使用来自 libsast 的简单模式匹配器以及语法感知的语义代码模式搜索工具 semgrep,在您的 node.js 应用程序中查找不安全的代码模式。
在印度用  制作


支持 njsscan
- 通过 Paypal 捐赠:

- 赞助本项目:

在线学习课程与认证
 OpSecX Node.js Security: Pentesting and Exploitation - NJS
安装
pip install njsscan
需要 Python 3.10+,仅支持 Mac 和 Linux
命令行选项
$ njsscan
usage: njsscan [-h] [--json] [--sarif] [--sonarqube] [--defectdojo] [--gitlab-sast] [--html] [-o OUTPUT] [-c CONFIG] [--missing-controls] [-w] [-v] [path ...]

positional arguments:
  path                  Path can be file(s) or directories with source code

optional arguments:
  -h, --help            show this help message and exit
  --json                set output format as JSON
  --sarif               set output format as SARIF 2.1.0
  --sonarqube           set output format compatible with SonarQube
  --defectdojo          set output format compatible with DefectDojo Generic Findings Import
  --gitlab-sast         set output format as GitLab SAST report
  --html                set output format as HTML
  -o OUTPUT, --output OUTPUT
                        output filename to save the result
  -c CONFIG, --config CONFIG
                        Location to .njsscan config file
  --missing-controls    enable missing security controls check
  -w, --exit-warning    non zero exit code on warning
  -v, --version         show njsscan version
使用示例
$ njsscan test.js
- Pattern Match ████████████████████████████████████████████████████████████ 1
- Semantic Grep ███████████████████████████ 160

njsscan: v0.1.9 | Ajin Abraham | opensecurity.in
╒═════════════╤═══════════════════════════════════════════════════════════════════════════════════════════════╕
│ RULE ID     │ express_xss                                                                                   │
├─────────────┼───────────────────────────────────────────────────────────────────────────────────────────────┤
│ OWASP       │ A1: Injection                                                                                 │
├─────────────┼───────────────────────────────────────────────────────────────────────────────────────────────┤
│ CWE         │ CWE-79: Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting')  │
├─────────────┼───────────────────────────────────────────────────────────────────────────────────────────────┤
│ DESCRIPTION │ Untrusted User Input in Response will result in Reflected Cross Site Scripting Vulnerability. │
├─────────────┼───────────────────────────────────────────────────────────────────────────────────────────────┤
│ SEVERITY    │ ERROR                                                                                         │
├─────────────┼───────────────────────────────────────────────────────────────────────────────────────────────┤
│ FILES       │ ╒════════════════╤═══════════════════════════════════════════════╕                            │
│             │ │ File           │ test.js                                       │                            │
│             │ ├────────────────┼───────────────────────────────────────────────┤                            │
│             │ │ Match Position │ 5 - 46                                        │                            │
│             │ ├────────────────┼───────────────────────────────────────────────┤                            │
│             │ │ Line Number(s) │ 7: 8                                          │                            │
│             │ ├────────────────┼───────────────────────────────────────────────┤                            │
│             │ │ Match String   │ const { name } = req.query;                   │                            │
│             │ │                │     res.send('<h1> Hello :' + name + "</h1>") │                            │
│             │ ╘════════════════╧═══════════════════════════════════════════════╛                            │
╘═════════════╧═══════════════════════════════════════════════════════════════════════════════════════════════╛
nodejsscan SAST
nodejsscan 构建于 njsscan 之上,提供了一套完整的漏洞管理用户界面以及其他实用的集成功能。
参见 nodejsscan
Python API
>>> from njsscan.njsscan import NJSScan
>>> node_source = '/node_source/true_positives/sqli_node.js'
>>> scanner = NJSScan([node_source], json=True, check_controls=False)
>>> scanner.scan()
{
    'templates': {},
    'nodejs': {
        'node_sqli_injection': {
            'files': [{
                'file_path': '/node_source/true_positives/sqli_node.js',
                'match_position': (1, 24),
                'match_lines': (4, 11),
                'match_string': 'var employeeId = req.foo;\n\nvar sql = "SELECT * FROM trn_employee WHERE employee_id = " + employeeId;\n\n\n\nconnection.query(sql, function (error, results, fields) {\n\n    if (error) {\n\n        throw error;\n\n    }\n\n    console.log(results);'
            }],
            'metadata': {
                'owasp': 'A1: Injection',
                'cwe': "CWE-89: Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection')",
                'description': 'Untrusted input concatinated with raw SQL query can result in SQL Injection.',
                'severity': 'ERROR'
            }
        }
    },
    'errors': []
}
配置 njsscan
源代码目录根部的 .njsscan 文件允许您配置 njsscan。您也可以使用 --config 参数指定自定义的 .njsscan 文件。
---
- nodejs-extensions:
  - .js

  template-extensions:
  - .new
  - .hbs
  - ''

  ignore-filenames:
  - skip.js

  ignore-paths:
  - __MACOSX
  - skip_dir
  - node_modules

  ignore-extensions:
  - .jsx

  ignore-rules:
  - regex_injection_dos
  - pug_jade_template

  severity-filter:
  - WARNING
  - ERROR

  severity-overrides:
    express_xss: WARNING
    node_secret: ERROR
抑制发现结果
您可以通过在触发发现结果的行上添加注释 // njsscan-ignore: rule_id1, rule_id2 来抑制 javascript 源文件中的发现结果。
示例:
app.get('/some/redirect', function (req, res) {
    var target = req.param("target");
    res.redirect(target); // njsscan-ignore: express_open_redirect
});
CI/CD 集成
您可以在 CI/CD 或 DevSecOps 流水线中启用 njsscan。
Github Action
将以下内容添加到文件 .github/workflows/njsscan.yml 中。
name: njsscan
on:
  push:
    branches: [ master, main ]
  pull_request:
    branches: [ master, main ]
jobs:
  njsscan:
    runs-on: ubuntu-latest
    name: njsscan check
    steps:
    - name: Checkout the code
      uses: actions/checkout@3d3c42e5aac5ba805825da76410c181273ba90b1 # v7.0.1
    - uses: actions/setup-python@5fda3b95a4ea91299a34e894583c3862153e4b97 # v7.0.0
      with:
        python-version: '3.12'
    - name: nodejsscan scan
      id: njsscan
      uses: ajinabraham/njsscan-action@231750a435d85095d33be7d192d52ec650625146 # v9
      with:
        args: '.'
示例:dvna with njsscan github action
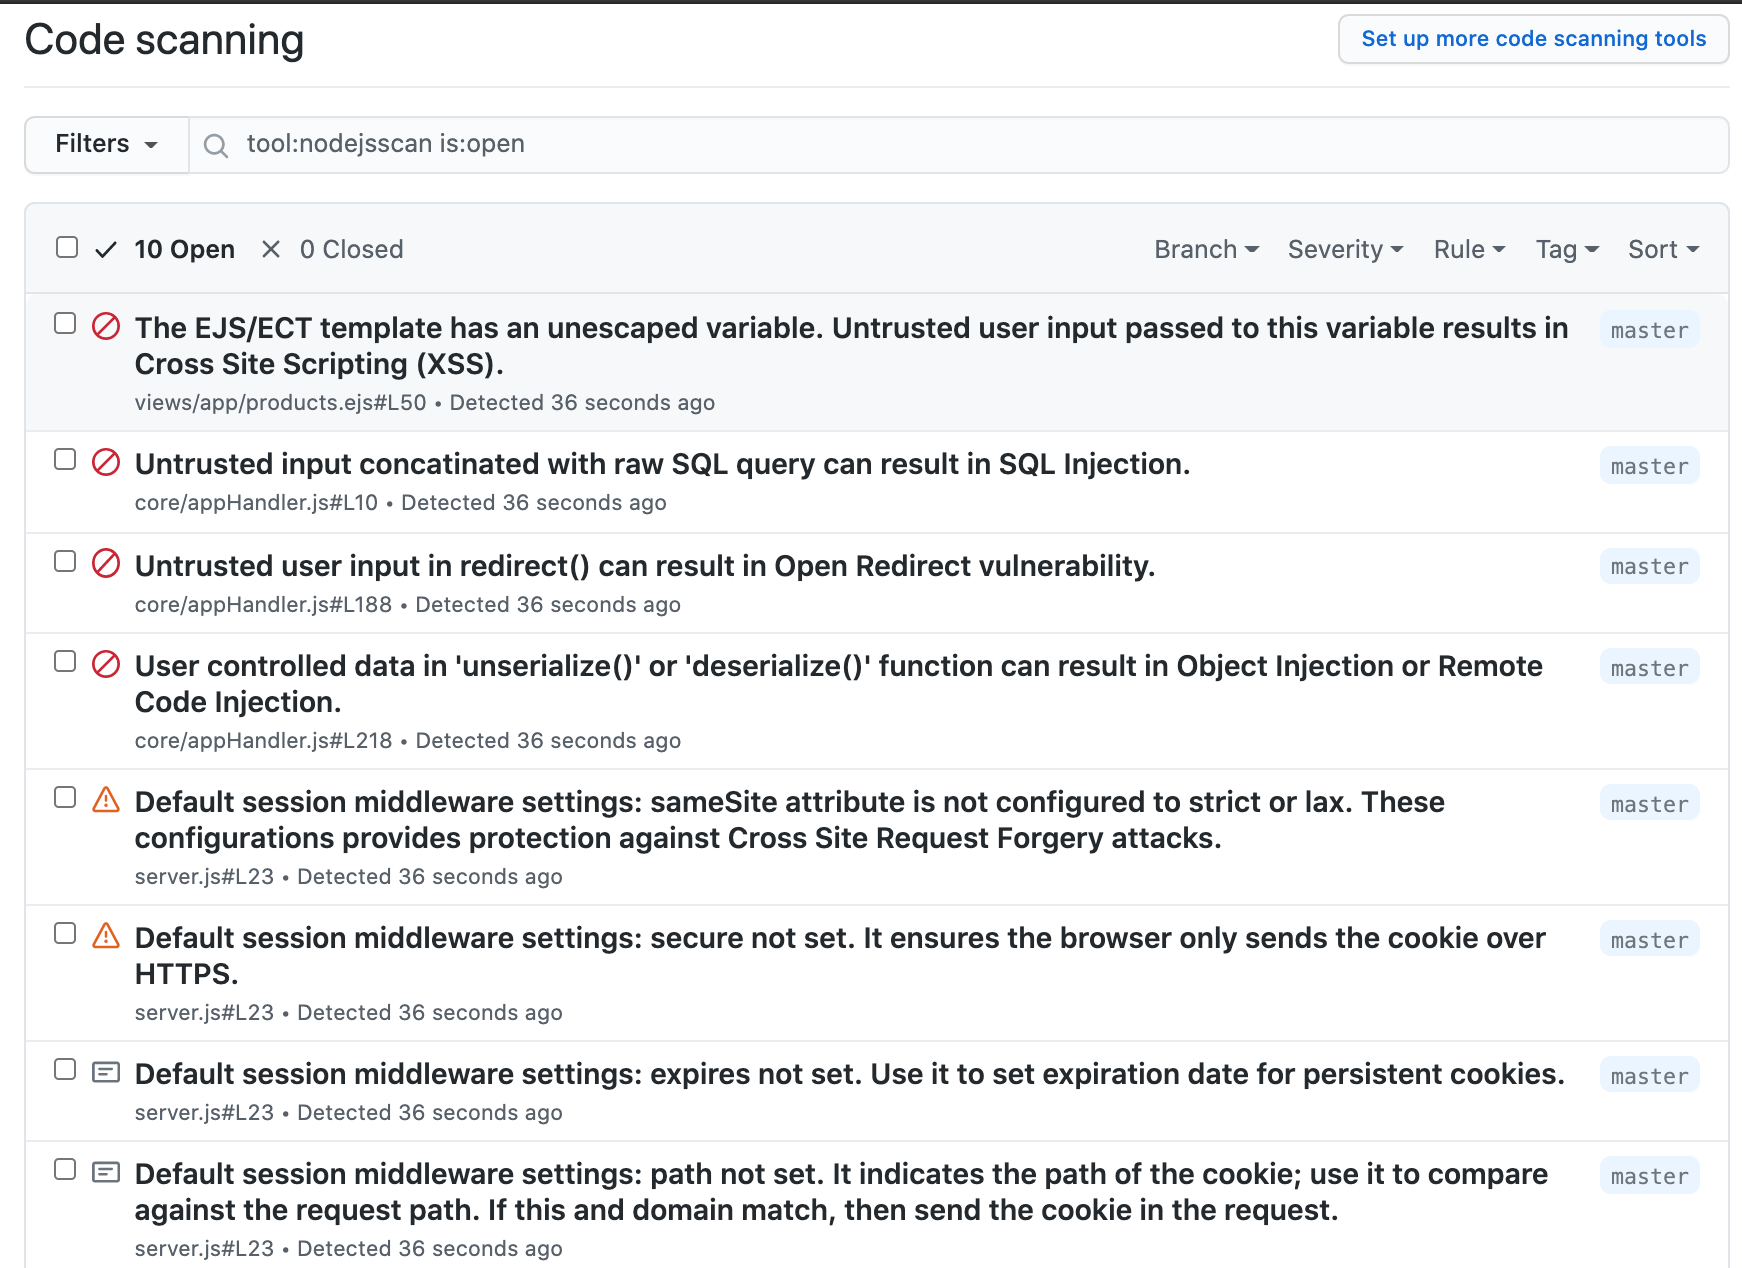
Github 代码扫描集成
将以下内容添加到文件 .github/workflows/njsscan_sarif.yml 中。
name: njsscan sarif
on:
  push:
    branches: [ master, main ]
  pull_request:
    branches: [ master, main ]
jobs:
  njsscan:
    runs-on: ubuntu-latest
    name: njsscan code scanning
    steps:
    - name: Checkout the code
      uses: actions/checkout@3d3c42e5aac5ba805825da76410c181273ba90b1 # v7.0.1
    - uses: actions/setup-python@5fda3b95a4ea91299a34e894583c3862153e4b97 # v7.0.0
      with:
        python-version: '3.12'
    - name: nodejsscan scan
      id: njsscan
      uses: ajinabraham/njsscan-action@231750a435d85095d33be7d192d52ec650625146 # v9
      with:
        args: '. --sarif --output results.sarif || true'
    - name: Upload njsscan report
      uses: github/codeql-action/upload-sarif@1c5b675653bb5c22dbe9b12b556ec555138e09fd # v4.38.1
      with:
        sarif_file: results.sarif
Gitlab CI/CD
将以下内容添加到文件 .gitlab-ci.yml 中。
stages:
  - test

njsscan:
  image: python:3.12
  stage: test
  before_script:
    - pip3 install --upgrade njsscan
  script:
    - njsscan . --gitlab-sast -o gl-sast-report.json
  artifacts:
    when: always
    reports:
      sast: gl-sast-report.json
示例命令(本地):
njsscan . --gitlab-sast -o gl-sast-report.json
这会生成原生的 GitLab SAST 报告,使发现结果无需 SARIF 转换器即可显示在漏洞报告 / MR 安全小组件中。
Travis CI
将以下内容添加到文件 .travis.yml 中。
language: python
install:
    - pip3 install --upgrade njsscan
script:
    - njsscan .
Circle CI
将以下内容添加到文件 .circleci/config.yaml 中
version: 2.1
jobs:
  njsscan:
    docker:
      - image: cimg/python:3.9.6
    steps:
      - checkout
      - run:
          name: Install njsscan
          command: pip install --upgrade njsscan
      - run:
           name: njsscan check
           command: njsscan .
Docker
来自 DockerHub 的预构建镜像
docker pull opensecurity/njsscan
docker run -v /path-to-source-dir:/src opensecurity/njsscan /src
本地构建
docker build -t njsscan .
docker run -v /path-to-source-dir:/src njsscan /src