


Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
分类

红队

对手模拟、红队基础设施、C2 框架和操作安全工具。

Kitploit 推荐

精选工具

10 已选择
sliver preview#1

sliver

GitHubbishopfox/sliver
11.7k3天前
metasploit-framework preview#2

metasploit-framework

GitHubrapid7/metasploit-framework
38.8k16小时53分前
Empire preview#3

Empire

GitHubbc-security/empire
5.2k1天前
Mythic preview#4

Mythic

GitHubits-a-feature/mythic
4.7k1个月前
NetExec preview#7

NetExec

GitHubpennyw0rth/netexec
5.8k2天前
impacket preview#8

impacket

GitHubfortra/impacket
16.0k1天前
BloodHound-Legacy preview#9

BloodHound-Legacy

GitHubspecterops/bloodhound-legacy
10.6k8个月前
mimikatz preview#10

mimikatz

GitHubgentilkiwi/mimikatz
21.8k21天前
Rubeus preview#11

Rubeus

GitHubghostpack/rubeus
5.1k1年前
PEASS-ng preview#12

PEASS-ng

GitHubpeass-ng/peass-ng
20.3k3天前
最新相关性最受欢迎最近更新
5516 结果
EDR-Redir preview

EDR-Redir

GitHubtwosevenonet/edr-redir

使用绑定筛选器(bindflt.sys)重定向 EDR 工作文件夹,从而绕过端点检测、破坏 EDR 服务,或将其替换为攻击者控制的目录,以支持红队行动。

defensive-toolsprivilege-escalationpersistence-mechanisms+5
2386个月前
Fiber preview

Fiber

GitHubkudaes/fiber

基于Rust的PoC,利用Windows纤程隐蔽地执行内存代码,通过在不触发内核回调的情况下切换控制纤程和有效载荷纤程,隐藏有效载荷堆栈以避开EDR检测。

post-exploitationred-teamingpayload-development
2453年前
LsassReflectDumping preview

LsassReflectDumping

GitHuboffensive-panda/lsassreflectdumping

该工具利用进程分叉技术,通过 RtlCreateProcessReflection API 克隆 lsass.exe 进程。创建克隆后,它使用 MINIDUMP_CALLBACK_INFORMATION 回调来生成克隆进程的内存转储。

memory-forensicspassword-attackspost-exploitation+1
2202年前
CVE-2018-13382 preview

CVE-2018-13382

GitHubmilo2012/cve-2018-13382

CVE-2018-13382

vulnerability-analysisexploitationweb-application-exploitation+3
1467年前
RandomTSScripts preview

RandomTSScripts

GitHubxpn/randomtsscripts

红队交战脚本集合,包括通过 TGS 进行 Pre2K 默认凭据检查、LAPSv2 密码解密以及 IIS 应用程序池凭据解密。

password-attacksexploitationscripting-automation+4
2132年前
DuplicateDump preview

DuplicateDump

GitHubhagrid29/duplicatedump

使用自定义LSA插件中的重复句柄转储LSASS

privilege-escalationpost-exploitationred-teaming
2074年前
CVE-2024-43044-jenkins preview

CVE-2024-43044-jenkins

GitHubconvisolabs/cve-2024-43044-jenkins

针对 Jenkins 中漏洞 CVE-2024-43044 的利用工具

vulnerability-analysisexploitationweb-application-exploitation+3
1862年前
WEBFANG preview

WEBFANG

GitHubtalyx66/webfang

WEBFANG,我的第一款命令行工具,是一个模块化的 OSINT 与侦察工具包,专为道德黑客和红队人员打造。利用被动情报收集、主动爬虫、DNS/WHOIS 查询以及 Shodan,将毒牙刺入 Web 目标——所有功能集成在一个轻量级包中。选择你的武器,狩猎愉快。

osintreconnaissanceinformation-gathering+6
1172个月前
HSC24RedTeamInfra preview

HSC24RedTeamInfra

GitHubdazzyddos/hsc24redteaminfra

用于红队基础设施自动化研讨会的幻灯片和代码
cloud-infrastructure-securityeducationred-teaming
1932年前
pwnflow preview

pwnflow

GitHubrb-x/pwnflow

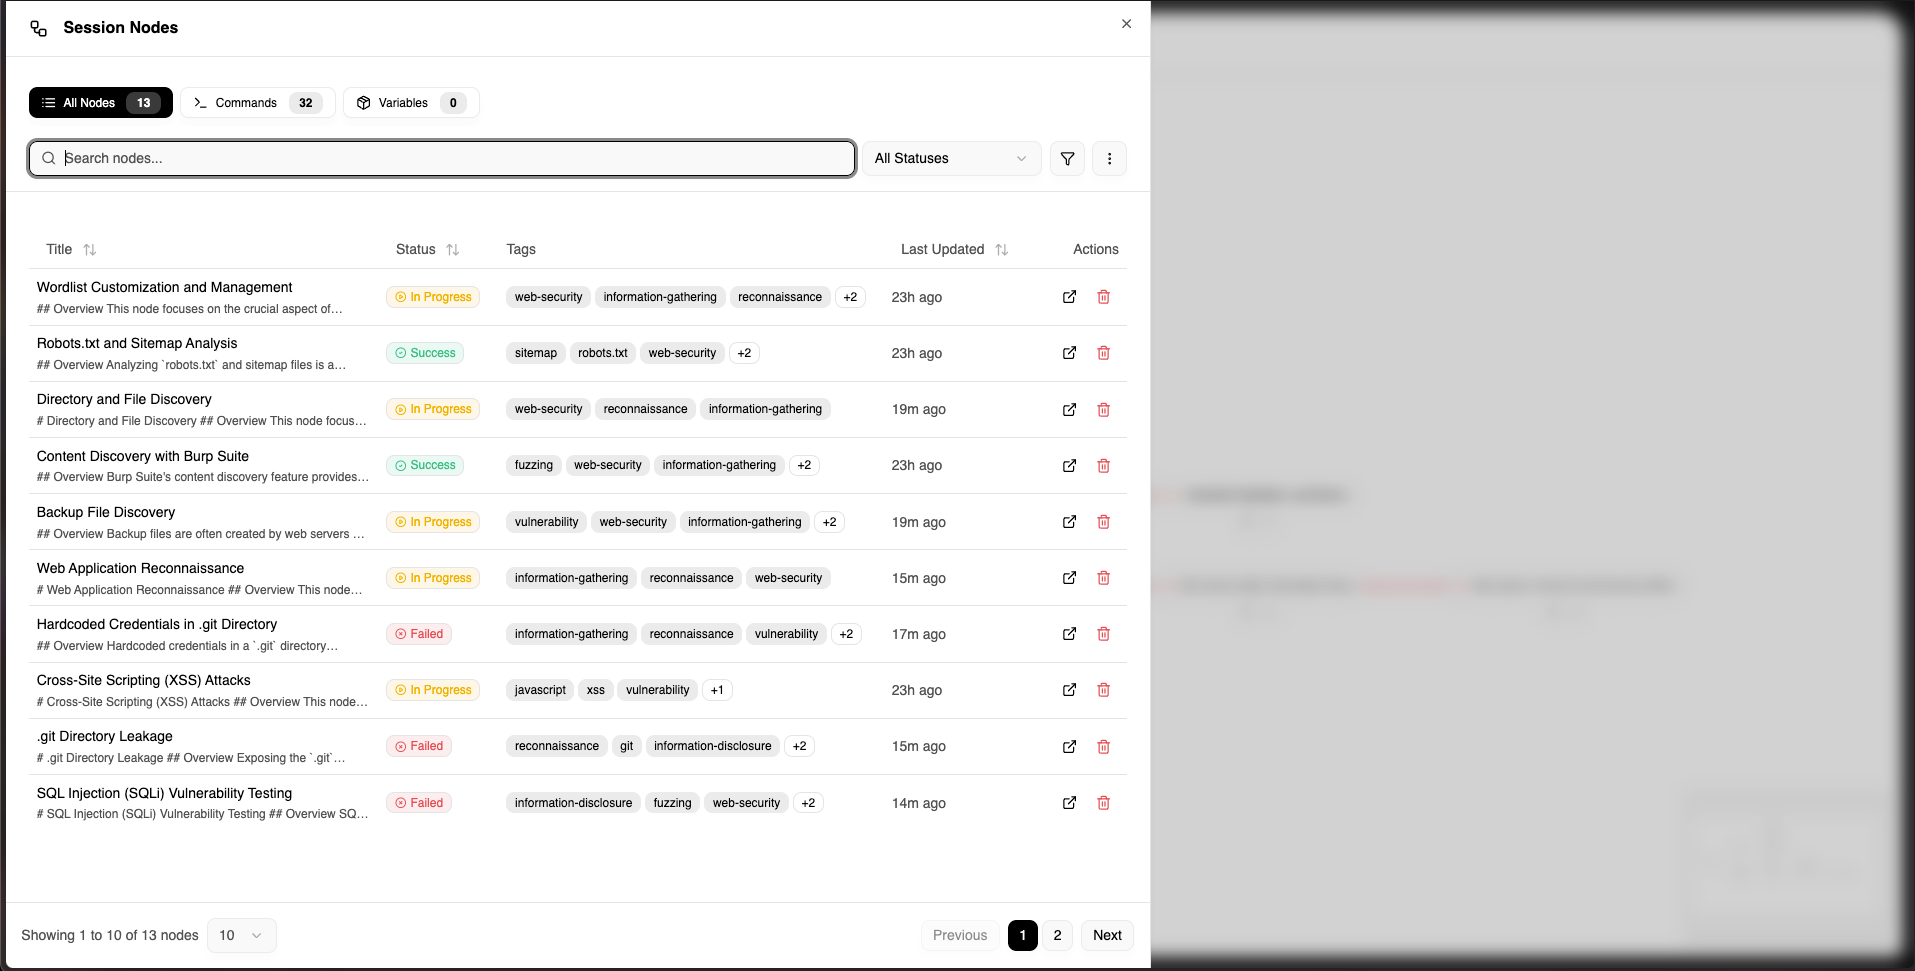
专为进攻性安全评估量身定制的可视化方法论追踪平台

penetration-testingutilities-frameworkseducation+1
2751年前
CypherDog preview

CypherDog

GitHubsadprocessor/cypherdog

PoSh BloodHound 犬语者

reconnaissanceinformation-gatheringpenetration-testing+2
1933年前
DbgNexum preview

DbgNexum

GitHubdis0rder0x00/dbgnexum

使用 Windows 调试 API 进行 Shellcode 注入

payload-generationexploitationshellcode+6
18310个月前
KDStab preview

KDStab

GitHuboctoberfest7/kdstab

KillDefender 和 Backstab 的 BOF 组合

defensive-toolsprivilege-escalationexploit-frameworks+3
1703年前
SILVERPICK preview

SILVERPICK

GitHubwinterknife/silverpick

Windows 用户模式 Shellcode 开发框架 (WUMSDF)

exploitationshellcodered-teaming+2
1584个月前
dns-black-cat preview

dns-black-cat

GitHubzux0x3a/dns-black-cat

跨平台工具包,用于交互式 DNS shell 命令外泄。通过使用 DNS-Cat,你将能够在 DNS 协议上以 shell 模式执行系统命令。

encryption-decryption-toolspayload-generationdata-exfiltration+3
1134年前
Citrix-Virtual-Apps-XEN-Exploit preview

Citrix-Virtual-Apps-XEN-Exploit

GitHubwatchtowrlabs/citrix-virtual-apps-xen-exploit

Citrix Virtual Apps and Desktops (XEN) 未认证远程代码执行漏洞

vulnerability-analysisexploitationweb-application-exploitation+2
2022年前
Lockbit3.0-MpClient-Defender-PoC preview

Lockbit3.0-MpClient-Defender-PoC

GitHubsh0ckfr/lockbit3.0-mpclient-defender-poc

Lockbit3.0 微软 Defender MpClient.dll DLL 劫持 PoC

exploitationmalware-analysisred-teaming+2
1774年前
SneakyEXE preview

SneakyEXE

GitHubhackernese/sneakyexe

在权限提升测试期间,对自定义有效载荷进行自动UAC绕过

privilege-escalationexploitationred-teaming+1
974年前
上一页1…808182…100下一页







