
Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
后渗透利用 — 第 99 页 | Kitploit
分类

后渗透利用

用于在受损系统和网络中维护访问、探索和扩大控制的工具。

Kitploit 推荐

精选工具

10 已选择
NetExec preview#1

NetExec

GitHubpennyw0rth/netexec
5.8k12小时24分前
impacket preview#2

impacket

GitHubfortra/impacket
16.0k1天前
mimikatz preview#3

mimikatz

GitHubgentilkiwi/mimikatz
21.8k6个月前
PEASS-ng preview#4

PEASS-ng

GitHubpeass-ng/peass-ng
20.3k11小时32分前
Rubeus preview#5

Rubeus

GitHubghostpack/rubeus
5.1k11个月前
Seatbelt preview#6

Seatbelt

GitHubghostpack/seatbelt
4.7k1年前
Empire preview#7

Empire

GitHubbc-security/empire
5.2k1个月前
sliver preview#8

sliver

GitHubbishopfox/sliver
11.7k8小时23分前
LaZagne preview#10

LaZagne

GitHubalessandroz/lazagne
11.0k1年前
PowerUpSQL preview#11

PowerUpSQL

GitHubnetspi/powerupsql
2.7k1年前
最新相关性最受欢迎最近更新
6165 结果
CVE-2025-14018 preview

CVE-2025-14018

GitHubkaleth4/cve-2025-14018

针对 CVE-2025-14018 的概念验证漏洞利用,该漏洞是 NetBT e-Fatura 中因服务路径未加引号导致的本地权限提升漏洞,可实现以 LocalSystem 身份执行任意代码。

privilege-escalationvulnerability-analysisexploitation+2
6个月前
CVE-2026-30862 preview

CVE-2026-30862

GitHubdrkim-dev/cve-2026-30862

概念验证,演示 Appsmith 表格组件中的存储型 XSS,可导致垂直权限提升,并通过 XSS 到 CSRF 攻击实现完全接管管理员账户。
privilege-escalationvulnerability-analysisexploitation+4
36个月前
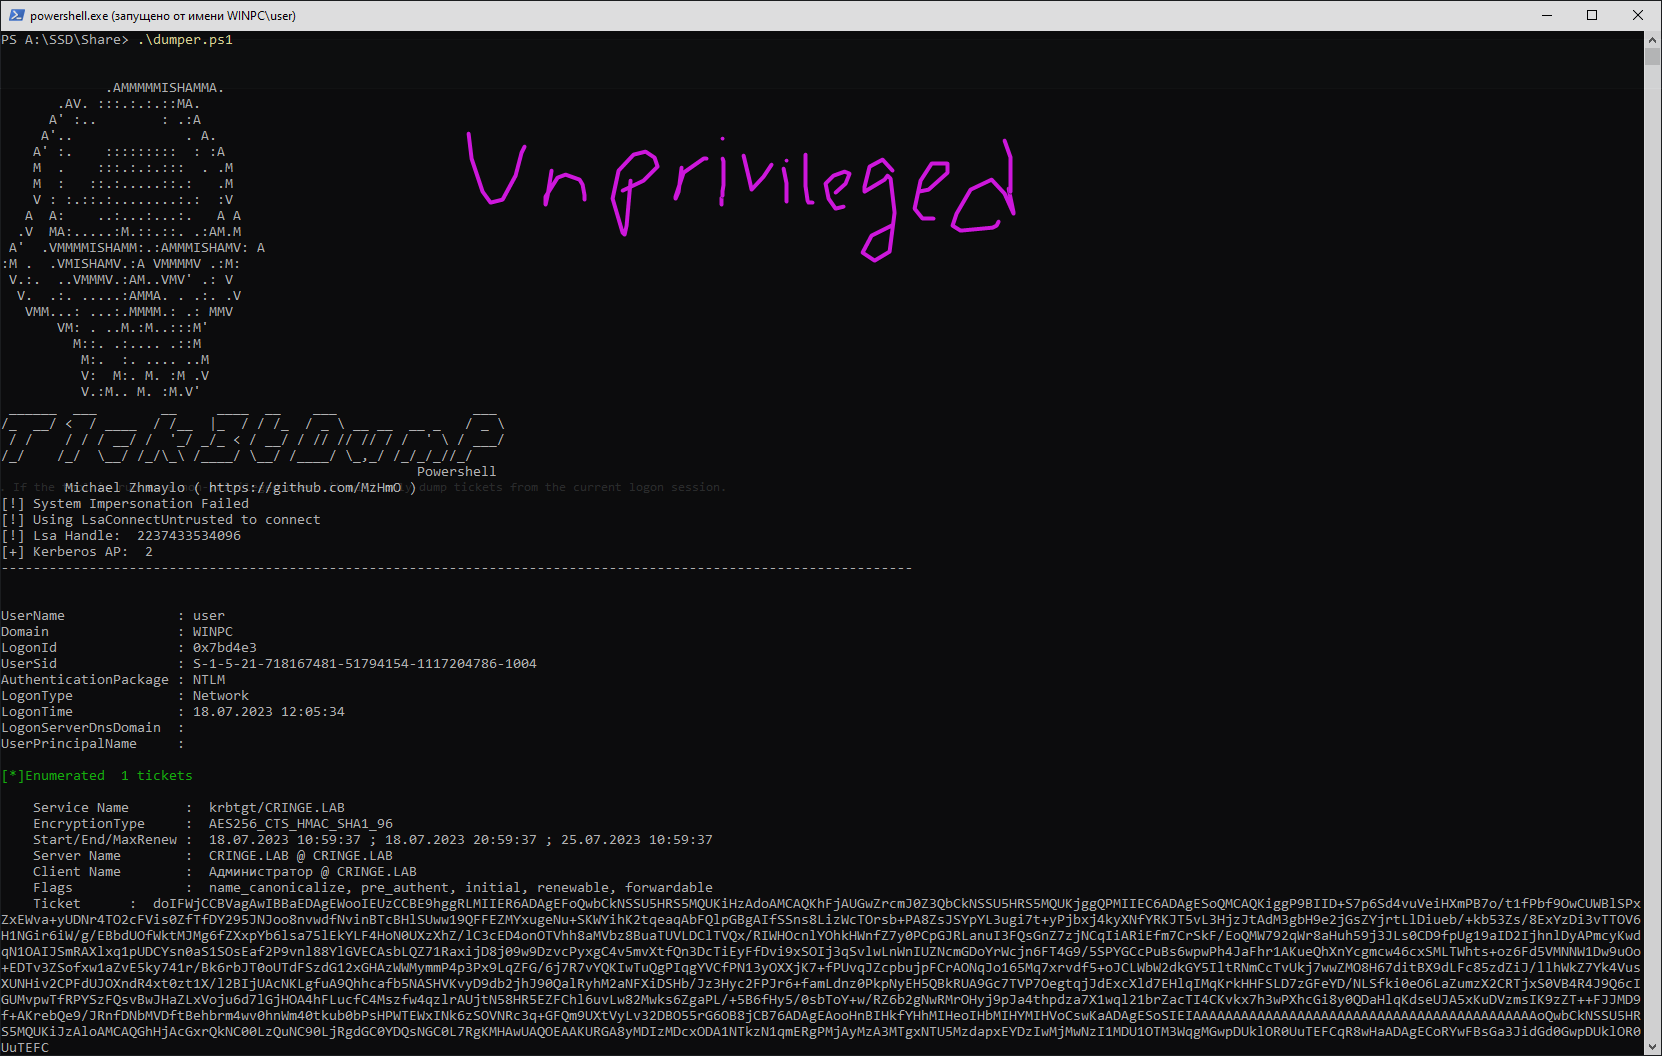
CVE-2022-30190 preview

CVE-2022-30190

GitHubshndnth/cve-2022-30190

CVE-2022-30190 (Follina) 漏洞的教育性概念验证。
privilege-escalationvulnerability-analysisexploitation+8
6个月前
PowershellKerberos preview

PowershellKerberos

GitHubmzhmo/powershellkerberos

一些使用 PowerShell 滥用 Kerberos 的脚本

impersonation-toolslateral-movementpost-exploitation+3
3666个月前
win32k-callback-detouring preview

win32k-callback-detouring

GitHubn0qword/win32k-callback-detouring

滥用 win32k.sys 内核回调机制实现任意代码执行
exploitationshellcodepost-exploitation+3
1086个月前
CVE-2026-5530 preview

CVE-2026-5530

GitHubdavidrxchester/cve-2026-5530

CVE-2026-5530 的概念验证漏洞利用程序,针对 Ollama 的 Pull/Push API 中的 SSRF 漏洞,可通过恶意 OCI 注册表实现内部端点枚举及完整响应数据外泄。
vulnerability-analysisexploitationweb-application-exploitation+2
6个月前
pypykatz preview

pypykatz

GitHubskelsec/pypykatz

纯Python实现的Mimikatz

password-crackingencryption-decryption-toolsmemory-forensics+4
3.3k6个月前
CVE-2025-60709 preview

CVE-2025-60709

GitHubkondordevsecuritycorp/cve-2025-60709

Windows CLFS LPE 漏洞利用 PoC,用于安全研究
defensive-toolsprivilege-escalationvulnerability-analysis+4
6个月前
Web-Penetration-Test preview

Web-Penetration-Test

GitHubsalimelh94/web-penetration-test

利用 WordPress 漏洞(CVE-2025-34077),通过 Cookie 注入绕过身份验证,并将权限提升至 root。这是我网络安全专项的一部分。
privilege-escalationvulnerability-analysisexploitation+6
6个月前
CVE-2025-15260 preview

CVE-2025-15260

GitHubd3kc4rt1/cve-2025-15260

插件中的缺失授权/访问控制漏洞 - MyRewards – WooCommerce 的忠诚积分和奖励
privilege-escalationvulnerability-analysisweb-application-exploitation+3
6个月前
CVE-2020-12446 preview

CVE-2020-12446

GitHubenessakircolak/cve-2020-12446

Windows 内核利用针对 LOL 驱动 eneio64.sys
privilege-escalationvulnerability-analysisexploitation+2
6个月前
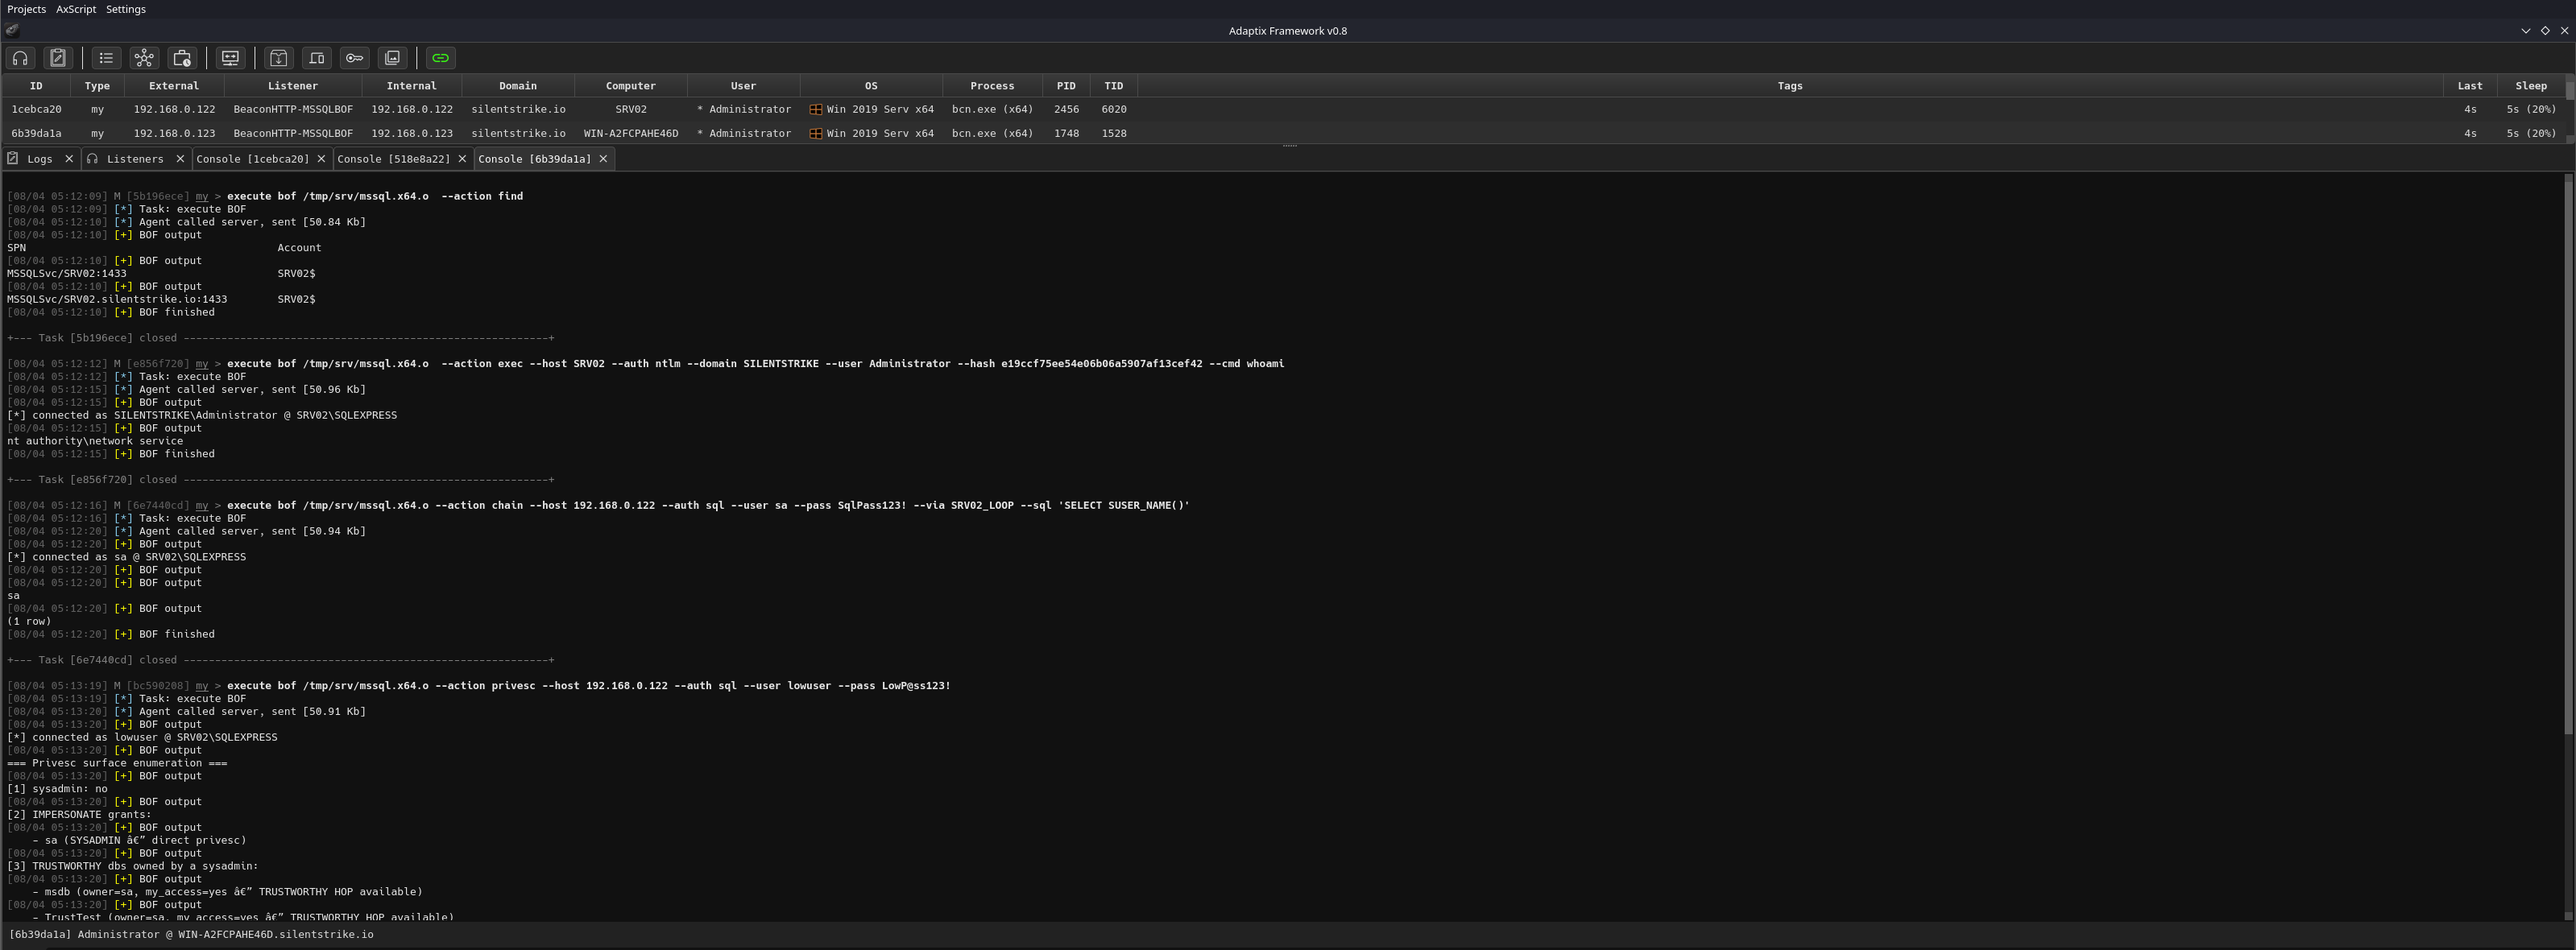
mssqlbof preview

mssqlbof

GitHubmazx0p/mssqlbof

一个针对 Microsoft SQL Server 的 Beacon Object File 套件,它自身在线上使用 TDS 7.4 协议。
privilege-escalationpassword-attacksexploitation+8
1016个月前
CVE-2025-9074-docker-escape preview

CVE-2025-9074-docker-escape

GitHubchernandez321/cve-2025-9074-docker-escape

此脚本仅供教育目的和在授权环境(如 HackTheBox)中使用。未经明确许可针对系统使用是违法的。

privilege-escalationcontainer-securityexploitation+3
6个月前
ChromeKatz preview

ChromeKatz

GitHubmeckazin/chromekatz

直接从 Chrome/Edge 进程内存中转储 Cookie 和凭据
memory-forensicspassword-attacksdata-exfiltration+3
1.5k6个月前
TotalRecall preview

TotalRecall

GitHubxaitax/totalrecall

该工具提取并显示 Windows 11 中 Recall 功能的数据,提供一种便捷的方式来访问有关你电脑活动快照的信息。
privilege-escalationreconnaissanceexploitation+5
1646个月前
CVE-2026-4112 preview

CVE-2026-4112

GitHubhann1bl3l3ct3r/cve-2026-4112

SonicWall SMA1000 系列设备中,对 SQL 命令中特殊元素的中和不当(“SQL 注入”)允许具有只读管理员权限的远程已认证攻击者将权限提升为主要管理员。
privilege-escalationvulnerability-analysisexploitation+2
16个月前
Windows-11-24h2-Kernel-Exploit preview

Windows-11-24h2-Kernel-Exploit

GitHubenessakircolak/windows-11-24h2-kernel-exploit

Windows 11 24h2 本地权限提升内核漏洞利用。CVE-2020-12446(eneio64.sys)
privilege-escalationvulnerability-analysisexploitation+1
66个月前
HTB-Pterodactyl-Writeup preview

HTB-Pterodactyl-Writeup

GitHubv0idw1re/htb-pterodactyl-writeup

HackTheBox — Pterodactyl(中等难度/Linux)通关指南。CVE-2025-49132 本地文件包含(LFI)→ pearcmd 远程代码执行(RCE)→ bcrypt 哈希破解 → SSH。通过 CVE-2025-6018(PAM pam_environment 绕过)+…


password-crackingprivilege-escalationreconnaissance+9
6个月前
上一页1…9899100下一页