Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
横向移动 — 第 34 页 | Kitploit
分类

横向移动

用于通过在系统之间移动来探索和扩大受损网络内控制的工具。

Kitploit 推荐
精选工具

10 已选择
impacket preview#1

impacket

GitHubfortra/impacket
16.0k10小时39分前
NetExec preview#2

NetExec

GitHubpennyw0rth/netexec
5.8k8小时17分前
Rubeus preview#3

Rubeus

GitHubghostpack/rubeus
5.1k11个月前
BloodHound-Legacy preview#4

BloodHound-Legacy

GitHubspecterops/bloodhound-legacy
10.6k8个月前
SharpHound preview#5

SharpHound

GitHubspecterops/sharphound
1.4k12天前
kerbrute preview#6

kerbrute

GitHubropnop/kerbrute
3.4k5年前
Responder preview#7

Responder

GitHublgandx/responder
6.5k4个月前
Snaffler preview#8

Snaffler

GitHubsnaffcon/snaffler
2.9k8个月前
PowerUpSQL preview#9

PowerUpSQL

GitHubnetspi/powerupsql
2.7k1年前
SharpMapExec preview#10

SharpMapExec

GitHubcube0x0/sharpmapexec
6714年前
最新相关性最受欢迎最近更新
656 结果
HTB-Pterodactyl-Writeup preview

HTB-Pterodactyl-Writeup

GitHubkarimelsheikh1/htb-pterodactyl-writeup

HTB 第 10 季 - Pterodactyl 靶机 writeup。中等难度 Linux 靶机,涵盖 CVE-2025-49132(Pterodactyl Panel RCE)和 CVE-2025-6018/6019(udisks2 权限提升)。
password-crackingprivilege-escalationreconnaissance+7
6个月前
SMB-Penetration-Testing-NTLM-Relay-Version-2- preview

SMB-Penetration-Testing-NTLM-Relay-Version-2-

GitHubyouneskc/smb-penetration-testing-ntlm-relay-version-2-

SMB 红队实验室——通过 LLMNR 投毒实现 NTLM 中继、CVE-2007-2447、NTLMv2 哈希破解及 Windows 10 上的 NT AUTHORITY\SYSTEM
privilege-escalationreconnaissancepassword-attacks+9
5个月前
WMImplant preview

WMImplant

GitHubredsiege/wmimplant

这是一个基于PowerShell的工具,旨在充当RAT。其界面是一个shell,任何受支持的命令都会被转换为WMI等效命令,以便在网络/远程机器上使用。WMImplant基于WMI。
lateral-movementinformation-gatheringpost-exploitation+3
8628年前
PenetrationTesting_Notes- preview

PenetrationTesting_Notes-

GitHub0xdigimon/penetrationtesting_notes-

我的渗透测试笔记
privilege-escalationvulnerability-analysisexploitation+6
7414个月前
WMIcmd preview

WMIcmd

GitHubnccgroup/wmicmd

一个仅使用 WMI 的 Microsoft Windows 命令外壳包装器
reconnaissancelateral-movementinformation-gathering+3
3349年前
ZeroCrumb preview

ZeroCrumb

GitHubinternetangel/zerocrumb

无需特权即可转储应用绑定保护的凭据与 Cookie。
password-crackingexploitationlateral-movement+6
1691年前
OUned preview

OUned

GitHubsynacktiv/ouned

OUned 项目通过 gPLink 投毒自动化 Active Directory 组织单位 ACL 利用
privilege-escalationexploitationlateral-movement+3
1612个月前
PowerPriv preview

PowerPriv

GitHubg0ldengunsec/powerpriv

一款 PowerShell 实现的 PrivExchange,设计为在当前用户上下文中运行
privilege-escalationexploitationlateral-movement+2
1257年前
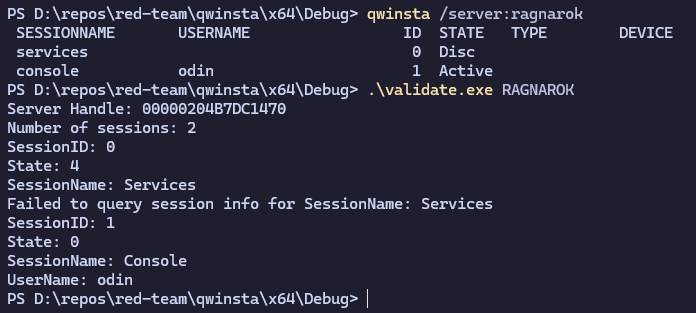
RemoteSessionEnum preview

RemoteSessionEnum

GitHub0xv1n/remotesessionenum

使用未记录的 Windows Station API 远程枚举会话
reconnaissancelateral-movementinformation-gathering+2
1192年前
CVE-2019-0887 preview

CVE-2019-0887

GitHubt43wiu6/cve-2019-0887

CVE-2019-0887的exp
privilege-escalationpersistence-mechanismsexploitation+4
185年前
injection preview

injection

GitHubjymcheong/injection

Windows 进程注入方法

privilege-escalationexploitationlateral-movement+3
78年前
CVE-2009-0229-PoC preview

CVE-2009-0229-PoC

GitHubzveriu/cve-2009-0229-poc

针对 CVE-2009-0229 "打印后台处理程序读文件漏洞" 的 LPE AFR PoC(与 CVE-2020-1048 相关)
privilege-escalationvulnerability-analysisexploitation+4
36年前
docker-lab-cve-2017-5638-cve-2021-41773 preview

docker-lab-cve-2017-5638-cve-2021-41773

GitHubkouf320/docker-lab-cve-2017-5638-cve-2021-41773

基于 Docker 的多阶段攻击模拟实验,演示 CVE-2017-5638 和 CVE-2021-41773 的漏洞利用、横向移动,以及 Suricata IDS 在现实 10 容器网络环境中的检测能力。
reconnaissanceexploitationids-ips-evasion+6
25个月前
printix-CVE-2022-29551 preview

printix-CVE-2022-29551

GitHubcomparedarray/printix-cve-2022-29551

PrintixService.exe 中的“暴露危险方法或函数”漏洞存在于 Kofax Printix 的“Printix Secure Cloud Print Management”1.3.1156.0 及更低版本中,该漏洞允许本地或远程攻击者安装恶意打印机驱动程序并通过 Printix…
privilege-escalationvulnerability-analysisexploitation+3
14年前
CVE-2025-33073 preview

CVE-2025-33073

GitHubobscura-cert/cve-2025-33073

概念验证工具,通过串联 DNS 注入、NTLM 中继和基于 RPC 的强制认证,测试 Windows Active Directory 环境中的认证中继路径。
privilege-escalationreconnaissancevulnerability-analysis+7
11年前
WinRAR-CVE-2025-8088-Exploitation-Toolkit preview

WinRAR-CVE-2025-8088-Exploitation-Toolkit

GitHubxi0onamdev/winrar-cve-2025-8088-exploitation-toolkit

GUI 工具,用于创建利用 CVE-2025-8088 路径遍历漏洞的恶意 RAR 压缩包。采用 NTFS ADS 隐蔽技术及 RAR5 头注入实现载荷投递,并利用 Windows 启动项实现持久化。
privilege-escalationpayload-generationpersistence-mechanisms+7
11个月前
CVE-2025-47810 preview

CVE-2025-47810

GitHubptrstr/cve-2025-47810

PunkBuster LPI 提权至 NT AUTHORITY\SYSTEM
privilege-escalationvulnerability-analysisexploitation+2
1年前
CVE-2021-1675 preview

CVE-2021-1675

GitHubccordeiro/cve-2021-1675

# PrintNightmare CVE-2021-1675/CVE-2021-34527 的 C# 与 Impacket 实现

privilege-escalationpayload-generationvulnerability-analysis+3
11个月前
上一页1…333435…37下一页