Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
实验室与实践 — 第 76 页 | Kitploit
分类

实验室与实践

用于授权且安全的网络安全实践的训练实验室、动手环境和可复现挑战。

Kitploit 推荐

精选工具

10 已选择
vulhub preview#1

vulhub

GitHubvulhub/vulhub
21.1k1个月前
juice-shop preview#2

juice-shop

GitHubjuice-shop/juice-shop
13.6k2天前
WebGoat preview#3

WebGoat

GitHubwebgoat/webgoat
9.5k13天前
DVWA preview#4

DVWA

GitHubdigininja/dvwa
13.5k5天前
crAPI preview#5

crAPI

GitHubowasp/crapi
1.6k2个月前
NodeGoat preview#6

NodeGoat

GitHubowasp/nodegoat
2.1k3年前
SecurityShepherd preview#7

SecurityShepherd

GitHubowasp/securityshepherd
1.5k2天前
wrongsecrets preview#8

wrongsecrets

GitHubowasp/wrongsecrets
1.5k3天前
metasploitable3 preview#9

metasploitable3

GitHubrapid7/metasploitable3
5.7k1年前
GOAD preview#10

GOAD

GitHuborange-cyberdefense/goad
8.1k29天前
最新相关性最受欢迎最近更新
3042 结果
BIT-EternalBlue-for-macOS_Linux preview

BIT-EternalBlue-for-macOS_Linux

GitHubi-rinka/bit-eternalblue-for-macos_linux

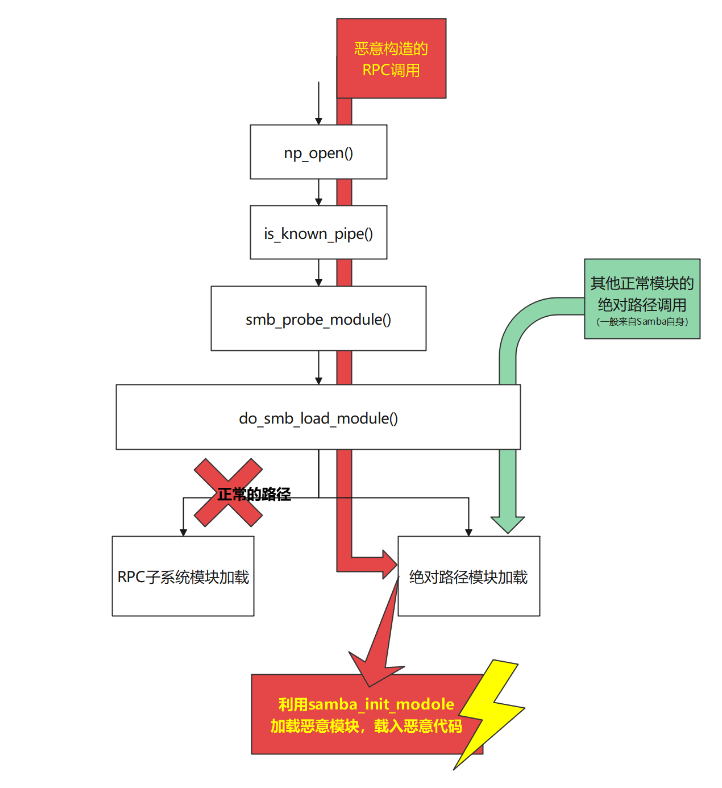
利用CVE-2017-7494完成网络安全课程期末作业。这将揭示以管理员权限运行在Linux上的服务的漏洞。

vulnerability-analysisexploitationnetwork-security+5
45年前
DIRTY-FRAG-Detection-with-Wazuh-4.14.4 preview

DIRTY-FRAG-Detection-with-Wazuh-4.14.4

GitHubmym0us3r/dirty-frag-detection-with-wazuh-4.14.4

Wazuh 4.14.4 用于检测 CVE-2026-43284 / CVE-2026-43500 (Dirty Frag) 的规则 - 通过页面缓存写入实现 Linux 本地权限提升

privilege-escalationvulnerability-analysisexploitation+6
36个月前
CVE-2024-21626-demo preview

CVE-2024-21626-demo

GitHublaysakura/cve-2024-21626-demo

演示 CVE-2024-21626 容器逃逸漏洞利用,通过恶意 Docker 镜像获取宿主机 root 权限,并包含逐步攻击场景,仅用于教育目的。

container-securityvulnerability-analysisexploitation+3
32年前
CVE-2025-54424 preview

CVE-2025-54424

GitHubhophtien/cve-2025-54424

CVE-2025-54424: 1Panel TLS 客户端证书绕过可通过伪造 CN 'panel_client' 并使用捆绑的扫描与利用工具实现 RCE。受影响版本: <= v2.0.5。🔐

vulnerability-scannersexploitationweb-security+3
31个月前
sudoinjection preview

sudoinjection

GitHubmikivirus0/sudoinjection

Sudo本地权限提升 CVE-2025-32463(适用于shell不稳定无法生成新的root shell的情况)

privilege-escalationvulnerability-analysisexploitation+5
21年前
CVE-2026-42048 preview

CVE-2026-42048

GitHubeqstlab/cve-2026-42048

Langflow 任意目录删除

vulnerability-analysisexploitationweb-application-exploitation+3
26个月前
text4shell-cve-2022-42889 preview

text4shell-cve-2022-42889

GitHubdevenes/text4shell-cve-2022-42889

CVE-2022-42889 的 Kubernetes 实验室
container-securityvulnerability-analysisweb-application-exploitation+3
23年前
Libssh2-Exploit preview

Libssh2-Exploit

GitHubviz27/libssh2-exploit

创建一个针对 libssh2 漏洞(CVE-2019-13115)的利用程序。
vulnerability-analysisexploitationpenetration-testing+3
16年前
CVE-2020-7246 preview

CVE-2020-7246

GitHubpswalia2u/cve-2020-7246

# CVE-2020-7246 的实验室环境与利用脚本 qdPM 9.1 中 PHP 代码注入漏洞(CVE-2020-7246)的实验室环境与利用脚本。包含 Docker 搭建环境以及基于 Python2 的利用方法,用于实现认证后的远程代码执行。

vulnerability-analysisexploitationweb-application-exploitation+3
14年前
CVE-2026-26980-PoC preview

CVE-2026-26980-PoC

GitHubn0bitaemon/cve-2026-26980-poc

Ghost CMS Content API 盲SQL注入

vulnerability-analysisexploitationweb-application-exploitation+4
14个月前
CVE-2021-41773S preview

CVE-2021-41773S

GitHubmightysai1997/cve-2021-41773s

基于Docker的漏洞实验室,针对CVE-2021-41773 Apache路径遍历,提供在受控环境中进行文件读取和远程代码执行的PoC配置。

container-securityvulnerability-analysisexploitation+3
15年前
CVE-2026-43494-PinTheft-PoC preview

CVE-2026-43494-PinTheft-PoC

GitHubjayhutajulu1/cve-2026-43494-pintheft-poc

针对CVE-2026-43494(PinTheft)的概念验证:通过RDS零拷贝引用计数漏洞加io_uring固定缓冲区实现Linux本地提权 → SUID页缓存覆盖。仅限授权研究。
privilege-escalationmemory-forensicsvulnerability-analysis+4
14个月前
SOC_287 preview

SOC_287

GitHubhashdr1ft/soc_287

SOC287 - Checkpoint Security Gateway 上的任意文件读取 [CVE-2024-24919]

vulnerability-analysisexploitationweb-application-exploitation+3
11年前
Penetration-Testing-on-Metasploitable2 preview

Penetration-Testing-on-Metasploitable2

GitHubseifeldienahmad/penetration-testing-on-metasploitable2

使用 Kali Linux 对 Metasploitable2 进行实战渗透测试项目。包含完整工作流程:Nmap 扫描、枚举、Metasploit 漏洞利用(Samba CVE-2007-2447)、后渗透验证和缓解步骤。仓库包含命令、输出以及展示攻击技术和防御建议的报告。

reconnaissancevulnerability-scannersnetwork-mapping+6
11年前
TXDXCristhian_2023-CVE-38831 preview

TXDXCristhian_2023-CVE-38831

GitHubcristhiansm0/txdxcristhian_2023-cve-38831

CVE-2023-38831 WinRAR 实验室:使用 Sysmon/Wazuh 进行检测、使用 Ghidra 进行逆向工程、补丁分析与修复。
vulnerability-analysisreverse-engineeringeducation+3
3个月前
vulnmachines preview

vulnmachines

GitHubvulnmachines/vulnmachines

平台

ctfeducationcurated-resources+2
4年前
CVE-2026-61946-Easy-Appointments-IDOR preview

CVE-2026-61946-Easy-Appointments-IDOR

GitHubrat5ak/cve-2026-61946-easy-appointments-idor

CVE-2026-61946: 未经身份验证的IDOR漏洞,影响Easy Appointments <= 3.12.27

vulnerability-analysisexploitationweb-application-exploitation+3
4个月前
Research-CVE-2016-5195 preview

Research-CVE-2016-5195

GitHubh1n4mx0z/research-cve-2016-5195

CVE-2016-5195 (Dirty COW) 的详细技术分析和概念验证利用代码,这是一个利用写时复制内存管理中的竞态条件的Linux内核权限提升漏洞。

privilege-escalationvulnerability-analysisexploitation+3
3年前
上一页1…757677…100下一页