
Skip to content
KitploitKITPLOIT
工具漏洞利用博客
Log in
提交
工具漏洞利用博客
提交

黑客、渗透测试和网络安全工具,武装您的安全武器库!

Kitploit 是一个黑客、网络安全和渗透测试工具的目录。发现最新的项目更新,查找漏洞、分析系统、自动化测试并加强你的安全。

订阅源联系隐私© 2026 Kitploit

工具目录

分类

查看所有分类
Loading categories
IDS/IPS规避 — 第 13 页 | Kitploit
分类

IDS/IPS规避

用于绕过入侵检测和预防系统(IDS/IPS)以及网络安全控制的工具。

Kitploit 推荐

精选工具

10 已选择
scapy preview#1

scapy

GitHubsecdev/scapy
12.5k15小时36分前
nmap preview#2

nmap

GitHubnmap/nmap
13.3k6小时2分前
bettercap preview#3

bettercap

GitHubbettercap/bettercap
19.8k2个月前
sgn preview#5

sgn

GitHubegebalci/sgn
2.0k2个月前
unicorn preview#6

unicorn

GitHubtrustedsec/unicorn
3.9k1个月前
donut preview#7

donut

GitHubthewover/donut
4.7k1年前
sRDI preview#8

sRDI

GitHubmonoxgas/srdi
2.5k4年前
chisel preview#9

chisel

GitHubjpillora/chisel
16.4k11天前
ligolo-ng preview#10

ligolo-ng

GitHubnicocha30/ligolo-ng
4.8k27天前
dnscat2 preview#12

dnscat2

GitHubiagox86/dnscat2
4.0k4年前
最新相关性最受欢迎最近更新
655 结果
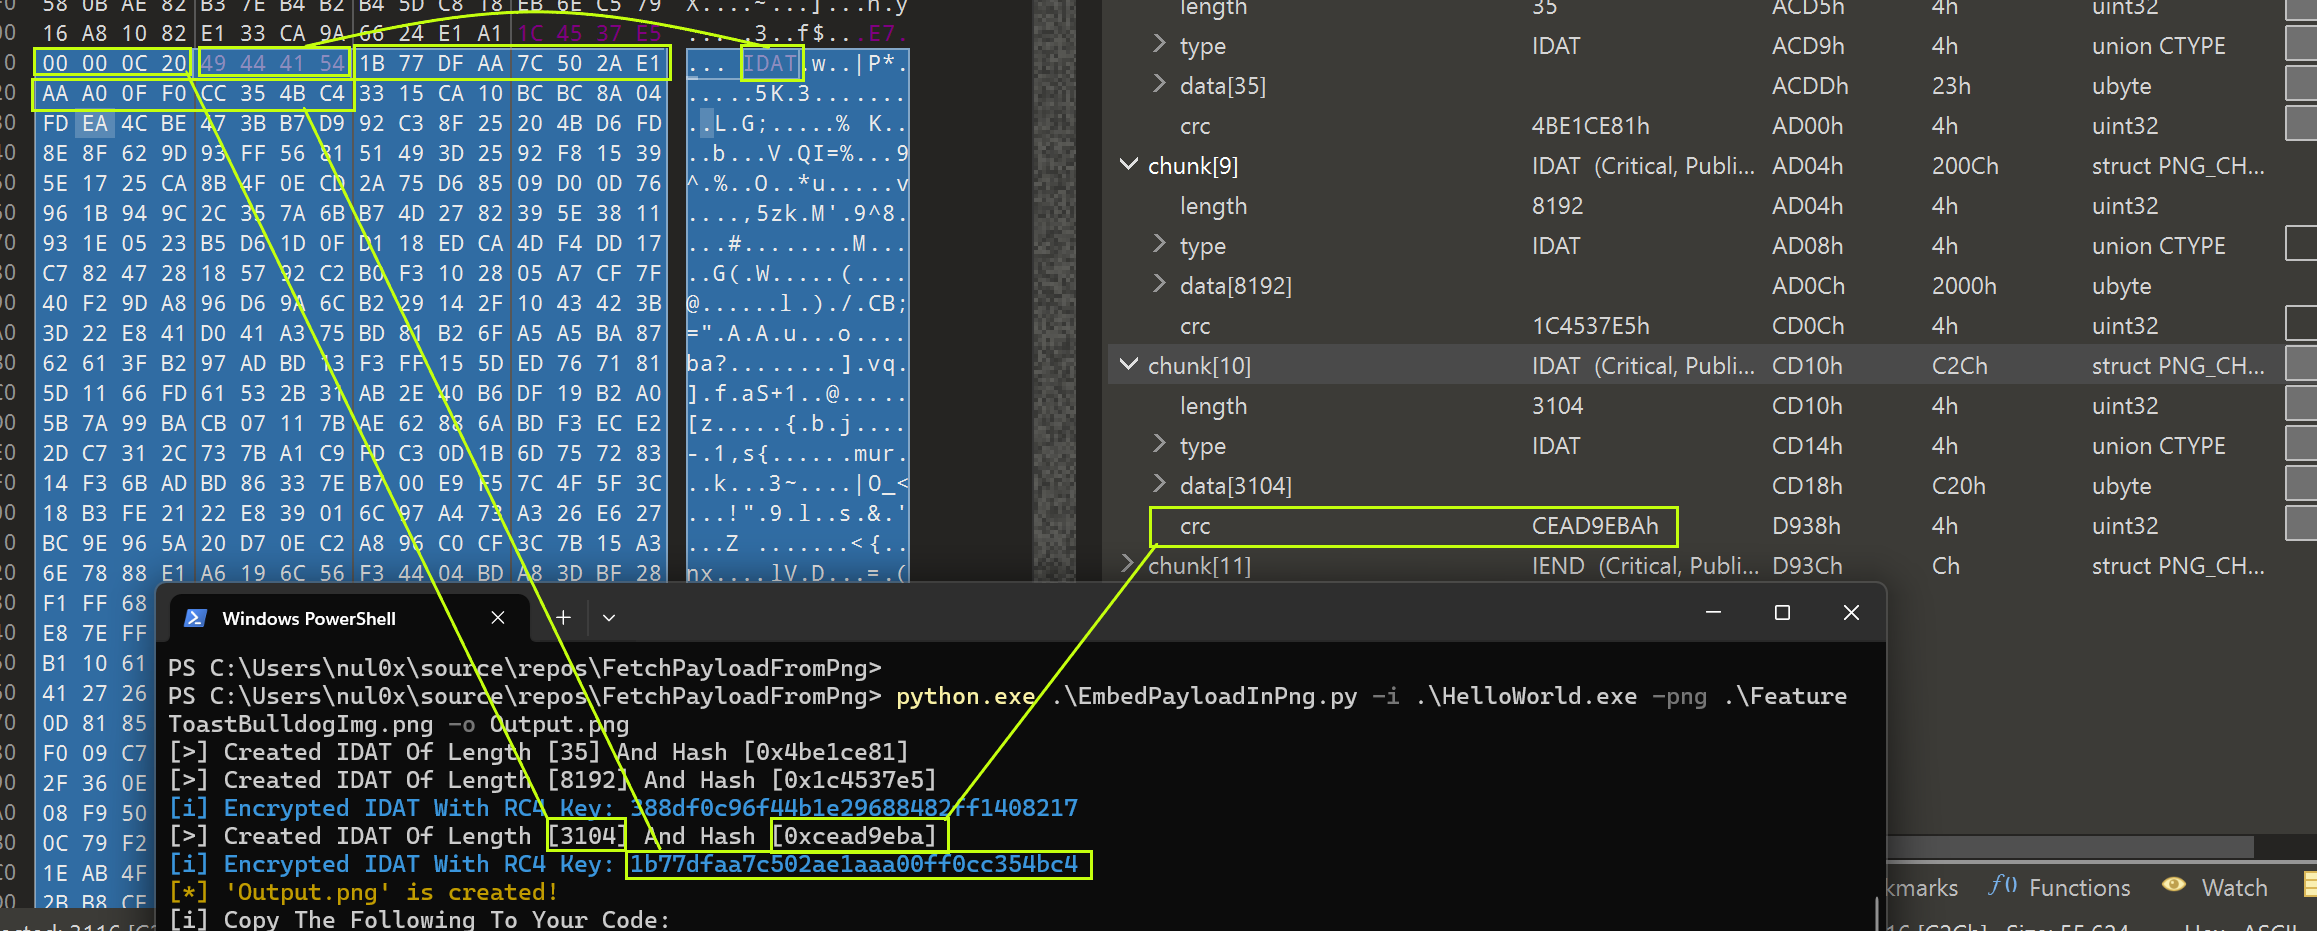
EmbedPayloadInPng preview

EmbedPayloadInPng

GitHubmaldev-academy/embedpayloadinpng

将有效载荷嵌入PNG文件中

ids-ips-evasiondata-exfiltrationsteganography+2
3731年前
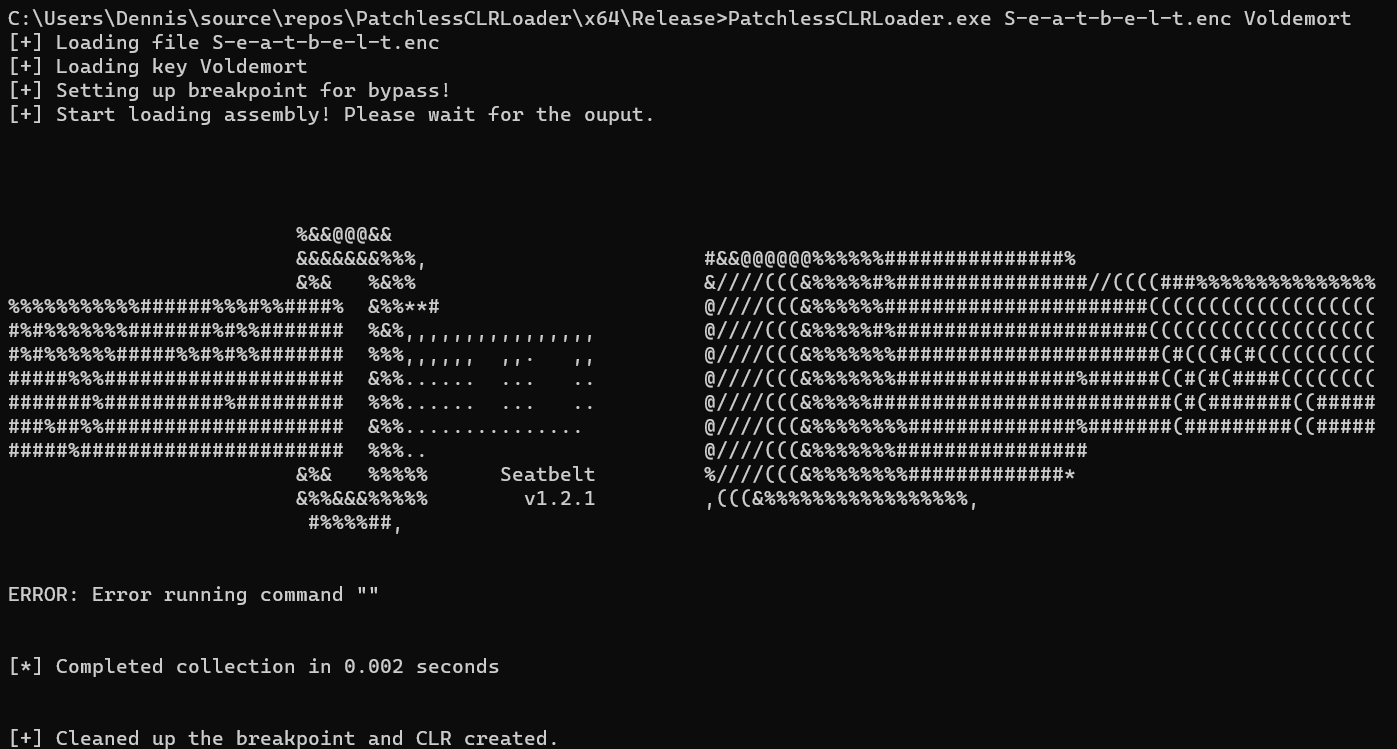
PatchlessCLRLoader preview

PatchlessCLRLoader

GitHubvoldesec/patchlessclrloader

.NET 程序集加载器,带无补丁 AMSI 与 ETW 绕过功能
ids-ips-evasionpost-exploitationred-teaming+1
3873年前
Fireaway preview

Fireaway

GitHubtcstool/fireaway

下一代防火墙审计与绕过工具

ids-ips-evasiondata-exfiltrationnetwork-security+1
2669年前
AsmLdr preview

AsmLdr

GitHub0xninjacyclone/asmldr

具备复杂规避能力的动态 Shellcode 加载器

payload-generationids-ips-evasionshellcode+3
3461年前
KTO preview

KTO

GitHubymsniper/kto

自动Wi-Fi去认证工具,持续扫描目标SSID上的客户端并踢出非白名单设备。功能包括白名单支持、网状/多AP处理、PMF检测,以及通过EAPOL提取的实验性WPA2 PMF绕过。

wi-fi-auditingexploitationids-ips-evasion+4
2371个月前
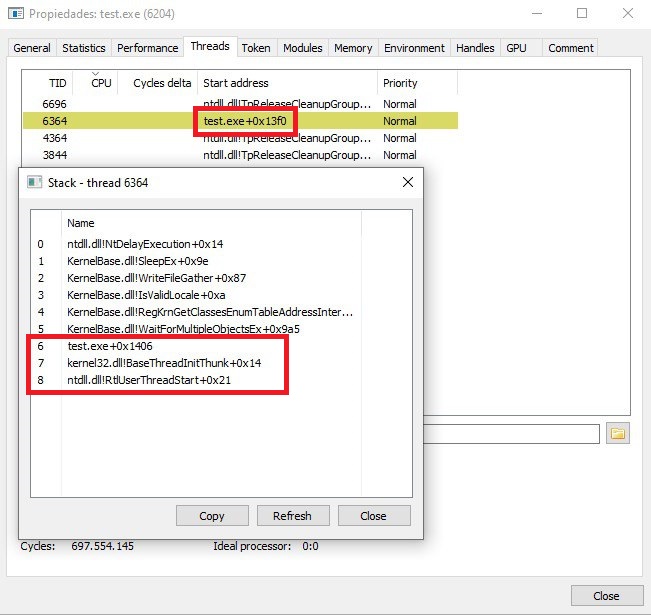
SleepyCrypt preview

SleepyCrypt

GitHubsolomonsklash/sleepycrypt

一个在进程休眠时加密运行中进程映像的 shellcode 函数。
ids-ips-evasionshellcodered-teaming+1
3385年前
Unwinder preview

Unwinder

GitHubkudaes/unwinder

调用栈伪装工具,适用于 Rust

ids-ips-evasionpost-exploitationred-teaming+2
3841年前
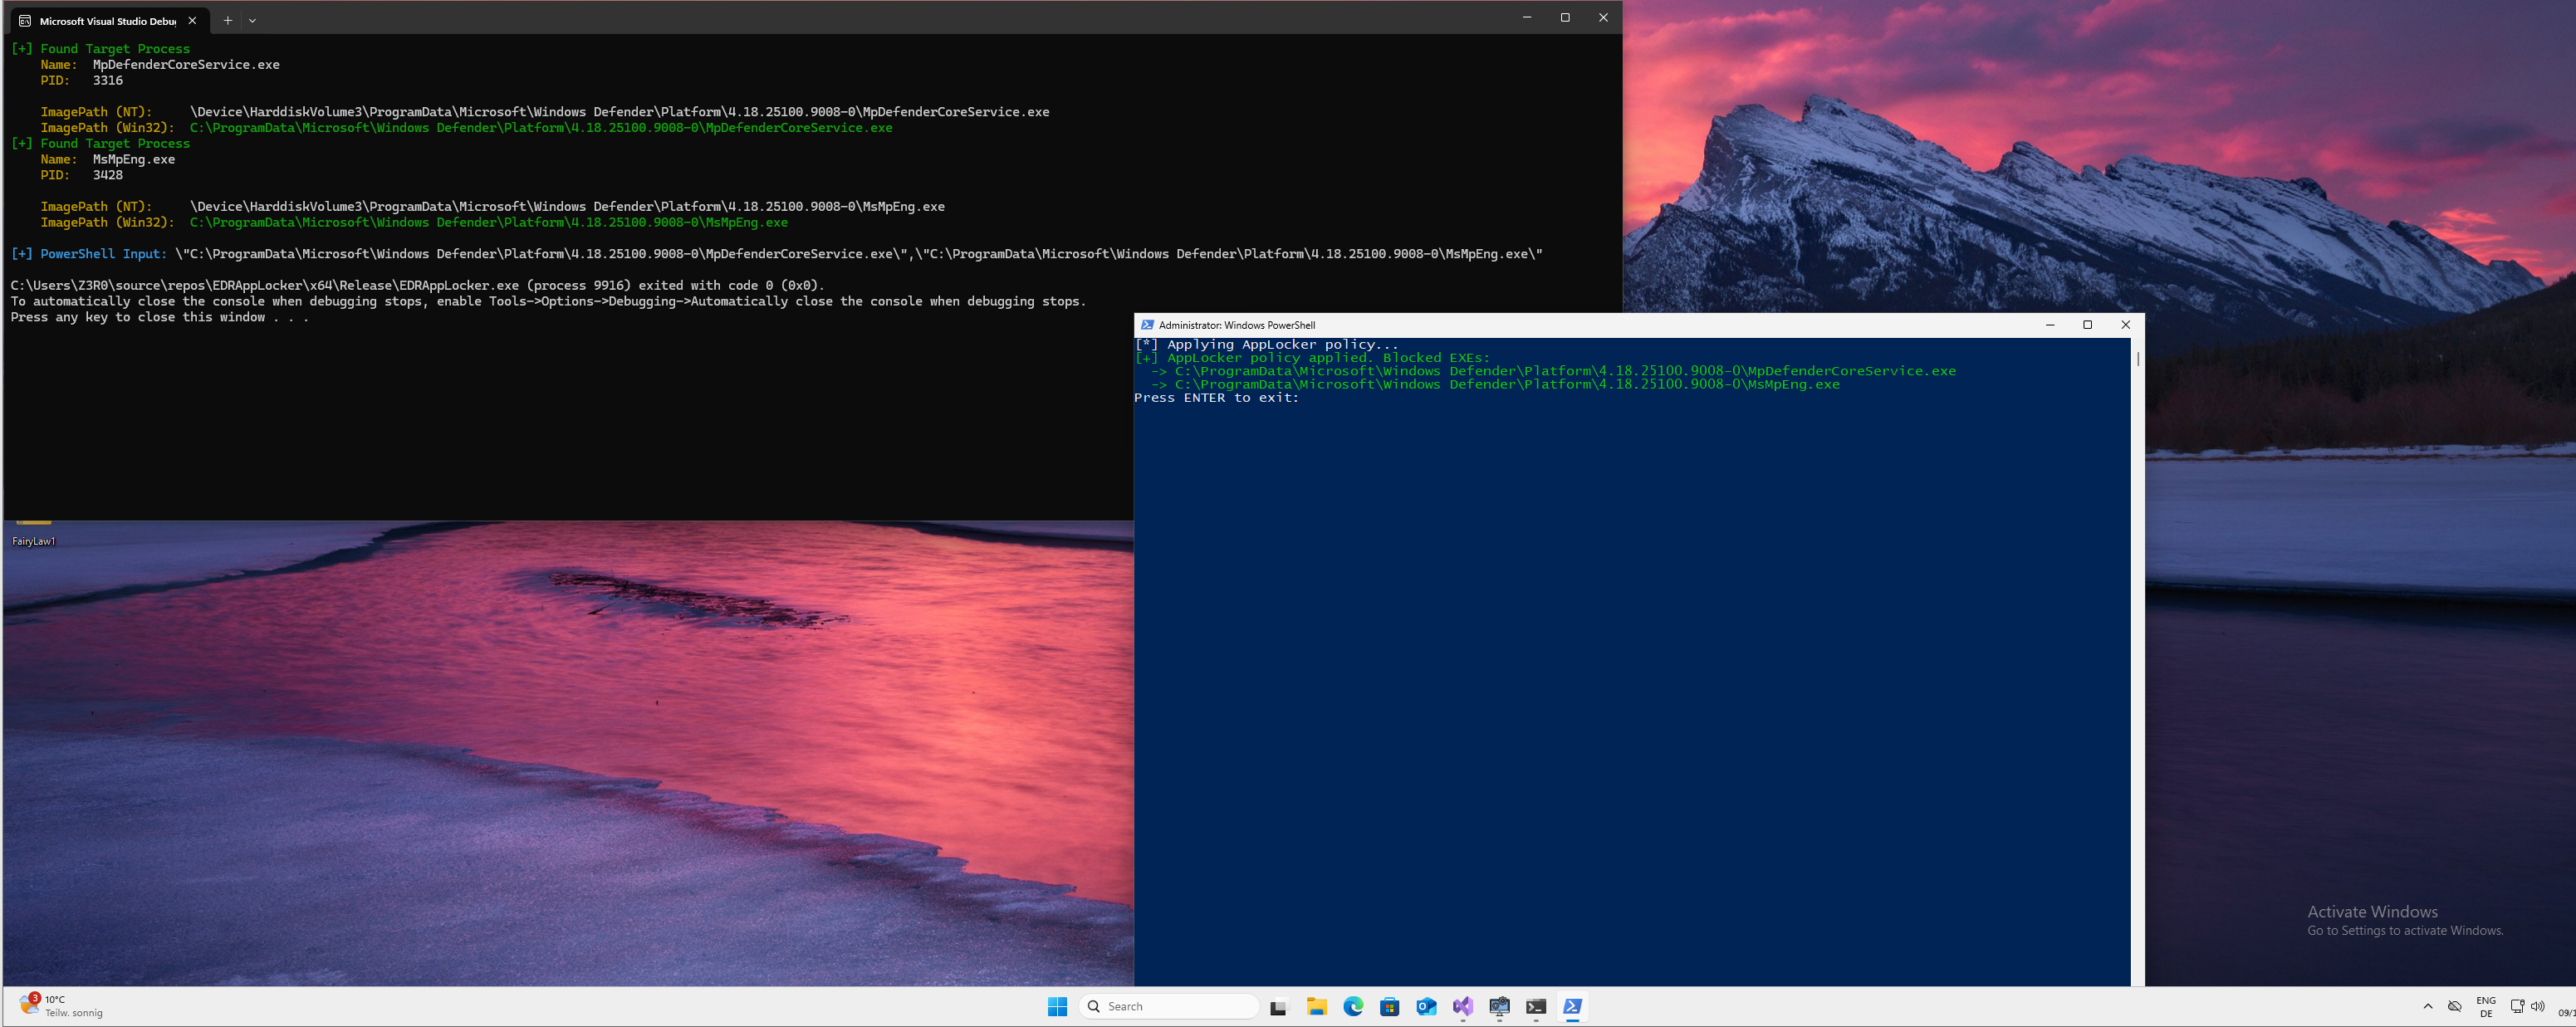
EDR-GhostLocker preview

EDR-GhostLocker

GitHubzero2504/edr-ghostlocker

基于AppLocker的EDR规避
defensive-toolsprivilege-escalationexploitation+5
34110个月前
AV-EDR-Killer preview

AV-EDR-Killer

GitHubxm0kht4r/av-edr-killer

通过利用易受攻击的驱动程序 (BYOVD) 终止 AV/EDR 进程
privilege-escalationpersistence-mechanismsexploitation+5
2969个月前
unhook-bof preview

unhook-bof

GitHubrsmudge/unhook-bof

移除 Beacon 进程中的 API 钩子。

ids-ips-evasionpost-exploitationred-teaming+1
2835年前
quickjack preview

quickjack

GitHubsamyk/quickjack

Quickjack 是一款点选式工具,用于直观地生成高级点击劫持和帧切片攻击。
exploitationids-ips-evasionphishing+4
24711年前
Lab4PurpleSec preview

Lab4PurpleSec

GitHub0xmr007/lab4purplesec

Lab4PurpleSec 是一个模块化的紫队家庭实验室,结合了一个脆弱的Active Directory环境(GOAD)、基于Docker的Web DMZ、pfSense + Suricata以及Wazuh SIEM。它提供了一个真实、开源式的训练环境,用于Web漏洞利用、横向移动、Active…
privilege-escalationids-ips-evasionweb-application-exploitation+5
3069个月前
UnhookingPatch preview

UnhookingPatch

GitHubsaadahla/unhookingpatch

绕过 EDR 钩子,通过修补 NT API 存根,并在运行时解析 SSN 和系统调用指令。
ids-ips-evasionpost-exploitationred-teaming+2
3093年前
MorphAES preview

MorphAES

GitHubcryptolok/morphaes

IDPS & SandBox & AntiVirus 隐形杀手。MorphAES 是世界上首个多态 shellcode 引擎,具有变形特性,并具备绕过沙箱的能力,这使得它对于 IDPS 而言无法被检测;它同时也是跨平台的,且不依赖任何库。
exploitationids-ips-evasionshellcode+4
3244年前
CallMeWin32kDriver preview

CallMeWin32kDriver

GitHubgmh5225/callmewin32kdriver

加载你的驱动程序,例如 win32k.sys
ids-ips-evasionpost-exploitationred-teaming+1
2574年前
Windows-SignedBinary preview

Windows-SignedBinary

GitHubmr-un1k0d3r/windows-signedbinary

对已签名的 Windows 二进制文件进行变异,在改变文件哈希的同时保留有效的目录签名,从而绕过基于哈希的端点拦截并暴露 Authenticode 验证漏洞。
hash-analysisids-ips-evasionreverse-engineering+4
2597年前
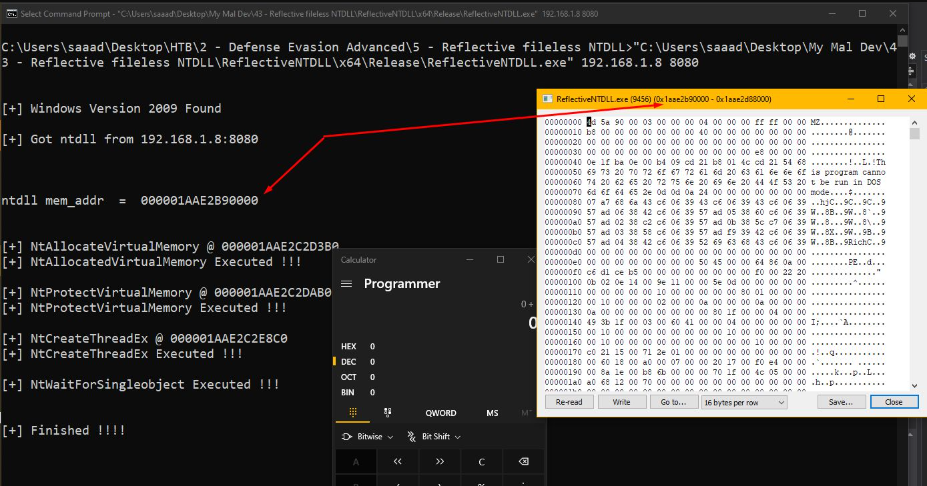
NTDLLReflection preview

NTDLLReflection

GitHubsaadahla/ntdllreflection

通过基于 Windows ReleaseID 从远程服务器在内存中加载反射式 Ntdll 来绕过用户态 EDR 钩子,从而避免打开 ntdll 的句柄,并从导出表中触发导出的 API
ids-ips-evasionpost-exploitationred-teaming+1
3083年前
SilentButDeadly preview

SilentButDeadly

GitHubloosehose/silentbutdeadly

SilentButDeadly 是一款网络通信阻断器,专门设计用于通过 Windows 过滤平台(WFP)阻止 EDR/AV 软件的云连接,从而使其失效。此版本仅专注于网络隔离,不涉及进程终止。


defensive-toolsprivilege-escalationexploitation+7
45511个月前
上一页1…121314…37下一页