#1

 atlasvector/kestra-cve-2026-53576
End-to-end reproduction and cross-layer detection of CVE-2026-53576, the unauthenticated RCE in Kestra - taken past the base PoC to show how a common…
 pwnvader/cve-2026-88877-poc-pwnvader
CVE-2026-88877 的概念验证与可复现实验环境,该漏洞是 Traefik ingress-nginx 通过 from-to-www-redirect 实现的认证绕过,并带有只读检查模式。
 mondoohq/cnspec
一个开源、云原生安全工具,保护从构建到运行时的所有环节
 joaovicdev/exploit-cve-2026-33634
故意存在漏洞的 Docker 实验环境,复现 CVE-2026-33634:LiteLLM 网关通过 api_base 的 SSRF 以及被植入木马的依赖,并包含用于凭据窃取的多阶段利用。
 joaovicdev/exploit-cve-2026-87902
针对 CVE-2026-87902 的漏洞实验环境(Docker)+ Python PoC —— WordPress Core 中未经身份验证的路径遍历(page-template -> LFI -> 条件性 RCE)。仅限教育/授权用途。
 mc493/linux-kernel-zero-day-mitigation-zero-downtime-kernel-defense-
Zero-downtime Linux kernel zero-day defense case study. For the automated CLI and dual-witness notary framework, see mc493/kshield.
 owasp/owasp-ctf-in-a-box
自托管 OWASP CTF 套件:一台机器、一个免费的 GitHub 组织、无云依赖
 saina15/cve-2020-14343-lab
Controlled vulnerability research and reproduction lab for CVE-2020-14343 in PyYAML
 mingqizhang7710/cve-2022-0847-poc-dockerimage
Docker 镜像,打包了 CVE-2022-0847(Dirty Pipe)的概念验证漏洞利用程序,这是一个 Linux 内核权限提升漏洞。
 abhaybansal16/cve-2025-55182-lab
基于 Docker 的实验环境,复现 CVE-2025-55182(React2Shell),即 React Server Components Flight Protocol 中的未授权 RCE 漏洞,包含 PoC 利用脚本及修复版本对比。
 amulyakaushik/cve-2023-27163-lab
基于 Docker 的实验环境,复现 Request-Baskets 中的 CVE-2023-27163 SSRF 漏洞,包含利用验证、检测脚本和网络隔离修复措施。
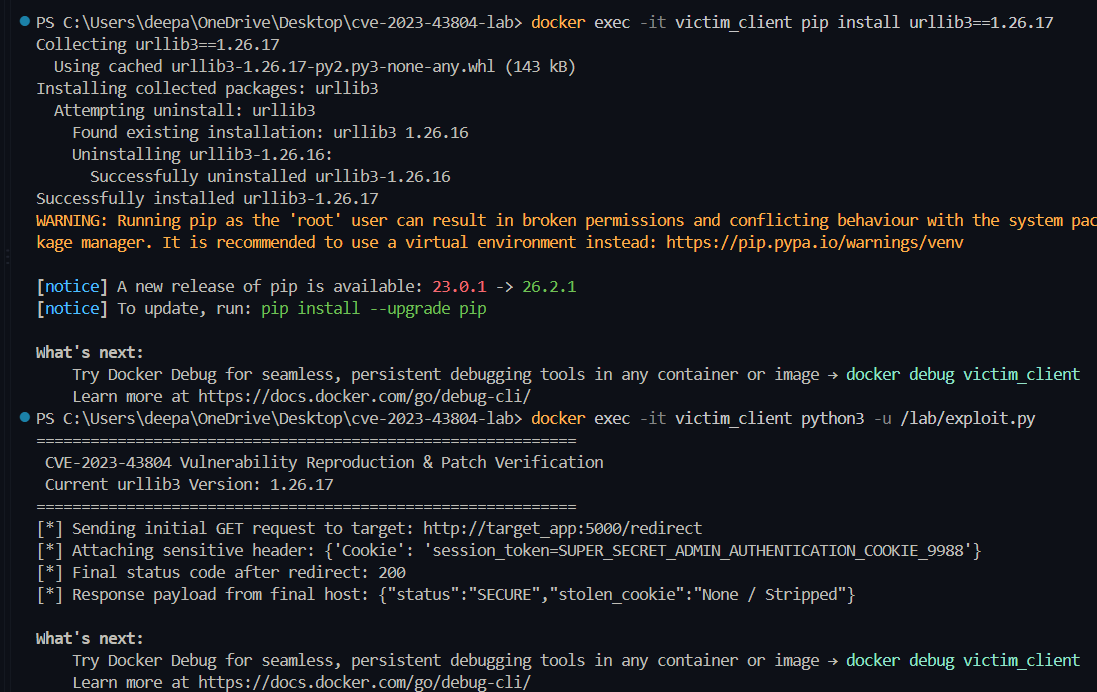 deepanshu-khurana/cve-2023-43804
容器化三层实验环境,通过跨源重定向复现 CVE-2023-43804 urllib3 cookie 泄露,包含漏洞利用脚本和补丁验证。
 shambhavim18/cve-2019-15107-lab
基于Docker的实验室,演示CVE-2019-15107,即Webmin未认证RCE漏洞,涵盖部署、利用、检测和修复。
 shivamg2004/-ine_shivam_gupta_23104003
CVE-2021-43798 Grafana 未授权路径遍历 - 安全实验室 | Shivam Gupta | 23104003
 alixiacf/hpim-training-lab
Trained to Escalate: Forensic Analysis and Local Replication of RLHF-Induced Privilege Escalation in AI Agents (CVE-2026-65616)
 damnkrishna/cve-2025-32433-lab
A Flaw in SSH protocol message handling, a malicious actor could gain unauthorized access to affected systems and execute arbitrary commands without…
 markakd/container_escape
Container escape proof-of-concept exploits for CVE-2026-80521 and CVE-2026-52910, with a disposable QEMU/Ubuntu VM harness for safe PoC execution.