 bunnybuzz/enigma
Native C++ reverse-engineering engine with disassembly, decompilation, and analysis pipeline for PE/ELF binaries, featuring interactive GUI and Ghidra-compatible decompiler.

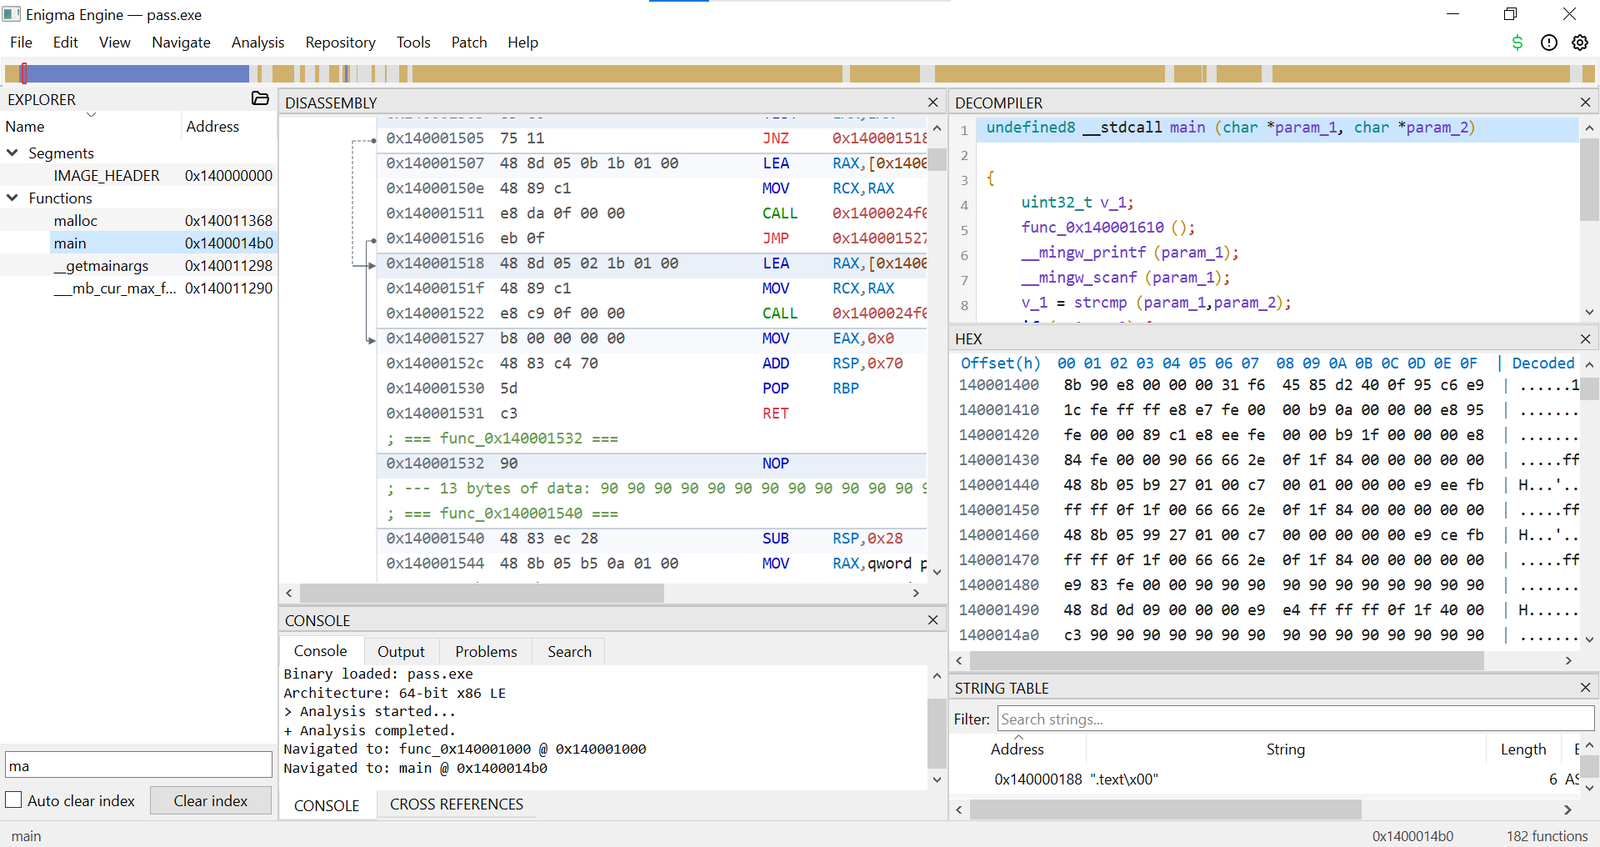
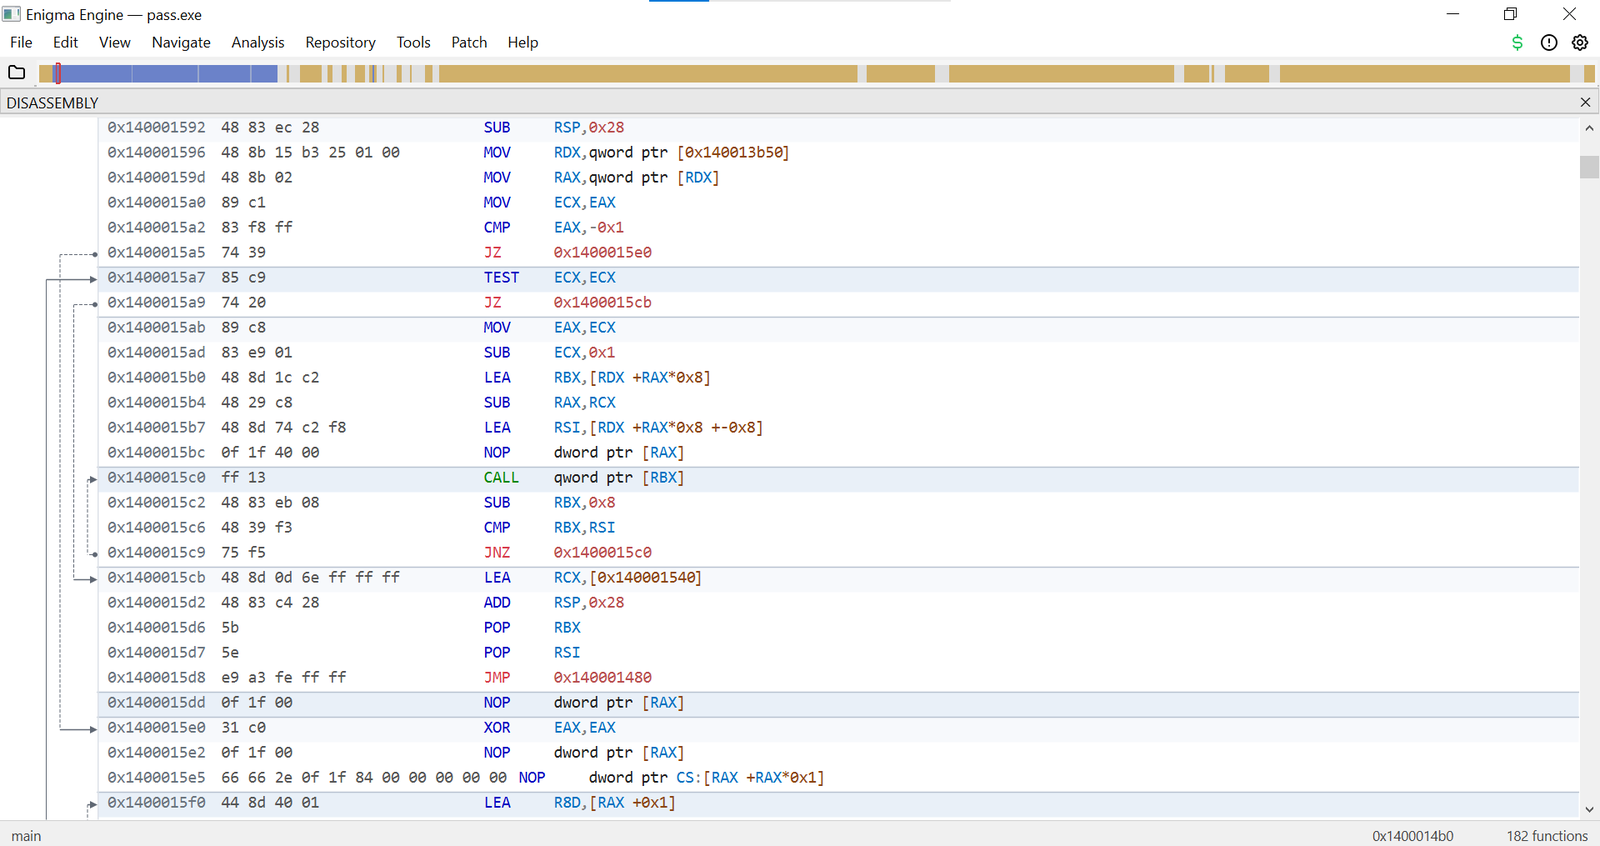
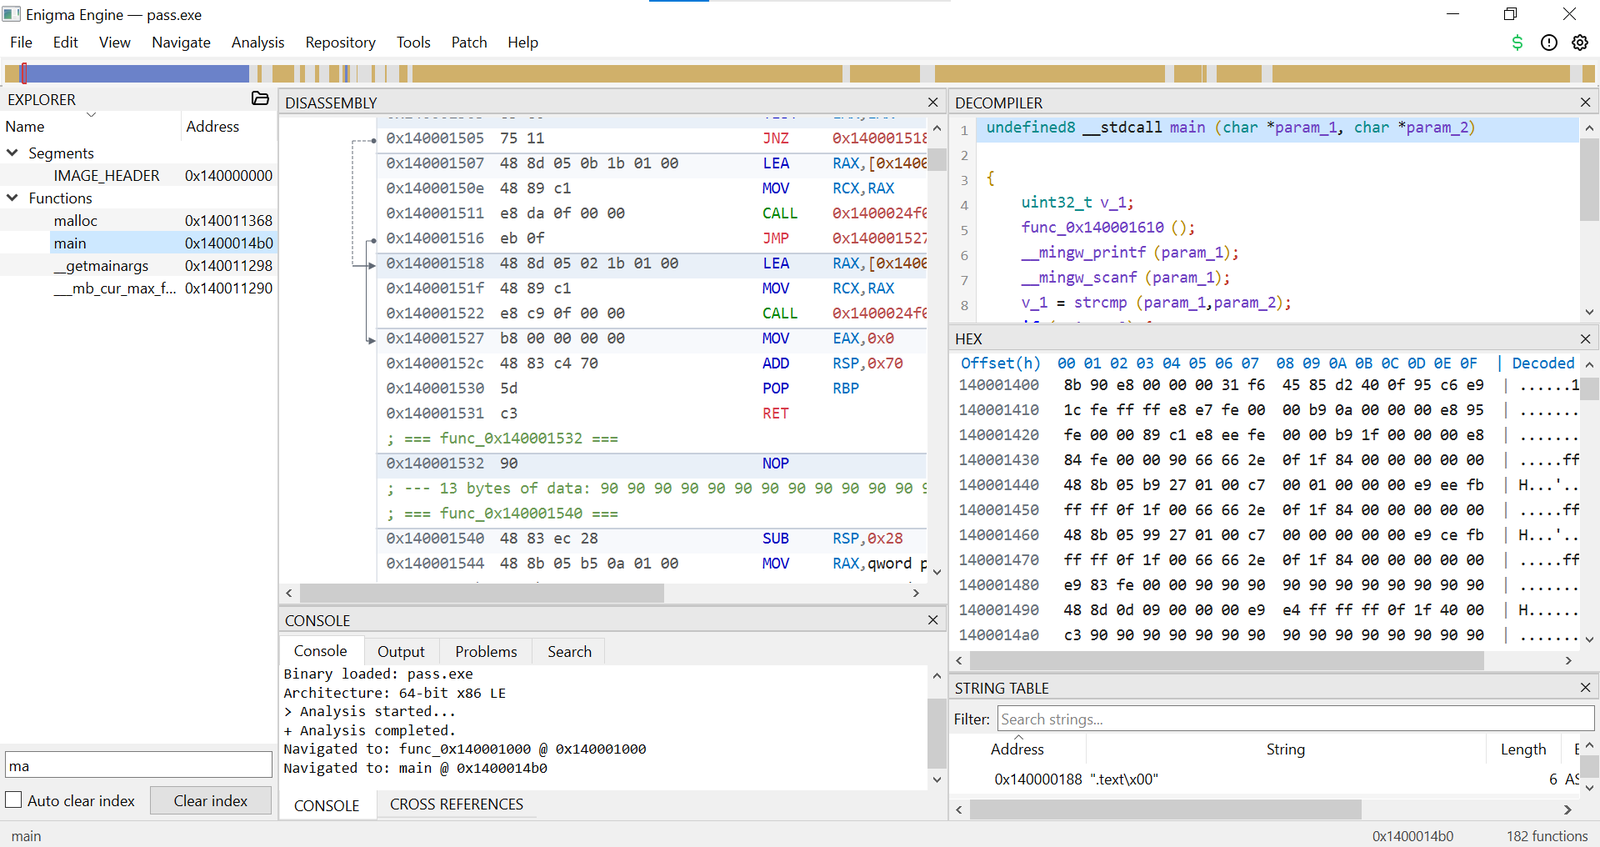
A native C++ reverse-engineering engine inspired by Ghidra's analysis pipeline.
Enigma removes the JVM dependency and provides a standalone analysis core that can be embedded, extended, and integrated directly with native tools and AI systems.
Enigma is under active development and already has a functional end-to-end analysis pipeline.
.gzf import pathThe core pipeline is stable, and the current work focuses on expanding feature coverage, improving engine/GUI integration, and closing remaining capability gaps identified during Ghidra 12.1.3 parity testing.
Binary (PE / ELF)
        │
        ▼
Binary Loader
        │
        ▼
Capstone Disassembler
        │
        ▼
Pcode / Decompiler Engine
        │
        ▼
Analysis Pipeline
        │
        ├── Function Detection
        ├── Type Recovery
        ├── Symbols
        ├── References
        └── Other Analyses
        │
        ▼
Program Model
        │
        ├── Functions
        ├── Symbols
        ├── Types
        ├── Memory
        └── References
        │
        ▼
Storage
        │
        ├── FlatBuffers snapshots
        ├── LMDB index
        └── Git-like commits / branches
        │
        ▼
Qt GUI
        │
        ├── Disassembly
        ├── Decompiler
        ├── Hex View
        ├── CFG / Call Graph
        └── Explorers
| Component | Source |
|---|---|
| Decompiler engine | Ghidra native C++ decompiler library |
| Sleigh processor specifications | Ghidra |
| Program model | Native Enigma C++ implementation |
| Type and memory systems | Native Enigma C++ implementation |
| Analysis pipeline | Native Enigma C++ implementation |
| Function detection | Native Enigma implementation |
| Binary loaders | Native Enigma implementation |
| Storage | Native Enigma implementation |
| GUI | Native Qt6 implementation |
Enigma uses Ghidra components where they provide the required low-level analysis technology, while the surrounding engine architecture is implemented natively in C++.
git clone https://github.com/adam-040/Enigma.git
cd Enigma/enigma-engine

cmake -B build -G Ninja -DCMAKE_BUILD_TYPE=Release
cmake --build build
Enigma is no longer only a prototype analysis core. The native pipeline, storage layer, analysis systems, and GUI are operational.
Current development is focused on expanding the engine's capabilities and connecting functionality that already exists in the backend to the GUI, while implementing the remaining gaps identified during parity analysis.
This project is licensed under the Apache License 2.0.
Third-party components used by Enigma remain subject to their respective licenses.
