 target/strelka
Escaneamento de arquivos em tempo real, baseado em contêineres, em escala empresarial.

<h1 align="center">
<img src="https://assets.kitploit.com/production/public/readmes/2436/2065ad071dd20cf7e35ddddfba0598d78452e4670e89342eed6f7a190a0a1fcb.png" alt="Banner Strelka" />
</h1>
<div align="center">
[Lançamentos][release] | [Documentação][wiki] | [Pull Requests][pr] | [Issues][issues]
[![GitHub release][img-version-badge]][repo] [![Build Status][img-actions-badge]][actions-ci] [![Pull Requests][img-pr-badge]][pr] [![Slack][img-slack-badge]][slack] [![License][img-license-badge]][license]
</div>
Strelka é um sistema de varredura de arquivos em tempo real, baseado em contêineres, usado para caça a ameaças, detecção de ameaças e resposta a incidentes. Originalmente baseado no design estabelecido pelo [Laika BOSS](https://github.com/lmco/laikaboss) da Lockheed Martin e projetos similares (veja: [projetos relacionados](#related-projects)), o Strelka tem como objetivo realizar extração de arquivos e coleta de metadados em escala empresarial.
O Strelka difere de seus projetos irmãos em alguns aspectos significativos:
* O código-fonte principal é Go e Python3.10+
* Os componentes do servidor rodam em contêineres para facilidade e flexibilidade de implantação
* Aplicativos clientes nativos do SO para Windows, Mac e Linux
* Construído usando [bibliotecas e formatos](#architecture) que permitem suporte multiplataforma e multilinguagem
## Recursos
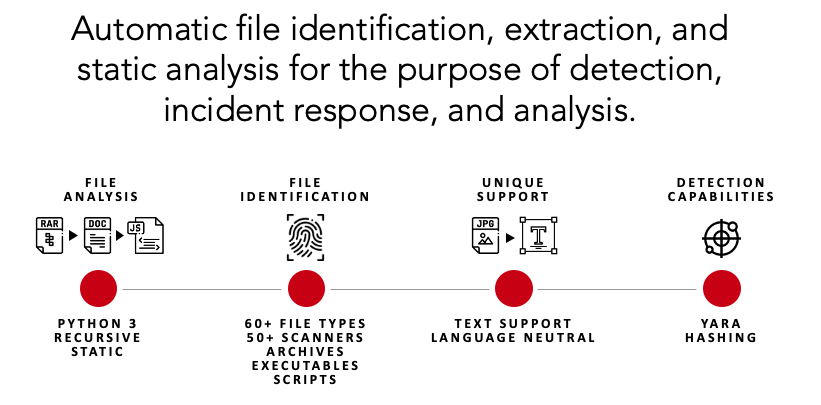
Strelka é uma plataforma modular de varredura de dados, permitindo que usuários ou sistemas enviem arquivos com o objetivo de analisar, extrair e relatar conteúdo e metadados de arquivos. Combinado com um [SIEM](https://en.wikipedia.org/wiki/Security_information_and_event_management), o Strelka é capaz de agregar, alertar e fornecer aos analistas a capacidade de entender melhor seu ambiente sem ter que realizar coleta direta de dados ou análise demorada de arquivos.
## Início rápido
Executar um arquivo através do Strelka é simples. Nesta seção, as capacidades de extração e análise do Strelka são demonstradas para uma análise única.
*Por favor, revise a [documentação](https://target.github.io/strelka/) para detalhes sobre como construir e implantar corretamente o Strelka em um ambiente empresarial.*
#### Passo 1: Instalar pré-requisitos
```bash
# Ubuntu 23.04
sudo apt install -y wget git docker docker-compose golang jq && \
sudo usermod -aG docker $USER && \
newgrp docker
````
#### Passo 2: Baixar o Strelka
```bash
git clone https://github.com/target/strelka.git && \
cd strelka
```
#### Passo 3: Baixar e instalar regras yara preferidas (opcional)
```bash
rm configs/python/backend/yara/rules.yara && \
git clone https://github.com/Yara-Rules/rules.git configs/python/backend/yara/rules/ && \
echo 'include "./rules/index.yar"' > configs/python/backend/yara/rules.yara
```
#### Passo 4a: Baixar imagens pré-compiladas e iniciar o Strelka
**Nota**: Você pode pular o processo `go build` e usar a `Interface do Strelka` em `http://0.0.0.0:9980` para analisar arquivos.
```bash
docker compose -f build/docker-compose-no-build.yaml up -d && \
go build github.com/target/strelka/src/go/cmd/strelka-oneshot
```
#### Passo 4b: Construir e iniciar o Strelka
**Nota**: Você pode pular o processo `go build` e usar a `Interface do Strelka` em `http://0.0.0.0:9980` para analisar arquivos.
```bash
docker compose -f build/docker-compose.yaml build && \
docker compose -f build/docker-compose.yaml up -d && \
go build github.com/target/strelka/src/go/cmd/strelka-oneshot
```
#### Passo 5: Preparar um arquivo para analisar
Use qualquer amostra de malware, ou outro arquivo que você gostaria que o Strelka analisasse.
```bash
wget https://github.com/ytisf/theZoo/raw/master/malware/Binaries/Win32.Emotet/Win32.Emotet.zip -P samples/
```
#### Passo 6: Analisar o arquivo com o Strelka usando o oneshot dockerizado
```bash
./strelka-oneshot -f samples/Win32.Emotet.zip -l - | jq
```
#### O que está acontecendo aqui?
1. O Strelka determinou que o arquivo enviado era um ZIP criptografado (Veja: [taste.yara](https://github.com/target/strelka/blob/master/configs/python/backend/taste/taste.yara) [backend.yaml](https://github.com/target/strelka/blob/master/configs/python/backend/backend.yaml))
2. [ScanEncryptedZip](https://github.com/target/strelka/blob/master/src/python/strelka/scanners/scan_encrypted_zip.py) usou um dicionário para quebrar a senha do arquivo ZIP e extrair o arquivo comprimido
3. O arquivo extraído foi enviado de volta ao pipeline do Strelka pelo scanner, e o Strelka determinou que o arquivo extraído era um EXE
4. [ScanPe](https://github.com/target/strelka/blob/master/src/python/strelka/scanners/scan_pe.py) dissecou o arquivo EXE e adicionou metadados úteis à saída
5. [ScanYara](https://github.com/target/strelka/blob/master/src/python/strelka/scanners/scan_yara.py) analisou o arquivo EXE, usando as regras fornecidas, e adicionou numerosas correspondências à saída, algumas indicando que o arquivo pode ser malicioso
*A seguinte saída foi editada para brevidade.*
```json
{
"file": {
"depth": 0,
"flavors": {
"mime": ["application/zip"],
"yara": ["encrypted_zip", "zip_file"]
},
"scanners": [
"ScanEncryptedZip",
"ScanEntropy",
"ScanFooter",
"ScanHash",
"ScanHeader",
"ScanYara",
"ScanZip"
]
},
"scan": {
"encrypted_zip": {
"cracked_password": "infected",
"elapsed": 0.114269,
"total": {"extracted": 1, "files": 1}
}
}
}
```
```json
{
"file": {
"depth": 1,
"flavors": {
"mime": ["application/x-dosexec"],
"yara": ["mz_file"]
},
"name": "29D6161522C7F7F21B35401907C702BDDB05ED47.bin",
"scanners": [
"ScanEntropy",
"ScanFooter",
"ScanHash",
"ScanHeader",
"ScanPe",
"ScanYara"
]
},
"scan": {
"pe": {
"address_of_entry_point": 5168,
"base_of_code": 4096,
"base_of_data": 32768,
"checksum": 47465,
"compile_time": "2015-03-31T08:53:51",
"elapsed": 0.013076,
"file_alignment": 4096,
"file_info": {
"company_name": "In CSS3",
"file_description": "Note: In CSS3, the text-decoration property is a shorthand property for text-decoration-line, text-decoration-color, and text-decoration-style, but this is currently.",
"file_version": "1.00.0065",
"fixed": {"operating_systems": ["WINDOWS32"]},
"internal_name": "Callstb",
"original_filename": "NOFAstb.exe",
"product_name": "Goodreads",
"product_version": "1.00.0065",
"var": {"character_set": "Unicode", "language": "U.S. English"}
}
},
"yara": {
"elapsed": 0.068918,
"matches": [
"SEH__vba",
"SEH_Init",
"Big_Numbers1",
"IsPE32",
"IsWindowsGUI",
"HasOverlay",
"HasRichSignature",
"Microsoft_Visual_Basic_v50v60",
"Microsoft_Visual_Basic_v50",
"Microsoft_Visual_Basic_v50_v60",
"Microsoft_Visual_Basic_v50_additional",
"Microsoft_Visual_Basic_v50v60_additional"
],
"tags": [
"AntiDebug",
"SEH",
"Tactic_DefensiveEvasion",
"Technique_AntiDebugging",
"SubTechnique_SEH",
"PECheck",
"PEiD"
]
}
}
}
```
#### E agora?
Se o Strelka estivesse implantado e ingerindo arquivos em seu ambiente, você poderia estar coletando esses eventos em seu SIEM. Com essa análise, você poderia escrever uma regra que procura por eventos correspondentes às tags yara suspeitas, alertando sobre um arquivo potencialmente malicioso.
```
scan.yara.tags:("Technique_AntiDebugging" && "SubTechnique_SEH")
```
## Interface Fileshot
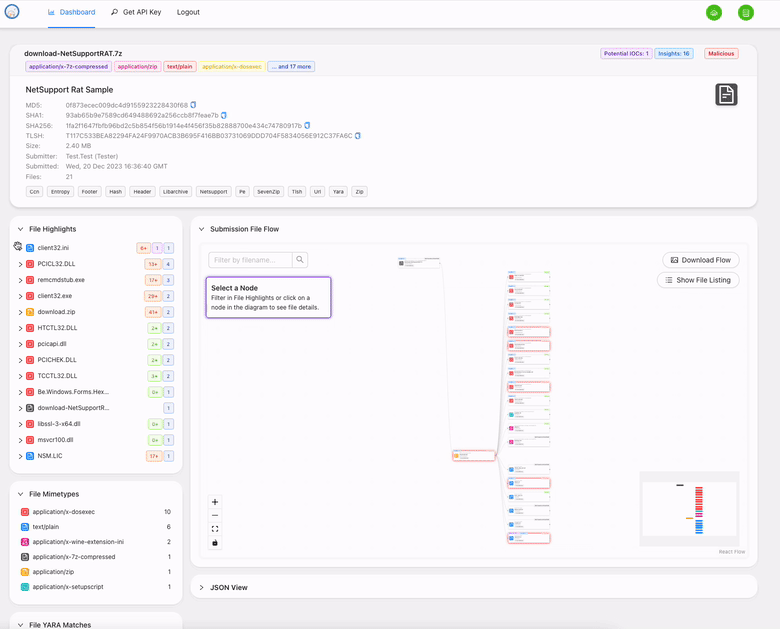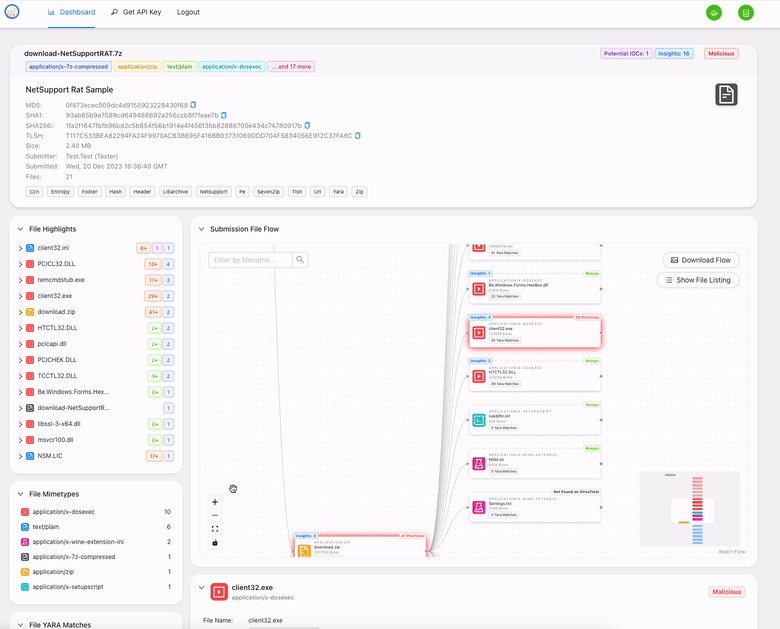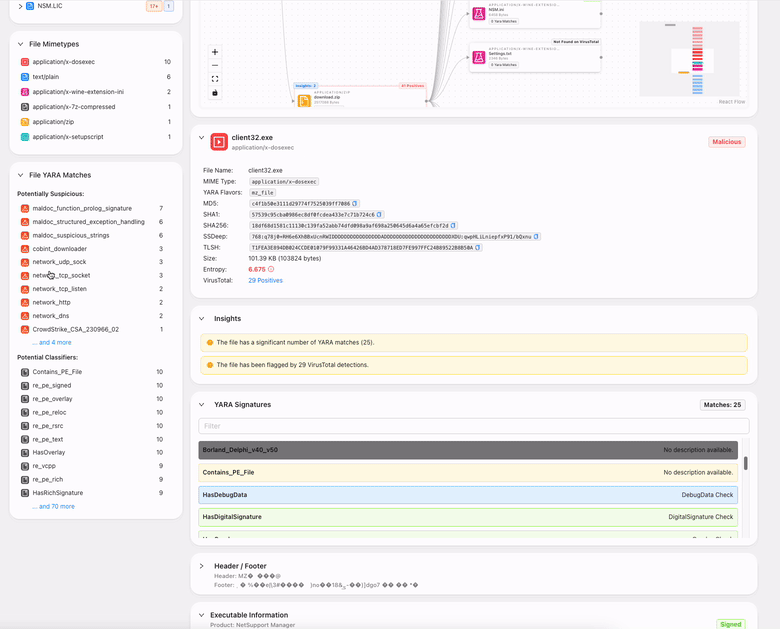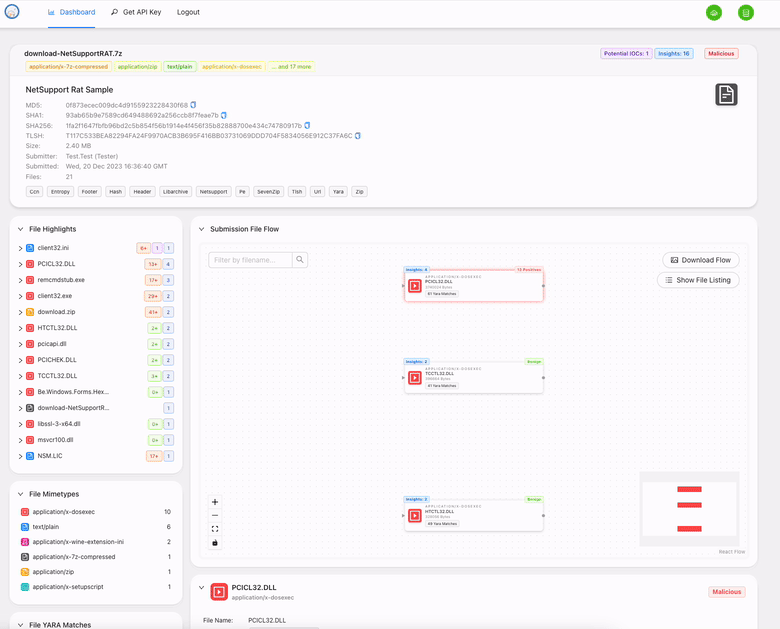
A [Interface do Strelka](https://github.com/target/strelka-ui) está disponível quando você constrói os contêineres fornecidos. Esta interface web permite que você faça upload de arquivos para o Strelka e capture os eventos, que são armazenados localmente.
Navegue até http://localhost:9980/ e use o login strelka/strelka.
## Usos Potenciais
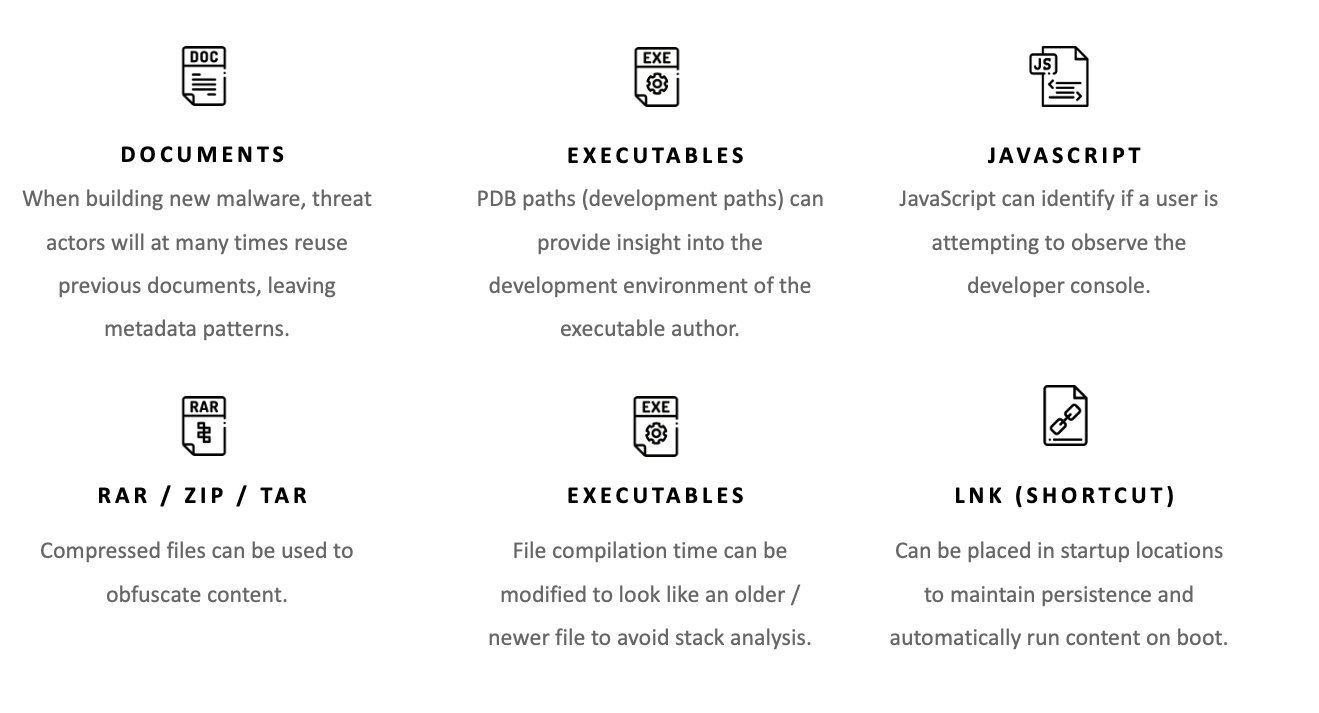
Com mais de 50 scanners de arquivos para os tipos de arquivos mais comuns (ex.: exe, docx, js, zip), o Strelka oferece aos usuários a capacidade de obter novos insights sobre arquivos em seu host, rede ou empresa. Embora o Strelka *não seja* um mecanismo de detecção por si só (embora utilize [YARA](https://virustotal.github.io/yara/)), ele pode fornecer metadados suficientes para identificar arquivos suspeitos ou maliciosos. Alguns usos potenciais para o Strelka incluem:
## Documentação Adicional
Mais documentação sobre o Strelka pode ser encontrada no [README](https://target.github.io/strelka/), incluindo:
- [Instalação](https://target.github.io/strelka/#/?id=installation)
- [Implantação](https://target.github.io/strelka/#/?id=deployment)
- [Design](https://target.github.io/strelka/#/?id=design)
- [Arquitetura](https://target.github.io/strelka/#/?id=architecture)
- [FAQ](https://target.github.io/strelka/#/?id=frequently-asked-questions)
## Contribua
Diretrizes para contribuição podem ser encontradas [aqui](https://github.com/target/strelka/blob/master/CONTRIBUTING.md).
## Problemas Conhecidos
### Problemas ao Carregar Regras YARA
Recomenda-se que os usuários pré-compilem suas regras YARA para desempenho ideal e para evitar possíveis problemas durante a execução.
Usar arquivos YARA pré-compilados ajuda a reduzir o tempo de carregamento e o uso de recursos, especialmente em ambientes com um grande
conjunto de regras. Certifique-se de usar a [opção compilada na configuração do Strelka](https://github.com/target/strelka/blob/master/configs/python/backend/backend.yaml)
para apontar para o arquivo de regras pré-compilado.
### Outros Problemas
Veja [issues marcadas como `bug`](https://github.com/target/strelka/issues?q=is%3Aissue+is%3Aopen+label%3Abug) no rastreador para quaisquer problemas adicionais.
## Projetos Relacionados
* [Laika BOSS](https://github.com/lmco/laikaboss)
* [File Scanning Framework](https://github.com/EmersonElectricCo/fsf)
* [Assemblyline](https://cybercentrecanada.github.io/assemblyline4_docs/)
## Licenciamento
O Strelka e seu código associado são liberados sob os termos da [Licença Apache 2.0](https://github.com/target/strelka/blob/master/LICENSE).
<div align="center">
<img src="https://assets.kitploit.com/production/public/readmes/2436/1bbf5d22a15b9058f400fdd15b49dc4bbca672a6e4ad5bd4773998390025305b.png" alt="Banner Target" />
</div>
<!--
Links
-->
[release]:https://github.com/target/strelka/releases/latest "Último Lançamento do Strelka ➶"
[issues]:https://github.com/target/strelka/issues "Issues do Strelka ➶"
[pull-requests]:https://github.com/target/strelka/pulls "Pull Requests do Strelka ➶"
[wiki]:https://target.github.io/strelka/#/ "Documentação do Strelka ➶"
[repo]:https://github.com/target/strelka "Repositório do Strelka ➶"
[slack]:https://join.slack.com/t/cfc-open-source/shared_invite/zt-e54crchh-a6x4iDy18D5lVwFKQoEeEQ "Slack (link externo) ➶"
[actions-ci]:https://github.com/target/strelka/actions/workflows/build_strelka_nightly.yml "Github Actions ➶"
[pr]:https://github.com/target/strelka/pulls "Pull Requests do Strelka ➶"
[license]:https://raw.githubusercontent.com/target/strelka/master/LICENSE "Arquivo de Licença do Strelka ➶"
[docker]:https://www.docker.com/ "Docker (link externo) ➶"
<!--
Badges
-->
[img-version-badge]:https://img.shields.io/github/release/target/strelka.svg?style=for-the-badge
[img-slack-badge]:https://img.shields.io/badge/slack-join-red.svg?style=for-the-badge&logo=slack
[img-actions-badge]:https://img.shields.io/github/actions/workflow/status/target/strelka/build_strelka_nightly.yml?branch=master&style=for-the-badge
[img-pr-badge]:https://img.shields.io/badge/PRs-welcome-orange.svg?style=for-the-badge&logo=data:image/svg+xml;base64,PD94bWwgdmVyc2lvbj0iMS4wIiBlbmNvZGluZz0iVVRGLTgiPz48c3ZnIGlkPSJzdmcyIiB3aWR0aD0iNjQ1IiBoZWlnaHQ9IjU4NSIgdmVyc2lvbj0iMS4wIiB4bWxucz0iaHR0cDovL3d3dy53My5vcmcvMjAwMC9zdmciPiA8ZyBpZD0ibGF5ZXIxIj4gIDxwYXRoIGlkPSJwYXRoMjQxNyIgZD0ibTI5Ny4zIDU1MC44N2MtMTMuNzc1LTE1LjQzNi00OC4xNzEtNDUuNTMtNzYuNDM1LTY2Ljg3NC04My43NDQtNjMuMjQyLTk1LjE0Mi03Mi4zOTQtMTI5LjE0LTEwMy43LTYyLjY4NS01Ny43Mi04OS4zMDYtMTE1LjcxLTg5LjIxNC0xOTQuMzQgMC4wNDQ1MTItMzguMzg0IDIuNjYwOC01My4xNzIgMTMuNDEtNzUuNzk3IDE4LjIzNy0zOC4zODYgNDUuMS02Ni45MDkgNzkuNDQ1LTg0LjM1NSAyNC4zMjUtMTIuMzU2IDM2LjMyMy0xNy44NDUgNzYuOTQ0LTE4LjA3IDQyLjQ5My0wLjIzNDgzIDUxLjQzOSA0LjcxOTcgNzYuNDM1IDE4LjQ1MiAzMC40MjUgMTYuNzE0IDYxLjc0IDUyLjQzNiA2OC4yMTMgNzcuODExbDMuOTk4MSAxNS42NzIgOS44NTk2LTIxLjU4NWM1NS43MTYtMTIxLjk3IDIzMy42LTEyMC4xNSAyOTUuNSAzLjAzMTYgMTkuNjM4IDM5LjA3NiAyMS43OTQgMTIyLjUxIDQuMzgwMSAxNjkuNTEtMjIuNzE1IDYxLjMwOS02NS4zOCAxMDguMDUtMTY0LjAxIDE3OS42OC02NC42ODEgNDYuOTc0LTEzNy44OCAxMTguMDUtMTQyLjk4IDEyOC4wMy01LjkxNTUgMTEuNTg4LTAuMjgyMTYgMS44MTU5LTI2LjQwOC0yNy40NjF6IiBmaWxsPSIjZGQ1MDRmIi8+IDwvZz48L3N2Zz4=
[img-license-badge]:https://img.shields.io/badge/license-apache-ff69b4.svg?style=for-the-badge&logo=apache
[img-docker-badge]:https://img.shields.io/badge/Supports-Docker-yellow.svg?style=for-the-badge&logo=docker