Skip to content
KitploitKITPLOIT
FerramentasExploitsBlog
Log in
Enviar
FerramentasExploitsBlog
Enviar

Ferramentas de Hacking, PenTest e Cibersegurança para o seu Arsenal de Segurança!

Kitploit é um diretório de ferramentas de hacking, cibersegurança e pentesting. Descubra as últimas atualizações de projetos para encontrar vulnerabilidades, analisar sistemas, automatizar testes e fortalecer sua segurança.

FeedsContatoPrivacidade© 2026 Kitploit

Diretório de Ferramentas

Categorias

Ver todas as categorias
Loading categories
APTs-Adversary-Simulation — This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2 servers, backdoors, exploitation techniques, stagers, bootloaders, and other malicious artifacts that mirror those used in real world attacks . | Kitploit
Ferramentas/GitHubGitHub/s3n4t0r-0x0/apts-adversary-simulation
Privilege EscalationReconnaissancePersistence MechanismsExploitationLateral MovementPost-ExploitationPenetration TestingCommand and ControlLearning & EducationRed TeamingPayload DevelopmentAdversarial Attack
1.1k19044há 3 diasRevisado pelo Kitploit

Mais Populares

Ver todos →

Descubra as ferramentas mais usadas pela nossa comunidade.

Explore todas as ferramentas

Navegue pela nossa coleção de ferramentas

Ver todas as ferramentas →

Sobre

This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, C2 servers, backdoors, exploitation techniques, stagers, bootloaders, and other malicious artifacts that mirror those used in real world attacks .

GitHubs3n4t0r-0x0/apts-adversary-simulation
APTs-Adversary-Simulation

Ver Repositório
Compartilhar
Conteúdo não disponível no idioma solicitado. Mostrando versão em inglês.

APTs Adversary Simulation

Adversary Simulation APT Simulation MITRE ATT&CK TTPs Red Team

A comprehensive collection of simulated Advanced Persistent Threat (APT) attacks based on real world tactics, techniques, and procedures (TTPs) used by state sponsored APT Groups from Russia, China, Iran, and North Korea
hollywood-Comp-02

[!CAUTION] Important Notice: This project is strictly for educational, research, and defensive security purposes only. Unauthorized use of these techniques may violate laws and result in serious legal consequences.

🧠 Overview

This repository contains detailed adversary simulation APT campaigns targeting various critical sectors. Each simulation includes custom tools, command and control (C2) servers, backdoors, exploitation techniques, stagers, bootloaders, and other malicious artifacts that mirror those used in real world attacks. The simulations are based on extensive research from leading cybersecurity firms, including PaloAlto Unit42, Kaspersky, Microsoft, Cisco, Trellix, CrowdStrike, and WithSecure.

Learn More About the Importance and Outcomes of the Experience:

  • Why Adversary Simulation? - Understanding the strategic value of simulating advanced threats
  • Adversary Simulation VS Adversary Emulation - Key differences and when to use each approach
  • How do I simulate an APT - Adversary Simulation Is Not a Methodology It's the Outcome of Experience

🎯 Simulated APT Groups

Note: APT group names in this repository follow the naming conventions used by different security vendors. The same APT group may have different names depending on the vendor (e.g., Mandiant, CrowdStrike, Microsoft, Kaspersky, etc.).
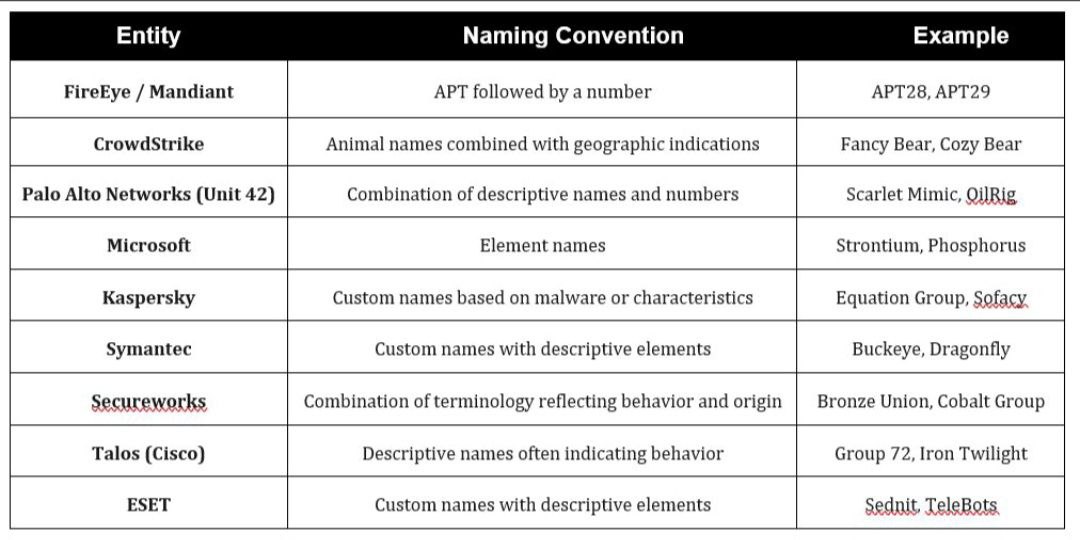
photo_2025-11-09_04-26-38

Below is the complete list of simulated APT Groups:

Country
of Origin
Russia 🇷🇺 China 🇨🇳 North Korea 🇰🇵 Iran 🇮🇷
APT Groups

Cozy Bear
Voodoo Bear
Fancy Bear
Energetic Bear
Berserk Bear
Gossamer Bear
Primitive Bear
Ember Bear
Venomous Bear

Mustang Panda
Wicked Panda
Goblin Panda
Deep Panda
Glacial Panda
Anchor Panda
Samurai Panda
Phantom Panda
Sunrise Panda
Ethereal Panda

Lazarus
Labyrinth Chollima
Velvet Chollima
Famous Chollima
Ricochet Chollima
Silent Chollima

Helix Kitten
Charming Kitten
Static Kitten
Muddy Water
Tracer Kitten
Pioneer Kitten
Nemesis Kitten
Clever Kitten
Pulsar Kitten
Remix Kitten
Haywire Kitten

🛠️ Adversary Framework

All adversary simulations are powered by BEAR-C2 a custom command and control framework designed for realistic threat simulation.
image psd(1)

📫 Contact

Telegram Twitter/X LinkedIn Reddit
Baixar ferramenta