Skip to content
KitploitKITPLOIT
FerramentasExploitsBlog
Log in
Enviar
FerramentasExploitsBlog
Enviar

Ferramentas de Hacking, PenTest e Cibersegurança para o seu Arsenal de Segurança!

Kitploit é um diretório de ferramentas de hacking, cibersegurança e pentesting. Descubra as últimas atualizações de projetos para encontrar vulnerabilidades, analisar sistemas, automatizar testes e fortalecer sua segurança.

FeedsContatoPrivacidade© 2026 Kitploit

Diretório de Ferramentas

Categorias

Ver todas as categorias
Loading categories
prismor — Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt injection, supply chain etc in a local dashboard. Agent agnostic (Claude, codex, langchain etc.) | Kitploit
Ferramentas/GitHubGitHub/prismorsec/prismor
Defensive ToolsContainer SecurityDevSecOpsSecret DetectionThreat IntelligenceSupply Chain SecurityIncident ResponseAI Security
GitHubprismorsec/prismor

prismor

Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt injection, supply chain etc in a local dashboard. Agent agnostic (Claude, codex, langchain etc.)

28326126há 5h 59mRevisado pelo Kitploit
Compartilhar
Ver RepositórioSite
Conteúdo não disponível no idioma solicitado. Mostrando versão em inglês.

Prismor

PyPI License OpenSSF Best Practices PRs Welcome X DeepWiki Discord

Runtime security for Claude Code, Codex, Langchain and other AI agents frameworks/harness.

Prismor is highly customizable based on user's own policies. Observe or enforce mode to see and control agent activity in a local self-serve dashboard

Website • Onboard with Skill

Claude Code   Codex CLI   Gemini CLI   Cursor   GitHub Copilot   OpenCode   Pi Agent   Kiro   Kimi Code   Trae / Trae CN   Google Antigravity

Plus Grok Build, Crush, OpenHands, Qwen Code, Continue CLI, Goose, Hermes, OpenClaw, Devin CLI, Factory Droid, Aider, and more — see AGENT_INTEGRATIONS.md for the full coverage matrix
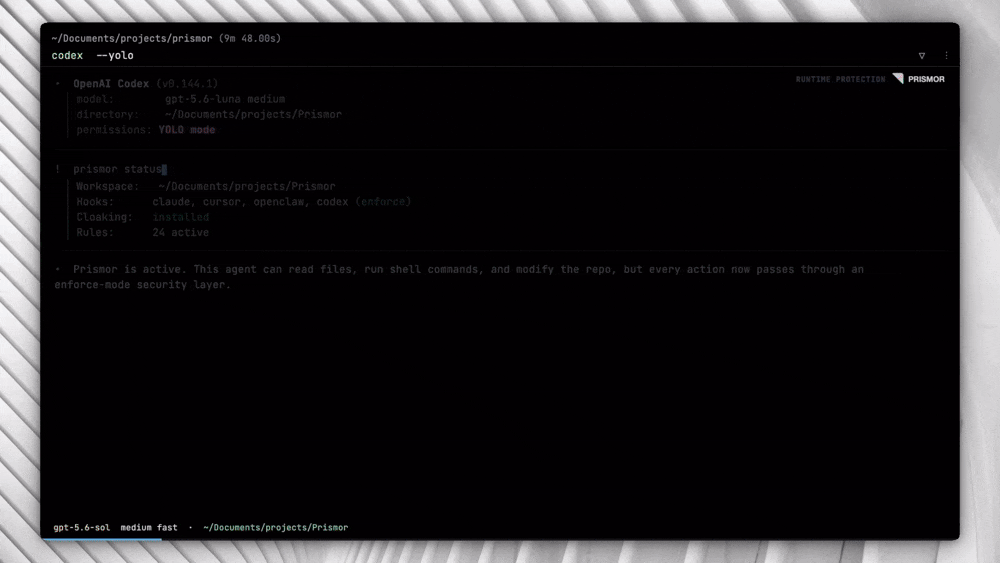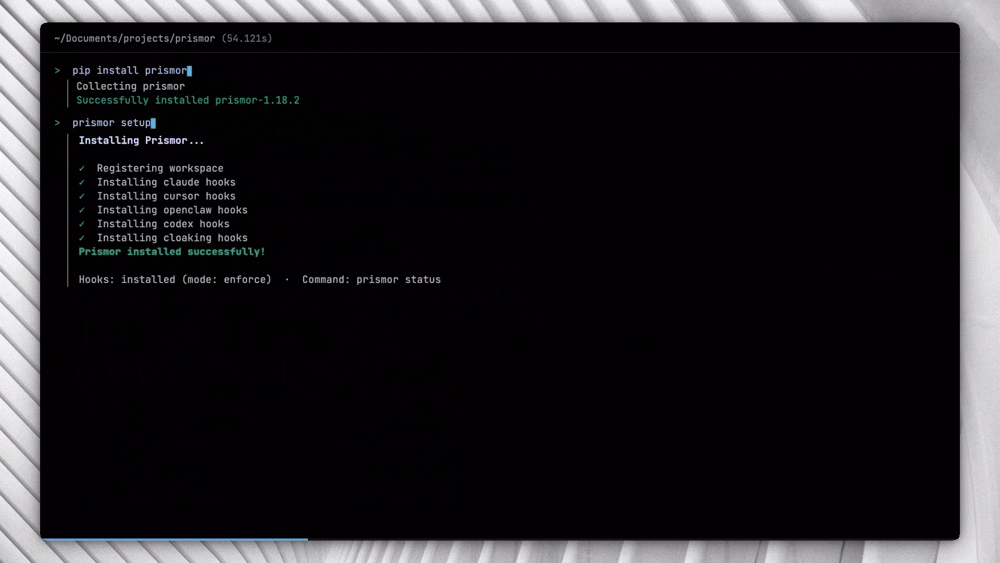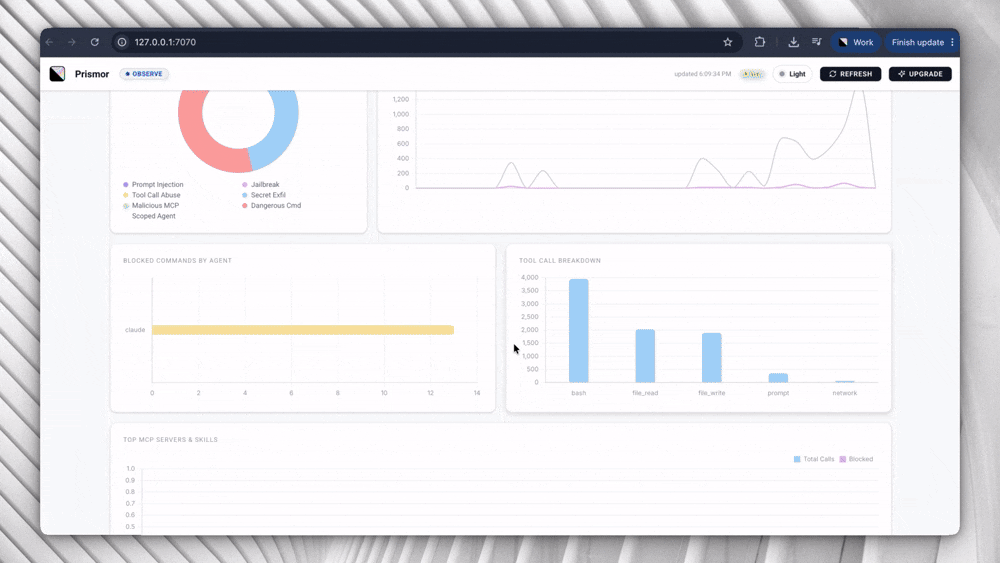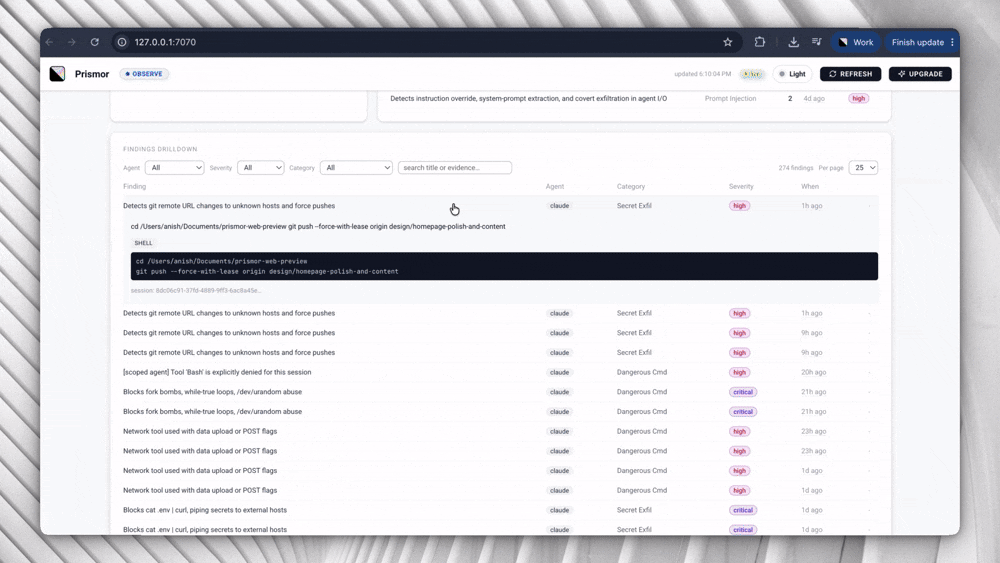

Prismor demo: pip install prismor, prismor setup, then the dashboard's overview, sessions, extensions and MCP servers views


The Problem

AI agents execute shell commands, read and write files, access credentials, and call external APIs. They do this autonomously, often across many steps, with limited checkpoints.

This creates risks that traditional security tooling isn't designed for:

  • Prompt injection - malicious content in a file, issue, or web page can redirect the agent mid-task
  • Unintended destructive actions - an agent misinterprets an instruction and runs something irreversible
  • Secret exfiltration - an agent reads .env or credential files as part of a debugging task and sends the content outbound
  • Lack of visibility and identity - an agent can spawn subagents and lack complete visibility for the end user
  • Privilege escalation - an agent modifies sudoers, CI pipelines, or file permissions to resolve a permission error
  • Dependency manipulation - an agent installs or rewrites a package at the direction of injected input
  • Supply chain risk - an agent installs a vulnerable or 0-day package while optimizing for code velocity

Standard OS-level and endpoint security tools monitor the kernel and filesystem. But they lack the context to make AI usable


Quick Start (30s)

pip install prismor
prismor setup

For the Skill, curl, and git-clone alternatives, plus PEP 668 systems and secret-cloaking setup, see the full installation guide.



Supported Agents

Baixar ferramenta

Mais Populares

Ver todos →

Descubra as ferramentas mais usadas pela nossa comunidade.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 O kit definitivo de OSINT: grafo de investigação, pontuação de confiança, famílias de alias, mapa, linha do tempo e relatórios. 49 módulos, mais de 400 sites, sem necessidade de chaves de API.

    654
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # Aplicativo de Execução em Um Toque GhostLock (CVE-2026-43499)

    490
  • 3

    ARTEX

    baarai/artex

    Plataforma autônoma de testes de penetração multiagente com LLM, com agentes planejador/executor, grafos de ativos e de exploração, registro de tráfego MITM e reteste de vulnerabilidades.

    395
  • 4

    redforge

    cybersecurity91/redforge

    Kit de ferramentas de red team do lado do navegador com 102 ferramentas offline para reconhecimento, geração de payloads, ataques a credenciais, criptografia, codificação e relatórios de engajamento.

    336
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    O sistema de ação para cibersegurança nativa em IA—onde a intenção se torna execução governada, a evidência se torna memória operacional, e cada operação melhora a próxima.

    258
  • 6

    antifox

    antifox-ai/antifox

    Plataforma de testes de penetração autónoma com multiagentes de IA que executa reconhecimento, descoberta de superfície de ataque, validação de exploração e entrega de relatórios com evidências.

    252

Explore todas as ferramentas

Navegue pela nossa coleção de ferramentas

Ver todas as ferramentas →