
Skip to content
KitploitKITPLOIT
FerramentasExploitsBlog
Log in
Enviar
FerramentasExploitsBlog
Enviar

Ferramentas de Hacking, PenTest e Cibersegurança para o seu Arsenal de Segurança!

Kitploit é um diretório de ferramentas de hacking, cibersegurança e pentesting. Descubra as últimas atualizações de projetos para encontrar vulnerabilidades, analisar sistemas, automatizar testes e fortalecer sua segurança.

FeedsContatoPrivacidade© 2026 Kitploit

Diretório de Ferramentas

Categorias

Ver todas as categorias
Loading categories
Anthropic-Credited-CVEs — Tracking Vulnerabilities That Appear to be Credited to the Anthropic Research Team | Kitploit

Ferramentas/GitHubGitHub/patrickmgarrity/anthropic-credited-cves
Vulnerability AnalysisThreat IntelligenceCurated Resources
GitHubpatrickmgarrity/anthropic-credited-cves

Anthropic-Credited-CVEs

Tracking Vulnerabilities That Appear to be Credited to the Anthropic Research Team

Ver Repositório
30450há 12h 34mRevisado pelo Kitploit

Mais Populares

Ver todos →

Descubra as ferramentas mais usadas pela nossa comunidade.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 O kit definitivo de OSINT: grafo de investigação, pontuação de confiança, famílias de alias, mapa, linha do tempo e relatórios. 49 módulos, mais de 400 sites, sem necessidade de chaves de API.

    972
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # Aplicativo de Execução em Um Toque GhostLock (CVE-2026-43499)

    666
  • 3

    looking-glass

    anonghosty/looking-glass

    Plataforma CSIRT que ingere relatórios do Shadowserver no MongoDB e os reproduz como mapas interativos, análises, descobertas, avisos e painéis executivos.

    424
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServer é uma plataforma de código aberto de Gerenciamento de Acesso Privilegiado (PAM) que fornece às equipes de DevOps e TI acesso seguro e sob demanda a endpoints SSH, RDP, Kubernetes, Banco de Dados e RemoteApp através de um navegador web.

    389
  • 5

    SafeLine

    chaitin/safeline

    WAF auto-hospedado e proxy reverso que filtra tráfego HTTP malicioso, bloqueia injeção SQL, XSS e ataques de bots, com limitação de taxa e criptografia dinâmica de HTML/JS.

    337
  • 6

    ARTEX

    baarai/artex

    Plataforma autônoma de testes de penetração multiagente com LLM, com agentes planejador/executor, grafos de ativos e de exploração, registro de tráfego MITM e reteste de vulnerabilidades.

    331

Explore todas as ferramentas

Navegue pela nossa coleção de ferramentas

Ver todas as ferramentas →
Compartilhar
Conteúdo não disponível no idioma solicitado. Mostrando versão em inglês.

ANTHROPIC CVE TRACKER

Overview

Tracking vulnerabilities that credit the Anthropic research team and are possibly discovered by Project Glasswing.

CVEs: 501

GHSAs w/o CVE: 17

Advisories w/o GHSA/CVE: 120

Findings Withdrawn by Anthropic: 415
Distributions

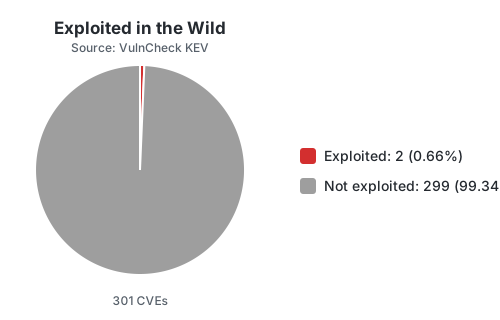
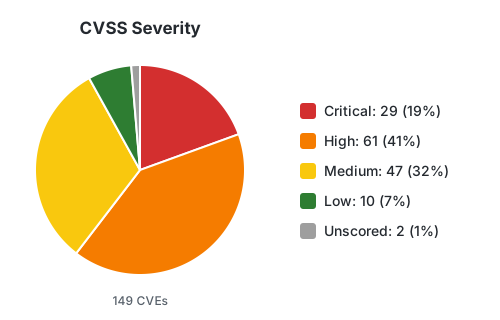
CVSS severity distribution Exploited in the wild (VulnCheck KEV)
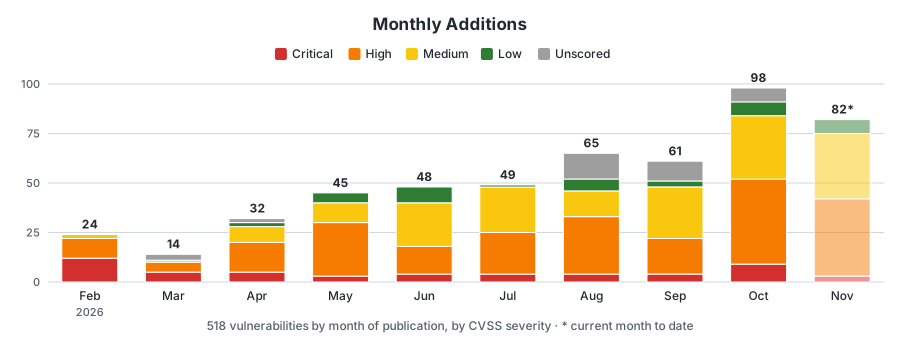
CVEs added per month

Anthropic Research

  • Tracking CVEs Attributed to Anthropic Researchers and Project Glasswing
  • Observations on Anthropic’s Vulnerability Disclosure Ledger
  • Has Anthropic Glasswing Lived Up to the Hype it brought this year?
  • The Anthropic Glasswing Receipts Are Starting to Trickle In
  • After 7-months, Glasswing Overwelms Maintainers with Underwhelming Findings

Add a Vulnerability

If you find an Anthropic credited vulnerability, please open a Pull Request or Send me a message on linkedin or in the Extended Vulnerability Community Discord.

Considerations

This project is maintained on a best effort basis.

The List

Baixar ferramenta