Skip to content
KitploitKITPLOIT
FerramentasExploitsBlog
Log in
Enviar
FerramentasExploitsBlog
Enviar

Ferramentas de Hacking, PenTest e Cibersegurança para o seu Arsenal de Segurança!

Kitploit é um diretório de ferramentas de hacking, cibersegurança e pentesting. Descubra as últimas atualizações de projetos para encontrar vulnerabilidades, analisar sistemas, automatizar testes e fortalecer sua segurança.

FeedsContatoPrivacidade© 2026 Kitploit

Diretório de Ferramentas

Categorias

Ver todas as categorias
Loading categories
kingfisher — Detecte segredos. Valide-os em tempo real. Mapeie o raio de impacto. Revogue rapidamente. Execute a CLI ou integre em Rust, Python ou Node.js. | Kitploit
Ferramentas/GitHubGitHub/mongodb/kingfisher
Análise EstáticaScanners de VulnerabilidadesSegurança de ContêineresAnálise Dinâmica de Código (DAST)Coleta de InformaçõesSegurança na NuvemDevSecOpsUtilitários e FrameworksDetecção de SegredosSegurança da Cadeia de Suprimentos
GitHub
1.3k126178há 2 diasRevisado pelo Kitploit
mongodb/kingfisher

kingfisher

Detecte segredos. Valide-os em tempo real. Mapeie o raio de impacto. Revogue rapidamente. Execute a CLI ou integre em Rust, Python ou Node.js.
Ver RepositórioSite
Compartilhar
Conteúdo não disponível no idioma solicitado. Mostrando versão em inglês.

Detect and Validate Secrets Anywhere. Map Access. Revoke Fast.

Kingfisher Logo
Apache 2.0 License Container downloads
GitHub downloads PyPI downloads

Find leaked secrets. Validate what’s live. Map the blast radius. Revoke fast.

Kingfisher is a fast, free, open-source secret scanner and credential response tool built in Rust. It detects leaked secrets with hundreds of built-in rules, validates which credentials are active, maps access for supported credential types, and revokes supported secrets—all in one Apache-2.0-licensed release:

Detect → Validate → Map → Triage → Revoke

  • scan source code, Git history, cloud storage, container images, archives, and developer platforms
  • validate which credentials are active
  • map a leaked secret's identity, permissions, and reachable resources
  • triage findings in a browser, or output as SARIF, JSON, TOON
  • send real-time alerts to Slack, Microsoft Teams, Discord, Mattermost, Google Chat, or any JSON webhook
  • revoke supported secrets

Defender workflow: Follow the end-to-end defender workflow for secret detection, validation, notifications, blast-radius mapping, and revocation.

Embed Kingfisher in Python, Node.js, or Rust

Add native secret detection, live credential validation, and explicit revocation to your Python, JavaScript/TypeScript (Node.js), or Rust application. The same Rust engine and rule catalog run in-process, with no CLI subprocess required. Kingfisher is an embeddable secret scanner that also runs as a standalone CLI.
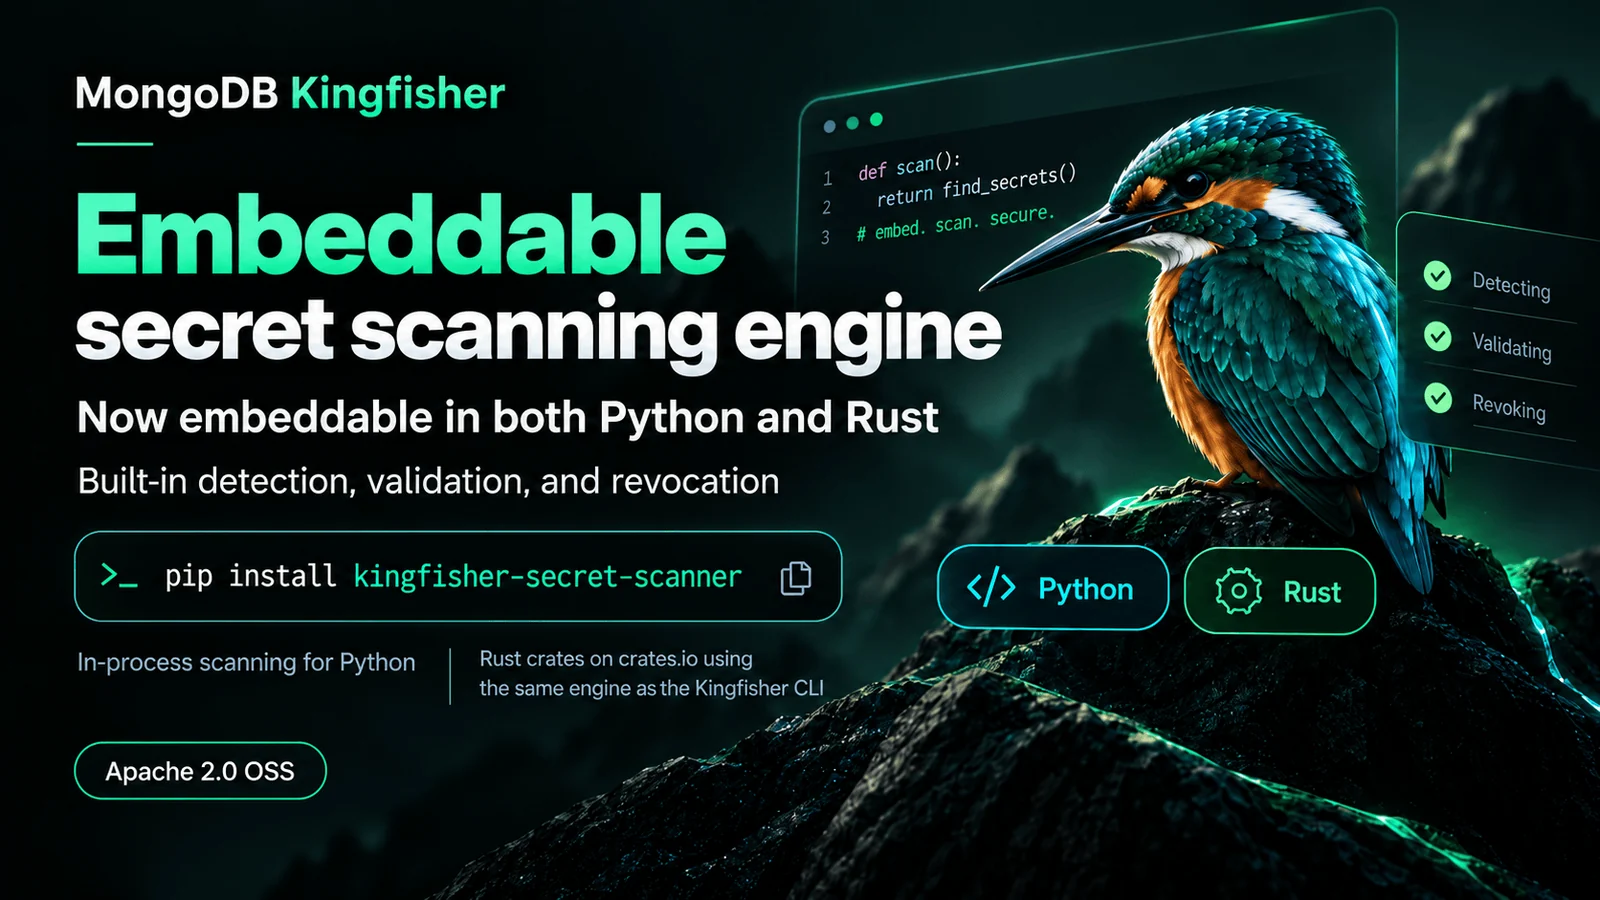
Kingfisher embeddable secret scanner: Detect Secrets → Validate → Map Blast Radius → Revoke. Native Python, Node.js/TypeScript and Rust SDK installs, plus CLI installation and HTML report commands.

Choose your language and add the SDK to your existing application:

  • Python:

    uv add kingfisher-secret-scanner
    

    Import kingfisher_sdk. See the Python SDK guide and runnable examples for scanning, validation, rule inspection, and explicit revocation.

  • Node.js / TypeScript:

    npm install kingfisher-secret-scanner
    

    The stable npm SDK 1.0.0 wraps the same Rust crates with napi-rs. See the Node SDK guide and source/examples. It targets Node.js, including VS Code workspace extensions, rather than browser/WASM runtimes. Explore Kingfisher Workbench, a commented showcase with live progress, Git-history scanning and a redacted HTML report, or start with the runnable recipe walkthrough; maintainers can follow the npm trusted-publishing setup.

  • Rust:

    cargo add kingfisher-scanner --features validation
    

    The validation feature enables live validation and revocation; omit --features validation for detection only. See the library guide, runnable examples, and revocation guide.

Or install the CLI, scan a codebase, and open the interactive HTML report:

uv tool install kingfisher-bin
kingfisher scan /path/to/code --view-report

Replace /path/to/code with your source directory. Scans validate credentials by default; add --no-validate for detection only. Add --blast-radius to map supported credentials' access when authorized. Revocation remains a separate, explicit action. See the CLI installation guide and usage guide for more options.

Scan Targets

Kingfisher handles local files and directories, Git repositories and history, compressed and office-document archives, SQLite databases, Python bytecode, Docker images, source-hosting organizations, cloud object storage, collaboration tools, and API-development platforms.

Files / DirsLocal GitGitHubGitLabAzure ReposBitbucketGiteaHugging Face
Files / Dirs
Files / Dirs
Local Git
Local Git
GitHub
GitHub
GitLab
GitLab
Azure Repos
Azure Repos
Bitbucket
Bitbucket
Gitea
Gitea
Hugging Face
Hugging Face
Baixar ferramenta

Mais Populares

Ver todos →

Descubra as ferramentas mais usadas pela nossa comunidade.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 O kit definitivo de OSINT: grafo de investigação, pontuação de confiança, famílias de alias, mapa, linha do tempo e relatórios. 49 módulos, mais de 400 sites, sem necessidade de chaves de API.

    837
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # Aplicativo de Execução em Um Toque GhostLock (CVE-2026-43499)

    536
  • 3

    ARTEX

    baarai/artex

    Plataforma autônoma de testes de penetração multiagente com LLM, com agentes planejador/executor, grafos de ativos e de exploração, registro de tráfego MITM e reteste de vulnerabilidades.

    424
  • 4

    redforge

    cybersecurity91/redforge

    Kit de ferramentas de red team do lado do navegador com 102 ferramentas offline para reconhecimento, geração de payloads, ataques a credenciais, criptografia, codificação e relatórios de engajamento.

    355
  • 5

    looking-glass

    anonghosty/looking-glass

    Plataforma CSIRT que ingere relatórios do Shadowserver no MongoDB e os reproduz como mapas interativos, análises, descobertas, avisos e painéis executivos.

    294
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    O sistema de ação para cibersegurança nativa em IA—onde a intenção se torna execução governada, a evidência se torna memória operacional, e cada operação melhora a próxima.

    276

Explore todas as ferramentas

Navegue pela nossa coleção de ferramentas

Ver todas as ferramentas →