 xcapri/subdosec
빠르고 정확하며 거짓 긍정(false positive)이 전혀 없는 서브도메인 탈취 스캐너입니다. 취약한 서브도메인을 탐지하고, 메타데이터(IP, CNAME, 제목, 상태 코드)를 수집하며, 정찰을 위한 AI 기반 분석을 제공합니다.

Subdosec
서브도메인 탈취 스캐너 및 정찰 도구.
설치 • 사용법 • 웹 기반 • 기여 • 온라인 스캔 • 감사의 말
Subdosec는 거짓 양성(false positive)이 없는 빠르고 정확한 서브도메인 탈취 스캐너입니다. 취약한 서브도메인의 공개 데이터베이스와 정찰을 위한 상세한 비취약 메타데이터(IP, CNAME, 제목, 상태 코드)를 제공합니다.
subdosec 설치 또는 업그레이드
pipx install git+https://github.com/xcapri/subdosec.git
pipx upgrade subdosec
그런 다음 새 터미널 세션을 시작할 때마다 다음을 실행하세요 (서버가 성공적으로 시작될 때까지).
$ subdosec -ins

Starting Node.js server...
Node.js server started successfully.
[경고] test.txt에 있는 모든 서브도메인을 탈취하지 마세요. 모든 사람이 데모에 사용할 수 있도록 하세요.
[정보] 릴리스 섹션도 확인하세요. 흥미로운 정보를 찾을 수 있습니다.
$ subdosec -h
   _____       __        __
  / ___/__  __/ /_  ____/ /___  ________  _____
  \__ \/ / / / __ \/ __  / __ \/ ___/ _ \/ ___/
 ___/ / /_/ / /_/ / /_/ / /_/ (__  )  __/ /__
/____/\__,_/_.___/\__,_/\____/____/\___/\___/


usage: subdosec [-h] [-mode {private,public}] [-initkey INITKEY] [-vo] [-pe] [-ins] [-pf PF] [-subfng SUBFNG] [-lf LF] [-sfid] [-ks] [-o O] [-su] [-lu LU] [-lm] [-uf] [-unai UNAI] [-v] [-t THREADS]

Subdomain takeover scanner.

options:
  -h, --help            show this help message and exit
  -mode {private,public}
                        Mode of operation (private/public)
  -initkey INITKEY      Initialize the API key
  -vo                   VULN Only: Hide UNDETECT messages
  -pe                   Print Error: When there are problems detecting your target
  -ins                  Prepar node & start server
  -pf PF                Private Fingerprint: uses your local fingerprint. Example: -pf /path/to/tko.json
  -subfng SUBFNG        Submit fingerprint: submit local fingerprint to admin. Example: -subfng localfinger.json
  -lf LF                Fingerprint lock: to focus on one or multiple fingerprints. (-lf github.io,surge.sh) and leave this arg to scan all fingerprints
  -sfid                 To view all available fingerprint ids.
  -ks                   To shut down the server node if you want to not use subdosec for a long time.
  -o O                  Save result locally to the specified path. Example: -o /path/to/dir
  -su                   Skip undetect will not stored to server (https://subdosec.vulnshot.com/result/undetected)
  -lu LU                Undetec stored localy to the specified path. Example: -lu /path/to/dir
  -lm                   Local Mode: Save vuln and undetect to default inside tools directory (auto -su)
  -uf                   Update Fingerprint
  -unai UNAI            Analyze undetected subdomains using AI. Example: -unai /path/to/undetect.json
  -v, --verbose         Show progress count (e.g. [1/10])
  -t THREADS, --threads THREADS
                        Number of threads to use for scanning (default: 10)
목록 준비
프로토콜 없이 지원
cat list

https://careers.rotacloud.com
http://creators.thinkorion.com
https://docs.polygon-nightfall.technology
a.anchorsawaytpt.com
help.oceges.com
CMD 1
서버에 저장된 미감지 항목을 건너뛰고 로컬에 저장
cat test.txt | subdosec -lm

https://subdosec.vulnshot.com [UNDETECT]
http://feedback.bazoom.com [sleekplan.com] [VULN] [SAVED]
http://demodev.destinojet.co [meteor.com] [VULN] [SAVED]
http://creators.thinkorion.com [UNDETECT]
https://www.www.savillerow.status.lnt.cl [ohdear.app] [VULN] [SAVED]
https://careers.rotacloud.com [gohire.io] [VULN] [SAVED]
https://careers.rotacloud.com [gohire.io] [VULN] [SAVED]
https://ai.yooture.com [UNDETECT]
https://help.oceges.com [UNDETECT]
http://ftp.thiagolima.com [surge.sh] [VULN] [SAVED]


VULN DIRECTORY  : /home/alice/.subdosec/vulns
UNDETECT FILE   : /home/alice/.subdosec/undetect/undetect.json
출력 읽기
~$ ls /home/alice/.subdosec/vulns
gohire.io_tko.txt  meteor.com_tko.txt  ohdear.app_tko.txt  sleekplan.com_tko.txt  surge.sh_tko.txt
~$ cat /home/alice/.subdosec/vulns/gohire.io_tko.txt
careers.rotacloud.com
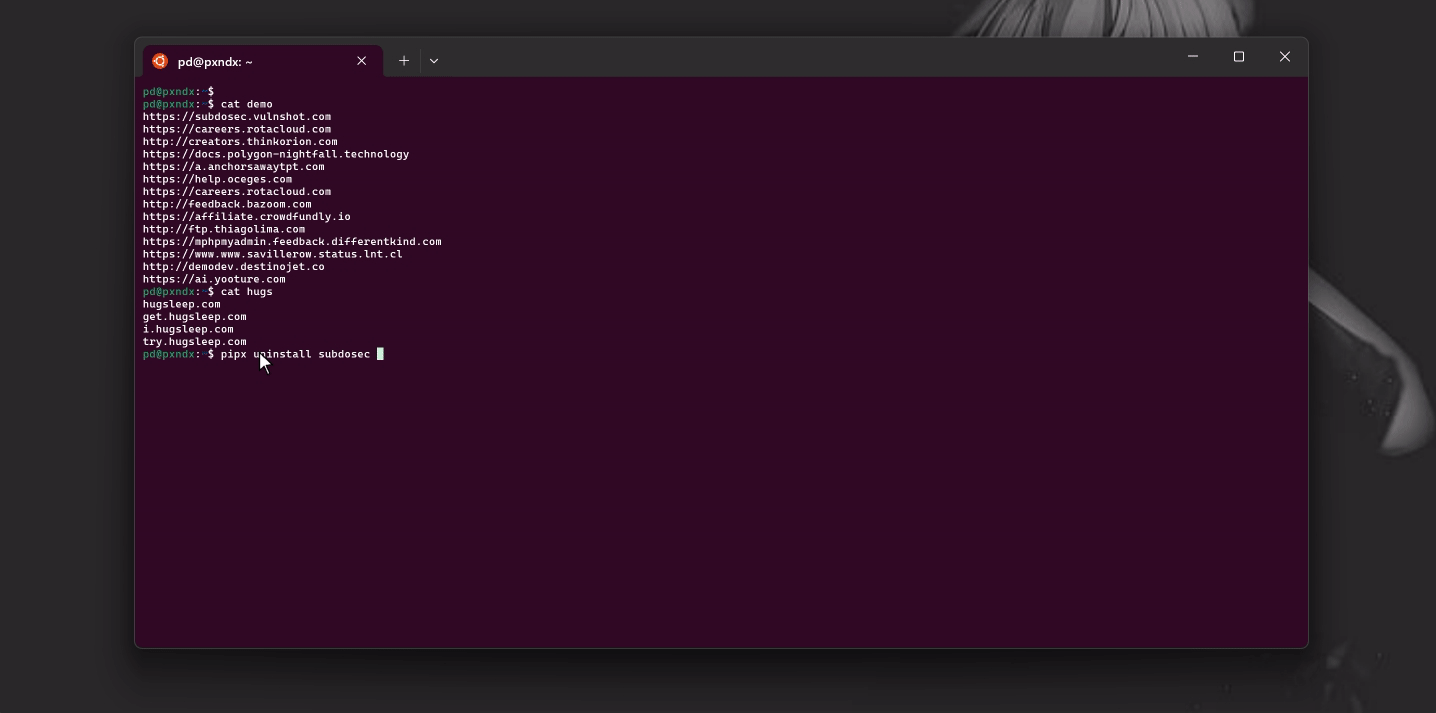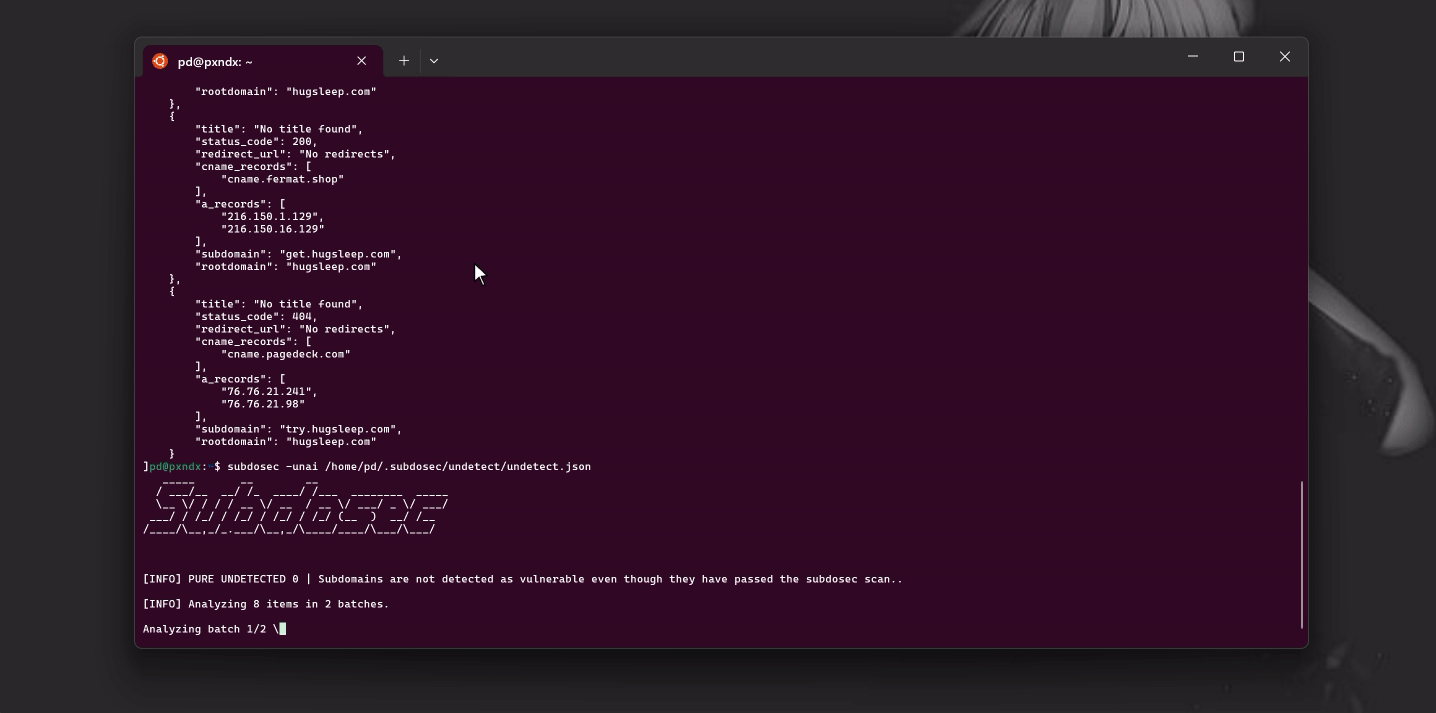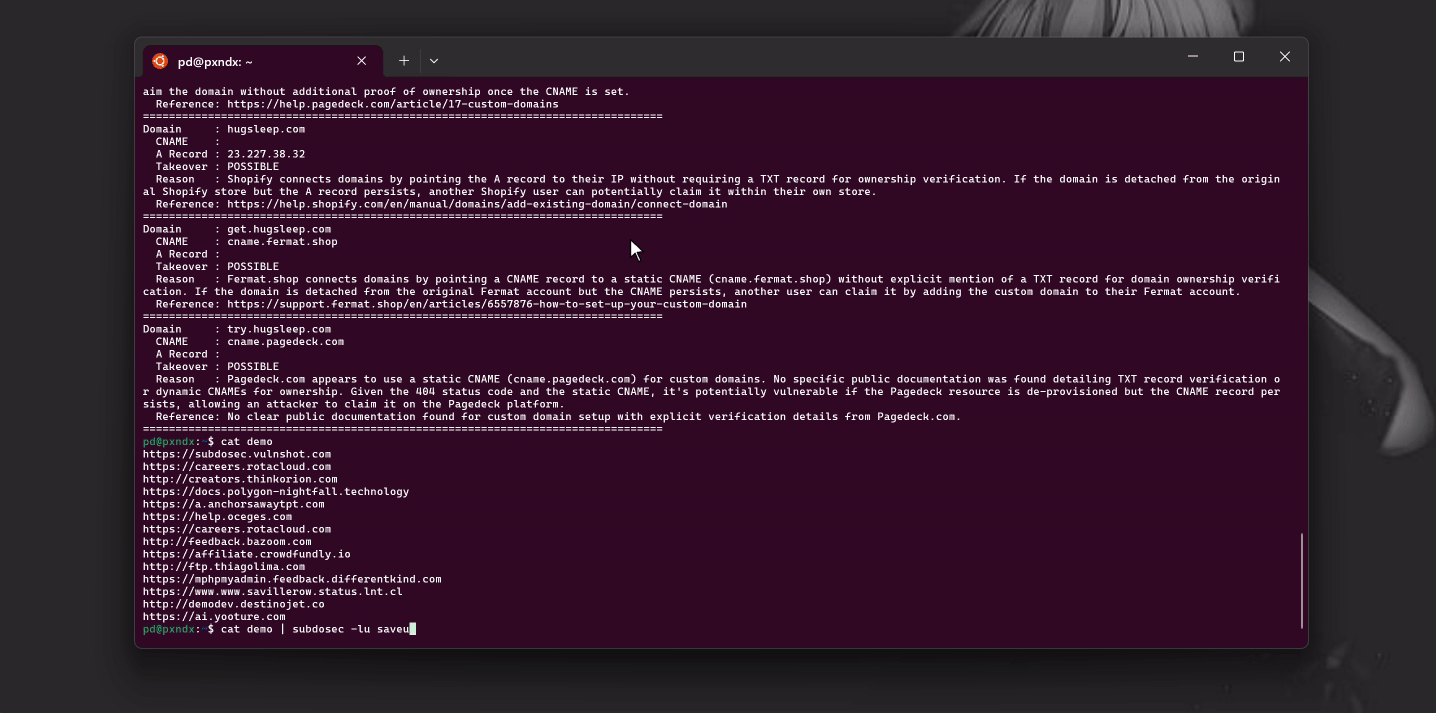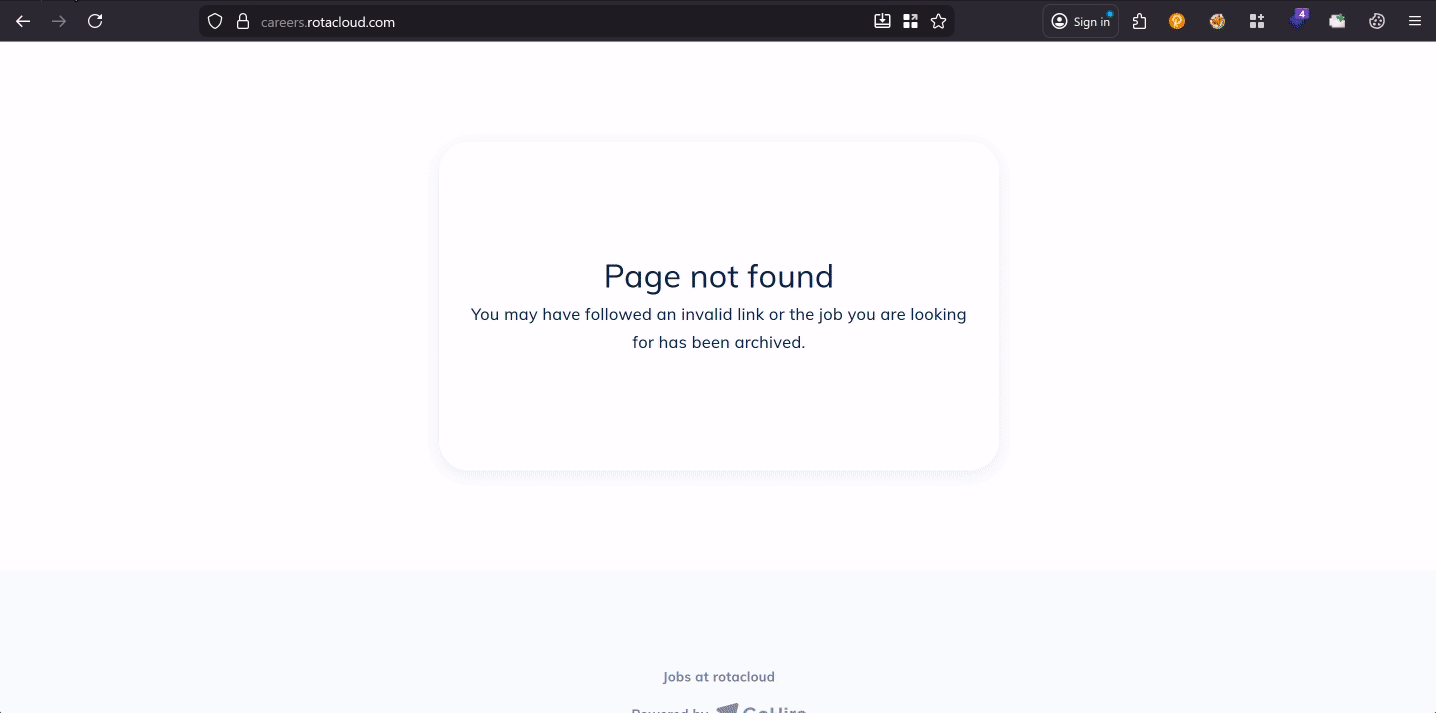
미감지 항목을 읽고 -unai로 자동 분석하여 새로운 잠재적 취약점 분석
cat /home/alice/.subdosec/undetect/undetect.json
[
    {
        "title": "No title found",
        "status_code": 404,
        "redirect_url": "No redirects",
        "cname_records": [
            "cname.redacted.com"
        ],
        "a_records": [
            "76.76.21.98",
            "76.76.21.241"
        ],
        "subdomain": "try.redacted.com",
        "rootdomain": "redacted.com"
    },
    {
        "title": "No title found",
        "status_code": 200,
        "redirect_url": "No redirects",
        "cname_records": [
            "cname.fermat.shop"
        ],
        "a_records": [
            "216.150.16.129",
            "216.150.1.129"
        ],
        "subdomain": "get.redacted.com",
        "rootdomain": "redacted.com"
    }
]
subdosec -unai /home/pd/.subdosec/undetect/undetect.json

[INFO] PURE UNDETECTED 0 | Subdomains are not detected as vulnerable even though they have passed the subdosec scan..

[INFO] Analyzing 8 items in 2 batches.

[INFO] Progress: 5/8 data analyzed.

NEW POTENTIAL :


Domain     : try.redacted.com
  CNAME    : cname.redacted-service.com
  A Record : 76.76.21.98, 76.76.21.241
  Takeover : NOT
  Reason   : The redacted-service custom domain setup guide explicitly states the requirement of adding a TXT record (e.g., 'redacted-service-verification=<your_site_id>') for domain ownership verification. The presence of a TXT record verification step makes it not vulnerable.
  Reference: https://www.redacted-service.com/blog/how-to-setup-custom-domain/
================================================================================
Domain     : get.redacted.com
  CNAME    : cname.fermat.shop
  A Record : 216.150.16.129, 216.150.1.129
  Takeover : POSSIBLE
  Reason   : The service uses a static CNAME (cname.fermat.shop) for custom domain setup. Publicly available documentation for Fermat's custom domain setup does not clearly specify a requirement for a TXT record or any dynamic verification method for domain ownership. Without such verification, a static CNAME makes the subdomain potentially vulnerable if the corresponding Fermat account is deleted or becomes unlinked.
  Reference: https://fermat.shop/
================================================================================
CMD 2
루트 도메인 사용 및 파이프라인 서브도메인 파인더 도구(subfinder, assetfinder, amass 등) 활용
cat list
example.com
cat list | subfinder -silent | subdosec -lm

https://subdosec.vulnshot.com [UNDETECT]
http://feedback.bazoom.com [sleekplan.com] [VULN] [SAVED]
http://demodev.destinojet.co [meteor.com] [VULN] [SAVED]
http://creators.thinkorion.com [UNDETECT]
https://www.www.savillerow.status.lnt.cl [ohdear.app] [VULN] [SAVED]
https://careers.rotacloud.com [gohire.io] [VULN] [SAVED]
https://careers.rotacloud.com [gohire.io] [VULN] [SAVED]
https://ai.yooture.com [UNDETECT]
https://help.oceges.com [UNDETECT]
http://ftp.thiagolima.com [surge.sh] [VULN] [SAVED]


VULN DIRECTORY  : /home/alice/.subdosec/vulns
UNDETECT FILE   : /home/alice/.subdosec/undetect/undetect.json
CMD 3
(결과를 notify로 전달)
cat list | subdosec -lm -vo | notify -silent

https://careers.rotacloud.com [100.00%] [gohire.io] [VULN] [SAVED]
CMD 4
개인 지문 사용, 이 플래그는 공개 + 개인 지문을 자동으로 병합합니다.
cat priv8.json






