 tintinweb/striptls
STARTTLS 스트리핑 공격의 프록시 POC 구현

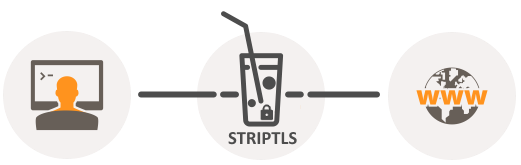
범용 TCP 프록시 구현 및 감사 도구로, 프로토콜 독립적인 ssl/tls 가로채기와 SMTP, POP3, IMAP, FTP, NNTP, XMPP, ACAP, IRC에 대한 STARTTLS 제거 공격을 수행합니다.
Python2!
//이 프로젝트의 도움으로 취약점을 발견하셨나요? 연락 주세요!
SSLContext) < Python 3--key=server.pem결과:```python
[Vulnerable!] <class striptls.StripWithInvalidResponseCode at 0xffd3138c>
[Vulnerable!] <class striptls.StripWithTemporaryError at 0xffd4611c>
[ ] <class striptls.StripFromCapabilities at 0xffd316bc>
[Vulnerable!] <class striptls.StripWithError at 0xffd4614c>
[Vulnerable!] <class striptls.StripInboundTLS at 0x7f08319a6808>
[Vulnerable!] <class striptls.StripFromCapabilities at 0x7f08319a67a0>
[Vulnerable!] <class striptls.UntrustedIntercept at 0x7f08319a6870>
## 사용법```
#> python2 -m pip install striptls
#> python2 -m striptls --help
The input is empty. Please provide the content for chunk 5 so I can translate it according to the instructions.``` #> python -m striptls --help # from pip/setup.py #> python striptls --help # from source / root folder Usage: striptls.py [options]
example: striptls.py --listen 0.0.0.0:25 --remote mail.server.tld:25
Options: -h, --help show this help message and exit -q, --quiet be quiet [default: True] -l LISTEN, --listen=LISTEN listen ip:port [default: 0.0.0.0:<remote_port>] -r REMOTE, --remote=REMOTE remote target ip:port to forward sessions to -k KEY, --key=KEY SSL Certificate and Private key file to use, PEM format assumed [default: server.pem] -s, --generic-ssl-intercept dynamically intercept SSL/TLS -b BUFFER_SIZE, --bufsiz=BUFFER_SIZE -x VECTORS, --vectors=VECTORS Comma separated list of vectors. Use 'ALL' (default) to select all vectors, 'NONE' for tcp/ssl proxy mode. Available vectors: ACAP.StripFromCapabilities, ACAP.StripWithError, ACAP.UntrustedIntercept, FTP.StripFromCapabilities, FTP.StripWithError, FTP.UntrustedIntercept, GENERIC.Intercept, IMAP.ProtocolDowngradeToV2, IMAP.StripFromCapabilities, IMAP.StripWithError, IMAP.UntrustedIntercept, IRC.StripCAPWithNotRegistered, IRC.StripFromCapabilities, IRC.StripWithError, IRC.StripWithNotRegistered, IRC.StripWithSilentDrop, IRC.UntrustedIntercept, NNTP.StripFromCapabilities, NNTP.StripWithError, NNTP.UntrustedIntercept, POP3.StripFromCapabilities, POP3.StripWithError, POP3.UntrustedIntercept, SMTP.InboundStarttlsProxy, SMTP.InjectCommand, SMTP.ProtocolDowngradeStripExtendedMode, SMTP.StripFromCapabilities, SMTP.StripWithError, SMTP.StripWithInvalidResponseCode, SMTP.StripWithTemporaryError, SMTP.UntrustedIntercept, XMPP.StripFromCapabilities, XMPP.StripInboundTLS, XMPP.UntrustedIntercept [default: ALL]
## 설치 (선택사항)

pip에서

    #> pip install striptls

소스에서

    #> setup.py install

## 예제

	                  inbound                    outbound
	[inbound_peer]<------------->[listen:proxy]<------------->[outbound_peer/target]
	  smtp-client                   striptls                    remote/target

local `smtp-client` -> `localhost:8825` (proxy) -> `mail.gmx.net:25`

### 일반 SSL/TLS 가로채기

`--generic-ssl-intercept`는 일반적인 SSL/TLS 핸드셰이크 감지 및 세션 변환을 활성화하는 전역 스위치입니다. 모든 맹글/벡터와 결합할 수 있습니다.

`GENERIC.Intercept`는 SSL/TLS 핸드셰이크 감지 및 변환 기능의 맹글/벡터 구현입니다.
