Skip to content
KitploitKITPLOIT
도구익스플로잇블로그
Log in
제출
도구익스플로잇블로그
제출

해킹, 침투 테스트 및 사이버 보안 도구를 당신의 보안 무기고에!

Kitploit은 해킹, 사이버 보안 및 침투 테스트 도구 디렉토리입니다. 최신 프로젝트 업데이트를 발견하여 취약점을 찾고, 시스템을 분석하고, 테스트를 자동화하고, 보안을 강화하세요.

피드문의개인정보© 2026 Kitploit

도구 디렉토리

카테고리

모든 카테고리 보기
Loading categories
wrongsecrets — Vulnerable app with examples showing how to not use secrets | Kitploit
도구/GitHubGitHub/owasp/wrongsecrets
Container SecurityVulnerability AnalysisCTFCloud SecurityDevSecOpsSecret DetectionLearning & EducationLabs & PracticeLabs & Practice #8위Secret Detection #19위
GitHubowasp/wrongsecrets

wrongsecrets

Vulnerable app with examples showing how to not use secrets
저장소 보기웹사이트
1.5k5999411시간 11분 전Kitploit 검토 완료

인기

모두 보기 →

커뮤니티에서 가장 많이 사용되는 도구를 찾아보세요.

모든 도구 탐색

도구 컬렉션을 둘러보세요

모든 도구 보기 →
공유
요청한 언어로 콘텐츠를 사용할 수 없습니다. 영어 버전을 표시합니다.

OWASP WrongSecrets

Tweet

Java checkstyle and testing Pre-commit Terraform FMT CodeQL Dead Link Checker Javadoc and Swaggerdoc generator Test Heroku with cypress Build Dev Container

Test minikube script (k8s) Test minikube script (k8s&vault) Docker container test Test container on podman DAST with ZAP PR Preview and Visual Diff Build Preview Visual Diff

OWASP Production Project OpenSSF Best Practices Discussions Docker pulls

Welcome to the OWASP WrongSecrets game! The game is packed with real life examples of how to not store secrets in your software. Each of these examples is captured in a challenge, which you need to solve using various tools and techniques. Solving these challenges will help you recognize common mistakes & can help you to reflect on your own secrets management strategy.

Can you solve all the challenges?

Try some of them on our Heroku demo environment.

Want to play the other challenges? Read the instructions on how to set them up below.

🚀 Quick Start

New to WrongSecrets? Start here:

  1. Try Online First: Visit our Heroku demo to get familiar with the challenges
  2. Run Locally: Use Docker for the full experience with all challenges:
    docker run -p 8080:8080 -p 8090:8090 jeroenwillemsen/wrongsecrets:latest-no-vault
    
    Then open http://localhost:8080
  3. Want to see what's ahead? Try our bleeding-edge master container with the latest features:
    docker run -p 8080:8080 -p 8090:8090 ghcr.io/owasp/wrongsecrets/wrongsecrets-master:latest-master
    
    ⚠️ Note: This is a development version and may be unstable
  4. Advanced Setup: For cloud challenges and Kubernetes exercises, see the detailed instructions below

What you'll learn:

  • Common secrets management mistakes
  • How to identify exposed credentials
  • Best practices for securing secrets
  • Tools and techniques for secret detection

How it works: This repository contains intentionally vulnerable code and configuration files with real and fake secrets hidden throughout the codebase. You'll examine source code, configuration files, Docker containers, and cloud deployments to discover these secrets. Each challenge teaches you different ways secrets can be accidentally exposed in real-world applications.
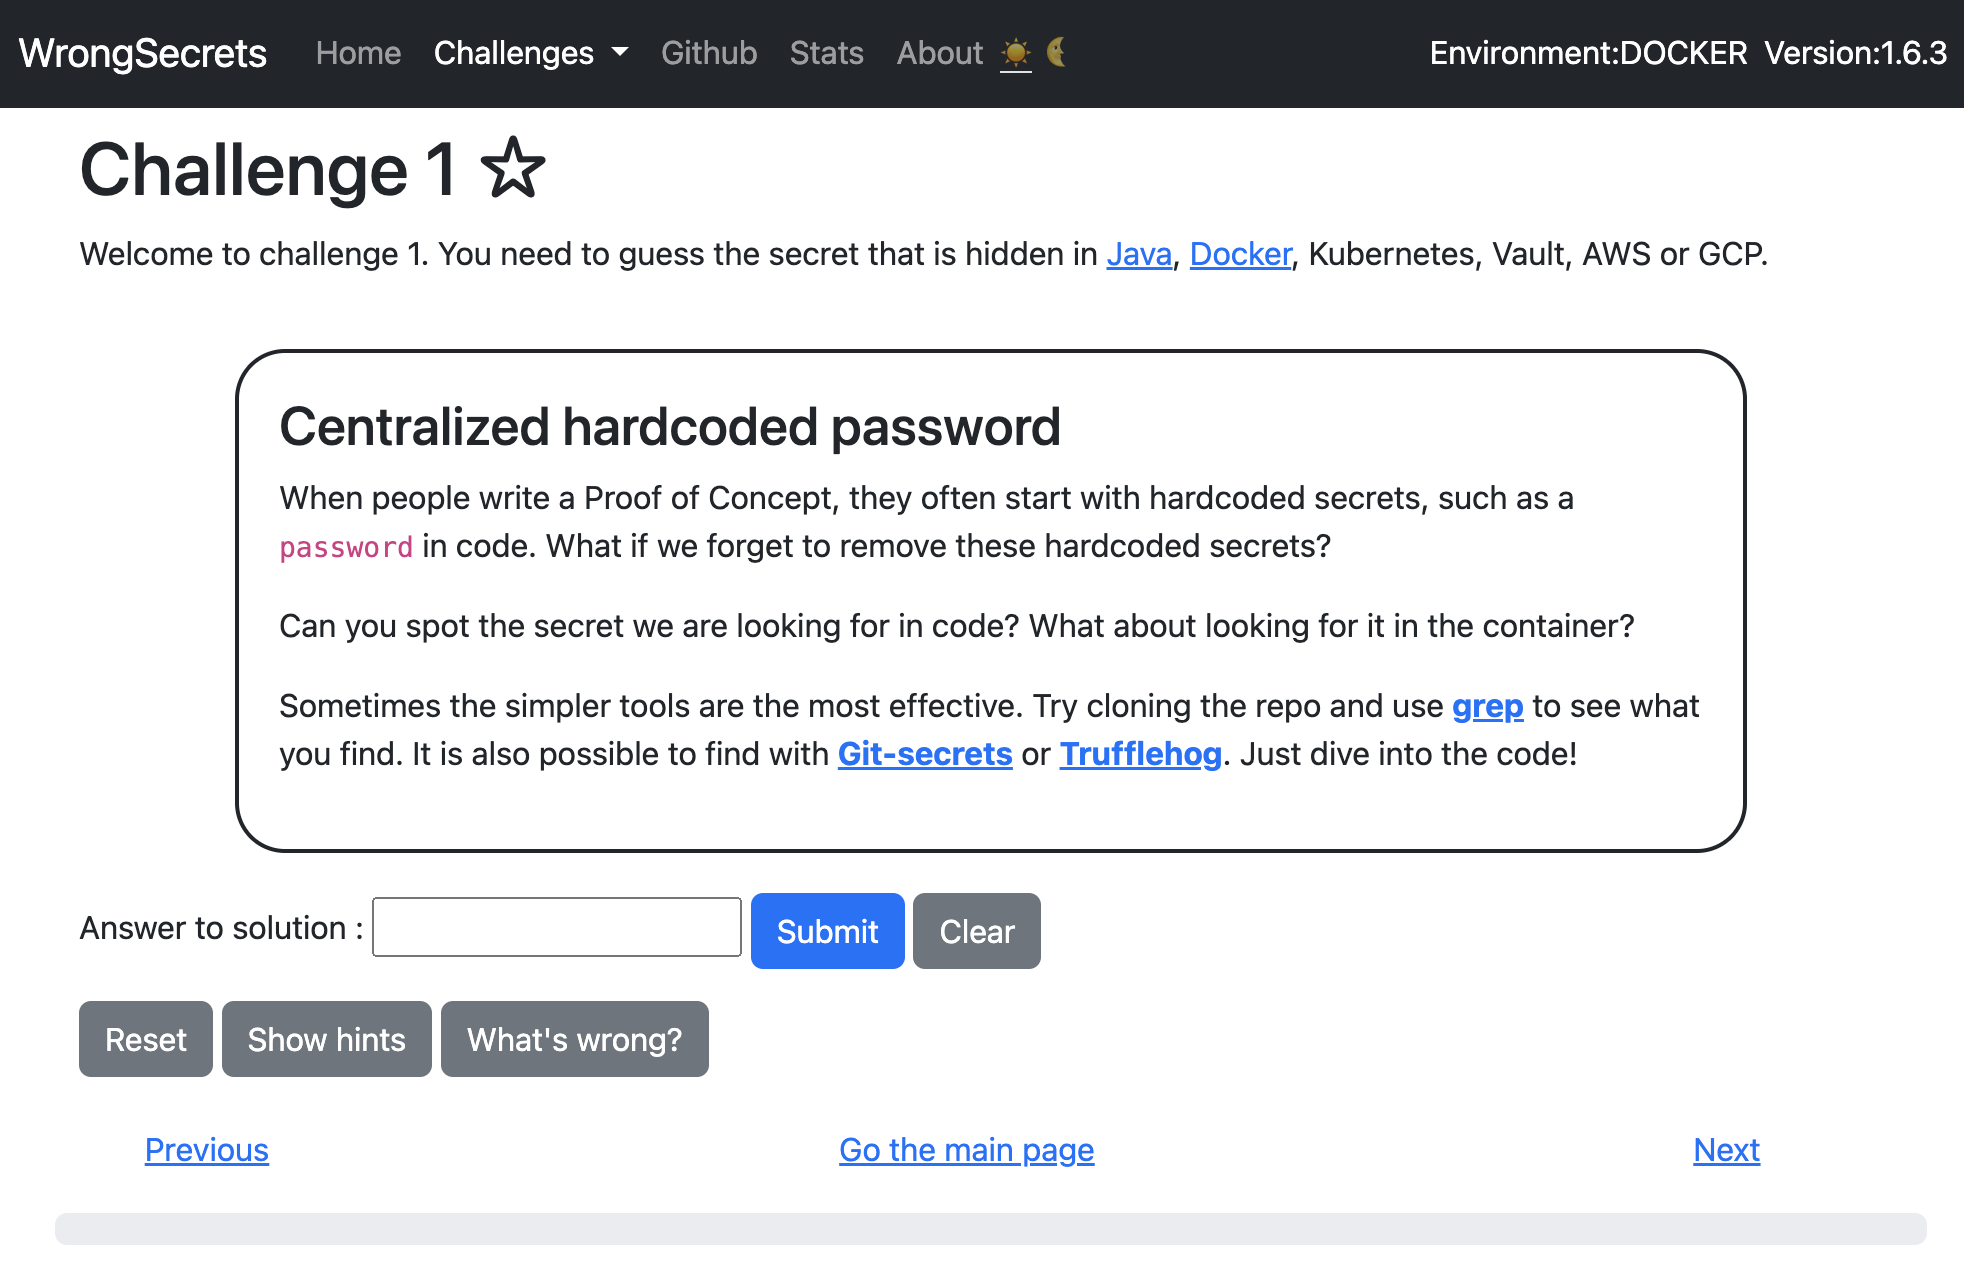
screenshotOfChallenge1

📋 Prerequisites

For basic usage:

  • A web browser
  • Docker (for local setup) - Install here

For advanced setups:

  • Kubernetes/Minikube - Install here
  • Cloud account (AWS/GCP/Azure) for cloud challenges
  • Command line familiarity
도구 다운로드