
 msuiche/elegant-bouncer
ELEGANTBOUNCER는 파일 기반 모바일 익스플로잇 탐지 도구입니다.


ELEGANTBOUNCER는 파일 기반 모바일 익스플로잇 탐지 도구입니다.
고급 파일 기반 위협 식별을 위한 혁신적인 접근 방식을 채택하여, 실제 공격에서 수집된 샘플이 필요 없고 정규 표현식이나 IOC에 기반한 전통적인 방법보다 뛰어난 성능을 보입니다. 현재는 주로 FORCEDENTRY(CVE-2021-30860), BLASTPASS(CVE-2023-4863, CVE-2023-41064), TRIANGULATION(CVE-2023-41990)과 같은 모바일 취약점 식별을 대상으로 합니다.
| 위협 이름 | CVE | 지원 여부 |
|---|---|---|
| FORCEDENTRY | CVE-2021-30860 | ✅ |
| BLASTPASS | CVE-2023-4863, CVE-2023-41064 | ✅ |
| TRIANGULATION | CVE-2023-41990 | ✅ |
| CVE-2025-43300 | CVE-2025-43300 | ✅ |
| CVE-2025-21043 | CVE-2025-21043 | ✅ |
| CVE-2026-32741 | CVE-2026-32741 | ✅ |
| HEIF mask underfill | CVE 없음 (libheif <= 1.21.2) | ✅ |
| CVE-2026-32882 | CVE-2026-32882, CVE-2025-68431 | ✅ |
| CVE-2026-86950 | CVE-2026-86950 | ✅ |

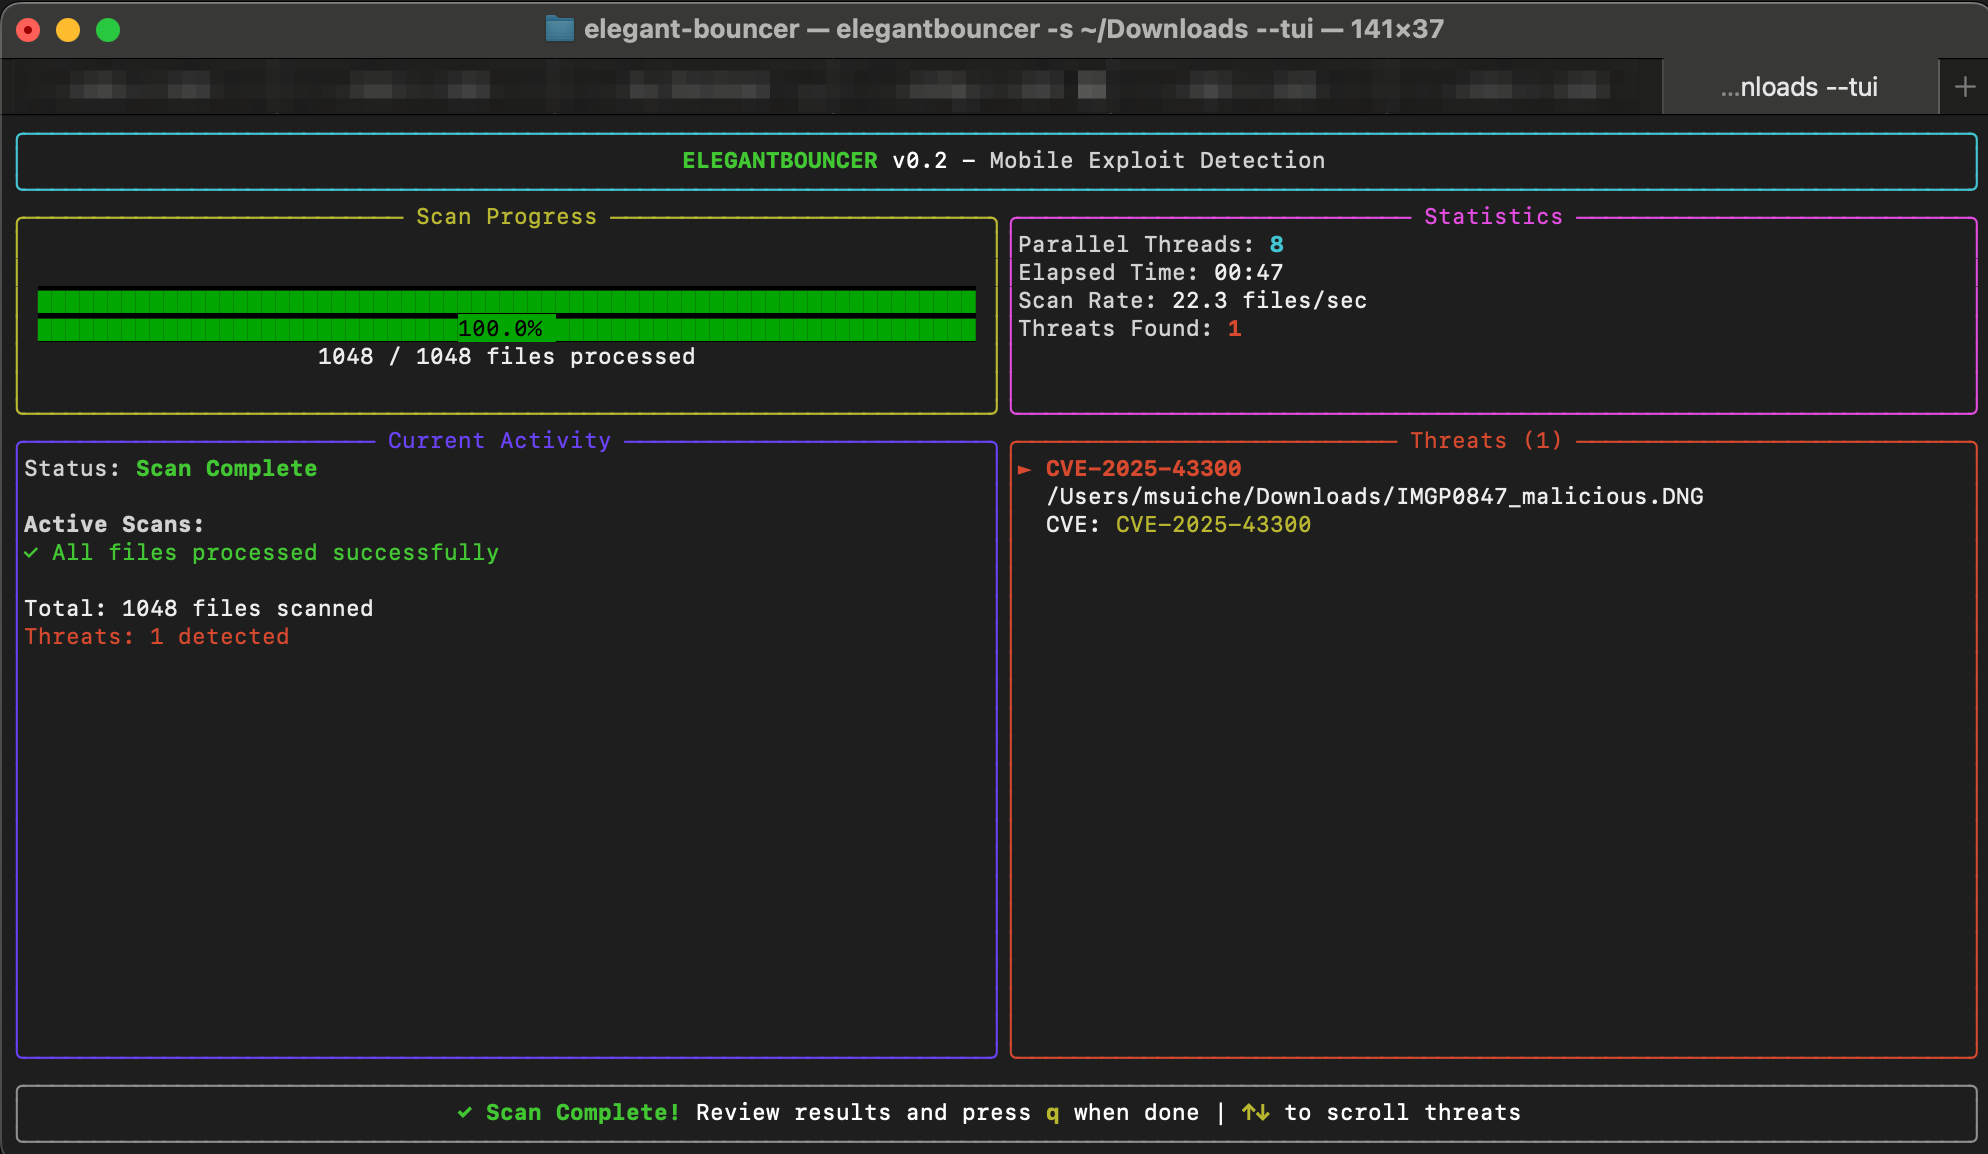
TUI 모드는 병렬 스캔 작업을 실시간으로 시각화하여 모든 활성 워커 스레드를 동시에 보여줍니다. 디렉터리를 스캔할 때 --tui 플래그로 활성화할 수 있습니다.
elegant-bouncer v0.2
ELEGANTBOUNCER Detection Tool
Detection tool for file-based mobile exploits.

A utility designed to detect the presence of known mobile APTs in commonly distributed files.

Usage: elegant-bouncer [OPTIONS] <Input path>

Arguments:
  <Input path>
          Path to the input file or folder

Options:
  -v, --verbose
          Print extra output while parsing

  -s, --scan
          Assess a given file or folder, checking for known vulnerabilities

  -c, --create-forcedentry
          Create a FORCEDENTRY-like PDF

  -r, --recursive
          Recursively scan subfolders

  -m, --messaging
          Scan messaging app databases for attachments (iOS backup format)

  --ios-extract
          Extract/reconstruct iOS backup to readable folder structure

  -o, --output <OUTPUT>
          Output directory for iOS backup extraction

  -f, --force
          Force overwrite of output directory if not empty

  -e, --extensions <EXTENSIONS>
          File extensions to scan (comma-separated, e.g., "pdf,webp,ttf")
          Default: pdf,gif,webp,jpg,jpeg,png,tif,tiff,dng,heic,heif,hif,avif,ttf,otf

  -h, --help
          Print help information (use `-h` for a summary)

  -V, --version
          Print version information
알려진 취약점에 대해 단일 파일을 평가하려면 --scan을 사용하십시오:
elegantbouncer --scan suspicious_file.pdf
디렉터리에 있는 지원되는 모든 파일을 스캔합니다:
elegantbouncer --scan /path/to/folder
-r 플래그를 사용하여 모든 하위 디렉터리를 재귀적으로 스캔합니다:
elegantbouncer --scan /path/to/folder -r
-e 플래그를 사용하여 스캔할 파일 유형을 지정합니다:
# Scan only PDF and DNG files
elegantbouncer --scan /path/to/folder -e pdf,dng

# Scan only image files recursively
elegantbouncer --scan /path/to/folder -r -e jpg,jpeg,png,webp,gif
기본적으로 이 도구는 다음 확장자를 가진 파일을 스캔합니다:
디렉터리를 스캔할 때 이 도구는 다음을 제공합니다:
[+] Scanning directory: /path/to/documents
[+] Recursive mode enabled
[+] Extensions: pdf, gif, webp, jpg, jpeg, png, tif, tiff, dng, heic, heif, hif, avif, ttf, otf

[1] Scanning: /path/to/documents/invoice.pdf
[2] Scanning: /path/to/documents/photo.jpg
[3] Scanning: /path/to/documents/malicious.webp
  └─ THREAT found: BLASTPASS
[4] Scanning: /path/to/documents/report.pdf
  └─ THREAT found: FORCEDENTRY

[+] Scanned 4 files

[+] Summary Results:
╭────────────────┬───────────────────────────────┬──────────────────────────────────────────────────────────────────────────┬──────────╮
│ name           │ cve_ids                       │ description                                                              │ detected │
├────────────────┼───────────────────────────────┼──────────────────────────────────────────────────────────────────────────┼──────────┤
│ FORCEDENTRY    │ CVE-2021-30860                │ Malicious JBIG2 PDF shared over iMessage                                 │ Yes      │
│ BLASTPASS      │ CVE-2023-4863, CVE-2023-41064 │ Malicious WebP presumably shared over iMessage and other mediums         │ Yes      │
│ TRIANGULATION  │ CVE-2023-41990                │ Maliciously crafted TrueType font embedded in PDFs shared over iMessage  │ No       │
│ CVE-2025-43300 │ CVE-2025-43300                │ Malicious DNG with JPEG Lossless compression exploiting RawCamera.bundle │ No       │
╰────────────────┴───────────────────────────────┴──────────────────────────────────────────────────────────────────────────┴──────────╯

[!] Infected Files Details:
╭────────────────────────────────┬─────────────┬───────────────────────────────╮
│ path                           │ threat_name │ cve_ids                       │
├────────────────────────────────┼─────────────┼───────────────────────────────┤
│ /path/to/documents/report.pdf  │ FORCEDENTRY │ CVE-2021-30860                │
│ /path/to/documents/malicious.webp │ BLASTPASS   │ CVE-2023-4863, CVE-2023-41064 │
╰────────────────────────────────┴─────────────┴───────────────────────────────╯
iOS 백업을 읽을 수 있는 폴더 구조로 재구성합니다:
# Extract backup to default location (creates _reconstructed folder)
elegantbouncer --ios-extract /path/to/ios/backup

# Extract to specific output directory
elegantbouncer --ios-extract /path/to/ios/backup -o /path/to/output

# Force overwrite if output directory exists
elegantbouncer --ios-extract /path/to/ios/backup -o /path/to/output --force
메시징 앱의 악성 첨부 파일을 iOS 백업에서 스캔합니다:
# Scan messaging databases (iMessage, WhatsApp, Viber, Signal, Telegram)
elegantbouncer --scan --messaging /path/to/ios/backup

# Combine with extraction for complete analysis
elegantbouncer --ios-extract /path/to/ios/backup -o /tmp/extracted
elegantbouncer --scan --messaging /tmp/extracted
이 기능은 다음에서 첨부 파일의 위협을 탐지합니다:
--create-forcedentry를 사용하면 CVE-2021-30860을 악용하도록 처음부터 설계된 PDF를 생성할 수 있습니다. 작업 진행 중입니다.
참고: 미리 만들어진 샘플은 samples/ 디렉터리에서 확인할 수 있습니다.
관심 대상 인물이라고 생각된다면 Lockdown Mode를 사용하여 공격 표면을 줄이십시오.






