 mobsf/mobsfscan
mobsfscan은 Android 및 iOS 소스 코드에서 안전하지 않은 코드 패턴을 찾을 수 있는 정적 분석 도구입니다. Java, Kotlin, Swift, Objective C 코드를 지원합니다. mobsfscan은 MobSF 정적 분석 규칙을 사용하며 semgrep 및 libsast 패턴 매처로 구동됩니다.

# mobsfscan
**mobsfscan**은 Android 및 iOS 소스 코드에서 안전하지 않은 코드 패턴을 찾을 수 있는 정적 분석 도구입니다. Java, Kotlin, Android XML, iOS Info.plist, Swift 및 Objective C 코드를 지원합니다. mobsfscan은 [MobSF](https://github.com/MobSF/Mobile-Security-Framework-MobSF) 정적 분석 규칙을 사용하며 [semgrep](https://github.com/returntocorp/semgrep)과 [libsast](https://github.com/ajinabraham/libsast) 패턴 매처를 기반으로 합니다.
Made with  in India [](https://twitter.com/intent/tweet/?text=mobsfscan%20is%20a%20static%20analysis%20tool%20that%20can%20find%20insecure%20code%20patterns%20in%20your%20Android%20and%20iOS%20source%20code.%20Supports%20Java,%20Kotlin,%20Swift,%20and%20Objective%20C%20Code.%20by%20%40ajinabraham%20%40OpenSecurity_IN&url=https://github.com/MobSF/mobsfscan)
[](https://badge.fury.io/py/mobsfscan)
[](https://www.gnu.org/licenses/lgpl-3.0.en.html)
[](https://www.python.org/downloads/)
[](https://github.com/MobSF/mobsfscan/)
[](https://github.com/MobSF/mobsfscan/actions?query=workflow%3ABuild)
### mobsfscan 후원하기
[](https://opensecurity.in/donate)
mobsfscan이 마음에 들고 유용하다고 생각하신다면 후원을 고려해 주세요.
## e-Learning 과정 및 자격증
 [Automated Mobile Application Security Assessment with MobSF -MAS](https://opsecx.com/index.php/product/automated-mobile-application-security-assessment-with-mobsf/)
 [Android Security Tools Expert -ATX](https://opsecx.com/index.php/product/android-security-tools-expert-atx/)
## 설치
`pip install mobsfscan`
Python 3.10–3.14 필요
## 명령줄 옵션```bash
$ mobsfscan
usage: mobsfscan [-h] [--json] [--sarif] [--sonarqube] [--gitlab-sast] [--html]
[--type {android,ios,auto}] [-o OUTPUT] [-c CONFIG]
[-mp {default,billiard,thread}] [-w] [--no-fail] [-v]
[path ...]
positional arguments:
path Path can be file(s) or directories with source code
options:
-h, --help show this help message and exit
--json set output format as JSON
--sarif set output format as SARIF 2.1.0
--sonarqube set output format as SonarQube generic issues (10.3+)
--gitlab-sast set output format as GitLab SAST report
--html set output format as HTML
--type {android,ios,auto}
optional: force android or ios rules explicitly
-o OUTPUT, --output OUTPUT
output filename to save the result
-c CONFIG, --config CONFIG
location to .mobsf config file
-mp {default,billiard,thread}, --multiprocessing {default,billiard,thread}
optional: specify multiprocessing strategy
-w, --exit-warning non zero exit code on warning
--no-fail force zero exit code, takes precedence over --exit-warning
-v, --version show mobsfscan version
```
## 사용 예시```bash
$ mobsfscan tests/assets/src/
- Pattern Match ████████████████████████████████████████████████████████████ 3
- Semantic Grep ██████ 37
mobsfscan: v0.3.0 | Ajin Abraham | opensecurity.in
╒══════════════╤════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════╕
│ RULE ID │ android_webview_ignore_ssl │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ DESCRIPTION │ Insecure WebView Implementation. WebView ignores SSL Certificate errors and accept any SSL Certificate. This application is vulnerable to MITM attacks │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ TYPE │ RegexAnd │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ PATTERN │ ['onReceivedSslError\\(WebView', '\\.proceed\\(\\);'] │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ SEVERITY │ ERROR │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ INPUTCASE │ exact │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ CVSS │ 7.4 │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ CWE │ CWE-295 Improper Certificate Validation │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ OWASP-MOBILE │ M3: Insecure Communication │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ MASVS │ MSTG-NETWORK-3 │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ REF │ https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05g-Testing-Network-Communication.md#webview-server-certificate-verification │
├──────────────┼────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────────┤
│ FILES │ ╒════════════════╤═════════════════════════════════════════════════════════════════════════════════════════════╕ │
│ │ │ File │ ../test_files/android_src/app/src/main/java/opensecurity/webviewignoressl/MainActivity.java │ │
│ │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤ │
│ │ │ Match Position │ 1480 - 1491 │ │
│ │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤ │
│ │ │ Line Number(s) │ 50 │ │
│ │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤ │
│ │ │ Match String │ .proceed(); │ │
│ │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤ │
│ │ │ File │ ../test_files/android_src/app/src/main/java/opensecurity/webviewignoressl/MainActivity.java │ │
│ │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤ │
│ │ │ Match Position │ 1331 - 1357 │ │
│ │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤ │
│ │ │ Line Number(s) │ 46 │ │
│ │ ├────────────────┼─────────────────────────────────────────────────────────────────────────────────────────────┤ │
│ │ │ Match String │ onReceivedSslError(WebView │ │
│ │ ╘════════════════╧═════════════════════════════════════════════════════════════════════════════════════════════╛ │
╘══════════════╧════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════════╛
```
## Python API```python
>>> from mobsfscan.mobsfscan import MobSFScan
>>> src = 'tests/assets/src/java/java_vuln.java'
>>> scanner = MobSFScan([src], json=True)
>>> scanner.scan()
{
'results': {
'android_logging': {
'files': [{
'file_path': 'tests/assets/src/java/java_vuln.java',
'match_position': (13, 73),
'match_lines': (19, 19),
'match_string': ' Log.d("htbridge", "getAllRecords(): " + records.toString());'
}],
'metadata': {
'cwe': 'CWE-532 Insertion of Sensitive Information into Log File',
'owasp-mobile': 'M1: Improper Platform Usage',
'masvs': 'MSTG-STORAGE-3',
'reference': 'https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05d-Testing-Data-Storage.md#logs',
'description': 'The App logs information. Please ensure that sensitive information is never logged.',
'severity': 'INFO'
}
},
'android_certificate_pinning': {
'metadata': {
'cwe': 'CWE-295 Improper Certificate Validation',
'owasp-mobile': 'M3: Insecure Communication',
'masvs': 'MSTG-NETWORK-4',
'reference': 'https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05g-Testing-Network-Communication.md#testing-custom-certificate-stores-and-certificate-pinning-mstg-network-4',
'description': 'This App does not use TLS/SSL certificate or public key pinning to detect or prevent MITM attacks in secure communication channel.',
'severity': 'INFO'
}
},
'android_root_detection': {
'metadata': {
'cwe': 'CWE-919 - Weaknesses in Mobile Applications',
'owasp-mobile': 'M8: Code Tampering',
'masvs': 'MSTG-RESILIENCE-1',
'reference': 'https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05j-Testing-Resiliency-Against-Reverse-Engineering.md#testing-root-detection-mstg-resilience-1',
'description': 'This App does not have root detection capabilities. Running a sensitive application on a rooted device questions the device integrity and affects users data.',
'severity': 'INFO'
}
},
'android_prevent_screenshot': {
'metadata': {
'cwe': 'CWE-200 Information Exposure',
'owasp-mobile': 'M2: Insecure Data Storage',
'masvs': 'MSTG-STORAGE-9',
'reference': 'https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05d-Testing-Data-Storage.md#finding-sensitive-information-in-auto-generated-screenshots-mstg-storage-9',
'description': 'This App does not have capabilities to prevent against Screenshots from Recent Task History/ Now On Tap etc.',
'severity': 'INFO'
}
},
'android_safetynet_api': {
'metadata': {
'cwe': 'CWE-353 Missing Support for Integrity Check',
'owasp-mobile': 'M8: Code Tampering',
'masvs': 'MSTG-RESILIENCE-1',
'reference': 'https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05j-Testing-Resiliency-Against-Reverse-Engineering.md#testing-root-detection-mstg-resilience-1',
'description': "This App does not uses SafetyNet Attestation API that provides cryptographically-signed attestation, assessing the device's integrity. This check helps to ensure that the servers are interacting with the genuine app running on a genuine Android device. ",
'severity': 'INFO'
}
},
'android_detect_tapjacking': {
'metadata': {
'cwe': 'CWE-200 Information Exposure',
'owasp-mobile': 'M1: Improper Platform Usage',
'masvs': 'MSTG-PLATFORM-9',
'reference': 'https://github.com/MobSF/owasp-mstg/blob/master/Document/0x05h-Testing-Platform-Interaction.md#testing-for-overlay-attacks-mstg-platform-9',
'description': "This app does not has capabilities to prevent tapjacking attacks. An attacker can hijack the user's taps and tricks him into performing some critical operations that he did not intend to.",
'severity': 'INFO'
}
}
},
'errors': []
}
```
## mobsfscan 구성
소스 코드 디렉터리 루트에 있는 `.mobsf` 파일을 사용하면 mobsfscan을 구성할 수 있습니다. `--config` 인수를 사용하여 사용자 정의 `.mobsf` 파일을 사용할 수도 있습니다.```yaml
---
- ignore-filenames:
- skip.java
ignore-paths:
- __MACOSX
- skip_dir
ignore-rules:
- android_kotlin_logging
- android_safetynet_api
- android_prevent_screenshot
- android_detect_tapjacking
- android_certificate_pinning
- android_root_detection
- android_certificate_transparency
severity-filter:
- WARNING
- ERROR
severity-overrides:
ios_log: ERROR
android_logging: WARNING
```
`severity-overrides`는 특정 rule ID(`INFO`, `WARNING`, `ERROR`)에 대해 보고되는 심각도를 변경합니다. Override는 `severity-filter` 이전에 적용되며 CLI 출력, 종료 코드, 보고서 형식(SARIF, SonarQube, GitLab SAST)에 영향을 줍니다.
## 발견 사항 억제
발견 사항을 트리거하는 줄에 `// mobsf-ignore: rule_id1, rule_id2` 주석을 추가하여 소스 파일의 발견 사항을 억제할 수 있습니다. 해당 일치 항목만 억제되며, 파일 내 동일한 규칙의 다른 일치 항목은 여전히 보고됩니다.
예시:```java
String password = "strong password"; // mobsf-ignore: hardcoded_password
```
## CI/CD 통합
CI/CD 또는 DevSecOps 파이프라인에서 mobsfscan을 활성화할 수 있습니다.
#### Github Action
`.github/workflows/mobsfscan.yml` 파일에 다음을 추가하세요.```yaml
name: mobsfscan
on:
push:
branches: [ master, main ]
pull_request:
branches: [ master, main ]
jobs:
build:
runs-on: ubuntu-latest
steps:
- uses: actions/checkout@3d3c42e5aac5ba805825da76410c181273ba90b1 # v7.0.1
- uses: actions/setup-python@5fda3b95a4ea91299a34e894583c3862153e4b97 # v7.0.0
with:
python-version: '3.12'
- name: mobsfscan
uses: MobSF/mobsfscan@main
with:
args: '. --json'
```
Example: [pivaa with mobsfscan github action](https://github.com/MobSF/pivaa/actions/workflows/mobsfscan.yml)
#### Github 코드 스캐닝 통합
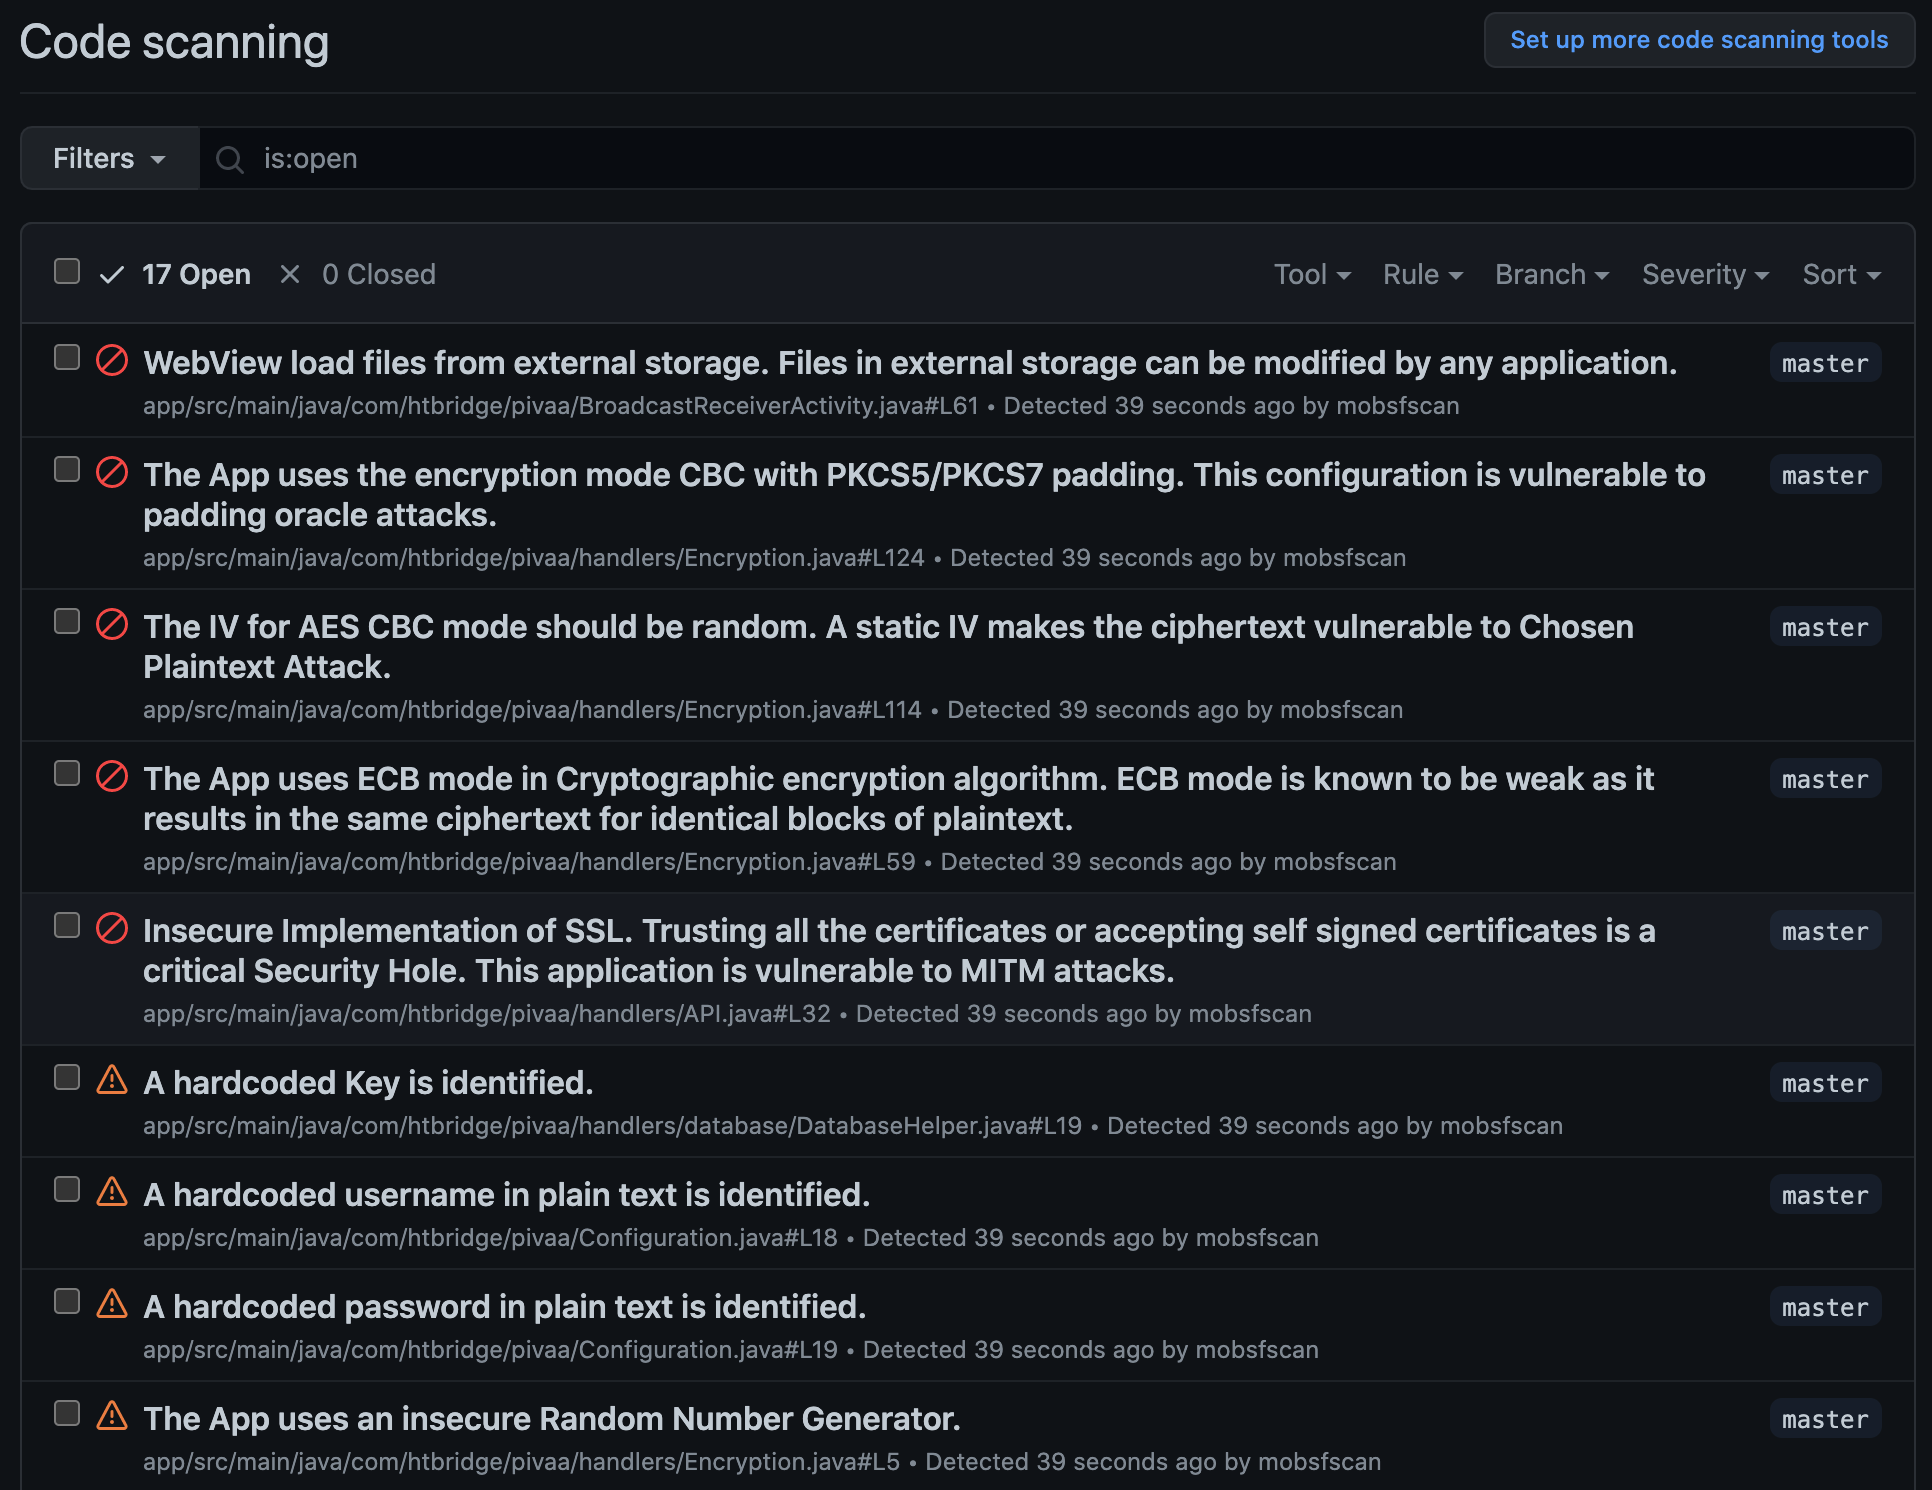
`.github/workflows/mobsfscan_sarif.yml` 파일에 다음을 추가하세요.```yaml
name: mobsfscan sarif
on:
push:
branches: [ master, main ]
pull_request:
branches: [ master, main ]
jobs:
mobsfscan:
runs-on: ubuntu-latest
name: mobsfscan code scanning
permissions:
security-events: write
actions: read
contents: read
steps:
- name: Checkout the code
uses: actions/checkout@3d3c42e5aac5ba805825da76410c181273ba90b1 # v7.0.1
- uses: actions/setup-python@5fda3b95a4ea91299a34e894583c3862153e4b97 # v7.0.0
with:
python-version: '3.12'
- name: mobsfscan
uses: MobSF/mobsfscan@main
with:
args: '. --sarif --output results.sarif || true'
- name: Upload mobsfscan report
uses: github/codeql-action/upload-sarif@1c5b675653bb5c22dbe9b12b556ec555138e09fd # v4.38.1
with:
sarif_file: results.sarif
```
#### Gitlab CI/CD
`.gitlab-ci.yml` 파일에 다음을 추가하세요.```yaml
stages:
- test
mobsfscan:
image: python:3.12
stage: test
before_script:
- pip3 install --upgrade mobsfscan
script:
- mobsfscan . --gitlab-sast -o gl-sast-report.json
artifacts:
reports:
sast: gl-sast-report.json
```
예시 명령(로컬):```bash
mobsfscan . --gitlab-sast -o gl-sast-report.json
```
이것은 네이티브 [GitLab SAST 보고서](https://docs.gitlab.com/user/application_security/sast/)를 작성하므로 SARIF 변환기 없이도 취약점 보고서 / MR 보안 위젯에 결과가 나타납니다.
#### SonarQube / SonarCloud
`--sonarqube`는 [일반 이슈 형식](https://docs.sonarsource.com/sonarqube-server/analyzing-source-code/importing-external-issues/generic-issue-import-format)(SonarQube 10.3+ / SonarCloud)을 작성하며, `rules`와 `issues` 배열이 분리되어 있습니다:```bash
mobsfscan . --sonarqube -o mobsfscan-sonar.json
```
`sonar.externalIssuesReportPaths=mobsfscan-sonar.json`로 가져옵니다.
#### Travis CI
`.travis.yml` 파일에 다음을 추가합니다.```yaml
language: python
install:
- pip3 install --upgrade mobsfscan
script:
- mobsfscan .
```
#### Circle CI
`.circleci/config.yaml` 파일에 다음을 추가하세요.```yaml
version: 2.1
jobs:
mobsfscan:
docker:
- image: cimg/python:3.12
steps:
- checkout
- run:
name: Install mobsfscan
command: pip install --upgrade mobsfscan
- run:
name: mobsfscan check
command: mobsfscan .
```
#### Bitrise
`bitrise.yml` 파일에 다음을 추가하세요.```yaml
security_audit:
steps:
- activate-ssh-key@4:
run_if: '{{getenv "SSH_RSA_PRIVATE_KEY" | ne ""}}'
- [email protected]: {}
- mobsfscan@1: {}
- deploy-to-bitrise-io@2: {}
```
## Docker
### [DockerHub](https://hub.docker.com/r/opensecurity/mobsfscan)에서 미리 빌드된 이미지```bash
docker pull opensecurity/mobsfscan
docker run -v /path-to-source-dir:/src opensecurity/mobsfscan /src
```
### 로컬에서 빌드하기```
docker build -t mobsfscan .
docker run -v /path-to-source-dir:/src mobsfscan /src
```