 mgeeky/decode-spam-headers
이메일이 스팸으로 분류된 이유를 이해하는 데 도움이 되는 스크립트

일상적인 관리 업무를 위해 특정 이메일이 스팸/정크함에 들어간 이유를 이해하려고 하든, 레드팀 피싱 시뮬레이션 목적으로 이해하려고 하든, 이 스크립트가 도움을 드릴 수 있습니다!
아이디어는 MS Office365 E5 환경(MS Defender for Office365 탑재)을 대상으로 상업용 피싱 시뮬레이션을 진행하던 중 떠올랐습니다. 짐작하시겠지만, 피싱 시뮬레이션 관점에서 보면 상당히 까다로운 보안 스택입니다. 이 모든 Office365 SMTP 헤더를 수동으로 파고들어 SCL 값을 골라내려던 끝에, SMTP 헤더용 제대로 된 파서를 만들 때가 왔다는 결론에 도달했습니다.
시간이 지나면서 점점 더 많은 SMTP 헤더에 대한 지원을 추가하게 되었고, 그래서 이 도구가 탄생했습니다. 이제 수십 가지의 다양한 헤더를 이해하는 도구입니다.
이 도구는 입력으로 모든 SMTP 헤더가 포함된 *.EML 또는 *.txt 파일을 받습니다. 그런 다음 흥미로운 헤더의 하위 집합을 추출하고 105개 이상의 테스트를 사용하여 가능한 한 많이 디코딩을 시도합니다.
이 스크립트는 또한 모든 IPv4 주소와 도메인 이름을 추출하여 전체 DNS 조회를 수행합니다.
결과 출력에는 이 이메일이 차단되었을 수 있는 이유에 대한 유용한 정보가 포함됩니다.
클라이언트에게 보내기 전에 피싱 HTML 코드를 다듬고 싶다면, 제 phishing-HTML-linter.py에 입력으로 넣는 것도 고려해 보세요. HTML에서 스팸 점수를 높일 수 있는 악취 를 찾아내는 데 꽤 괜찮은 성능을 발휘합니다.
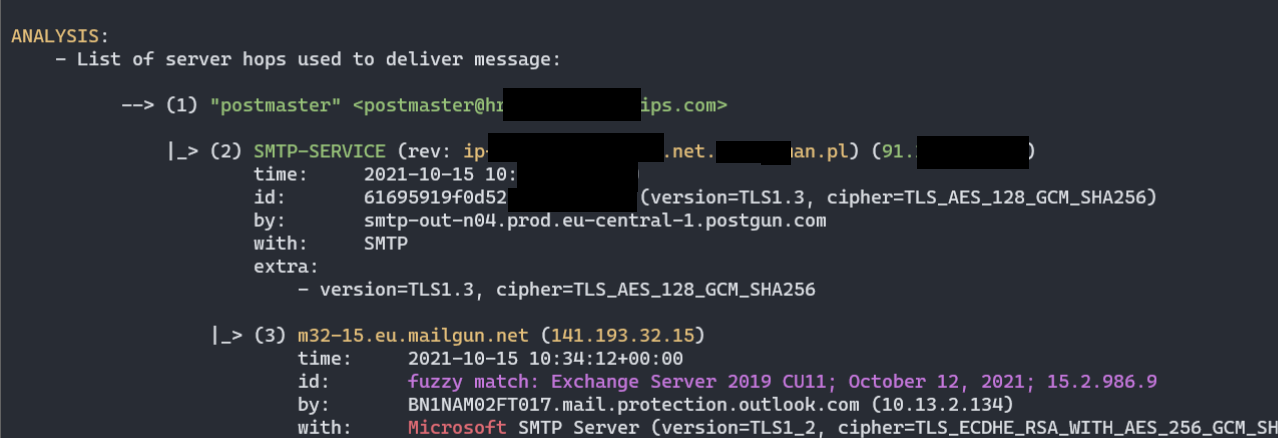
Received 헤더):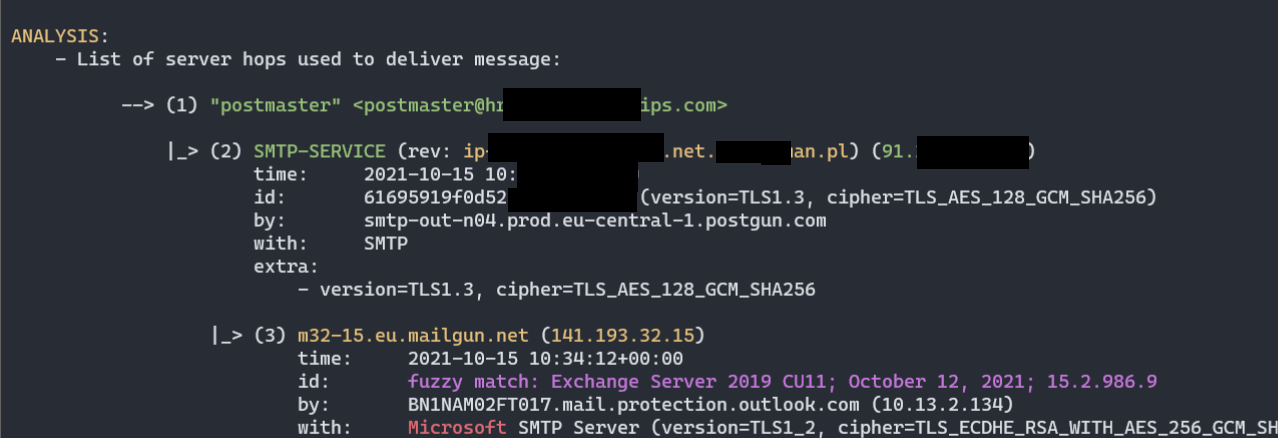
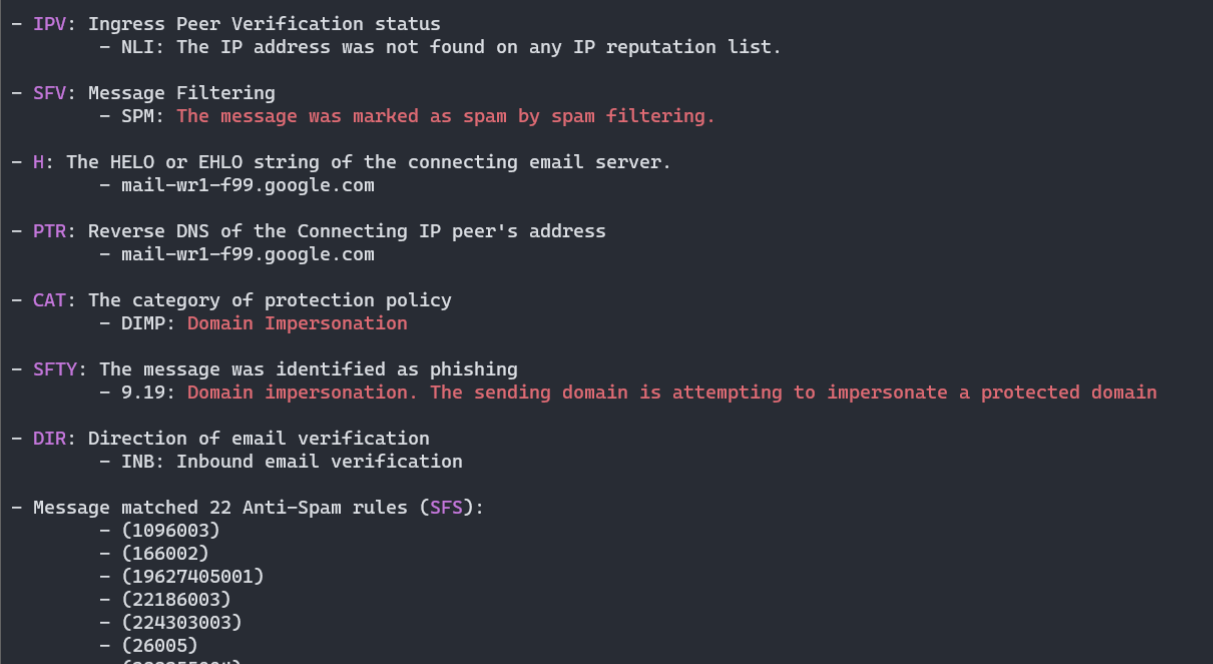
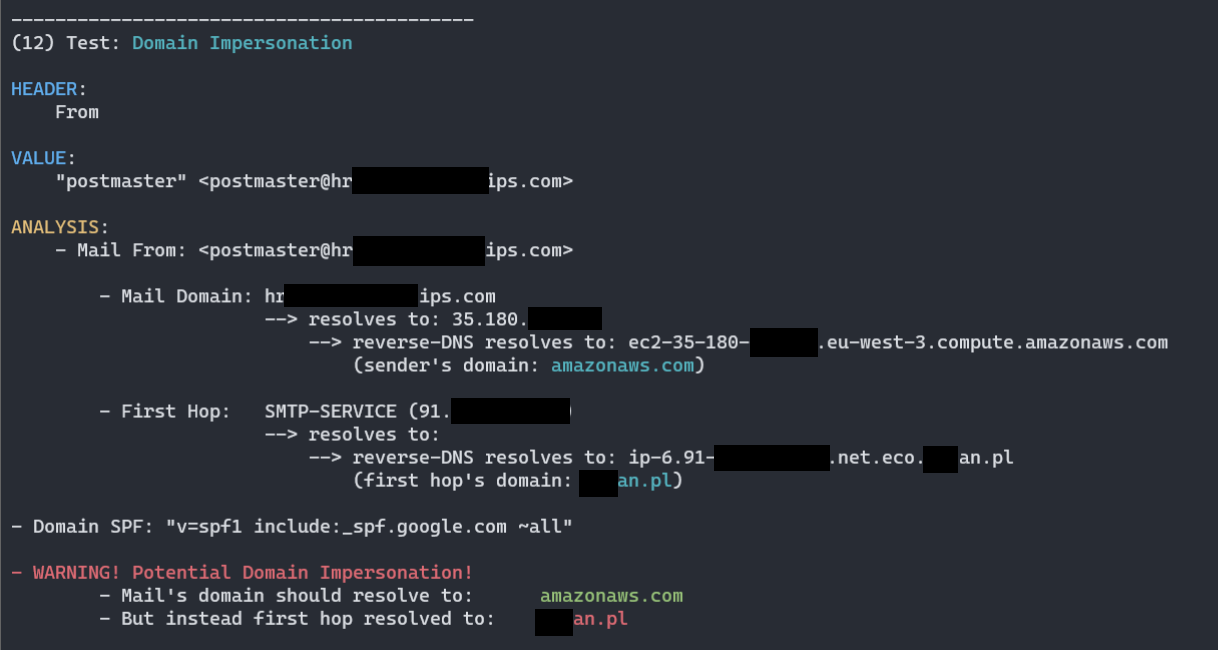

py decode-spam-headers.py headers.txt -f html -o report.html):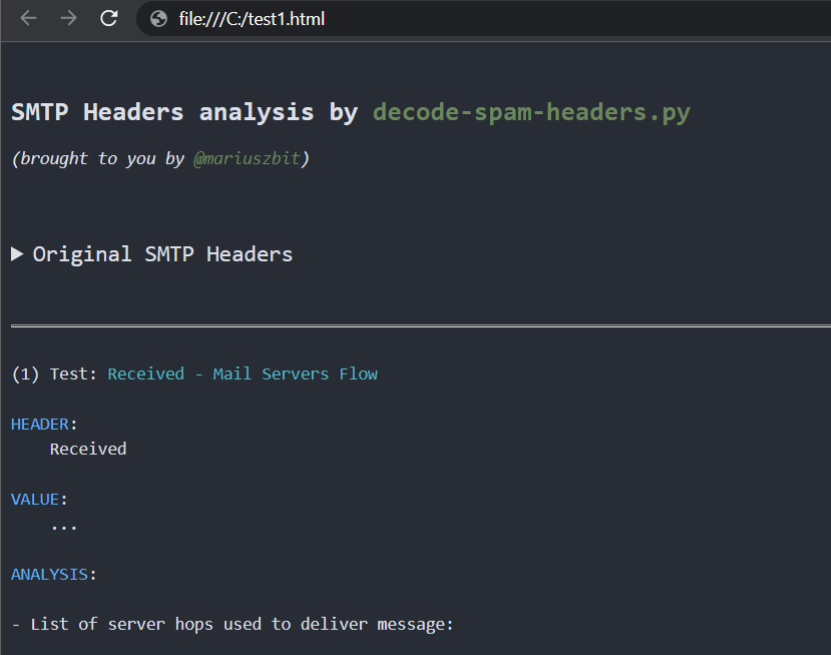
처리되는 헤더(85개 이상의 헤더가 파싱됨):
X-forefront-antispam-reportX-exchange-antispamX-exchange-antispam-mailbox-deliveryX-exchange-antispam-message-infoX-microsoft-antispam-report-cfa-testReceivedFromToSubjectThread-topicReceived-spfX-mailerX-originating-ipUser-agentX-forefront-antispam-reportX-microsoft-antispam-mailbox-deliveryX-microsoft-antispamX-exchange-antispam-report-cfa-testX-spam-statusX-spam-levelX-spam-flagX-spam-reportX-vr-spamcauseX-ovh-spam-reasonX-vr-spamscoreX-virus-scannedX-spam-checker-versionX-ironport-avX-ironport-anti-spam-filteredX-ironport-anti-spam-resultX-mimecast-spam-scoreSpamdiagnosticmetadataX-ms-exchange-atpmessagepropertiesX-msfblX-ms-exchange-transport-endtoendlatencyX-ms-oob-tlc-oobclassifiersX-ip-spam-verdictX-amp-resultX-ironport-remoteipX-ironport-reputationX-sbrsX-ironport-sendergroupX-policyX-ironport-mailflowpolicyX-remote-ipX-sea-spamX-fireeyeX-antiabuseX-tmase-versionX-tm-as-product-verX-tm-as-resultX-imss-scan-detailsX-tm-as-user-approved-senderX-tm-as-user-blocked-senderX-tmase-resultX-tmase-snap-resultX-imss-dkim-white-listX-tm-as-result-xfilterX-tm-as-smtpX-scanned-byX-mimecast-spam-signatureX-mimecast-bulk-signatureX-sender-ipX-forefront-antispam-report-untrustedX-microsoft-antispam-untrustedX-sophos-senderhistoryX-sophos-rescanX-MS-Exchange-CrossTenant-IdX-OriginatorOrgIronPort-DataIronPort-HdrOrdrX-DKIMDKIM-FilterX-SpamExperts-ClassX-SpamExperts-EvidenceX-Recommended-ActionX-AppInfoX-SpamX-TM-AS-MatchedIDX-MS-Exchange-EnableFirstContactSafetyTipX-MS-Exchange-Organization-BypassFocusedInboxX-MS-Exchange-SkipListedInternetSenderX-MS-Exchange-ExternalOriginalInternetSenderX-CNFS-AnalysisX-Authenticated-SenderX-Apparently-FromX-Env-SenderSender이 헤더들 대부분은 완전히 문서화되어 있지 않으므로, 이 스크립트가 모든 세부 사항을 정확히 집어내지는 못하지만, 적어도 제가 찾을 수 있는 모든 정보를 수집합니다.
(5) Test: X-Forefront-Antispam-Report
HEADER: X-Forefront-Antispam-Report
VALUE: CIP:209.85.167.100;CTRY:US;LANG:de;SCL:5;SRV:;IPV:NLI;SFV:SPM;H:mail-lf1-f100.google.com;PTR:mail-l f1-f100.google.com;CAT:DIMP;SFTY:9.19;SFS:(4636009)(956004)(166002)(6916009)(356005)(336012)(19 625305002)(22186003)(5660300002)(4744005)(6666004)(35100500006)(82960400001)(26005)(7596003)(7636003)(554460 02)(224303003)(1096003)(58800400005)(86362001)(9686003)(43540500002);DIR:INB;SFTY:9.19;
[...]
    - Message matched 24 Anti-Spam rules (SFS):           <============ opaque anti-spam rules
            - (1096003)
            - (166002)
            - (19625305002)
            - (22186003)
            - (224303003)
            - (26005)
            - (336012)
            - (356005)
            - (35100500006)         - (SPAM) Message contained embedded image.
이 프로세스는 순전히 수동으로 진행되며, 특별히 설계된 메일을 Office365 메일 서버로 전송한 다음 수집된 규칙을 수동으로 검토하고 연관시키는 방식입니다.

이미 60개 이상의 메일을 보냈으며, 지금까지 Microsoft의 규칙에 대해 알 수 있었던 내용은 다음과 같습니다:```py

    #
    # Below rules were collected solely in a trial-and-error manner or by scraping any
    # pieces of information from all around the Internet.
    #
    # They do not represent the actual Anti-Spam rule name or context and surely represent
    # something close to what is understood (or they may have totally different meaning).
    #
    # Until we'll be able to review anti-spam rules documention, there is no viable mean to map
    # rule ID to its meaning.
    #

    Anti_Spam_Rules_ReverseEngineered = \
    {
        '35100500006' : logger.colored('(SPAM) Message contained embedded image.', 'red'),

        # https://docs.microsoft.com/en-us/answers/questions/416100/what-is-meanings-of-39x-microsoft-antispam-mailbox.html
        '520007050' : logger.colored('(SPAM) Moved message to Spam and created Email Rule to move messages from this particular sender to Junk.', 'red'),

        # triggered on an empty mail with subject being: "test123 - viagra"
        '162623004' : 'Subject line contained suspicious words (like Viagra).',

        # triggered on mail with subject "test123" and body being single word "viagra"
        '19618925003' : 'Mail body contained suspicious words (like Viagra).',

        # triggered on mail with empty body and subject "Click here"
        '28233001' : 'Subject line contained suspicious words luring action (ex. "Click here"). ',

        # triggered on a mail with test subject and 1500 words of http://nietzsche-ipsum.com/
        '30864003' : 'Mail body contained a lot of text (more than 10.000 characters).',

        # mails that had simple message such as "Hello world" triggered this rule, whereas mails with
        # more than 150 words did not.
        '564344004' : 'HTML mail body with less than 150 words of text (not sure how much less though)',

        # message was sent with a basic html and only one <u> tag in body.
        '67856001' : 'HTML mail body contained underline <u> tag.',

        # message with html,head,body and body containing simple text with no b/i/u formatting.
        '579124003' : 'HTML mail body contained text, but no text formatting (<b>, <i>, <u>) was present',

        # This is a strong signal. Mails without <a> doesnt have this rule.
        '166002' : 'HTML mail body contained URL <a> link.',
